On September 21, 2026, Gartner predicted that by 2027, 60% of organizations that fail to address the cultural challenges of data and analytics governance will fail to govern AI successfully. Most teams already have a data governance framework on paper. The trouble starts when an auditor, a regulator, or your own AI program asks you to prove a policy was followed. This guide covers the seven parts of a framework and how signed records turn each rule into evidence.
What is a data governance framework?
The Federal Data Strategy’s playbook puts it plainly: “Data governance is the process of setting and enforcing priorities for managing and using data as a strategic asset.” A data governance framework is the structure that makes that process repeatable. It names who decides, what the rules are, where the rules are enforced, and what evidence shows they worked.
Most definitions stop at the first two. They describe owners, stewards, councils, and policy documents. Those matter, but a policy that lives only in a document can’t stop a bad record from entering a system, and it can’t prove anything after the fact.
So a working framework has four layers:
- Decision rights: who owns each kind of data and who can grant exceptions.
- Rules: policies and standards for quality, classification, access, and retention.
- Controls: the places in your systems where those rules actually run.
- Evidence: the records that show each rule ran, for each piece of data.
The last two layers are where most programs are thin. If your governance problem starts at intake, where forms and approvals create the data in the first place, see how a data governance platform that enforces policy at intake removes the silos that spreadsheets and one-off form tools leave behind.
The seven parts of a data governance framework
Frameworks such as DAMA-DMBOK and the DGI model use different names, but they cover the same ground. The table below adds the two columns most guides leave out: where each rule is enforced, and what evidence it leaves.
| Part | What it decides | Where it’s enforced | Evidence it leaves |
|---|---|---|---|
| Ownership and stewardship | Who is accountable for each data domain | Project and role setup | Named owners, role assignments |
| Policies and standards | What the rules are | Schemas, configuration, procedures | Versioned policy and schema history |
| Data quality | What a valid record looks like | Validation at the point of capture | Rejected submissions, validation logs |
| Classification and metadata | How sensitive each field is | Field settings, storage location | Field-level tags, separated collections |
| Access control | Who can read, create, change, or delete | Roles and permissions on every API call | Access logs tied to user IDs |
| Lifecycle and retention | How long data is kept and when it’s removed | Retention jobs, log pipelines | Retention settings, deletion records |
| Audit and evidence | How you show the rules held | Revisions, audit logs, signatures | Revision history, signed records |
Read the table from right to left and you get a test for your own program. For every part, can you point to the evidence column today? If the answer is “we’d have to ask someone,” that part of your framework exists on paper only.
Why most governance frameworks stall
Gartner’s view is that people, not budgets, are the usual blocker. Its survey of 223 data and analytics leaders in March 2026 found that cultural resistance outweighed funding constraints as the primary reason governance initiatives fail, 60% versus 40%. Its advice is to embed governance into business workflows instead of running it as a separate program.
The security data points the same way. In IBM’s Cost of a Data Breach Report 2026, 68% of breached organizations lacked governance to manage AI or detect shadow AI, and only 19% said their governance and security teams coordinated their efforts. The policies existed somewhere. The systems weren’t enforcing them.
There is a structural reason for that gap. Most governance tooling works downstream, in the warehouse, the lake, or the catalog, after data has already landed. The point of creation gets far less attention: the intake form, the approval step, the consent screen, the spreadsheet someone emailed around. By the time a catalog classifies a field, the record may already be wrong, over-shared, or impossible to trace back to the person who entered it.
Signed records: where governance becomes proof
The UK Information Commissioner’s Office describes accountability this way: “You must have appropriate measures and records in place to be able to demonstrate your compliance.” Measures and records. A framework supplies the measures. The records have to come from the systems that create and change the data.
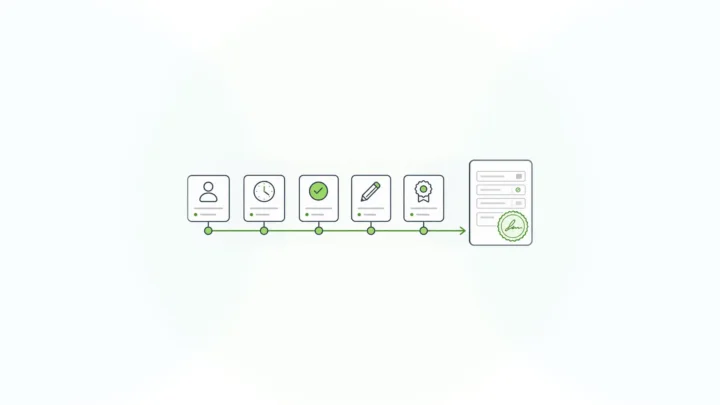
A signed record carries that evidence with it. It holds the data, the schema version it was captured against, who touched it, every later change, and a signature that shows whether the signed values still match. Four steps get you there.
Capture: the schema is the policy
Quality rules belong in the schema that collects the data. In Form.io, validation rules that run on the server are defined once in the form’s JSON schema, and the API rejects any submission that violates them, even one that skips the browser entirely. Form revisions that keep every schema version mean each submission records which version of the rules it was captured under.
Control: roles decide who reads and changes data
Access policy becomes real when every read and write passes through the same permission check. Role-based access ties each action to an authenticated identity and a role. For how that works across forms, APIs, and automated callers, see role-based access control for forms, APIs, and AI agents. For data that must stay apart by classification, Form.io’s Security Module can write submissions to separate database collections.
Change: every edit leaves a revision
Records change. Governance needs to show how. Submission revisions and server audit logging keep the complete state of a record at each change, with the user, the timestamp, and an optional note on why. Reverting creates a new revision instead of erasing history.
Commit: the signature covers the data
Some records need proof of a decision: a consent, an approval, an attestation. E-Sign+ digital signatures sign the submission data inside your own environment. The signature attaches to the submission data itself: change the data, and the signature breaks. So the record can show, on its own, that the signed values haven’t changed since the moment of signing.
How to build a data governance framework you can prove
You don’t need to govern everything at once. Start where the obligations are.
- List the records that carry obligations. Consents, approvals, attestations, disclosures, and regulated intake come first. These are the records an auditor will ask about.
- Name an owner and a steward for each record type. Owners decide policy. Stewards handle exceptions and quality issues.
- Write each policy into the schema. Required fields, formats, conditional rules, and allowed values should be enforced by the system, not described in a wiki.
- Map roles to actions. Decide who can create, read, update, delete, and sign each record type, and apply that on the API, not only in the interface.
- Turn on revisions and audit logs, then set retention. Route logs to the tools your security team already uses. Form.io doesn’t impose retention limits, so your own retention policy sets how long revisions and logs are kept.
- Sign the records that need proof of a decision. Use signatures where you must later show that nobody changed what was agreed.
- Hold AI agents to the same rules. IBM found only 40% of organizations use access controls on AI models and data. With the Universal Agent Gateway (UAG), agents authenticate like users, inherit your RBAC, and send data through the same validation pipeline as your human forms, with every action logged.
Where Form.io fits, and where it doesn’t
Form.io sits at the point of creation. It turns forms into governed data capture: one JSON schema that drives the form, the validation, and the API, with roles, revisions, audit logs, and signatures on the same record. A self-hosted Form.io deployment runs inside your own environment; apart from license validation, which sends only the license key, it doesn’t contact Form.io servers. That lets it fit within your SOC 2 Type II and ISO 27001 controls. For how that maps to compliance programs, see compliance management software for SOC 2 and ISO data collection.
Public-sector teams use it too. As the Dept. of Justice, Ireland put it on the Form.io home page: “Of all the systems we use to deliver our end products, Form.io has been probably the most straightforward and issue free to use, with excellent support.”
Form.io is the wrong tool for some governance jobs. It isn’t a data catalog, a master data management system, or a lineage tool for hundreds of warehouse pipelines; pair it with those. If you only need a quick internal survey with no regulatory weight, the extra structure may be more than you need. And no tool makes you compliant on its own. Your policies, controls, and auditors decide that.
Key Takeaways
- A working framework needs four layers: decision rights, rules, controls, and evidence.
- For each of the seven parts, know where the rule is enforced and what evidence it leaves.
- Governance stalls when it lives in documents and downstream tools instead of the systems that create data.
- Put quality rules in the schema, access rules on every API call, and change history on every record.
- Sign the records that need proof of a decision, so the record itself shows nothing changed.
- Apply the same access and validation rules to AI agents as to people.
FAQ
What is a data governance framework?
A data governance framework is the structure an organization uses to decide who owns data, what rules apply to it, where those rules are enforced, and how it proves they were followed. It usually covers ownership, policies, quality, classification, access, lifecycle, and audit.
What are the seven parts of data governance?
Most frameworks include seven parts: ownership and stewardship, policies and standards, data quality, classification and metadata, access control, lifecycle and retention, and audit and evidence. Named models such as DAMA-DMBOK and the DGI framework group them differently but cover the same areas.
What is the difference between data governance and data management?
Data governance sets the decisions and rules: who owns data, what is allowed, and how compliance is shown. Data management is the day-to-day work of storing, moving, cleaning, and securing data under those rules. Governance without management is a document; management without governance has no agreed rules.
Who owns a data governance framework?
A governance body, often chaired by a chief data officer, owns the framework and its policies. Data owners in each business area are accountable for their domains, and data stewards handle quality issues, access requests, and exceptions day to day.
How do signed records support data governance?
A signed record shows who signed, when, against which version of the form, and whether the signed values have changed since. That turns a policy such as “approvals can’t be altered after sign-off” into something you can check on the record itself, instead of relying on a separate log or a person’s memory.
Does a governance framework make an organization compliant?
No framework or tool makes an organization compliant by itself. Compliance depends on your policies, controls, and auditors. A good framework, and systems that enforce it, give you the evidence to demonstrate accountability when you’re asked.
How does data governance apply to AI agents?
AI agents should be treated like any other user of governed data. They should authenticate, hold a role, pass the same validation as human submissions, and leave the same audit trail. Gartner expects many organizations to struggle to govern AI without first fixing their data governance foundations.
Schedule a Call