# Form.io - Full Content
Form.io is a self-hosted developer productivity platform that uses JSON schema as a single source of truth for forms, APIs, and agentic workflows. It is middleware infrastructure: every form generates a REST API automatically, configurable server-side Actions handle integrations and authentication, and the Universal Agent Gateway (UAG) extends the same JSON schemas into runtime context, guardrails, and data access for AI agents. Regulated industries — government, financial services, healthcare, insurance — deploy Form.io entirely inside their own IT environment and achieve their own compliance certifications (FedRAMP, HIPAA, etc.) on top of it.
---
# From 60 Pages to a Single Click: How Form.io Powered a Government Agency's Digitization
*Published:* 2026-06-15
*Author:* Form.io Wizard
*URL:* https://form.io/case-studies/from-60-pages-to-a-single-click/
From Paper-Based Applications and Processing Backlogs to a Fully Digital Portal Handling Over a Dozen Form/Data Processes
June 15, 2026 [  ](https://form.io/case-studies/from-60-pages-to-a-single-click/)### Download Case Study:
Compare audit trail software needs for enterprise forms: audit logs, form revisions, submission history, staged promotion, and self-hosted controls.
Learn when a web form builder is enough, when forms need APIs and workflow control, and how Form.io fits self-hosted enterprise form infrastructure.
Compare e signature software for enterprise form workflows, including DocuSign alternatives, self-hosting, audit trails, APIs, and Form.io E-Sign+.
Compare JSON Schema validator tools for production apps: Ajv, Python libraries, form generators, API contracts, governance, and Form.io infrastructure.
Compare embedded forms and white-label form builders for B2B SaaS teams, from simple embeds to governed APIs, tenant controls, and secure data ownership.
Evaluate claims management software through the form infrastructure behind FNOL, documents, APIs, audit trails, PDFs, and regulated insurance workflows.
Evaluate KYC onboarding software for banks and fintechs through forms, APIs, identity checks, audit trails, self-hosted control, and governed workflows.
Compare Typeform alternatives for surveys, self-hosting, compliance, embedded forms, APIs, governance, and infrastructure fit for regulated teams in 2026.
Compare Jotform alternatives for regulated teams needing self-hosted forms, APIs, audit trails, permissions, embedded workflows, and better data control.
Compare Formbricks and Form.io across open source surveys, self-hosting, APIs, embedding, governance, pricing, and form infrastructure use cases for teams.
Compare Budibase and Form.io across forms, APIs, self-hosting, governance, embedding, pricing, and best-fit use cases for enterprise form infrastructure.
Compare HIPAA-compliant form builder options for healthcare SaaS teams, from BAAs and audit logs to APIs, self-hosting, and PHI control.
Your First Custom Form.io Theme: Solving the most common use case: CSS class overrides.
When “Close Enough” Stops Being Good Enough and You Need Your Forms to Match the Rest of Your Application, Pixel-for-Pixel.
Compare MCP server list options for regulated enterprise developers. See official registries, GitHub, AWS, Playwright, Form.io, and governance criteria.
Compare AI governance platform layers for agentic workflows, including Form.io UAG, Appian, Camunda 8.9, Flowable 2025.1, and Microsoft AGT.
#### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# From Six-Week Release Cycles To Same-Day Form Changes - Patagonia Health
*Published:* 2026-06-15
*Author:* Form.io Wizard
*URL:* https://form.io/case-studies/from-six-week-release-cycles-to-same-day-form-changes-patagonia-health/
How Patagonia Health Made Form.io The Default Across 60+ Public And Behavioral Health Customers
June 15, 2026 [  ](https://form.io/case-studies/from-six-week-release-cycles-to-same-day-form-changes-patagonia-health/)### Download Case Study:
Compare audit trail software needs for enterprise forms: audit logs, form revisions, submission history, staged promotion, and self-hosted controls.
Learn when a web form builder is enough, when forms need APIs and workflow control, and how Form.io fits self-hosted enterprise form infrastructure.
Compare e signature software for enterprise form workflows, including DocuSign alternatives, self-hosting, audit trails, APIs, and Form.io E-Sign+.
Compare JSON Schema validator tools for production apps: Ajv, Python libraries, form generators, API contracts, governance, and Form.io infrastructure.
Compare embedded forms and white-label form builders for B2B SaaS teams, from simple embeds to governed APIs, tenant controls, and secure data ownership.
Evaluate claims management software through the form infrastructure behind FNOL, documents, APIs, audit trails, PDFs, and regulated insurance workflows.
Evaluate KYC onboarding software for banks and fintechs through forms, APIs, identity checks, audit trails, self-hosted control, and governed workflows.
Compare Typeform alternatives for surveys, self-hosting, compliance, embedded forms, APIs, governance, and infrastructure fit for regulated teams in 2026.
Compare Jotform alternatives for regulated teams needing self-hosted forms, APIs, audit trails, permissions, embedded workflows, and better data control.
Compare Formbricks and Form.io across open source surveys, self-hosting, APIs, embedding, governance, pricing, and form infrastructure use cases for teams.
Compare Budibase and Form.io across forms, APIs, self-hosting, governance, embedding, pricing, and best-fit use cases for enterprise form infrastructure.
Compare HIPAA-compliant form builder options for healthcare SaaS teams, from BAAs and audit logs to APIs, self-hosting, and PHI control.
Your First Custom Form.io Theme: Solving the most common use case: CSS class overrides.
When “Close Enough” Stops Being Good Enough and You Need Your Forms to Match the Rest of Your Application, Pixel-for-Pixel.
Compare MCP server list options for regulated enterprise developers. See official registries, GitHub, AWS, Playwright, Form.io, and governance criteria.
Compare AI governance platform layers for agentic workflows, including Form.io UAG, Appian, Camunda 8.9, Flowable 2025.1, and Microsoft AGT.
#### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# Accelerated Development Timeline By Two Years
*Published:* 2025-05-07
*Author:* Form.io Wizard
*URL:* https://form.io/case-studies/accelerated-development-time-line-by-two-years/
*Description:* Insurance customer cut a multi-year build cycle to under a year by replacing a custom form/API stack with Form.io.
How Vasion Went From An Open Source Sandbox To A Full-Fledged Enterprise Product As A Form.io Partner
May 7, 2025 [  ](https://form.io/case-studies/accelerated-development-time-line-by-two-years/)### Download Case Study:
Compare audit trail software needs for enterprise forms: audit logs, form revisions, submission history, staged promotion, and self-hosted controls.
Learn when a web form builder is enough, when forms need APIs and workflow control, and how Form.io fits self-hosted enterprise form infrastructure.
Compare e signature software for enterprise form workflows, including DocuSign alternatives, self-hosting, audit trails, APIs, and Form.io E-Sign+.
Compare JSON Schema validator tools for production apps: Ajv, Python libraries, form generators, API contracts, governance, and Form.io infrastructure.
Compare embedded forms and white-label form builders for B2B SaaS teams, from simple embeds to governed APIs, tenant controls, and secure data ownership.
Evaluate claims management software through the form infrastructure behind FNOL, documents, APIs, audit trails, PDFs, and regulated insurance workflows.
Evaluate KYC onboarding software for banks and fintechs through forms, APIs, identity checks, audit trails, self-hosted control, and governed workflows.
Compare Typeform alternatives for surveys, self-hosting, compliance, embedded forms, APIs, governance, and infrastructure fit for regulated teams in 2026.
Compare Jotform alternatives for regulated teams needing self-hosted forms, APIs, audit trails, permissions, embedded workflows, and better data control.
Compare Formbricks and Form.io across open source surveys, self-hosting, APIs, embedding, governance, pricing, and form infrastructure use cases for teams.
Compare Budibase and Form.io across forms, APIs, self-hosting, governance, embedding, pricing, and best-fit use cases for enterprise form infrastructure.
Compare HIPAA-compliant form builder options for healthcare SaaS teams, from BAAs and audit logs to APIs, self-hosting, and PHI control.
Your First Custom Form.io Theme: Solving the most common use case: CSS class overrides.
When “Close Enough” Stops Being Good Enough and You Need Your Forms to Match the Rest of Your Application, Pixel-for-Pixel.
Compare MCP server list options for regulated enterprise developers. See official registries, GitHub, AWS, Playwright, Form.io, and governance criteria.
Compare AI governance platform layers for agentic workflows, including Form.io UAG, Appian, Camunda 8.9, Flowable 2025.1, and Microsoft AGT.
#### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# The Digital Transformation Of Supporting New Services For The German Public Sector—On Repeat
*Published:* 2024-12-02
*Author:* Form.io Wizard
*URL:* https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/
*Description:* German public-sector deployment reused as the standard intake platform across regulated government services.
How publicplan GmbH Underwent Digital Transformation To Support Over 400 Services And 1,000+ Forms With Strict Standards And A Short Timeline
December 2, 2024 [  ](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)### Download Case Study:
Compare audit trail software needs for enterprise forms: audit logs, form revisions, submission history, staged promotion, and self-hosted controls.
Learn when a web form builder is enough, when forms need APIs and workflow control, and how Form.io fits self-hosted enterprise form infrastructure.
Compare e signature software for enterprise form workflows, including DocuSign alternatives, self-hosting, audit trails, APIs, and Form.io E-Sign+.
Compare JSON Schema validator tools for production apps: Ajv, Python libraries, form generators, API contracts, governance, and Form.io infrastructure.
Compare embedded forms and white-label form builders for B2B SaaS teams, from simple embeds to governed APIs, tenant controls, and secure data ownership.
Evaluate claims management software through the form infrastructure behind FNOL, documents, APIs, audit trails, PDFs, and regulated insurance workflows.
Evaluate KYC onboarding software for banks and fintechs through forms, APIs, identity checks, audit trails, self-hosted control, and governed workflows.
Compare Typeform alternatives for surveys, self-hosting, compliance, embedded forms, APIs, governance, and infrastructure fit for regulated teams in 2026.
Compare Jotform alternatives for regulated teams needing self-hosted forms, APIs, audit trails, permissions, embedded workflows, and better data control.
Compare Formbricks and Form.io across open source surveys, self-hosting, APIs, embedding, governance, pricing, and form infrastructure use cases for teams.
Compare Budibase and Form.io across forms, APIs, self-hosting, governance, embedding, pricing, and best-fit use cases for enterprise form infrastructure.
Compare HIPAA-compliant form builder options for healthcare SaaS teams, from BAAs and audit logs to APIs, self-hosting, and PHI control.
Your First Custom Form.io Theme: Solving the most common use case: CSS class overrides.
When “Close Enough” Stops Being Good Enough and You Need Your Forms to Match the Rest of Your Application, Pixel-for-Pixel.
Compare MCP server list options for regulated enterprise developers. See official registries, GitHub, AWS, Playwright, Form.io, and governance criteria.
Compare AI governance platform layers for agentic workflows, including Form.io UAG, Appian, Camunda 8.9, Flowable 2025.1, and Microsoft AGT.
#### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# From Open Source Forms To Enterprise In 3 Weeks To Service 1000s Of Processes
*Published:* 2024-11-13
*Author:* Form.io Wizard
*URL:* https://form.io/case-studies/from-open-source-forms-to-enterprise-in-3-weeks-to-service-1000s-of-processes/
*Description:* Migration from formio.js OSS to Form.io Enterprise in 3 weeks; now serves thousands of government / regulated processes.
How Texas Tech University Saved Months Launching New Enrollment Management Services And Switched From Open Source Forms To Enterprise In 3 Weeks
November 13, 2024 [  ](https://form.io/case-studies/from-open-source-forms-to-enterprise-in-3-weeks-to-service-1000s-of-processes/)### Download Case Study:
Compare audit trail software needs for enterprise forms: audit logs, form revisions, submission history, staged promotion, and self-hosted controls.
Learn when a web form builder is enough, when forms need APIs and workflow control, and how Form.io fits self-hosted enterprise form infrastructure.
Compare e signature software for enterprise form workflows, including DocuSign alternatives, self-hosting, audit trails, APIs, and Form.io E-Sign+.
Compare JSON Schema validator tools for production apps: Ajv, Python libraries, form generators, API contracts, governance, and Form.io infrastructure.
Compare embedded forms and white-label form builders for B2B SaaS teams, from simple embeds to governed APIs, tenant controls, and secure data ownership.
Evaluate claims management software through the form infrastructure behind FNOL, documents, APIs, audit trails, PDFs, and regulated insurance workflows.
Evaluate KYC onboarding software for banks and fintechs through forms, APIs, identity checks, audit trails, self-hosted control, and governed workflows.
Compare Typeform alternatives for surveys, self-hosting, compliance, embedded forms, APIs, governance, and infrastructure fit for regulated teams in 2026.
Compare Jotform alternatives for regulated teams needing self-hosted forms, APIs, audit trails, permissions, embedded workflows, and better data control.
Compare Formbricks and Form.io across open source surveys, self-hosting, APIs, embedding, governance, pricing, and form infrastructure use cases for teams.
Compare Budibase and Form.io across forms, APIs, self-hosting, governance, embedding, pricing, and best-fit use cases for enterprise form infrastructure.
Compare HIPAA-compliant form builder options for healthcare SaaS teams, from BAAs and audit logs to APIs, self-hosting, and PHI control.
Your First Custom Form.io Theme: Solving the most common use case: CSS class overrides.
When “Close Enough” Stops Being Good Enough and You Need Your Forms to Match the Rest of Your Application, Pixel-for-Pixel.
Compare MCP server list options for regulated enterprise developers. See official registries, GitHub, AWS, Playwright, Form.io, and governance criteria.
Compare AI governance platform layers for agentic workflows, including Form.io UAG, Appian, Camunda 8.9, Flowable 2025.1, and Microsoft AGT.
#### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# Formio-Enterprise 9.8.0 and PDF-Server 5.14.0
*Published:* 2026-06-05
*Author:* Lane Doughtie
*URL:* https://form.io/release-notes/formio-enterprise-9-8-0-and-pdf-server-5-14-0/
We’re pleased to announce the release of Form.io Enterprise v9.8.0 and PDF-Server v5.14.0. This release brings dynamic translation support to PDF generation, conflict resolution to the Enterprise Form Builder Module, … [Continue reading Formio-Enterprise 9.8.0 and PDF-Server 5.14.0](https://form.io/release-notes/formio-enterprise-9-8-0-and-pdf-server-5-14-0/)
June 5, 2026 [  ](https://form.io/release-notes/formio-enterprise-9-8-0-and-pdf-server-5-14-0/)Compare audit trail software needs for enterprise forms: audit logs, form revisions, submission history, staged promotion, and self-hosted controls.
Learn when a web form builder is enough, when forms need APIs and workflow control, and how Form.io fits self-hosted enterprise form infrastructure.
Compare e signature software for enterprise form workflows, including DocuSign alternatives, self-hosting, audit trails, APIs, and Form.io E-Sign+.
Compare JSON Schema validator tools for production apps: Ajv, Python libraries, form generators, API contracts, governance, and Form.io infrastructure.
Compare embedded forms and white-label form builders for B2B SaaS teams, from simple embeds to governed APIs, tenant controls, and secure data ownership.
Evaluate claims management software through the form infrastructure behind FNOL, documents, APIs, audit trails, PDFs, and regulated insurance workflows.
Evaluate KYC onboarding software for banks and fintechs through forms, APIs, identity checks, audit trails, self-hosted control, and governed workflows.
Compare Typeform alternatives for surveys, self-hosting, compliance, embedded forms, APIs, governance, and infrastructure fit for regulated teams in 2026.
Compare Jotform alternatives for regulated teams needing self-hosted forms, APIs, audit trails, permissions, embedded workflows, and better data control.
Compare Formbricks and Form.io across open source surveys, self-hosting, APIs, embedding, governance, pricing, and form infrastructure use cases for teams.
Compare Budibase and Form.io across forms, APIs, self-hosting, governance, embedding, pricing, and best-fit use cases for enterprise form infrastructure.
Compare HIPAA-compliant form builder options for healthcare SaaS teams, from BAAs and audit logs to APIs, self-hosting, and PHI control.
Your First Custom Form.io Theme: Solving the most common use case: CSS class overrides.
When “Close Enough” Stops Being Good Enough and You Need Your Forms to Match the Rest of Your Application, Pixel-for-Pixel.
Compare MCP server list options for regulated enterprise developers. See official registries, GitHub, AWS, Playwright, Form.io, and governance criteria.
Compare AI governance platform layers for agentic workflows, including Form.io UAG, Appian, Camunda 8.9, Flowable 2025.1, and Microsoft AGT.
# [AI Governance Platform: Agentic Workflow Governance Layers Compared](https://form.io/ai-governance-platform-agentic-workflow-governance-layers-compared/)
Compare AI governance platform layers for agentic workflows, including Form.io UAG, Appian, Camunda 8.9, Flowable 2025.1, and Microsoft AGT.
June 5, 2026 ### To track specific tickets within, please reference the:
#### Recent Release Notes
# [](https://form.io/release-notes/formio-enterprise-9-8-0-and-pdf-server-5-14-0/)[Formio-Enterprise 9.8.0 and PDF-Server 5.14.0](https://form.io/release-notes/formio-enterprise-9-8-0-and-pdf-server-5-14-0/)
# June 5, 2026 [](https://form.io/release-notes/formio-enterprise-9-7-0/)[Formio-Enterprise 9.7.0](https://form.io/release-notes/formio-enterprise-9-7-0/)
# February 4, 2026 [](https://form.io/release-notes/formio-enterprise-9-6-0/)[Formio-Enterprise 9.6.0](https://form.io/release-notes/formio-enterprise-9-6-0/)
# September 12, 2025 [](https://form.io/release-notes/formio-enterprise-9-4-0/)[Formio-Enterprise 9.4.0](https://form.io/release-notes/formio-enterprise-9-4-0/)
April 10, 2025 #### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# Formio-Enterprise 9.7.0
*Published:* 2026-02-04
*Author:* Lane Doughtie
*URL:* https://form.io/release-notes/formio-enterprise-9-7-0/
*Description:* E-Sign+ module added. Audit trail expanded with submission-level diff history.
We’re incredibly excited to announce the release of Form.io Enterprise v9.7.0! This release introduces E-Sign+, a new module that provides a zero-trust, API-driven approach to capturing and verifying digital signatures. … [Continue reading Formio-Enterprise 9.7.0](https://form.io/release-notes/formio-enterprise-9-7-0/)
February 4, 2026 [  ](https://form.io/release-notes/formio-enterprise-9-7-0/)Compare audit trail software needs for enterprise forms: audit logs, form revisions, submission history, staged promotion, and self-hosted controls.
Learn when a web form builder is enough, when forms need APIs and workflow control, and how Form.io fits self-hosted enterprise form infrastructure.
Compare e signature software for enterprise form workflows, including DocuSign alternatives, self-hosting, audit trails, APIs, and Form.io E-Sign+.
Compare JSON Schema validator tools for production apps: Ajv, Python libraries, form generators, API contracts, governance, and Form.io infrastructure.
Compare embedded forms and white-label form builders for B2B SaaS teams, from simple embeds to governed APIs, tenant controls, and secure data ownership.
Evaluate claims management software through the form infrastructure behind FNOL, documents, APIs, audit trails, PDFs, and regulated insurance workflows.
Evaluate KYC onboarding software for banks and fintechs through forms, APIs, identity checks, audit trails, self-hosted control, and governed workflows.
Compare Typeform alternatives for surveys, self-hosting, compliance, embedded forms, APIs, governance, and infrastructure fit for regulated teams in 2026.
Compare Jotform alternatives for regulated teams needing self-hosted forms, APIs, audit trails, permissions, embedded workflows, and better data control.
Compare Formbricks and Form.io across open source surveys, self-hosting, APIs, embedding, governance, pricing, and form infrastructure use cases for teams.
Compare Budibase and Form.io across forms, APIs, self-hosting, governance, embedding, pricing, and best-fit use cases for enterprise form infrastructure.
Compare HIPAA-compliant form builder options for healthcare SaaS teams, from BAAs and audit logs to APIs, self-hosting, and PHI control.
Your First Custom Form.io Theme: Solving the most common use case: CSS class overrides.
When “Close Enough” Stops Being Good Enough and You Need Your Forms to Match the Rest of Your Application, Pixel-for-Pixel.
Compare MCP server list options for regulated enterprise developers. See official registries, GitHub, AWS, Playwright, Form.io, and governance criteria.
Compare AI governance platform layers for agentic workflows, including Form.io UAG, Appian, Camunda 8.9, Flowable 2025.1, and Microsoft AGT.
# [AI Governance Platform: Agentic Workflow Governance Layers Compared](https://form.io/ai-governance-platform-agentic-workflow-governance-layers-compared/)
Compare AI governance platform layers for agentic workflows, including Form.io UAG, Appian, Camunda 8.9, Flowable 2025.1, and Microsoft AGT.
June 5, 2026 ### To track specific tickets within, please reference the:
#### Recent Release Notes
# [](https://form.io/release-notes/formio-enterprise-9-8-0-and-pdf-server-5-14-0/)[Formio-Enterprise 9.8.0 and PDF-Server 5.14.0](https://form.io/release-notes/formio-enterprise-9-8-0-and-pdf-server-5-14-0/)
# June 5, 2026 [](https://form.io/release-notes/formio-enterprise-9-7-0/)[Formio-Enterprise 9.7.0](https://form.io/release-notes/formio-enterprise-9-7-0/)
# February 4, 2026 [](https://form.io/release-notes/formio-enterprise-9-6-0/)[Formio-Enterprise 9.6.0](https://form.io/release-notes/formio-enterprise-9-6-0/)
# September 12, 2025 [](https://form.io/release-notes/formio-enterprise-9-4-0/)[Formio-Enterprise 9.4.0](https://form.io/release-notes/formio-enterprise-9-4-0/)
April 10, 2025 #### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# Formio-Enterprise 9.6.0
*Published:* 2025-09-12
*Author:* Lane Doughtie
*URL:* https://form.io/release-notes/formio-enterprise-9-6-0/
*Description:* File components rendered inside Review Pages with clickable image previews; otherwise a maintenance release covering minor bug fixes and dependency / security updates.
We’re excited to announce the release of Form.io Enterprise v9.6.0! This release emphasizes minor bug fixes and dependency/security updates. The Form.io SaaS (portal.form.io) will be upgraded soon with version 9.6.0. … [Continue reading Formio-Enterprise 9.6.0](https://form.io/release-notes/formio-enterprise-9-6-0/)
September 12, 2025 [  ](https://form.io/release-notes/formio-enterprise-9-6-0/)Compare audit trail software needs for enterprise forms: audit logs, form revisions, submission history, staged promotion, and self-hosted controls.
Learn when a web form builder is enough, when forms need APIs and workflow control, and how Form.io fits self-hosted enterprise form infrastructure.
Compare e signature software for enterprise form workflows, including DocuSign alternatives, self-hosting, audit trails, APIs, and Form.io E-Sign+.
Compare JSON Schema validator tools for production apps: Ajv, Python libraries, form generators, API contracts, governance, and Form.io infrastructure.
Compare embedded forms and white-label form builders for B2B SaaS teams, from simple embeds to governed APIs, tenant controls, and secure data ownership.
Evaluate claims management software through the form infrastructure behind FNOL, documents, APIs, audit trails, PDFs, and regulated insurance workflows.
Evaluate KYC onboarding software for banks and fintechs through forms, APIs, identity checks, audit trails, self-hosted control, and governed workflows.
Compare Typeform alternatives for surveys, self-hosting, compliance, embedded forms, APIs, governance, and infrastructure fit for regulated teams in 2026.
Compare Jotform alternatives for regulated teams needing self-hosted forms, APIs, audit trails, permissions, embedded workflows, and better data control.
Compare Formbricks and Form.io across open source surveys, self-hosting, APIs, embedding, governance, pricing, and form infrastructure use cases for teams.
Compare Budibase and Form.io across forms, APIs, self-hosting, governance, embedding, pricing, and best-fit use cases for enterprise form infrastructure.
Compare HIPAA-compliant form builder options for healthcare SaaS teams, from BAAs and audit logs to APIs, self-hosting, and PHI control.
Your First Custom Form.io Theme: Solving the most common use case: CSS class overrides.
When “Close Enough” Stops Being Good Enough and You Need Your Forms to Match the Rest of Your Application, Pixel-for-Pixel.
Compare MCP server list options for regulated enterprise developers. See official registries, GitHub, AWS, Playwright, Form.io, and governance criteria.
Compare AI governance platform layers for agentic workflows, including Form.io UAG, Appian, Camunda 8.9, Flowable 2025.1, and Microsoft AGT.
# [AI Governance Platform: Agentic Workflow Governance Layers Compared](https://form.io/ai-governance-platform-agentic-workflow-governance-layers-compared/)
Compare AI governance platform layers for agentic workflows, including Form.io UAG, Appian, Camunda 8.9, Flowable 2025.1, and Microsoft AGT.
June 5, 2026 ### To track specific tickets within, please reference the:
#### Recent Release Notes
# [](https://form.io/release-notes/formio-enterprise-9-8-0-and-pdf-server-5-14-0/)[Formio-Enterprise 9.8.0 and PDF-Server 5.14.0](https://form.io/release-notes/formio-enterprise-9-8-0-and-pdf-server-5-14-0/)
# June 5, 2026 [](https://form.io/release-notes/formio-enterprise-9-7-0/)[Formio-Enterprise 9.7.0](https://form.io/release-notes/formio-enterprise-9-7-0/)
# February 4, 2026 [](https://form.io/release-notes/formio-enterprise-9-6-0/)[Formio-Enterprise 9.6.0](https://form.io/release-notes/formio-enterprise-9-6-0/)
# September 12, 2025 [](https://form.io/release-notes/formio-enterprise-9-4-0/)[Formio-Enterprise 9.4.0](https://form.io/release-notes/formio-enterprise-9-4-0/)
April 10, 2025 #### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# Introducing E-Sign+: Enterprise Digital Signatures for Self-Hosted Applications
*Published:* 2026-07-07
*Author:* Form.io Wizard
*URL:* https://form.io/product-announcement/introducing-e-sign-plus-enterprise-digital-signatures-for-self-hosted-applications/
Keep digital signatures inside your own environment, built for enterprise security, governance, and compliance.
July 7, 2026 [  ](https://form.io/product-announcement/introducing-e-sign-plus-enterprise-digital-signatures-for-self-hosted-applications/)Compare audit trail software needs for enterprise forms: audit logs, form revisions, submission history, staged promotion, and self-hosted controls.
Learn when a web form builder is enough, when forms need APIs and workflow control, and how Form.io fits self-hosted enterprise form infrastructure.
Compare e signature software for enterprise form workflows, including DocuSign alternatives, self-hosting, audit trails, APIs, and Form.io E-Sign+.
Compare JSON Schema validator tools for production apps: Ajv, Python libraries, form generators, API contracts, governance, and Form.io infrastructure.
Compare embedded forms and white-label form builders for B2B SaaS teams, from simple embeds to governed APIs, tenant controls, and secure data ownership.
Evaluate claims management software through the form infrastructure behind FNOL, documents, APIs, audit trails, PDFs, and regulated insurance workflows.
Evaluate KYC onboarding software for banks and fintechs through forms, APIs, identity checks, audit trails, self-hosted control, and governed workflows.
Compare Typeform alternatives for surveys, self-hosting, compliance, embedded forms, APIs, governance, and infrastructure fit for regulated teams in 2026.
Compare Jotform alternatives for regulated teams needing self-hosted forms, APIs, audit trails, permissions, embedded workflows, and better data control.
Compare Formbricks and Form.io across open source surveys, self-hosting, APIs, embedding, governance, pricing, and form infrastructure use cases for teams.
Compare Budibase and Form.io across forms, APIs, self-hosting, governance, embedding, pricing, and best-fit use cases for enterprise form infrastructure.
Compare HIPAA-compliant form builder options for healthcare SaaS teams, from BAAs and audit logs to APIs, self-hosting, and PHI control.
Your First Custom Form.io Theme: Solving the most common use case: CSS class overrides.
When “Close Enough” Stops Being Good Enough and You Need Your Forms to Match the Rest of Your Application, Pixel-for-Pixel.
Compare MCP server list options for regulated enterprise developers. See official registries, GitHub, AWS, Playwright, Form.io, and governance criteria.
Compare AI governance platform layers for agentic workflows, including Form.io UAG, Appian, Camunda 8.9, Flowable 2025.1, and Microsoft AGT.
[ Share](https://www.facebook.com/sharer/sharer.php?u=https://form.io/ai-governance-platform-agentic-workflow-governance-layers-compared/%2F&src=sdkpreparse)#### Webinars
# [](https://form.io/webinars/agentic-coding-for-the-enterprise/)[Agentic Coding for the Enterprise (LIVE Demo: Form.io Agentic Coding Toolset)](https://form.io/webinars/agentic-coding-for-the-enterprise/)
# Date: Wednesday, August 19, 2026 Time: Central [](https://form.io/webinars/enable-self-service-forms-in-your-application/)[Enable Self-Service Forms in Your Application (LIVE Demo: Form.io’s Enterprise Form Builder Module)](https://form.io/webinars/enable-self-service-forms-in-your-application/)
# Date: Thursday, June 25, 2026 Time: 11:00 pm Central [](https://form.io/webinars/byo-css-the-new-standard-for-white-labeling-form-io/)[BYO-CSS: The New Standard for White Labeling Form.io](https://form.io/webinars/byo-css-the-new-standard-for-white-labeling-form-io/)
Date: Thursday, March 26, 2026 Time: 11:00 am Central #### Recent Posts
# [](https://form.io/web-form-builder-apis-self-hosted-control/)[Web Form Builder: When Online Forms Need APIs, Workflows, and Self-Hosted Control](https://form.io/web-form-builder-apis-self-hosted-control/)
# August 5, 2026 [](https://form.io/e-signature-software-self-hosted-form-workflows/)[E Signature Software for Self-Hosted Form Workflows: DocuSign Alternatives for Enterprise Control](https://form.io/e-signature-software-self-hosted-form-workflows/)
# July 21, 2026 [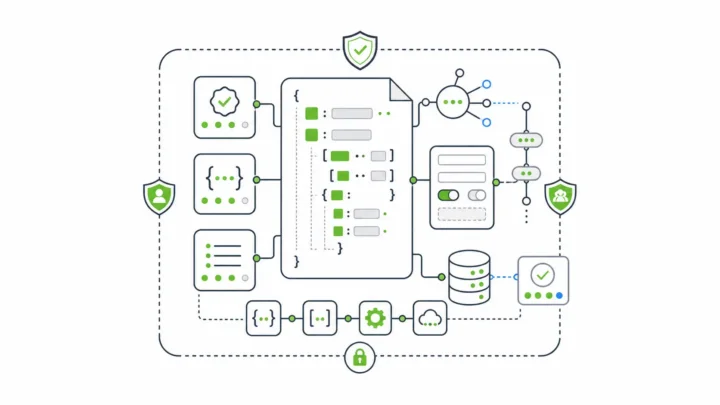](https://form.io/json-schema-validator-tools-production-apps/)[JSON Schema Validator Tools for Production Apps](https://form.io/json-schema-validator-tools-production-apps/)
# July 20, 2026 [](https://form.io/embedded-forms-b2b-saas-white-label-comparison/)[Embedded Forms for B2B SaaS: The White-Label Form Builder Comparison](https://form.io/embedded-forms-b2b-saas-white-label-comparison/)
# July 17, 2026 [](https://form.io/claims-management-software-insurance-form-builders/)[Claims Management Software Starts With The Forms That Feed It](https://form.io/claims-management-software-insurance-form-builders/)
# July 16, 2026 [](https://form.io/kyc-onboarding-software-financial-services-form-platforms/)[KYC Onboarding Software for Financial Services: Forms, APIs, and Audit-Ready Intake](https://form.io/kyc-onboarding-software-financial-services-form-platforms/)
July 15, 2026 #### Recent Case Studies
# [](https://form.io/case-studies/from-60-pages-to-a-single-click/)[From 60 Pages to a Single Click: How Form.io Powered a Government Agency’s Digitization](https://form.io/case-studies/from-60-pages-to-a-single-click/)
# June 15, 2026 [](https://form.io/case-studies/from-six-week-release-cycles-to-same-day-form-changes-patagonia-health/)[From Six-Week Release Cycles To Same-Day Form Changes – Patagonia Health](https://form.io/case-studies/from-six-week-release-cycles-to-same-day-form-changes-patagonia-health/)
# June 15, 2026 [](https://form.io/case-studies/accelerated-development-time-line-by-two-years/)[Accelerated Development Timeline By Two Years](https://form.io/case-studies/accelerated-development-time-line-by-two-years/)
# May 7, 2025 [](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)[The Digital Transformation Of Supporting New Services For The German Public Sector—On Repeat](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)
December 2, 2024 #### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# Enterprise Form Builder Module
*Published:* 2026-03-27
*Author:* Form.io Wizard
*URL:* https://form.io/product-announcement/enterprise-form-builder-module/
*Description:* Fully customizable, white-labeled form-building interface that customers embed inside their applications, enabling end-users to build and manage forms without developer intervention.
A new, fully embeddable, white labeled form-building interface — built for enterprise applications.
March 27, 2026 [  ](https://form.io/product-announcement/enterprise-form-builder-module/)Compare audit trail software needs for enterprise forms: audit logs, form revisions, submission history, staged promotion, and self-hosted controls.
Learn when a web form builder is enough, when forms need APIs and workflow control, and how Form.io fits self-hosted enterprise form infrastructure.
Compare e signature software for enterprise form workflows, including DocuSign alternatives, self-hosting, audit trails, APIs, and Form.io E-Sign+.
Compare JSON Schema validator tools for production apps: Ajv, Python libraries, form generators, API contracts, governance, and Form.io infrastructure.
Compare embedded forms and white-label form builders for B2B SaaS teams, from simple embeds to governed APIs, tenant controls, and secure data ownership.
Evaluate claims management software through the form infrastructure behind FNOL, documents, APIs, audit trails, PDFs, and regulated insurance workflows.
Evaluate KYC onboarding software for banks and fintechs through forms, APIs, identity checks, audit trails, self-hosted control, and governed workflows.
Compare Typeform alternatives for surveys, self-hosting, compliance, embedded forms, APIs, governance, and infrastructure fit for regulated teams in 2026.
Compare Jotform alternatives for regulated teams needing self-hosted forms, APIs, audit trails, permissions, embedded workflows, and better data control.
Compare Formbricks and Form.io across open source surveys, self-hosting, APIs, embedding, governance, pricing, and form infrastructure use cases for teams.
Compare Budibase and Form.io across forms, APIs, self-hosting, governance, embedding, pricing, and best-fit use cases for enterprise form infrastructure.
Compare HIPAA-compliant form builder options for healthcare SaaS teams, from BAAs and audit logs to APIs, self-hosting, and PHI control.
Your First Custom Form.io Theme: Solving the most common use case: CSS class overrides.
When “Close Enough” Stops Being Good Enough and You Need Your Forms to Match the Rest of Your Application, Pixel-for-Pixel.
Compare MCP server list options for regulated enterprise developers. See official registries, GitHub, AWS, Playwright, Form.io, and governance criteria.
Compare AI governance platform layers for agentic workflows, including Form.io UAG, Appian, Camunda 8.9, Flowable 2025.1, and Microsoft AGT.
[ Share](https://www.facebook.com/sharer/sharer.php?u=https://form.io/ai-governance-platform-agentic-workflow-governance-layers-compared/%2F&src=sdkpreparse)#### Webinars
# [](https://form.io/webinars/agentic-coding-for-the-enterprise/)[Agentic Coding for the Enterprise (LIVE Demo: Form.io Agentic Coding Toolset)](https://form.io/webinars/agentic-coding-for-the-enterprise/)
# Date: Wednesday, August 19, 2026 Time: Central [](https://form.io/webinars/enable-self-service-forms-in-your-application/)[Enable Self-Service Forms in Your Application (LIVE Demo: Form.io’s Enterprise Form Builder Module)](https://form.io/webinars/enable-self-service-forms-in-your-application/)
# Date: Thursday, June 25, 2026 Time: 11:00 pm Central [](https://form.io/webinars/byo-css-the-new-standard-for-white-labeling-form-io/)[BYO-CSS: The New Standard for White Labeling Form.io](https://form.io/webinars/byo-css-the-new-standard-for-white-labeling-form-io/)
Date: Thursday, March 26, 2026 Time: 11:00 am Central #### Recent Posts
# [](https://form.io/web-form-builder-apis-self-hosted-control/)[Web Form Builder: When Online Forms Need APIs, Workflows, and Self-Hosted Control](https://form.io/web-form-builder-apis-self-hosted-control/)
# August 5, 2026 [](https://form.io/e-signature-software-self-hosted-form-workflows/)[E Signature Software for Self-Hosted Form Workflows: DocuSign Alternatives for Enterprise Control](https://form.io/e-signature-software-self-hosted-form-workflows/)
# July 21, 2026 [](https://form.io/json-schema-validator-tools-production-apps/)[JSON Schema Validator Tools for Production Apps](https://form.io/json-schema-validator-tools-production-apps/)
# July 20, 2026 [](https://form.io/embedded-forms-b2b-saas-white-label-comparison/)[Embedded Forms for B2B SaaS: The White-Label Form Builder Comparison](https://form.io/embedded-forms-b2b-saas-white-label-comparison/)
# July 17, 2026 [](https://form.io/claims-management-software-insurance-form-builders/)[Claims Management Software Starts With The Forms That Feed It](https://form.io/claims-management-software-insurance-form-builders/)
# July 16, 2026 [](https://form.io/kyc-onboarding-software-financial-services-form-platforms/)[KYC Onboarding Software for Financial Services: Forms, APIs, and Audit-Ready Intake](https://form.io/kyc-onboarding-software-financial-services-form-platforms/)
July 15, 2026 #### Recent Case Studies
# [](https://form.io/case-studies/from-60-pages-to-a-single-click/)[From 60 Pages to a Single Click: How Form.io Powered a Government Agency’s Digitization](https://form.io/case-studies/from-60-pages-to-a-single-click/)
# June 15, 2026 [](https://form.io/case-studies/from-six-week-release-cycles-to-same-day-form-changes-patagonia-health/)[From Six-Week Release Cycles To Same-Day Form Changes – Patagonia Health](https://form.io/case-studies/from-six-week-release-cycles-to-same-day-form-changes-patagonia-health/)
# June 15, 2026 [](https://form.io/case-studies/accelerated-development-time-line-by-two-years/)[Accelerated Development Timeline By Two Years](https://form.io/case-studies/accelerated-development-time-line-by-two-years/)
# May 7, 2025 [](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)[The Digital Transformation Of Supporting New Services For The German Public Sector—On Repeat](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)
December 2, 2024 #### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# Audit Trail Software for Enterprise Forms: Logs, Revisions, and SDLC Control
*Published:* 2026-08-06
*Author:* Veronika Druck
*URL:* https://form.io/audit-trail-software-enterprise-form-builders-with-native-sdlc/
*Description:* A buyer guide to audit trail software for enterprise form workflows, explaining how audit logs, form revisions, submission revisions, stage promotion, permissions, generated APIs, and self-hosted deployment affect regulated form infrastructure decisions.
Audit trail software sounds simple until the record being audited is not just a file, invoice, login, or database row.
Enterprise forms change. Submitted data changes. Validation rules change. Permissions change. Workflow actions fire. APIs read and update the same records that users see in the interface.
For regulated form workflows, the question is not only "Do we have logs?" It is "Can we prove what happened, who did it, what version of the form governed it, and whether the workflow moved through the right control path?"
## **What audit trail software has to prove**
Audit trail software creates a chronological record of activity inside a system.
At minimum, that record should help answer:
- Who performed the action?
- What changed?
- When did it happen?
- Which object, record, form, user, or system was affected?
- What context explains the change?
- Can the record be reviewed later without reconstructing it from guesswork?
That matters because audit trails are not only for after-the-fact compliance reviews. They are also useful for security monitoring, troubleshooting, workflow accountability, and incident investigation.
NIST's log management guidance treats logging as part of a broader cybersecurity evidence system. The draft [NIST SP 800-92 Rev. 1 Cybersecurity Log Management Planning Guide](https://csrc.nist.gov/pubs/sp/800/92/r1/ipd) treats logging as part of a broader cybersecurity evidence system.
Regulated systems make the point even more concrete. [21 CFR 11.10](https://www.law.cornell.edu/cfr/text/21/11.10) requires procedures and controls for closed systems that include secure, computer-generated, time-stamped audit trails for actions that create, modify, or delete electronic records, and it says record changes must not obscure previously recorded information. HIPAA's technical safeguards similarly include [audit controls](https://www.law.cornell.edu/cfr/text/45/164.312) for information systems that contain or use electronic protected health information.
That is the right starting point. Logs are evidence.
But enterprise form workflows need a more specific kind of evidence.
If a claims intake form changes, a patient referral submission is corrected, a public-sector application moves from draft to review, or an embedded customer form is updated through an API, a generic event log may not be enough. The system needs to preserve the relationship between the action and the form infrastructure that governed it.
## **Why enterprise forms need a different audit model**
A form in an enterprise application is not just a page.
It can be:
- a user interface
- a JSON schema
- a validation contract
- a submission model
- a generated API
- a workflow trigger
- a permission boundary
- a document-generation source
- a long-term record
That is why auditability gets harder when forms become application infrastructure.
A simple audit log might show that a user updated a record at 2:14 PM. That is useful, but it does not answer every question an auditor, compliance team, or engineering lead may ask later.
For example:
- Which form version was active when the user submitted the record?
- Did the form have the same required fields then that it has now?
- Was the submitted value changed after capture?
- Was there a documented reason for the change?
- Did a webhook, email, approval action, or downstream integration fire?
- Did the change happen in development, staging, or production?
- Did the API update follow the same permission rules as the portal update?
Those are form-infrastructure questions, not just logging questions.
IBM's 2025 [Cost of a Data Breach Report](https://www.ibm.com/reports/data-breach) puts the global average breach cost at $4.4 million and reports that 63% of organizations lacked AI governance policies. That statistic is not form-specific, but it gives the right scale for the decision. When sensitive data workflows are hard to trace, the risk is not cosmetic.
For enterprise forms, the audit model has to cover both sides of the system: the form definition and the submitted data.
## **The four audit layers enterprise form builders should support**
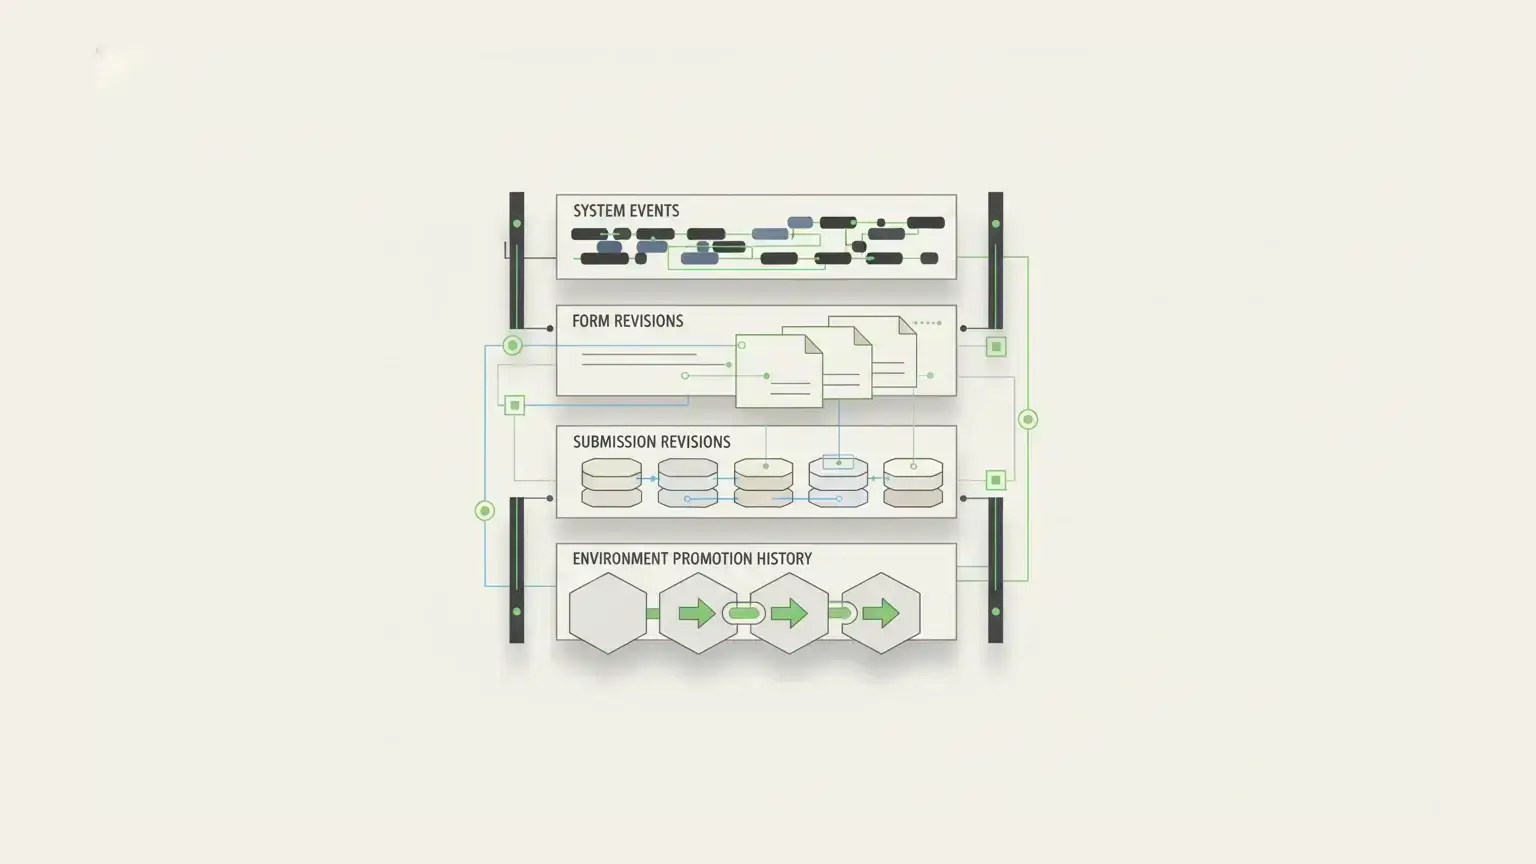Most form tools can tell you that a submission exists.
Enterprise form infrastructure needs to tell a deeper story.
### **1. System activity and access logs**
The first layer is the system-level audit log.
This is the record of access, authentication, API requests, data reads, data writes, and other platform activity. It answers questions like:
- Who viewed this submission?
- Who authenticated?
- Which API request changed the record?
- Which project, form, or user was involved?
- Did a request fail?
- Can related events be correlated?
Form.io's [audit logging documentation](https://help.form.io/dev/audit-logging) describes a system-level audit log format with date, event, UUID, project ID, session ID, user ID, and event-specific context. The docs also state that audit logs output to standard out for the Docker container and can be routed into a log aggregation system.
Another note: high-volume system logs should not necessarily store complete submission payloads inside every event. Sensitive form values may need a different audit mechanism than API access events.
The right audit design separates broad activity logging from field-level revision history, then lets teams correlate the two when they need to investigate.
### **2. Form revisions**
The second layer is form revision history.
Enterprise forms change over time. Teams add fields, remove fields, rename fields, update validation rules, change conditional logic, revise consent text, and adjust workflow requirements.
If the form changes after a record is submitted, the system still needs to explain what the form looked like when the record was captured.
Form.io's [Form Revisions documentation](https://help.form.io/userguide/forms/form-revisions) is built for that problem. Form Revisions let teams preserve form versions as forms evolve and can display submission data in the form revision that captured it. The revision interface also exposes who made a revision, when the revision was made, the revision number, and revision notes.
That distinction is central to auditability.
If an auditor reviews a historical submission, the question is not only "What data is in the record now?" It is also "What fields, labels, rules, and structure governed the user when the record was created?"
Without form revision history, teams often have to reconstruct that context from release notes, screenshots, old code, or database backups. That is fragile.
### **3. Submission revisions**
The third layer is submission revision history.
This is the field-level history of changes to submitted data after initial capture.
A submitted form might be corrected by a staff member. A patient record might need an updated value. A claims workflow might need a revised amount. A government service application might need a supporting detail added after review.
In those cases, the system needs to preserve the previous state, the new state, the user who made the change, the time of the change, and any revision note explaining why the change happened.
Form.io's [Submissions documentation](https://help.form.io/userguide/submissions) describes Submission Revisions as an audit logging capability that tracks who updated a submission, when the change was made, and notes associated with the update. The documentation also says the PDF change log can include the revision ID, updating user, date and time, revision note, and list of revision changes.
That is the difference between editing a record and governing a record.
An edit changes the current value. A revision trail preserves the accountable history behind that value.
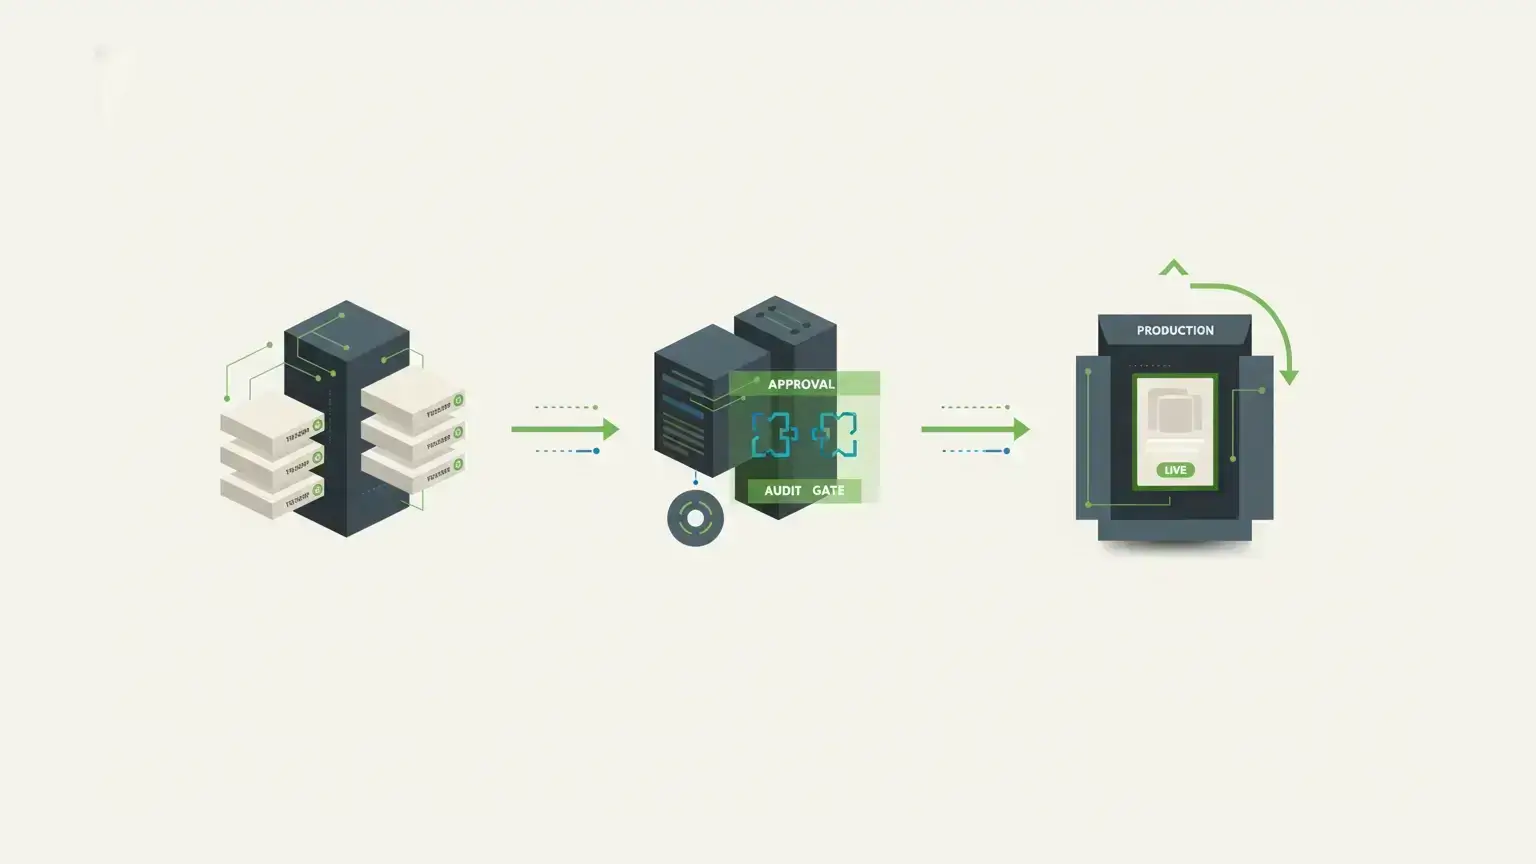
### **4. Stage, action, and deployment history**
The fourth layer is the SDLC layer.
For enterprise form teams, auditability is not limited to runtime activity. It also includes how form definitions, resources, roles, and actions move through development, staging, and production.
Form.io's [Stages documentation](https://help.form.io/userguide/projects/stages) describes stages as a way to isolate project forms and resources for form management between different environments. The same documentation frames a typical enterprise workflow around Live, Authoring, QA/Test, and Development stages.
That matters because regulated teams often need controlled promotion.
They need a place to build and test form changes before production. They need to know which form version moved forward. They need to avoid ad hoc edits that change production behavior without review. This should not be inflated into a claim that Form.io replaces a full CI/CD or release-management system for all application code. The narrower point is still valuable: form configuration has its own lifecycle, and enterprise teams need a controlled way to manage it.
Audit trail software that ignores the lifecycle layer misses a major part of the form governance problem.
## **A practical comparison framework**
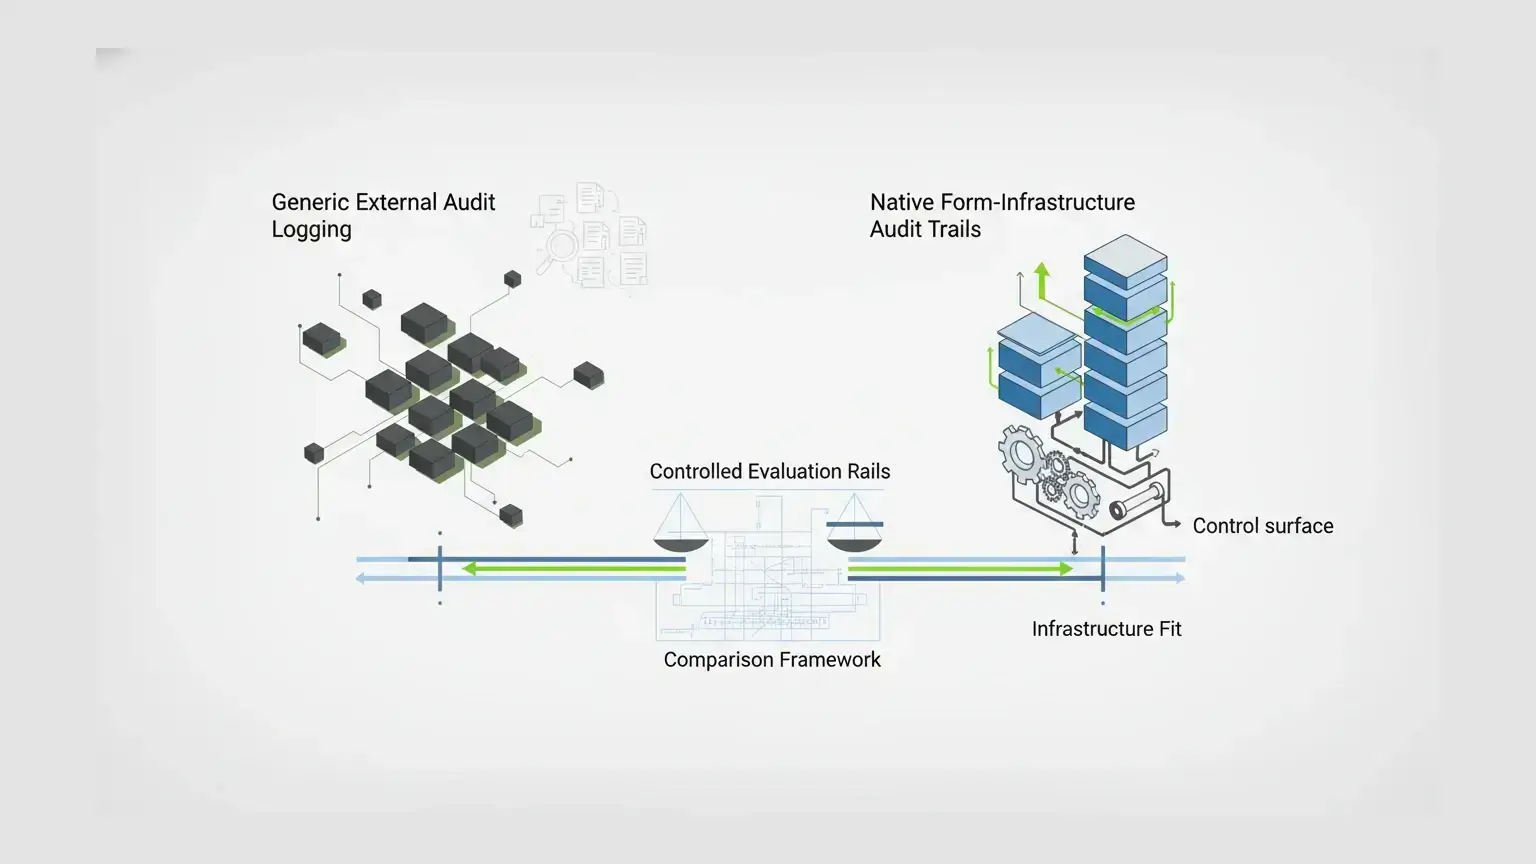The right audit trail software depends on what kind of system you are auditing.
**Category****Best fit****What it proves****Where it can fall short for enterprise forms**Generic audit log toolingBroad system activity, application events, operational monitoringWho did what, when, and where across systemsUsually does not understand form schema versions or submission-level change historyCompliance audit management toolsPolicy controls, audit programs, evidence management, compliance workflowsWhether controls exist and evidence was collectedOften manages audit process, not the runtime form record itselfAccounting or finance audit trail toolsFinancial transactions, invoices, approvals, accounting changesTransaction history and financial accountabilityUsually narrow to finance workflowsBasic form builders with logsSimple submissions, admin edits, response exportsBasic submission history and account activityMay not preserve form schema history, API-level activity, or stage promotionCustom-built audit trailHighly specific internal applicationsWhatever the team designs and maintainsExpensive to build, test, secure, document, and keep consistent across formsForm infrastructure with native audit controlsRegulated form workflows, embedded forms, generated APIs, long-lived submissionsSystem activity, form revisions, submission revisions, permissions, actions, and stage movementRequires technical ownership and a clear governance modelThe key is fit.
If your team only needs a basic activity log for a contact form, enterprise form infrastructure is probably too much. If your team is managing high-value workflows where form definitions and submitted data both matter, the audit model needs to be native to the form platform.
## **Where Form.io fits**
Form.io is strongest when the form is part of the application infrastructure.
That usually means a team needs some mix of [self-hosted form deployment](/features/self-hosted-forms-for-enterprise/), embedded forms, generated APIs, permissions, workflow actions, form revisions, submission revisions, audit logging, and environment promotion.
The reason is architectural.
Form.io forms and resources are JSON-driven definitions that can render user interfaces, generate APIs, validate submissions, store submitted data, and participate in roles, permissions, actions, stages, and revisions.
That makes auditability part of the same system that owns the form workflow.
[The Security Module](/features/secure-forms-compliance-readiness/) bundles advanced audit logging, action logs, form revisions, submission revision logs, submission collections, and container security scanning. The [complete audit trail feature](/features/log-forms-complete-audit-trail/) separates system-wide audit logs from field-level submission revisions, which is the right separation for high-volume enterprise workflows. The [Form Revisions feature](/features/form-revisions-form-json-schema/) preserves form JSON schema versions so historical submissions can remain explainable as forms evolve.
Form.io also matters when APIs are part of the record. A form workflow may be updated through the portal, an embedded application, or a generated API. The buyer should not have to accept one audit posture for the UI and another for API-driven operations.
That is why generated APIs are relevant to audit trail software. Form.io's [form API model](/features/form-api/) lets teams treat forms and resources as API-connected infrastructure, not isolated web pages. Permissions, submissions, and actions then sit closer to the form data model.
This is also where customer proof matters. [G2's Form.io review page](https://www.g2.com/products/form-io/reviews) describes the platform as deployable into on-premise or private cloud environments, giving customers control of submission data. One enterprise reviewer summarized the practical product experience this way: "Form.io is an intuitive, developer-friendly framework that provides excellent data management." That is not an audit claim by itself. It is buyer proof for the control-and-customization posture that makes audit-heavy form infrastructure worth evaluating.
## **When simple audit logging is enough**
Not every workflow needs all of this.
Simple audit logging may be enough when:
- The form is short-lived.
- Submitted data is low risk.
- Responses are rarely edited after capture.
- The form schema rarely changes.
- The form is not embedded into a regulated application.
- There is no need for DEV/STAGE/PROD promotion.
- Exports are enough for downstream systems.
- The audit question is limited to account activity or submission timestamps.
In those cases, a lighter form builder, basic form backend, or general application log may be a better fit.
The mistake is keeping that model after the workflow becomes infrastructure.
Once forms drive eligibility, claims, intake, onboarding, financial review, patient workflows, public-sector services, insurance applications, or internal approvals, the audit trail has to explain more than "a record changed."
It has to explain the governed context around the change.
## **Evaluation checklist for audit trail software in form workflows**
Use these questions before choosing a form platform for an audit-heavy workflow.
### **Does the platform track system-level activity?**
Look for access events, authentication events, API requests, data reads, data writes, request correlation, and log export options.
### **Does it preserve form schema versions?**
If a field, validation rule, label, or conditional path changes, the platform should preserve enough form history to explain historical submissions.
### **Does it preserve submitted-data history?**
Submission revisions should show who changed a value, when it changed, what changed, and why.
### **Can historical submissions render against the original form version?**
This matters when auditors, legal teams, or operations teams need to understand what a user actually saw at capture time.
### **Are workflow actions included in the governance model?**
Actions such as emails, webhooks, approvals, PDF generation, and save-to-resource operations can affect the record. They should not be invisible.
### **Can forms move through controlled stages?**
Enterprise teams need a way to test, version, and promote forms, resources, roles, and actions without treating production as the editing surface.
### **Do permissions apply close to the form and submission model?**
[Form permissions](/features/form-permissions/) matter because different people may be allowed to create, read, update, delete, approve, or export different records.
### **Can the platform run inside the required deployment boundary?**
Self-hosting does not automatically make a system compliant. It does let the customer place the form platform inside the environment, monitoring, identity, logging, and operational controls the organization already governs.
### **Are forms still usable for builders and developers?**
Audit controls only help if the team can still build and maintain the workflow. A usable [form builder](/features/form-builder/) and a clear [JSON-powered form model](/features/json-powered-forms/) reduce the temptation to route around governance.
## **Key takeaways**
- Audit trail software is not only a logging feature when forms become application infrastructure.
- Enterprise form workflows need evidence across system activity, form revisions, submission revisions, workflow actions, permissions, and stage promotion.
- Generic logs can show that something happened. Form infrastructure should show what version of the form governed the record when it happened.
- Form.io fits best when the form schema, generated API, submitted data, and governance controls need to stay connected.
- The right buyer is not looking for the lightest form tool. They are looking for a form platform that can defend the record later.
## **FAQ**
### **What is audit trail software?**
Audit trail software records system activity in chronological order so teams can review who performed an action, what changed, when it happened, and which record or system was affected.
### **Why do enterprise forms need audit trails?**
Enterprise forms often collect data that drives decisions, approvals, compliance records, customer onboarding, claims, patient workflows, government services, or financial review. If the record changes later, the organization needs evidence of what happened.
### **What is the difference between an audit log and a submission revision?**
An audit log records system-level activity such as access, authentication, API requests, and data modification events. A submission revision preserves field-level history for a specific submitted record.
### **What is the difference between form revisions and submission revisions?**
Form revisions track changes to the form schema: fields, validation rules, conditional logic, layout, and related form structure. Submission revisions track changes to submitted data after capture.
### **Why does form versioning matter for audit trails?**
Form versioning helps explain historical records. If a submission was captured under an older form version, the team may need to review the exact schema, fields, labels, and validation rules that governed that submission.
### **Does self-hosting make audit trail software compliant?**
No. Self-hosting gives the organization more control over deployment, data, logs, identity, monitoring, and infrastructure. Compliance still depends on configuration, policy, controls, documentation, and review.
### **Should audit trail software store every field value in every log?**
Not always. High-volume system logs can become expensive and sensitive if they store full payloads in every event. A better model often separates system audit logs from field-level submission revisions.
### **What should regulated teams look for in form audit trails?**
They should look for system audit logs, form revisions, submission revisions, permissions, workflow/action evidence, stage promotion, exportable evidence, and deployment control.
### **Can generic log management replace native form revision history?**
Generic log management can help centralize and review system events, but it usually does not understand form schema versions, submission rendering, or field-level form data history unless the application sends that context deliberately.
### **When is Form.io a good fit for audit-heavy forms?**
Form.io is a good fit when forms are part of a larger application workflow and the team needs [form workflows](/features/form-workflows/), generated APIs, permissions, revisions, submission history, and customer-controlled deployment.
### **When is Form.io probably too much?**
Form.io may be more platform than needed for a simple contact form, survey, or lead-capture page where the data is low risk and the audit requirement is limited to basic timestamps or account activity.
## **Build audit-ready form infrastructure with Form.io**
---
# Web Form Builder: When Online Forms Need APIs, Workflows, and Self-Hosted Control
*Published:* 2026-08-05
*Author:* Veronika Druck
*URL:* https://form.io/web-form-builder-apis-self-hosted-control/
A web form builder sounds like a simple category until the form becomes part of a real application. A contact form, signup form, or feedback survey can live in a lightweight tool. A regulated intake process, embedded customer workflow, or API-connected business process needs more than fields on a page.
That is where the buying question changes.
## **What a Web Form Builder Should Do**
A web form builder is software for creating forms users can complete in a browser. At the basic level, it should let a team create fields, set required answers, publish a form, collect submissions, and send the data somewhere useful.
For many teams, that is enough.
Zapier's long-running online form builder list shows how the broad market is usually framed: quick form creation, automation, advanced logic, conversational form experiences, AI-assisted building, Excel sync, approval flows, and reporting options ([Zapier](https://zapier.com/blog/best-online-form-builder-software/)). That is the default expectation buyers bring to the phrase.
The problem is that "web form builder" covers several different jobs:
- a marketing team collecting leads
- an operations team routing internal requests
- a product team embedding forms inside a SaaS application
- a healthcare, insurance, finance, or government team collecting sensitive data
- a development team using forms as part of an API-backed workflow
Those jobs should not be evaluated with the same checklist.
If the form is only a standalone page, the most important questions are speed, templates, design, notifications, and basic integrations. If the form is part of application infrastructure, the questions become more serious: who owns the schema, where does submission data live, what APIs exist, how validation runs, what happens after submit, and whether the platform can operate inside the customer's environment.
## **When a Simple Web Form Builder Is Enough**
A simple web form builder is a good fit when the form is low-risk, isolated, and easy to replace.
Use a lightweight tool when:
- the form collects basic marketing or event information
- submissions can live in the vendor's hosted system
- exporting to a spreadsheet is acceptable
- the workflow after submission is simple
- there are no unusual data residency or deployment requirements
- the form is not deeply embedded in a product experience
- developers do not need to treat the form as an API-backed component
In that world, the best tool is often the fastest tool your team will actually use. A simple builder can be the right decision for a campaign, a workshop signup, a small survey, or a basic internal request.
The mistake is keeping that same mental model after the requirements change.
## **Where Web Form Builders Start To Break Down**
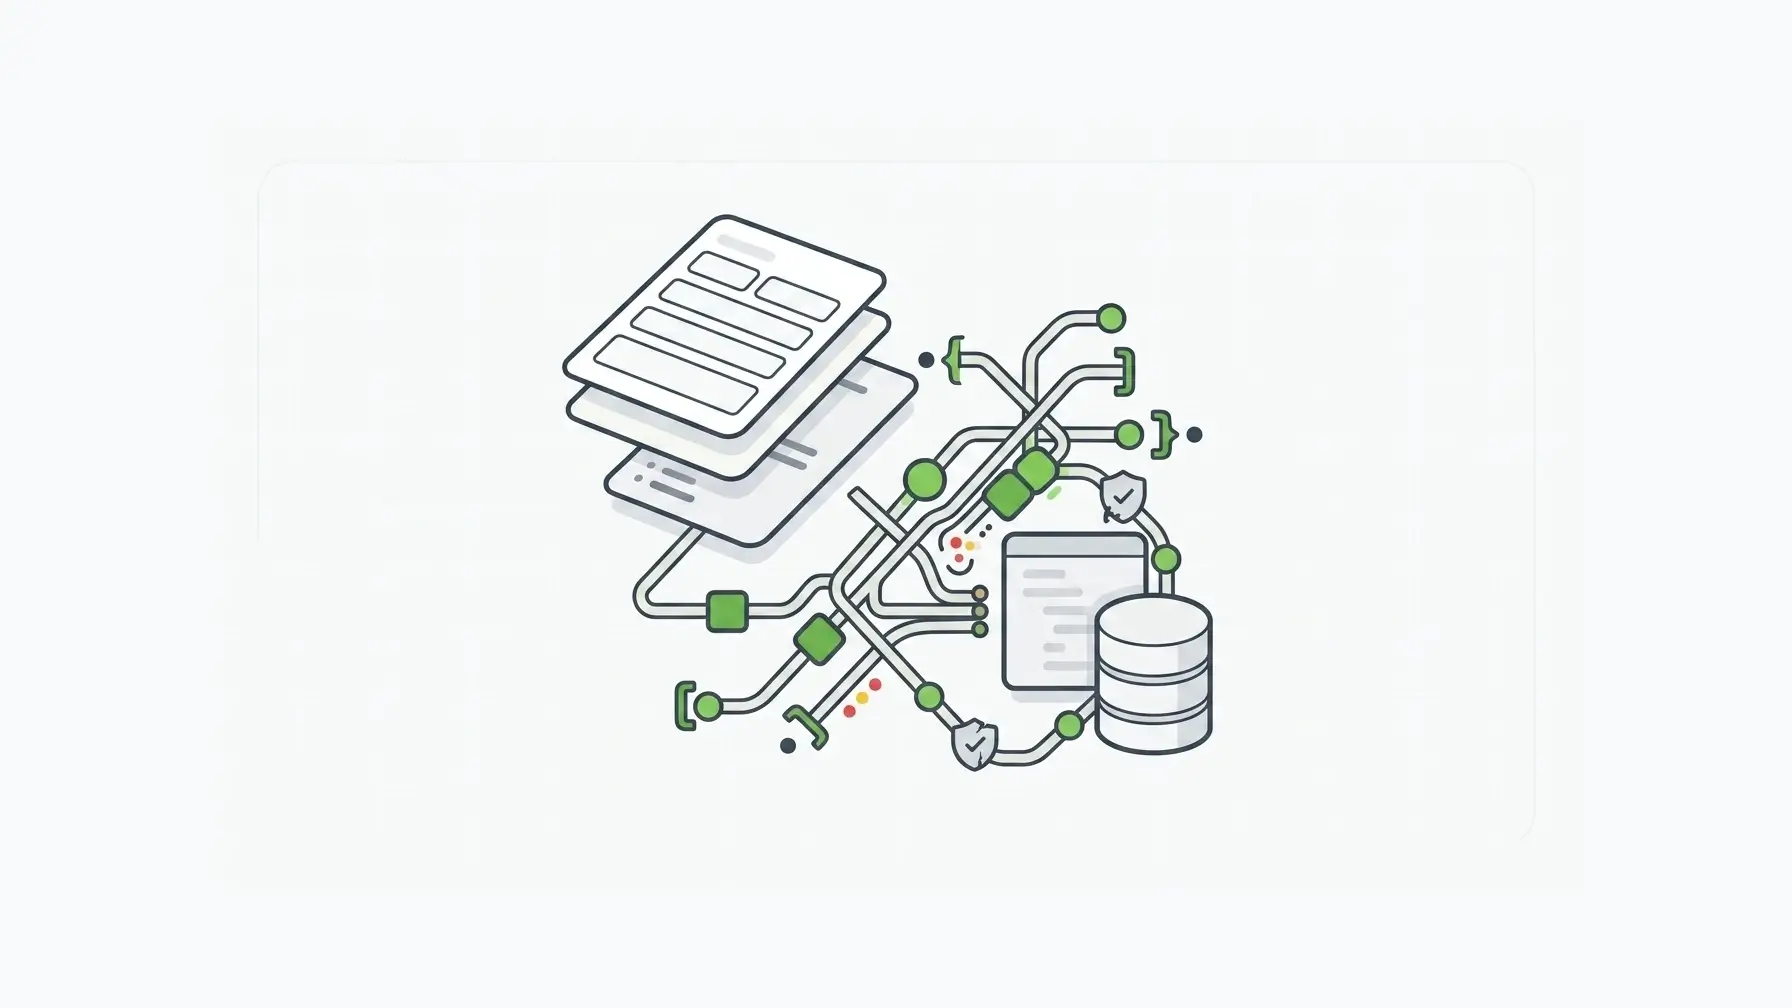Web forms become harder when the submission is not the end of the process.
A user submits an intake form. Then the data has to create a case, trigger a review, update a CRM, route to a queue, generate a PDF, notify a downstream system, enforce role-based access, or become part of a customer-facing application.
At that point, the form has a second job. It is no longer just collecting answers. It is becoming the front door to a process.
The breakdown usually shows up in five places.
### **The Data Model Lives Somewhere Else**
Many web form builders make it easy to create fields, but the real application data model lives outside the form tool. That creates drift. A field is required in the form but optional in the backend. A dropdown changes in the builder but not in the API. A validation rule exists in the browser but not server-side.
This is small until the form becomes important.
Then every disconnected rule becomes a place where bad data can enter the system.
### **Integrations Become Workflow Logic**
Basic integrations are helpful. They send a notification, create a spreadsheet row, add a CRM contact, or post to a collaboration tool.
But integration is not the same as workflow ownership.
Enterprise forms often need conditional routing, retries, identity context, external IDs, error handling, and clean handoff to other systems. Form.io's webhook documentation, for example, treats a submission as a payload that can call an external API, map response IDs back to the submission, and optionally wait for the webhook response before continuing actions ([Form.io webhook actions docs](https://help.form.io/form-building/actions/webhook-actions)).
That is a different requirement than "send this form to a spreadsheet."
### **Security And Compliance Become Architecture Questions**
The more sensitive the data, the less acceptable it is to treat the form builder as a detached SaaS box.
IBM's 2025 Cost of a Data Breach Report puts the global average breach cost at USD 4.4 million ([IBM](https://www.ibm.com/reports/data-breach)). That statistic should not be used to scare every team away from hosted tools. It should remind buyers that data capture is part of the security boundary.
For sensitive forms, the evaluation should include:
- where submissions are stored
- who administers the environment
- how access is controlled
- how data moves between systems
- how logs, evidence, and audit needs are handled
- whether the form platform can live inside the organization's deployment model
Self-hosting does not automatically make a system compliant. It gives the organization more control over the environment where compliance controls are implemented and reviewed.
### **Product Teams Need Embedding, Not Just Publishing**
Publishing a hosted form is not the same as embedding a form builder into a product.
If a B2B SaaS team wants customers to create or manage their own forms inside the application, the builder has to respect the product's authentication, permissions, tenant boundaries, styling, and data model. That is closer to an embedded product capability than a public web form.
This is why Form.io's [Enterprise Form Builder Module](https://form.io/features/enterprise-form-builder-module/) matters for platform teams. The point is not only that a user can drag fields onto a canvas. The point is that a company can provide a white-labeled, pre-wired form-building experience inside its own application.
### **Developers Need A Stable Contract**
Developers can work around almost anything once. The cost shows up when every new form requires custom backend glue.
A stronger web form builder for application teams should create a stable contract between the form, the submission record, the API, validation, permissions, and downstream systems.
Form.io's own project documentation says that when a new form is created, a REST API is automatically generated to serve as the backend for the form and for other systems that need to create submissions ([Form.io project docs](https://help.form.io/admin/projects/creating-a-project)). That is the key architectural distinction: the form is not only a UI artifact. It is part of the API surface.
## **A Web Form Builder Evaluation Checklist**
Before choosing a web form builder, separate the easy questions from the questions that determine long-term fit.
Evaluation AreaLightweight Form NeedInfrastructure-Grade Form NeedBuilderDrag-and-drop fields, templates, brandingConfigurable builder, reusable schemas, controlled componentsDataHosted submissions and exportsStructured submission records with API accessWorkflowNotifications and simple integrationsWebhooks, Actions, retries, external IDs, routingValidationClient-side rules and required fieldsSchema-linked validation across UI and server pathsEmbeddingPublic link or iframeNative application embedding and white-label controlDeploymentVendor-hosted SaaSHosted, private cloud, on-premises, or local deployment optionsGovernanceAdmin settingsRoles, permissions, stages, evidence, and environment controlFitCampaigns, surveys, simple intakeProduct workflows, regulated intake, internal systems, multi-tenant SaaSThis checklist prevents a common buying mistake: choosing the easiest form tool for the first version, then rebuilding the entire intake layer once the forms become operationally important.
## **Why APIs Change The Category**
APIs change a web form builder from a page-building tool into an application component.
Without APIs, the form is mostly a destination. Users go there, submit data, and the team exports or forwards the result.
With APIs, the form can become part of the system:
- applications can create and read submissions
- forms can populate fields from external data
- downstream systems can consume structured payloads
- teams can build reporting, review, and workflow layers on top of submission records
- developers can integrate forms into products without treating each one as a one-off project
Form.io's [data integration tools](https://form.io/features/data-integration-tools-for-enterprise-forms/) positioning makes this point directly: forms, resources, submissions, and projects are accessible through REST APIs. The practical value is not just "there is an API." It is that the form builder, schema, submission data, and integration surface are part of the same model.
That matters when teams are building internal tools, partner portals, insurance workflows, healthcare intake, public-sector services, or SaaS onboarding flows.
The user sees a web form. The architecture sees a contract.
## **Why Deployment And Data Control Matter**
Deployment is one of the clearest dividing lines between a simple web form builder and enterprise form infrastructure.
If the form is low-risk, vendor-hosted SaaS is usually fine. If the form handles regulated data, internal process data, customer application data, or data that has to move through controlled systems, deployment becomes part of the buying decision.
Form.io's deployment documentation says the platform can be installed in cloud environments, on-premise data centers, or local machines, and that enterprise deployments can use multi-environment architecture across private cloud or on-prem environments ([Form.io deployment overview](https://help.form.io/deploy/deployment-overview)). Its on-premises deployment documentation frames on-prem as relevant when infrastructure, compliance, or data-security requirements call for that model ([Form.io on-premises deployment docs](https://help.form.io/deploy/on-premises-deployment)).
This does not make Form.io the right fit for every form.
It makes Form.io relevant when the form layer has to live where the rest of the application lives.
For teams with strict environment rules, that is often the real requirement hiding underneath the phrase "web form builder." They are not only asking for a form canvas. They are asking whether the form system can respect their data boundary, deployment model, access controls, and integration paths.
## **Where Form.io Fits**
Form.io is a stronger fit when the form is part of an application, not just a standalone collection page.
The core difference is that Form.io combines a [drag-and-drop form builder with APIs](https://form.io/features/drag-and-drop-form-builder-apis/). Teams can design forms visually while keeping the underlying structure available as JSON and exposed through generated REST APIs.
That combination is useful when:
- developers need forms embedded in a product
- business users need controlled form authoring
- submissions need to be available through APIs
- workflows need webhooks or server-side actions
- the organization needs self-hosted or on-premises deployment
- forms need to share a governance model with the surrounding application
Form.io is not the best answer when a team only needs a quick public survey or a simple contact form. That buyer should choose the fastest lightweight tool that fits the job.
But when a web form builder has to support real application infrastructure, the decision changes. The value is not only the builder UI. It is the connection between form schema, submission data, generated APIs, deployment control, and workflow actions.
Customer language points to the same distinction. A Trustpilot reviewer described Form.io as useful "for integration and standalone" work ([Trustpilot](https://www.trustpilot.com/review/form.io)). A Form.io case study customer put the infrastructure burden more bluntly: Form.io "cleans up all the dirty work" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)).
That is the real category line.
A basic web form builder helps a team make a form. Form.io is for teams that need the form to become a governed part of the application.
## **Key Takeaways**
- A web form builder can mean anything from a simple contact form to an embedded application workflow.
- Lightweight tools are a good fit when forms are low-risk, standalone, and easy to replace.
- Enterprise teams should evaluate APIs, validation, submissions, workflow actions, permissions, and deployment control.
- Form.io fits when the form layer needs to operate as controlled application infrastructure, not just a hosted form page.
- Self-hosting is not a compliance shortcut; it is a control model for teams that need to own the environment.
## **FAQ**
### **What Is A Web Form Builder?**
A web form builder is software for creating forms that users complete in a browser. Basic builders focus on fields, templates, publishing, notifications, and exports. More advanced builders support APIs, workflows, permissions, embedding, and controlled deployment.
### **What Is The Difference Between A Web Form Builder And An Online Form Builder?**
The terms often overlap. "Online form builder" usually points to hosted SaaS tools for creating and publishing forms quickly. "Web form builder" can mean the same thing, but it is also used by product and development teams looking for embeddable form-building inside a web application.
### **When Is A Basic Form Builder Enough?**
A basic form builder is enough when the form is low-risk, standalone, and does not need deep integration with internal systems. Examples include event registration, simple lead capture, small surveys, and basic internal requests.
### **When Does A Web Form Builder Need APIs?**
A web form builder needs APIs when other systems must create, read, update, route, or report on submissions. APIs matter when forms are part of a product, portal, approval workflow, regulated intake process, or internal system of record.
### **Why Does Form Schema Matter?**
The schema defines the form's structure and behavior. In a schema-driven model, the same definition can support rendering, validation, submissions, APIs, workflow actions, and governance. That reduces drift between what the user sees and what the backend expects.
### **Can A Web Form Builder Be Self-Hosted?**
Some web form builders are hosted-only. Form.io supports self-hosted deployment models, including cloud, on-premises, and local environments according to its deployment documentation. That matters when the organization needs control over hosting, network boundaries, data storage, and operational review.
### **Is Self-Hosting The Same As Compliance?**
No. Self-hosting gives the customer more control over the environment, but compliance still depends on configuration, policies, controls, monitoring, documentation, and the broader system boundary. The value is control, not a shortcut around responsibility.
### **Why Would A SaaS Product Need An Embedded Form Builder?**
A SaaS product may need customers or internal teams to create forms inside the product itself. In that case, the builder has to respect tenant boundaries, authentication, permissions, styling, and data storage. A public form link is not enough.
### **How Is Form.io Different From A Simple Form Tool?**
Form.io is built for teams that need forms, submission data, generated APIs, workflow actions, and deployment control together. It can still provide a drag-and-drop builder, but the stronger reason to use it is when forms need to operate inside application infrastructure.
## **Build Web Forms That Fit Your Application Architecture**
---
# E Signature Software for Self-Hosted Form Workflows: DocuSign Alternatives for Enterprise Control
*Published:* 2026-07-21
*Author:* Veronika Druck
*URL:* https://form.io/e-signature-software-self-hosted-form-workflows/
*Description:* A buyer guide to e signature software for enterprise form workflows, comparing standalone document-signing tools with Form.io E-Sign+ for self-hosted, API-driven, submission-data signature proof inside controlled environments.
E signature software is usually evaluated as a document workflow tool: send a PDF, collect a signature, store an audit trail, and move on.
That is enough for many contracts. It is not enough when the signature is attached to regulated intake, eligibility data, consent records, financial applications, healthcare workflows, or other form submissions that must stay inside your application boundary.
The better question is not only, "Can this document be signed?" It is, "Can we defend the signed record later, with the data, schema, context, and audit trail intact?"
## **What E Signature Software Usually Solves**
Most e signature software helps teams replace wet signatures with an electronic signing process. The standard workflow is familiar: upload a document, place signature fields, route it to signers, authenticate the signer, collect consent, and retain a completed envelope.
That category is large because the paper problem is large. [Grand View Research estimated](https://www.grandviewresearch.com/industry-analysis/digital-signature-market-report) the global digital signature market at USD 6.9 billion in 2025 and projected a 43.9% CAGR from 2026 to 2033.
But market size does not tell you which architecture fits your use case.
Standalone signing platforms are strongest when the signed artifact is the document itself: contracts, sales agreements, HR forms, procurement packets, vendor agreements, and legal paperwork. In those cases, the system of record is often the completed document package.
Form-driven applications are different. The signed evidence may need to stay attached to a submission record, user identity, form version, field values, workflow state, API transaction, and downstream system update.
That is where a normal e-signature checklist starts to miss the real buyer risk.
## **Why DocuSign Alternatives Become Relevant**
DocuSign is the name many buyers know first. Adobe, Dropbox Sign, PandaDoc, Zoho Sign, OneSpan, and other tools also belong in the traditional e-signature conversation.
Those tools can be the right choice when your team mainly needs a document-signing workflow. The mistake is assuming that the best document-signing platform is automatically the best signing architecture for application data.
Teams start looking for DocuSign alternatives when one or more constraints appears:
- signature data must stay inside a private cloud, VPC, on-premise, or controlled deployment boundary
- the signed record begins as structured form data, not a static PDF
- signer consent needs to connect to the exact fields and submission context that were signed
- APIs, webhooks, roles, permissions, and audit history matter as much as the visual signature
- pricing or operations become hard to forecast when signatures scale across many workflows
For these teams, the word "alternative" does not simply mean cheaper. It means architecturally different.
## **The Enterprise Evaluation Criteria**
Before choosing e signature software, separate legal acceptance from operational evidence.
The U.S. [ESIGN Act](https://uscode.house.gov/view.xhtml?edition=prelim&path=%2Fprelim%40title15%2Fchapter96) says electronic signatures and records generally cannot be denied legal effect solely because they are electronic. It also points to record retention: electronic records must remain accurate, accessible, and reproducible for later reference.
That retention point matters. A signature event is only as useful as the record your team can reproduce when someone asks what was signed, by whom, under which form version, with which field values, and under which business process.
Evaluate each platform across six criteria.
**Criterion****Why it matters**Deployment controlDetermines where sensitive data, signature proof, and operational evidence live.Record modelShows whether the signed artifact is a PDF envelope, a submission record, or both.Audit trailCaptures the evidence needed to defend the transaction later.API accessDetermines whether signatures can participate in application workflows.Identity and access controlsConnects signing to the right user, role, tenant, or workflow boundary.Pricing modelDetermines whether cost scales predictably across high-volume workflows.The wrong platform can still collect a signature. The problem appears later, when the team needs to prove what the signature means inside the larger system.
## **Where Self-Hosted Form Workflows Change The Question**
Self-hosted form workflows change the center of gravity.
Instead of asking, "Which e-signature vendor should host this envelope?" the team asks, "How do we keep the signed record inside the same infrastructure that owns the form, data, APIs, permissions, and audit history?"
That shift matters for regulated teams, embedded SaaS products, government contractors, healthcare platforms, insurance workflows, financial services onboarding, and internal enterprise portals.
The signature is not a decorative mark. It is a control point in the data lifecycle.
NIST's [digital signature project](https://csrc.nist.gov/projects/digital-signatures) frames digital signatures around generation, verification, and data protection. That distinction is useful for buyers: a visible signature image is not the same thing as verifiable proof that the protected data and context have not changed.
In a form workflow, the strongest signature system should answer questions like:
- Which form version captured the data?
- Which fields were protected by the signature?
- Did the data change after signing?
- Can the application verify the signature through an API?
- Does the signed record remain inside the customer's environment?
- Can the team reproduce the record without depending on a third-party envelope as the only source of truth?
Those are infrastructure questions, not just signing questions.
## **How Form.io E-Sign+ Fits**
[Form.io E-Sign+](/features/cryptographic-e-signatures-for-form-data/) is built for a narrower, more controlled version of the e-signature problem: cryptographically secure signatures associated with Form.io submission data inside the customer's own environment.
That is a different posture than a standalone document-signing workflow.
With Form.io, the [form schema and submission data](/form-json-schema-vs-submission/), generated APIs, permissions, workflow actions, and deployment boundary are already part of the application infrastructure. E-Sign+ extends that infrastructure by letting teams verify signed submission data and context rather than treating the signature as only a PDF-layer event.
The [product documentation](https://help.form.io/dev/integrations/e-sign%2B) describes E-Sign+ as tied to submission data, usable through native submission IDs, and decoupled from PDFs. It can protect selected fields, all form data, and/or submission properties, depending on configuration.
That makes Form.io a strong fit when the signature needs to travel with application data.
Form.io's broader customer proof reinforces the infrastructure value. One customer quote on [Form.io's homepage](https://form.io/) says, "Speed to market using Form.io worked fantastically well," because the team did not have to spend most of its time building its own solution. Another proof point describes cutting data-processing workload by 50%.
Those quotes are not E-Sign+ specific. They do show the larger pattern: Form.io is strongest when teams need to stop rebuilding form, data, API, and workflow plumbing from scratch.
## **E Signature Software Comparison**
**Best fit****Typical tools****Watch the tradeoff**Standard document signingDocuSign, Adobe Acrobat Sign, Dropbox Sign, PandaDoc, Zoho SignStrong for envelopes and documents, but not always ideal when signed evidence must remain attached to application-owned submission data.Developer signing APIsAPI-first signing platformsFlexible for document workflows, but your team still owns the surrounding form schema, data model, and governance path.Self-hosted form signing infrastructureForm.io E-Sign+Strong fit when forms, submissions, APIs, permissions, and signature verification need to stay in the customer's controlled environment.The point is not that every team should leave document-signing platforms. Many should not.
The point is that e signature software has to match the record you are actually signing.
If the record is a contract document, a document-signing tool may be enough. If the record is a governed application submission, the signature belongs closer to the form infrastructure.
## **Key Takeaways**
- E signature software is a broad category, but enterprise form workflows need more than a signed PDF.
- Legal validity is only one part of the evaluation. Record retention, reproducibility, and context matter.
- DocuSign alternatives become relevant when teams need deployment control, API access, data ownership, or application-level signature proof.
- Form.io E-Sign+ fits teams that need cryptographic signature verification tied to submission data inside their own environment.
- The stronger question is not "Which tool signs documents fastest?" It is "Which system protects the signed record your application actually depends on?"
## **FAQ**
### **What Is E Signature Software?**
E signature software lets people sign electronic records or documents without printing and scanning paper. In business workflows, it usually includes signer routing, authentication, consent capture, audit history, completed document storage, and API or integration options.
### **Is E Signature Software Legally Binding?**
Electronic signatures can be legally valid in many contexts, including under the U.S. ESIGN Act and [EU eIDAS rules](https://ec.europa.eu/digital-building-blocks/sites/spaces/DIGITAL/pages/467109069/What%2Bis%2BeSignature). Buyers should still review the specific transaction type, jurisdiction, identity process, consent language, retention rules, and audit evidence with legal counsel.
### **What Is The Best DocuSign Alternative?**
The best DocuSign alternative depends on the job. If the job is standard document signing, a standalone signing platform may fit. If the job is signing structured form submissions inside a controlled application, Form.io E-Sign+ is worth evaluating because the signature proof stays closer to the form data and API workflow.
### **When Should A Team Choose Self-Hosted E Signature Software?**
A team should consider self-hosted signing infrastructure when sensitive submission data, regulatory obligations, customer architecture, data residency, or private deployment requirements make third-party-hosted signing workflows difficult to justify.
### **How Is Form.io E-Sign+ Different From A PDF Signature Tool?**
Form.io E-Sign+ is designed around submission-linked signature proof. PDFs can still be part of a workflow, but the stronger distinction is that E-Sign+ can verify signed form data and context inside the customer's own [self-hosted Form.io environment](/enterprise-self-hosting/).
### **Does Form.io Replace DocuSign?**
Not for every use case. DocuSign is a strong document-signing platform. Form.io is a stronger fit when signatures are part of a governed form workflow, embedded application, or self-hosted data pipeline where submission context matters.
### **What Should Enterprises Look For In E Signature Software?**
Enterprises should evaluate deployment control, signer identity, audit trail quality, API access, retention and reproducibility, [configuration-based pricing](/configuration-based-pricing/), integration fit, and whether the signed record is a document envelope or application data.
### **Can E Signature Software Work With APIs?**
Yes. Many signing platforms provide APIs, but the important question is what the API controls. For form-driven applications, APIs should connect signatures to submission records, permissions, workflow state, and downstream systems.
### **Why Does Signature Context Matter?**
Signature context matters because a signature without the surrounding record can be hard to defend. Teams may need to know the form version, field values, signer identity, submission ID, timestamp, protected fields, and whether anything changed after signing.
### **How Does Form.io Help With Controlled Form Workflows?**
Form.io gives teams [form management infrastructure](/form-management-software/) for forms, submissions, generated APIs, permissions, workflow actions, and self-hosted deployment. E-Sign+ extends that model by connecting signature verification to submission data instead of treating signing as a disconnected document event.
## **Build Signature Proof Into Your Form Infrastructure**
If your team needs signatures that stay attached to governed form data, application APIs, and your own deployment boundary, [try Form.io for self-hosted form workflows](/try-formio-for-free/).
---
# JSON Schema Validator Tools for Production Apps
*Published:* 2026-07-20
*Author:* Veronika Druck
*URL:* https://form.io/json-schema-validator-tools-production-apps/
*Description:* Developer guide to JSON Schema validator tools for production applications, comparing online validators, Ajv, Python jsonschema, Java validators, form generators, API contract tools, and Form.io's schema-driven form and API infrastructure.
Searches for **json schema validator** often start with a simple need: check whether this JSON payload matches this schema.
That is useful. It is also only the first layer.
In a production app, a schema may validate API requests, generate a form, drive documentation, define a submission shape, feed an AI tool, or become part of a governed application contract. The right tool depends on which job the schema has to do.
## **Key takeaways**
- A JSON Schema validator checks whether JSON data conforms to a declared structure, types, required fields, constraints, and references.
- Online validators are useful for quick checks, but production teams usually need runtime libraries, CI checks, API contract tooling, or form infrastructure.
- Ajv, Python `jsonschema`, and Java validators solve the library problem. They do not own form authoring, submissions, permissions, or deployment governance.
- Form generators turn schema into UI, but the backend still has to store, secure, expose, and govern submitted data.
- Form.io fits when schema needs to become form and API infrastructure: builder, renderer, submissions, generated APIs, permissions, workflow actions, revisions, and customer-controlled deployment.
## **Quick answer: which JSON Schema validator tool should you use?**
Use an online validator when you need to test a small schema and sample payload quickly.
Use Ajv when your JavaScript or TypeScript application needs fast JSON Schema validation in Node.js, the browser, an API gateway, or a build process.
Use Python `jsonschema` when your Python services need to validate instances against JSON Schema drafts and report validation errors in application code.
Use a Java validator such as NetworkNT when JSON Schema validation belongs in a JVM service, API layer, or request/response validation path.
Use Spectral or a schema lifecycle tool when the problem is not one payload, but API governance, linting, bundling, testing, and CI.
Use RJSF, JSON Forms, or SurveyJS when the goal is to generate a form interface from structured schema.
Use Form.io when the schema must become production form infrastructure: a human-facing form, submission record, generated REST API, workflow surface, permission boundary, and governed deployment model.
## **What a JSON Schema validator actually proves**
JSON syntax validation and JSON Schema validation are different jobs.
A JSON syntax validator answers: is this valid JSON?
A JSON Schema validator answers: does this valid JSON match the structure and rules the application expects?
That can include object shape, required fields, string formats, numeric ranges, enum values, array constraints, nested objects, and references to other schema definitions.
The official JSON Schema site describes JSON Schema as the vocabulary that enables JSON data consistency, validity, and interoperability at scale ([JSON Schema](https://json-schema.org/)). The specification hub also separates JSON Schema Core from JSON Schema Validation, where validation defines the keywords used to assert whether data is valid ([JSON Schema specification](https://json-schema.org/specification)).
That distinction matters because many production failures are not syntax failures. They are contract failures.
The payload is valid JSON, but it is missing the field the downstream service expects. The field exists, but the type changed. The UI allowed a value that the backend rejects. The API docs say one thing, but the runtime accepts another. The schema was copied into three services, and now nobody knows which version is authoritative.
A validator can catch part of that. It cannot, by itself, decide where schema ownership lives.
## **The five tool layers behind the search**
The search result page for `json schema validator` looks crowded because people use the same phrase for several different jobs.
**Tool layer****Best fit****What it proves or creates****What the team still owns**Online validatorQuick testing and debuggingA sample JSON instance matches a schemaProduction runtime, security, CI, versioningRuntime validatorAPI requests, service boundaries, app codePayloads satisfy schema rules in a language/runtimeUI, storage, workflows, governanceAPI contract toolingOpenAPI, linting, docs, API style rulesAPI definitions follow a contract and style rulesForm authoring, submissions, application stateForm generatorRendering forms from schemaA schema can produce a user-facing formBackend APIs, permissions, data lifecycleForm/API infrastructureProduction forms, APIs, submissions, workflowsSchema governs form UX, submission shape, generated APIs, and data handlingProduct fit, deployment ownership, policy configurationThe mistake is asking, "What is the best JSON Schema validator?" without asking, "What part of the system needs validation?"
## **Online validators are useful, but limited**
Online validators are useful for quick checks. They help developers paste in a schema, paste in sample JSON, and see errors immediately.
That is often exactly what the searcher wants.
But online validators should not become the production validation strategy. They are poor places for sensitive payloads. They do not enforce validation in your application. They do not live in CI. They do not control what happens after data is accepted.
Use them like a scratchpad.
For production, validation needs to move into the system path: application code, API gateway, test suite, CI pipeline, schema registry, form builder, or platform boundary.
## **Runtime validators: Ajv, Python, Java, and the application path**
Runtime validators belong where your application receives, transforms, or emits JSON.
Ajv is the obvious JavaScript and TypeScript example. Its documentation says it supports JSON Schema draft-04, draft-06, draft-07, draft 2019-09, draft 2020-12, and JSON Type Definition ([Ajv schema language guide](https://ajv.js.org/guide/schema-language.html)). Snyk's package database currently lists Ajv at more than 272 million weekly npm downloads, which shows how deeply validation libraries can sit inside the JavaScript ecosystem ([Snyk Ajv package page](https://security.snyk.io/package/npm/ajv)).
Python teams commonly reach for `jsonschema`, whose documentation shows the simple `validate` function and the validator classes behind it ([Python jsonschema validation docs](https://python-jsonschema.readthedocs.io/en/stable/validate/)).
Java teams may use NetworkNT's JSON Schema Validator, which describes support for multiple drafts and OpenAPI 3 request/response validation ([NetworkNT JSON Schema Validator](https://github.com/networknt/json-schema-validator)).
These tools are important because validation should happen where the system can reject bad data before it spreads.
The practical checklist is straightforward:
- Confirm which JSON Schema draft or dialect your validator supports.
- Reuse compiled validators where the library recommends it.
- Decide whether validation should fail fast or collect all errors.
- Make error messages useful enough for logs, developers, or users.
- Treat `$ref`, remote references, and bundled schemas as design choices, not incidental details.
- Benchmark against your actual schemas and payload sizes if validation runs in a hot path.
Runtime validators are the right answer when the job is validation.
They are not the whole answer when the same schema also needs to create forms, APIs, permissions, workflows, submission records, and audit evidence.
## **API contract tools: where JSON Schema meets OpenAPI**
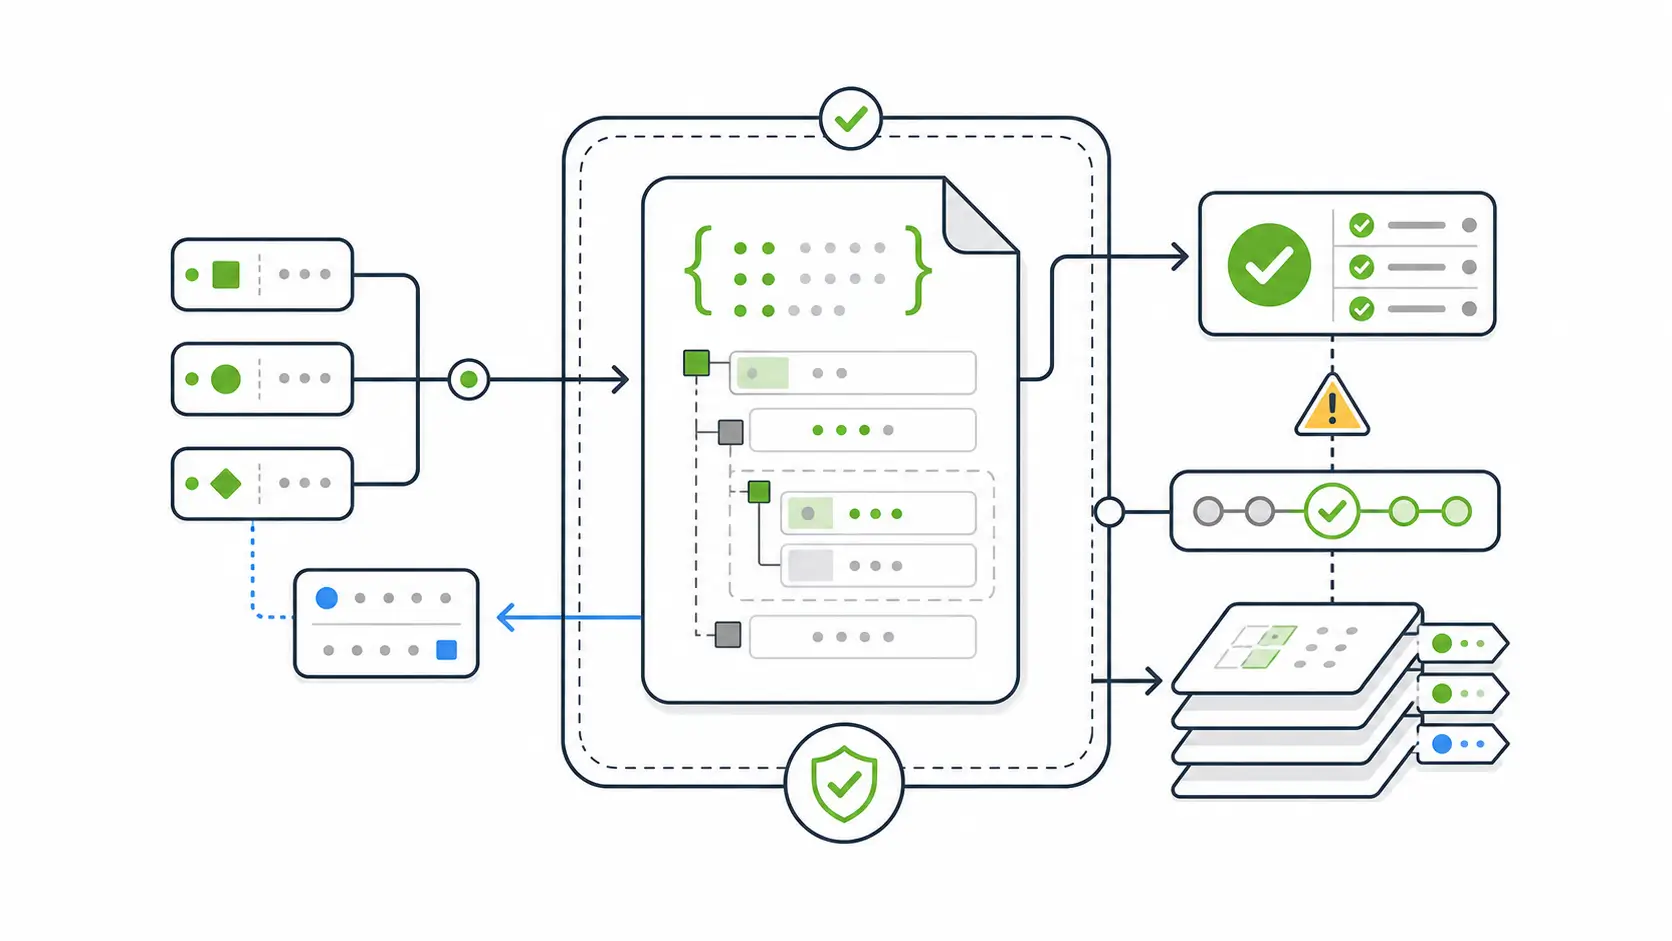For API teams, JSON Schema often appears through OpenAPI.
The OpenAPI Initiative's 3.1 release announcement says OpenAPI Schema Objects are now fully compatible with JSON Schema draft 2020-12 ([OpenAPI 3.1 release](https://www.openapis.org/blog/2021/02/18/openapi-specification-3-1-released)). That matters because the schema can become part of request validation, response validation, documentation, mock servers, SDK generation, and contract testing.
This is where tools such as Spectral fit. Spectral is a JSON/YAML linter designed with OpenAPI, AsyncAPI, and JSON Schema in mind ([Spectral](https://stoplight.io/open-source/spectral)). A validator asks whether data satisfies a schema. A linter can ask whether an API definition follows a team rule.
That is a different level of governance.
For production apps, the better question is not "Can we validate this object?" It is:
- Can we keep the API contract and implementation aligned?
- Can we catch drift in CI before release?
- Can we enforce style and security rules across many APIs?
- Can generated docs, mocks, clients, and tests inherit the same contract?
That is where JSON Schema starts becoming part of operational discipline.
## **Schema lifecycle tools: keep schemas from becoming loose files**
When schemas are shared across teams, a single validator is not enough.
Schema files need formatting, linting, testing, bundling, versioning, and promotion through environments. The official JSON Schema tools page shows how broad the ecosystem has become, including validators, documentation generators, schema-to-code tools, schema-to-web-UI tools, benchmarks, and compliance reports ([JSON Schema tools](https://json-schema.org/tools)).
Sourcemeta's JSON Schema CLI is a good example of the production-lifecycle layer. Its repository describes a CLI for maintaining schema repositories and ensuring quality during local development and CI/CD, including formatting, linting, testing, and bundling ([Sourcemeta JSON Schema CLI](https://github.com/sourcemeta/jsonschema)).
This layer matters when a schema is not a one-off file. It is a source artifact.
If multiple services, teams, or applications depend on it, schema changes need review. References need to resolve. Tests need to run. Breaking changes need to be understood before they reach production.
That is the point where teams stop treating JSON Schema as an isolated validator input and start treating it as part of the application contract.
## **Form generators: when schema becomes UI**
Some teams search for a JSON Schema validator and really need a form generator.
RJSF, for example, is a React component capable of building HTML forms out of JSON Schema. JSON Forms is another JSON Schema-based form renderer with data binding, validation, and rule-based visibility.
These tools are useful when a team wants schema to reduce repetitive form UI work.
But a form generator still leaves major production questions open:
- Where are submissions stored?
- Which API receives the data?
- How are permissions enforced?
- How are form changes versioned?
- How do non-developers safely edit forms?
- How does the schema move between dev, test, and production?
- What happens when the form becomes part of a regulated workflow?
A React JSON Schema form can render fields. That does not make it a form platform.
This is the line Form.io crosses.
## **Where Form.io fits**
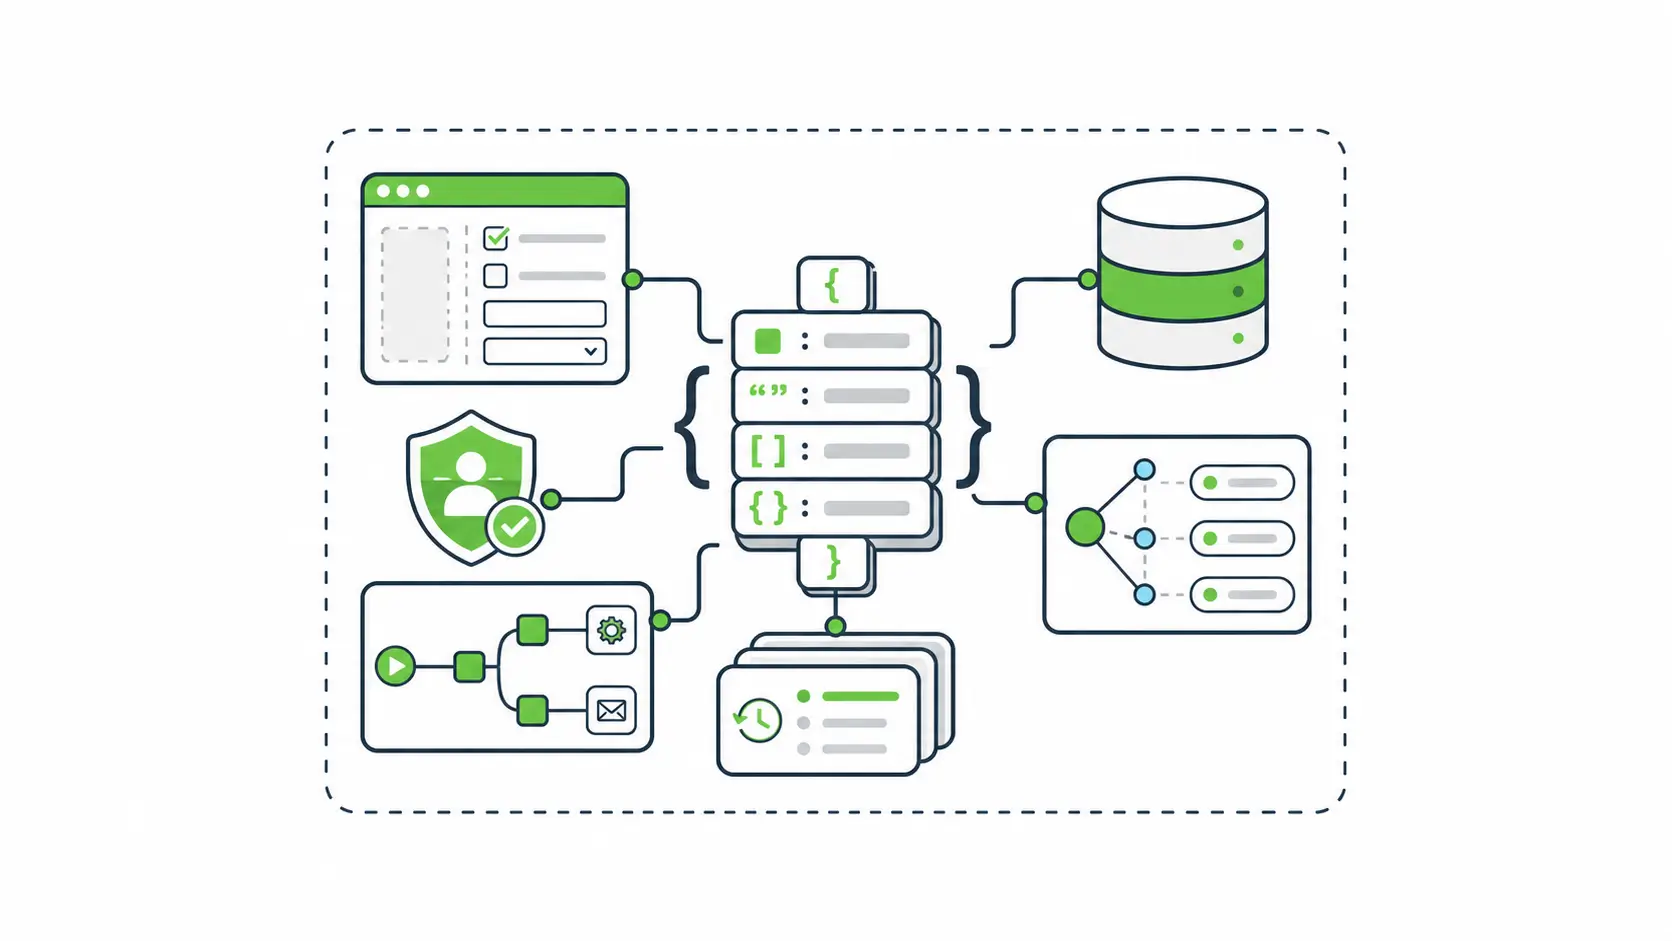Form.io belongs in this conversation only after the lower layers are clear.
It is not a replacement for Ajv, Python `jsonschema`, the JSON Schema specification, or OpenAPI tooling.
Form.io is the better fit when schema needs to become form and API infrastructure.
Form.io's Form JSON documentation says Form JSON defines the structure, appearance, and functionality of a form, and that the schema is used for rendering forms, generating REST API interfaces, and hosting the form schema for embedding ([Form.io Form JSON docs](https://help.form.io/form-building/form-json)).
Its feature documentation also explains that the builder outputs JSON schemas rather than static HTML, and that the same schema defines the UI, validation rules, data model, and REST API endpoints ([drag-and-drop form builder and APIs](https://form.io/features/drag-and-drop-form-builder-apis/)).
That is the infrastructure difference.
A validator can say, "This payload is valid."
A form generator can say, "This schema can render a form."
Form.io can connect the form definition, rendered experience, submission data, generated API, permission model, workflow actions, revisions, and deployment boundary.
That includes the operational pieces validators do not try to own: [self-hosted form deployment](https://form.io/features/self-hosted-forms-for-enterprise/), [form revisions](https://form.io/features/form-revisions-form-json-schema), [complete audit trails](https://form.io/features/log-forms-complete-audit-trail/), [secure forms compliance readiness](https://form.io/features/secure-forms-compliance-readiness/), and [fillable PDF workflows](https://form.io/features/fillable-pdf-forms) when the submitted record also needs document output.
That matters for teams building customer portals, healthcare intake, insurance claims, government services, financial onboarding, internal approval workflows, and B2B SaaS products where forms are part of the application architecture.
There is also customer proof behind this pattern. G2's indexed Form.io reviews include a State of Ohio pandemic-response example where Form.io was used to stand up forms, store and present data through an API, and feed analytics dashboards. The same reviewer called the model "easy to manage" across hundreds of websites ([G2 Form.io reviews](https://www.g2.com/products/form-io/reviews)).
Form.io's own customer proof makes the same point from the build-vs-buy side. Edify.ai said speed to market with Form.io "worked fantastically well" and that the team could focus development time on proprietary work instead ([Form.io customer proof](https://form.io/)).
The honest framing is this:
Use a JSON Schema validator when validation is the job.
Use Form.io when the schema needs to become a governed form, API, and submission system.
## **A production checklist for choosing JSON Schema tools**
Before choosing a tool, answer these questions.
### **1. Where does validation happen?**
Validation may belong in the browser, backend service, API gateway, test suite, CI pipeline, ETL job, or form platform.
One schema may need several validators in different places. That is normal. The risk is when each surface evolves its own slightly different rules.
### **2. Which schema version do you support?**
JSON Schema draft support is not trivia. Draft-07, 2019-09, and 2020-12 do not behave identically.
Pin the version. Document it. Make sure your tooling supports it before using draft-specific keywords in production.
### **3. Who owns schema changes?**
If schemas define production behavior, they need ownership.
A change to a field, type, required value, nested object, or reference may affect UI, API behavior, stored submissions, integrations, reports, and historical records.
### **4. Is the schema only validating data, or generating behavior?**
If the schema only validates API payloads, a runtime library may be enough.
If the schema renders forms, generates APIs, controls submissions, and drives workflow behavior, the decision belongs at the platform layer.
### **5. What happens after validation passes?**
This is the question most validator pages skip.
Where does the data go? Who can see it? Can it be edited? Is there revision history? Does it trigger a webhook? Can the workflow be audited? Can the platform run inside your environment?
If those questions matter, you are no longer only choosing a JSON Schema validator.
## **Key takeaways**
JSON Schema validators are necessary tools, but the phrase hides several different jobs.
Online validators help with quick checks. Runtime validators enforce contracts in code. API tooling keeps definitions consistent. Schema lifecycle tools keep shared schemas maintainable. Form generators turn schema into UI.
Form.io is for the next layer: production forms and APIs governed by schema, with submissions, permissions, workflows, revisions, and deployment control attached.
That is the practical distinction. Do not make a validator carry the full application burden. Use the validator where validation belongs, and choose infrastructure when the schema becomes infrastructure.
## **FAQ**
### **What is a JSON Schema validator?**
A JSON Schema validator checks whether JSON data conforms to rules described in a JSON Schema. Those rules can define object structure, required fields, data types, arrays, enums, numeric limits, string formats, and references to other schemas.
### **Is JSON validation the same as JSON Schema validation?**
No. JSON validation usually means checking whether the text is valid JSON syntax. JSON Schema validation checks whether valid JSON data matches an expected schema.
### **What is the best JSON Schema validator for JavaScript?**
Ajv is one of the default choices for JavaScript and TypeScript teams. It supports multiple JSON Schema drafts and is widely used across Node.js and browser environments.
### **What is the best JSON Schema validator for Python?**
Python teams commonly use the `jsonschema` package. It implements JSON Schema validation and provides validator classes, error handling, and draft-aware behavior.
### **Can JSON Schema generate forms?**
Yes, some tools can render forms from JSON Schema. RJSF and JSON Forms are common examples. The important distinction is that rendering a form does not automatically provide backend APIs, submission storage, permissions, or workflow governance.
### **Does OpenAPI use JSON Schema?**
OpenAPI 3.1 aligns its Schema Object with JSON Schema draft 2020-12. That makes JSON Schema more important for API contracts, documentation, request and response validation, and API tooling.
### **Should I paste sensitive data into an online JSON Schema validator?**
For sensitive production data, avoid it. Online validators are useful for examples and debugging, but regulated or customer data should be validated inside tools and environments your team controls.
### **What should production teams check before choosing a validator?**
Check draft support, runtime support, error quality, performance, custom formats, `$ref` handling, CI integration, schema bundling, and how schema changes are governed over time.
### **Is Form.io a JSON Schema validator?**
Form.io is not best understood as a standalone JSON Schema validator. It is a schema-driven form and API platform. It uses schema to help govern forms, submissions, generated APIs, permissions, workflows, and deployment control.
### **When should a team use Form.io instead of only a validator library?**
Use Form.io when the schema needs to operate a production form workflow, not just validate a payload. That includes embedded forms, submission records, generated REST APIs, permissions, workflow actions, revisions, and self-hosted deployment.
### **Can Form.io work alongside validators like Ajv?**
Yes. A production architecture can use validation libraries at service boundaries while using Form.io for the form, API, submission, and workflow layer. The key is deciding which system owns each contract.
If your schema needs to do more than validate JSON, [try Form.io for free](/try-formio-for-free/) and see how forms, APIs, submissions, and workflow controls can live on one foundation.
---
# Embedded Forms for B2B SaaS: The White-Label Form Builder Comparison
*Published:* 2026-07-17
*Author:* Veronika Druck
*URL:* https://form.io/embedded-forms-b2b-saas-white-label-comparison/
*Description:* A B2B SaaS buyer guide to embedded forms, embedded form builders, and white-label form infrastructure, comparing simple hosted embeds with Form.io's governed, API-aware, tenant-aware form platform for customer-facing SaaS products.
Embedded forms are easy to misunderstand.
For a marketing team, an embedded form might mean a signup widget pasted into a page. For a B2B SaaS platform, it can mean something much heavier: a branded form experience inside the product, customer-managed form creation, tenant-specific permissions, API-backed submissions, and workflow rules that cannot drift from the rest of the application.
That is the difference this comparison is about.
## **Embedded forms become product infrastructure**
An embedded form is a form rendered inside a webpage or application, usually through an iframe, script, SDK, component, or framework integration.
That definition is useful, but too broad. It puts a newsletter signup form and a customer-facing SaaS form builder in the same bucket.
B2B SaaS teams need a sharper distinction:
- Embedded form: a finished form appears inside your website or app.
- Embedded form builder: your users or admins can create and edit forms inside your product.
- White-label form infrastructure: the forms, builder, submissions, APIs, branding, roles, tenant boundaries, and workflow behavior all operate as part of your product.
That last category is where Form.io belongs. The [Form.io Enterprise Form Builder Module](https://form.io/enterprise-form-builder-module/) is built to embed a white-labeled form builder inside an application while the platform owner keeps control over components, data model, permissions, and workflow behavior.
## **Quick comparison**
**Option****Best fit****Main strength****Main tradeoff**Form.ioB2B SaaS teams that need embedded forms, embedded form building, APIs, tenant-aware control, and deployment flexibilityForms behave like governed application infrastructureMore platform than a simple marketing form team needsJotformHosted enterprise teams that want template-rich no-code form building and broad business workflowsFast, familiar hosted form creationStrongest when the form system can remain vendor-hosted and account-centeredFeatheryProduct teams that want polished embedded form UX and a white-label editor experienceStrong product-form experience and editor customizationTeams still need to evaluate backend governance, deployment, and data ownership depthSurveyJSJavaScript teams that want form libraries and a builder they can wire into their own stackDeveloper control inside front-end applicationsMore assembly work around storage, APIs, permissions, and operationsFormsortTeams building branded conversion flowsManaged branded flows with conversion focusNarrower fit when forms become governed product infrastructure123FormBuilder / similar toolsTeams that primarily need branded hosted forms and account-level white labelingFamiliar form-builder packagingWhite label often centers on branding more than application architectureThe right choice depends less on the phrase "embedded forms" and more on what the embedded form has to own.
## **The SaaS evaluation checklist**
If customers only need to submit a contact form, almost any credible form builder can work.
If customers need to create forms inside your application, the checklist changes:
- Can the finished form be embedded cleanly?
- Can the builder itself be embedded?
- Can vendor branding be removed from the form, builder, emails, URLs, and exports?
- Can each tenant have separate forms, submissions, themes, permissions, and workflows?
- Can you restrict which components, validation rules, logic, and publishing actions customers can use?
- Are submissions available through APIs, not only exports or webhooks?
- Where does submission data live?
- Can the form layer run inside the deployment boundary your customers require?
- Are revisions, access controls, and audit evidence part of the model?
- Does the pricing model still work when every customer creates forms?
Those questions are not cosmetic. They are architecture questions.
[Postman's 2025 State of the API report](https://voyager.postman.com/doc/postman-state-of-the-api-report-2025.pdf) found that 82% of organizations had adopted some level of API-first approach. That matters because embedded forms in a SaaS product are not just pixels. They create records, trigger workflows, and pass data to the rest of the application.
## **Where Form.io fits**
Form.io is the strongest fit when embedded forms need to behave like part of the product infrastructure.
The [Form.io form embedding documentation](https://help.form.io/dev/form-embedding) covers quick inline embedding, JavaScript embedding, iframe fallback, builder embedding, and framework embedding. That gives teams a practical path from simple rendering to deeper application integration.
But the more important distinction is what sits behind the embed.
Form.io forms are JSON-driven definitions connected to rendering, validation, submissions, APIs, permissions, and workflow behavior. The [drag-and-drop form builder with APIs](https://form.io/features/drag-and-drop-form-builder-apis/) is not only a UI for arranging fields. It is part of a system where form definitions can become application contracts.
That matters for SaaS platforms where customers need their own forms, variations, permissions, and branded experiences. The [Form.io homepage](https://form.io/) explicitly frames white-label SaaS use around form, API, and data management under the platform's brand or the customer's brand. It also describes multi-tenant child-project patterns for separating forms, data, and form building.
For more controlled environments, the [self-hosted Form.io deployment model](https://form.io/features/self-hosted-forms-for-enterprise/) matters because the form layer can live closer to the customer's infrastructure boundary instead of becoming an external data silo.
## **White label is more than branding**
Most white-label form pages talk about logos, colors, custom domains, badge removal, and branded emails.
Those are real requirements. They are not enough.
In a B2B SaaS product, white label also means the form capability has to respect the product's operating model. A tenant should not see another tenant's forms. A customer admin should not publish components that break downstream processing. A support team should be able to diagnose what changed. A developer should know how submissions map into APIs and workflows.
This is where a light embed starts to strain.
OWASP's API Security Top 10 puts [broken object-level authorization](https://owasp.org/API-Security/editions/2023/en/0xa1-broken-object-level-authorization/) first. That is a useful reminder for SaaS form architecture: if embedded forms create or expose customer records through APIs, authorization has to be object-aware and tenant-aware. Front-end hiding is not governance.
The same logic applies to validation and workflow behavior. The [conditional logic and validation features](https://form.io/features/form-conditional-logic-form-validation/) matter because the form should enforce rules before bad data becomes an API or workflow problem.
## **When a simpler embedded form is enough**
Use a simpler hosted embed when the form is not central to the product.
That includes:
- newsletter signup
- marketing lead capture
- event registration
- contact and support requests
- one-off surveys
- public feedback forms
- low-risk forms that can live in an external form account
In those cases, a hosted form builder with templates, brand settings, and a quick embed code may be the best decision. Jotform, Formsort, 123FormBuilder, and similar tools can be strong fits when speed and convenience are the main job.
The mistake is keeping that architecture after forms become a customer-facing product capability.
## **When embedded form infrastructure is needed**
Embedded form infrastructure becomes important when the form is part of how your SaaS product works.
Examples include:
- customer onboarding flows that differ by tenant
- partner and vendor portals
- regulated intake workflows
- customer-managed form libraries
- embedded application builders
- productized approval flows
- internal workflow forms exposed to external customers
- multi-office or multi-group customer operations
In these cases, forms need lifecycle control. NIST's [Secure Software Development Framework](https://csrc.nist.gov/pubs/sp/800/218/final) treats security practices as part of the software development lifecycle, which is the right lens for embedded form capability that ships inside a SaaS product. The form builder is no longer an outside utility. It is part of the product surface.
Data risk also changes the decision. [Thales' 2025 Cloud Security Study](https://cpl.thalesgroup.com/cloud-security-research) reported that 54% of cloud data is sensitive and that only 8% of respondents encrypt 80% or more of cloud data. That does not mean every embedded form needs self-hosting. It does mean SaaS teams should know where form data lives, who can access it, how it is encrypted, and how it moves through APIs.
## **Customer proof: white-label forms as a business model**
The white-label use case is not theoretical for Form.io.
In Form.io's Bursting Silver case study, the company describes how a regulatory-industry platform [white-labeled Form.io](https://form.io/case-studies/from-facing-the-risk-of-losing-an-entire-industry-to-generating-millions-and-having-new-clients-call-them/) to support its industry, sign dozens of new clients, and increase revenue by 25%.
That proof point matters because it connects embedded forms to a business model, not just a UI decision. When forms are a capability customers use inside your product, the form layer can influence retention, onboarding, service load, expansion, and product differentiation.
## **The decision framework**
Choose a simple embedded form when the form is a page element.
Choose a hosted enterprise form builder when business users need fast form creation and the external vendor account model is acceptable.
Choose a JavaScript form library when your team wants front-end control and is ready to build the backend, storage, permissions, and operational layer around it.
Choose Form.io when the form capability needs to become part of your product architecture: embedded rendering, embedded building, customer self-service, white-label experience, structured schemas, generated APIs, permissions, validation, workflow behavior, and deployment control.
That is the real difference.
Embedded forms are not automatically infrastructure. But in B2B SaaS, they often become infrastructure faster than teams expect.
## **Key takeaways**
- Embedded forms can mean a simple widget, an embedded form builder, or full white-label form infrastructure.
- SaaS teams should evaluate builder embedding, tenant separation, data ownership, APIs, permissions, workflow behavior, and deployment model.
- Competitors can be good fits for hosted no-code forms, polished product forms, developer libraries, or branded conversion flows.
- Form.io is strongest when the form layer needs to stay connected to schemas, APIs, submissions, permissions, and workflows inside the product architecture.
- A simple embed is enough for low-risk marketing forms. It is not enough when customers need to build and govern forms inside your SaaS.
## **FAQ**
### **What are embedded forms?**
Embedded forms are forms rendered inside a webpage or application through an iframe, script, SDK, component, or framework integration. The user completes the form without leaving the surrounding site or product experience.
### **What is an embedded form builder?**
An embedded form builder is a builder or editor exposed inside your application so users can create or change forms without going to a separate vendor dashboard.
### **What does white-label mean for forms?**
At minimum, white label usually means custom branding, colors, domains, and removal of vendor badges. For SaaS platforms, it should also include builder experience, tenant separation, emails, exports, permissions, and workflow behavior.
### **Can customers create their own forms inside a SaaS product?**
Yes, if the platform supports embedded form building. The important question is whether customers can do that inside guardrails your product controls.
### **Are iframe embedded forms enough?**
Sometimes. Iframes can be practical for low-risk or simple use cases. They are often weaker when the form needs deep styling, app authentication, event handling, tenant-aware permissions, or tight workflow integration.
### **Which embedded form builder is best for multi-tenant SaaS?**
Form.io is a strong fit when multi-tenant SaaS teams need white-labeled form creation, APIs, permissions, structured submissions, workflow behavior, and deployment control. Simpler tools may fit when the requirement is only branded form capture.
### **Do embedded forms create security risks?**
They can if teams treat them as front-end widgets while the data becomes sensitive application data. The right controls depend on authorization, validation, tenant separation, encryption, auditability, and where submissions are stored.
### **When should I choose Form.io over a simpler form builder?**
Choose Form.io when forms are part of the application infrastructure: customers create forms, submissions feed APIs, permissions matter, workflows depend on form data, and the deployment boundary is important.
### **Can Form.io replace my whole application backend?**
No. Form.io is infrastructure for forms, APIs, submissions, validation, permissions, and workflow-related actions. Your application still needs its own product logic, user experience, integrations, and surrounding architecture.
## **Build embedded forms that behave like your product**
If your SaaS customers only need a form on a page, keep it simple.
If they need governed, branded, customer-managed forms inside your product, start with infrastructure that can carry the form, data, API, and workflow model together.
[Try Form.io for white-label embedded form infrastructure](/try-formio-for-free/).
---
# HIPAA-Compliant Form Builder: What Healthcare SaaS Teams Should Evaluate
*Published:* 2026-07-06
*Author:* Veronika Druck
*URL:* https://form.io/hipaa-compliant-form-builder-healthcare-saas-platforms/
*Description:* A healthcare SaaS evaluation guide for HIPAA-compliant form builders, explaining BAA boundaries, PHI storage, audit trails, APIs, self-hosted deployment, and when Form.io fits as form infrastructure.
## **Key Takeaways**
- A HIPAA-compliant form builder is not compliant because it has a healthcare template or a lock icon.
- If a vendor creates, receives, maintains, or transmits ePHI for a covered entity or business associate, the BAA and operational responsibility boundary matter.
- Hosted HIPAA form builders can be a good fit for simple intake, consent, appointment, or website forms.
- Healthcare SaaS teams usually need more than a hosted form link: APIs, embedded rendering, role-aware access, audit logs, revision history, and deployment control.
- Form.io is strongest when HIPAA-governed forms are part of application infrastructure rather than a standalone intake tool.
## **What "HIPAA-Compliant Form Builder" Actually Means**
The phrase "HIPAA-compliant form builder" is useful shorthand, but it can hide the real decision.
HIPAA compliance is not a feature that one vendor turns on for the whole organization. It is a legal, contractual, administrative, technical, and operational responsibility. The form builder can support that responsibility. It cannot replace it.
The U.S. Department of Health and Human Services explains that when a covered entity or business associate uses a cloud service to create, receive, maintain, or transmit ePHI, the cloud service provider is generally a business associate and the parties need a HIPAA-compliant business associate agreement. [HHS also notes](https://www.hhs.gov/hipaa/for-professionals/special-topics/health-information-technology/cloud-computing/index.html) that this can still be true even when the provider stores only encrypted ePHI and does not hold the decryption key.
That point matters for online forms.
If a form collects PHI, the risk does not stop at the submit button. The data may be stored, emailed, exported, routed through webhooks, copied into a CRM, written to a database, attached to a PDF, shown in an admin portal, or sent to downstream systems. A HIPAA-ready form tool has to be evaluated across that whole path.
The [HHS Security Rule](https://www.hhs.gov/hipaa/for-professionals/security/index.html) frames the obligation around administrative, physical, and technical safeguards for the confidentiality, integrity, and availability of ePHI. In plain terms: the form is only one surface. The system around the form has to be governed too.
The risk is not theoretical. IBM's 2025 Cost of a Data Breach report puts the global average breach cost at [$4.4 million](https://www.ibm.com/reports/data-breach?app=true). That is not a healthcare-form-specific number, but it gives the right scale for the decision: a form that collects sensitive health data is not a minor website feature when the surrounding workflow is weak.
## **The Quick Decision: Practice Intake Tool Or Healthcare SaaS Infrastructure?**
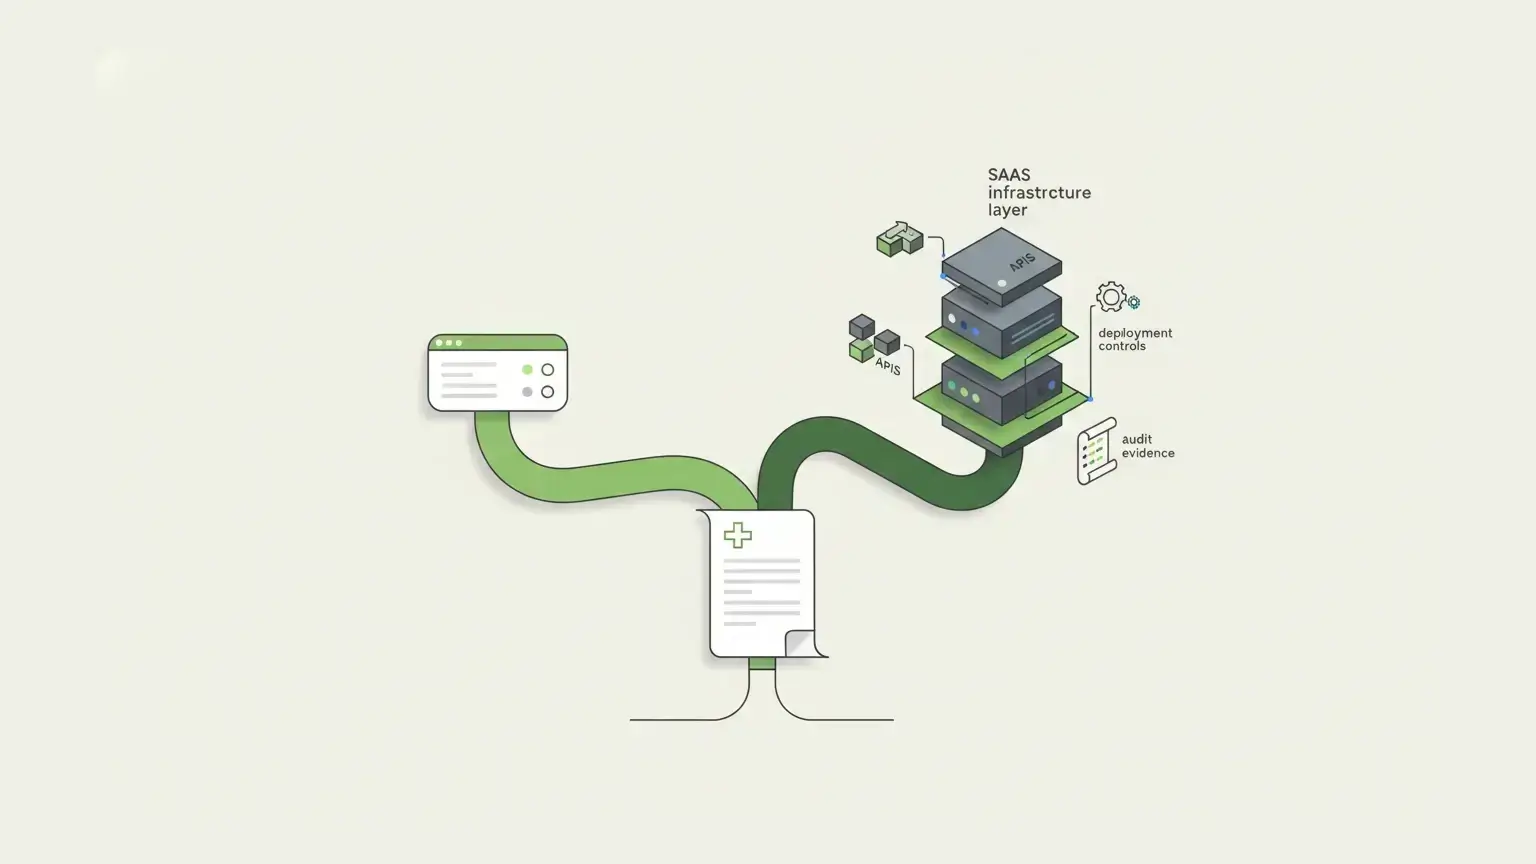Most buyers searching for a HIPAA-compliant form builder fall into one of two groups.
The first group needs a faster way to collect patient information. A clinic, therapy practice, dental office, or small healthcare provider may need intake forms, consent forms, appointment requests, file uploads, and e-signatures. A hosted HIPAA-enabled form builder can work well here if the vendor signs the right BAA, the account is configured correctly, and the workflow keeps PHI inside approved systems.
The second group is building a healthcare product. That buyer does not only need a form. It needs form capability inside an application.
For healthcare SaaS teams, forms may power onboarding, eligibility, clinical screening, referrals, patient-reported outcomes, provider workflows, prior authorization, records updates, care-team routing, and follow-up check-ins. A [third-party digital health article from Light-it](https://lightit.io/blog/5-ways-to-apply-hipaa-compliant-form-builders-to-your-digital-health-product/) describes HIPAA-compliant forms as part of ongoing product workflows such as patient intake, assessments, appointment scheduling, regular check-ins, and feedback surveys. That is a different problem than publishing a secure contact form on a website.
The distinction is simple:
**Buyer situation****Better fit**One practice needs intake forms and patient packetsHosted HIPAA-enabled form builderA healthcare SaaS product needs forms inside its appEmbedded form infrastructureA team needs patient data routed to internal systemsAPI-first form platformA team must keep PHI inside its own environmentSelf-hosted form infrastructureA product needs tenant-specific forms and permissionsWhite-label or multi-tenant form infrastructureThe mistake is treating these as the same purchase.
## **The Requirements Checklist**
Before comparing logos, healthcare teams should define the control boundary.
### **BAA Scope**
A BAA is not a marketing badge. It establishes the permitted uses and disclosures of PHI, requires appropriate safeguards, covers reporting obligations, addresses subcontractors, and should align with the actual workflow. [HHS sample BAA guidance](https://www.hhs.gov/hipaa/for-professionals/covered-entities/sample-business-associate-agreement-provisions/index.html) says these contracts should clarify and limit how a business associate may use or disclose PHI and require safeguards to prevent unauthorized use or disclosure.
The practical question is: which vendor is creating, receiving, maintaining, or transmitting ePHI?
If the form builder stores submissions, handles uploaded files, sends notifications containing PHI, or passes data to another system, the BAA and subcontractor chain need to match that reality.
### **Where PHI Is Stored**
Data location is not a minor implementation detail. It determines who administers the database, where backups live, which security controls apply, who can access logs, what happens at termination, and how incident response works.
For a simple hosted form workflow, vendor-managed storage may be acceptable. For a healthcare SaaS product, the team may need submissions in its own database, cloud account, region, network, or compliant infrastructure boundary.
This is one reason self-hosting matters. It does not make an application HIPAA compliant by itself. It gives the customer more control over where PHI lives and which controls surround it.
### **Access Control And Identity**
HIPAA-governed forms usually need more than a shared admin login.
Ask who can view submissions, edit forms, export data, upload files, change permissions, configure webhooks, or see audit logs. Then map those permissions to real roles: patient, provider, customer admin, internal support, implementation partner, compliance reviewer, and developer.
For SaaS products, this gets harder. One customer's admin should not see another customer's submissions. A support user may need temporary access. A provider may need access to only assigned patients. A form builder may need schema-editing rights without PHI access.
The form system has to support those boundaries instead of forcing the application to patch them later.
### **Audit Logs And Revision History**
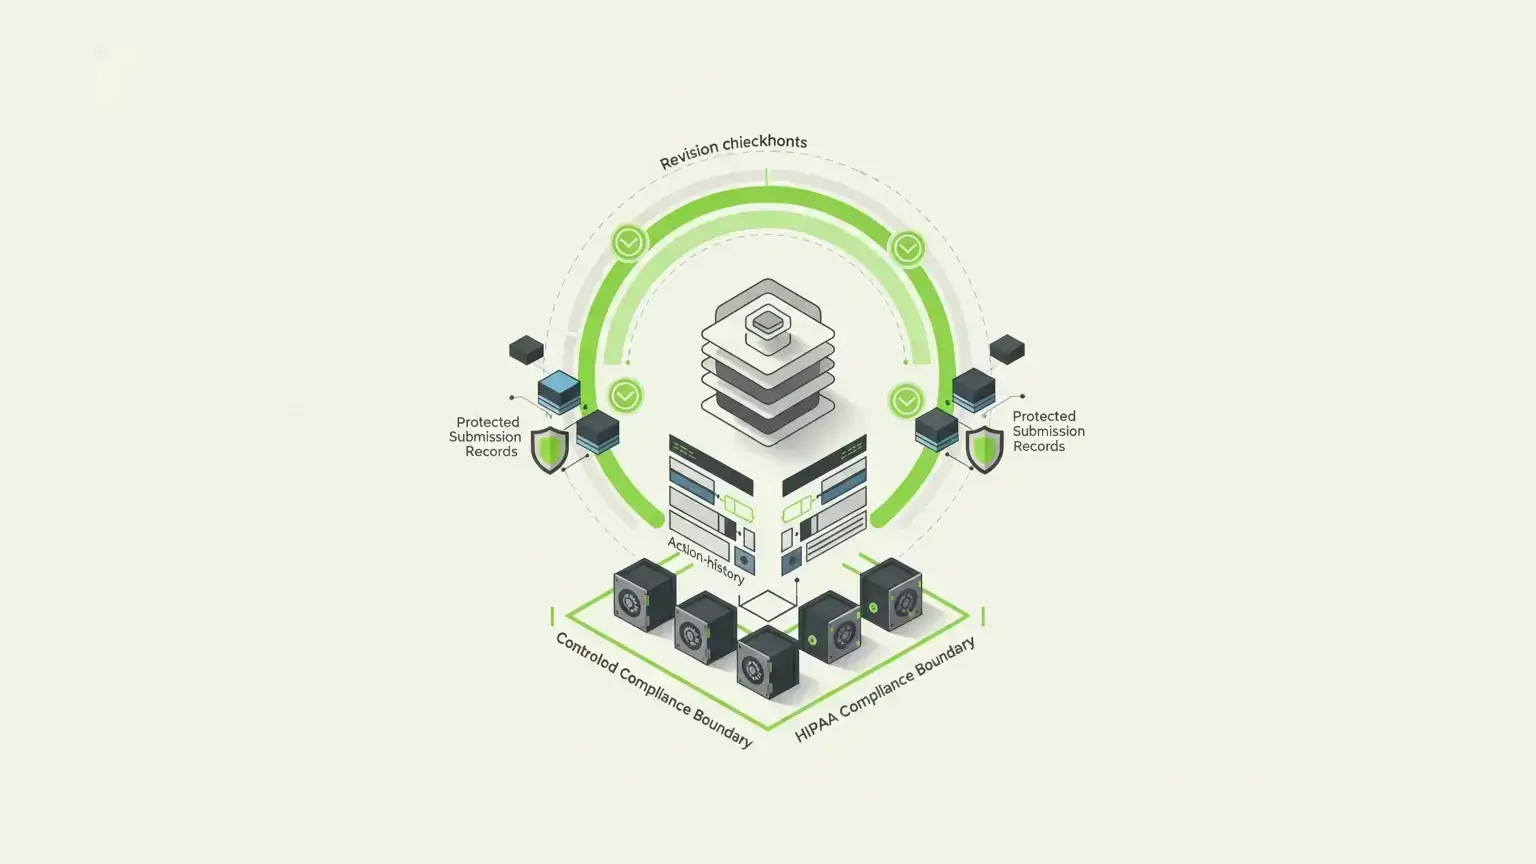The highest-risk part of a healthcare form often starts after submission.
What changed? Who changed it? Which version of the form captured the original data? Did a webhook run? Did an email action send? Did the submitted value get edited later? Can the team reconstruct the record if an auditor asks?
Generic form builders often focus on collection. Healthcare SaaS teams need evidence.
Form.io's Security Module is built around this kind of evidence. Its [secure forms and compliance readiness documentation](https://form.io/features/secure-forms-compliance-readiness/) describes advanced audit logging, action logs, form revisions, submission revision logs, submission collections, and container security scanning. The important distinction is that form revisions track changes to the form schema, while submission revisions track changes to submitted data.
That distinction sounds small. It is not.
A historical submission is not only the answers a patient gave. It is the form version, validation rules, field labels, conditional logic, workflow context, and submission state that governed the data at the time.
### **APIs And Integration Control**
Healthcare forms rarely stay inside the form tool.
An intake form may need to create a patient profile, update a resource, trigger a referral workflow, generate a PDF, route a task to a care team, or feed an internal dashboard. A screening form may need validation, conditional follow-up, file uploads, and downstream review. A provider form may need to connect with legacy systems or internal case management.
If the form builder only gives you CSV exports or a fragile integration layer, the application team inherits the risk.
Form.io's [concepts documentation](https://help.form.io/start/form.io-concepts) explains that as a form is built, Form.io constructs the JSON schema and defines a REST API endpoint. Submissions are API-accessible, owned by users for permission enforcement, portable, and revision-trackable with the Security & Compliance package. That is the infrastructure argument: the form definition, submitted data, API, and access model belong in the same system.
### **Tenant And Customer Boundaries**
Healthcare SaaS teams often serve many customers from one product. That means the form layer may need tenant-aware configuration, customer-specific forms, white-labeled experiences, separate roles, different workflows, and different data retention expectations.
This is where "HIPAA form builder" searches become too small. The issue is not only whether one form can collect PHI. It is whether a platform can support repeated, governed form workflows across customers without collapsing into one-off custom code.
## **Common HIPAA Form Builder Categories**
The market is easier to understand when you separate platform types.
**Category****Best fit****Strength****Gap**Hosted HIPAA form builderPractices and clinics that need intake, consent, and website formsFast setup, templates, vendor-managed hostingLimited architecture and data-boundary controlHealthcare intake platformPatient intake, appointment, and engagement workflowsHealthcare-specific UX and workflowsMay be too narrow for broader SaaS infrastructureEnterprise form/workflow platformLarger teams with governed workflowsMore controls and integrationsOften still vendor-hosted or workflow-product centeredSelf-hosted form infrastructureHealthcare SaaS and regulated product teamsDeployment control, APIs, data ownership, auditabilityRequires technical ownershipCustom buildUnique workflows with no acceptable platform fitMaximum controlExpensive to build, secure, test, document, and maintainThere is no universal winner. There is only the right layer for the job.
## **Where Form.io Fits For Healthcare SaaS**
Form.io is not the lightest way to publish a HIPAA-ready website form. It is a stronger fit when forms are part of healthcare application infrastructure.
That usually means the team needs some combination of embedded forms, generated APIs, custom roles, submission storage, workflow actions, form revisions, submission revisions, audit logs, file/PDF handling, and customer-controlled deployment.
Form.io's [self-hosted forms documentation](https://form.io/features/self-hosted-forms-for-enterprise/) says the platform can run in AWS, Azure, Google Cloud, private data centers, or Docker-based environments, with submission data stored in the customer's MongoDB instance and security boundary. The same page is careful about the boundary: self-hosted deployment enables compliance control, but the customer still needs proper access controls, encryption, audit logging, network security, and the rest of the compliance program.
That honesty is useful.
Healthcare SaaS teams do not need another vendor promising that complexity disappears. They need a platform that gives them the right control surfaces: forms, resources, generated APIs, submissions, actions, [roles and permissions](https://form.io/features/forms-for-teams/), revisions, and audit evidence.
Form.io's [healthcare forms page](https://form.io/industries/healthcare-forms/) points to use cases such as patient registration, records, appointments, routing inquiries, notifications, [conditional logic](https://form.io/features/form-conditional-logic-form-validation/), mobile-responsive forms, offline mode, form revisions, autosave, accessibility, and the Security Module. The better strategic reading is not "Form.io makes healthcare simple." It is that Form.io gives healthcare teams a form infrastructure layer they can govern inside their own architecture.
The [CHESS Health case study](https://form.io/how-a-flexible-form-solution-helped-get-to-market-in-6-weeks-instead-of-6-months/) is a useful proof point. Form.io describes a healthcare technology company managing EMRs, EHRs, interoperability, strict security and compliance requirements, sensitive data in its own environment, legacy integrations, and the need to get to market faster. The case headline says CHESS Health got to market in 6 weeks instead of 6 months. That is the category fit: not a simple intake form, but a healthcare product workflow that needed speed without giving up architectural control.
There is also a buyer sentiment signal from [Trustpilot](https://www.trustpilot.com/review/form.io), where one reviewer called Form.io "really great software, both for integration and standalone." The quote is broad, but it matches the central buying reason for this article: the form layer has to work as part of a larger system.
## **When A Hosted HIPAA Form Builder Is Enough**
A hosted HIPAA form builder may be the better answer when the workflow is simple and the organization accepts the vendor-managed model.
That can include:
- Patient intake forms for one practice
- Consent forms
- Appointment request forms
- Simple file uploads
- Basic medical history forms
- Feedback surveys
- Website-embedded forms
- Staff-created forms with limited integration needs
In these cases, speed matters. Templates matter. A no-code builder matters. A signed BAA, encrypted submissions, access controls, and a clean admin experience may be enough.
The important word is "enough."
If a workflow starts simple but will later need custom identity, tenant-specific configuration, deeper APIs, application-owned submission records, role-aware workflows, and evidence-grade revision history, the cheapest or fastest hosted option can become expensive later.
## **When Healthcare SaaS Teams Should Avoid Standalone Form Tools**
Standalone form tools become risky when the form is part of the product's core workflow.
Watch for these signals:
- PHI must remain inside your own cloud, database, or approved deployment boundary.
- Forms need to be embedded directly into your product experience.
- Customers need their own form configuration, roles, branding, or workflows.
- Submissions need to become application records, not just entries in a vendor dashboard.
- The product needs generated APIs, webhooks, resources, permissions, and workflow actions.
- Historical records need to resolve to the form version that captured them.
- Support, operations, providers, and customer admins need different access rules.
- Exports, notifications, analytics, and AI tools must not create uncontrolled PHI copies.
These are not edge cases for healthcare SaaS. They are ordinary product requirements.
The wrong tool can still pass the first demo. The problem appears later, when the team needs to prove who accessed PHI, why a submission changed, whether a field existed at the time of capture, where a file was stored, or why one tenant's workflow affected another.
That is the moment when "just use a form builder" stops being a plan.
## **Evaluation Table**
## 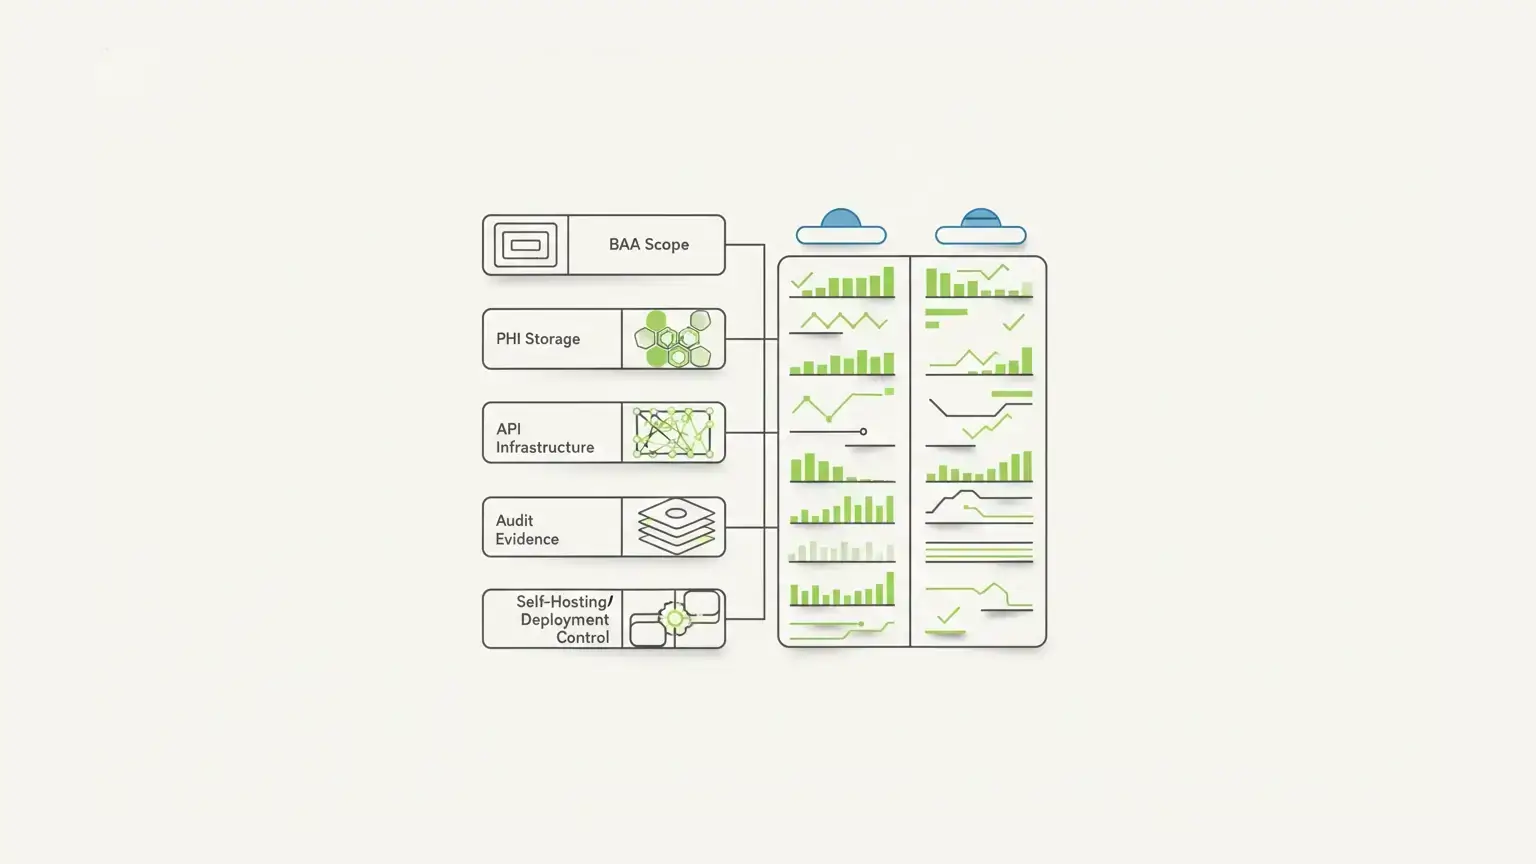 **Evaluation question****Why it matters****What to look for**Will the vendor sign the right BAA?PHI handling needs a contractual boundaryBAA scope, subcontractors, permitted uses, breach/security incident termsWhere is PHI stored?Data location shapes risk and responsibilityCustomer-controlled database, approved region, backup and termination termsCan access map to real roles?Healthcare workflows are role-sensitiveRBAC, SSO/MFA options, admin separation, own-vs-all submission accessAre form changes versioned?Historical records need contextForm revisions, schema history, promotion/stage controlsAre submission changes versioned?Modified PHI needs accountabilitySubmission revisions, who/when/what logs, revert or history viewsAre actions auditable?Integrations are common failure pointsAction logs for emails, webhooks, resource saves, and workflow stepsDoes the platform generate APIs?SaaS products need system integrationREST APIs, submission endpoints, resources, webhooksCan forms be embedded and white-labeled?Healthcare SaaS forms live inside productsRenderer libraries, embedded builder, brand controlCan the platform be self-hosted?Some teams need customer-controlled infrastructureDocker, cloud/on-prem deployment, environment variables, customer databaseDoes the vendor overclaim compliance?Overclaiming creates riskClear shared-responsibility language and technical-control boundaries**What Not To Assume**
Do not assume a healthcare template makes a workflow compliant.
Do not assume encryption solves the whole problem. HHS cloud guidance is clear that encryption alone does not remove business associate obligations when a provider maintains ePHI.
Do not assume a BAA covers every downstream action. If submissions are emailed to the wrong inbox, copied into a non-approved CRM, exported to spreadsheets, or passed through an unreviewed automation, the form builder's feature list is not the whole risk picture.
Do not assume self-hosting removes responsibility. It increases control. It also increases the customer's obligation to configure and operate the environment correctly.
Do not assume a standalone form tool will scale into product infrastructure. Sometimes it will. Often it will not.
## **FAQ**
### **Is A Form Builder HIPAA Compliant If It Signs A BAA?**
No. A BAA is necessary in many PHI workflows, but it is not the whole compliance answer. The organization still needs appropriate safeguards, policies, configuration, access control, risk analysis, monitoring, and incident-response processes.
### **Can Healthcare Teams Use Google Forms For PHI?**
Do not use a general form workflow for PHI unless the entire vendor relationship, configuration, storage model, access controls, and BAA requirements are approved for that use. For most healthcare SaaS teams, the safer default is to use a platform designed for regulated data workflows.
### **What Features Should HIPAA-Compliant Forms Have?**
At minimum, evaluate BAA support, encryption, access control, audit logs, secure storage, user management, file handling, retention/deletion, and integration behavior. For healthcare SaaS, also evaluate APIs, embedding, tenant boundaries, revision history, and deployment control.
### **Do Healthcare SaaS Teams Need Self-Hosted Forms?**
Not always. But self-hosting becomes important when PHI must stay inside the customer's environment, when the form layer needs to align with internal security controls, or when product architecture requires direct control over database, network, logging, and deployment boundaries.
### **Does Self-Hosting Make A Form Platform HIPAA Compliant?**
No. Self-hosting enables more control over infrastructure and data boundaries. Compliance still depends on how the environment is configured, monitored, documented, and governed.
### **Can Form.io Be Used For HIPAA Workflows?**
Form.io provides healthcare-oriented form infrastructure and security/compliance capabilities that can support HIPAA-governed workflows in customer-controlled environments. The customer's organization remains responsible for its HIPAA compliance program, configuration, policies, and deployment controls.
### **Does Form.io Certify My Application As HIPAA Compliant?**
No. Form.io's own compliance-readiness language is clear that the platform provides technical capabilities that support regulated deployments; it does not certify a customer's application or organization for HIPAA.
### **Why Do Audit Logs Matter For HIPAA Forms?**
Audit logs help answer who accessed or changed data, when it happened, what entity was affected, and which workflow action ran. For healthcare SaaS teams, that evidence can matter as much as the original form submission.
### **Should PHI Be Stored In A Third-Party Form Vendor Account?**
It depends on the workflow, BAA, risk analysis, and organizational policy. For simple intake forms, vendor-managed storage may be acceptable. For healthcare SaaS platforms, application-owned or customer-controlled storage may be a better fit.
### **What Should I Ask Before Collecting PHI Through An Online Form?**
Ask where PHI is stored, who can access it, which BAA covers it, whether uploads and notifications are protected, how audit logs work, how long data is retained, how submissions are deleted or exported, and what happens when the form changes.
## **Build HIPAA-Governed Form Infrastructure With Form.io**
If your healthcare product only needs a simple intake form, choose the fastest HIPAA-enabled tool that satisfies your compliance review.
If your forms define product workflows, API contracts, submissions, permissions, audit evidence, and data boundaries, choose infrastructure that respects that complexity from the start.
[Try Form.io for healthcare SaaS form infrastructure](/try-formio-for-free/).
---
# MCP Server List: What Regulated Enterprise Developers Should Actually Use
*Published:* 2026-06-08
*Author:* Veronika Druck
*URL:* https://form.io/mcp-server-list-regulated-enterprise-developers/
*Description:* A regulated-enterprise guide to MCP server lists and MCP server selection, covering the official MCP Registry, GitHub, GitLab, AWS, Azure, Atlassian, Playwright, Sentry, Docker, Form.io MCP Server, governance criteria, security boundaries, and when domain-specific servers belong in an AI coding workflow.
You can find an MCP server list in seconds. That is not the hard part. The hard part is deciding which servers deserve access to your source code, cloud accounts, tickets, documentation, test environments, and production-adjacent business data.
For regulated enterprise developers, the question is not "which MCP servers are popular?" It is "which MCP servers can we trust inside a governed workflow?"
## **The quick answer**
Start with the official MCP Registry, then filter by control surface.
For regulated enterprise development, the strongest shortlist usually includes:
**MCP surface****Best fit****Enterprise question**Official MCP RegistryDiscovery and metadataIs this server officially published, namespace-authenticated, and still current?GitHub MCP ServerRepos, pull requests, issues, Actions, security findingsCan the agent work inside the same SDLC boundary developers already use?GitLab MCP ServerGitLab.com, self-managed GitLab, Duo workflowsDoes it respect the deployment model and permissions your GitLab instance already enforces?AWS MCP ServersCloud architecture, docs, API operationsAre IAM, least privilege, CloudWatch metrics, and CloudTrail evidence understood before use?Azure MCP ServerAzure resources, Entra ID-backed cloud workflowsDoes the server inherit the identity and guardrail model your Azure teams already use?Atlassian Rovo MCP ServerJira, Confluence, CompassDoes the agent see only what the user has permission to see?Playwright MCPBrowser automation and UI testingAre unsafe direct-code tools disabled unless the client is trusted?Sentry MCPDebugging and observabilityCan the agent inspect errors without turning observability into an unbounded data pipe?Docker MCP toolingLocal gateway, catalog, containerized MCP operationsCan servers be packaged and scoped consistently across teams?Form.io MCP ServerForms, resources, actions, APIs, and schema-driven application infrastructureCan the agent build against governed form and API patterns instead of improvising them?That is the useful MCP server list for regulated teams: not a popularity contest, but a map of which systems an agent can touch, how it authenticates, what it can change, and where the audit evidence lands.
## **What an MCP server list can and cannot tell you**
MCP, or Model Context Protocol, gives AI clients a standard way to connect to external tools and data. An MCP server is the bridge between the agent and a system such as GitHub, AWS, Jira, a browser, a database, or a domain platform such as Form.io.
An MCP server list helps with discovery. It does not prove that a server belongs in your enterprise agent environment.
That distinction matters because the official MCP Registry itself is a metadata layer. The registry documentation describes it as the official centralized repository for publicly accessible MCP server metadata, while also noting that it is still in preview and does not support private servers. It supports discovery, namespace authentication, installation metadata, and REST API access. It is not a substitute for enterprise security review.
That is the first mistake many teams make. They treat discovery as approval.
For a developer testing locally, that may be tolerable. For a regulated team, it is a weak control. A server that reads public docs is not in the same risk category as a server that can open pull requests, read customer tickets, execute cloud API calls, or inspect production error traces.
The list is the beginning. The trust decision comes after.
## **The regulated-enterprise filter**
Before you add a server to Claude Code, Cursor, VS Code, Windsurf, or another MCP client, ask six questions.
### **Who maintains it?**
Prefer official or vendor-maintained servers when the system is critical. A community server can be useful, but enterprise teams need a clear owner, release trail, issue history, and support path.
This is why GitHub, GitLab, AWS, Azure, Atlassian, Playwright, Docker, Sentry, and Form.io deserve separate treatment from generic directories. They are not just "available MCP servers." They are maintained by, or directly tied to, the systems they expose.
### **What identity model does it inherit?**
A lower-risk server is usually one that inherits the identity and permission model already governing the system.
[GitLab's MCP docs](https://docs.gitlab.com/user/gitlab_duo/model_context_protocol/mcp_server/), for example, describe OAuth registration and HTTP transport options, and they support GitLab.com, Self-Managed, and Dedicated environments. [Atlassian's remote MCP server](https://support.atlassian.com/atlassian-rovo-mcp-server/docs/getting-started-with-the-atlassian-remote-mcp-server/) uses OAuth 2.1 and respects Jira, Confluence, and Compass permissions. [Azure MCP Server](https://learn.microsoft.com/en-us/azure/developer/azure-mcp-server/overview) uses Microsoft Entra ID through Azure Identity.
That matters more than convenience. If the server works around identity, it works around governance.
### **What can it mutate?**
Read-only access is one risk. Write access is another. Production mutation is another.
A server that searches docs can still leak context. A server that changes infrastructure, submits forms, opens tickets, or modifies code can create operational state. Treat those differently.
The [MCP security guidance](https://modelcontextprotocol.io/specification/2025-06-18/basic/security_best_practices) calls out risks such as confused deputy behavior, token passthrough, SSRF, session hijacking, local server compromise, and the need to minimize scopes. Those are not abstract security concerns. They are what happens when an agent can act through a server whose authority is broader than the user's intent.
### **Where are logs written?**
Regulated teams need evidence. If an agent uses a server to retrieve context, change an issue, call an API, or update a form definition, the team needs to know where that action is logged.
AWS is a useful benchmark here. AWS announced the [AWS MCP Server general availability](https://aws.amazon.com/about-aws/whats-new/2026/05/aws-mcp-server/) on May 6, 2026, describing IAM-based guardrails, Amazon CloudWatch metrics, and AWS CloudTrail logging. That does not make every AWS MCP use case automatically approved, but it does give enterprise teams a familiar evidence model.
### **What data crosses the boundary?**
Some MCP servers expose local files. Some expose SaaS data. Some connect to cloud accounts. Some connect to internal systems. Some domain-specific servers, such as the Form.io AI toolset, connect to a customer's self-hosted environment.
The boundary is the point.
Form.io describes its MCP Server as connecting to a customer's self-hosted Form.io deployment so AI coding agents can work with forms, resources, actions, and APIs without moving that governed surface outside the enterprise boundary. That is a different posture from a generic public directory listing.
### **Is this build-time or runtime?**
Do not collapse every agentic tool into one bucket.
MCP servers are usually build-time or operator-time connectors. They help coding agents and assistants read context, call tools, scaffold work, or interact with systems.
Runtime agent governance is different. Form.io's [Universal Agent Gateway](https://form.io/uag/) belongs in that adjacent category. UAG is not the same thing as the Form.io MCP Server. The MCP Server helps AI coding agents build against Form.io patterns. UAG governs production agent workflows at runtime.
Regulated teams need both concepts, but they should not confuse them.
## **The MCP servers worth knowing**
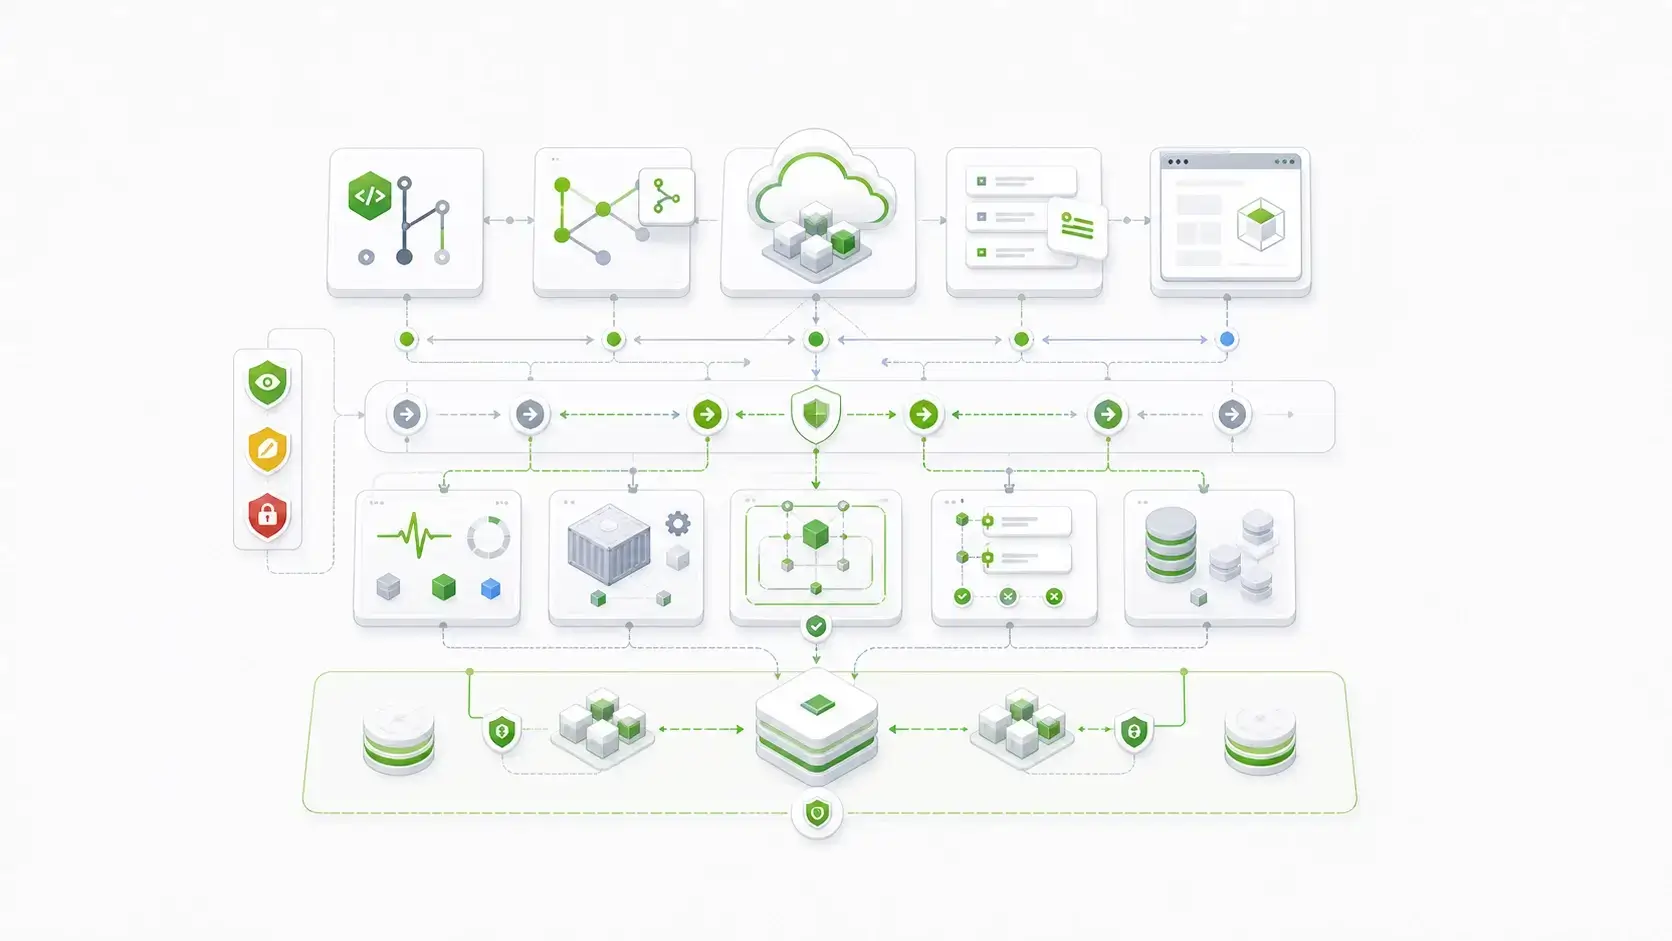### **1. Official MCP Registry**
Use the official registry as the starting point, not the finish line.
The [official registry](https://modelcontextprotocol.io/registry/about) is valuable because it gives teams a canonical discovery surface for public MCP servers. It supports server metadata, namespace authentication, REST API discovery, package references, and standardized installation information.
For enterprise teams, the important detail is the limit. The registry is public. It is still in preview. It is not where private enterprise servers should live. It also does not remove the need to review code, packages, transport, authentication, scopes, and data handling.
Use it to find servers. Do not use it as your approval workflow.
### **2. GitHub MCP Server**
The [GitHub MCP Server](https://github.com/github/github-mcp-server) belongs in many enterprise developer shortlists because GitHub is where source code, issues, pull requests, Actions, security findings, and review state already live for many teams.
That makes it powerful. It also makes it sensitive.
A coding agent that can inspect a repo, summarize issues, open a pull request, or reason over security findings is operating close to the SDLC evidence trail. That can be a good thing when the team scopes access properly. It can be a problem when every repo is available by default.
Use GitHub MCP when the agent needs to work inside the same development boundary developers already use. Scope it to the repositories and operations needed for the task.
### **3. GitLab MCP Server**
GitLab deserves its own place because many regulated organizations use self-managed GitLab or GitLab Dedicated rather than a purely public SaaS setup.
The official GitLab MCP documentation supports GitLab.com, Self-Managed, and Dedicated environments. It also warns that users are responsible for guarding against prompt injection and should use MCP tools only with trusted GitLab objects.
That warning is useful. It says the quiet part plainly: permission inheritance is not the whole security model. If an agent reads hostile issue content, merge request comments, or documentation, those objects can become part of the instruction stream.
Use GitLab MCP where GitLab is already the system of record for code and planning, but pair it with prompt-injection hygiene and object-scope limits.
### **4. AWS MCP Servers**
AWS MCP belongs in the list because cloud infrastructure is where agent mistakes become expensive.
AWS has multiple MCP surfaces, including [AWS Labs servers](https://github.com/awslabs/mcp/) and the generally available [AWS MCP Server](https://aws.amazon.com/blogs/aws/the-aws-mcp-server-is-now-generally-available/). The managed server is especially relevant to enterprise teams because AWS describes IAM guardrails, SigV4-style authenticated access through the Agent Toolkit, CloudWatch metrics, CloudTrail logging, AWS Knowledge MCP, AWS API MCP capabilities, and access to more than 15,000 AWS APIs.
That is exactly why the risk bar is high.
An agent that can ask AWS docs questions is one thing. An agent that can call AWS APIs is another. The minimum viable control is least-privilege IAM, environment separation, and CloudTrail visibility. Without those, cloud MCP access is too broad for regulated workflows.
Use AWS MCP for documentation, architecture support, and tightly scoped operations. Do not give a general coding agent broad cloud authority just because the server exists.
### **5. Azure MCP Server**
Azure MCP is important for teams whose cloud control plane already sits under Microsoft identity.
Microsoft's Azure MCP Server documentation describes integration with Azure resources, developer tools such as VS Code and GitHub Copilot, and authentication through Azure Identity. For enterprise teams, the key phrase is not "Azure resources." It is identity inheritance.
If the server can operate through Entra ID-backed access patterns and the same Azure permissions teams already govern, it fits better than a standalone connector with its own unmanaged secrets.
Use Azure MCP where the team already has mature Azure role design, environment separation, and resource governance.
### **6. Atlassian Rovo MCP Server**
Jira and Confluence are where a lot of enterprise work actually lives: requirements, tickets, runbooks, decisions, incident notes, acceptance criteria, and stakeholder context.
Atlassian's Rovo MCP Server documentation describes OAuth 2.1, support for Jira, Confluence, and Compass, permission inheritance, and IP allowlisting behavior in Atlassian Cloud.
That makes it a strong context server, especially for coding agents that need product intent or implementation history.
The risk is also obvious. Tickets and docs often contain sensitive business context, customer details, credentials copied where they should not be, and architectural notes. Permission inheritance helps, but it does not classify the content for you.
Use Atlassian MCP for project and documentation context, with clear limits on what spaces, projects, and user scopes are exposed.
### **7. Playwright MCP**
Playwright MCP is one of the most useful developer servers because it gives agents a structured way to interact with web pages and browser workflows.
The [Playwright MCP docs](https://playwright.dev/docs/getting-started-mcp) describe use of accessibility snapshots rather than screenshots or pixel-based interaction. That is the right foundation for repeatable browser automation.
But the same documentation also warns that direct Playwright code execution is effectively remote code execution and should only be enabled for trusted MCP clients.
That is the regulated-enterprise lesson in miniature. A tool can be both useful and unsafe if enabled in the wrong mode.
Use Playwright MCP for testing, QA, browser workflows, and UI validation. Disable unsafe direct-code tools unless the client and execution environment are trusted.
### **8. Sentry MCP**
The [Sentry MCP Server](https://github.com/getsentry/sentry-mcp) belongs in the operational layer. It helps agents inspect errors, traces, issues, and debugging context.
That can compress the time between "the build failed" and "the actual production error is understood." It also exposes operational data that may include request context, user metadata, stack traces, and environment details.
For regulated teams, observability MCP should be scoped like production support access, not like a convenience plugin.
Use Sentry MCP when the agent is doing debugging or remediation work, and restrict the projects, environments, and data fields that should be visible.
### **9. Docker MCP tooling**
[Docker's MCP tooling](https://docs.docker.com/reference/cli/docker/mcp/) is less about one business system and more about packaging, gateway behavior, and local developer operations.
That makes it useful for standardization. Enterprise teams do not want every developer hand-rolling MCP server installation and transport decisions in a different local config file.
Use Docker MCP tooling to make server setup more repeatable, especially when you need a catalog or gateway-style operating model across teams.
### **10. Form.io MCP Server**
Form.io belongs in this MCP server list because regulated applications often begin at the data-capture layer: forms, resources, validation rules, submission records, workflow actions, APIs, permissions, revisions, and audit evidence.
That is the layer where generic coding agents can create drift fastest.
One team builds a React form. Another builds a different submission API. A third adds an agent workflow. Each piece works. None of them share the same governance contract.
The [Form.io AI toolset](https://form.io/ai/) exists to push the agent toward the governed path at build time. The Form.io MCP Server connects AI coding agents to a customer's self-hosted Form.io deployment so they can read, create, and scaffold forms, resources, actions, and APIs from the same platform primitives. Form.io Skills guide the agent toward platform-specific patterns. The Agentic Coding Plugin brings that MCP Server and skill library into the developer's coding environment.
That makes Form.io different from a generic connector.
It is not just giving an agent another data source. It is giving the agent a governed application primitive: schemas that can produce interfaces, APIs, validation behavior, submissions, permissions, and workflow hooks from the same definition.
For teams using Form.io as [schema-driven application infrastructure](https://form.io/platform/), this is the right kind of MCP server: one that makes the governed path easier than building around it.
That value shows up in customer language too. In a [Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/), a long-time Form.io platform user put it plainly: "Form.io cleans up all the dirty work and does it for you." The surrounding case study frames that value as months of development time saved on a next-generation application launch.
## **How to decide what belongs in your agent context**
The fastest way to create MCP sprawl is to install every useful server globally.
Do not do that.
Treat MCP servers like permissions. Most should be project-specific, task-specific, or environment-specific.
Use this sequence:
1. Start with read-only discovery.
2. Prefer official or vendor-maintained servers.
3. Scope by project, repo, workspace, tenant, or environment.
4. Keep mutation tools disabled until the workflow needs them.
5. Separate local development access from production access.
6. Route secrets through existing identity systems where possible.
7. Log agent actions in the system of record.
8. Review prompt-injection exposure when the server reads user-authored content.
9. Revoke unused servers.
That may sound slower than "install the top 20 MCP servers." It is not slower when you count remediation.
A regulated team that cannot explain which server had which permission at which point in a workflow does not have an MCP strategy. It has a collection of shortcuts.
## **Why domain-specific MCP matters**
Generic MCP servers are good at giving agents access to tools. Domain-specific MCP servers are better when the agent needs to create governed artifacts.
That difference is especially important for forms and workflow data.
A generic file server can read a schema file. A GitHub server can modify code. A browser server can test a form. None of those, by itself, tells the agent what a valid governed form workflow should look like inside the enterprise.
Form.io's MCP Server does.
The reason is architectural. Form.io is not only a form renderer. Its [drag-and-drop form builder and API model](https://form.io/features/drag-and-drop-form-builder-apis/) treats form definitions as JSON-backed application infrastructure. Forms can produce APIs. Submission data is managed separately from Form JSON. Form revisions and submission management matter because historical state and current state are not always the same thing.
That is why the Form.io MCP Server matters for regulated developers. It helps the coding agent build with the same primitives the platform governs: forms, resources, actions, APIs, roles, group permissions, server-side actions, [form revision history](https://form.io/features/form-revisions-form-json-schema/), and [complete audit trails](https://form.io/features/log-forms-complete-audit-trail/).
That does not mean Form.io replaces GitHub, GitLab, AWS, Azure, Playwright, Sentry, or Atlassian. It means Form.io occupies a different layer: the form and workflow infrastructure layer where business data enters the system and becomes governed submission state.
## **What proof should enterprise teams look for?**
Popularity is weak proof.
Stars, upvotes, and directory rank tell you that a server is visible. They do not tell you whether the server is appropriate for regulated work.
Better proof looks like this:
- Official or vendor-maintained source.
- Clear authentication model.
- Clear transport model.
- Least-privilege configuration.
- Permission inheritance from the system of record.
- Audit logging for meaningful actions.
- Environment separation.
- Versioned releases.
- Security guidance.
- Support for private or self-managed deployment where needed.
The production-readiness gap is real. A [2026 research paper on production MCP](https://arxiv.org/abs/2603.13417) reports more than 10,000 active MCP servers and 97 million monthly SDK downloads, while also arguing that production MCP still needs stronger identity propagation, adaptive tool budgeting, structured error semantics, and observability.
That is the point. MCP adoption is moving faster than MCP governance.
The answer is not to wait. The answer is to be precise.
Use servers that inherit controls you already trust. Scope them narrowly. Prefer domain-specific servers when the agent is creating governed artifacts. Treat runtime agent governance as a separate layer from coding-time MCP.
## **Key takeaways**
- An MCP server list helps you discover options, but it does not approve them for regulated use.
- Official and vendor-maintained servers should carry more weight than generic directory entries.
- Evaluate each server by identity, permissions, audit evidence, transport, data boundary, and mutation risk.
- GitHub, GitLab, AWS, Azure, Atlassian, Playwright, Sentry, Docker, and Form.io each occupy different control surfaces.
- Form.io's MCP Server is a build-time path into governed form and API infrastructure; UAG is the separate runtime governance layer.
## **FAQ**
### **What is an MCP server list?**
An MCP server list is a directory, registry, repository, or article that helps developers find Model Context Protocol servers. The best starting point is the official MCP Registry, but regulated teams should treat any list as discovery rather than approval.
### **What is the safest way to find MCP servers?**
Start with official sources: the official MCP Registry, vendor documentation, vendor-maintained GitHub repositories, and your own internal registry for private servers. Avoid installing servers only because they appear in a public directory or social post.
### **Are MCP servers secure?**
MCP servers are not automatically secure or unsafe. Security depends on the server's code, maintainer, transport, authentication model, tool scope, permissions, data access, and execution environment. The MCP security guidance specifically calls out risks such as confused deputy behavior, token passthrough, SSRF, session hijacking, local compromise, and scope minimization.
### **Should regulated teams use community MCP servers?**
Sometimes, but not casually. A community server can be useful for low-risk local workflows, prototypes, or read-only tasks. For sensitive systems, prefer official or vendor-maintained servers, or run an internal review before adding the server to an enterprise agent environment.
### **Which MCP servers are best for developers?**
A practical regulated-enterprise list usually starts with GitHub or GitLab for SDLC work, Playwright for browser testing, AWS or Azure for cloud workflows, Atlassian for ticket and documentation context, Sentry for debugging, Docker for packaging and gateway patterns, and Form.io for governed form/API infrastructure.
### **What is the difference between an MCP registry and an MCP server?**
An MCP registry helps you discover servers and their metadata. An MCP server is the actual connector that exposes tools, data, or actions to an MCP client. A registry is not a security review, and it does not mean the server is safe for your environment.
### **How does Form.io fit into an MCP server list?**
Form.io fits when the agent needs to work with governed form and workflow infrastructure. The Form.io MCP Server gives AI coding agents access to Form.io forms, resources, actions, and APIs inside the customer's deployment boundary, while Form.io Skills guide the agent toward platform-specific implementation patterns.
### **Is Form.io UAG an MCP server?**
No. Form.io's MCP Server is build-time infrastructure for AI coding agents. UAG is runtime governance for production agent workflows. They belong in the same agentic architecture conversation, but they are not the same component.
### **Should MCP servers be installed globally?**
Usually no. Global installation encourages overbroad access. Regulated teams should scope MCP servers by project, workspace, environment, repository, tenant, or task. Mutation tools should be enabled only when the workflow requires them.
### **What should an enterprise MCP policy include?**
At minimum, it should define approved server sources, identity requirements, permission scopes, logging expectations, data-boundary rules, prompt-injection handling, environment separation, and a removal process for unused or deprecated servers.
### **When should a team build its own MCP server?**
Build your own MCP server when the system is internal, private, highly regulated, domain-specific, or poorly represented by public servers. Private systems should not be forced into public registries just to make them usable by agents.
## **Build Governed Form And API Workflows With Form.io**
If your team needs AI coding agents to build against governed forms, generated APIs, submission records, permissions, revisions, and self-hosted infrastructure, [try Form.io for governed form and API workflows](/try-formio-for-free/).
---
# AI Governance Platform: Agentic Workflow Governance Layers Compared
*Published:* 2026-06-05
*Author:* Veronika Druck
*URL:* https://form.io/ai-governance-platform-agentic-workflow-governance-layers-compared/
*Description:* A comparison of AI governance platform layers for enterprise agentic workflows, explaining model governance, runtime agent governance, process orchestration, and schema-driven Form.io UAG governance.
AI governance platform searches hide several different problems under one phrase. A policy registry is not runtime tool-call control. A process engine is not schema-driven data access. If agents can read data, invoke tools, submit records, and trigger workflows, governance has to live where the agent acts. This comparison names the layer before judging the tool.
## **The AI Governance Gap Is Now Operational**
Most AI governance conversations started with model risk, policy documentation, and compliance review. Those still matter.
But agentic workflows add a sharper question: what happens when the AI system can do something?
Grant Thornton's 2026 AI Impact Survey found that 78% of senior business leaders lacked full confidence that their organization could pass an independent AI governance audit within 90 days. The same survey said 46% of leaders believed AI underperformed because controls and compliance were not working ([Grant Thornton](https://www.grantthornton.com/insights/press-releases/2026/april/grant-thornton-survey-on-ai-proof-gap)).
That is not just a board-level policy problem. It is an infrastructure problem.
Gartner's 2025 strategic technology trends report predicted that by 2028, at least 15% of day-to-day work decisions would be made autonomously through agentic AI, up from 0% in 2024 ([Gartner](https://www.gartner.com/en/newsroom/press-releases/2024-10-21-gartner-identifies-the-top-10-strategic-technology-trends-for-2025)). If even a small share of ordinary operational decisions moves through agents, governance has to follow the action, not only the policy record.
If an agent can approve a request, update a record, route a case, draft a decision, trigger an integration, or submit structured data into a system of record, the organization needs more than a governance statement. It needs an execution path that can answer:
- What was the agent allowed to do?
- Which identity or role gave it that permission?
- What schema, validation rule, or process state constrained the action?
- Was a human required to approve it?
- What audit evidence exists after the action?
An AI governance platform can help with policy, inventory, and risk. An agentic workflow needs that, plus runtime controls at the exact layer where the agent touches the business system.
## **Five Governance Layers To Compare**
The phrase "AI governance platform" is too broad unless you name the layer.
For agentic workflows, the main layers are:
**Governance layer****What it governs****Example fit**AI policy and risk governanceAI inventory, use cases, risk tiering, compliance evidence, board reportingCredo AI, OneTrust, IBM watsonx.governance, classic GRC-style AI governance suitesRuntime agent governanceTool calls, resource access, inter-agent messages, action-level policy enforcementMicrosoft Agent Governance ToolkitProcess orchestration governanceBPMN, case state, human tasks, SLAs, process audit trails, exception handlingCamunda 8.9, Flowable 2025.1, Appian process workflowsPlatform-native agent governanceAgents built and managed inside a specific app/process platformAppian Agent StudioSchema/API/data-access governanceThe forms, fields, validation rules, submissions, APIs, roles, and actions an agent uses to do workForm.io Universal Agent GatewayThese layers can overlap. They can also coexist.
A bank might use Microsoft Entra for agent identities, Microsoft Agent Governance Toolkit for action-level policy, Camunda for cross-system process orchestration, and Form.io UAG for governed access to intake forms, validation, submissions, and downstream workflow actions.
The mistake is treating those as interchangeable.
## **Quick Comparison**
## **Platform or toolkit****Governance center of gravity****Strongest fit****Watch the boundary**Form.io UAGSchema, form, API, submission, RBAC, and action governance exposed to agents through MCPAgents that need governed access to forms, submissions, validation, and workflow infrastructureNot a generic AI GRC dashboard or full BPMN engineAppian Agent StudioAgents embedded inside Appian's process/application platformTeams already building workflows in AppianStrong inside Appian's platform boundary; less about portable schema/API ownershipCamunda 8.9BPMN-based agentic orchestration, human tasks, process state, audit logs, MCP/A2ATeams that govern work through explicit process modelsGovernance starts at orchestration; the data-capture/schema layer may still live elsewhereFlowable 2025.1Agent engine beside BPMN/CMMN/DMN, agent exchange tracking, case/process controlDynamic case work and process automation with first-class agentsStrong process layer; still needs source-of-truth data contractsMicrosoft AGTRuntime policy enforcement, identity, sandboxing, OWASP agentic risk controlsDevelopers adding action-level governance to agent frameworksA toolkit, not a business workflow or forms infrastructure platform**Form.io UAG: When The Governed Schema Should Become Agent Context**
Form.io's Universal Agent Gateway is strongest when the agent has to operate through a governed form and workflow layer instead of a loose collection of prompts, tools, and credentials.
Form.io's core argument starts below the agent. In Form.io, Form JSON is the schema created by the form builder. The Form.io documentation says that schema is used to render forms inside applications, generate REST API interfaces on the server, and host the form schema at the embed URL ([Form.io Form JSON documentation](https://help.form.io/userguide/forms/form-building/form-json)).
That matters because an agent needs structured context.
An agent does not need a vague prompt saying "collect the right onboarding details." It needs to know which fields exist, which fields are required, what validation rules apply, how submissions are shaped, which actions can run, and what permissions apply to the current actor.
Form.io UAG turns that existing application infrastructure into the agent surface. The UAG page explains that agents can authenticate through existing Form.io auth and SSO, inherit enterprise RBAC, retrieve and route secure data inside the private network, and execute actions governed by Form.io Actions and audit trails ([Form.io UAG](https://form.io/uag/)).
That is a specific kind of governance. It is not "AI governance" as a board dashboard. It is governance at the layer where forms, APIs, submissions, validation, and workflow actions already meet.
This is why Form.io should not be framed as simply another AI agent platform. Form.io's AI page describes UAG as the runtime governance layer for production agentic workflows, while the MCP Server, Skills, and Agentic Coding Plugin support build-time development ([Form.io AI](https://form.io/ai/)). That separation is important. Build-time agents need patterns for creating software. Runtime agents need permissioned, logged access to production workflow surfaces.
The customer proof is not AI-specific yet, so it should be used carefully. But it does show why this infrastructure layer matters. In one Form.io public-sector case study, publicplan supported more than 400 digital public-sector services and 1,000+ forms while meeting strict standards and a short timeline ([Form.io publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)). In another Form.io banking case study, an international banking deployment served 5,000 banking groups and recovered 50% of the team's capacity ([Form.io banking case study](https://form.io/case-studies/how-many-technologies-can-actually-support-the-business-process-transformation-of-serving-5000-banking-groups/)).
Those are not UAG deployment claims. They are infrastructure claims. They show why a governed forms/API/submission layer is valuable before agents arrive. UAG extends that same layer to agents.
### **Strongest Fit**
Form.io UAG is the strongest fit when:
- forms are part of the application contract, not just hosted collection pages
- agents need to understand field structure, validation rules, submission shape, and workflow actions
- the customer needs self-hosted or private-network control
- RBAC, auth, audit trails, and form revisions are already part of the governance model
- the team wants humans and agents operating through the same governed schema layer
Form.io is not the right answer if the buyer only needs a general AI policy registry. It is the right answer when the agent's work touches form-driven application infrastructure.
## **Appian Agent Studio: When Agents Belong Inside The Appian Process Platform**
Appian's governance story is platform-native.
Agent Studio is built for teams that already use Appian to design applications, workflows, data fabric patterns, and enterprise processes. Appian's 25.4 release material frames Agent Studio as a guided way to create enterprise AI agents and drag them into business processes. Appian also says agents embedded in processes can use guardrails, tools, data, and human review inside the process context (Appian Agent Studio release material).
That is a clear fit when Appian is already the process application platform.
The governance center is not the open schema/API layer. It is the Appian platform boundary. Agents live inside the Appian design and process model, use Appian objects and tools, and inherit governance from the Appian environment.
That can be exactly what an Appian customer wants. It is less compelling when a team needs agent access to application-owned forms, APIs, validation rules, submissions, and deployment boundaries outside Appian.
### **Strongest Fit**
Appian Agent Studio fits when:
- the business process already lives in Appian
- low-code process design is the center of gravity
- agents need to operate inside Appian's app/process/data fabric layer
- the organization wants human review and process guardrails inside the same platform
The Form.io contrast is not "Appian cannot govern agents." It can govern them inside its platform. The Form.io distinction is that governance starts at the schema and form infrastructure layer agents use to collect, validate, submit, and route data.
## **Camunda 8.9: When BPMN Orchestration Is The Governance Backbone**
Camunda approaches agentic governance from the process orchestration layer.
In its 8.9 release, Camunda frames agentic orchestration as coordinating AI agents, knowledge workers, tools, and systems across end-to-end business processes. The release emphasizes deterministic process logic, global user task listeners, centralized audit logs, MCP access to running clusters, and A2A support for multi-agent communication (Camunda 8.9 release material).
That is a strong governance story for teams that already model work as BPMN.
The useful distinction is this: Camunda governs the flow of work. It controls process state, human tasks, incidents, retries, escalation, and the audit trail around the process. That is different from governing the form schema, validation logic, submission payload, or field-level context an agent uses before it reaches a process step.
In many architectures, both layers matter.
A government service workflow might use Form.io to collect and validate service request data through self-hosted forms and generated APIs, then use Camunda to orchestrate downstream case routing, approvals, exceptions, and cross-system work. The agent should respect both layers.
### **Strongest Fit**
Camunda fits when:
- BPMN is already the operating language for process governance
- the organization needs explicit process state and incident handling
- agents participate in workflows with human tasks and deterministic rules
- auditability needs to follow the end-to-end process path
Form.io fits earlier in the path: where the agent needs governed access to the structured data, forms, validation rules, and APIs that feed the process.
## **Flowable 2025.1: When Case And Process Work Need First-Class Agents**
Flowable's 2025.1 release puts agents beside BPMN and CMMN rather than treating them as external helpers.
Flowable says the release adds an agent engine alongside its BPMN and CMMN automation engines, with internal agent types such as utility, document, knowledge, and orchestrator agents. It also describes agent exchange tracking as a way to store AI interactions for traceability and audit support (Flowable 2025.1 release material).
That makes Flowable a serious process/case governance comparison.
Its strongest fit is dynamic work: cases, documents, human judgment, process variation, and AI-assisted decisions that need to stay inside a process/case model. If a case state determines what an agent can and cannot do, Flowable's governance center makes sense.
The Form.io distinction is again layer ownership.
Flowable can govern the case or process. Form.io can govern the structured form and submission layer that feeds the case. In agentic workflows, those are connected but not identical.
### **Strongest Fit**
Flowable fits when:
- work is case-heavy and may not follow one fixed process path
- AI agents need to operate inside CMMN/BPMN-style orchestration
- traceability of agent exchanges matters
- the organization wants an agent engine inside the process platform
Form.io fits when the agent's most important constraint is the governed schema, validation, permission, submission, and action surface around data intake and form-driven workflows.
## **Microsoft Agent Governance Toolkit: When Developers Need Runtime Action Controls**
Microsoft Agent Governance Toolkit is the most developer-centered entry in this comparison.
Microsoft introduced AGT as an open-source runtime security governance project for autonomous AI agents. The announcement says the toolkit is designed to work with existing frameworks and includes deterministic policy enforcement, identity, sandboxing, reliability controls, and mapping to OWASP agentic AI risks ([Microsoft open-source announcement](https://opensource.microsoft.com/blog/2026/04/02/introducing-the-agent-governance-toolkit-open-source-runtime-security-for-ai-agents/)).
That layer matters because agents can misuse tools even when the surrounding workflow looks well designed.
Microsoft's later Agent Framework guidance makes the layer even clearer: Agent Framework handles build and orchestration, while Agent Governance Toolkit handles govern and audit. It evaluates tool calls, resource access, and inter-agent messages against policy before execution ([Microsoft Agent Framework and AGT](https://devblogs.microsoft.com/agent-framework/governance-at-the-speed-of-agents-microsoft-agent-framework-and-agent-governance-toolkit-better-together/)).
That is not the same job as Form.io UAG.
AGT helps govern the agent's actions at runtime. Form.io UAG gives agents governed access to Form.io's form, submission, schema, API, RBAC, and action layer. In some architectures, AGT could sit beside or around an agent framework, while UAG provides the business-specific tools and context the agent is allowed to use.
### **Strongest Fit**
Microsoft AGT fits when:
- developers need action-level policy checks inside an agent framework
- tool-call misuse, goal hijacking, rogue agents, or inter-agent trust are the main concern
- the team wants an open-source runtime governance toolkit
- the application/workflow platform is already chosen elsewhere
Form.io fits when the agent needs a governed business surface for form-driven work, not only a policy wrapper around tool calls.
## **How To Choose The Right Governance Layer**
The useful question is not "which AI governance platform should we buy?"
The useful question is: where can the agent create the most risk?
### **If The Risk Is AI Inventory And Compliance Evidence**
Start with a classic AI governance platform.
This is the layer for model inventory, use-case approvals, risk tiers, policy mapping, regulatory documentation, monitoring, and executive accountability. It matters most when the organization cannot answer which AI systems exist, who owns them, what risk category they fall into, or what evidence supports approval.
Form.io does not replace that layer.
### **If The Risk Is Tool-Call Misuse**
Look at runtime agent governance.
This is where Microsoft Agent Governance Toolkit is relevant. It helps evaluate actions before execution and provides runtime security controls for autonomous agent frameworks.
Form.io can supply governed business tools and context; AGT can help enforce broader action-layer policies.
### **If The Risk Is Process Visibility**
Look at process orchestration.
Camunda, Flowable, and Appian are stronger when the work has to be governed as a process or case: state, sequence, incidents, handoffs, human review, SLAs, escalation, and full process auditability.
Form.io can still matter if the workflow starts with governed forms, submissions, and APIs.
### **If The Risk Is Data, Schema, And API Drift**
This is where Form.io belongs.
If humans use one form definition, APIs use another contract, agents use a prompt-based tool description, and workflow actions use yet another set of assumptions, governance will drift. The agent may still complete the task. The organization may not be able to prove that the task followed the governed path.
Form.io's stronger argument is that the same Form JSON and platform layer can define the form, the validation, the generated API surface, the submission shape, permissions, and the runtime agent context.
That starts with deployment control. A [self-hosted Form.io](https://form.io/features/self-hosted-forms-for-enterprise/) environment lets the form and submission layer live inside the customer's own infrastructure boundary.
It also starts with the form contract itself. The [drag-and-drop form builder with APIs](https://form.io/features/drag-and-drop-form-builder-apis/) is not only a visual authoring surface; it produces structured definitions that can become application interfaces.
Governance then depends on behavior, not just fields. [Conditional logic and validation](https://form.io/features/form-conditional-logic-form-validation/) help define what data is acceptable before a workflow or agent acts on it.
Finally, the work has to map to people and roles. [Teams and permissions](https://form.io/features/forms-for-teams/) belong in the same architecture conversation because agent access should inherit the same governance model that controls human access.
## **Where Form.io Fits**
Form.io is not trying to be every layer of AI governance.
That is a strength, not a weakness.
Form.io is strongest when forms are application infrastructure: the schema, user interface, generated API, validation model, submission record, permission boundary, and workflow trigger are connected. When agents enter that environment, the agent should not get a separate shadow contract. It should operate through the same governed layer as the application.
That is the UAG argument.
If your organization only needs an AI policy dashboard, choose an AI governance suite. If it needs action-level runtime policy enforcement across agent frameworks, evaluate a toolkit like Microsoft AGT. If it needs process orchestration, evaluate Camunda, Flowable, or Appian.
If the agent needs governed access to forms, fields, submissions, APIs, validation rules, permissions, and workflow actions inside a customer-controlled deployment, Form.io should be in the conversation.
## **Key Takeaways**
- AI governance platform is too broad unless you name the layer.
- Agentic workflows need governance where agents act, not only where policies are documented.
- Form.io UAG governs the schema/API/form/submission/action layer for production agents.
- Appian, Camunda, and Flowable govern agents through process or case platforms.
- Microsoft AGT governs runtime tool calls and action policies.
- The strongest architecture can combine layers instead of forcing one product to do every job.
- Form.io's strongest claim is not generic AI governance. It is governed application infrastructure for agents working through forms, APIs, validation, submissions, permissions, and actions.
## **FAQ**
### **What Is An AI Governance Platform?**
An AI governance platform helps organizations manage AI risk, policy, accountability, compliance evidence, monitoring, and operational controls. In classic enterprise usage, it often includes AI inventory, use-case approvals, risk classification, policy mapping, audit evidence, and reporting.
For agentic workflows, the term needs more precision. A platform that governs model risk is not automatically the same as a tool that governs agent actions, process state, form submissions, or API access.
### **What Is Agentic Workflow Governance?**
Agentic workflow governance is the set of controls that determines what an AI agent can do inside a business process. It covers tool access, data access, identity, permissions, validation, human review, logging, audit trails, exception handling, and policy enforcement.
The key difference is action. A chatbot that answers a question needs content safety. An agent that updates a submission or triggers a workflow needs execution governance.
### **Is Form.io UAG An AI Governance Platform?**
Form.io UAG is most accurately understood as a runtime governance layer for agents operating through Form.io infrastructure. It is not a general AI GRC dashboard.
UAG gives agents governed access to the Form.io layer: forms, field definitions, validation, submissions, actions, auth, RBAC, and application workflow context. That makes it highly relevant to agentic workflow governance, especially when forms and APIs are part of the customer-controlled application stack.
### **How Is Form.io UAG Different From Microsoft Agent Governance Toolkit?**
Microsoft Agent Governance Toolkit focuses on runtime policy enforcement for agent actions: tool calls, resource access, identity, sandboxing, and auditability around the agent framework.
Form.io UAG focuses on the business surface the agent uses when work involves forms, submissions, validation, APIs, and workflow actions. AGT can help govern the agent's behavior. UAG gives the agent a governed Form.io context to operate through.
### **How Is Form.io UAG Different From Process Engines?**
Process engines such as Camunda and Flowable govern processes and cases. They are strong when the main governance problem is end-to-end orchestration: state, sequence, human tasks, incidents, escalation, and process audit trails.
Form.io governs the form and data infrastructure layer. It is stronger when the main governance problem is schema, validation, submissions, permissions, APIs, and form-driven workflow actions. Many enterprise architectures can use both layers.
### **When Should A Team Use A Classic AI Governance Suite Instead?**
Use a classic AI governance suite when the main problem is enterprise oversight: AI inventory, use-case approvals, risk scoring, regulatory mapping, model monitoring, audit evidence, and board-level accountability.
Use Form.io UAG when the main problem is operational: agents need governed access to forms, submissions, validation, APIs, and workflow actions. The two layers can complement each other.
### **Why Does Schema Matter For Agent Governance?**
Agents need structured context. A schema tells the agent what fields exist, which data is required, what validation rules apply, how submissions are shaped, and which actions are meaningful.
When the same schema drives human forms, APIs, validation, and agent context, the organization reduces drift. The agent is less likely to operate from stale prompt instructions or a parallel tool definition that no longer matches the application.
### **Can Form.io Replace A Process Engine?**
No. Form.io should not be framed as a full process engine replacement.
Form.io is infrastructure for forms, APIs, submissions, validation, permissions, and workflow-related actions. If the organization needs full BPMN or case orchestration, a process engine may still be appropriate. Form.io's role is to make the form and data capture layer governed enough for humans, developers, systems, and agents to use safely.
## **Build Governed Agentic Workflows With Form.io**
If your agents need to work through forms, submissions, APIs, validation rules, permissions, and workflow actions inside your own deployment boundary, start with the governed infrastructure layer.
[Try Form.io for governed agentic workflow infrastructure](/try-formio-for-free/).
---
# Best MCP Servers for Enterprise Forms and Workflows
*Published:* 2026-05-07
*Author:* Veronika Druck
*URL:* https://form.io/best-mcp-servers-formio-uag-ranked/
*Description:* Explains how to evaluate the best MCP servers for developer workflows and governed enterprise forms, showing why Form.io UAG matters when agents need schema, RBAC, validation, submissions, and auditability.
If you’re building forms inside Claude Code, Cursor, Windsurf, or another agentic coding environment, the question is not whether to use MCP. It is which MCP server does the job you actually have.
That distinction matters because most “forms for AI” tools are solving different problems. Some manage a hosted form account. Some only read existing forms. Some route through middleware. Some help developers build. Others try to expose runtime workflows.
Those are not the same surface.
This guide ranks **dev-time MCP servers for forms**: the servers a developer points a coding agent at to generate, modify, validate, or inspect form infrastructure during application development. It also explains where **runtime UAG** fits, because production agents need a different governance layer after the form ships.
## Two surfaces, not one
A form MCP can have two possible jobs.
**Dev-time MCP** helps a developer build. A developer working in Claude Code, Cursor, Windsurf, or another coding environment asks an agent to generate or modify a form. The agent calls an MCP server, receives schema and tool context, and helps create or update assets the application owns. This is a build-time surface. It should be opinionated about schema, useful inside the IDE, compatible with source control, and safe enough not to damage existing production forms.
**Runtime UAG** helps an agent operate. A production agent executes a workflow that includes form logic: routing, validation, submission handling, data capture, approvals, or updates inside the application’s actual governance envelope. This is the runtime surface. It should inherit the auth, RBAC, validation, audit patterns, revision control, and deployment boundaries of the system around it.
A dev-time MCP that pretends to be a runtime governance layer is dangerous. A runtime gateway that pretends to be a developer tooling surface is awkward. They have different users, trust boundaries, and architectural requirements.
This is where the recent schema-driven application infrastructure argument matters. In regulated environments, the core problem is not just form creation speed. The problem is governance drift. AI-assisted developers can generate applications faster than governance teams can review them, and runtime agents can act inside workflows faster than auditors can sample them. The white paper’s answer is a governed, JSON-based schema as the source of truth for forms, APIs, validation, human interfaces, and agentic context.
That is why dev-time and runtime both matter. Build-time agents should create against the governed schema pattern. Runtime agents should operate through the governed schema surface. The easy path and the governed path need to be the same path.
Formio is the only entry in this forms ranking that currently has both surfaces as distinct products: a dev-time MCP server for developers building forms, and Universal Agent Gateway (UAG) for runtime agentic workflows. UAG does not belong inside the dev-time ranking as though it were the same product. Its existence is still important because it answers the question most form MCP comparisons avoid: what happens after the form ships?
## The ranking
1. **Formio dev-time MCP server** — vendor-maintained, open-source, self-hostable, full form CRUD, and paired with a separate runtime governance surface.
2. **Jotform MCP** — hosted, OAuth-based, vendor-maintained, useful for managing forms inside a Jotform account.
3. **Tally MCP** — hosted, OAuth/API-key based, beta, useful for lightweight form creation and submission access.
4. **Typeform MCP** — vendor-maintained beta with limited form read access and contact write access.
5. **Retool MCP for the forms path** — official but read-focused; useful for inspecting Retool orgs, not a forms-first schema layer.
6. **n8n MCP Server Trigger** — flexible workflow exposure, self-hostable, but not form-native.
7. **Zapier MCP / Pipedream MCP gateways** — broad middleware access to many app APIs, but not vendor-native form infrastructure.
The short version: if your team is building form-driven application infrastructure, Formio is the strongest fit. If your team is managing forms inside an existing SaaS form account, Jotform or Tally may be enough. If your team needs generic workflow automation, n8n, Zapier, or Pipedream can help, but they are not form-native MCP servers.
## The criteria that matter
MCP is an open standard for connecting AI applications to external systems, tools, data sources, and workflows ([Model Context Protocol docs](https://modelcontextprotocol.io/docs/getting-started/intro)). Anthropic introduced MCP as a way to replace fragmented one-off integrations with a standard method for connecting AI assistants to systems where data lives, including content repositories, business tools, and development environments ([Anthropic](https://www.anthropic.com/news/model-context-protocol)).
That standard matters. But for forms, the standard connection layer is only the beginning. A dev-time form MCP has to answer six harder questions.
### 1. Can the AI generate and modify forms, or only read them?
Read-only MCP servers are useful for inspection. They are not enough for developers building applications.
A coding agent needs to create forms, update forms, inspect schema, validate components, and avoid destructive changes to existing assets. If a server can only list forms or fetch submissions, it may be a helpful assistant for account management, but it is not a serious dev-time form-building surface.
### 2. What schema is underneath?
For application infrastructure, schema portability matters.
A proprietary form JSON object may work well inside one hosted product. It becomes a constraint when the application needs to own its forms, APIs, submissions, validation rules, and workflow behavior over time.
Formio’s advantage is not merely that forms are represented as JSON. The stronger distinction is the atomic component model: one JSON object can carry structure, validation, conditional logic, calculated values, rendering intent, and labeling intent together. That keeps shape and behavior closer to the same contract, instead of forcing teams to rebuild behavior in separate code paths.
### 3. Can you self-host?
Hosted-only MCP servers route form definitions, submissions, and tool calls through vendor infrastructure. That may be fine for a lightweight marketing form. It can be a non-starter for healthcare, public sector, financial services, or air-gapped environments.
Teams already evaluating [self-hosted Formio](https://form.io/features/self-hosted-forms-for-enterprise/) usually ask the right question: can this run inside the environment where the governed system already lives?
### 4. Is it vendor-maintained or community-built?
Community wrappers can be useful for experimentation. Production tooling needs a maintainer who understands the underlying product and its API changes.
For form workflows, this matters because a quiet schema change or permission change can break more than a demo. It can break the layer where structured data enters an application.
### 5. Does the vendor have a runtime answer?
A dev-time MCP helps create or modify forms. It does not automatically govern what production agents do after those forms are deployed.
That is why runtime matters as a separate criterion. If the vendor’s only answer is a build-time server, the burden of production agent governance shifts back to your application team. If the vendor has a distinct runtime surface, the architecture is at least acknowledging that production agents need different controls from coding agents.
### 6. Is it discoverable where developers search?
Developers find MCP servers in client registries, GitHub, Smithery, mcp.so, Glama, PulseMCP, vendor docs, and coding-tool setup guides. Distribution is not architecture, but it affects adoption.
A good server still needs to be easy for developers to find, install, configure, and verify.
## 1. Formio dev-time MCP server
**What it is.** Formio’s dev-time MCP server enables AI assistants to interact with Formio’s API to create, read, update, and manage forms using natural language. The public README lists tools for listing forms, retrieving form details, creating forms, updating forms, deleting forms, and building properly structured Formio components. It also includes safety guardrails so the MCP can modify only forms it created, protecting existing forms from accidental changes ([Formio MCP GitHub](https://github.com/fwextensions/formio-mcp)).
The server supports stdio transport for Claude Desktop-style clients and HTTP transport for HTTP-capable clients or remote access. It uses Formio project credentials through an API key or JWT token.
### Scorecard
CriterionFormio dev-time MCPRead + writeCreate, read, update, delete, and component-building toolsSchemaFormio JSON schema / schema-driven form infrastructureSelf-hostedYes, deployable by the customerVendor-maintainedYesRuntime answerYes — UAG, as a separate runtime productDirectory presenceGitHub now; broader directory distribution should be verified before publication### Why it is #1
Formio wins this ranking because it treats forms as application infrastructure, not just hosted assets in an account.
At dev time, the MCP server gives coding agents structured access to the forms layer: list forms, inspect schemas, create forms, update MCP-created forms, delete MCP-created forms, and build components. That is the right shape for Claude Code, Cursor, or Windsurf because the developer is still building the application.
The safety guardrail is also important. The README states that Formio MCP prepends `\[MCP\]` to form titles and `mcp-` to form paths for created forms, then rejects update or delete attempts against non-MCP forms. That is exactly the kind of boring constraint AI coding tools need. It prevents the agent from treating a real project like a sandbox.
The larger reason Formio ranks first is the dev-time/runtime separation. Formio’s MCP server is for building. UAG is for runtime agentic workflow execution. A vendor that ships both surfaces is making a stronger architectural claim than a vendor that ships one MCP endpoint and hopes it covers everything.
### Where it falls short
Distribution is the current weak spot. The server is available on GitHub and can be run with Formio project credentials, but directory presence should be checked before the final WordPress update. Developers searching inside specific MCP directories may not find it everywhere yet.
The article should also avoid pretending dev-time MCP automatically makes runtime workflows safe. It does not. Dev-time MCP helps build against the schema pattern. Runtime governance belongs to UAG and the surrounding Formio deployment, permissions, validation, and audit design.
### Best for
Developers building forms inside Claude Code, Cursor, Windsurf, or similar tools when the form is part of the application, not just a hosted object in a third-party form account.
It is especially relevant for teams that care about [embedded forms and APIs](https://form.io/features/drag-and-drop-form-builder-apis/), self-hosted deployment, governed submissions, and long-term schema ownership.
## 2. Jotform MCP
**What it is.** Jotform’s official MCP server exposes Jotform forms and submissions through a hosted endpoint at `https://mcp.jotform.com`. Jotform documents five standard tools: `form\_list`, `create\_form`, `edit\_form`, `create\_submission`, and `get\_submissions`. It uses OAuth and requires one-time approval for each user ([Jotform MCP docs](https://www.jotform.com/developers/mcp/)).
Jotform also documents an MCP App variant with interactive UI components for visual form building, previews, browsing forms, and working with submissions inside MCP-App-capable clients.
### Scorecard
CriterionJotform MCPRead + writeCreate/edit forms, create submissions, fetch submissionsSchemaJotform form modelSelf-hostedNo; local server capabilities are described as in development for enterpriseVendor-maintainedYesRuntime answerJotform-hosted form runtime, not a separate runtime agent governance layerDirectory presenceOfficial docs and hosted endpoint### Why it is #2
Jotform has one of the clearer vendor-maintained MCP stories in the category. OAuth is documented. The remote endpoint is simple. The five-tool surface covers the core account-management jobs most Jotform users will want from an AI assistant.
For teams already living inside Jotform, this is a reasonable on-ramp. The assistant can list forms, create a form, edit a form, create a submission, or fetch submissions without the team building a custom connector.
### Where it falls short
It is still a Jotform account-management surface. The application does not own the form infrastructure in the same way it would with a self-hosted schema-driven platform. The MCP server helps operate inside Jotform; it does not turn Jotform into an application-owned schema layer.
Jotform’s enterprise section mentions SSO, access control, higher rate limits, custom branding, and dedicated support. It also says local server capabilities are actively being developed. That is useful, but it is not the same as a current self-hosted dev-time plus runtime governance architecture.
### Best for
Teams already using Jotform who want AI-assisted form management and submission access. It is not the strongest foundation for form-driven applications that need to live inside the customer’s own infrastructure.
## 3. Tally MCP
**What it is.** Tally’s MCP server is a hosted beta server at `https://api.tally.so/mcp`. The docs say it can build Tally forms, retrieve forms, and fetch submissions using natural language through assistants like Claude. Tally supports OAuth and API-key authentication, with setup examples for Claude Desktop, Claude Code, and Cursor ([Tally MCP docs](https://developers.tally.so/api-reference/mcp)).
### Scorecard
CriterionTally MCPRead + writeCreate and update forms, list forms, fetch submissionsSchemaTally form modelSelf-hostedNoVendor-maintainedYes, betaRuntime answerNone beyond the Tally hosted productDirectory presenceOfficial docs and Claude/Cursor setup examples### Why it is #3
Tally is credible for lightweight form building because the MCP server can create and update forms directly, not only read them. The setup story is practical, especially for Claude Code and Cursor users.
For small teams, prototypes, internal surveys, and low-governance forms, that may be enough.
### Where it falls short
The docs explicitly mark the MCP server as beta. Tally is also hosted-only, which limits its fit for enterprise infrastructure requirements. There is no separate runtime governance answer for production agents operating against form workflows.
That is not a criticism of Tally’s core product. It is a fit distinction. Tally can be a good lightweight form tool and still be the wrong infrastructure choice for governed enterprise workflows.
### Best for
Solo developers and small teams that want AI-assisted Tally form creation without self-hosting or regulated-workflow requirements.
## 4. Typeform MCP
**What it is.** Typeform’s MCP server is an early-access beta connector for interacting with a Typeform account from an LLM client. Typeform says it currently supports basic read-only access to forms and basic read-write access to contacts. Authentication currently uses a personal access token; OAuth support is on the roadmap ([Typeform MCP docs](https://www.typeform.com/developers/get-started/mcp/)).
### Scorecard
CriterionTypeform MCPRead + writeBasic read-only forms; basic read-write contactsSchemaTypeform form modelSelf-hostedNoVendor-maintainedYes, betaRuntime answerNoneDirectory presenceEmerging### Why it is #4
Typeform has brand recognition and a real vendor-maintained MCP beta. That matters. It means the MCP story is not only a third-party wrapper.
### Where it falls short
For form-building with AI, the current tool surface is too limited. Read-only form access does not satisfy the dev-time form generation use case. Personal access token authentication is also a current-state limitation compared with OAuth-based flows.
Until the tool surface expands, Typeform MCP is better understood as an early connector than a production-ready form-building MCP.
### Best for
Typeform users who want to experiment with an official beta and can tolerate limited capabilities.
## 5. Retool MCP for the forms path
**What it is.** Retool’s official MCP server is an admin-oriented beta that lets AI agents inspect and query a Retool organization, including apps, automations, resources, users, and related assets. Retool described the initial release as read-focused for admins, with expanded capabilities planned based on beta feedback ([Retool community announcement](https://community.retool.com/t/announcing-the-beta-for-retool-s-mcp-server/65038)).
### Scorecard
CriterionRetool MCPRead + writeRead-focused betaSchemaRetool app/resource modelSelf-hostedRetool deployment model varies; MCP specifics should be verified per deploymentVendor-maintainedYesRuntime answerRetool agents / broader Retool platform story, not forms-first UAGDirectory presenceRetool ecosystem### Why it is #5
Retool is a credible platform for internal-tool teams. If your forms exist as part of Retool apps, an MCP server that can inspect the Retool organization may be useful.
### Where it falls short
This is not a forms-first MCP server. Retool is a general internal-app platform, and the MCP server reflects that. It helps inspect a Retool environment; it does not primarily generate application-owned forms against a portable form schema.
### Best for
Retool-centric teams that want AI visibility into their internal-tool footprint. Not teams looking for a form infrastructure layer.
## 6. n8n MCP Server Trigger
**What it is.** n8n’s MCP Server Trigger node lets n8n act as an MCP server, making n8n tools and workflows available to MCP clients. The node exposes a URL clients can call, supports test and production URLs, and can require bearer or header authentication. n8n also notes deployment caveats around SSE or streamable HTTP when running with multiple webhook replicas ([n8n MCP Server Trigger docs](https://docs.n8n.io/integrations/builtin/core-nodes/n8n-nodes-langchain.mcptrigger/)).
### Scorecard
Criterionn8n MCP Server TriggerRead + writeWhatever the exposed workflow allowsSchemaWorkflow-definedSelf-hostedYes, if n8n is self-hostedVendor-maintainedYesRuntime answern8n workflows, same general surfaceDirectory presencen8n ecosystem### Why it is #6
n8n is flexible. If your team already runs n8n, exposing a workflow as an MCP server is a natural extension. It can be a useful bridge between agents and existing automations.
### Where it falls short
It is not a form MCP. It is a way to expose workflows through MCP. Developers can build something form-shaped with it, but the schema, validation, submission model, and governance pattern are whatever the team designs.
That is useful flexibility for automation teams. It is not a shortcut to schema-driven form infrastructure.
### Best for
n8n shops exposing existing workflows to agents. Not teams that need a forms-first dev-time MCP.
## 7. Zapier MCP / Pipedream MCP gateways
**What they are.** Zapier MCP connects AI tools to thousands of apps through Zapier’s existing app ecosystem. Zapier positions it as one governed connection for AI agents such as Claude, ChatGPT, and Cursor, with account-level restrictions, managed connections, and workspace controls ([Zapier MCP](https://zapier.com/mcp)). Pipedream offers a similar broad integration posture across app APIs, though public fetch access to the MCP page is less readable from this environment.
### Scorecard
CriterionZapier / Pipedream MCP gatewaysRead + writeWhatever the underlying app/API allowsSchemaInherits from the wrapped vendorSelf-hostedNoVendor-maintainedGateway-maintained, not form-vendor-nativeRuntime answerGateway workflow controls, not form-native runtime governanceDirectory presenceStrong### Why they are #7
They exist, they are broad, and they can be practical when the form tool you use does not have its own MCP server. For teams already standardizing on Zapier or Pipedream, the gateway path can be faster than waiting for every vendor to ship a first-party MCP.
### Where they fall short
A gateway is still a gateway. It does not know forms as a primitive unless the underlying app API exposes that structure clearly. It inherits the wrapped vendor’s schema, auth model, rate limits, task costs, and workflow constraints.
For production form infrastructure, this adds another layer rather than clarifying the contract.
### Best for
Teams that need AI access to many SaaS apps and can accept gateway latency, task cost, and inherited vendor constraints.
## Honorable mentions that are not really in the category
**Google Forms, Microsoft Forms, and SurveyMonkey.** No first-party forms MCP story strong enough to treat them as category leaders here. Gateway wrappers or community connectors may exist, but they are not the same as vendor-maintained form infrastructure.
**Community Jotform, Paperform, Gravity Forms, and similar wrappers.** Useful for experimentation. Riskier for production because maintenance, auth behavior, and schema changes can drift quietly.
**Onform and new MCP-native form tools.** Worth watching, but too early to evaluate for regulated-enterprise use without a longer product and deployment record.
## Why runtime UAG is a separate evaluation
UAG should not be ranked as though it were the same thing as a dev-time MCP server. It has a different job.
Formio’s UAG documentation says Universal Agent Gateway uses MCP to enable Formio functionality through an AI agent workflow and provides agents with dynamic context for using Formio JSON forms. It describes UAG as the package sitting between the Formio Platform and the AI agent, including the stock MCP server, authorization infrastructure, and custom tools or modules ([Formio UAG docs](https://help.form.io/ai-and-form.io/uag.md)).
That is runtime language. UAG is about agents operating against forms, fields, and submissions in a project. The standard tool set includes:
- `get\_forms`, which returns forms tagged for UAG use
- `get\_form\_fields`, which gives the agent a high-level overview of the fields needed to submit a form
- `get\_field\_info`, which provides validation, conditionals, input formats, and field structure
- `collect\_field\_data`, which helps gather required information from the user
- `confirm\_form\_submission`, which confirms collected information before submission
- `submit\_completed\_form`, which creates the form submission
- `find\_submissions`, which queries submissions from natural language intent
- `submission\_update`, which updates existing submissions when allowed
The UAG landing page frames this as JSON schemas becoming agent context: form definitions, validation rules, conditional logic, data models, RBAC policies, auth integration, form settings, and data routing become the binding set of rules for agents ([Formio UAG](https://form.io/uag/)).
That is the runtime distinction. A coding agent creating a form needs a dev-time MCP. A production agent collecting intake data, finding submissions, or updating records needs a runtime gateway that works through the form and submission layer rather than around it.
## What schema-driven infrastructure changes
The white paper’s most useful contribution is the distinction between a document validation schema and an application infrastructure schema.
A document validation schema defines shape. An application infrastructure schema must define shape, behavior, cross-runtime rendering, and network-transportable meaning. It needs to survive the trip from builder to renderer to API to runtime agent without losing the rules that make the workflow governed.
This matters for MCP because agents do not need more generic text. They need structured context they can act on safely.
In Formio, the atomic component is the key architectural unit. A field can carry type, structure, validation, conditional logic, calculated values, rendering intent, and labeling intent together. A repeating container such as an Edit Grid or Data Grid can carry nested child components with their behavior inline. Reused components carry behavior and governance with them.
For dev-time MCP, that means the coding agent is not merely generating a visual form. It is generating against the same schema pattern that defines API behavior and submission handling. For runtime UAG, it means the production agent can ask what fields exist, what validation applies, what input is missing, and what submission shape is required.
The same contract matters at both surfaces.
## MCP safety: practical rules before agents touch real systems
The difference between dev-time MCP and runtime UAG does not remove the need for safety. It clarifies where safety belongs.
OWASP’s LLM Top 10 warns that prompt injection can lead to unauthorized access, tool misuse, data disclosure, execution of arbitrary commands in connected systems, and manipulation of critical decisions. It also calls out indirect prompt injection from external sources such as websites or files ([OWASP LLM01:2025](https://genai.owasp.org/llmrisk/llm01-prompt-injection/)).
IBM’s 2025 Cost of a Data Breach report shows why this is not theoretical governance theater: 63% of organizations lacked AI governance policies to manage AI or prevent shadow AI, and 97% of organizations that reported an AI-related security incident lacked proper AI access controls ([IBM](https://www.ibm.com/reports/data-breach)).
Use these rules before connecting MCP servers to real systems.
### Start read-only when possible
Read-only access is not harmless, but it is a safer starting point. Let agents inspect schemas, docs, forms, or submissions before granting write capabilities.
For dev-time form generation, write access may be necessary. That is why Formio MCP’s guardrail around MCP-created forms matters: the agent can create and modify its own generated forms without receiving blanket authority over every form in the project.
### Scope credentials tightly
Do not hand an MCP server a broad production token unless the workflow truly requires it.
Use project-level credentials, narrow scopes, user-specific OAuth grants, or environment-specific API keys wherever possible. Separate dev, staging, and production access.
### Require human approval for high-risk actions
Creating a draft form in a dev project is not the same as updating a production intake workflow.
Require human confirmation before destructive actions, submission updates, workflow changes, external sends, or production writes. Formio UAG’s `confirm\_form\_submission` tool is an example of a runtime confirmation step inside the form workflow itself.
### Separate trusted and untrusted context
Agents that read web pages, tickets, uploaded files, or submission text are reading untrusted content. Do not let that content silently steer tool use.
This matters when form workflows include uploaded documents, open text fields, or public intake channels. Treat user-provided content as data, not instructions.
### Log the tool calls
If an agent can touch production data, the organization needs to know what happened.
Who initiated the action? Which tool was called? What data was retrieved? What submission was created or updated? Was confirmation required? Which identity or role allowed it?
Without those answers, MCP becomes another shadow integration layer.
### Use existing governance artifacts where possible
The right answer is not to recreate governance in prompts.
Use the artifacts the application already trusts: schema, validation rules, roles, permissions, form revisions, submission records, staged promotion, and audit patterns. That is the schema-driven infrastructure argument in practical form.
## Comparison table
## Server / categoryPrimary jobBest fitGovernance strengthWrite-risk levelFormio dev-time MCPGenerate and manage Formio forms during developmentDevelopers building application-owned formsStrongest dev-time fit; separate UAG runtime answerMedium; constrained by MCP-created-form guardrailsJotform MCPManage forms and submissions in JotformExisting Jotform teamsGood account-level OAuth storyMedium; hosted account writesTally MCPCreate/update lightweight Tally formsSolo developers and small teamsBasic hosted-account governanceMedium; beta hosted writesTypeform MCPRead forms and manage contactsTypeform beta experimentersLimited current surfaceLow-to-medium; limited form writes currentlyRetool MCPInspect Retool org assetsRetool admins and internal-tool teamsAdmin visibility, not forms-first governanceLow currently because read-focusedn8n MCP Server TriggerExpose workflows as MCP toolsn8n automation teamsDepends on workflow designVariable; whatever the workflow allowsZapier / Pipedream MCPGateway access to many SaaS APIsTeams needing broad app connectivityGateway/workspace controls, not form-nativeVariable; inherited from each appWhen Formio should be on your shortlist
Formio should be on your shortlist when forms are part of the application contract.
That includes:
- regulated intake workflows
- healthcare referrals and patient onboarding
- government benefit applications or service requests
- customer onboarding and KYC
- insurance claims and policy intake
- internal service requests that trigger downstream workflows
- multi-tenant applications where customers need embedded or white-labeled form creation
- any workflow where submissions, validation, roles, and revisions need to remain governed over time
The difference is ownership. If your team just needs to create a survey in a hosted account, Formio is probably more infrastructure than you need. If your forms define data models, APIs, validation rules, user-facing interfaces, and agentic context, then the form layer is no longer a convenience tool. It is part of the application stack.
That is where [Formio’s form builder and APIs](https://form.io/features/drag-and-drop-form-builder-apis/), [form validation and conditional logic](https://form.io/features/form-conditional-logic-form-validation/), [teams and permissions](https://form.io/features/forms-for-teams/), and [self-hosted deployment](https://form.io/features/self-hosted-forms-for-enterprise/) become relevant to the MCP decision.
The G2 review line used in the earlier draft still captures the fit well: “The form.io design is intuitive and easy to use but also has the advanced capabilities needed for our more complex client requirements.” That is the point. The right buyer is not looking for the simplest possible form tool. They are looking for a form layer that will not collapse when real application requirements arrive.
## Key takeaways
- Dev-time MCP and runtime UAG are different surfaces. Do not evaluate them as one product.
- Dev-time MCP helps coding agents generate, inspect, and modify forms during application development.
- Runtime UAG helps production agents operate through governed form, field, submission, and workflow context.
- Formio ranks first because it treats both surfaces as real architectural problems.
- Hosted form MCPs can be useful, but they usually keep forms inside the vendor’s account model.
- For regulated or self-hosted workloads, schema ownership, permissions, validation, and auditability matter more than quick setup.
- The strongest architecture makes the easy path and the governed path the same path.
## FAQ
### What is an MCP server?
An MCP server exposes tools, data, or workflows to an AI application through the Model Context Protocol. Instead of building a custom connector for every AI assistant and every system, teams can expose capabilities through a standard protocol that MCP-capable clients can call.
For forms, an MCP server might list forms, create forms, update form schemas, fetch submissions, or expose form-related workflow actions.
### What is the best MCP server for forms?
For application-owned forms, Formio’s dev-time MCP server is the strongest fit because it is vendor-maintained, open-source, self-hostable, and built around Formio’s schema-driven form infrastructure.
For teams already using a hosted form account, Jotform or Tally may be a better lightweight fit. The best choice depends on whether the form belongs to your application or to a third-party form account.
### What is the difference between dev-time MCP and runtime UAG?
Dev-time MCP helps developers build. It belongs in tools like Claude Code, Cursor, or Windsurf and helps generate, inspect, or modify forms while the application is being developed.
Runtime UAG helps production agents operate. It belongs inside the application workflow and gives agents governed access to forms, fields, submissions, validation, and confirmation steps. Dev-time MCP is for building the form. Runtime UAG is for operating through the form after it ships.
### Does UAG replace Formio’s dev-time MCP server?
No. UAG and the dev-time MCP server solve different problems.
The dev-time MCP server helps coding agents create and manage Formio forms during development. UAG provides runtime agent context and tools for production workflows. Treating them as interchangeable creates the exact confusion this category needs to avoid.
### Are MCP servers safe for enterprise systems?
They can be, but safety depends on configuration, credential scope, deployment model, tool design, logging, and human approval for risky actions.
A server that is safe for reading documentation may not be safe for updating production submissions. Start with least privilege, separate development from production, and do not give agents broad write access without a clear approval and audit model.
### Do MCP servers replace APIs?
No. MCP servers usually sit on top of APIs or application services. They give agents a structured way to discover and call capabilities, but the underlying system still needs stable APIs, authentication, authorization, validation, and logging.
In Formio’s case, MCP and UAG are valuable because they connect agents to the form and submission infrastructure rather than bypassing it.
### Why does JSON schema matter for form MCP servers?
A coding agent needs structured context. JSON-based schemas can describe fields, validation, nesting, required values, and submission shape in a machine-readable format.
The stronger Formio argument goes beyond generic JSON Schema. Formio’s component model keeps field structure, validation, conditional logic, calculated values, rendering intent, and labeling intent together, which makes the schema more useful as application infrastructure.
### Should agents have write access to forms?
Only when the workflow requires it and the boundary is clear.
For development, write access can be useful if the agent is creating or modifying sandboxed or MCP-created forms. For production, write access should require scoped credentials, runtime permissions, logging, and often human confirmation. A blanket production write token is not a governance strategy.
### When should a team use Jotform or Tally instead?
Use Jotform or Tally when the form is meant to live inside that hosted form product and the team values fast setup over application-owned infrastructure.
Use Formio when the form is part of the application’s schema, API, submission, permission, or workflow layer, especially when self-hosting, embedded deployment, or regulated governance matters.
### What should developers check before adopting a form MCP server?
Check whether the server can create and modify forms, what schema it uses, whether it can be self-hosted, who maintains it, what credentials it needs, whether it protects existing forms from accidental changes, and whether the vendor has a runtime answer for production agents.
The final question matters most: what happens after the form ships?
## The actual decision
Three questions answer this for most teams.
**Are you building forms inside an existing SaaS account or inside your own application?** If the form belongs inside a hosted account, Jotform or Tally may be enough. If the form belongs to your application, Formio is the stronger architectural fit.
**Does your data need to stay inside your infrastructure?** If yes, start with Formio or a self-hosted workflow tool such as n8n. Hosted-only form MCPs will usually fail the deployment requirement before the feature comparison begins.
**What happens after the form ships?** This is the question most MCP-for-forms comparisons avoid. Dev-time generation is only half the story. Production agents need a runtime governance surface. If the answer needs to be “agents operate inside our application’s governance envelope, with schema, validation, permissions, submissions, and audit patterns aligned,” then Formio is the vendor in this category that has treated both halves of the problem seriously.
If your forms are already application infrastructure, your agent layer should respect that infrastructure too. Start with the [Formio Universal Agent Gateway](https://form.io/uag/) when production agents need governed access to real form workflows, or explore [self-hosted Formio](https://form.io/features/self-hosted-forms-for-enterprise/) when the form layer needs to run inside your environment.
---
# Why Form.io Is Not Google Forms, Jotform, Typeform, or Retool, But Instead a Developer-First Approach to Form Automation
*Published:* 2026-02-03
*Author:* Form.io Wizard
*URL:* https://form.io/why-form-io-is-not-just-a-form-builder-but-a-developer-first-approach-to-form-automation/
*Description:* Form.io is data infrastructure for developer teams, not a SaaS form tool. Direct comparison vs. Google Forms / Jotform / Typeform / Retool.
When developers search for form automation solutions, they encounter a confusing landscape. Google Forms appears alongside enterprise form builders. Typeform competes with Retool. Jotform markets to the same audience as platforms that require MongoDB deployments. The category “form builder” has become meaningless because it groups together tools that solve fundamentally different problems for fundamentally different users.
Form.io exists in this space but operates on different assumptions. Understanding what those assumptions are, and why they matter, helps you determine whether Form.io belongs in your evaluation or whether a simpler tool serves your actual needs better.
## **The Consumer Form Builder Category**
Google Forms, Typeform, and Jotform occupy the consumer and small business segment of form automation. Their value proposition centers on accessibility: anyone can create a form without technical knowledge, distribute it via link or embed, and collect responses in a managed database or spreadsheet.
Google Forms optimizes for speed and zero friction. You create a form in minutes, share a link, and responses flow into Google Sheets. There is no setup, no deployment, no configuration. The tradeoff is limited customization, basic conditional logic, and forms that look like Google Forms regardless of your brand.
Typeform differentiates on user experience. The one-question-at-a-time interface creates a conversational feel that increases completion rates for surveys and lead capture. The design is polished. The templates are extensive. The tradeoff is that you are paying for aesthetics and engagement metrics, not for data infrastructure or developer tooling.
Jotform sits between these poles with broader feature coverage: payment processing, more field types, PDF generation, and integrations with common business tools. It handles more complex use cases than Google Forms while remaining accessible to non-technical users.
These tools share a common architecture. You build forms in their interface. Data lives in their database. Integrations happen through their connection layer. Your application, if you have one, interacts with their API to pull data after submission. The form is a separate service your users visit, not a component embedded in your application.
This architecture works well when forms are standalone data collection points. Marketing surveys. Event registrations. Contact forms. Lead capture. Situations where the form exists independently from any larger application context.
## **The Internal Tool Builder Category**
Retool, Appsmith, and similar platforms solve a different problem. They help developers build internal applications quickly by providing pre-built UI components, database connectors, and a visual development environment. Forms are one component type among many: tables, charts, buttons, modals.
Retool’s value proposition is speed for internal tools. Instead of building an admin panel from scratch, you drag components onto a canvas, write SQL queries to populate them, and deploy an internal application in hours instead of weeks. The forms within Retool connect directly to your database. You write the queries. You control the schema.
The tradeoff is that Retool builds applications, not reusable form infrastructure. Each Retool app is a distinct artifact. The forms within it are not portable, not embeddable in external applications, and not designed for end-user-facing contexts. Retool optimizes for internal operations teams, not for customer-facing data collection at scale.
Retool also requires developers. Despite the visual interface, you write SQL, JavaScript, and configure integrations. This is appropriate for its target audience (internal tool development by engineering teams) but means it does not solve the “business users building forms without code” problem that drives adoption of consumer form builders.
## **Where Form.io Actually Fits**
Form.io occupies a category that neither consumer form builders nor internal tool platforms address: forms as embeddable infrastructure for bespoke applications.
The distinction matters at the architecture level. Consumer form builders host your forms and data on their infrastructure. You visit their service to build forms, and users visit their service (or an iframe) to complete them. Internal tool builders create standalone applications that happen to include forms. Form.io provides a form and API platform that deploys inside your infrastructure and integrates directly into applications you are building. That level of integration means form automation capabilities, third-party connections, automated data flows, and so forth are within reach.
When you drag components onto a Form.io form, you are not just creating a UI. You are defining a [JSON schema](/form-json-schema-vs-submission) that simultaneously describes the form’s appearance, validation rules, and the API structure for submissions. The form builder generates both the frontend component and the backend API in a single operation. This is what “forms + APIs” means in practice.
The platform deploys as Docker containers connected to your [MongoDB instance](/why-form-io-requires-the-mongodb-document-model). You control the infrastructure. Data never leaves your environment unless you send it somewhere. This matters for regulated industries, enterprise security requirements, and organizations that cannot accept third-party data hosting.
The JavaScript renderer embeds directly in Angular, React, Vue, or vanilla JavaScript applications. No iframes. No redirects to external services. The form appears as a native component in your application, styled with your CSS, authenticated through your session management, and submitting to APIs running in your environment.
## **Different Problems, Different Tools**
The “which form builder should I use” question has no universal answer because the question conflates different problems.
**If you need a survey or feedback form** that exists independently, Google Forms or Typeform is probably correct. They are faster to set up, require no infrastructure, and optimize for the standalone form use case. Typeform if completion rates and design matter. Google Forms if cost and simplicity matter.
**If you need internal admin tools** that query your database and let operations teams manage data, Retool or similar platforms make sense. They optimize for that specific workflow and provide components beyond forms that internal tools require.
**If you are building an application** where forms are embedded data collection components that feed into application logic, where the form schema defines your data model, where you need the form builder to produce reusable form definitions that render across web and mobile, where forms update independently of application deployment cycles, and where data and infrastructure must remain under your control, then Form.io addresses requirements that the other categories do not.
## **What Form.io Requires That Others Do Not**
Form.io assumes you have a development team. The platform provides the form building, API generation, and rendering infrastructure, but you integrate that infrastructure into an application you are building. If you do not have an application, if you are not planning to build one, Form.io solves a problem you do not have.
Installation means deploying containers and configuring MongoDB. The [Form.io GitHub repository](https://github.com/formio/formio) provides the open source core, and enterprise features require licensing. You manage upgrades, scaling, and operations for your deployment. This is infrastructure you own, with the responsibilities that ownership entails.
The learning curve involves understanding JSON schemas, the relationship between forms and Resources, how Actions work as middleware \[(/features/form-actions)\], and how the renderer integrates with your frontend framework. The [documentation](https://help.form.io) and [API reference](https://apidocs.form.io) are comprehensive, but you will spend time learning the platform’s concepts before becoming productive.
Pricing does not scale with usage. Form.io charges per project and per environment, not per form, per submission, or per user. This makes cost predictable for high-volume applications but means the economics only make sense at sufficient scale. A contact form collecting 50 submissions per month does not justify Form.io’s complexity. An enterprise application processing thousands of structured data submissions across multiple tenants begins to reveal why the infrastructure approach matters.
## **The “Low-Code” Distinction**
Form.io sometimes appears in low-code or no-code platform comparisons, but the categorization obscures more than it clarifies.
Consumer form builders are no-code tools. Business users create forms without developer involvement. The platform handles everything.
Internal tool builders like Retool are low-code. Developers use visual interfaces but write queries and logic. The visual layer accelerates development without eliminating code.
Form.io is what the company calls “pro-code/low-code.” The form building interface is visual and accessible to non-developers. Business users can create and modify forms without code changes. But the platform itself deploys into a developer-managed environment. Integration requires code. Custom components require code. The platform accelerates form development while remaining firmly developer-infrastructure.
[This post](https://form.io/blog/low-code-app-development-without-the-lock-in-effects) articulates the position directly: Form.io is not an application development platform (ADP) in the traditional sense. Your developers still build the application. Form.io handles the forms, their APIs, and the submission infrastructure so developers do not have to build that layer from scratch.
## **When Consumer Form Builders Break Down**
Consumer form builders work until your requirements exceed their assumptions. Common breaking points include:
**Nested and repeating data structures.** A form that collects multiple addresses, or line items with variable quantities, or hierarchical data that maps to document structures rather than flat rows. Consumer form builders flatten everything into spreadsheet-compatible formats. Form.io preserves nested JSON structures because MongoDB stores documents, not rows.
**Application integration beyond webhooks.** If your application needs to render forms dynamically, prepopulate data from user context, validate against business logic before submission, or respond to submission events within application flow, iframe-based embedding and webhook integrations become limiting. Form.io’s renderer operates inside your application context with full access to application state.
**Multi-tenant deployments.** SaaS platforms that need to provide form building to their own customers, with data isolation between tenants, and white-labeled interfaces, cannot accomplish this with tools designed for single-organization use. Form.io’s [multi-tenancy architecture](/features/platform-as-a-service-paas) supports these hierarchical structures.
**Compliance and data residency.** HIPAA, FedRAMP, GDPR data residency requirements, or organizational security policies that prohibit third-party data hosting eliminate consumer form builders from consideration regardless of their features. Self-hosted Form.io deployments keep data in environments you control.
**Complex conditional logic and validation.** Consumer form builders offer show/hide logic and basic validation. When you need validation rules that query external APIs, [conditional flows](/features/form-conditional-logic-form-validation) that span multiple pages with draft saving, or business logic that exceeds what simple condition builders express, you need programmable form infrastructure.
## **When Form.io Is Overkill**
Form.io is overkill when simpler tools solve your actual problem.
If your forms exist independently and do not integrate into an application, consumer form builders are faster and cheaper. The infrastructure overhead of Form.io provides no benefit when forms stand alone.
If you need internal admin tools for your team, Retool or similar platforms optimize for that workflow with features Form.io does not prioritize.
If you are evaluating form solutions for a project that does not yet have committed developer resources, the platform’s dependency on technical implementation becomes a blocker rather than an enabler.
If your organization cannot support self-hosted infrastructure, the operational requirements exceed what your team can maintain. Form.io’s SaaS offering exists but the platform’s design assumes self-hosted deployments for enterprise use cases.
If your forms collect survey data that exports to spreadsheets for analysis, the JSON document model and MongoDB storage add complexity without corresponding benefit.
## **The Infrastructure Mental Model**
The category confusion around Form.io dissolves when you adopt the infrastructure mental model. Consumer form builders are SaaS services you use. Internal tool platforms are application builders. Form.io is infrastructure you deploy, like a database or authentication service.
You do not compare PostgreSQL to Airtable even though both store data. You do not compare Auth0 to a simple password field even though both relate to authentication. Similarly, comparing Form.io to Google Forms based on the presence of drag-and-drop form building obscures that they occupy different layers of the technology stack.
Form.io’s positioning as “forms as infrastructure” reflects this distinction. The platform provides form rendering, schema management, submission APIs, and action pipelines as services your application consumes. You choose this approach when forms are a core component of applications you are building, when you need the control and integration depth that infrastructure ownership provides, and when you have the technical resources to deploy and maintain that infrastructure.
The companion piece on why Form.io is not Google Forms / Typeform / Retool explores these distinctions in technical detail. For now, the key takeaway is categorical: Form.io belongs in evaluations alongside embeddable form infrastructure, not alongside SaaS form services or visual application builders.
## **Related Resources**
- [Why Form.io Requires MongoDB](/why-form-io-requires-the-mongodb-document-model) explains the data model implications
- [Form Schemas vs Submissions](/form-json-schema-vs-submission) covers the JSON schema architecture
- [Why Form.io Is Infrastructure, Not an App Builder](/formio-is-infrastructure-as-a-forms-solution) elaborates the infrastructure positioning
- [Why You Should Not Use Form.io Without a Dev Team](/why-you-shouldnt-use-formio-if-you-dont-have-a-dev-team) addresses the developer requirement directly
- [formio/formio on GitHub](https://github.com/formio/formio) provides the open source core
---
# Form.io is Middleware Infrastructure as a Forms Solution, Not an App Builder
*Published:* 2026-01-14
*Author:* Form.io Wizard
*URL:* https://form.io/form-io-is-middleware-infrastructure-as-a-forms-solution-not-an-app-builder/
*Description:* Form.io sits between user-facing apps and systems of record — handling intake, validation, governance, and routing. It's not an app builder.
Form.io is a forms solution that operates as infrastructure. It provides a rendering engine, a submission API, validation logic, and data storage. It does not provide navigation, user dashboards, business logic orchestration, or the screens that surround your forms. You build those parts. Form.io handles the form capture layer inside them.
This distinction matters because it determines what problems Form.io solves and what problems remain yours to solve. Teams expecting an app builder will be frustrated. Teams building bespoke applications who need a forms solution that stays out of their way will find exactly what they need.
## **What Infrastructure Means in Practice**
Infrastructure provides capabilities that applications consume. A database is infrastructure. An authentication service is infrastructure. A payment processor is infrastructure. You do not expect PostgreSQL to generate your admin dashboard or Stripe to build your checkout flow. They provide APIs and data storage. Your application provides everything else.
Form.io operates the same way. It gives you:
**A form renderer** that takes a JSON schema and produces an interactive form. The renderer handles field display, validation feedback, conditional logic, and submission. You embed the renderer in your application using a JavaScript library or framework component.
**A submission API** that receives form data, validates it server-side, stores it in [MongoDB](/why-form-io-requires-the-mongodb-document-model), and returns the result. Your application calls this API or lets the embedded renderer call it automatically.
**A schema API** that stores and retrieves form definitions. Your application fetches schemas to pass to the renderer, or you build forms in the portal and reference them by path.
**An access control layer** that determines who can submit to which forms and who can read which submissions. You configure this through Teams and Permissions and integrate it with your application’s authentication.
What Form.io does not provide: the application shell, routing, user registration flows, email notifications, approval workflows, reporting dashboards, or any screen that is not a form. Those are application concerns. Form.io is the forms solution inside the application, not the application itself.
## **The Difference From App Builders**
App builders like Retool, OutSystems, or Mendix generate complete applications. You define data models, screens, navigation, and logic inside the platform. The platform produces a running application that users interact with directly.
This model works when your requirements fit the platform’s assumptions. It struggles when you need custom behavior, specific performance characteristics, integration with proprietary systems, or a user experience the platform cannot produce.
Form.io makes a different tradeoff. It solves forms completely and their APIs, but not the whole application. This means:
**You control the application architecture.** Form.io does not impose a framework, hosting environment, or deployment model. Embed the renderer in React, Angular, Vue, or plain JavaScript. Host your application anywhere. Deploy however your organization deploys software.
**You control the user experience.** The form is one component in your interface. Everything around it, including headers, navigation, progress indicators, help text, and branding, comes from your application. Form.io renders what is inside the form boundary. You render everything outside it.
**You control the data flow.** Submissions go to Form.io’s API, but you decide what happens next. Webhooks can trigger your backend services. The [submission API](https://apidocs.form.io/) lets you query and transform data. You can export submissions to other systems. Form.io stores the data; your application decides what to do with it.
**You write business logic.** Form.io validates form fields. It does not know whether a submitted insurance claim should be approved, whether an expense report needs manager review, or whether a patient intake form should trigger a scheduling workflow. Your application implements these decisions.
## **What This Requires From Your Team**
Treating Form.io as infrastructure means your team handles infrastructure integration. This is not no-code or low-code. This is code-required.
**Frontend development.** Someone must embed the form renderer in your application, style it to match your [design system](/features/customizable-forms-with-css), and handle the integration points where form events trigger application behavior.
**Backend development.** If submissions need to trigger workflows, sync to other databases, or integrate with external services, someone writes that code. Form.io provides webhooks and APIs. Your services consume them.
**DevOps or platform engineering.** [Self-hosted deployments](/features/self-hosted-forms-for-enterprise) require provisioning MongoDB, configuring the Form.io server, managing secrets, and maintaining the infrastructure. Even cloud-hosted deployments require integration work around authentication and network access.
**Form building.** The [drag-and-drop builder](/features/drag-and-drop-form-builder-apis) lets non-developers create forms, but someone still needs to understand how components map to [submission data](/form-json-schema-vs-submission), how [validation rules work](/features/form-conditional-logic-form-validation), and how the form integrates with the surrounding application.
Teams without development resources should look elsewhere. The article Why You Should Not Use Form.io Without a Dev Team explains this constraint in detail.
## **Where Form.io Fits in Application Architecture**
A typical architecture using Form.io looks like this:
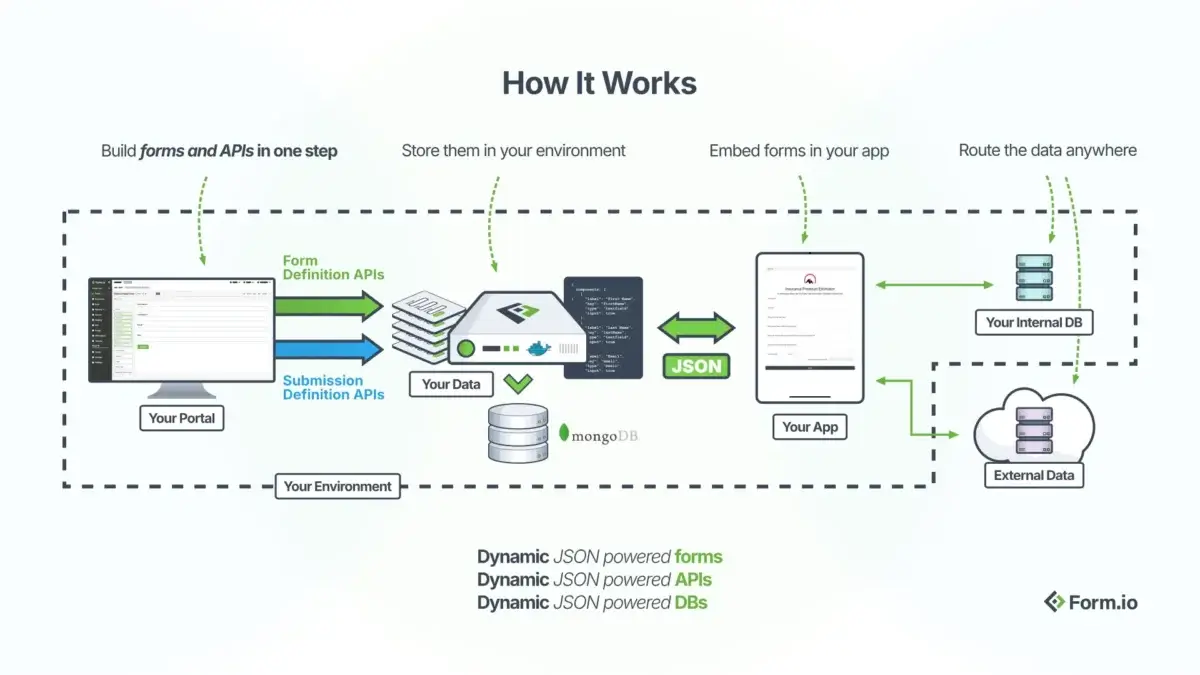When a user reaches a screen that needs a form, your application renders the Form.io component with the appropriate schema. The renderer handles everything inside the form boundary. On submission, data goes to Form.io’s server, which validates and stores it. Webhooks notify your backend services to trigger downstream processes.
This architecture separates concerns cleanly. Form.io does not know about your user model, your business domain, or your other services. It knows about forms, submissions, and access rules. Your application orchestrates everything else.
## **Comparison With Embedded Versus Platform Approaches**
Forms solutions fall into three categories, each with different integration models.
**Standalone form tools** like Google Forms or Typeform provide complete form experiences [at their own URLs](/why-form-io-is-not-just-a-form-builder-but-a-). Users visit the form tool’s domain to fill out forms. Data lives in the form tool’s database. You access it through exports or limited APIs. These tools work for simple data collection but cannot embed into custom applications or match enterprise UI requirements. The article Why Form.io Is Not Google Forms or Typeform explores this comparison.
**App builder platforms** like Retool or OutSystems include form components as part of a larger application generation system. Forms exist inside applications the platform builds. If you want forms inside an application the platform did not build, you cannot extract just the form component. The form capability is coupled to the platform’s application model.
**Forms infrastructure** like Form.io provides form capabilities as embeddable components and APIs. The renderer runs inside your application. The API integrates with your backend. The form system is decoupled from any specific application architecture. You use as much or as little as your application needs.
The infrastructure approach requires more development work. It provides more architectural flexibility. This is the fundamental tradeoff.
## **What Form.io Handles Completely**
Despite being infrastructure, Form.io solves certain problems end-to-end so your application does not have to.
**Field-level validation** runs both client-side for immediate feedback and server-side for security. You configure validation rules in the form schema. The renderer and API enforce them. Your application does not validate individual fields.
**[Conditional logic](/features/form-conditional-logic-form-validation)** shows, hides, enables, or disables fields based on other field values. Complex [multi-step wizards](/features/multi-page-form-wizards) with branching paths work through configuration, not custom code.
**[File uploads](/features/form-file-uploads)** handle the complexity of multipart uploads, storage provider integration, and reference management. Submissions contain file references.
**[Offline support](/features/offline-forms)** queues submissions when connectivity drops and syncs when it returns. Your application gets this capability by embedding the renderer with offline mode enabled.
**[Multi-tenancy](/features/platform-as-a-service-paas)** isolates forms and submissions between tenants at the platform level. If your application serves multiple organizations, Form.io’s tenant model can map to your tenant boundaries.
**[Revision tracking](/features/form-revisions-form-json-schema)** maintains form schema history so you can audit what version of a form captured any given submission. The revision logs provide this automatically.
These are form-specific concerns that Form.io handles so your application team focuses on application-specific concerns.
## **When Infrastructure Is the Wrong Choice**
The infrastructure model does not fit every project.
**Prototyping and MVPs** often benefit from app builders that generate working software quickly. If your goal is validating an idea before committing to custom development, the speed of a platform may outweigh the flexibility of infrastructure.
**Simple data collection** where you need a form and a spreadsheet of responses does not require Form.io’s capabilities. Google Forms or Typeform solve this with less setup.
**Teams without developers** cannot integrate infrastructure. If no one on your team writes code, you need a platform that generates the entire application, not a forms solution that requires integration work.
**Rigid compliance environments** that mandate specific platforms may not have evaluated Form.io. If your organization requires all applications to run on a particular low-code platform for governance reasons, that constraint overrides technical fit.
The article What Form.io Does Not Do lists specific capabilities outside Form.io’s scope.
## **Evaluating Fit for Your Project**
Ask these questions to determine if Form.io’s infrastructure model fits your needs.
**Are you building a custom application?** If yes, Form.io provides the forms layer inside it. If you want a platform to build the application for you, look elsewhere.
**Do you have developers?** If yes, they can integrate Form.io’s renderer and APIs. If no, you need a no-code solution that Form.io is not.
**Do your forms need to match a specific design system?** Form.io forms can be [styled with CSS](/features/customizable-forms-with-css) to match any visual design. App builder forms typically constrain you to the platform’s styling options.
**Do submissions need to trigger complex workflows?** Form.io provides the data capture and webhook triggers. Your application implements the workflow logic. If you need workflow automation built in, evaluate platforms that include it.
**Is data portability important?** Form.io stores submissions in MongoDB that you can query, export, and migrate. Vendor lock-in is minimal because the data layer is transparent. Closed platforms may restrict data access. You can even use your own submission APIs and store data outside of Form.io.
## **Related Resources**
- [Why Form.io Is Not Google Forms or Typeform](/why-form-io-is-not-just-a-form-builder-but-a-developer-first-approach-to-form-automation) compares platform models
- [Why You Shouldn’t Use Form.io Without a Dev Team](/why-you-shouldnt-use-formio-if-you-dont-have-a-dev-team) explains the development requirement
- [Form Schemas vs Submissions](/form-json-schema-vs-submission) details the data model
- [JSON-Driven Forms](/features/form-from-json-schema) explains the schema-driven rendering approach
- [Integrations](/features/data-integration-tools-for-enterprise-forms) covers webhook and third-party connections
- [Form.io Renderer Repository](https://github.com/formio/formio.js) contains embedding documentation
- [API Documentation](https://apidocs.form.io/) provides endpoint references
---
# Form JSON Schema vs Submission: Understanding the Two Documents That Power Form.io
*Published:* 2025-12-09
*Author:* Form.io Wizard
*URL:* https://form.io/form-json-schema-vs-submission/
*Description:* The two documents that power Form.io: schema is the contract; submission is the data. Conflating them is the most common architectural mistake.
Every form system stores two fundamentally different things: the definition of what a form looks like and the data that users enter into it. Most form builders obscure this distinction. Form.io makes it explicit because the separation is what enables forms to function as infrastructure rather than a closed application feature.
A Form.io deployment works with two document types. The [form JSON schema](/features/form-from-json-schema) defines the structure, validation rules, layout, and behavior of a form. The submission document contains the actual data a user entered, stored separately and linked back to its parent schema. Understanding how these two documents relate is essential for building applications on Form.io, querying data correctly, and avoiding architectural mistakes that surface months into a project.
## **The Form JSON Schema: Structure Without Data**
A form JSON schema is a complete definition of a form’s components, validation logic, conditional display rules, and metadata. It does not contain any user-submitted data. Here is a simplified example:
```
{
"_id": "507f1f77bcf86cd799439012",
"title": "Employee Onboarding",
"name": "employeeOnboarding",
"path": "employeeonboarding",
"type": "form",
"components": [
{
"type": "textfield",
"key": "firstName",
"label": "First Name",
"validate": {
"required": true,
"maxLength": 50
}
},
{
"type": "email",
"key": "email",
"label": "Work Email",
"validate": {
"required": true
}
},
{
"type": "datagrid",
"key": "emergencyContacts",
"label": "Emergency Contacts",
"components": [
{
"type": "textfield",
"key": "name",
"label": "Contact Name"
},
{
"type": "phoneNumber",
"key": "phone",
"label": "Phone Number"
}
]
}
]
}
```
The `components` array is recursive. Each component can contain child components, which is how Form.io represents nested structures like Data Grids, Edit Grids, and container layouts. The `key` property on each component determines where that field’s value will appear in the submission data.
This schema tells the Form.io renderer exactly how to display the form, what validation to apply client-side and server-side, and how to structure incoming data. The schema is the source of truth for form behavior.
## **The Submission Document: Data Without Structure**
A submission document contains the data a user entered, wrapped in metadata about when and by whom. The same form schema above produces submissions that look like this:
```
{
"_id": "507f1f77bcf86cd799439011",
"form": "507f1f77bcf86cd799439012",
"data": {
"firstName": "Sarah",
"email": "sarah.chen@company.com",
"emergencyContacts": [
{"name": "Michael Chen", "phone": "303-555-0142"},
{"name": "Lisa Chen", "phone": "303-555-0187"}
]
},
"owner": "507f1f77bcf86cd799439013",
"created": "2024-01-15T14:32:00.000Z",
"modified": "2024-01-15T14:32:00.000Z",
"state": "submitted"
}
```
Notice that the submission references the form by ID in the `form` field. The actual user data lives inside the `data` object, with keys that match the component keys from the schema. The nested `emergencyContacts` array mirrors the Data Grid structure defined in the form schema.
This separation means you can update a form schema without invalidating existing submissions. You can query submissions independently of their parent forms. You can store millions of submissions across thousands of form versions without schema migrations corrupting your data.
## **Why the Separation Matters**
The two-document model creates architectural flexibility that single-document approaches cannot match.
**Schema versioning becomes possible.** When you update a form schema using Form Revisions, existing submissions remain intact. A submission captured under version 3 of a form still contains exactly the data it captured, even after version 4 adds new fields or changes validation rules. The Form Revision Logs track which schema version was active when each submission arrived, enabling audit trails that compliance requirements often demand.
**Querying scales independently.** Submissions live in their own MongoDB collection. You can index submission data, run aggregation queries, and export subsets without touching form schemas at all. The Data Reporting features leverage this by querying the submissions collection directly using MongoDB aggregation pipelines.
**Rendering separates from storage.** The Form.io renderer needs only the schema to display a form. It does not need to know anything about existing submissions. This is why forms can be embedded in any application with a single JavaScript include and a schema reference.
## **How Components Map to Submission Keys**
The key property on each form component determines where submitted data appears in the data object. This mapping is direct and predictable, which matters when you write code that processes submissions.
Simple components create simple keys:
**Component Type****Schema Key****Submission Data**Text Field`firstName``data.firstName: "Sarah"`Email`email``data.email: "sarah@example.com"`Number`salary``data.salary: 75000`Checkbox`agreedToTerms``data.agreedToTerms: true`Nested components create nested structures. A Data Grid with key `emergencyContacts` containing child components with keys `name` and `phone` produces an array at `data.emergencyContacts` where each element has `name` and `phone` properties.
Container components like Panels, Columns, and Field Sets do not create keys by default. They exist for layout purposes only. A Text Field inside a Panel still writes directly to `data.fieldKey`, not `data.panelKey.fieldKey`. This trips up developers who expect container nesting to affect data structure. It does not, unless you explicitly configure the container to have a key.
Edit Grids and Data Grids behave identically for data purposes. Both produce arrays. The difference is in the editing interface: Data Grids show all rows in a table, while Edit Grids show one row at a time in a modal or inline editor.
## **The Form Schema Is Not JSON Schema**
Form.io’s schema format is proprietary. It is not [JSON Schema](https://json-schema.org/), the specification used for validating JSON documents. This distinction matters when integrating with systems that expect standard JSON Schema.
JSON Schema defines validation rules for JSON data. It answers the question “is this document valid?” Form.io’s schema defines both validation rules and rendering instructions. It answers “how do I display this form and validate its input?”
A JSON Schema for the employee onboarding example would look different:
```
{
"type": "object",
"properties": {
"firstName": {"type": "string", "maxLength": 50},
"email": {"type": "string", "format": "email"},
"emergencyContacts": {
"type": "array",
"items": {
"type": "object",
"properties": {
"name": {"type": "string"},
"phone": {"type": "string"}
}
}
}
},
"required": ["firstName", "email"]
}
```
This JSON Schema could validate Form.io submission data, but it cannot render a form. It has no concept of labels, layout, conditional visibility, or the dozens of component-specific properties that control form behavior.
Form.io chose a proprietary format because form rendering requires information that JSON Schema was never designed to carry. The JSON-Driven Forms documentation explains how the schema drives the renderer and why the additional properties exist.
## **Querying Submissions Through the API**
The [Form.io API](https://apidocs.form.io/) provides endpoints for both schemas and submissions. Understanding the separation helps you construct correct queries.
To retrieve a form schema:
```
GET /form/:formId
```
To retrieve submissions for that form:
```
GET /form/:formId/submission
```
To retrieve a specific submission:
```
GET /form/:formId/submission/:submissionId
```
Submission queries support MongoDB-style filtering on the data object:
```
GET /form/:formId/submission?data.email=sarah@example.com
```
For nested data, use dot notation:
```
GET /form/:formId/submission?data.emergencyContacts.name=Michael%20Chen
```
The [Export Form Data](/features/exporting-csv-forms-data) feature uses these same endpoints internally. When you export to JSON through the portal, you receive an array of submission documents. When you export to CSV, the system flattens the nested data object into columns.
## **Common Mistakes and How to Avoid Them**
**Storing derived data in the schema.** Form schemas should contain structure, not data. If you need to store metadata about a form (deployment environment, business unit owner, etc.), use a separate configuration document or your application’s database. The schema belongs in MongoDB as Form.io stores it.
**Expecting container keys to nest data.** Panels, Columns, and similar layout components do not create data nesting by default. If you need nested data structures, use components designed for that purpose: Data Grids, Edit Grids, or containers with explicit keys enabled.
**Querying schemas when you need submissions.** New developers sometimes query the form endpoint expecting to find submitted data. Forms and submissions live in different collections and serve different purposes. The form endpoint returns structure; the submission endpoint returns data.
**Assuming schema updates migrate existing data.** When you add a new required field to a form, existing submissions do not suddenly gain that field. They contain exactly what users submitted at the time. Your application code must handle submissions that predate schema changes. The Form Revisions feature helps track which schema version captured each submission.
## **When This Model Does Not Fit**
The two-document model assumes you want to capture structured data through forms and store it for later retrieval. This fits most enterprise applications, but not all use cases.
If you need real-time collaborative editing where multiple users modify the same document simultaneously, Form.io submissions do not support that natively. Each submission is a discrete document created by a single save operation. You would need Collision Control to prevent overwrites, but that is conflict prevention, not real-time collaboration.
If you need the form structure to live inside a relational database alongside your application data, you will hit friction. Form.io requires [MongoDB](/why-form-io-requires-the-mongodb-document-model) (or a compatible equivalent) for its schema and submission storage. You can synchronize submission data to SQL databases using [webhooks and middleware](https://help.form.io/developers/integrations/relational-databases) or you can choose to use your own submission API and store your data elsewhere.
If your application generates forms dynamically from external metadata (database columns, API responses), you will need to transform that metadata into Form.io schema format. The schema is specific and detailed. This is not a limitation so much as an explicit interface contract: give the renderer exactly what it expects, and it will render exactly what you specified.
## **Related Resources**
- [JSON-Driven Forms](/features/form-from-json-schema) explains how the schema drives rendering
- [Form Revisions](/features/form-revisions-form-json-schema) covers schema versioning
- [Export Form Data](/features/exporting-csv-forms-data) documents submission extraction
- [Data Reporting](/features/data-analysis-reports-mongodb-aggregation-pipelines) explains MongoDB aggregation access
- [Why Form.io Requires MongoDB](/why-form-io-requires-the-mongodb-document-model) details database dependencies
- [API Documentation](https://apidocs.form.io/) provides endpoint references
- [Form Building Guide](https://help.form.io/userguide/forms/form-building) covers component configuration
---
# Form.io Introduces the Universal Agent Gateway (UAG) for Enterprise AI Adoption
*Published:* 2025-11-19
*Author:* Form.io Wizard
*URL:* https://form.io/press/form-io-introduces-the-universal-agent-gateway-uag-for-enterprise-ai-adoption/
*Description:* UAG launch announcement: open-source MIT-licensed MCP server purpose-built for governing AI agents inside regulated enterprises.
Transforming how developers build, standardize, and scale agentic workflows.
November 19, 2025  Universal Agent Gateway (UAG) by Form.io Compare audit trail software needs for enterprise forms: audit logs, form revisions, submission history, staged promotion, and self-hosted controls.
Learn when a web form builder is enough, when forms need APIs and workflow control, and how Form.io fits self-hosted enterprise form infrastructure.
Compare e signature software for enterprise form workflows, including DocuSign alternatives, self-hosting, audit trails, APIs, and Form.io E-Sign+.
Compare JSON Schema validator tools for production apps: Ajv, Python libraries, form generators, API contracts, governance, and Form.io infrastructure.
Compare embedded forms and white-label form builders for B2B SaaS teams, from simple embeds to governed APIs, tenant controls, and secure data ownership.
Evaluate claims management software through the form infrastructure behind FNOL, documents, APIs, audit trails, PDFs, and regulated insurance workflows.
Evaluate KYC onboarding software for banks and fintechs through forms, APIs, identity checks, audit trails, self-hosted control, and governed workflows.
Compare Typeform alternatives for surveys, self-hosting, compliance, embedded forms, APIs, governance, and infrastructure fit for regulated teams in 2026.
Compare Jotform alternatives for regulated teams needing self-hosted forms, APIs, audit trails, permissions, embedded workflows, and better data control.
Compare Formbricks and Form.io across open source surveys, self-hosting, APIs, embedding, governance, pricing, and form infrastructure use cases for teams.
Compare Budibase and Form.io across forms, APIs, self-hosting, governance, embedding, pricing, and best-fit use cases for enterprise form infrastructure.
Compare HIPAA-compliant form builder options for healthcare SaaS teams, from BAAs and audit logs to APIs, self-hosting, and PHI control.
Your First Custom Form.io Theme: Solving the most common use case: CSS class overrides.
When “Close Enough” Stops Being Good Enough and You Need Your Forms to Match the Rest of Your Application, Pixel-for-Pixel.
Compare MCP server list options for regulated enterprise developers. See official registries, GitHub, AWS, Playwright, Form.io, and governance criteria.
Compare AI governance platform layers for agentic workflows, including Form.io UAG, Appian, Camunda 8.9, Flowable 2025.1, and Microsoft AGT.
[ Share](https://www.facebook.com/sharer/sharer.php?u=https://form.io/ai-governance-platform-agentic-workflow-governance-layers-compared/%2F&src=sdkpreparse)#### Webinars
# [](https://form.io/webinars/agentic-coding-for-the-enterprise/)[Agentic Coding for the Enterprise (LIVE Demo: Form.io Agentic Coding Toolset)](https://form.io/webinars/agentic-coding-for-the-enterprise/)
# Date: Wednesday, August 19, 2026 Time: Central [](https://form.io/webinars/enable-self-service-forms-in-your-application/)[Enable Self-Service Forms in Your Application (LIVE Demo: Form.io’s Enterprise Form Builder Module)](https://form.io/webinars/enable-self-service-forms-in-your-application/)
# Date: Thursday, June 25, 2026 Time: 11:00 pm Central [](https://form.io/webinars/byo-css-the-new-standard-for-white-labeling-form-io/)[BYO-CSS: The New Standard for White Labeling Form.io](https://form.io/webinars/byo-css-the-new-standard-for-white-labeling-form-io/)
Date: Thursday, March 26, 2026 Time: 11:00 am Central #### Recent Posts
# [](https://form.io/web-form-builder-apis-self-hosted-control/)[Web Form Builder: When Online Forms Need APIs, Workflows, and Self-Hosted Control](https://form.io/web-form-builder-apis-self-hosted-control/)
# August 5, 2026 [](https://form.io/e-signature-software-self-hosted-form-workflows/)[E Signature Software for Self-Hosted Form Workflows: DocuSign Alternatives for Enterprise Control](https://form.io/e-signature-software-self-hosted-form-workflows/)
# July 21, 2026 [](https://form.io/json-schema-validator-tools-production-apps/)[JSON Schema Validator Tools for Production Apps](https://form.io/json-schema-validator-tools-production-apps/)
# July 20, 2026 [](https://form.io/embedded-forms-b2b-saas-white-label-comparison/)[Embedded Forms for B2B SaaS: The White-Label Form Builder Comparison](https://form.io/embedded-forms-b2b-saas-white-label-comparison/)
# July 17, 2026 [](https://form.io/claims-management-software-insurance-form-builders/)[Claims Management Software Starts With The Forms That Feed It](https://form.io/claims-management-software-insurance-form-builders/)
# July 16, 2026 [](https://form.io/kyc-onboarding-software-financial-services-form-platforms/)[KYC Onboarding Software for Financial Services: Forms, APIs, and Audit-Ready Intake](https://form.io/kyc-onboarding-software-financial-services-form-platforms/)
July 15, 2026 #### Recent Case Studies
# [](https://form.io/case-studies/from-60-pages-to-a-single-click/)[From 60 Pages to a Single Click: How Form.io Powered a Government Agency’s Digitization](https://form.io/case-studies/from-60-pages-to-a-single-click/)
# June 15, 2026 [](https://form.io/case-studies/from-six-week-release-cycles-to-same-day-form-changes-patagonia-health/)[From Six-Week Release Cycles To Same-Day Form Changes – Patagonia Health](https://form.io/case-studies/from-six-week-release-cycles-to-same-day-form-changes-patagonia-health/)
# June 15, 2026 [](https://form.io/case-studies/accelerated-development-time-line-by-two-years/)[Accelerated Development Timeline By Two Years](https://form.io/case-studies/accelerated-development-time-line-by-two-years/)
# May 7, 2025 [](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)[The Digital Transformation Of Supporting New Services For The German Public Sector—On Repeat](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)
December 2, 2024 #### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# Why Form.io Requires the MongoDB Document Model (And What Breaks Without It)
*Published:* 2025-11-04
*Author:* Form.io Wizard
*URL:* https://form.io/why-form-io-requires-the-mongodb-document-model/
*Description:* Form.io's document model isn't a vendor preference; it's a schema-evolution requirement that breaks under relational stores.
Form.io requires MongoDB or a compatible equivalent. This is not a preference or a default that you can swap out during installation. The entire data layer assumes the MongoDB document model, query language, and indexing capabilities. Attempting to substitute PostgreSQL, MySQL, or another database will break core functionality in ways that cannot be patched around.
This document explains why the dependency exists, what specifically breaks if you try to work around it, and how to plan your infrastructure accordingly.
## **The Architectural Dependency**
Form.io stores two primary document types: form schemas and submissions. Both are JSON documents with nested structures, variable fields, and arrays of arbitrary depth. MongoDB stores JSON natively. Relational databases do not.
A typical form schema contains a recursive `components` array where each component can contain child components. A Data Grid component might contain five child fields. An Edit Grid inside a Panel inside a Wizard step creates four levels of nesting. The schema must preserve this structure exactly because the Form.io renderer reads it directly to display forms.
```
{
"components": [
{
"type": "panel",
"key": "employeeInfo",
"components": [
{
"type": "editgrid",
"key": "workHistory",
"components": [
{"type": "textfield", "key": "company"},
{"type": "textfield", "key": "title"},
{"type": "datetime", "key": "startDate"},
{"type": "datetime", "key": "endDate"}
]
}
]
}
]
}
```
MongoDB stores this document as-is. A relational database would require either a recursive table structure with joins to reconstruct the hierarchy, or a JSON column that cannot be indexed or queried efficiently. Neither approach matches how Form.io reads and writes schema data.
Submissions follow the same pattern. The `data` object inside each [submission](/form-json-schema-vs-submission) mirrors the form structure, including nested arrays from Data Grids and Edit Grids. MongoDB’s query language can filter, sort, and aggregate across these nested structures. SQL cannot do this without significant preprocessing or denormalization.
## **What Breaks With Relational Databases**
If you attempt to replace MongoDB with a relational database, the following capabilities fail.
**Schema storage and retrieval.** Form.io reads the entire form schema as a single document and passes it to the renderer. The renderer expects the exact JSON structure stored in MongoDB. A relational reconstruction would need to join multiple tables and reassemble the component hierarchy in the correct order. The Form.io server does not contain this logic because it was never designed to work that way.
**Submission queries with nested filters.** The [Form.io API](https://apidocs.form.io/) accepts MongoDB query syntax for filtering submissions. A request like `?data.workHistory.company=Acme` filters on a nested array field. This query syntax is passed directly to MongoDB. Relational databases use SQL, which has no equivalent single-query pattern for filtering inside JSON arrays without database-specific extensions.
**Aggregation pipelines for reporting.** The Data Reporting feature uses MongoDB aggregation pipelines to compute statistics, group submissions, and join data across forms. These pipelines operate on the document structure as stored. There is no abstraction layer that translates aggregation pipelines to SQL.
**Indexing on dynamic fields.** Form schemas vary between projects. One form might have fields named `firstName` and `lastName`; another might have `patientId` and `encounterDate`. MongoDB allows you to create indexes on `data.firstName` or `data.patientId` directly. Relational databases cannot index inside JSON columns in the same way, and creating tables with columns matching every possible form field defeats the purpose of a flexible form builder.
**Atomic document updates.** When a submission updates, Form.io writes the entire `data` object in a single operation. MongoDB handles this atomically. Relational storage would require updating multiple rows across multiple tables within a transaction, adding complexity and failure modes that the Form.io server does not manage.
## **Why Not PostgreSQL JSONB?**
PostgreSQL’s JSONB column type stores JSON documents and supports some querying. Developers familiar with PostgreSQL often ask why Form.io cannot use JSONB instead of MongoDB.
The short answer: JSONB solves storage but not querying, indexing, or the aggregation pipeline.
JSONB stores JSON as a binary format and allows basic operators like -> and ->> to extract fields. You can write queries like:
```
SELECT * FROM submissions WHERE data->>'firstName' = 'Sarah';
```
This works for simple top-level fields. It does not work well for the following scenarios that Form.io requires.
**Nested array queries.** Finding submissions where any element in a nested array matches a condition requires `jsonb_array_elements` and subqueries. The syntax is verbose and performance degrades on large datasets without specialized indexes.
**Dynamic indexing.** Creating a GIN index on a JSONB column indexes the entire document, not specific paths. Path-specific indexes require knowing the paths in advance. Form.io forms have arbitrary field structures defined by users, not by application code.
**Aggregation.** PostgreSQL has no equivalent to MongoDB’s aggregation pipeline. Computing grouped statistics across nested submission data requires extracting data into temporary structures, running standard SQL aggregations, and reassembling results. Form.io’s reporting features assume pipeline operations are available.
**Query language compatibility.** The Form.io API accepts MongoDB query objects. Translating these to PostgreSQL JSONB queries would require a query compiler that handles every MongoDB operator. This compiler does not exist in Form.io because the architecture assumes MongoDB.
## **Why Not Firestore or DynamoDB?**
Cloud-native document databases like Firestore and DynamoDB store JSON-like documents but lack features Form.io depends on.
**Firestore** uses a hierarchical data model with collections and subcollections. It does not support the query flexibility MongoDB provides. You cannot query across subcollections, filter on arbitrary nested fields, or run aggregation pipelines. Firestore also limits document size to 1MB, which large form schemas can exceed when forms contain many components with extensive configuration.
**DynamoDB** is a key-value store with document support. Queries require defining indexes in advance for every access pattern. Form.io’s dynamic query API, where users filter on any field in their submission data, would require indexes on every possible field combination. DynamoDB’s pricing model also charges per read/write operation, which becomes expensive for applications with high submission volumes and frequent queries.
Both databases are designed for specific access patterns defined at application design time. Form.io is a platform where users define their own data structures through form building. The database must support queries on structures that did not exist when the application was deployed. MongoDB does this. Firestore and DynamoDB do not.
## **What You Can Do With Relational Databases**
MongoDB is required for Form.io’s core operation, but that does not prevent you from using relational databases elsewhere in your architecture.
**Synchronize submissions to SQL.** The [webhook action](https://help.form.io/userguide/forms/form-building/actions) sends submission data to external endpoints in real-time. You can build a small service that receives webhooks and inserts data into PostgreSQL, MySQL, or any other database. The [relational database integration guide](https://help.form.io/developers/integrations/relational-databases) documents this pattern.
**Export and transform.** The Export Form Data feature produces JSON and CSV files. You can schedule exports, transform the data, and load it into a data warehouse. This is a batch approach rather than real-time, but it gives you submission data in whatever format your analytics stack requires.
**Query MongoDB alongside SQL.** Many deployments run MongoDB for Form.io and PostgreSQL or MySQL for application data. Your application code queries both databases as needed. This adds operational complexity but lets you use the right database for each workload.
The pattern to avoid is attempting to make Form.io itself run against a non-MongoDB database. That path leads to forking the codebase, rewriting the data layer, and maintaining a divergent version that cannot receive upstream updates.
## **Infrastructure Planning**
If you are evaluating Form.io, plan for MongoDB from the start. [Self-hosted deployments](/features/self-hosted-forms-for-enterprise) require you to provision and manage MongoDB infrastructure.
**MongoDB Atlas** is the managed cloud option. Atlas handles replication, backups, scaling, and maintenance. You connect Form.io to an Atlas cluster using a connection string. This is the lowest operational burden for teams without MongoDB expertise.
**Self-managed MongoDB** gives you full control over the database server. You handle installation, configuration, replication, and backups. This fits organizations with existing MongoDB operations teams or strict requirements about where data resides.
**Replica sets** are required for production deployments. Form.io uses MongoDB transactions in some operations, and transactions require a replica set. A single MongoDB instance works for development but will fail in production scenarios that trigger transaction logic.
For capacity planning, form schemas are small (typically under 100KB each). Submissions vary based on form complexity and file attachment references. A form with 50 fields capturing text data produces submissions around 5-10KB. Plan storage based on submission volume and retention requirements.
The [Form.io server repository](https://github.com/formio/formio) documents MongoDB version requirements and connection configuration. Current deployments should use MongoDB 5.0 or later to ensure compatibility with all Form.io features.
## **When MongoDB Is a Blocker**
Some organizations have policies that prohibit MongoDB. Common reasons include standardization on a single database platform, lack of MongoDB operational expertise, or compliance frameworks that have not been evaluated for MongoDB deployments.
If you cannot run MongoDB or a compatible equivalent, Form.io is not the right choice for your project. This is a hard constraint, not a soft preference. Attempting to work around it will consume engineering time without producing a stable result.
Alternatives to evaluate in this situation:
You do not have to store data in Form.io. Form.io can be used to store your form definitions, but you can use your own submission API to store the data elsewhere.
Form builders that store data in relational databases exist, though they typically sacrifice the schema flexibility and API-first architecture that Form.io provides. You trade the MongoDB requirement for other constraints.
Building a custom form solution on your preferred database is possible if your requirements are narrow. Form.io solves a broad set of problems around form rendering, validation, submission handling, multi-tenancy, and access control. Replicating all of this is substantial work.
Using Form.io in a sandboxed environment with data synchronization to your primary database is a middle path. Form.io runs with MongoDB in its own infrastructure boundary. Webhooks or scheduled exports move submission data into your SQL database for integration with other systems. This adds architectural complexity but can satisfy both Form.io’s requirements and organizational database standards.
## **Related Resources**
- [Form Schemas vs Submissions](/form-json-schema-vs-submission) explains the two document types Form.io stores
- [Self-Hosted](/features/self-hosted-forms-for-enterprise) covers deployment options
- [Data Reporting](/features/data-analysis-reports-mongodb-aggregation-pipelines) documents MongoDB aggregation pipeline access
- [Export Form Data](/features/exporting-csv-forms-data) explains extraction to JSON and CSV
- [Relational Database Integration](https://help.form.io/developers/integrations/relational-databases) guides SQL synchronization
- [Form.io Server Repository](https://github.com/formio/formio) contains configuration documentation
- [API Documentation](https://apidocs.form.io/) details query syntax for submissions
---
# Why You Shouldn't Use Form.io If You Don't Have a Dev Team, HINT: It's Infrastructure Software
*Published:* 2025-10-14
*Author:* Form.io Wizard
*URL:* https://form.io/why-you-shouldnt-use-formio-if-you-dont-have-a-dev-team/
*Description:* Form.io is infrastructure, not a SaaS tool. If you don't have a dev team, you're not the buyer.
Form.io is not a form builder for non-technical users. It is an OEM form runtime designed for software developers who are building custom applications. If you are looking for a tool where marketing can create forms without involving IT, Form.io is the wrong choice. If you need a form live this afternoon and nobody on your team can write JavaScript, Form.io will not help you.
This is not a limitation. It is the design. Form.io solves a different problem than tools like Google Forms, Typeform, or Jotform. Understanding this distinction will save you months of frustration and thousands of dollars in failed implementation.
## **Form.io Requires Developers at Most Stages**
Form.io’s architecture assumes that developers are involved in initial setup, ongoing integration, and production deployment. Here is what each of those stages requires.
**Initial setup requires:**
- Deploying Docker containers to your infrastructure (if self-hosted)
- Configuring MongoDB or a MongoDB-compatible database
- Setting up environment variables for authentication, CORS, and API secrets
- Integrating the [Form.io JavaScript renderer](https://github.com/formio/formio.js) into your application
- Building the application UI that wraps the rendered forms
**Ongoing integration requires:**
- Writing code to handle form submissions in your application logic
- Implementing authentication flows using JWT tokens, OAuth, or SAML
- Connecting forms to your existing databases and services via webhooks or custom actions
- Building custom components when the standard component library does not meet your requirements
- Managing the project hierarchy and permission structure
**Production deployment requires:**
- Monitoring container health and database performance
- Managing SSL certificates and load balancers
- Handling upgrades when Form.io releases new versions
- Troubleshooting API issues and submission failures
- Scaling infrastructure as form volume increases
None of these tasks can be completed by someone who cannot read code or manage servers. If your organization expects to hand Form.io to a business analyst and have them fully integrate forms in production applications, that expectation is incorrect.
See the [deployment guide](https://help.form.io/deployments/deployment-guide) for a detailed look at what self-hosted installation involves. If reading that documentation feels like reading a foreign language, Form.io is not for you.
However, it’s worth noting that for many cases developers themselves do not need to be the ones building the forms. You can hand Form.io’s developer portal to a power user who will be able to build complex, [drag and drop forms](/features/drag-and-drop-form-builder-apis/) without having to code.
## **The Drag and Drop Builder Does Not Replace Development**
Form.io has a visual drag and drop form builder. This creates a misconception that Form.io is a low-code or no-code tool. It’s not.
The builder’s primary function is to create JSON schemas. It does not create the application that displays those forms. It does not build the page layout that surrounds the form. It does not route submission data outside of itself without custom development.
**What the builder does:**
- Provides a visual interface for constructing form schemas
- [Generates the JSON](/features/form-from-json) that the Form.io renderer interprets
- Allows configuration of [validation rules and conditional logic](/features/form-conditional-logic-form-validation)
- Enables non-developers to modify forms after developers set up the system
**What the builder does not do:**
- Create applications
- Build database integrations
- Design page layouts (though there are some limited layout components)
- Replace development work in totality (though it replaces a lot)
The builder is useful because it allows product managers, business analysts, or customer success teams to modify forms without pulling developers off other work. But those non-technical users can only do this after developers have built the application infrastructure that hosts and renders those forms.
Think of it this way: the builder lets you edit a form that already exists in an already-running application. A developer had to build that application first.
## **What Breaks Without Technical Staff**
If you deploy Form.io without adequate developer support, here is what will go wrong.
**Database issues will stop everything.** Form.io requires MongoDB. When queries slow down, when indexes need optimization, when storage fills up, when replication fails, you need someone who can diagnose and fix MongoDB problems. Without that person, your forms stop working and your submissions become inaccessible.
**Container failures will cause downtime.** The Form.io Enterprise server runs as a Docker container. Without someone who understands containerized applications, you cannot keep the system running reliably.
**Integration failures will block business processes.** Form.io sends data to other systems via webhooks and integrations. When those integrations fail, submissions pile up, business processes stall, and someone has to debug the connection. That person needs to understand HTTP requests, authentication tokens, and API error responses.
**Authentication problems will lock out users.** Form.io supports multiple authentication methods: JWT tokens, OAuth providers, SAML, and custom authentication. When users cannot log in, when tokens expire unexpectedly, when SSO breaks, someone needs to trace the authentication flow and identify the failure point. This requires reading code and understanding authentication protocols.
**Custom requirements will not be met.** Every organization eventually needs something that Form.io does not provide out of the box. A specific calculation logic. A custom validation rule. A unique component type. Meeting these requirements means writing code. Without developers, custom requirements become blockers.
**Upgrades will be ignored or fail.** Form.io releases updates regularly. Applying those updates requires pulling new Docker images, testing for compatibility with your customizations, and managing database migrations. Organizations without technical staff either skip updates (accumulating technical debt and security vulnerabilities) or attempt updates and break their systems.
These are not edge cases. They are certainties. Form.io is infrastructure software. Infrastructure software requires operational expertise.
## **Who Should Not Use Form.io**
**Marketing teams creating standalone forms:** If you need a contact form on your website or a survey for customer feedback, use Typeform, Google Forms, or Jotform. These tools create embeddable forms without technical integration work. Form.io is overkill for standalone forms.
**Small businesses without IT staff:** If your company has fewer than five employees and no one with a software development background, Form.io will consume more resources than it provides. The time spent trying to deploy and maintain Form.io would be better spent using simpler tools.
**Organizations expecting immediate results:** Form.io deployments can be done in a day, but full implementations and integrations into your business processes can take weeks to months, not hours. The initial deployment, integration, and testing require sustained developer attention. If you need forms working tomorrow and you are starting from scratch today, Form.io is not the right choice.
**Projects with no budget for ongoing technical support:** Form.io delivers rock-solid stability and is trusted by governments, global banks, and the most demanding business verticals, but it’s not a set-and-forget tool. It provides monthly releases and requires ongoing updates.
**Teams looking for an alternative to hiring developers:** Sometimes organizations evaluate Form.io hoping it will eliminate the need for developers altogether. It will not. Form.io significantly reduces developer time spent on form-specific code and deployments, but it does not eliminate the need for developers. If you cannot hire developers, Form.io does not solve your problem.
For comparison with consumer form tools, see Why Form.io Is Not Google Forms, Jot Form, Typeform, or Retool.
## **Who Should Use Form.io**
Form.io is the right choice for organizations with development teams building form-intensive applications. If any of the following describe you, Form.io probably fits.
**Software companies building SaaS products:** You have developers. You are building a custom application. You need forms throughout your product. You want to stop writing form rendering and submission handling code for every form. Form.io gives you schema-driven data capture that your developers can integrate once and use everywhere.
**Development agencies building client applications:** You build custom applications for clients repeatedly. Many of those applications involve complex forms. You want a repeatable system for form management across projects. Form.io provides that system, and your developers can use it across multiple client engagements.
**Enterprise IT teams building internal applications:** You have a development team responsible for internal business applications. Those applications involve data collection, workflow management, and approval processes. You want to empower business users to modify forms without developer involvement for every change. Form.io allows that division of labor after initial setup.
**Organizations with strict data compliance requirements:** You must keep form data in your own infrastructure for regulatory reasons. You cannot use SaaS form tools that store data on third-party servers. Form.io deploys into your environment so data never leaves your control. But you need developers to deploy and manage it there.
The common thread: all of these organizations have technical staff who can deploy, integrate, and maintain Form.io. The question is not whether you want a form builder. The question is whether you have the technical resources to operate forms as infrastructure.
## **The Minimum Technical Team**
What is the minimum technical capability required to use Form.io successfully?
**For self-hosted deployments:**
- At least one developer familiar with Docker containers and container orchestration
- Database administration capability for MongoDB
- Backend development skills in Node.js or equivalent for building integrations
- Frontend development skills in React, Angular, Vue, or vanilla JavaScript for application integration
- DevOps capability for managing environments, deployments, and monitoring
**For SaaS deployments (Form.io hosted):**
- Frontend development skills for embedding forms in your application
- Backend development skills for handling webhooks and building integrations
- Understanding of REST APIs and JSON data structures
- Ability to read and write JavaScript
Even with Form.io’s SaaS offering (which handles infrastructure for you), you still need developers to build the application that uses Form.io. The hosted option reduces operational burden but does not eliminate the need for technical staff.
**Part-time technical support is usually insufficient.** Form.io implementations are not one-time projects. They require ongoing attention. Plan for dedicated technical ownership or recognize that you will accumulate problems faster than you can solve them.
## **The Cost of Ignoring This Advice**
Organizations that deploy Form.io without adequate technical resources follow a predictable trajectory.
**Months 1-3:** Excitement about the drag and drop builder. Non-technical staff create forms. Everything seems to work. The system appears simpler than expected.
**Months 4-6:** First integration issues emerge. Webhooks fail intermittently. Performance degrades as submission volume increases. Nobody understands why, and nobody can fix it. Workarounds accumulate.
**Months 7-12:** The system becomes unreliable. Business users lose trust. Critical forms fail at critical moments. Leadership questions the decision. Someone suggests migrating to Typeform or Google Forms “just to get something that works.”
**Months 12+:** The organization either invests in proper technical support (often through expensive consultants because the original team lacks the expertise) or abandons Form.io entirely, writing off the implementation investment.
This trajectory wastes six to twelve months and significant budget. It also damages internal trust in technology decisions and makes future enterprise software implementations harder to advocate for.
The honest assessment is this: Form.io is powerful infrastructure for the right organization. Deploying it without the right technical resources is like buying a commercial kitchen when you need a microwave. The capability is there, but you cannot use it, and you have spent far more than necessary for what you actually need.
## **Alternatives If You Do Not Have Developers**
If you have read this far and recognize that your organization lacks the technical resources for Form.io, here are better options.
**For simple surveys and feedback forms:** Google Forms is free and works immediately. Typeform creates visually engaging forms with conditional logic. SurveyMonkey handles more sophisticated survey requirements. None of these require technical integration.
**For forms embedded in marketing websites:** Jotform, Wufoo, and Formstack create embeddable forms with visual builders and handle data storage. They integrate with common marketing tools without code. You can have a working form in an hour.
**For forms in internal business processes:** Microsoft Forms integrates with Office 365 and SharePoint. Google Forms integrates with Google Workspace. If your organization already uses these platforms, the form tools are available and require no additional deployment.
**For application building without code:** Retool, AppSheet, and similar platforms let non-developers build internal applications with forms. They handle data storage, user authentication, and application hosting. The tradeoff is limited customization compared to developer-built applications.
These alternatives involve tradeoffs. They may not support your specific integration requirements. They may not meet compliance needs. They may not scale to your volume. But they work without developers, which means they actually work for organizations that lack developers.
Form.io is the right choice when those alternatives cannot meet your requirements and you have the technical team to operate it. If the alternatives work for you, use them. The best tool is the one you can actually operate.
---
## **Related Documentation**
- Why Form.io is Infrastructure as a Forms Solution, Not an App Builder
- Why Form.io Is Not Google Forms, Jotform, Typeform, or Retool, But Instead a Developer-First Approach to Form Automation
- [Self-Hosted Deployment Guide](https://help.form.io/deployments/deployment-guide)
- [Form.io GitHub Repository](https://github.com/formio/formio)
- [API Documentation](https://apidocs.form.io)
## **Related Features**
- [Drag & Drop Form Builder](/features/drag-and-drop-form-builder-apis/): What the builder does and does not do
- [Authentication Support](/features/secure-authentication-for-enterprise-form-infrastructure): Technical requirements for authentication
- [Integrations](/features/data-integration-tools-for-enterprise-forms): What integration setup involves
- [Fully Deployed](/features/self-hosted-forms-for-enterprise): Self-hosted deployment requirements
- [Multi-Tenancy](/features/platform-as-a-service-paas): Technical architecture for SaaS implementations
---
# Time To Get Serious About HOW To Build AI-Driven Apps For Business Processes
*Published:* 2025-07-07
*Author:* Form.io Wizard
*URL:* https://form.io/time-to-get-serious-about-how-to-build-ai-driven-apps-for-business-processes/
*Description:* Building agentic / AI-driven business apps requires schema-governed intake. UAG and Form.io's JSON model as the substrate.
If you’re a developer building AI-powered business process applications, you already know the stakes. You’re on a timeline and need to deliver huge ROI in an application that’s secure, scalable, and so easy to use that a high school dropout could smash business outcomes with it…something that’s a true bridge between human and machine interactions.
But here’s the gut punch: every hour spent wrestling with clunky integrations, opaque AI agent behavior, or compliance nightmares is costing you and your organization thousands in missed opportunities. Worse, it’s pushing your project closer to another delay.
The pain is real: disjointed systems, unpredictable AI outputs, and ***endless*** custom coding to make it all work. It’s like trying to herd cats while riding a unicycle and juggling flaming torches.
### **The Hidden Costs of AI Chaos**
This is not merely a code problem to be solved.
***It’s about orchestrating complex interactions between AI agents, human users, and enterprise systems.***
Without the right tools, you’re facing:
- **Integration Hell**: Your AI agents need to talk to legacy systems, modern APIs, and everything in between. Each integration is a custom-coded battle, eating up weeks of dev time.
- **Security Risks**: AI agents often need broad access to sensitive data, leaving you exposed to breaches and compliance violations. One misstep could cost millions in fines, or worse, your reputation
- **Opaque AI Behavior**: Everyone already knows AI agents can be unpredictable, hallucinating outputs or making decisions that don’t align with business rules. Without transparency, you’re flying blind.
- **Scaling Struggles**: That shiny AI pilot? It’s a ticking time bomb when you try to scale it across teams or departments. Inconsistent data models and workflows can grind everything to a halt.
- **Team Resistance**: Your non-technical stakeholders may not trust AI-driven processes, and they lack the tools to interact with them effectively, ***in the context of your business***. Adoption stalls and your project fizzles out.
If at any point you said to yourself “I can see that,” then keep reading, because makeshift solutions aren’t going to cut it.
Question: *what if there was a way to cut through all the chaos and place guardrails on everything you need without hiring an army of developers?*
**Form.io: The Developer’s Secret Weapon For AI-Powered Applications That Lets You Take Control Of AI-Workflows**
Form.io isn’t just another tool in your stack. It’s the foundation that makes AI-powered business processes work. It might just be ***THE*** tool.
It’s the bridge between chaotic agents, human users, and enterprise systems that delivers a straightforward, secure, and scalable solution that developers love.
Here’s why:
#### **1. API-First Data Interfaces: Speak AI’s Language Without The Hassle**
AI agents thrive on **structured data**. So much so that ***marketers*** and ***sales people*** on social media are offering AI prompts ***written in JSON*** as lead magnets to their audience. However, getting the agents to play nice with enterprise systems can be a bad dream full of shadows and jump scares.
Form.io solves this by generating a full REST API layer behind every form, every resource, every field, every user, every form action, every project, every submission, the server…everything.
What this means is that there’s no more hand-coding integrations for every system.
Whether it’s a legacy database, a modern cloud platform, or a 3rd-party service, Form.io normalizes data and exposes clean, RESTful endpoints that AI agents can read from and write to without flying off a cliff.
**Why It Matters:**
You eviscerate integration time by weeks, letting you focus on building features, not fighting middleware. Form.io becomes the universal translator for your AI agents, ensuring they speak the same language as your backend systems.
**How To Win:**
Imagine cutting your integration timeline from 6 weeks to 6 days, or your entire timeline [from 6 months to 6 weeks](https://form.io/case-studies/going-to-market-in-6-weeks-with-total-flexibility/). That’s the power of Form.io’s API-first approach.
#### **2. Dynamic UI for Human + AI Collaboration: Make Workflows Feel Natural**
AI agents are powerful, but they need human oversight to shine. Form.io’s schema-driven front end lets you dynamically assemble user interfaces that make hybrid interactions feel like works of software art.
Whether it’s pre-populating forms with AI-generated data or enabling human review of agent outputs, Form.io creates the perfect baton handoff between man and machine.
**Why It Matters:**
Your stakeholders, technical and non-technical alike, get intuitive, user-friendly interfaces that make AI-driven workflows feel like second nature. No more clunky dashboards or confusing UX.
**How To Win:**
Your team builds forms that AI pre-fills with customer data and sales reps validate it in seconds. That’s a level of efficiency you can feel. [Read about the POC](https://form.io/leveraging-generative-ai-agents-to-automate-form-completion/).
#### **3. Rapid Integration Without Rewriting Backends: The Zero-Insanity Approach**
Rewriting backends for AI is not a vacation destination that developers like to visit. Form.io’s configurable middleware connects UIs and AI agents to existing systems, enforcing business logic, validation, and security without having to custom code all of it.
**Why It Matters:**
You integrate AI without touching your backend, deploying faster with fewer headaches.
**How To Win:**
Connect AI-driven analytics to the untouchable, don’t-mess-with-it, don’t-change-anything-in-it ***ERP system*** in days, not months, with the Form.io middleware platform.
#### **4. Tailored, Secure, Auditable Interactions: Stay Compliant, Stay Secure**
AI accessing sensitive data triggers security and compliance concerns. Form.io’s self-hosted, white-labeled architecture gives full control over data residency, access, and governance, integrating with SSO, OAuth, and LDAP. Audit trails track every interaction.
**Why It Matters:**
You meet HIPAA, GDPR, and FedRAMP requirements effortlessly, keeping AI processes secure and auditable.
**How To Win:**
Host the Form.io platform, in which everything meets the highest compliance requirements in the world, deployed in your environment.
#### **5. AI Rehab: Guardrails For AI Autonomy And Hallucinations**
AI agents can hallucinate or act unpredictably. Form.io gets them off the shrooms by enforcing validation rules, conditional logic, and approval workflows, with human review for high-risk decisions.
**Why It Matters:**
You reduce AI errors while maintaining automations’ speed to ensure AI is working for you.
**How To Win:**
Build your own prompt bank using drag and drop fields, accessible via API, and call them when conditions are met to output tailored recommendations, summaries, content, and more.
### **The Predestination Effect**
If you’ve read this far, I don’t think you’ve found this post by accident. You’re a developer. You’re tired of chaos and you’re ready to build AI applications that work. Form.io is the tool you’ve been searching for.
It’s going to feel like it was built for you:
- **Developer-First:** Programmatic APIs, JSON data structures, and enough easy-mode functionality like drag and drop forms and schemas that mesh with your workflows and tech stack.
- **Scales Without The Cost**: You’re only billed per project (collection of related forms and resources), your API/PDF configuration, and optional enterprise addons. You’re never billed per form, per submission, per end user of forms, per form builder, per developer, per API call, or any other usage-based metric.
- **Builds Trust**: Transparent, open source-based code base means you can extend and customize as you like with human-in-the-loop controls that win over non-developer resources and stakeholders.
- **Proves ROI**: Rapid prototyping and integrations can show value in days, or [even minutes like these guys saw](https://form.io/case-studies/building-a-crm-took-2-months-instead-of-2-years/).
- **Self-Hosted Control**: Deploy in your infrastructure for security, compliance, and 100% ownership.
Two last things.
First, I’ve already hinted at this, but I want you to have clarity about this ONE thing. Explicit clarity:
Form.io does not interfere with how you already do things. It does require MongoDB, but you don’t even have to store data in it and we have an SQL connector anyway. Remember, it’s ***middleware***. Keep using your tech stack, your tools, your services, your whatever.
Second, we’re confident you’ll see immediate value and we’re happy to do a technical deep dive with you at no charge, so don’t wait to talk to us, especially if you’re already in the process of building. You’re not going to want to write another line of code until you see what it can do.
---
# E-Sign Plus: Prove The Signed Data Stayed Intact
*Published:* 2026-08-31
*Author:* Veronika Druck
*URL:* https://form.io/e-sign-plus-proven/
*Description:* Ad squeeze landing page for Form.io E-Sign+, aimed at regulated and enterprise teams that need cryptographic digital signatures attached to submission data, form context, APIs, revision-aware workflows, and customer-controlled deployment boundaries.
For Regulated Form Workflows
# Prove The Signed Data Stayed Intact
## For teams who have to prove a signed record is still the record that was signed, on their own infrastructure, with their own keys.
The signature attaches to the submission data itself. Change the data, and the signature breaks.
## The Signature Lives Somewhere Else
### Document-first signing separates the proof from the record your application actually runs on.
Your team captures data in one system, exports it into a document flow, waits for a separate signature event, then has to reconcile the signed artifact back to the original submission. The signature may be complete, but the workflow now depends on two records staying aligned.
That gap gets worse when signed values feed downstream approvals, eligibility checks, underwriting, case management, or customer service workflows. Teams are left asking whether the document, the submission, the form revision, and the visible audit trail still describe the same transaction.
The risk surfaces the day a signed record has to survive an audit, a dispute, or a regulator's question. If the proof lives in a vendor's account, a PDF export, or a custom integrity layer, someone on your team has to explain where the signed data sits and what would invalidate it, under pressure, on the record.
You can build around it. It is rarely small. Cryptographic signing, key management, revision-aware validation, signature stamps, and API access all become infrastructure you own, patch, and defend the moment signed data has to stay trustworthy.
The stronger path is to bind signature proof to the form submission itself.
## Enterprise Form Infrastructure In Production     E-Sign+ Signs The Submission Layer
### E-Sign+ signs the submission data itself, not a document generated from it. The signature stays with the native record, the API, and the form revision inside the deployment you control.
### Signed Data Stays Yours
E-Sign+ is built for self-hosted Form.io environments, so signature records and protected submission data remain inside the customer's deployment. Teams do not have to move sensitive forms into an external signature service just to complete a regulated approval, consent, disclosure, or attestation step.
### The Proof Comes Back With The Record
Signed data can be accessed through the native Form.io submission ID and APIs. That keeps the signature attached to the record your application already uses, instead of forcing developers to reconcile a detached document artifact with the form workflow that created the data.
### Change The Data, Break The Signature
Teams can configure signatures to protect selected fields, all form data, or chosen submission properties. When protected values or context change, the digital signature becomes invalid and the data is expected to be signed again, making integrity failure visible instead of hidden.
##  E-Sign+ ties signature proof to submission data, form context, and customer-controlled key strategy. "Speed to market using Form.io worked fantastically well. We didn't have to spend 80% of our time building our own solution and instead could focus our dev time on things proprietary to us." Cory Linton, CEO of Edify.ai Avoid Custom Signature Plumbing "Of all the systems we use to deliver our end products, Form.io has been probably the most straightforward and issue free to use, with excellent support." Dept. of Justice, Ireland Fit For Regulated Delivery "Speed to market for setting up a form or application is what we liked best. Form IO allows us to set up a form with easy front end validation and business logic, instant API accessable database." Neal G., Technical Administrator for State of Ohio Forms And APIs Together The Fair Questions Come First
### E-Sign+ is not for every signature workflow, and that distinction matters before a team builds around it.
#### Does E-Sign+ Cost Per Signature or Envelope?
No. E-Sign+ is licensed as part of your self-hosted Form.io environment. There is no per-envelope or per-document meter, so signature volume is a capacity question inside your own deployment rather than a per-transaction line item.
#### Is This A PDF Signature Tool?
Secondarily. E-Sign+ is decoupled from PDFs. It supports workflows that export to PDF when needed, but the core value is an immutable snapshot of form data inside the application. That matters when the submission record, not the document file, is the system of truth.
#### Who Controls The Signing Keys?
The customer supplies the private key strategy. E-Sign+ can use a private key configured in the enterprise server deployment or project-level integration with AWS KMS. The useful promise is not outsourced trust. It is cryptographic proof inside the environment your team governs.
#### Can Any Form Use It?
E-Sign+ is an enterprise module for eligible self-hosted environments licensed for both the Security Compliance Module and E-Sign+. Configuration also depends on submission revisions and form revisions using the original form revision when viewing submissions, because signature validity depends on revision-aware context.
## Find Out What You Should Be Signing
### Book a short working session and Form.io will help identify where E-Sign+ fits into your form, submission, API, revision, and key-management model.
You will leave with a clearer view of what data needs to be signed, which fields or submission properties should be protected, how signature invalidation should work, and whether your current self-hosted license path supports E-Sign+. No production migration decision is required on the first call.
Bring one workflow. You will leave knowing what has to be signed for the record to hold up.
## Keep Signed Data Attached To Reality
When signatures drift away from the submission layer, every review has to reconstruct what was signed and whether it still matches. E-Sign+ makes integrity part of the form workflow itself.
Per Form.io documentation, E-Sign+ verifies that the signed data and its context have not changed since signing.
---
# AI Governance for Runtime: Govern Production Agents Without Losing Control
*Published:* 2026-08-06
*Author:* Veronika Druck
*URL:* https://form.io/ai-governance-for-runtime/
*Description:* Ad squeeze landing page for Form.io AI Governance for Runtime, aimed at platform, security, and operations teams moving AI agents into production workflows. The page focuses on Universal Agent Gateway as the runtime governance layer for dynamic context, authenticated access, RBAC-aware data access, validation, actions, and auditability.
AI governance for runtime
# Govern Production Agents Without Losing Control
## For platform, security, and operations teams moving AI agents from demos into real workflows where data access, validation, permissions, and auditability matter.
See how Form.io Universal Agent Gateway gives production agents governed context and controlled access to the same forms, resources, actions, APIs, and rules your human workflows already use.
## Production Agents Break When Context Lives Outside The System
### An agent can reason fluently, but it still needs governed data, real permissions, validated actions, and an audit trail before it belongs inside enterprise operations.
The hard part of enterprise AI is not getting an agent to answer a prompt. The hard part is letting that agent touch production systems without creating a second, weaker path around the rules your teams already enforce.
Most teams try to solve runtime governance with prompt instructions, copied data, custom glue services, or one-off agent integrations. Those approaches can work in a demo, but they drift as soon as forms change, permissions change, or the workflow moves across systems.
Runtime agents need more than a smart model. They need dynamic context from the system of record, authenticated access, role-aware boundaries, validated submissions, controlled actions, and logs that explain what happened.
Universal Agent Gateway is the runtime layer for that problem. It turns existing Form.io JSON definitions into agent context and gives agents a governed way to read, validate, route, and act on structured workflow data.
## Built for enterprise teams moving AI agents into governed operations     Put A Runtime Gateway Between Agents And Enterprise Data
### UAG uses Form.io's schema-driven foundation to give production agents dynamic context, authenticated access, validation, actions, and auditability through the same controlled workflow layer.
### Dynamic Context From Living Schemas
UAG interprets Form.io JSON definitions for agents the way rendered forms interpret them for people. When a form, field, validation rule, resource, or workflow changes, the agent context follows the governed definition instead of depending on stale prompt instructions.
### Authenticated, Role-Aware Access
Production agents should not operate through a shadow permission model. UAG lets agents authenticate through the enterprise boundary, inherit RBAC-aware access, and work with governed forms and resources instead of loose copies of sensitive data.
### Validated Actions With Audit Evidence
Agent output can become structured submissions, trigger configured actions, and move through existing workflow paths. The interaction is authorized, validated, logged, and tied back to the agent's identity so review does not depend on trusting a black box.
## 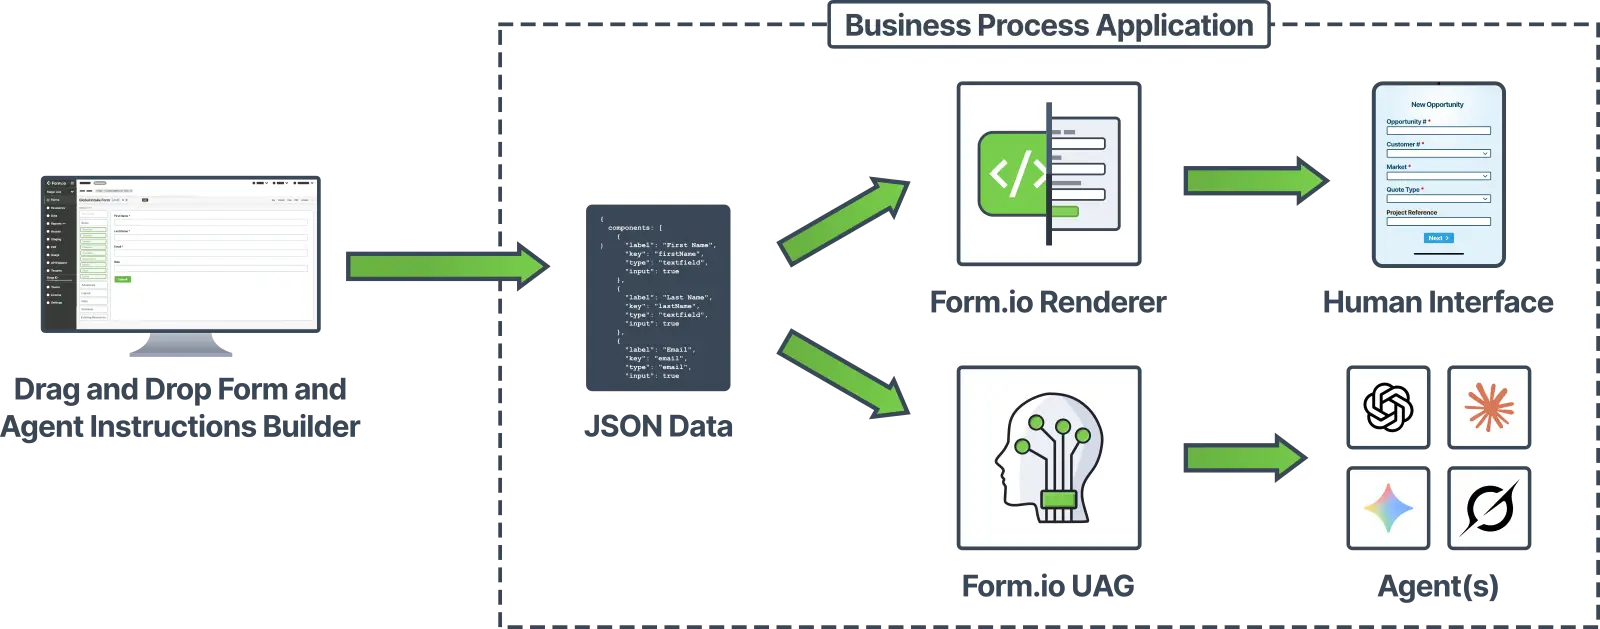 UAG turns Form.io JSON definitions into runtime context, access rules, validation paths, actions, and audit evidence for production AI agents. "Unmatched capability in its product class, particularly for complex use cases where complete ownership of your data is a must." Midnight Health Control over complex data "Of all the systems we use to deliver our end products, Form.io has been probably the most straightforward and issue free to use, with excellent support." Dept. of Justice, Ireland Confidence in complex delivery "Speed to market using Form.io worked fantastically well. We didn't have to spend 80% of our time building our own solution and instead could focus our dev time on things proprietary to us." Cory Linton, CEO of Edify.ai More time on proprietary work Runtime Governance Starts After The Demo
### UAG governs what production agents can see, validate, submit, route, and trigger after an AI workflow is live.
#### Does UAG replace the application stack?
No. UAG sits between agents and the Form.io-powered data and workflow layer. Your team still owns the surrounding application, deployment model, integrations, and operational policy.
#### What changes when a form changes?
The governed JSON definition changes the context an agent receives. A new field, validation rule, role boundary, or workflow path becomes part of the agent-facing contract without retraining a model or rebuilding a parallel AI configuration layer.
#### Can agents act on live workflow data?
Yes, when they are authorized to do so. UAG is built for agents that need to discover relevant forms and resources, assemble valid submission data, respect configured access boundaries, and trigger controlled actions into downstream systems.
## Map Your Runtime Agent Governance Path
### Book a short working session and Form.io will help identify where UAG belongs between your agents, governed data, workflow actions, and production systems.
Bring one agentic workflow your team wants to move beyond the demo stage. Form.io will map where the agent needs context, where it needs authenticated access, where validation must happen, and which actions must remain controlled and auditable.
If the problem is production-agent governance, this is the right conversation: make the live workflow rules available where agents read, decide, submit, route, and trigger work.
## Let Agents Act Through The Same Rules Humans Follow
Production AI only becomes useful when agents can operate on real workflow data without bypassing the controls that make the system trustworthy. UAG gives agents dynamic context, governed access, validation, actions, and audit evidence from the same Form.io foundation.
The goal is not to let every agent improvise a new operating layer. The goal is to extend the governed data and workflow infrastructure you already use so agents become controlled participants in the process.
---
# AI Toolset For Developers: Give Coding Agents The Right Build Patterns
*Published:* 2026-08-06
*Author:* Veronika Druck
*URL:* https://form.io/ai-toolset-for-developers/
*Description:* Ad squeeze landing page for Form.io AI Toolset For Developers, aimed at developers and platform teams using AI coding agents. The page focuses on MCP Server, Form.io Skills, and the Agentic Coding Plugin as developer-layer tools for building form-driven applications with Form.io patterns.
AI toolset for developers
# Give AI Coding Agents The Right Build Patterns
## For developers and platform teams using Claude Code, Cursor, Windsurf, and MCP-aware tools to build form-driven applications without letting every prompt invent the architecture.
See how the Form.io AI Toolset gives coding agents access to real forms, resources, roles, actions, APIs, and reusable implementation guidance inside the developer workflow.
## AI Coding Speed Breaks When Every Agent Starts From Scratch
### Developers can move faster with coding agents, but generated form applications still need shared data models, access rules, actions, and API patterns.
A coding agent can create a working form in minutes. That is useful. The risk starts when each prompt also invents the resource structure, validation rules, role model, submission path, action behavior, and front-end integration pattern.
One developer asks for a customer intake workflow. Another asks for a claim form. A third asks for an internal approval wizard. Without a shared Form.io-aware toolset, each agent can produce a different interpretation of how forms, APIs, resources, and permissions should fit together.
That is not a runtime-agent problem. It is a developer workflow problem. The code may compile, the form may render, and the demo may pass, while the underlying application pattern drifts away from the way your team actually uses Form.io.
Developers do not need another wiki page telling them to be careful with AI-generated work. They need the coding environment itself to understand the Form.io primitives the application is supposed to use.
The Form.io AI Toolset gives agents a better starting point: real platform access, reusable skills, and coding-environment integration built around Form.io's schema-driven foundation.
## Built for enterprise development teams that need repeatable application patterns     Bring Form.io Into The Agentic Coding Workflow
### The developer toolset combines MCP access, Form.io Skills, and the Agentic Coding Plugin so AI coding agents build against real Form.io primitives instead of guessing from general prompt context.
### MCP Gives Agents Real Platform Access
The Form.io MCP Server exposes first-party operations for forms, roles, actions, project export, and project import. Agents can inspect and scaffold against the Form.io deployment your team actually uses instead of inventing a disconnected model from prompt memory.
### Skills Carry The Form.io Pattern
The skill library gives coding agents guidance for application planning, form building, resource planning, JSON schema authoring, actions, auth, SDK usage, API usage, and framework implementation. The agent has a Form.io-aware path to follow before it writes.
### The Plugin Puts It In Claude Code
The Form.io Claude Code plugin bundles the MCP Server and the skill library into the developer environment. Developers can ask for forms, resources, actions, access controls, project templates, or embedded UI work while the agent reasons in Form.io primitives.
## 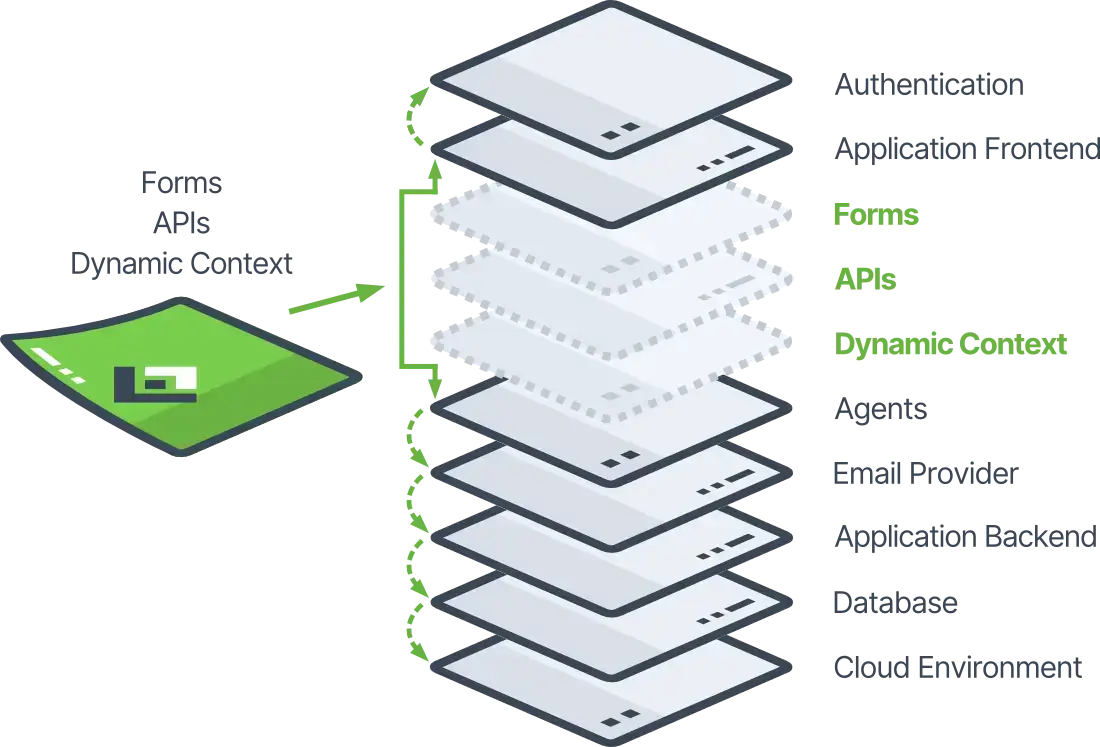 The developer toolset gives AI coding agents access to Form.io primitives, reusable skills, and coding-workflow integration so generated forms, resources, actions, and APIs follow the same application pattern. "Speed to market using Form.io worked fantastically well. We didn't have to spend 80% of our time building our own solution and instead could focus our dev time on things proprietary to us." Cory Linton, CEO of Edify.ai More time on proprietary work "Of all the systems we use to deliver our end products, Form.io has been probably the most straightforward and issue free to use, with excellent support." Dept. of Justice, Ireland Confidence in complex delivery "Speed to market for setting up a form or application is what we liked best. Form IO allows us to set up a form with easy front end validation and business logic, instant API accessable database." Neal G., Technical Administrator for State of Ohio Fast form-to-API setup Developers Still Own The Application
### The AI Toolset does not replace engineering judgment. It gives agents a governed Form.io surface to work from before human review begins.
#### Does this replace architecture review?
No. Developers still own the application boundary, release process, integration choices, and code review. The value is that AI-generated work starts with Form.io-aware primitives for forms, resources, actions, access, APIs, and schema instead of generic assumptions.
#### What if our team already uses Claude Code, Cursor, or Windsurf?
That is the intended context. The standalone MCP server can work with MCP-aware clients, while the Form.io plugin brings the MCP Server and Skills directly into Claude Code. The point is to meet developers where agentic coding already happens.
#### Can agents build complete applications on this?
They can build Form.io-backed application pieces such as data models, forms, wizards, resources, actions, access controls, project templates, and embedded UI work. The surrounding application stack still belongs to your team.
## Map Your Developer AI Tooling Path
### Book a short working session and Form.io will help identify where MCP, Skills, and the Agentic Coding Plugin fit into your developer workflow.
Bring one form-driven workflow your team wants AI help building. Form.io will map which forms, resources, roles, actions, APIs, SDK patterns, and project templates the coding agent should work from.
If the problem is AI-generated development drift, this is the right conversation: make the Form.io pattern available where developers already prompt, plan, scaffold, and review.
## Let Coding Agents Build With The Same Form.io Foundation
AI coding tools can accelerate delivery, but speed only helps when the generated work follows a pattern your developers can maintain. Form.io gives agents a governed developer path through MCP access, Skills, and coding-environment integration.
The public formio/ai repository describes the toolset for Form.io primitives including forms, resources, roles, group permissions, field-based ACLs, server-side actions, project templates, SDK usage, API usage, and framework implementation.
---
# Accessibility: Build Forms That Hold Up under WCAG Review
*Published:* 2026-08-06
*Author:* Veronika Druck
*URL:* https://form.io/accessibility/
*Description:* Ad squeeze landing page for Form.io Accessibility, aimed at government, healthcare, and enterprise teams that need WCAG 2.1 AA or Section 508 aligned forms, accessibility-first component behavior, USWDS template support, and governance over what form authors can build.
Accessible forms for regulated teams
# Build Forms That Hold Up under WCAG Review
## For government, healthcare, and enterprise teams that need WCAG 2.1 AA or Section 508 alignment without rebuilding form accessibility from scratch.
See how Form.io keeps accessibility tied to components, rendering, templates, and form governance instead of leaving every form to a one-off audit cycle.
## Accessibility Breaks Inside the Form Details
### Labels, errors, focus behavior, keyboard navigation, and dynamic fields all have to work together before a form is truly usable.
Most teams do not fail accessibility because they forgot that it matters. They fail because every new form introduces dozens of small requirements: labels must be programmatically connected, required states must be announced, help text must be reachable, and validation errors must make sense outside a visual layout.
The problem compounds when forms are built across departments. One team fixes focus order, another changes component behavior, another adds conditional logic, and the resulting form becomes difficult to defend during accessibility review because the rules are not enforced at the form layer.
For public-facing government services, healthcare intake, employee systems, and regulated customer portals, accessibility gaps become procurement, legal, and reputational risk. A form that cannot be completed with assistive technology is not only frustrating. It can block access to the service itself.
Retrofitting every form after an audit is expensive because the work happens too late. Teams have to inspect component markup, rewrite instructions, rework validation messages, and retest the same patterns every time a form changes.
Accessible forms need reusable guardrails inside the system that builds and renders them.
## Built for accessibility-sensitive public and enterprise services     Keep Accessibility Inside the Form Layer
### Form.io is accessibility-first, giving teams accessible component behavior, USWDS template support, and builder constraints that help keep form authors inside a tested path.
### Use Tested Component Patterns
Form.io supports form building with components tested against WCAG 2.1 AA expectations. That helps teams avoid fields and interaction patterns that depend on visual-only behavior, unsupported focus handling, or controls that cannot be used reliably with assistive technology.
### Render with Accessible Templates
Form.io supports accessible rendering through the US Web Design System template, including associated labels, ARIA attributes, and markup patterns designed for federal accessibility contexts. The form can stay dynamic while the output follows a more defensible accessibility structure.
### Govern What Authors Can Build
Accessibility is easier to sustain when authors are not free to choose every possible component pattern. Form.io lets platform teams guide form builders toward approved components, validation behavior, labels, and templates while still supporting the workflows each department needs.
##  Form.io connects accessible components, rendering behavior, templates, and authoring guardrails inside the same form infrastructure. "Speed to market using Form.io worked fantastically well. We didn't have to spend 80% of our time building our own solution and instead could focus our dev time on things proprietary to us." Cory Linton, CEO of Edify.ai Less custom form infrastructure "Of all the systems we use to deliver our end products, Form.io has been probably the most straightforward and issue free to use, with excellent support." Dept. of Justice, Ireland Confidence for public services "Speed to market for setting up a form or application is what we liked best. Form IO allows us to set up a form with easy front end validation and business logic, instant API accessable database." Neal G., Technical Administrator for State of Ohio Fast controlled form delivery Accessibility Questions Deserve Direct Answers
### Compliance-sensitive teams need to know what the platform handles, what still belongs to the implementation team, and where testing remains necessary.
#### Does This Guarantee Every Form Is Accessible?
No. Form.io provides accessible building blocks, renderer behavior, and template support. Form design still matters. Labels, instructions, content order, error language, surrounding application markup, and real assistive-technology testing still affect the final accessibility outcome.
#### Can We Use This for Section 508 Work?
Form.io’s public accessibility materials specifically address WCAG 2.1 AA and Section 508 use cases, including the USWDS template for federal accessibility contexts. The final compliance position still depends on your deployment, forms, content, application shell, and review process.
#### Will Form Authors Need New Rules?
Usually, yes. Accessible infrastructure works best when authors know which components are approved, how labels and instructions should be written, and when a field pattern requires review. Form.io helps enforce the technical path, but governance makes it repeatable.
## Map Your Accessibility Requirements
### Book a working session and Form.io will help compare your form requirements against the accessibility-first rendering path and authoring controls.
Bring one accessibility-sensitive form or workflow. Form.io will review the form type, users, required standard, component patterns, dynamic behavior, template needs, and deployment model. The goal is to identify whether accessibility should be handled through Form.io’s module, custom implementation work, or a hybrid path.
The first step is reversible: map the requirement before committing implementation time.
## Make Accessible Forms Easier to Sustain
Accessibility cannot depend on every form author remembering every technical rule. Put more of the accessibility path inside the components, renderer, templates, and governance model your teams already use.
"Of all the systems we use to deliver our end products, Form.io has been probably the most straightforward and issue free to use, with excellent support." — Dept. of Justice, Ireland
---
# Turn PDF Workflows into Governed Digital Web Forms
*Published:* 2026-08-06
*Author:* Veronika Druck
*URL:* https://form.io/pdf-forms/
*Description:* Ad squeeze landing page for Form.io PDF Forms, aimed at operations and IT teams that need to transform legacy PDF workflows into governed digital web forms, collect structured submissions, connect PDFs to data, and generate customizable document outputs.
PDF forms for enterprise operations teams
# Turn PDF Workflows into Governed Digital Web Forms
## For operations and IT teams that need to modernize document based workflows, collect structured data online, and generate controlled PDF outputs from the same form infrastructure.
See how Form.io connects PDF documents, digital web forms, submissions, APIs, and workflow actions without treating PDF management as a separate island.
## PDFs Are Where Modern Digital Workflows Start to Break
### The document looks official, but the data behind it often moves through manual entry, disconnected files, and brittle handoffs.
Enterprise teams rarely get to abandon PDFs just because they modernize intake. Agencies, insurers, healthcare teams, financial services groups, and internal operations teams still need applications, confirmations, reports, signed packets, legacy document formats, and pixel-aligned outputs.
The hard part is not only generating a PDF. It is keeping the PDF tied to the form schema, submitted data, validation rules, API access, permissions, and workflow logic that make the record trustworthy.
PDFs are usually where modern digital workflow benefits begin to fall down. The front-end form may be online, but the document step can still force teams back into re-entry, email routing, manual export, and reconciliation when the form changes.
That creates friction for users and risk for the business. A PDF that cannot trace back to governed submission data becomes another document to manage instead of part of the application workflow.
PDF forms need to be connected to the same controlled intake, data, and workflow layer as every other enterprise form.
## Built for document-heavy enterprise workflows     Connect PDF Documents to the Data Layer
### Form.io helps teams transform legacy PDF processes into digital web forms, while keeping document outputs connected to JSON-driven forms, submissions, APIs, and actions.
### Output Digital Submissions
Form.io web forms capture submissions as structured digital records that can move through APIs, actions, exports, and downstream systems. The PDF can remain connected to the submitted data instead of becoming the only record of the workflow.
### Auto-Convert Existing PDFs
Teams can start from an existing PDF and convert it into a digital web form path instead of manually rebuilding the workflow from scratch. The legacy document remains useful, while the collection layer becomes structured, governed, and easier to connect.
### Design Customizable Outputs
The PDF Template Designer helps teams decide what submitted data appears in the generated document and how it should be formatted. That matters when the output is a report, application, confirmation, packet, or compliance record.
##  Form.io keeps PDF input and output connected to the same form schema, submission data, API access, and workflow layer. "We had the whole thing up and running in 6 weeks, that includes us building our side AND integrating into Form.io. It was going to take 6 months if we did it ourselves." Hans Morefield, CEO of CHESS Health Document-heavy workflows shipped faster "Of all the systems we use to deliver our end products, Form.io has been probably the most straightforward and issue free to use, with excellent support." Dept. of Justice, Ireland Confidence in complex delivery "Speed to market for setting up a form or application is what we liked best. Form IO allows us to set up a form with easy front end validation and business logic, instant API accessable database." Neal G., Technical Administrator for State of Ohio Fast form-to-API setup The PDF Question Is Really a Workflow Question
### Teams need to know how document output, data capture, APIs, permissions, and downstream systems stay aligned.
#### Do we have to rebuild every PDF as a web form?
No. Some workflows should start as responsive webforms and generate PDF outputs later. Others need PDF-first forms where a legacy PDF remains the visual background. The right implementation depends on who fills the form, what downstream system needs the data, and whether the final document must match an existing format.
#### What happens to the submitted data?
The PDF should not become the only source of truth. Form.io submissions remain structured records that can be accessed through the platform, APIs, exports, actions, and integrations according to the permissions and deployment model your team defines.
#### Can this fit regulated document workflows?
Form.io is often a fit when document workflows need customer-controlled deployment, structured records, API routing, revision-aware forms, and permission boundaries. The compliance answer still depends on your environment, modules, controls, and implementation requirements.
## Map Your PDF Workflow
### Book a working session and Form.io will help identify whether your PDF process should start from a webform, a PDF-first form, a custom template, or a hybrid model.
Bring one PDF-heavy workflow. Form.io will walk through intake, validation, submission storage, document output, API access, role boundaries, and downstream routing. The goal is to understand the architecture before your team commits to another document workaround.
If Form.io is not the right layer for the workflow, you will know before implementation planning begins.
## Keep the PDF, Fix the System Around It
PDFs are not disappearing from enterprise operations. The question is whether they stay disconnected from the application layer or become part of governed form infrastructure.
Form.io helps teams collect structured data, render PDF outputs, overlay existing documents, and route submissions through APIs and actions without losing control of the workflow behind the document.
---
# AI Toolset: Give AI Development A Governed Build Path
*Published:* 2026-08-06
*Author:* Veronika Druck
*URL:* https://form.io/ai-toolset/
*Description:* Ad squeeze landing page rewrite for Form.io AI Toolset, aimed at platform, architecture, and engineering teams adopting AI coding agents. The page clearly separates build-time developer-layer governance through MCP Server, Skills, and Agentic Coding Plugin from runtime governance through Universal Agent Gateway (UAG).
AI toolset for enterprise application control
# Give AI Development A Governed Build Path
## For platform, architecture, and engineering leaders adopting AI coding agents without letting every prompt invent a new form, API, permission, and workflow pattern.
See how Form.io separates build-time AI development governance from runtime agent governance, while keeping both tied to the same schema-driven foundation.
## AI Coding Speed Exposes The Build-Time Governance Gap
### Before UAG ever governs a production agent, you need a way to keep AI-generated application work from drifting during development.
An AI coding agent can create a form, scaffold a resource, wire an endpoint, and draft workflow logic before architecture review catches up, which is useful. The risk is that each agent makes its own decisions about data models, validation, RBAC, actions, and API patterns.
AI has not changed the underlying problem. It has made the existing requirements problem easier to see. You can move faster with Claude Code, Cursor, Windsurf, and other agentic coding tools, but the same business workflow can still become five incompatible implementations if every prompt invents its own model for intake, permissions, actions, and review.
This is development-layer governance. The concern is not a production agent acting on live data yet. The concern is AI-generated application infrastructure that looks complete while quietly bypassing the patterns you need every build path to share.
Prompt rules and code reviews still matter, but they are a weak standardization layer for agentic development. The stronger control point is the infrastructure layer where your forms, resources, APIs, actions, RBAC, and submissions already meet.
You need governed build-time primitives before runtime governance ever becomes the question.
## Built for enterprise application control at scale     Separate Build-Time Governance From Runtime Governance
### Form.io's AI Toolset gives your coding agents governed access to the development layer through MCP, Skills, and the Agentic Coding Plugin. UAG is different: it governs production agent workflows at runtime through dynamic context, guardrails, and controlled data access.
### MCP Gives Coding Agents Governed Access
The Form.io MCP Server connects your AI coding agents to a self-hosted Form.io deployment so they can read, create, and scaffold forms, resources, actions, APIs, and project structures inside your enterprise boundary. The agent builds against real platform primitives instead of fabricated prompt context.
### Skills Carry The Development Pattern
Form.io Skills give your AI coding agents reusable guidance for application orchestration, form building, resource planning, JSON schema, actions, auth, API usage, SDK usage, and framework implementation. They reduce prompt-by-prompt improvisation by making your approved development pattern easier to follow.
### UAG Governs Production Agents
UAG is the runtime governance layer, not just another developer tool. It gives production agents dynamic context, guardrails, authentication, RBAC-aware data access, validation, and auditability when agents interact with live business workflows.
##  Build-time tools standardize what your agents generate. UAG governs what production agents can see and do at runtime. The shared foundation is Form.io schema-driven application infrastructure. "Speed to market using Form.io worked fantastically well. We didn't have to spend 80% of our time building our own solution and instead could focus our dev time on things proprietary to us." Cory Linton, CEO of Edify.ai More time on proprietary work "Of all the systems we use to deliver our end products, Form.io has been probably the most straightforward and issue free to use, with excellent support." Dept. of Justice, Ireland Confidence in complex delivery "Speed to market for setting up a form or application is what we liked best. Form IO allows us to set up a form with easy front end validation and business logic, instant API accessable database." Neal G., Technical Administrator for State of Ohio Fast form-to-API setup The Layer Boundary Matters
### The strongest AI governance story is clear about which layer is being governed and when.
#### Does the AI Toolset replace architecture review?
No. MCP, Skills, and the Agentic Coding Plugin give your AI-assisted builders a governed foundation to work against, but you still own architecture, deployment, integration boundaries, and release. The value is that generated work starts closer to the right Form.io primitives before human review begins.
#### What if you already use Claude Code, Cursor, or Windsurf?
That is the point. The build-time toolset is meant for the environment where agentic coding already happens. MCP gives tools access, Skills carry platform guidance, and the plugin brings both into your coding workflow so generated form applications follow patterns you can maintain.
#### Is runtime agent governance the same problem?
No. Runtime governance is a different control surface. MCP, Skills, and the Agentic Coding Plugin help you generate better Form.io-backed applications. UAG governs production agents operating against live systems, with dynamic context, RBAC-aware access, validation, actions, and audit trails.
#### Should the enterprise build this from scratch?
Usually, no. Enterprises often do not want to build every layer of form, API, permission, and workflow infrastructure themselves. They want to buy what already works, then keep enough control to fit their security, deployment, integration, and governance requirements.
## Map The Right AI Governance Layer
### Book a short working session and Form.io will help separate development-layer AI governance from runtime agent governance in your application stack.
Bring one AI-built or AI-planned workflow. Form.io will map where coding agents need MCP access, where Skills should standardize development, where the Agentic Coding Plugin fits, and where UAG is the better runtime control layer for live agent access.
If the issue is build-time drift, the AI Toolset may be the right conversation. If the issue is production agent behavior, UAG may be the right layer instead.
## Let AI Build Fast Without Blurring The Governance Layer
AI-assisted development can accelerate delivery, but it does not remove your responsibility for data collection, form behavior, validation, permissions, workflow actions, and release control. You can build almost anything with AI. The question is whether the foundation keeps the work in check once the prototype becomes part of your application.
The existing problems have not changed: requirements still need structure, sensitive data still needs governance, and form-driven workflows still need patterns you can operate after launch. AI has simply made it more evident that you need the right tools and stack before speed outruns review.
Form.io gives your coding agents a governed development path, then uses UAG when production agents need runtime governance.
The public formio/ai repository describes the developer-layer toolset: Claude Code plugin, MCP server, and Skills for Form.io primitives including forms, resources, roles, actions, APIs, auth, SDK usage, and framework implementation.
---
# Give Internal or External Customers Controlled Form Creation Inside Your Application
*Published:* 2026-08-06
*Author:* Veronika Druck
*URL:* https://form.io/formio-enterprise-form-builder-module/
*Description:* Ad squeeze landing page for Form.io Enterprise Form Builder Module, aimed at enterprise IT leads, engineering managers, and platform architects who need embedded, branded, configurable form creation for internal or external customers without routing every form variation through custom development.
Embedded form building for enterprise platforms
# Give Internal or External Customers Controlled Form Creation Inside Your Application
## For software teams that need self-service form building without handing customers a separate portal or losing control of schema, permissions, and workflow behavior.
See how embedded form creation changes the support, product, and engineering equation.
## Every Custom Form Request Hits Engineering
### When forms live outside the application model, every new customer workflow becomes a product, support, and governance problem.
A customer needs one more intake screen, a different field label, or a form that matches how their team actually works. Product calls it small. Support says it is urgent. Engineering has to decide whether this belongs in the roadmap, a one-off branch, or a brittle admin setting.
The first request is manageable. The fiftieth becomes a queue of form changes that distracts the team from the application itself. Each variation creates another place for data shape, validation, permissions, and downstream workflow behavior to drift from the platform standard.
Leadership feels it when customer implementation slows down, support headcount rises, or a regulated customer asks who can change form fields and what happens to the data afterward. The issue stops being interface polish and becomes operational control at the edge of the product.
Most teams try a settings panel, a generic form tool, or a request process. Those help until customers need the builder inside the product, with branded UX, allowed components, controlled data, and the same workflow path the application already depends on.
The better answer is customer autonomy constrained by your application architecture.
## Used where form control matters at scale     Embed the Builder, Keep the Form System Governed
### Form.io's Enterprise Form Builder Module lets teams expose form building inside their own application experience. Customers get self-service creation while your platform keeps control over components, schema, roles, workflows, and the branded experience.
### Customers Build Inside Your Product
The builder is embedded directly into your application instead of sending users to a separate form portal. You decide which form-building experience they see, how it is branded, and which controls are exposed. That turns form creation into a product capability instead of a support ticket or a custom engineering request.
### Shape the Builder Around Your Product
EFBM can be branded, configured, simplified, and embedded directly into the application experience you own. You decide which controls appear, how much complexity users see, and how form building fits the customer workflow. Non-developers can handle legitimate form variation while engineering keeps responsibility for the backend architecture.
### Security in Data Collection
Customer-created forms stay inside your Form.io-backed application boundary instead of becoming another third-party point solution. Your team controls where form definitions live, how submissions are captured, which permissions apply, and how collected data moves into the systems your product already depends on.
## 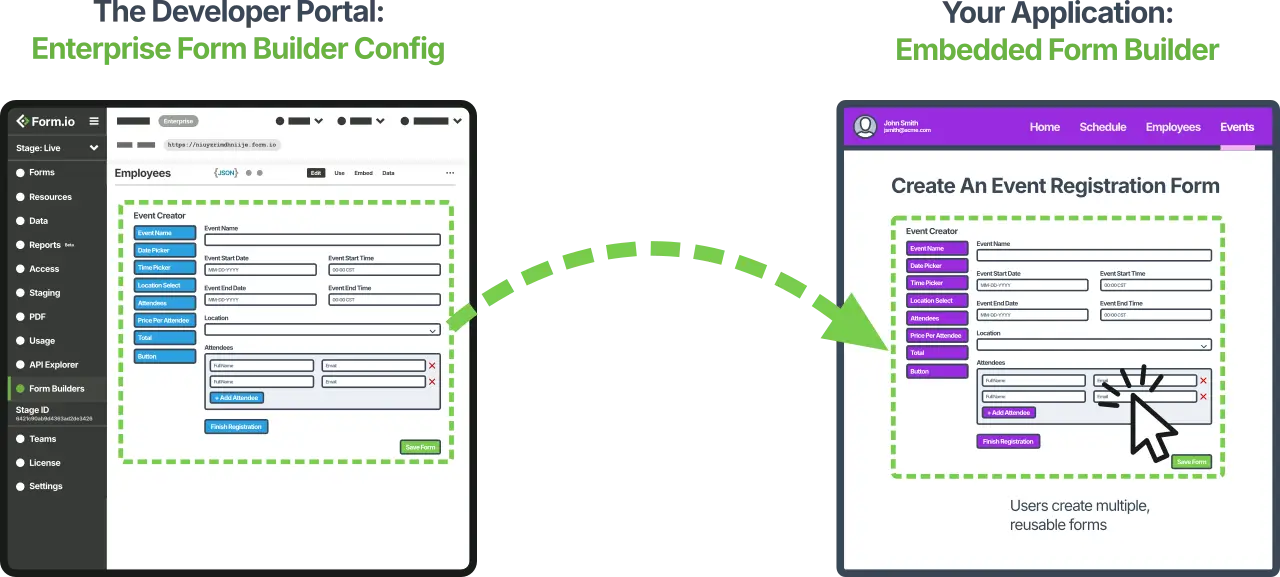 Embedded form building inside the application experience, with the platform owner controlling what users can configure. "Speed to market using Form.io worked fantastically well. We didn't have to spend 80% of our time building our own solution and instead could focus our dev time on things proprietary to us." Cory Linton, CEO of Edify.ai Less custom form work "Of all the systems we use to deliver our end products, Form.io has been probably the most straightforward and issue free to use, with excellent support." Dept. of Justice, Ireland Enterprise support confidence "Speed to market for setting up a form or application is what we liked best. Form IO allows us to set up a form with easy front end validation and business logic, instant API accessable database." Neal G., Technical Administrator for State of Ohio Fast form-to-API setup The Concerns Are Real
### Embedding form creation affects product boundaries, customer permissions, and data governance, so the questions deserve direct answers.
#### Will customers break our data model?
They can if you expose a generic builder with no platform guardrails. Form.io's EFBM is designed for customized, pre-wired form building inside your app, so teams can limit the experience to the components, labels, behavior, and permissions that fit the product.
#### Does this only matter for complex forms?
No. Many EFBM use cases involve industry-specific forms that are structurally simple but need customer-by-customer variation. One customer may capture a person's name as first and last name, another may need preferred name, suffix, or organization-specific naming fields. Form.io lets teams customize the capture experience while keeping the submitted data normalized for the application.
#### What does engineering still own?
Engineering still owns the application, deployment model, integration boundaries, and what customers are allowed to configure. The point is not to remove engineering from the system. The point is to stop routing every legitimate form variation through custom development.
## Map Your Embedded Builder Path
### Book a short working session and Form.io will help map where customer-created forms should live inside your application boundary.
You will bring the application context: who creates forms, what they are allowed to change, where submissions go, and which systems receive the data. Form.io will walk through the fit for embedded form creation, the guardrails that matter, and the likely implementation path. The first conversation is a scoping call, not a purchase commitment.
If EFBM is not the right layer, you will know before implementation planning begins.
## Let Customers Create Forms Without Losing Control
When every customer form request reaches engineering, the product slows down for reasons that have little to do with the core roadmap. Embedded form building gives customers useful autonomy while your application keeps the rules.
"Forms are not just inputs — they're mission-critical data infrastructure," said Gary Wetzel, Co-Founder and CEO of Form.io.
---
# Build vs. Buy vs. Source: Enterprise Form Infrastructure
*Published:* 2026-07-14
*Author:* Veronika Druck
*URL:* https://form.io/build-vs-buy-vs-source-enterprise-form-infrastructure/
*Description:* Defines the Build vs. Buy vs. Source framework for enterprise form infrastructure, comparing custom development, SaaS form builders, and self-hosted Form.io infrastructure across TCO, governance, data control, compliance, scalability, and AI-readiness.
[ 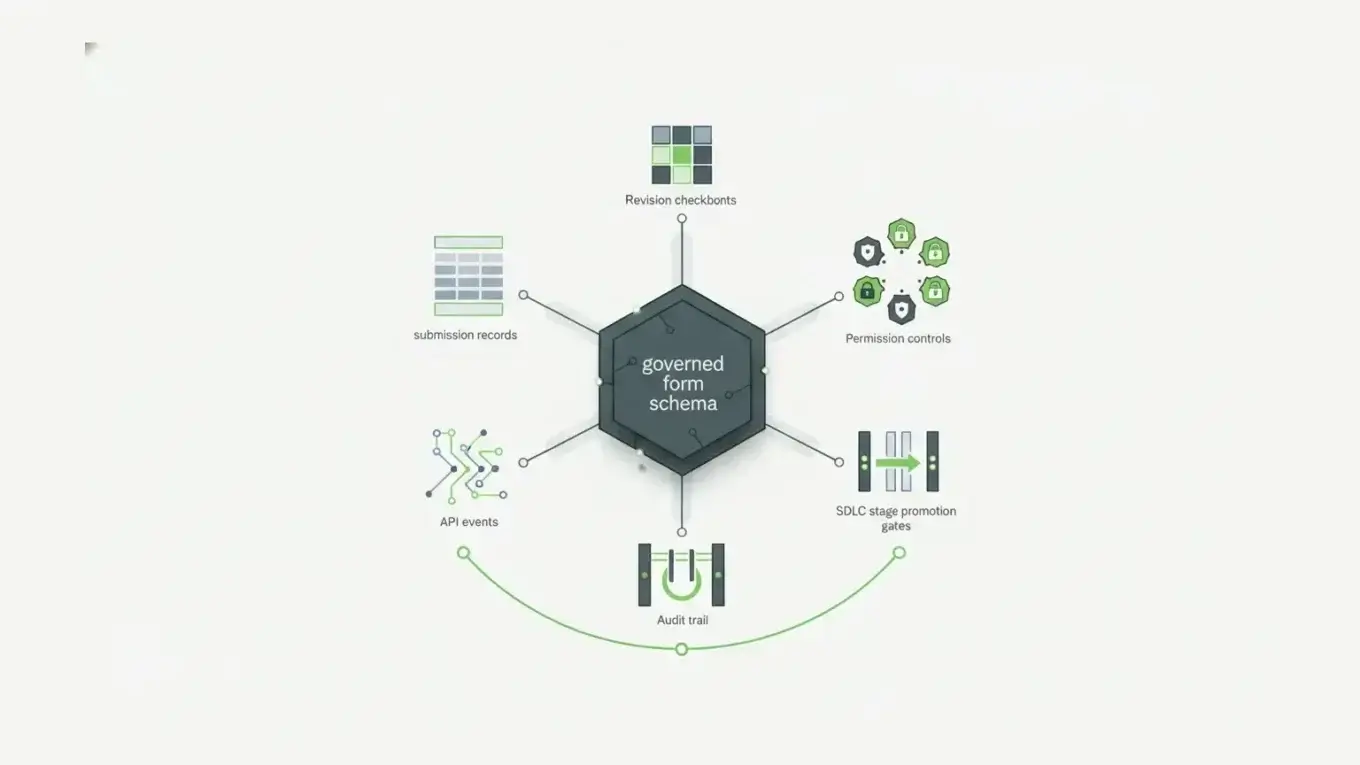 ](https://form.io/audit-trail-software-enterprise-form-builders-with-native-sdlc/)Audit trail software sounds simple until the record being audited is not just a file, invoice, login, or database row.
Enterprise forms change. Submitted data changes. Validation rules change. Permissions change. Workflow actions fire. APIs read and update the same records that users see in the interface.
For regulated form workflows, the question is not only "Do we have logs?" It is "Can we prove what happened, who did it, what version of the form governed it, and whether the workflow moved through the right control path?"
## **What audit trail software has to prove**
Audit trail software creates a chronological record of activity inside a system.
At minimum, that record should help answer:
- Who performed the action?
- What changed?
- When did it happen?
- Which object, record, form, user, or system was affected?
- What context explains the change?
- Can the record be reviewed later without reconstructing it from guesswork?
That matters because audit trails are not only for after-the-fact compliance reviews. They are also useful for security monitoring, troubleshooting, workflow accountability, and incident investigation.
NIST's log management guidance treats logging as part of a broader cybersecurity evidence system. The draft [NIST SP 800-92 Rev. 1 Cybersecurity Log Management Planning Guide](https://csrc.nist.gov/pubs/sp/800/92/r1/ipd) treats logging as part of a broader cybersecurity evidence system.
Regulated systems make the point even more concrete. [21 CFR 11.10](https://www.law.cornell.edu/cfr/text/21/11.10) requires procedures and controls for closed systems that include secure, computer-generated, time-stamped audit trails for actions that create, modify, or delete electronic records, and it says record changes must not obscure previously recorded information. HIPAA's technical safeguards similarly include [audit controls](https://www.law.cornell.edu/cfr/text/45/164.312) for information systems that contain or use electronic protected health information.
That is the right starting point. Logs are evidence.
But enterprise form workflows need a more specific kind of evidence.
If a claims intake form changes, a patient referral submission is corrected, a public-sector application moves from draft to review, or an embedded customer form is updated through an API, a generic event log may not be enough. The system needs to preserve the relationship between the action and the form infrastructure that governed it.
## **Why enterprise forms need a different audit model**
A form in an enterprise application is not just a page.
It can be:
- a user interface
- a JSON schema
- a validation contract
- a submission model
- a generated API
- a workflow trigger
- a permission boundary
- a document-generation source
- a long-term record
That is why auditability gets harder when forms become application infrastructure.
A simple audit log might show that a user updated a record at 2:14 PM. That is useful, but it does not answer every question an auditor, compliance team, or engineering lead may ask later.
For example:
- Which form version was active when the user submitted the record?
- Did the form have the same required fields then that it has now?
- Was the submitted value changed after capture?
- Was there a documented reason for the change?
- Did a webhook, email, approval action, or downstream integration fire?
- Did the change happen in development, staging, or production?
- Did the API update follow the same permission rules as the portal update?
Those are form-infrastructure questions, not just logging questions.
IBM's 2025 [Cost of a Data Breach Report](https://www.ibm.com/reports/data-breach) puts the global average breach cost at $4.4 million and reports that 63% of organizations lacked AI governance policies. That statistic is not form-specific, but it gives the right scale for the decision. When sensitive data workflows are hard to trace, the risk is not cosmetic.
For enterprise forms, the audit model has to cover both sides of the system: the form definition and the submitted data.
## **The four audit layers enterprise form builders should support**
Most form tools can tell you that a submission exists.
Enterprise form infrastructure needs to tell a deeper story.
### **1. System activity and access logs**
The first layer is the system-level audit log.
This is the record of access, authentication, API requests, data reads, data writes, and other platform activity. It answers questions like:
- Who viewed this submission?
- Who authenticated?
- Which API request changed the record?
- Which project, form, or user was involved?
- Did a request fail?
- Can related events be correlated?
Form.io's [audit logging documentation](https://help.form.io/dev/audit-logging) describes a system-level audit log format with date, event, UUID, project ID, session ID, user ID, and event-specific context. The docs also state that audit logs output to standard out for the Docker container and can be routed into a log aggregation system.
Another note: high-volume system logs should not necessarily store complete submission payloads inside every event. Sensitive form values may need a different audit mechanism than API access events.
The right audit design separates broad activity logging from field-level revision history, then lets teams correlate the two when they need to investigate.
### **2. Form revisions**
The second layer is form revision history.
Enterprise forms change over time. Teams add fields, remove fields, rename fields, update validation rules, change conditional logic, revise consent text, and adjust workflow requirements.
If the form changes after a record is submitted, the system still needs to explain what the form looked like when the record was captured.
Form.io's [Form Revisions documentation](https://help.form.io/userguide/forms/form-revisions) is built for that problem. Form Revisions let teams preserve form versions as forms evolve and can display submission data in the form revision that captured it. The revision interface also exposes who made a revision, when the revision was made, the revision number, and revision notes.
That distinction is central to auditability.
If an auditor reviews a historical submission, the question is not only "What data is in the record now?" It is also "What fields, labels, rules, and structure governed the user when the record was created?"
Without form revision history, teams often have to reconstruct that context from release notes, screenshots, old code, or database backups. That is fragile.
### **3. Submission revisions**
The third layer is submission revision history.
This is the field-level history of changes to submitted data after initial capture.
A submitted form might be corrected by a staff member. A patient record might need an updated value. A claims workflow might need a revised amount. A government service application might need a supporting detail added after review.
In those cases, the system needs to preserve the previous state, the new state, the user who made the change, the time of the change, and any revision note explaining why the change happened.
Form.io's [Submissions documentation](https://help.form.io/userguide/submissions) describes Submission Revisions as an audit logging capability that tracks who updated a submission, when the change was made, and notes associated with the update. The documentation also says the PDF change log can include the revision ID, updating user, date and time, revision note, and list of revision changes.
That is the difference between editing a record and governing a record.
An edit changes the current value. A revision trail preserves the accountable history behind that value.
### **4. Stage, action, and deployment history**
The fourth layer is the SDLC layer.
For enterprise form teams, auditability is not limited to runtime activity. It also includes how form definitions, resources, roles, and actions move through development, staging, and production.
Form.io's [Stages documentation](https://help.form.io/userguide/projects/stages) describes stages as a way to isolate project forms and resources for form management between different environments. The same documentation frames a typical enterprise workflow around Live, Authoring, QA/Test, and Development stages.
That matters because regulated teams often need controlled promotion.
They need a place to build and test form changes before production. They need to know which form version moved forward. They need to avoid ad hoc edits that change production behavior without review. This should not be inflated into a claim that Form.io replaces a full CI/CD or release-management system for all application code. The narrower point is still valuable: form configuration has its own lifecycle, and enterprise teams need a controlled way to manage it.
Audit trail software that ignores the lifecycle layer misses a major part of the form governance problem.
## **A practical comparison framework**
The right audit trail software depends on what kind of system you are auditing.
**Category****Best fit****What it proves****Where it can fall short for enterprise forms**Generic audit log toolingBroad system activity, application events, operational monitoringWho did what, when, and where across systemsUsually does not understand form schema versions or submission-level change historyCompliance audit management toolsPolicy controls, audit programs, evidence management, compliance workflowsWhether controls exist and evidence was collectedOften manages audit process, not the runtime form record itselfAccounting or finance audit trail toolsFinancial transactions, invoices, approvals, accounting changesTransaction history and financial accountabilityUsually narrow to finance workflowsBasic form builders with logsSimple submissions, admin edits, response exportsBasic submission history and account activityMay not preserve form schema history, API-level activity, or stage promotionCustom-built audit trailHighly specific internal applicationsWhatever the team designs and maintainsExpensive to build, test, secure, document, and keep consistent across formsForm infrastructure with native audit controlsRegulated form workflows, embedded forms, generated APIs, long-lived submissionsSystem activity, form revisions, submission revisions, permissions, actions, and stage movementRequires technical ownership and a clear governance modelThe key is fit.
If your team only needs a basic activity log for a contact form, enterprise form infrastructure is probably too much. If your team is managing high-value workflows where form definitions and submitted data both matter, the audit model needs to be native to the form platform.
## **Where Form.io fits**
Form.io is strongest when the form is part of the application infrastructure.
That usually means a team needs some mix of [self-hosted form deployment](/features/self-hosted-forms-for-enterprise/), embedded forms, generated APIs, permissions, workflow actions, form revisions, submission revisions, audit logging, and environment promotion.
The reason is architectural.
Form.io forms and resources are JSON-driven definitions that can render user interfaces, generate APIs, validate submissions, store submitted data, and participate in roles, permissions, actions, stages, and revisions.
That makes auditability part of the same system that owns the form workflow.
[The Security Module](/features/secure-forms-compliance-readiness/) bundles advanced audit logging, action logs, form revisions, submission revision logs, submission collections, and container security scanning. The [complete audit trail feature](/features/log-forms-complete-audit-trail/) separates system-wide audit logs from field-level submission revisions, which is the right separation for high-volume enterprise workflows. The [Form Revisions feature](/features/form-revisions-form-json-schema/) preserves form JSON schema versions so historical submissions can remain explainable as forms evolve.
Form.io also matters when APIs are part of the record. A form workflow may be updated through the portal, an embedded application, or a generated API. The buyer should not have to accept one audit posture for the UI and another for API-driven operations.
That is why generated APIs are relevant to audit trail software. Form.io's [form API model](/features/form-api/) lets teams treat forms and resources as API-connected infrastructure, not isolated web pages. Permissions, submissions, and actions then sit closer to the form data model.
This is also where customer proof matters. [G2's Form.io review page](https://www.g2.com/products/form-io/reviews) describes the platform as deployable into on-premise or private cloud environments, giving customers control of submission data. One enterprise reviewer summarized the practical product experience this way: "Form.io is an intuitive, developer-friendly framework that provides excellent data management." That is not an audit claim by itself. It is buyer proof for the control-and-customization posture that makes audit-heavy form infrastructure worth evaluating.
## **When simple audit logging is enough**
Not every workflow needs all of this.
Simple audit logging may be enough when:
- The form is short-lived.
- Submitted data is low risk.
- Responses are rarely edited after capture.
- The form schema rarely changes.
- The form is not embedded into a regulated application.
- There is no need for DEV/STAGE/PROD promotion.
- Exports are enough for downstream systems.
- The audit question is limited to account activity or submission timestamps.
In those cases, a lighter form builder, basic form backend, or general application log may be a better fit.
The mistake is keeping that model after the workflow becomes infrastructure.
Once forms drive eligibility, claims, intake, onboarding, financial review, patient workflows, public-sector services, insurance applications, or internal approvals, the audit trail has to explain more than "a record changed."
It has to explain the governed context around the change.
## **Evaluation checklist for audit trail software in form workflows**
Use these questions before choosing a form platform for an audit-heavy workflow.
### **Does the platform track system-level activity?**
Look for access events, authentication events, API requests, data reads, data writes, request correlation, and log export options.
### **Does it preserve form schema versions?**
If a field, validation rule, label, or conditional path changes, the platform should preserve enough form history to explain historical submissions.
### **Does it preserve submitted-data history?**
Submission revisions should show who changed a value, when it changed, what changed, and why.
### **Can historical submissions render against the original form version?**
This matters when auditors, legal teams, or operations teams need to understand what a user actually saw at capture time.
### **Are workflow actions included in the governance model?**
Actions such as emails, webhooks, approvals, PDF generation, and save-to-resource operations can affect the record. They should not be invisible.
### **Can forms move through controlled stages?**
Enterprise teams need a way to test, version, and promote forms, resources, roles, and actions without treating production as the editing surface.
### **Do permissions apply close to the form and submission model?**
[Form permissions](/features/form-permissions/) matter because different people may be allowed to create, read, update, delete, approve, or export different records.
### **Can the platform run inside the required deployment boundary?**
Self-hosting does not automatically make a system compliant. It does let the customer place the form platform inside the environment, monitoring, identity, logging, and operational controls the organization already governs.
### **Are forms still usable for builders and developers?**
Audit controls only help if the team can still build and maintain the workflow. A usable [form builder](/features/form-builder/) and a clear [JSON-powered form model](/features/json-powered-forms/) reduce the temptation to route around governance.
## **Key takeaways**
- Audit trail software is not only a logging feature when forms become application infrastructure.
- Enterprise form workflows need evidence across system activity, form revisions, submission revisions, workflow actions, permissions, and stage promotion.
- Generic logs can show that something happened. Form infrastructure should show what version of the form governed the record when it happened.
- Form.io fits best when the form schema, generated API, submitted data, and governance controls need to stay connected.
- The right buyer is not looking for the lightest form tool. They are looking for a form platform that can defend the record later.
## **FAQ**
### **What is audit trail software?**
Audit trail software records system activity in chronological order so teams can review who performed an action, what changed, when it happened, and which record or system was affected.
### **Why do enterprise forms need audit trails?**
Enterprise forms often collect data that drives decisions, approvals, compliance records, customer onboarding, claims, patient workflows, government services, or financial review. If the record changes later, the organization needs evidence of what happened.
### **What is the difference between an audit log and a submission revision?**
An audit log records system-level activity such as access, authentication, API requests, and data modification events. A submission revision preserves field-level history for a specific submitted record.
### **What is the difference between form revisions and submission revisions?**
Form revisions track changes to the form schema: fields, validation rules, conditional logic, layout, and related form structure. Submission revisions track changes to submitted data after capture.
### **Why does form versioning matter for audit trails?**
Form versioning helps explain historical records. If a submission was captured under an older form version, the team may need to review the exact schema, fields, labels, and validation rules that governed that submission.
### **Does self-hosting make audit trail software compliant?**
No. Self-hosting gives the organization more control over deployment, data, logs, identity, monitoring, and infrastructure. Compliance still depends on configuration, policy, controls, documentation, and review.
### **Should audit trail software store every field value in every log?**
Not always. High-volume system logs can become expensive and sensitive if they store full payloads in every event. A better model often separates system audit logs from field-level submission revisions.
### **What should regulated teams look for in form audit trails?**
They should look for system audit logs, form revisions, submission revisions, permissions, workflow/action evidence, stage promotion, exportable evidence, and deployment control.
### **Can generic log management replace native form revision history?**
Generic log management can help centralize and review system events, but it usually does not understand form schema versions, submission rendering, or field-level form data history unless the application sends that context deliberately.
### **When is Form.io a good fit for audit-heavy forms?**
Form.io is a good fit when forms are part of a larger application workflow and the team needs [form workflows](/features/form-workflows/), generated APIs, permissions, revisions, submission history, and customer-controlled deployment.
### **When is Form.io probably too much?**
Form.io may be more platform than needed for a simple contact form, survey, or lead-capture page where the data is low risk and the audit requirement is limited to basic timestamps or account activity.
## **Build audit-ready form infrastructure with Form.io**
# Web Form Builder: When Online Forms Need APIs, Workflows, and Self-Hosted Control
[  ](https://form.io/web-form-builder-apis-self-hosted-control/)A web form builder sounds like a simple category until the form becomes part of a real application. A contact form, signup form, or feedback survey can live in a lightweight tool. A regulated intake process, embedded customer workflow, or API-connected business process needs more than fields on a page.
That is where the buying question changes.
## **What a Web Form Builder Should Do**
A web form builder is software for creating forms users can complete in a browser. At the basic level, it should let a team create fields, set required answers, publish a form, collect submissions, and send the data somewhere useful.
For many teams, that is enough.
Zapier's long-running online form builder list shows how the broad market is usually framed: quick form creation, automation, advanced logic, conversational form experiences, AI-assisted building, Excel sync, approval flows, and reporting options ([Zapier](https://zapier.com/blog/best-online-form-builder-software/)). That is the default expectation buyers bring to the phrase.
The problem is that "web form builder" covers several different jobs:
- a marketing team collecting leads
- an operations team routing internal requests
- a product team embedding forms inside a SaaS application
- a healthcare, insurance, finance, or government team collecting sensitive data
- a development team using forms as part of an API-backed workflow
Those jobs should not be evaluated with the same checklist.
If the form is only a standalone page, the most important questions are speed, templates, design, notifications, and basic integrations. If the form is part of application infrastructure, the questions become more serious: who owns the schema, where does submission data live, what APIs exist, how validation runs, what happens after submit, and whether the platform can operate inside the customer's environment.
## **When a Simple Web Form Builder Is Enough**
A simple web form builder is a good fit when the form is low-risk, isolated, and easy to replace.
Use a lightweight tool when:
- the form collects basic marketing or event information
- submissions can live in the vendor's hosted system
- exporting to a spreadsheet is acceptable
- the workflow after submission is simple
- there are no unusual data residency or deployment requirements
- the form is not deeply embedded in a product experience
- developers do not need to treat the form as an API-backed component
In that world, the best tool is often the fastest tool your team will actually use. A simple builder can be the right decision for a campaign, a workshop signup, a small survey, or a basic internal request.
The mistake is keeping that same mental model after the requirements change.
## **Where Web Form Builders Start To Break Down**
Web forms become harder when the submission is not the end of the process.
A user submits an intake form. Then the data has to create a case, trigger a review, update a CRM, route to a queue, generate a PDF, notify a downstream system, enforce role-based access, or become part of a customer-facing application.
At that point, the form has a second job. It is no longer just collecting answers. It is becoming the front door to a process.
The breakdown usually shows up in five places.
### **The Data Model Lives Somewhere Else**
Many web form builders make it easy to create fields, but the real application data model lives outside the form tool. That creates drift. A field is required in the form but optional in the backend. A dropdown changes in the builder but not in the API. A validation rule exists in the browser but not server-side.
This is small until the form becomes important.
Then every disconnected rule becomes a place where bad data can enter the system.
### **Integrations Become Workflow Logic**
Basic integrations are helpful. They send a notification, create a spreadsheet row, add a CRM contact, or post to a collaboration tool.
But integration is not the same as workflow ownership.
Enterprise forms often need conditional routing, retries, identity context, external IDs, error handling, and clean handoff to other systems. Form.io's webhook documentation, for example, treats a submission as a payload that can call an external API, map response IDs back to the submission, and optionally wait for the webhook response before continuing actions ([Form.io webhook actions docs](https://help.form.io/form-building/actions/webhook-actions)).
That is a different requirement than "send this form to a spreadsheet."
### **Security And Compliance Become Architecture Questions**
The more sensitive the data, the less acceptable it is to treat the form builder as a detached SaaS box.
IBM's 2025 Cost of a Data Breach Report puts the global average breach cost at USD 4.4 million ([IBM](https://www.ibm.com/reports/data-breach)). That statistic should not be used to scare every team away from hosted tools. It should remind buyers that data capture is part of the security boundary.
For sensitive forms, the evaluation should include:
- where submissions are stored
- who administers the environment
- how access is controlled
- how data moves between systems
- how logs, evidence, and audit needs are handled
- whether the form platform can live inside the organization's deployment model
Self-hosting does not automatically make a system compliant. It gives the organization more control over the environment where compliance controls are implemented and reviewed.
### **Product Teams Need Embedding, Not Just Publishing**
Publishing a hosted form is not the same as embedding a form builder into a product.
If a B2B SaaS team wants customers to create or manage their own forms inside the application, the builder has to respect the product's authentication, permissions, tenant boundaries, styling, and data model. That is closer to an embedded product capability than a public web form.
This is why Form.io's [Enterprise Form Builder Module](https://form.io/features/enterprise-form-builder-module/) matters for platform teams. The point is not only that a user can drag fields onto a canvas. The point is that a company can provide a white-labeled, pre-wired form-building experience inside its own application.
### **Developers Need A Stable Contract**
Developers can work around almost anything once. The cost shows up when every new form requires custom backend glue.
A stronger web form builder for application teams should create a stable contract between the form, the submission record, the API, validation, permissions, and downstream systems.
Form.io's own project documentation says that when a new form is created, a REST API is automatically generated to serve as the backend for the form and for other systems that need to create submissions ([Form.io project docs](https://help.form.io/admin/projects/creating-a-project)). That is the key architectural distinction: the form is not only a UI artifact. It is part of the API surface.
## **A Web Form Builder Evaluation Checklist**
Before choosing a web form builder, separate the easy questions from the questions that determine long-term fit.
Evaluation AreaLightweight Form NeedInfrastructure-Grade Form NeedBuilderDrag-and-drop fields, templates, brandingConfigurable builder, reusable schemas, controlled componentsDataHosted submissions and exportsStructured submission records with API accessWorkflowNotifications and simple integrationsWebhooks, Actions, retries, external IDs, routingValidationClient-side rules and required fieldsSchema-linked validation across UI and server pathsEmbeddingPublic link or iframeNative application embedding and white-label controlDeploymentVendor-hosted SaaSHosted, private cloud, on-premises, or local deployment optionsGovernanceAdmin settingsRoles, permissions, stages, evidence, and environment controlFitCampaigns, surveys, simple intakeProduct workflows, regulated intake, internal systems, multi-tenant SaaSThis checklist prevents a common buying mistake: choosing the easiest form tool for the first version, then rebuilding the entire intake layer once the forms become operationally important.
## **Why APIs Change The Category**
APIs change a web form builder from a page-building tool into an application component.
Without APIs, the form is mostly a destination. Users go there, submit data, and the team exports or forwards the result.
With APIs, the form can become part of the system:
- applications can create and read submissions
- forms can populate fields from external data
- downstream systems can consume structured payloads
- teams can build reporting, review, and workflow layers on top of submission records
- developers can integrate forms into products without treating each one as a one-off project
Form.io's [data integration tools](https://form.io/features/data-integration-tools-for-enterprise-forms/) positioning makes this point directly: forms, resources, submissions, and projects are accessible through REST APIs. The practical value is not just "there is an API." It is that the form builder, schema, submission data, and integration surface are part of the same model.
That matters when teams are building internal tools, partner portals, insurance workflows, healthcare intake, public-sector services, or SaaS onboarding flows.
The user sees a web form. The architecture sees a contract.
## **Why Deployment And Data Control Matter**
Deployment is one of the clearest dividing lines between a simple web form builder and enterprise form infrastructure.
If the form is low-risk, vendor-hosted SaaS is usually fine. If the form handles regulated data, internal process data, customer application data, or data that has to move through controlled systems, deployment becomes part of the buying decision.
Form.io's deployment documentation says the platform can be installed in cloud environments, on-premise data centers, or local machines, and that enterprise deployments can use multi-environment architecture across private cloud or on-prem environments ([Form.io deployment overview](https://help.form.io/deploy/deployment-overview)). Its on-premises deployment documentation frames on-prem as relevant when infrastructure, compliance, or data-security requirements call for that model ([Form.io on-premises deployment docs](https://help.form.io/deploy/on-premises-deployment)).
This does not make Form.io the right fit for every form.
It makes Form.io relevant when the form layer has to live where the rest of the application lives.
For teams with strict environment rules, that is often the real requirement hiding underneath the phrase "web form builder." They are not only asking for a form canvas. They are asking whether the form system can respect their data boundary, deployment model, access controls, and integration paths.
## **Where Form.io Fits**
Form.io is a stronger fit when the form is part of an application, not just a standalone collection page.
The core difference is that Form.io combines a [drag-and-drop form builder with APIs](https://form.io/features/drag-and-drop-form-builder-apis/). Teams can design forms visually while keeping the underlying structure available as JSON and exposed through generated REST APIs.
That combination is useful when:
- developers need forms embedded in a product
- business users need controlled form authoring
- submissions need to be available through APIs
- workflows need webhooks or server-side actions
- the organization needs self-hosted or on-premises deployment
- forms need to share a governance model with the surrounding application
Form.io is not the best answer when a team only needs a quick public survey or a simple contact form. That buyer should choose the fastest lightweight tool that fits the job.
But when a web form builder has to support real application infrastructure, the decision changes. The value is not only the builder UI. It is the connection between form schema, submission data, generated APIs, deployment control, and workflow actions.
Customer language points to the same distinction. A Trustpilot reviewer described Form.io as useful "for integration and standalone" work ([Trustpilot](https://www.trustpilot.com/review/form.io)). A Form.io case study customer put the infrastructure burden more bluntly: Form.io "cleans up all the dirty work" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)).
That is the real category line.
A basic web form builder helps a team make a form. Form.io is for teams that need the form to become a governed part of the application.
## **Key Takeaways**
- A web form builder can mean anything from a simple contact form to an embedded application workflow.
- Lightweight tools are a good fit when forms are low-risk, standalone, and easy to replace.
- Enterprise teams should evaluate APIs, validation, submissions, workflow actions, permissions, and deployment control.
- Form.io fits when the form layer needs to operate as controlled application infrastructure, not just a hosted form page.
- Self-hosting is not a compliance shortcut; it is a control model for teams that need to own the environment.
## **FAQ**
### **What Is A Web Form Builder?**
A web form builder is software for creating forms that users complete in a browser. Basic builders focus on fields, templates, publishing, notifications, and exports. More advanced builders support APIs, workflows, permissions, embedding, and controlled deployment.
### **What Is The Difference Between A Web Form Builder And An Online Form Builder?**
The terms often overlap. "Online form builder" usually points to hosted SaaS tools for creating and publishing forms quickly. "Web form builder" can mean the same thing, but it is also used by product and development teams looking for embeddable form-building inside a web application.
### **When Is A Basic Form Builder Enough?**
A basic form builder is enough when the form is low-risk, standalone, and does not need deep integration with internal systems. Examples include event registration, simple lead capture, small surveys, and basic internal requests.
### **When Does A Web Form Builder Need APIs?**
A web form builder needs APIs when other systems must create, read, update, route, or report on submissions. APIs matter when forms are part of a product, portal, approval workflow, regulated intake process, or internal system of record.
### **Why Does Form Schema Matter?**
The schema defines the form's structure and behavior. In a schema-driven model, the same definition can support rendering, validation, submissions, APIs, workflow actions, and governance. That reduces drift between what the user sees and what the backend expects.
### **Can A Web Form Builder Be Self-Hosted?**
Some web form builders are hosted-only. Form.io supports self-hosted deployment models, including cloud, on-premises, and local environments according to its deployment documentation. That matters when the organization needs control over hosting, network boundaries, data storage, and operational review.
### **Is Self-Hosting The Same As Compliance?**
No. Self-hosting gives the customer more control over the environment, but compliance still depends on configuration, policies, controls, monitoring, documentation, and the broader system boundary. The value is control, not a shortcut around responsibility.
### **Why Would A SaaS Product Need An Embedded Form Builder?**
A SaaS product may need customers or internal teams to create forms inside the product itself. In that case, the builder has to respect tenant boundaries, authentication, permissions, styling, and data storage. A public form link is not enough.
### **How Is Form.io Different From A Simple Form Tool?**
Form.io is built for teams that need forms, submission data, generated APIs, workflow actions, and deployment control together. It can still provide a drag-and-drop builder, but the stronger reason to use it is when forms need to operate inside application infrastructure.
## **Build Web Forms That Fit Your Application Architecture**
# E Signature Software for Self-Hosted Form Workflows: DocuSign Alternatives for Enterprise Control
[  ](https://form.io/e-signature-software-self-hosted-form-workflows/)E signature software is usually evaluated as a document workflow tool: send a PDF, collect a signature, store an audit trail, and move on.
That is enough for many contracts. It is not enough when the signature is attached to regulated intake, eligibility data, consent records, financial applications, healthcare workflows, or other form submissions that must stay inside your application boundary.
The better question is not only, "Can this document be signed?" It is, "Can we defend the signed record later, with the data, schema, context, and audit trail intact?"
## **What E Signature Software Usually Solves**
Most e signature software helps teams replace wet signatures with an electronic signing process. The standard workflow is familiar: upload a document, place signature fields, route it to signers, authenticate the signer, collect consent, and retain a completed envelope.
That category is large because the paper problem is large. [Grand View Research estimated](https://www.grandviewresearch.com/industry-analysis/digital-signature-market-report) the global digital signature market at USD 6.9 billion in 2025 and projected a 43.9% CAGR from 2026 to 2033.
But market size does not tell you which architecture fits your use case.
Standalone signing platforms are strongest when the signed artifact is the document itself: contracts, sales agreements, HR forms, procurement packets, vendor agreements, and legal paperwork. In those cases, the system of record is often the completed document package.
Form-driven applications are different. The signed evidence may need to stay attached to a submission record, user identity, form version, field values, workflow state, API transaction, and downstream system update.
That is where a normal e-signature checklist starts to miss the real buyer risk.
## **Why DocuSign Alternatives Become Relevant**
DocuSign is the name many buyers know first. Adobe, Dropbox Sign, PandaDoc, Zoho Sign, OneSpan, and other tools also belong in the traditional e-signature conversation.
Those tools can be the right choice when your team mainly needs a document-signing workflow. The mistake is assuming that the best document-signing platform is automatically the best signing architecture for application data.
Teams start looking for DocuSign alternatives when one or more constraints appears:
- signature data must stay inside a private cloud, VPC, on-premise, or controlled deployment boundary
- the signed record begins as structured form data, not a static PDF
- signer consent needs to connect to the exact fields and submission context that were signed
- APIs, webhooks, roles, permissions, and audit history matter as much as the visual signature
- pricing or operations become hard to forecast when signatures scale across many workflows
For these teams, the word "alternative" does not simply mean cheaper. It means architecturally different.
## **The Enterprise Evaluation Criteria**
Before choosing e signature software, separate legal acceptance from operational evidence.
The U.S. [ESIGN Act](https://uscode.house.gov/view.xhtml?edition=prelim&path=%2Fprelim%40title15%2Fchapter96) says electronic signatures and records generally cannot be denied legal effect solely because they are electronic. It also points to record retention: electronic records must remain accurate, accessible, and reproducible for later reference.
That retention point matters. A signature event is only as useful as the record your team can reproduce when someone asks what was signed, by whom, under which form version, with which field values, and under which business process.
Evaluate each platform across six criteria.
**Criterion****Why it matters**Deployment controlDetermines where sensitive data, signature proof, and operational evidence live.Record modelShows whether the signed artifact is a PDF envelope, a submission record, or both.Audit trailCaptures the evidence needed to defend the transaction later.API accessDetermines whether signatures can participate in application workflows.Identity and access controlsConnects signing to the right user, role, tenant, or workflow boundary.Pricing modelDetermines whether cost scales predictably across high-volume workflows.The wrong platform can still collect a signature. The problem appears later, when the team needs to prove what the signature means inside the larger system.
## **Where Self-Hosted Form Workflows Change The Question**
Self-hosted form workflows change the center of gravity.
Instead of asking, "Which e-signature vendor should host this envelope?" the team asks, "How do we keep the signed record inside the same infrastructure that owns the form, data, APIs, permissions, and audit history?"
That shift matters for regulated teams, embedded SaaS products, government contractors, healthcare platforms, insurance workflows, financial services onboarding, and internal enterprise portals.
The signature is not a decorative mark. It is a control point in the data lifecycle.
NIST's [digital signature project](https://csrc.nist.gov/projects/digital-signatures) frames digital signatures around generation, verification, and data protection. That distinction is useful for buyers: a visible signature image is not the same thing as verifiable proof that the protected data and context have not changed.
In a form workflow, the strongest signature system should answer questions like:
- Which form version captured the data?
- Which fields were protected by the signature?
- Did the data change after signing?
- Can the application verify the signature through an API?
- Does the signed record remain inside the customer's environment?
- Can the team reproduce the record without depending on a third-party envelope as the only source of truth?
Those are infrastructure questions, not just signing questions.
## **How Form.io E-Sign+ Fits**
[Form.io E-Sign+](/features/cryptographic-e-signatures-for-form-data/) is built for a narrower, more controlled version of the e-signature problem: cryptographically secure signatures associated with Form.io submission data inside the customer's own environment.
That is a different posture than a standalone document-signing workflow.
With Form.io, the [form schema and submission data](/form-json-schema-vs-submission/), generated APIs, permissions, workflow actions, and deployment boundary are already part of the application infrastructure. E-Sign+ extends that infrastructure by letting teams verify signed submission data and context rather than treating the signature as only a PDF-layer event.
The [product documentation](https://help.form.io/dev/integrations/e-sign%2B) describes E-Sign+ as tied to submission data, usable through native submission IDs, and decoupled from PDFs. It can protect selected fields, all form data, and/or submission properties, depending on configuration.
That makes Form.io a strong fit when the signature needs to travel with application data.
Form.io's broader customer proof reinforces the infrastructure value. One customer quote on [Form.io's homepage](https://form.io/) says, "Speed to market using Form.io worked fantastically well," because the team did not have to spend most of its time building its own solution. Another proof point describes cutting data-processing workload by 50%.
Those quotes are not E-Sign+ specific. They do show the larger pattern: Form.io is strongest when teams need to stop rebuilding form, data, API, and workflow plumbing from scratch.
## **E Signature Software Comparison**
**Best fit****Typical tools****Watch the tradeoff**Standard document signingDocuSign, Adobe Acrobat Sign, Dropbox Sign, PandaDoc, Zoho SignStrong for envelopes and documents, but not always ideal when signed evidence must remain attached to application-owned submission data.Developer signing APIsAPI-first signing platformsFlexible for document workflows, but your team still owns the surrounding form schema, data model, and governance path.Self-hosted form signing infrastructureForm.io E-Sign+Strong fit when forms, submissions, APIs, permissions, and signature verification need to stay in the customer's controlled environment.The point is not that every team should leave document-signing platforms. Many should not.
The point is that e signature software has to match the record you are actually signing.
If the record is a contract document, a document-signing tool may be enough. If the record is a governed application submission, the signature belongs closer to the form infrastructure.
## **Key Takeaways**
- E signature software is a broad category, but enterprise form workflows need more than a signed PDF.
- Legal validity is only one part of the evaluation. Record retention, reproducibility, and context matter.
- DocuSign alternatives become relevant when teams need deployment control, API access, data ownership, or application-level signature proof.
- Form.io E-Sign+ fits teams that need cryptographic signature verification tied to submission data inside their own environment.
- The stronger question is not "Which tool signs documents fastest?" It is "Which system protects the signed record your application actually depends on?"
## **FAQ**
### **What Is E Signature Software?**
E signature software lets people sign electronic records or documents without printing and scanning paper. In business workflows, it usually includes signer routing, authentication, consent capture, audit history, completed document storage, and API or integration options.
### **Is E Signature Software Legally Binding?**
Electronic signatures can be legally valid in many contexts, including under the U.S. ESIGN Act and [EU eIDAS rules](https://ec.europa.eu/digital-building-blocks/sites/spaces/DIGITAL/pages/467109069/What%2Bis%2BeSignature). Buyers should still review the specific transaction type, jurisdiction, identity process, consent language, retention rules, and audit evidence with legal counsel.
### **What Is The Best DocuSign Alternative?**
The best DocuSign alternative depends on the job. If the job is standard document signing, a standalone signing platform may fit. If the job is signing structured form submissions inside a controlled application, Form.io E-Sign+ is worth evaluating because the signature proof stays closer to the form data and API workflow.
### **When Should A Team Choose Self-Hosted E Signature Software?**
A team should consider self-hosted signing infrastructure when sensitive submission data, regulatory obligations, customer architecture, data residency, or private deployment requirements make third-party-hosted signing workflows difficult to justify.
### **How Is Form.io E-Sign+ Different From A PDF Signature Tool?**
Form.io E-Sign+ is designed around submission-linked signature proof. PDFs can still be part of a workflow, but the stronger distinction is that E-Sign+ can verify signed form data and context inside the customer's own [self-hosted Form.io environment](/enterprise-self-hosting/).
### **Does Form.io Replace DocuSign?**
Not for every use case. DocuSign is a strong document-signing platform. Form.io is a stronger fit when signatures are part of a governed form workflow, embedded application, or self-hosted data pipeline where submission context matters.
### **What Should Enterprises Look For In E Signature Software?**
Enterprises should evaluate deployment control, signer identity, audit trail quality, API access, retention and reproducibility, [configuration-based pricing](/configuration-based-pricing/), integration fit, and whether the signed record is a document envelope or application data.
### **Can E Signature Software Work With APIs?**
Yes. Many signing platforms provide APIs, but the important question is what the API controls. For form-driven applications, APIs should connect signatures to submission records, permissions, workflow state, and downstream systems.
### **Why Does Signature Context Matter?**
Signature context matters because a signature without the surrounding record can be hard to defend. Teams may need to know the form version, field values, signer identity, submission ID, timestamp, protected fields, and whether anything changed after signing.
### **How Does Form.io Help With Controlled Form Workflows?**
Form.io gives teams [form management infrastructure](/form-management-software/) for forms, submissions, generated APIs, permissions, workflow actions, and self-hosted deployment. E-Sign+ extends that model by connecting signature verification to submission data instead of treating signing as a disconnected document event.
## **Build Signature Proof Into Your Form Infrastructure**
If your team needs signatures that stay attached to governed form data, application APIs, and your own deployment boundary, [try Form.io for self-hosted form workflows](/try-formio-for-free/).
# JSON Schema Validator Tools for Production Apps
[  ](https://form.io/json-schema-validator-tools-production-apps/)Searches for **json schema validator** often start with a simple need: check whether this JSON payload matches this schema.
That is useful. It is also only the first layer.
In a production app, a schema may validate API requests, generate a form, drive documentation, define a submission shape, feed an AI tool, or become part of a governed application contract. The right tool depends on which job the schema has to do.
## **Key takeaways**
- A JSON Schema validator checks whether JSON data conforms to a declared structure, types, required fields, constraints, and references.
- Online validators are useful for quick checks, but production teams usually need runtime libraries, CI checks, API contract tooling, or form infrastructure.
- Ajv, Python `jsonschema`, and Java validators solve the library problem. They do not own form authoring, submissions, permissions, or deployment governance.
- Form generators turn schema into UI, but the backend still has to store, secure, expose, and govern submitted data.
- Form.io fits when schema needs to become form and API infrastructure: builder, renderer, submissions, generated APIs, permissions, workflow actions, revisions, and customer-controlled deployment.
## **Quick answer: which JSON Schema validator tool should you use?**
Use an online validator when you need to test a small schema and sample payload quickly.
Use Ajv when your JavaScript or TypeScript application needs fast JSON Schema validation in Node.js, the browser, an API gateway, or a build process.
Use Python `jsonschema` when your Python services need to validate instances against JSON Schema drafts and report validation errors in application code.
Use a Java validator such as NetworkNT when JSON Schema validation belongs in a JVM service, API layer, or request/response validation path.
Use Spectral or a schema lifecycle tool when the problem is not one payload, but API governance, linting, bundling, testing, and CI.
Use RJSF, JSON Forms, or SurveyJS when the goal is to generate a form interface from structured schema.
Use Form.io when the schema must become production form infrastructure: a human-facing form, submission record, generated REST API, workflow surface, permission boundary, and governed deployment model.
## **What a JSON Schema validator actually proves**
JSON syntax validation and JSON Schema validation are different jobs.
A JSON syntax validator answers: is this valid JSON?
A JSON Schema validator answers: does this valid JSON match the structure and rules the application expects?
That can include object shape, required fields, string formats, numeric ranges, enum values, array constraints, nested objects, and references to other schema definitions.
The official JSON Schema site describes JSON Schema as the vocabulary that enables JSON data consistency, validity, and interoperability at scale ([JSON Schema](https://json-schema.org/)). The specification hub also separates JSON Schema Core from JSON Schema Validation, where validation defines the keywords used to assert whether data is valid ([JSON Schema specification](https://json-schema.org/specification)).
That distinction matters because many production failures are not syntax failures. They are contract failures.
The payload is valid JSON, but it is missing the field the downstream service expects. The field exists, but the type changed. The UI allowed a value that the backend rejects. The API docs say one thing, but the runtime accepts another. The schema was copied into three services, and now nobody knows which version is authoritative.
A validator can catch part of that. It cannot, by itself, decide where schema ownership lives.
## **The five tool layers behind the search**
The search result page for `json schema validator` looks crowded because people use the same phrase for several different jobs.
**Tool layer****Best fit****What it proves or creates****What the team still owns**Online validatorQuick testing and debuggingA sample JSON instance matches a schemaProduction runtime, security, CI, versioningRuntime validatorAPI requests, service boundaries, app codePayloads satisfy schema rules in a language/runtimeUI, storage, workflows, governanceAPI contract toolingOpenAPI, linting, docs, API style rulesAPI definitions follow a contract and style rulesForm authoring, submissions, application stateForm generatorRendering forms from schemaA schema can produce a user-facing formBackend APIs, permissions, data lifecycleForm/API infrastructureProduction forms, APIs, submissions, workflowsSchema governs form UX, submission shape, generated APIs, and data handlingProduct fit, deployment ownership, policy configurationThe mistake is asking, "What is the best JSON Schema validator?" without asking, "What part of the system needs validation?"
## **Online validators are useful, but limited**
Online validators are useful for quick checks. They help developers paste in a schema, paste in sample JSON, and see errors immediately.
That is often exactly what the searcher wants.
But online validators should not become the production validation strategy. They are poor places for sensitive payloads. They do not enforce validation in your application. They do not live in CI. They do not control what happens after data is accepted.
Use them like a scratchpad.
For production, validation needs to move into the system path: application code, API gateway, test suite, CI pipeline, schema registry, form builder, or platform boundary.
## **Runtime validators: Ajv, Python, Java, and the application path**
Runtime validators belong where your application receives, transforms, or emits JSON.
Ajv is the obvious JavaScript and TypeScript example. Its documentation says it supports JSON Schema draft-04, draft-06, draft-07, draft 2019-09, draft 2020-12, and JSON Type Definition ([Ajv schema language guide](https://ajv.js.org/guide/schema-language.html)). Snyk's package database currently lists Ajv at more than 272 million weekly npm downloads, which shows how deeply validation libraries can sit inside the JavaScript ecosystem ([Snyk Ajv package page](https://security.snyk.io/package/npm/ajv)).
Python teams commonly reach for `jsonschema`, whose documentation shows the simple `validate` function and the validator classes behind it ([Python jsonschema validation docs](https://python-jsonschema.readthedocs.io/en/stable/validate/)).
Java teams may use NetworkNT's JSON Schema Validator, which describes support for multiple drafts and OpenAPI 3 request/response validation ([NetworkNT JSON Schema Validator](https://github.com/networknt/json-schema-validator)).
These tools are important because validation should happen where the system can reject bad data before it spreads.
The practical checklist is straightforward:
- Confirm which JSON Schema draft or dialect your validator supports.
- Reuse compiled validators where the library recommends it.
- Decide whether validation should fail fast or collect all errors.
- Make error messages useful enough for logs, developers, or users.
- Treat `$ref`, remote references, and bundled schemas as design choices, not incidental details.
- Benchmark against your actual schemas and payload sizes if validation runs in a hot path.
Runtime validators are the right answer when the job is validation.
They are not the whole answer when the same schema also needs to create forms, APIs, permissions, workflows, submission records, and audit evidence.
## **API contract tools: where JSON Schema meets OpenAPI**
For API teams, JSON Schema often appears through OpenAPI.
The OpenAPI Initiative's 3.1 release announcement says OpenAPI Schema Objects are now fully compatible with JSON Schema draft 2020-12 ([OpenAPI 3.1 release](https://www.openapis.org/blog/2021/02/18/openapi-specification-3-1-released)). That matters because the schema can become part of request validation, response validation, documentation, mock servers, SDK generation, and contract testing.
This is where tools such as Spectral fit. Spectral is a JSON/YAML linter designed with OpenAPI, AsyncAPI, and JSON Schema in mind ([Spectral](https://stoplight.io/open-source/spectral)). A validator asks whether data satisfies a schema. A linter can ask whether an API definition follows a team rule.
That is a different level of governance.
For production apps, the better question is not "Can we validate this object?" It is:
- Can we keep the API contract and implementation aligned?
- Can we catch drift in CI before release?
- Can we enforce style and security rules across many APIs?
- Can generated docs, mocks, clients, and tests inherit the same contract?
That is where JSON Schema starts becoming part of operational discipline.
## **Schema lifecycle tools: keep schemas from becoming loose files**
When schemas are shared across teams, a single validator is not enough.
Schema files need formatting, linting, testing, bundling, versioning, and promotion through environments. The official JSON Schema tools page shows how broad the ecosystem has become, including validators, documentation generators, schema-to-code tools, schema-to-web-UI tools, benchmarks, and compliance reports ([JSON Schema tools](https://json-schema.org/tools)).
Sourcemeta's JSON Schema CLI is a good example of the production-lifecycle layer. Its repository describes a CLI for maintaining schema repositories and ensuring quality during local development and CI/CD, including formatting, linting, testing, and bundling ([Sourcemeta JSON Schema CLI](https://github.com/sourcemeta/jsonschema)).
This layer matters when a schema is not a one-off file. It is a source artifact.
If multiple services, teams, or applications depend on it, schema changes need review. References need to resolve. Tests need to run. Breaking changes need to be understood before they reach production.
That is the point where teams stop treating JSON Schema as an isolated validator input and start treating it as part of the application contract.
## **Form generators: when schema becomes UI**
Some teams search for a JSON Schema validator and really need a form generator.
RJSF, for example, is a React component capable of building HTML forms out of JSON Schema. JSON Forms is another JSON Schema-based form renderer with data binding, validation, and rule-based visibility.
These tools are useful when a team wants schema to reduce repetitive form UI work.
But a form generator still leaves major production questions open:
- Where are submissions stored?
- Which API receives the data?
- How are permissions enforced?
- How are form changes versioned?
- How do non-developers safely edit forms?
- How does the schema move between dev, test, and production?
- What happens when the form becomes part of a regulated workflow?
A React JSON Schema form can render fields. That does not make it a form platform.
This is the line Form.io crosses.
## **Where Form.io fits**
Form.io belongs in this conversation only after the lower layers are clear.
It is not a replacement for Ajv, Python `jsonschema`, the JSON Schema specification, or OpenAPI tooling.
Form.io is the better fit when schema needs to become form and API infrastructure.
Form.io's Form JSON documentation says Form JSON defines the structure, appearance, and functionality of a form, and that the schema is used for rendering forms, generating REST API interfaces, and hosting the form schema for embedding ([Form.io Form JSON docs](https://help.form.io/form-building/form-json)).
Its feature documentation also explains that the builder outputs JSON schemas rather than static HTML, and that the same schema defines the UI, validation rules, data model, and REST API endpoints ([drag-and-drop form builder and APIs](https://form.io/features/drag-and-drop-form-builder-apis/)).
That is the infrastructure difference.
A validator can say, "This payload is valid."
A form generator can say, "This schema can render a form."
Form.io can connect the form definition, rendered experience, submission data, generated API, permission model, workflow actions, revisions, and deployment boundary.
That includes the operational pieces validators do not try to own: [self-hosted form deployment](https://form.io/features/self-hosted-forms-for-enterprise/), [form revisions](https://form.io/features/form-revisions-form-json-schema), [complete audit trails](https://form.io/features/log-forms-complete-audit-trail/), [secure forms compliance readiness](https://form.io/features/secure-forms-compliance-readiness/), and [fillable PDF workflows](https://form.io/features/fillable-pdf-forms) when the submitted record also needs document output.
That matters for teams building customer portals, healthcare intake, insurance claims, government services, financial onboarding, internal approval workflows, and B2B SaaS products where forms are part of the application architecture.
There is also customer proof behind this pattern. G2's indexed Form.io reviews include a State of Ohio pandemic-response example where Form.io was used to stand up forms, store and present data through an API, and feed analytics dashboards. The same reviewer called the model "easy to manage" across hundreds of websites ([G2 Form.io reviews](https://www.g2.com/products/form-io/reviews)).
Form.io's own customer proof makes the same point from the build-vs-buy side. Edify.ai said speed to market with Form.io "worked fantastically well" and that the team could focus development time on proprietary work instead ([Form.io customer proof](https://form.io/)).
The honest framing is this:
Use a JSON Schema validator when validation is the job.
Use Form.io when the schema needs to become a governed form, API, and submission system.
## **A production checklist for choosing JSON Schema tools**
Before choosing a tool, answer these questions.
### **1. Where does validation happen?**
Validation may belong in the browser, backend service, API gateway, test suite, CI pipeline, ETL job, or form platform.
One schema may need several validators in different places. That is normal. The risk is when each surface evolves its own slightly different rules.
### **2. Which schema version do you support?**
JSON Schema draft support is not trivia. Draft-07, 2019-09, and 2020-12 do not behave identically.
Pin the version. Document it. Make sure your tooling supports it before using draft-specific keywords in production.
### **3. Who owns schema changes?**
If schemas define production behavior, they need ownership.
A change to a field, type, required value, nested object, or reference may affect UI, API behavior, stored submissions, integrations, reports, and historical records.
### **4. Is the schema only validating data, or generating behavior?**
If the schema only validates API payloads, a runtime library may be enough.
If the schema renders forms, generates APIs, controls submissions, and drives workflow behavior, the decision belongs at the platform layer.
### **5. What happens after validation passes?**
This is the question most validator pages skip.
Where does the data go? Who can see it? Can it be edited? Is there revision history? Does it trigger a webhook? Can the workflow be audited? Can the platform run inside your environment?
If those questions matter, you are no longer only choosing a JSON Schema validator.
## **Key takeaways**
JSON Schema validators are necessary tools, but the phrase hides several different jobs.
Online validators help with quick checks. Runtime validators enforce contracts in code. API tooling keeps definitions consistent. Schema lifecycle tools keep shared schemas maintainable. Form generators turn schema into UI.
Form.io is for the next layer: production forms and APIs governed by schema, with submissions, permissions, workflows, revisions, and deployment control attached.
That is the practical distinction. Do not make a validator carry the full application burden. Use the validator where validation belongs, and choose infrastructure when the schema becomes infrastructure.
## **FAQ**
### **What is a JSON Schema validator?**
A JSON Schema validator checks whether JSON data conforms to rules described in a JSON Schema. Those rules can define object structure, required fields, data types, arrays, enums, numeric limits, string formats, and references to other schemas.
### **Is JSON validation the same as JSON Schema validation?**
No. JSON validation usually means checking whether the text is valid JSON syntax. JSON Schema validation checks whether valid JSON data matches an expected schema.
### **What is the best JSON Schema validator for JavaScript?**
Ajv is one of the default choices for JavaScript and TypeScript teams. It supports multiple JSON Schema drafts and is widely used across Node.js and browser environments.
### **What is the best JSON Schema validator for Python?**
Python teams commonly use the `jsonschema` package. It implements JSON Schema validation and provides validator classes, error handling, and draft-aware behavior.
### **Can JSON Schema generate forms?**
Yes, some tools can render forms from JSON Schema. RJSF and JSON Forms are common examples. The important distinction is that rendering a form does not automatically provide backend APIs, submission storage, permissions, or workflow governance.
### **Does OpenAPI use JSON Schema?**
OpenAPI 3.1 aligns its Schema Object with JSON Schema draft 2020-12. That makes JSON Schema more important for API contracts, documentation, request and response validation, and API tooling.
### **Should I paste sensitive data into an online JSON Schema validator?**
For sensitive production data, avoid it. Online validators are useful for examples and debugging, but regulated or customer data should be validated inside tools and environments your team controls.
### **What should production teams check before choosing a validator?**
Check draft support, runtime support, error quality, performance, custom formats, `$ref` handling, CI integration, schema bundling, and how schema changes are governed over time.
### **Is Form.io a JSON Schema validator?**
Form.io is not best understood as a standalone JSON Schema validator. It is a schema-driven form and API platform. It uses schema to help govern forms, submissions, generated APIs, permissions, workflows, and deployment control.
### **When should a team use Form.io instead of only a validator library?**
Use Form.io when the schema needs to operate a production form workflow, not just validate a payload. That includes embedded forms, submission records, generated REST APIs, permissions, workflow actions, revisions, and self-hosted deployment.
### **Can Form.io work alongside validators like Ajv?**
Yes. A production architecture can use validation libraries at service boundaries while using Form.io for the form, API, submission, and workflow layer. The key is deciding which system owns each contract.
If your schema needs to do more than validate JSON, [try Form.io for free](/try-formio-for-free/) and see how forms, APIs, submissions, and workflow controls can live on one foundation.
# Embedded Forms for B2B SaaS: The White-Label Form Builder Comparison
[  ](https://form.io/embedded-forms-b2b-saas-white-label-comparison/)Embedded forms are easy to misunderstand.
For a marketing team, an embedded form might mean a signup widget pasted into a page. For a B2B SaaS platform, it can mean something much heavier: a branded form experience inside the product, customer-managed form creation, tenant-specific permissions, API-backed submissions, and workflow rules that cannot drift from the rest of the application.
That is the difference this comparison is about.
## **Embedded forms become product infrastructure**
An embedded form is a form rendered inside a webpage or application, usually through an iframe, script, SDK, component, or framework integration.
That definition is useful, but too broad. It puts a newsletter signup form and a customer-facing SaaS form builder in the same bucket.
B2B SaaS teams need a sharper distinction:
- Embedded form: a finished form appears inside your website or app.
- Embedded form builder: your users or admins can create and edit forms inside your product.
- White-label form infrastructure: the forms, builder, submissions, APIs, branding, roles, tenant boundaries, and workflow behavior all operate as part of your product.
That last category is where Form.io belongs. The [Form.io Enterprise Form Builder Module](https://form.io/enterprise-form-builder-module/) is built to embed a white-labeled form builder inside an application while the platform owner keeps control over components, data model, permissions, and workflow behavior.
## **Quick comparison**
**Option****Best fit****Main strength****Main tradeoff**Form.ioB2B SaaS teams that need embedded forms, embedded form building, APIs, tenant-aware control, and deployment flexibilityForms behave like governed application infrastructureMore platform than a simple marketing form team needsJotformHosted enterprise teams that want template-rich no-code form building and broad business workflowsFast, familiar hosted form creationStrongest when the form system can remain vendor-hosted and account-centeredFeatheryProduct teams that want polished embedded form UX and a white-label editor experienceStrong product-form experience and editor customizationTeams still need to evaluate backend governance, deployment, and data ownership depthSurveyJSJavaScript teams that want form libraries and a builder they can wire into their own stackDeveloper control inside front-end applicationsMore assembly work around storage, APIs, permissions, and operationsFormsortTeams building branded conversion flowsManaged branded flows with conversion focusNarrower fit when forms become governed product infrastructure123FormBuilder / similar toolsTeams that primarily need branded hosted forms and account-level white labelingFamiliar form-builder packagingWhite label often centers on branding more than application architectureThe right choice depends less on the phrase "embedded forms" and more on what the embedded form has to own.
## **The SaaS evaluation checklist**
If customers only need to submit a contact form, almost any credible form builder can work.
If customers need to create forms inside your application, the checklist changes:
- Can the finished form be embedded cleanly?
- Can the builder itself be embedded?
- Can vendor branding be removed from the form, builder, emails, URLs, and exports?
- Can each tenant have separate forms, submissions, themes, permissions, and workflows?
- Can you restrict which components, validation rules, logic, and publishing actions customers can use?
- Are submissions available through APIs, not only exports or webhooks?
- Where does submission data live?
- Can the form layer run inside the deployment boundary your customers require?
- Are revisions, access controls, and audit evidence part of the model?
- Does the pricing model still work when every customer creates forms?
Those questions are not cosmetic. They are architecture questions.
[Postman's 2025 State of the API report](https://voyager.postman.com/doc/postman-state-of-the-api-report-2025.pdf) found that 82% of organizations had adopted some level of API-first approach. That matters because embedded forms in a SaaS product are not just pixels. They create records, trigger workflows, and pass data to the rest of the application.
## **Where Form.io fits**
Form.io is the strongest fit when embedded forms need to behave like part of the product infrastructure.
The [Form.io form embedding documentation](https://help.form.io/dev/form-embedding) covers quick inline embedding, JavaScript embedding, iframe fallback, builder embedding, and framework embedding. That gives teams a practical path from simple rendering to deeper application integration.
But the more important distinction is what sits behind the embed.
Form.io forms are JSON-driven definitions connected to rendering, validation, submissions, APIs, permissions, and workflow behavior. The [drag-and-drop form builder with APIs](https://form.io/features/drag-and-drop-form-builder-apis/) is not only a UI for arranging fields. It is part of a system where form definitions can become application contracts.
That matters for SaaS platforms where customers need their own forms, variations, permissions, and branded experiences. The [Form.io homepage](https://form.io/) explicitly frames white-label SaaS use around form, API, and data management under the platform's brand or the customer's brand. It also describes multi-tenant child-project patterns for separating forms, data, and form building.
For more controlled environments, the [self-hosted Form.io deployment model](https://form.io/features/self-hosted-forms-for-enterprise/) matters because the form layer can live closer to the customer's infrastructure boundary instead of becoming an external data silo.
## **White label is more than branding**
Most white-label form pages talk about logos, colors, custom domains, badge removal, and branded emails.
Those are real requirements. They are not enough.
In a B2B SaaS product, white label also means the form capability has to respect the product's operating model. A tenant should not see another tenant's forms. A customer admin should not publish components that break downstream processing. A support team should be able to diagnose what changed. A developer should know how submissions map into APIs and workflows.
This is where a light embed starts to strain.
OWASP's API Security Top 10 puts [broken object-level authorization](https://owasp.org/API-Security/editions/2023/en/0xa1-broken-object-level-authorization/) first. That is a useful reminder for SaaS form architecture: if embedded forms create or expose customer records through APIs, authorization has to be object-aware and tenant-aware. Front-end hiding is not governance.
The same logic applies to validation and workflow behavior. The [conditional logic and validation features](https://form.io/features/form-conditional-logic-form-validation/) matter because the form should enforce rules before bad data becomes an API or workflow problem.
## **When a simpler embedded form is enough**
Use a simpler hosted embed when the form is not central to the product.
That includes:
- newsletter signup
- marketing lead capture
- event registration
- contact and support requests
- one-off surveys
- public feedback forms
- low-risk forms that can live in an external form account
In those cases, a hosted form builder with templates, brand settings, and a quick embed code may be the best decision. Jotform, Formsort, 123FormBuilder, and similar tools can be strong fits when speed and convenience are the main job.
The mistake is keeping that architecture after forms become a customer-facing product capability.
## **When embedded form infrastructure is needed**
Embedded form infrastructure becomes important when the form is part of how your SaaS product works.
Examples include:
- customer onboarding flows that differ by tenant
- partner and vendor portals
- regulated intake workflows
- customer-managed form libraries
- embedded application builders
- productized approval flows
- internal workflow forms exposed to external customers
- multi-office or multi-group customer operations
In these cases, forms need lifecycle control. NIST's [Secure Software Development Framework](https://csrc.nist.gov/pubs/sp/800/218/final) treats security practices as part of the software development lifecycle, which is the right lens for embedded form capability that ships inside a SaaS product. The form builder is no longer an outside utility. It is part of the product surface.
Data risk also changes the decision. [Thales' 2025 Cloud Security Study](https://cpl.thalesgroup.com/cloud-security-research) reported that 54% of cloud data is sensitive and that only 8% of respondents encrypt 80% or more of cloud data. That does not mean every embedded form needs self-hosting. It does mean SaaS teams should know where form data lives, who can access it, how it is encrypted, and how it moves through APIs.
## **Customer proof: white-label forms as a business model**
The white-label use case is not theoretical for Form.io.
In Form.io's Bursting Silver case study, the company describes how a regulatory-industry platform [white-labeled Form.io](https://form.io/case-studies/from-facing-the-risk-of-losing-an-entire-industry-to-generating-millions-and-having-new-clients-call-them/) to support its industry, sign dozens of new clients, and increase revenue by 25%.
That proof point matters because it connects embedded forms to a business model, not just a UI decision. When forms are a capability customers use inside your product, the form layer can influence retention, onboarding, service load, expansion, and product differentiation.
## **The decision framework**
Choose a simple embedded form when the form is a page element.
Choose a hosted enterprise form builder when business users need fast form creation and the external vendor account model is acceptable.
Choose a JavaScript form library when your team wants front-end control and is ready to build the backend, storage, permissions, and operational layer around it.
Choose Form.io when the form capability needs to become part of your product architecture: embedded rendering, embedded building, customer self-service, white-label experience, structured schemas, generated APIs, permissions, validation, workflow behavior, and deployment control.
That is the real difference.
Embedded forms are not automatically infrastructure. But in B2B SaaS, they often become infrastructure faster than teams expect.
## **Key takeaways**
- Embedded forms can mean a simple widget, an embedded form builder, or full white-label form infrastructure.
- SaaS teams should evaluate builder embedding, tenant separation, data ownership, APIs, permissions, workflow behavior, and deployment model.
- Competitors can be good fits for hosted no-code forms, polished product forms, developer libraries, or branded conversion flows.
- Form.io is strongest when the form layer needs to stay connected to schemas, APIs, submissions, permissions, and workflows inside the product architecture.
- A simple embed is enough for low-risk marketing forms. It is not enough when customers need to build and govern forms inside your SaaS.
## **FAQ**
### **What are embedded forms?**
Embedded forms are forms rendered inside a webpage or application through an iframe, script, SDK, component, or framework integration. The user completes the form without leaving the surrounding site or product experience.
### **What is an embedded form builder?**
An embedded form builder is a builder or editor exposed inside your application so users can create or change forms without going to a separate vendor dashboard.
### **What does white-label mean for forms?**
At minimum, white label usually means custom branding, colors, domains, and removal of vendor badges. For SaaS platforms, it should also include builder experience, tenant separation, emails, exports, permissions, and workflow behavior.
### **Can customers create their own forms inside a SaaS product?**
Yes, if the platform supports embedded form building. The important question is whether customers can do that inside guardrails your product controls.
### **Are iframe embedded forms enough?**
Sometimes. Iframes can be practical for low-risk or simple use cases. They are often weaker when the form needs deep styling, app authentication, event handling, tenant-aware permissions, or tight workflow integration.
### **Which embedded form builder is best for multi-tenant SaaS?**
Form.io is a strong fit when multi-tenant SaaS teams need white-labeled form creation, APIs, permissions, structured submissions, workflow behavior, and deployment control. Simpler tools may fit when the requirement is only branded form capture.
### **Do embedded forms create security risks?**
They can if teams treat them as front-end widgets while the data becomes sensitive application data. The right controls depend on authorization, validation, tenant separation, encryption, auditability, and where submissions are stored.
### **When should I choose Form.io over a simpler form builder?**
Choose Form.io when forms are part of the application infrastructure: customers create forms, submissions feed APIs, permissions matter, workflows depend on form data, and the deployment boundary is important.
### **Can Form.io replace my whole application backend?**
No. Form.io is infrastructure for forms, APIs, submissions, validation, permissions, and workflow-related actions. Your application still needs its own product logic, user experience, integrations, and surrounding architecture.
## **Build embedded forms that behave like your product**
If your SaaS customers only need a form on a page, keep it simple.
If they need governed, branded, customer-managed forms inside your product, start with infrastructure that can carry the form, data, API, and workflow model together.
[Try Form.io for white-label embedded form infrastructure](/try-formio-for-free/).
# Claims Management Software Starts With The Forms That Feed It
[  ](https://form.io/claims-management-software-insurance-form-builders/)Claims management software comparisons usually start with the core claims system.
That makes sense. Carriers, TPAs, MGAs, adjusters, and self-insured organizations need systems for assignment, reserves, adjudication, payments, subrogation, reporting, and closure.
But many claims problems start earlier.
They start at the first notice of loss. They start when a claimant uploads the wrong document, an adjuster captures incomplete field notes, an agent enters policy data twice, or a regulatory form has to be recreated from unstructured intake data.
Before a claim can be managed, the data has to be captured.
That is why insurance teams should evaluate the form infrastructure behind the claims workflow, not only the claims platform itself.
## **Key Takeaways**
- Claims management software and claims form infrastructure solve different layers of the same workflow.
- Full claims systems manage the claim lifecycle. Form infrastructure governs intake, validation, files, submissions, APIs, PDFs, permissions, and handoff.
- Claim handling is a high-risk customer and regulator touchpoint, so weak intake creates downstream cost.
- Form.io is not a full claims-core replacement. It is a strong fit when insurance forms need to become embedded, API-backed, self-hosted workflow infrastructure.
- The right evaluation question is not only "which claims system?" It is also "what form layer feeds and extends the claims system?"
## **What Claims Management Software Usually Means**
In most buyer guides, claims management software means a system that supports the claims lifecycle from first notice of loss through settlement and closure.
The category usually includes:
- FNOL and claims intake
- claim assignment and triage
- document and image management
- policy lookup
- investigation and adjudication
- reserve management
- payments and settlement
- regulatory reporting
- analytics and dashboards
- customer status updates
- closure and audit history
That is why systems like Guidewire ClaimCenter, Duck Creek Claims, Riskonnect, FINEOS, VCA, BriteCore, Snapsheet, and other claims platforms dominate the search results for **claims management software**.
They are solving a large operational problem.
Form.io should not be framed as a replacement for those systems when the buyer needs a full claims core. If your team needs end-to-end claims adjudication, reserve management, litigation tracking, payment workflows, subrogation, CAT-scale claims operations, or deep P&C suite functionality, a claims management platform is the right category to evaluate.
But claims systems do not remove the need for form infrastructure.
They often create more of it.
## **Why Claims Intake Is An Infrastructure Problem**
Claims are where the insurer's promise becomes visible.
The customer does not experience the claims system as a data model or an admin workflow. They experience it as a form, a file upload, a status update, an estimate, a call, a missing document request, or a delay.
That is why digital claims workflows have real retention stakes. J.D. Power's 2025 U.S. Claims Digital Experience Study reported that insurers deliver adequate digital updates only 22% of the time. Insurance Journal's coverage of the study also reported that 52% of auto and homeowners customers who rate their digital claim experience as "poor" or "just OK" are likely to leave or not renew, compared with 4% of customers who rate the experience as "excellent" or "perfect" ([Yahoo Finance syndication of J.D. Power release](https://finance.yahoo.com/news/fully-digital-claims-processing-drives-120000409.html), [Insurance Journal](https://www.insurancejournal.com/news/national/2025/12/09/850297.htm)).
Weak intake also shows up in complaint patterns. The NAIC says delays, denials, and unsatisfactory settlements are among common reasons consumers file complaints, and that consumers are asked to gather supporting documents, photographs, correspondence, phone logs, and detailed accounts when filing complaints ([NAIC](https://content.naic.org/article/how-file-complaint-and-research-complaints-against-insurance-carriers)). A ValuePenguin analysis of NAIC closed complaint data reported that claim handling accounted for 65.2% of closed insurance complaints in 2024, with delays and unsatisfactory settlements or offers as the top claim-handling complaint types ([ValuePenguin](https://www.valuepenguin.com/most-common-insurance-complaints)).
Those numbers do not prove a form platform fixes claims operations by itself.
They prove the stakes.
If claims data enters the workflow through weak forms, disconnected uploads, duplicated manual entry, unclear validation, or inconsistent status paths, the claims system inherits that mess.
## **The Claims Workflow Surfaces That Depend On Forms**
Insurance forms are not only contact forms.
In a claims environment, forms show up across the workflow:
- policyholder FNOL forms
- agent and broker claim submission forms
- adjuster field reports
- inspection and damage assessment forms
- photo, video, and document upload flows
- repair estimate collection
- medical record and proof-of-loss intake
- third-party claimant forms
- loss run request forms
- policy application and endorsement forms
- regulatory filing packets
- PDF outputs for records, signatures, reviews, or state-specific requirements
Some of these forms are customer-facing. Some are internal. Some are embedded in portals. Some are mobile. Some still need to map back to exact PDF-style layouts because insurance operations have not escaped document reality.
That is the layer where form infrastructure matters.
A claim can move through a core system, but the surrounding form layer still has to answer practical questions:
- Who can submit this form?
- Which fields are required for this claim type?
- Can the claimant save and resume?
- Can an adjuster collect data offline?
- Can photos and documents be attached securely?
- Does the submitted data become structured JSON, or does someone retype it later?
- Can the submission feed an API, webhook, claims core, document repository, or analytics pipeline?
- Can the same data produce a PDF output when a regulator, carrier, or partner still needs one?
- Can changes to the form and submission be audited?
Those are not cosmetic questions. They are workflow architecture.
## **What To Evaluate In The Claims Form Layer**
A serious claims-intake form layer should be evaluated on more than field layout.
### **Conditional Logic**
Insurance workflows vary by claim type, line of business, state, channel, and role.
A property claim does not ask the same questions as a cyber liability claim. A claimant portal does not need the same view as an adjuster workflow. A policyholder should not see every internal field an examiner needs.
The form layer should support conditional logic, role-specific screens, and dynamic form paths without forcing every variation into custom code.
### **Validation Before Handoff**
The worst time to discover bad data is after it reaches the claims system.
Claims forms should validate required fields, dates, policy identifiers, file requirements, numeric values, and conditional dependencies before submission. They should reduce preventable downstream rework without pretending every claim is simple.
### **File And Evidence Capture**
Claims intake often depends on documents and media: photos, estimates, police reports, medical documents, invoices, inspection records, correspondence, and proof-of-loss materials.
The form layer should treat uploads as part of the submission record, not as an afterthought in a shared inbox.
### **Generated APIs And System Handoff**
Claims data rarely stays in one place.
It may need to feed a claims core, policy system, CRM, document management platform, analytics warehouse, notification workflow, payment process, or regulatory reporting path.
That is why static forms are not enough. The form layer should expose structured submission data through APIs and integration patterns that developers can control. For Form.io, that includes [drag-and-drop forms with generated APIs](https://form.io/features/drag-and-drop-form-builder-apis/) rather than forms that stop at display and email notification.
### **Permissions And Submission Access**
Insurance workflows are role-sensitive.
Policyholders, agents, adjusters, claim supervisors, legal teams, compliance teams, and admins should not all see the same data. A useful form platform needs access control around forms and submissions, not just a login screen in front of everything.
### **Auditability**
Claims records can become evidence.
If a form changes, a submission is edited, a file is replaced, or a workflow action fires, teams need to understand what changed, who changed it, and when. Auditability is not decoration in regulated workflows.
That is why a claims form layer should include a [complete audit trail for form changes and submissions](https://form.io/features/log-forms-complete-audit-trail/), especially when operational records may later be reviewed by legal, compliance, or regulator-facing teams.
### **PDF And Regulatory Output**
Insurance still runs on documents.
NAIC's SERFF industry training page describes electronic rate and form filing as including form submittal, document management, and review access, while supporting compliance with consumer protection requirements ([NAIC SERFF](https://content.naic.org/node/10174)). That does not mean every claims form feeds SERFF. It does mean "forms" in insurance often exist inside regulated document and review workflows.
Good form infrastructure should let teams collect structured data through modern web forms while still producing PDF outputs when official, partner, regulatory, or legacy processes require them.
That can include [custom PDF templates](https://form.io/features/pdf-forms-pdf-template-designer/) and [fillable PDF forms](https://form.io/features/fillable-pdf-forms/) when the workflow has to preserve document fidelity without giving up structured submission data.
## **Where Form.io Fits**
Form.io fits when the forms around claims management need to become application infrastructure.
That does not mean Form.io is a claims adjudication engine. It does not calculate reserves, run a full claims core, or replace every specialized insurance platform.
It means Form.io can support the form, API, submission, PDF, and workflow layer that surrounds those systems.
Form.io's public insurance PDF page speaks directly to this type of insurance workflow: outputting submissions to PDF, turning PDFs into embeddable dynamic forms, tracking changes to fields and forms, auto-populating repeated data, autosaving unfinished forms, collecting offline, and using mobile-responsive forms ([Form.io insurance PDF forms](https://form.io/industries/pdf-forms-for-insurance/)).
The official Form.io documentation also describes two PDF paths: PDF output from webform submissions and PDF-first forms where teams upload a PDF and place interactive fields on top of it. PDF Plus adds PDF-first experiences with pixel-perfect PDF backgrounds and JSON-driven overlays, while PDF Basic supports printing and downloading webform submissions as PDFs ([Form.io docs](https://help.form.io/form.io-concepts.md?ask=How%20does%20Form.io%20support%20PDF%20forms%20and%20PDF%20output%20from%20webform%20submissions%3F)).
That matters for insurance because the buyer often needs both:
- modern, embedded, API-backed data capture
- document-style outputs that still match policy, claims, underwriting, or regulatory expectations
Form.io also matters when teams need forms and APIs together. The platform is designed around JSON-defined forms, submissions, generated APIs, permissions, workflow actions, and customer-controlled deployment. For insurance teams, that can support workflows such as:
- embedded FNOL forms inside a policyholder portal
- agent-facing application and claims intake
- adjuster inspection forms with file uploads
- internal review forms for claims operations
- self-hosted data capture for sensitive records
- structured submission APIs into existing claims or policy systems
- PDF outputs for claim packets, confirmations, or document-heavy workflows
This is the useful distinction:
Claims management software manages the claim.
Form.io can govern the form infrastructure that captures and moves the data the claim depends on.
## **Comparison: What To Ask Before Choosing The Form Layer**
## **Evaluation question****Why it matters****What to look for**Can the form handle different claim types?Claims vary by line, state, product, and roleConditional logic, reusable components, role-specific flowsCan users upload documents and photos?Evidence is often the claim recordSecure file upload, file metadata, submission associationDoes the form validate data before submission?Bad intake data creates downstream reworkRequired fields, conditional validation, typed data, calculated valuesDoes submission data have an API?Claims data must move into other systemsREST APIs, webhooks, JSON submissions, developer-controlled handoffCan permissions be scoped?Insurance workflows are role-sensitiveForm and submission permissions, own-vs-all access, admin boundariesCan changes be audited?Claims and regulated forms need evidenceChange history, audit logs, revision-aware workflowsCan web submissions become PDFs?Insurance still needs documentsPDF output, PDF templates, PDF-first forms, existing PDF conversionCan it be embedded?Claims intake lives inside portals and productsEmbeddable renderer, embedded builder, white-label controlsCan it be self-hosted?Some insurance data must stay inside controlled environmentsCustomer-controlled deployment, database, file storage, network boundary**When A Full Claims Management Platform Is The Better Fit**
Use a full claims management platform when the core problem is managing the claim lifecycle itself.
That includes:
- claim assignment and triage
- reserve management
- adjudication workflows
- payments and settlement
- subrogation and recovery
- litigation management
- catastrophe scale handling
- repair network workflows
- claims analytics
- policy and billing suite integration
- specialized P&C, health, life, or workers' compensation claim operations
This is where platforms like Guidewire, Duck Creek, Riskonnect, FINEOS, VCA, BriteCore, Snapsheet, and other insurance-specific systems belong in the evaluation.
Trying to force a form infrastructure platform to behave like a complete claims core would be the wrong move.
But it is equally risky to assume the claims core solves every form problem around it.
Many carriers already have core systems. The friction is in the portals, supplemental forms, customer-facing intake, partner workflows, document packets, regulatory outputs, and integration surfaces around those systems.
That is where a dedicated form infrastructure layer can make sense.
## **When To Evaluate Form Infrastructure Separately**
Evaluate the form layer separately when any of these are true:
- Your claims core works, but customer or agent intake is weak.
- You need embedded forms in a portal, app, or white-labeled product.
- Claims data must feed multiple downstream systems.
- Different teams need to create or modify forms without breaking the architecture.
- Documents and PDFs are still part of the official workflow.
- You need structured APIs instead of manual re-entry.
- You need submission-level permissions and audit evidence.
- You need to self-host the form and submission layer.
- You need offline or mobile-responsive collection.
- You need a repeatable way to turn form changes into governed application behavior.
This is the buyer Form.io should speak to.
Not the buyer looking for the quickest online form.
Not the buyer who wants to replace every claims system overnight.
The buyer whose forms have become infrastructure.
## **Customer Proof: Insurance Forms Are Operational Systems**
Form.io has public insurance-adjacent proof through E-Risk Services, LLC, described in a Form.io case study as a specialty-lines underwriting subsidiary of Nationwide Insurance Company. The case study says E-Risk built a CRM in two months instead of two years ([Form.io case study](https://form.io/case-studies/building-a-crm-took-2-months-instead-of-2-years/)).
That proof point should be used carefully. It is a Form.io-hosted case study, not an independent Nationwide-hosted validation of the timeline.
But it is still relevant because E-Risk's public Nationwide page shows the real insurance surfaces around specialty lines: product pages, applications and forms, policy forms, loss run requests, expiring policy requests, underwriting contact paths, quoting, and servicing ([Nationwide E-Risk](https://www.nationwide.com/excessandsurplus/e-risk/)).
That is the practical pattern.
Insurance teams do not only need one claims screen. They need many controlled data-capture and document workflows around underwriting, servicing, claims, renewals, requests, and regulated communications.
Form infrastructure is how those workflows stay usable without becoming disconnected spreadsheets, PDF piles, email chains, and one-off portals.
The customer language from another Form.io-hosted case study is useful here because it describes the same infrastructure burden in plain terms. In the Safety Mojo case study, a long-time Form.io platform user said, "Form.io cleans up all the dirty work and does it for you" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)). That quote is not insurance-specific, but it fits the architectural point: forms become expensive when every team has to rebuild the form, data, API, and workflow plumbing separately.
## **The Decision Rule**
Choose a claims management platform when the main requirement is claims-core operation.
Choose Form.io when the main requirement is governed form infrastructure around insurance workflows.
That means forms that can render in your application, collect structured data, validate submissions, handle files, expose APIs, support permissions, produce PDFs, and live inside your deployment boundary.
For teams with stricter data-control requirements, [self-hosted enterprise forms](https://form.io/features/self-hosted-forms-for-enterprise/) can keep the form, submission, and file-handling layer inside the environment the organization controls.
For insurance teams, this distinction matters because "claims management software" is not one decision.
It is at least two:
1\. What system manages the claim lifecycle? 2. What infrastructure captures, governs, and moves the data that feeds it?
Most comparisons answer only the first question.
The second question is where Form.io belongs.
## **FAQ**
### **What Is Claims Management Software?**
Claims management software helps insurance teams manage claims from intake through assignment, investigation, adjudication, settlement, reporting, and closure. It often includes FNOL, document management, workflow automation, payments, analytics, and compliance features.
### **Is Form.io Claims Management Software?**
Form.io is not a full claims management platform or claims-core system. It is form and API infrastructure that can support the intake, submission, document, PDF, permission, and integration layer around claims workflows.
### **Can Form.io Replace Guidewire Or Duck Creek?**
Not when the requirement is a full claims core. Guidewire, Duck Creek, and similar systems are built for end-to-end claims operations. Form.io is a better fit when teams need governed forms, APIs, submissions, PDFs, and embedded intake around those systems.
### **What Is FNOL Software?**
FNOL software supports first notice of loss: the initial claim report. A strong FNOL workflow captures structured claim data, claimant details, incident information, documents, photos, and routing data so the claim can move into the right downstream process.
### **Why Do Insurance Claims Workflows Need Better Forms?**
Claims workflows depend on accurate intake. If forms collect incomplete data, miss required documents, fail to validate fields, or force manual re-entry, the claims process slows down and customer experience suffers.
### **Can Claims Forms Collect Photos And Documents?**
Yes, but the important question is how those files are stored, associated with submissions, permissioned, and handed off. Claims evidence should be part of the structured submission workflow, not a loose email attachment.
### **How Do PDF Forms Fit Insurance Claims?**
Many insurance workflows still require PDF-style outputs, forms, packets, or official documents. A modern form layer should collect structured web data while still supporting PDF output or PDF-first forms when the workflow requires document fidelity.
### **What Should Insurers Evaluate In Claims Intake Software?**
Evaluate conditional logic, validation, file uploads, submission APIs, permissions, audit logs, embedded rendering, PDF output, mobile/offline support, and deployment control. The form layer should support the claims architecture, not just display fields.
### **Do Claims Workflows Need Self-Hosted Forms?**
Not always. Self-hosting matters when sensitive claims data, regulatory expectations, customer requirements, or enterprise architecture require the form and submission layer to run inside a controlled environment.
### **How Can Forms Connect To Claims Management Systems?**
Forms can connect through APIs, webhooks, submission exports, custom integrations, document workflows, or middleware. The important requirement is structured, validated submission data that downstream systems can consume reliably.
## **Build Claims Intake Infrastructure With Form.io**
If your team needs a full claims-core platform, evaluate claims management systems directly.
If your team needs better claims intake, embedded insurance forms, PDF outputs, generated APIs, controlled submissions, and customer-hosted form infrastructure, evaluate the form layer separately.
[Try Form.io for insurance form infrastructure](https://form.io/try-formio-for-free/).
# KYC Onboarding Software for Financial Services: Forms, APIs, and Audit-Ready Intake
[  ](https://form.io/kyc-onboarding-software-financial-services-form-platforms/)KYC onboarding software is usually evaluated as an identity verification purchase.
That is only part of the system.
Banks, fintechs, lenders, and other financial-services teams still have to collect customer data, route exceptions, connect verification providers, preserve evidence, and keep sensitive workflows under control. The right question is not only which KYC provider to buy. It is what intake infrastructure the provider connects to.
## **Key Takeaways**
- KYC onboarding software includes identity checks, but the surrounding intake layer matters just as much.
- Dedicated KYC vendors are strongest for document verification, sanctions screening, adverse media, KYB data, biometrics, and verification coverage.
- Form.io is a better fit for the application infrastructure around those checks: embedded forms, structured submissions, generated APIs, permissions, workflows, revisions, audit trails, and customer-controlled deployment.
- Financial-services teams should evaluate who owns the schema, submission record, API handoff, audit evidence, and change-control path.
- The strongest architecture often combines a KYC verification vendor with a governed form platform that controls intake inside the customer's own product and environment.
## **What KYC Onboarding Software Has To Handle**
KYC onboarding is not a simple signup form with a document upload bolted on.
In financial services, onboarding can involve customer identity, beneficial ownership, business entity details, risk indicators, attestations, document evidence, sanctions and PEP checks, adverse media review, manual exception handling, approvals, and ongoing updates.
The fraud pressure behind those workflows is real. The Federal Trade Commission reported that consumers lost more than $12.5 billion to fraud in 2024, a 25% increase from the prior year ([FTC](https://www.ftc.gov/news-events/news/press-releases/2025/03/new-ftc-data-show-big-jump-reported-losses-fraud-125-billion-2024)). That number does not prove any one onboarding product prevents fraud. It does show why financial-services teams treat identity, intake, and evidence workflows as risk infrastructure.
For covered financial institutions, customer due diligence also extends beyond one-time identity capture. FinCEN describes CDD as policies and procedures that identify and verify customers and beneficial owners, understand customer relationships for risk profiling, and support ongoing monitoring and customer-information updates ([FinCEN](https://www.fincen.gov/news/news-releases/fincen-reminds-financial-institutions-cdd-rule-becomes-effective-today)). FinCEN's 2026 exceptive relief narrowed repeat beneficial-owner verification at every new account opening, but preserved initial verification, risk-based updates, and ongoing monitoring obligations ([FinCEN](https://www.fincen.gov/news/news-releases/fincen-issues-exceptive-relief-streamline-customer-due-diligence-requirements)). Digital identity guidance makes the same point from another angle: NIST SP 800-63A-4 defines identity proofing and enrollment requirements across three identity assurance levels, with evidence, validation, and verification expectations that affect onboarding design ([NIST SP 800-63A-4](https://csrc.nist.gov/pubs/sp/800/63/a/4/final)). FFIEC authentication guidance also emphasizes layered security and stronger controls than single-factor authentication for financial institution services and systems ([FFIEC authentication guidance](https://www.ffiec.gov/news/press-releases/2021/pr-08-11)).
That is the operating reality KYC onboarding software has to support.
It has to help the organization answer:
- What information do we need for this customer type?
- Which evidence is required for this product, jurisdiction, or risk profile?
- Which verification provider or internal service should receive the data?
- Who reviews exceptions?
- Which decisions and changes need to be retained?
- Where does the submission record live?
- How do we update customer information later without losing history?
Those are not only compliance questions. They are application architecture questions.
## **The Three Layers Of KYC Onboarding Software**
Most KYC software pages collapse three different layers into one category.
That makes comparison harder than it needs to be.
### **1. KYC Verification And Data Providers**
This is the layer buyers usually think of first.
KYC verification providers handle identity document verification, database checks, liveness or biometric checks, sanctions screening, PEP screening, adverse media, fraud signals, KYB data, business registry checks, and beneficial ownership data.
If your main problem is global identity coverage, document authenticity, fraud detection, sanctions data, or KYB intelligence, this is the category you should evaluate.
Form.io does not replace that layer.
### **2. Client Lifecycle And Case Workflow Platforms**
Some financial institutions need a broader client lifecycle management system.
That can include onboarding cases, risk scoring, relationship-manager queues, remediation workflows, periodic refresh, monitoring, approvals, dashboards, and enterprise reporting.
If the primary buyer need is a complete CLM suite for a large financial institution, a specialized onboarding or CLM platform may be the right center of gravity.
Form.io does not claim to be a full AML case-management system.
### **3. Form And Application Infrastructure**
This is the layer many comparisons understate.
Before a verification service can check anything, the organization has to collect the right data, validate it, structure it, submit it, secure it, route it, and keep the record. That work often happens in forms embedded inside account-opening flows, borrower portals, investor onboarding flows, agent portals, internal review tools, and customer update workflows.
This is where Form.io belongs.
Form.io is not the sanctions database, fraud network, or identity bureau. It is the schema-driven form and API infrastructure that can sit around those systems when the customer needs to own the intake experience and the data path.
## **Why Static Forms Break KYC Workflows**
Static forms are comfortable until the onboarding workflow branches.
A retail deposit account does not collect the same evidence as a commercial lending application. A sole proprietor does not require the same entity structure as a multi-owner company. A low-risk domestic customer does not follow the same path as a higher-risk customer, foreign entity, trust, money-services business, or politically exposed person.
KYC onboarding software often has to branch by:
- individual versus business customer
- account or product type
- jurisdiction
- entity structure
- risk level
- ownership profile
- required documents
- missing or inconsistent information
- applicant role
- reviewer role
- periodic refresh or customer update
If those branches live in hard-coded forms, spreadsheets, PDFs, or ad hoc portal logic, the onboarding workflow becomes brittle. Compliance teams cannot change requirements cleanly. Developers cannot route data consistently. Reviewers inherit partial records. Customers get asked for the wrong information.
The stronger model is a governed intake schema: the form defines the data structure, validation, conditional logic, submission record, API handoff, and change path.
That is the Form.io argument.
## **What A KYC Intake Layer Should Provide**
The form layer behind KYC onboarding software should be evaluated as infrastructure, not as a decorative front end.
### **Dynamic Forms And Validation**
KYC intake should adapt to the customer, product, jurisdiction, entity type, and risk profile.
The platform should support [conditional logic and validation](https://form.io/features/form-conditional-logic-form-validation/), reusable components, calculated values, required evidence, document upload fields, consent language, and validation rules. The goal is not to make a long form look nicer. The goal is to collect the right information before the workflow reaches verification, review, or downstream systems.
### **Structured Submission Records**
For KYC, a submitted form is not just a message.
It is a record of what was asked, what was provided, which files were attached, what metadata came with the submission, and what later changed. Submission data needs to remain accessible for internal systems, reviewers, reports, and audit workflows.
Form.io's documentation describes forms as the structure that collects, validates, and stores user data, while the same form structure defines a backend API for managing and accessing submitted data ([Form.io docs](https://help.form.io/userguide/forms)). That structure matters when KYC data needs to move beyond a form inbox.
### **API Handoff To Verification And Core Systems**
KYC onboarding almost always depends on other systems.
Data may need to move into identity verification providers, sanctions or PEP screening services, CRM, core banking, lending systems, document management, case management, data warehouses, notification tools, and compliance reporting.
For Form.io, the strongest claim is architectural: every form, resource, submission, and project is accessible through a REST API, with predictable endpoints and submission paths that developers can connect to other systems ([data integration tools](https://form.io/features/data-integration-tools-for-enterprise-forms/)). Webhook actions can also send submission payloads to external endpoints when events occur.
That does not mean Form.io ships every KYC vendor integration out of the box.
It means teams can build the intake and handoff layer around the verification tools they choose.
### **Role-Based Access**
KYC data is role-sensitive.
Applicants, authorized representatives, relationship managers, compliance analysts, operations staff, auditors, developers, and administrators should not all see or edit the same data.
The intake layer should support [role and submission permissions](https://help.form.io/developers/roles-and-permissions.md) around forms, submissions, admin surfaces, and review workflows. This matters because KYC onboarding often blends customer-facing and internal workflows. One weak permission model can turn a controlled process into an overexposed one.
### **Revisions And Audit Logs**
Regulated onboarding workflows need history.
If a customer updates business ownership details, a reviewer changes a risk classification, a required field is added, or an administrator modifies access, the organization needs to know what happened.
Form.io describes two complementary logging systems: Submission Revisions for field-level submission changes and Server Audit Logging for system activity such as form access, authentication, and API-level data modifications ([audit trail capabilities](https://form.io/features/log-forms-complete-audit-trail/)). Those capabilities fit KYC intake because the evidence trail is part of the workflow, not an afterthought.
Availability and configuration still matter. Teams should confirm which modules, settings, and license terms apply before making compliance commitments.
### **Deployment And Data Boundary Control**
KYC onboarding touches sensitive personal and business information.
Some financial-services teams can use hosted tools without issue. Others need stricter control over environment, authentication, database, file storage, network access, logging, and vendor exposure.
That is where [self-hosted forms](https://form.io/features/self-hosted-forms-for-enterprise/) or customer-controlled deployment becomes part of the buying decision. Form.io is strongest when the intake layer needs to live inside the customer's architecture rather than as a disconnected third-party form surface.
## **How Form.io Fits Beside KYC Verification Vendors**
The right architecture is often not Form.io instead of a KYC vendor.
It is Form.io around the KYC vendor.
A financial-services team might use Form.io to build an [embedded onboarding flow](https://form.io/features/drag-and-drop-form-builder-apis/) that collects customer and entity data, validates required fields, captures documents, stores submissions, applies role-based access, and exposes the submission through APIs. The same workflow can then call identity verification, document verification, sanctions screening, fraud, CRM, or core system services.
That division of responsibility is clearer and more credible:
**Layer****What It Does****Typical Fit**KYC verification providerIdentity proofing, document checks, sanctions or PEP screening, KYB data, fraud signalsUse when verification intelligence and coverage are the core needCLM or onboarding suiteCases, queues, lifecycle workflows, risk review, remediation, dashboardsUse when the institution needs a broad onboarding operating systemForm.io intake infrastructureEmbedded forms, structured submissions, generated APIs, permissions, revisions, audit trails, workflow handoff, self-hosted deploymentUse when the team needs to own the intake layer inside its product and systemsThis distinction also keeps the compliance claim honest.
Form.io can support regulated KYC onboarding controls. It does not make an organization compliant by itself. It does not replace AML policy, compliance staff, model validation, legal review, sanctions data, transaction monitoring, or the specialized identity providers that verify people and businesses.
It gives teams the form/application layer those systems need to receive clean, structured, governed intake data.
## **KYC Onboarding Software Evaluation Checklist**
When evaluating KYC onboarding software, ask who owns each part of the workflow.
**Evaluation question****Why it matters****What to check**Who owns the intake schema?KYC requirements change by customer type, product, jurisdiction, and risk profileForm definitions, reusable components, conditional logic, validation, versioningCan the workflow collect documents and evidence?Verification and review often depend on file evidenceSecure uploads, metadata, submission association, downstream accessDoes the submission have an API?KYC data needs to move into verification, CRM, case, banking, lending, and reporting systemsREST APIs, webhooks, JSON submissions, authentication, retry/error patternsCan permissions be scoped by role?Applicants, reviewers, admins, and auditors need different accessForm permissions, submission permissions, own/all access, SSO role mappingIs the workflow auditable?Reviewers need to understand changes and decisionsSubmission revisions, form revisions, audit logs, timestamps, user identity, notesCan the system support ongoing updates?KYC and CDD are not always one-time eventsCustomer refresh flows, changed-information capture, reviewer routing, historical recordsCan the intake live inside your product?Customer onboarding often belongs inside a portal or applicationEmbedded renderer, white-label controls, developer-owned front endCan the environment be controlled?Some teams need strict data boundary and infrastructure controlSelf-hosted or customer-controlled deployment, database/storage options, logging integrationDoes the product overclaim compliance?Software supports controls; it does not replace legal obligationsClear scope, configuration details, module requirements, evidence of controlsThe checklist helps separate a strong verification tool from a strong intake platform.
Some buyers need both.
## **When A Dedicated KYC Vendor Is The Better Fit**
Use a dedicated KYC vendor when the primary need is verification intelligence.
That includes:
- identity document verification
- biometric or liveness checks
- sanctions, PEP, and adverse media screening
- KYB data and business registry checks
- beneficial ownership data services
- fraud network signals
- country-specific document coverage
- transaction monitoring or AML case management
Those are specialized capabilities. A form platform should not pretend to replace them.
The same is true for a full client lifecycle suite. If the institution needs enterprise case management, risk scoring, remediation workflows, onboarding dashboards, periodic refresh operations, and compliance-team queues in one packaged system, a CLM platform may be the better center of gravity.
Form.io becomes more relevant when the organization already has or plans to choose those systems, but still needs to own the form layer that feeds them.
## **Where Form.io Is The Better Fit**
Form.io is the better fit when the KYC onboarding workflow is also a product, integration, and governance problem.
That usually means:
- onboarding forms need to be embedded inside a customer portal or internal product
- the data model needs to be controlled by the application team
- submissions need to become API-accessible records
- KYC providers need to be called from the workflow rather than own the whole experience
- permissions need to be scoped across applicants, reviewers, admins, and service accounts
- form and submission changes need revision history
- audit logs need to feed operational or compliance tooling
- sensitive intake data needs to remain in customer-controlled infrastructure
- teams need one governed form layer across multiple onboarding use cases
That is the buyer who should evaluate Form.io as part of a KYC onboarding software stack.
A Trustpilot reviewer called Form.io a "powerful embedded form builder" and wrote that it was "seamlessly built into our B2B application" ([Trustpilot](https://www.trustpilot.com/review/form.io)). That is a small proof point, but it points at the right fit: Form.io is strongest when developers and regulated teams need data management, integration, and control around forms, not just a hosted questionnaire.
## **Bottom Line**
KYC onboarding software is not one product category.
It is a stack.
Verification vendors help confirm identity, screen risk, and supply data. CLM platforms help manage onboarding cases and lifecycle operations. Form infrastructure governs the intake layer: what gets asked, how it is validated, where the submission lives, which systems receive it, who can access it, and what evidence remains when the process changes.
For financial-services teams, that layer deserves its own evaluation.
If the problem is buying verification coverage, choose a KYC provider. If the problem is owning regulated intake across products, portals, APIs, reviewers, audit trails, and customer-controlled infrastructure, evaluate Form.io as the form/application infrastructure around the KYC workflow.
## **FAQ**
### **What is KYC onboarding software?**
KYC onboarding software helps financial-services teams collect customer information, verify identity, assess risk, route exceptions, and preserve records during account opening or customer onboarding. The category can include identity verification tools, KYB providers, CLM platforms, and form/application infrastructure. Buyers should separate those layers before comparing vendors.
### **Is Form.io a KYC verification provider?**
No. Form.io is not an identity verification bureau, sanctions database, biometric provider, AML case-management system, or KYB data provider. It can provide the embedded form, submission, API, permissions, and workflow infrastructure around those services.
### **Where does Form.io fit in a KYC onboarding stack?**
Form.io fits at the intake and application-infrastructure layer. Teams can use it to build embedded onboarding forms, collect structured data, manage submissions, connect APIs and webhooks, scope access, preserve revisions, and deploy in customer-controlled environments. Dedicated verification vendors can still handle identity checks and screening.
### **Why are forms important in KYC onboarding?**
The form layer determines what information is collected, how it is validated, how it is stored, and how it moves into downstream systems. Weak forms create incomplete data, manual rework, inconsistent review paths, and poor audit evidence. In KYC workflows, form design is also data architecture.
### **What should financial-services teams look for in KYC intake software?**
Look for dynamic forms, conditional logic, document upload support, structured submissions, API access, webhooks, role-based permissions, revision history, audit logging, authentication integration, and deployment control. Also confirm what the product does not do, especially around legal compliance, AML policy, sanctions data, and identity verification.
### **Can Form.io help with beneficial ownership collection?**
Form.io can help teams build intake workflows that collect business entity and beneficial ownership information, validate required fields, store submissions, and route data to review or verification systems. It does not determine the legal obligation by itself. Teams should map fields and processes to current regulatory counsel and compliance requirements.
### **Can Form.io connect to KYC or AML vendors?**
Yes, Form.io is built for API-connected form workflows. Forms and submissions can be exposed through REST APIs, and webhook actions can send submission data to external systems. Teams still need to implement and govern the specific integration with their chosen KYC, AML, CRM, banking, or case-management systems.
### **Does Form.io make a financial institution compliant?**
No software makes a financial institution compliant on its own. Form.io can support regulated onboarding controls through structured intake, permissions, APIs, revisions, audit logging, and customer-controlled deployment. Compliance still depends on policy, configuration, monitoring, staff judgment, legal review, and the broader control environment.
### **When should a team choose a full KYC platform instead of Form.io?**
Choose a full KYC platform when the main need is identity verification coverage, fraud signals, sanctions screening, KYB datasets, adverse media, transaction monitoring, or packaged case workflows. Choose Form.io when the main need is to own the embedded intake layer and connect it to those specialized services.
### **Is self-hosting important for KYC onboarding software?**
It depends on the organization's risk posture, architecture, and regulatory environment. Some teams can use hosted KYC products. Others need more control over data, authentication, file storage, logging, network boundaries, and deployment. Form.io is relevant when customer-controlled infrastructure is part of the requirement.
### **How should teams start evaluating Form.io for KYC onboarding?**
Start by mapping the intake workflow: customer types, fields, documents, verification calls, exception paths, reviewer roles, submission records, audit needs, and downstream systems. Then evaluate whether Form.io can provide the governed form and API layer around the verification tools the organization already uses or plans to adopt.
[Build controlled onboarding workflows](/try-formio-for-free/) with Form.io.
# Typeform Alternatives for Self-Hosted and Regulated Teams
[ 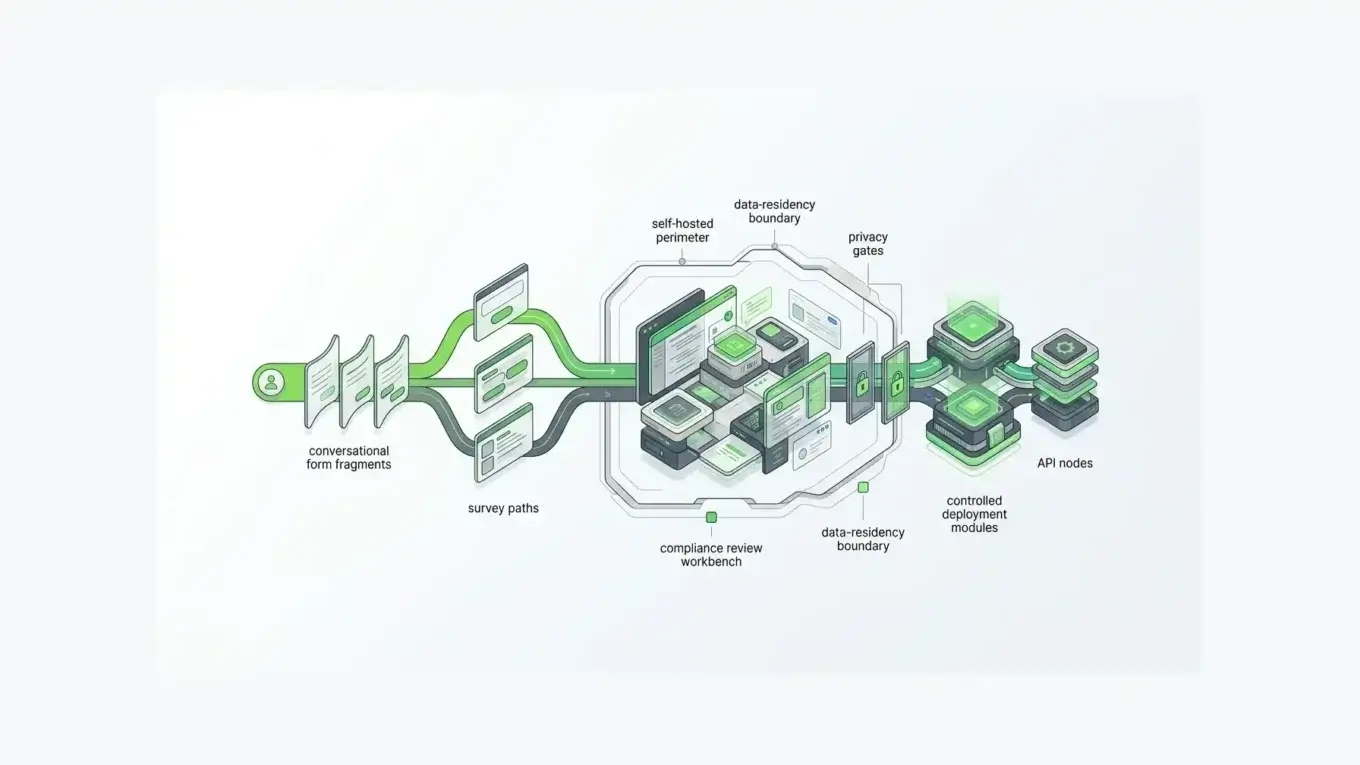 ](https://form.io/typeform-alternatives-self-hosted-compliance-bound/)Most searches for **typeform alternatives** start with a simple frustration: response limits, pricing, branding, or the one-question-at-a-time format.
Those are real reasons to compare tools. But they are not the whole decision.
If your forms collect regulated data, live inside a customer portal, support tenant-specific workflows, or need to connect directly to your application APIs, the better question is not "Which tool costs less than Typeform?" It is "Which layer of the system should own this form?"
## **Key takeaways**
- Typeform is strong for polished conversational forms, surveys, quizzes, and lead capture.
- Many Typeform alternatives compete on price, free response limits, design flexibility, or survey features.
- Self-hosted alternatives matter when the buyer needs more control over where response data lives.
- Compliance-bound teams need more than a form UX: they need permissions, auditability, deployment control, data routing, and clear responsibility boundaries.
- Form.io is a better fit when forms become embedded, API-backed application infrastructure rather than standalone surveys.
## **Quick comparison: which Typeform alternative fits the job?**
## **Scenario****Better-fit category****Examples to evaluate**Marketing forms, lead capture, quizzes, landing pagesPresentation-first form buildersTypeform, Tally, Fillout, JotformProduct feedback, NPS, CSAT, in-app surveysSurvey and feedback platformsFormbricks, SurveyMonkey, Qualtrics, SurveySparrowOpen-source or privacy-first survey collectionSelf-hosted survey toolsFormbricks, LimeSurvey, HeyForm, OpnFormRegulated intake, portals, claims, onboarding, internal workflowsForm infrastructureForm.ioCustomer-facing SaaS form buildingEmbedded and white-labeled form infrastructureForm.ioForms that need generated APIs and submission permissionsSchema-driven form/API platformsForm.io**Why teams look for Typeform alternatives**
Typeform has a clear job. It helps teams create polished, conversational forms without building a custom form experience from scratch. For many marketing, survey, quiz, and customer-feedback workflows, that is enough.
But the market around Typeform alternatives has grown because buyers often hit one of five limits.
First, pricing and response limits can become frustrating. Tally positions itself directly against Typeform by emphasizing unlimited forms and responses on its free plan, while Typeform's free plan is limited to 10 monthly responses in Tally's comparison.
Second, some teams want more layout flexibility. Fillout argues that Typeform is recognizable and polished, but more opinionated, while Fillout gives teams multi-page forms with more control over page structure and integrations.
Third, privacy and self-hosting are becoming a separate buying category. Formbricks frames itself as an open-source Typeform alternative with a self-hosted Community Edition for teams that want more control over data ownership.
Fourth, regulated teams need clearer data boundaries. Typeform publishes security, data-handling, and compliance guidance, including a compliance article stating that Typeform can provide a BAA for customers on its Enterprise plan. Its help center also documents that Typeform data is hosted on AWS, with main servers in Virginia and EU data hosting available for Enterprise and Growth Custom customers.
Fifth, some teams discover that the form is not really a survey anymore. It is intake. It is workflow. It is a record. It is a customer-facing feature. It is part of the application.
That fifth case is where Form.io belongs in the conversation.
## **The three types of Typeform alternatives**
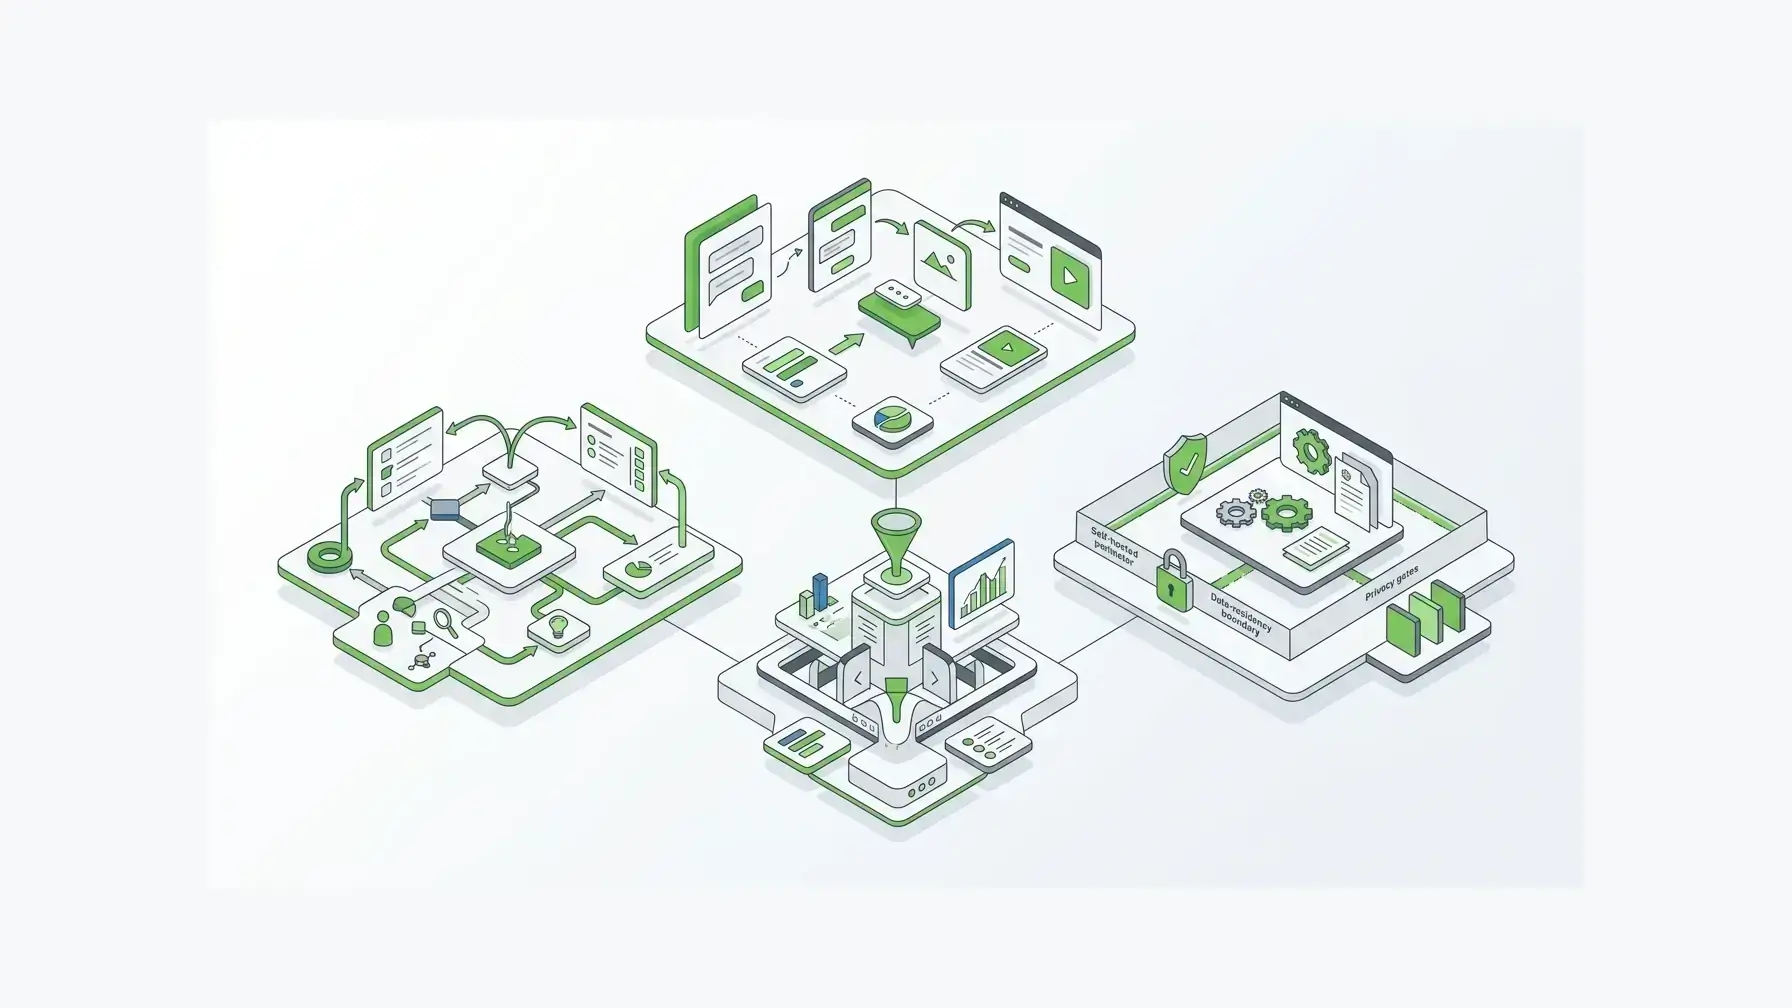The mistake is treating all Typeform alternatives as one category.
They are not.
### **1. Presentation-first form builders**
These tools compete with Typeform on form creation speed, design, free tiers, templates, payment collection, embeddability, and basic automation.
They are often the right answer when the form is a marketing asset or a lightweight business workflow. If the team needs a better-looking contact form, a free survey, a quiz, a registration form, or a lead-capture flow, a presentation-first tool may be enough.
This category is where Tally, Fillout, Jotform, Paperform, and similar tools usually compete.
The tradeoff is that the form usually remains a standalone tool. It may integrate with the rest of the stack, but it does not become the infrastructure layer that governs submissions, permissions, APIs, tenants, and deployment environments.
### **2. Privacy-first survey and feedback platforms**
These tools compete on self-hosting, open-source access, feedback workflows, product surveys, NPS, CSAT, in-app micro-surveys, and user research.
Formbricks is a good example. Its Typeform-alternative page emphasizes open source, self-hosting, link surveys, in-app micro-surveys, pop-up surveys, Dockerized deployment, and an open API.
That is a strong fit when the main object is feedback.
But feedback is not the same as application intake. A survey platform may own responses, contacts, segments, and feedback analytics. It may not be designed to become the form/API layer inside a regulated portal, insurance claim workflow, government service, or B2B SaaS product.
### **3. Form infrastructure platforms**
This is the category most Typeform-alternative lists miss.
Form infrastructure is for teams whose forms need to do more than collect answers. These forms need to render inside an application, validate structured data, create submission records, expose APIs, route data to internal systems, respect permissions, survive audits, and remain under the customer's deployment control.
That is the Form.io case.
Form.io describes itself as a self-hosted developer productivity platform for building forms, APIs, and workflows. Its "How Form.io Works" page explains that the drag-and-drop builder creates forms and APIs together, that every form and resource has an automatically generated REST API, and that the platform can be embedded in the customer's own environment ([How Form.io Works](https://form.io/how-it-works/)).
When the buyer needs that layer, Typeform alternatives should not be judged only by design, templates, or monthly response caps.
## **Where self-hosting changes the decision**
Self-hosting is not automatically required. Plenty of teams are better served by a managed SaaS form tool.
But self-hosting changes the evaluation when forms collect sensitive data, connect to internal systems, support regulated workflows, or sit inside a product your team owns.
IBM's 2025 Cost of a Data Breach report puts the global average cost of a data breach at $4.4 million ([IBM Cost of a Data Breach 2025](https://www.ibm.com/reports/data-breach)). That is not a form-builder statistic, and it should not be used that way. It is a reminder that data collection boundaries have real financial and operational consequences.
Data-control expectations are also moving into mainstream architecture decisions. BARC's 2026 data sovereignty survey found that 76% of respondents expect data sovereignty to become more important, which helps explain why "where does this form data live?" is no longer a niche legal question ([BARC data sovereignty survey](https://barc.com/news/data-sovereignty-2026-survey/)).
Verizon's 2026 DBIR summary says 31% of breaches now start with software vulnerabilities and 48% involve ransomware ([Verizon DBIR 2026](https://www.verizon.com/business/resources/reports/dbir/)). Again, that does not mean a form tool causes the risk. It means buyers should care about where software runs, how it is patched, how access works, and who controls the data path.
For a lightweight survey, a hosted form tool can be perfectly reasonable.
For regulated intake, the questions change:
- Where is submission data stored?
- Can the platform run in our environment?
- Can fields be encrypted where needed?
- Can permissions apply to submissions, not just workspace users?
- Can audit logs show what happened?
- Can dev/test/prod environments support controlled changes?
- Can forms connect to our APIs without routing sensitive data through unnecessary third parties?
Those are infrastructure questions.
## **Why Form.io is different from most Typeform alternatives**
Form.io is not trying to be a prettier Typeform clone.
That matters.
Form.io is built around the idea that a form can be a governed schema. The form definition can drive rendering, validation, submitted data shape, generated API endpoints, permissions, and workflow actions.
The practical difference shows up in four places.
### **Forms and APIs are connected**
In Typeform and many alternatives, the form is mainly a collection surface. You can export data, trigger integrations, or connect webhooks, but the form itself is not usually the application data layer.
Form.io's model is different. Its builder and platform center on JSON-powered forms and APIs. Form.io's own product documentation says every form and resource has an automatically generated REST API associated with it.
That is useful when every new form would otherwise require engineering work to create endpoints, validation, storage, and integration behavior.
### **Deployment can stay inside your environment**
Typeform and many alternatives are hosted SaaS products. Some newer alternatives offer self-hosting, especially in the open-source survey category.
Form.io's self-hosted story is more infrastructure-oriented. Its configuration-based pricing page describes API server environments, enterprise projects, PDF server options, dev/test/prod configurations, self-hosted databases, and security compliance features in API Plus configurations ([Form.io configuration-based pricing](https://form.io/configuration-based-pricing/)). Its self-hosted enterprise forms page also frames the Developer Portal, forms, projects, permissions, and submissions as running inside the customer's own environment ([self-hosted forms for enterprise](https://form.io/features/self-hosted-forms-for-enterprise/)).
That is a better match when the buyer is not allowed to treat form data as a casual SaaS export.
### **Governance is tied to the form layer**
Regulated forms often need more than account-level access control. Teams may need form-level permissions, submission-level access, field-level encryption, revision history, action logs, submission revision logs, and audit evidence.
Form.io's security-compliance materials describe advanced audit logging, action logs, form revisions, submission revision logs, submission collections, field-level encryption, and container security scanning as part of its security module and API Plus feature set ([Form.io secure forms compliance readiness](https://form.io/features/secure-forms-compliance-readiness/)).
That is also how broader security frameworks talk about control. NIST SP 800-53 treats security and privacy controls as part of organization-wide risk management, not as isolated software checkboxes ([NIST SP 800-53 Rev. 5](https://csrc.nist.gov/pubs/sp/800/53/r5/upd1/final)).
That does not mean every Form.io buyer needs every module. It does mean the platform is designed for teams that need those questions answered at the form infrastructure layer.
### **Embedded form building is a platform feature**
Some Typeform alternatives let you embed a form. That is not the same as embedding a governed form-building capability inside your own product.
Form.io can support teams that need form rendering and form building inside their application experience, including white-labeled and tenant-aware scenarios. Its Enterprise Form Builder Module is positioned for exposing a customized form-building experience inside the customer's own application ([Enterprise Form Builder Module](https://form.io/enterprise-form-builder-module/)).
That is where Form.io becomes relevant to SaaS platforms, government portals, healthcare products, insurance workflows, and financial services onboarding.
## **A practical shortlist of Typeform alternatives**
### **Choose Typeform when presentation matters most**
Typeform still makes sense when the primary goal is polished conversational UX, surveys, quizzes, lead capture, and a familiar visual form-building experience. If the form is not regulated, not deeply embedded, and not part of your product architecture, Typeform may be enough.
### **Choose Tally when free limits are the issue**
Tally is a strong fit when the buyer wants a simpler and more generous free form builder. Its comparison page emphasizes unlimited forms, unlimited responses, conditional logic, file uploads, payments, and API access on lower-cost or free tiers.
### **Choose Fillout when the issue is flexibility**
Fillout is worth evaluating when the buyer wants modern form building, stronger free response limits, database-style integrations, multi-page forms, and more layout flexibility than Typeform's one-question-at-a-time format.
### **Choose Formbricks when the job is self-hosted surveys**
Formbricks is a strong fit when the buyer wants open-source, self-hosted surveys, product feedback, NPS, CSAT, website surveys, or in-app micro-surveys. It is especially relevant when the team wants a privacy-first Typeform alternative but still thinks in survey and feedback terms.
### **Choose Form.io when forms become infrastructure**
Form.io is the better fit when the buyer needs forms to become part of the application stack: embedded rendering, generated APIs, submission storage, permissions, actions, security/compliance modules, self-hosted deployment, and controlled form lifecycle.
A Form.io customer proof point from Safety Mojo captures the reason this matters: "Form.io cleans up all the dirty work and does it for you" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)). On G2, another reviewer points to "the level of customization that can go into every form" ([Form.io reviews on G2](https://www.g2.com/products/form-io/reviews)). That is the value when the dirty work is not just building a form, but keeping forms, data, APIs, and workflow behavior aligned.
The scale proof points point in the same direction. Form.io's publicplan case study describes support for more than 400 services and 1,000+ forms in a German public-sector context, while the TauRes case study reports an estimated 50% reduction in data-processing workload after standardizing acquisition workflows around Form.io ([publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/), [TauRes case study](https://form.io/case-studies/taures-case-study-data-acquisition-and-analysis/)).
## **Decision framework**
Ask these questions before choosing a Typeform alternative:
**Question****If yes, look at**Do we mainly need a better free plan or lower-cost form builder?Tally, Fillout, JotformDo we mainly need surveys, NPS, CSAT, or product feedback?Formbricks, SurveyMonkey, QualtricsDo we need open-source or self-hosted survey collection?Formbricks, LimeSurvey, HeyFormDo forms need to live inside our application or portal?Form.ioDo submissions need generated APIs, permissions, and audit-relevant controls?Form.ioDo customers or tenants need to build forms inside our product?Form.ioDo we need a simple marketing form this week?Typeform or a presentation-first alternativeThe strongest decision comes from naming the job.
If the job is presentation, choose a presentation-first tool.
If the job is feedback, choose a survey platform.
If the job is governed application intake, choose form infrastructure.
## **FAQ**
### **Which Typeform alternative should you choose?**
There is no single universal Typeform alternative. Tally and Fillout are strong for lower-cost form building, Formbricks is strong for open-source and self-hosted surveys, and Form.io is stronger when forms need to become embedded, API-backed application infrastructure.
### **Is there a self-hosted Typeform alternative?**
Yes. Formbricks is a strong self-hosted survey alternative. Form.io is also self-hosted, but it solves a different problem: governed forms, generated APIs, submissions, permissions, and workflow behavior inside customer-controlled environments.
### **Is Typeform good for regulated data collection?**
Typeform publishes security and compliance materials and says it can provide a BAA for Enterprise customers in relevant HIPAA contexts. Regulated teams should still verify hosting, data residency, contractual scope, retention, access control, audit, and integration requirements before choosing any hosted form tool.
### **When is Form.io a Typeform alternative?**
Form.io is a Typeform alternative when the real requirement is not just a nice form experience, but embedded forms, self-hosted deployment, generated APIs, submission records, permissions, and governed workflow infrastructure.
### **Is Form.io a survey tool?**
Form.io can collect survey-like data, but it is better understood as a form and API platform. It is usually a stronger fit for application forms, portals, regulated intake, workflow forms, and customer-facing form infrastructure than for simple standalone surveys.
### **Which Typeform alternative fits product feedback?**
Formbricks is worth evaluating for product feedback, in-app micro-surveys, NPS, CSAT, and privacy-first survey workflows. It is designed around feedback collection rather than general form infrastructure.
### **Which Typeform alternative fits embedded forms?**
Form.io is usually the better fit when forms need to be embedded into a customer-facing application and governed as part of the product architecture rather than embedded as standalone survey widgets.
### **Which Typeform alternative fits compliance-bound workflows?**
It depends on the compliance requirement. A hosted tool may be enough for low-risk workflows with the right contracts and settings. For stricter control over deployment, storage, APIs, permissions, and audit evidence, Form.io is often the more relevant category fit.
### **Can Form.io replace Typeform?**
Form.io can replace Typeform when the organization needs self-hosted, embedded, API-backed form infrastructure. It may be too much platform for a simple marketing survey, quiz, or event-registration form.
### **What should developers compare before choosing?**
Developers should compare hosting model, schema ownership, API behavior, validation, permissions, submission storage, audit needs, SDK/rendering model, deployment environments, and whether the form needs to live inside an application users already trust.
## **Final recommendation**
For simple campaigns and surveys, choose the form tool that gets the job done with the least operational burden.
For feedback programs, choose a survey platform with the right data and research workflow.
For regulated intake, embedded portals, tenant-aware SaaS forms, and form-driven application workflows, evaluate Form.io as infrastructure, not as another prettier form builder.
The distinction matters because a form is sometimes just a form. But when the data, API, permissions, workflow, and deployment boundary all depend on it, the form has become part of the architecture.
[Try Form.io for free](https://form.io/try-formio-for-free/) to see how self-hosted forms, generated APIs, and governed submission workflows fit inside your application environment.
# Jotform Alternative for Regulated Teams: When Hosted Forms Are Not Enough
[  ](https://form.io/alternatives-to-jotform-regulated-industries/)Jotform is a strong hosted form builder when the job is to create a form quickly.
That is not the same as choosing form infrastructure for regulated work.
If your forms collect sensitive data, drive downstream decisions, live inside a product, or need to satisfy audit and security teams, the real question is not only which builder is easiest. It is which platform gives you enough control after the form is submitted.
## **The Short Version**
Most Jotform alternative lists compare templates, pricing, free plans, conditional logic, integrations, and form design.
Those things matter. They just do not settle the decision for regulated teams.
If your use case is a marketing form, event registration form, internal survey, or lightweight intake workflow, a hosted builder may be the right answer. If your use case is healthcare intake, government services, insurance claims, financial onboarding, customer portals, or embedded SaaS workflows, you need to evaluate a different layer.
For those teams, a serious Jotform alternative should be judged by:
- where the platform runs
- who controls submission data
- how authentication and permissions work
- whether forms generate APIs
- whether form and submission changes are auditable
- whether the form builder can be embedded and white-labeled
- whether the platform can fit into the systems you already govern
That is where Form.io belongs in the conversation.
Form.io is not the fastest option for a one-off hosted form. It is the stronger fit when forms become part of application infrastructure.
## **Why Most Jotform Alternative Lists Miss the Regulated Buyer**
Most search results for `jotform alternative` are written for broad software shoppers.
They usually ask familiar questions:
- Which tool is cheaper?
- Which one has better templates?
- Which one is easier for a nontechnical team?
- Which one has the most integrations?
- Which one has the cleanest form design?
That comparison is useful for simple workflows. It is incomplete for regulated ones.
A hospital intake workflow, public-sector application, insurance claim, KYC onboarding flow, or embedded customer portal cannot be evaluated only by front-end form features. The submitted data becomes part of a larger system. It may need to be retained, corrected, audited, routed, exported, approved, signed, versioned, or tied to a specific policy decision.
That moves the decision out of the form-builder category and into the architecture layer.
The right question becomes: can the form platform respect the control surface around the form?
## **The Real Buying Question: Hosted Builder or Controlled Infrastructure?**
There are two different jobs hiding behind the same keyword.
The first job is form creation. A team needs to publish a polished form, collect responses, and send data somewhere useful. Hosted builders are good at this. They reduce setup time, give nontechnical users a friendly workspace, and make common forms easy to ship.
The second job is governed data collection. A team needs forms to run inside a larger application boundary, use existing authentication, expose durable APIs, preserve record history, and support audit evidence when something changes.
Those are not the same job.
The first job rewards speed. The second rewards control.
That does not make hosted builders bad. It means regulated teams need to know when the category changes.
## **Where Hosted Form Builders Work Well**
A hosted form builder can be the right choice when the workflow is narrow and the organization accepts the vendor-managed model.
Use a hosted builder when:
- the form is standalone
- the data does not need to stay inside your own environment
- the workflow can live in the vendor's dashboard
- standard integrations are enough
- nontechnical creation matters more than developer control
- the form does not need to become part of a product or governed application
This is why broad Jotform alternative lists often recommend tools like Typeform, Google Forms, Tally, Fillout, Cognito Forms, Formstack, FormAssembly, or other hosted builders. For simple forms, those recommendations can make sense.
Regulated teams should be more careful.
The moment the form sits inside a controlled business process, the tool has to answer questions that template libraries cannot answer.
## **Where Regulated Teams Need More Than a Hosted Builder**
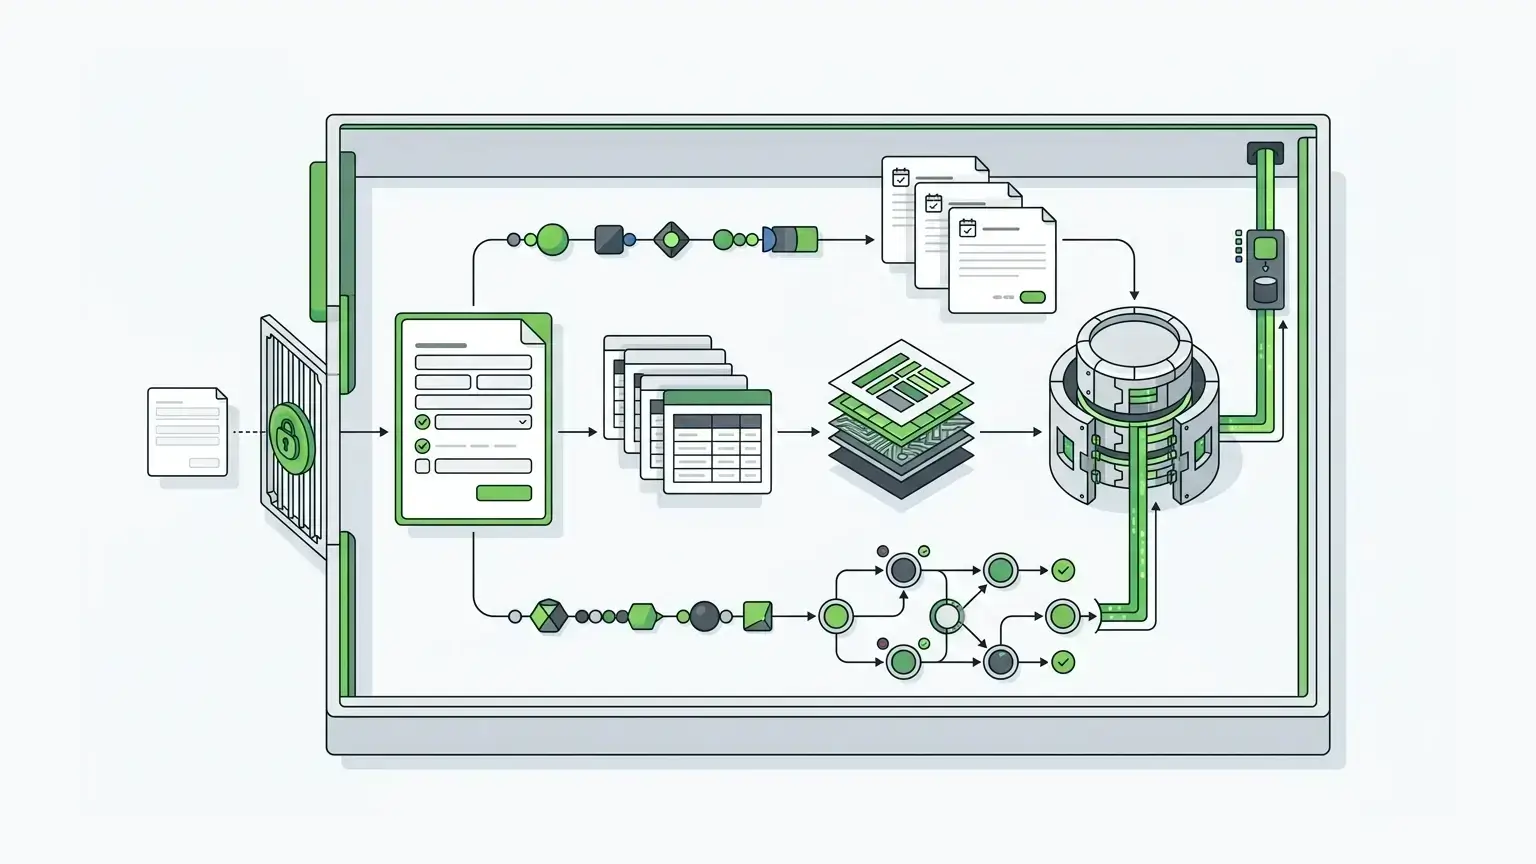Regulated workflows usually fail at the edges.
The form itself looks fine. The problem appears after submission.
Who can see the data? Which system owns the record? What happens when the form schema changes? Can a historical submission still be understood against the form version that captured it? Did the webhook fire? Who changed the claim amount, diagnosis note, eligibility field, or approval status? Can the organization prove it later?
These are ordinary questions in healthcare, government, finance, education, insurance, and other regulated settings.
They also map directly to formal control programs. NIST SP 800-53 Rev. 5 organizes security and privacy controls across families such as [Access Control, Audit and Accountability, Identification and Authentication, Incident Response, Risk Assessment, and System and Communications Protection](https://csrc.nist.gov/pubs/sp/800/53/r5/upd1/final). HHS says the [HIPAA Security Rule](https://www.hhs.gov/hipaa/for-professionals/security/laws-regulations/index.html) establishes national standards for electronic protected health information and requires administrative, physical, and technical safeguards. A form platform used in regulated work does not sit outside those concerns. It becomes one of the places those concerns show up.
IBM's 2025 Cost of a Data Breach report gives the risk scale. IBM reports a [global average breach cost of $4.4 million](https://www.ibm.com/reports/data-breach), and also reports that 63% of organizations lacked AI governance policies to manage AI or prevent shadow AI. Verizon's [2026 Data Breach Investigations Report](https://www.verizon.com/business/resources/reports/dbir/) adds another useful warning: software vulnerabilities now start 31% of breaches, which is why regulated teams should evaluate the form platform as software infrastructure, not only as a form-design surface.
Forms are one of those systems.
## **What a Regulated Jotform Alternative Should Prove**
A regulated team should not start with "Which form builder is easiest?"
Start with the control requirements.
### **Deployment Boundary**
Where does the platform run?
For some teams, vendor-managed SaaS is acceptable. For others, sensitive data must remain inside a private cloud, on-premise environment, government-approved network, customer-controlled database, or specific regional boundary.
That is one of Form.io's clearest differences. Form.io's [self-hosted forms for enterprise](/features/self-hosted-forms-for-enterprise/) model is built so the platform can deploy inside environments the customer controls. The same core surfaces, including form builder, REST API generation, submission handling, and renderer libraries, can run within the customer's infrastructure.
This matters because deployment is not just an IT preference. It shapes data residency, incident response, logging, backup strategy, access review, and compliance ownership.
### **Data Ownership and Submission Control**
The form response is not just a row in a vendor dashboard.
For regulated teams, a submission may become a patient record, claim record, case file, intake record, eligibility input, identity artifact, or workflow event. The platform needs to fit the system that owns that record.
Form.io's architecture stores forms, resources, submissions, users, and project data as JSON documents in the customer's MongoDB or MongoDB-compatible database. That document model is part of why Form.io can treat form definitions and submission records as application data rather than isolated form entries.
If your team needs application-owned data, this distinction matters more than builder polish.
### **Authentication and Permissions**
Regulated forms rarely have one kind of user.
A healthcare intake flow may involve patients, providers, administrators, support staff, and compliance reviewers. A government service workflow may involve applicants, case workers, supervisors, auditors, and external systems. A SaaS product may need tenant admins, end users, implementation teams, and internal support roles.
The platform has to respect those boundaries.
Form.io's [roles and permissions](/features/forms-for-teams/) model is built around controlling who can create forms, view submissions, modify data, manage projects, and interact with APIs. That matters when the same form infrastructure supports different departments, customers, tenants, or workflow stages.
For regulated teams, permissions are not an admin convenience. They are part of the evidence trail.
### **Generated APIs**
Many hosted form tools expose APIs. That does not mean the form is the API contract.
The stronger architecture is schema-driven: the same definition that renders the form also defines the submission structure and API behavior around it. Form.io's [form from JSON](/features/form-from-json/) model gives teams a JSON-based form definition that can render interfaces and support generated APIs from the same source.
This is useful when forms feed applications, not just spreadsheets.
It lets developers treat forms as governed application surfaces: forms, resources, submissions, validation, webhooks, and workflow actions can be reasoned about together instead of being scattered across a visual builder, a separate API layer, and custom glue code.
### **Audit Trails and Revisions**
Regulated teams need to know more than whether a form was submitted.
They need to know what changed.
Form.io's [complete audit trail](/features/log-forms-complete-audit-trail/) capabilities distinguish between submission revisions and server audit logging. Submission revisions track field-level changes to submitted data. Server audit logging captures system activity such as authentication, form access, API requests, and data modification events.
That distinction matters. An auditor may need to know that a submission was created by one user, modified by another, and later viewed through a specific role or project context. A support team may need to know whether a webhook ran. A compliance team may need to know which form revision captured a historical record.
For financial services, this is not an abstract preference. The [FTC Safeguards Rule](https://www.ecfr.gov/current/title-16/chapter-I/subchapter-C/part-314) requires financial institutions to monitor and log authorized-user activity and detect unauthorized access, use, or tampering with customer information. It also creates retention and change-management expectations around customer information systems.
Form.io's [secure forms compliance readiness](/features/secure-forms-compliance-readiness/) capabilities also include advanced audit logging, action logs, form revisions, submission revision logs, submission collections, and container security scanning as part of the Security Module.
That is a different category of answer than "the form has an activity log."
### **Embedded and White-Labeled Use**
Many regulated forms do not belong on a third-party hosted page.
They belong inside a patient portal, citizen service portal, claims application, financial onboarding flow, education system, or B2B SaaS product.
That creates two requirements at once: the form needs to feel native to the product, and the form data needs to move through the product's security and workflow model.
Form.io is designed for embedded use. Developers can render forms inside their own applications, use the platform's APIs, and let business users modify schemas after the application is in place. For software teams, this is often the useful compromise: developers own the system boundary, while business teams can still manage many form changes without reopening every application ticket.
## **Comparison Table: Jotform Alternative Categories**
**Category****Best fit****Strength****Risk for regulated teams**Hosted no-code form builderSimple forms, surveys, registration, marketing captureFast setup and low technical burdenData and workflow live primarily in the vendor-managed modelHosted enterprise form suiteBusiness teams that need more compliance features and admin controlBetter security, SSO, compliance options, supportMay still be separate from the customer's application infrastructureIndustry-specific form toolNarrow healthcare, education, legal, or government workflowsBetter fit for one vertical's common use casesCan be too narrow for cross-department or product-embedded workflowsCustom-built formsUnique internal systems with strong engineering ownershipMaximum controlExpensive to build, secure, document, version, and maintainSelf-hosted form infrastructureRegulated teams where forms are part of real applicationsDeployment control, APIs, permissions, revisions, audit evidence, embedded useRequires technical ownershipThe last row is where Form.io fits.
It is not the right answer for every team looking for a Jotform alternative. It is the right answer when the team has outgrown the assumption that forms are standalone assets.
## **Why Form.io Is Different From a Normal Form Builder**
Form.io is easier to understand when you stop treating it as a lighter or heavier version of a hosted form builder.
It is infrastructure for forms and the APIs around them.
The visual builder creates schemas. The renderer turns those schemas into forms inside applications. The API server manages forms, resources, submissions, permissions, projects, and actions. The self-hosted deployment model lets the customer run that infrastructure inside their own environment.
That is why Form.io's own guidance is direct about fit. In Form.io's article on [why teams should not use Form.io without a developer team](https://form.io/why-you-shouldnt-use-formio-if-you-dont-have-a-dev-team/), the product is framed as infrastructure software for software developers building custom applications, not a simple form builder for nontechnical users. In other words, it is the wrong choice if a marketing team needs a simple form live this afternoon, and the better choice if a software team needs forms to behave like governed application infrastructure.
That honesty is valuable.
The buyer who only wants speed should not be pushed into infrastructure. The buyer who needs control should not be pushed into convenience software that will fail later.
## **Proof That This Is a Real Deployment Problem**
This is not theoretical positioning.
Form.io's public case-study library includes publicplan GmbH, where the project supported [more than 400 public-sector services and 1,000+ forms](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/) with strict standards and a short timeline. That kind of workload is not a normal contact-form problem. It is a repeatable public-service infrastructure problem.
The same pattern shows up in customer sentiment. A Trustpilot reviewer described Form.io as useful for both integration and standalone use and praised support when users get stuck ([Trustpilot](https://www.trustpilot.com/review/form.io)). The wording is simple, but the integration point is doing real work. Regulated teams are rarely buying a form in isolation. They are buying a form layer that has to connect to the rest of the system.
## **When Form.io Is the Wrong Jotform Alternative**
Form.io is not the right replacement if the team wants the fastest possible hosted form with the least technical setup.
Choose a simpler hosted builder when:
- the form is temporary
- the data is low risk
- the workflow is not part of a product
- the team does not have developers available
- vendor-managed hosting is acceptable
- the organization does not need custom API, identity, or audit architecture
That is not a failure case. It is buyer fit.
For simple forms, infrastructure can be too much.
## **When Form.io Is the Right Jotform Alternative**
Form.io becomes the stronger answer when the form is part of the system.
That usually means one or more of these conditions is true:
- submission data must stay inside a controlled environment
- forms are embedded in a customer-facing application
- different users need different permissions
- submissions need to become application records
- the team needs APIs generated from form definitions
- changes to forms and submissions need revision history
- workflows depend on webhooks, actions, approvals, or integrations
- the organization needs audit evidence after submission
- the platform must support multiple teams, tenants, projects, or environments
These are the use cases where "easy form builder" becomes too small a category.
For those teams, Form.io's advantage is not that it hides complexity. It is that it gives the team places to put the complexity where it belongs: deployment, schema, API, permissions, revisions, audit logs, workflow actions, and application integration.
## **Key Takeaways**
- A broad Jotform alternative list is useful for simple form-building needs.
- Regulated teams need to evaluate deployment boundary, data ownership, permissions, APIs, auditability, and embedded use.
- Hosted builders can work when the form is standalone and vendor-managed storage is acceptable.
- Form.io is strongest when forms become application infrastructure inside customer-controlled environments.
- The right choice depends less on builder polish and more on what must happen after the form is submitted.
## **FAQ**
### **What is the best Jotform alternative for regulated teams?**
The best Jotform alternative depends on the control requirements. If the team only needs a hosted form with better pricing or templates, a simpler hosted builder may be enough. If the team needs self-hosting, APIs, permissions, audit trails, revisions, and embedded application workflows, Form.io is a stronger fit.
### **Is Form.io easier to use than Jotform?**
Not for simple hosted forms. Jotform is easier for nontechnical teams that need to create and publish forms quickly. Form.io is built for teams that need developer control, application integration, self-hosted deployment, generated APIs, and governance around forms and submissions.
### **When should a team avoid Form.io?**
Avoid Form.io when the form is simple, standalone, low risk, and needs to be created by a nontechnical user without developer involvement. Form.io expects technical ownership, especially for self-hosted deployments and production application integration.
### **Why would a regulated team outgrow a hosted form builder?**
Hosted form builders can become limiting when the workflow needs controlled data residency, internal authentication, custom permissions, API-driven records, audit logs, revision history, or direct embedding inside a product or portal. Those needs turn the form into part of the application architecture.
### **Does Form.io support self-hosted forms?**
Yes. Form.io can be deployed in customer-controlled environments, including cloud, private data center, and Docker-based deployments. That gives teams more control over where form infrastructure runs and how submission data fits their existing security boundary.
### **Does Form.io generate APIs from forms?**
Yes. Form.io's schema-driven model uses form and resource definitions to support REST API behavior around submissions, validation, resources, permissions, and workflow actions. That makes it useful when forms are interfaces into application data, not just hosted pages.
### **Is Form.io HIPAA compliant?**
Form.io provides technical capabilities that can support HIPAA-governed workflows in customer-controlled environments, but the customer remains responsible for its compliance program, configuration, policies, deployment controls, and business associate requirements.
### **Does a BAA make a form workflow compliant?**
No. HHS explains that [business associate contracts](https://www.hhs.gov/hipaa/for-professionals/covered-entities/sample-business-associate-agreement-provisions/index.html) define permitted uses, safeguards, breach reporting, access, amendment, accounting, subcontractor, and termination obligations. A BAA matters, but compliance also depends on how the workflow is configured, secured, monitored, and governed.
### **Why do audit trails matter for form submissions?**
Audit trails help answer who accessed data, who changed it, what changed, when it changed, and which workflow action ran. For regulated teams, that evidence can matter as much as the original submission.
### **Can Form.io be embedded inside a SaaS product?**
Yes. Form.io is designed for embedded application use. Developers can render forms inside their own applications, connect them to Form.io APIs, and let authorized business users manage form schemas after the product infrastructure is in place.
### **What should I ask before choosing a Jotform alternative?**
Ask where data is stored, who controls deployment, how permissions work, whether APIs are generated from the form schema, how revisions are handled, whether audit logs are available, and whether the form can live inside your own application or portal.
## **Build Regulated Form Infrastructure With Form.io**
If you only need a quick hosted form, choose the simplest tool that satisfies the job.
If your forms define application workflows, submission records, permissions, APIs, audit evidence, and deployment boundaries, choose infrastructure that respects that reality.
[Try Form.io for regulated form infrastructure](/try-formio-for-free/).
# Formbricks vs Form.io: Survey Tool or Form Infrastructure?
[  ](https://form.io/formbricks-formio-vs-formbricks-self-hosted-typeform-alternative/)Organizations looking for a self-hosted alternative to Typeform or a privacy-first feedback platform often compare Formbricks and Form.io. Both have open-source and self-hosted evaluation paths, but they solve fundamentally different problems.
Formbricks focuses on surveys, experience management, and product feedback. Form.io is designed as application infrastructure for forms, APIs, workflows, and enterprise governance, including agentic workflow patterns where governed forms and submissions need to stay connected to permissions, validation, actions, and audit evidence.
That distinction matters before the feature checklist begins. The question is not whether both products can build forms. It is whether the form is mainly a survey or part of the application architecture.
## **Key takeaways**
- Formbricks is best understood as an open-source experience management and survey platform for link surveys, website surveys, in-app surveys, email surveys, and customer feedback workflows.
- Form.io is best understood as form-driven application infrastructure: JSON-defined forms, generated APIs, submission data, permissions, workflow actions, self-hosted deployment, and governed patterns for agentic workflows.
- Formbricks is a credible choice when the buyer wants a self-hosted Typeform alternative or privacy-first feedback tool.
- Form.io is the better fit when forms need to be embedded in a product, reused across tenants, governed through submission-level permissions, exposed through APIs, managed across enterprise environments, or used as structured context for agentic workflows.
- The main question is not “Which one is open source?” It is “Does your form need to collect feedback, or does it need to become part of the application architecture?”
## **Quick comparison**
The comparison below summarizes the product jobs documented in Formbricks’ platform, API, self-hosting, and licensing docs and Form.io’s JSON schema, generated API, self-hosting, and embedded builder pages.
## **Decision area****Formbricks****Form.io**Primary jobOpen-source surveys and experience managementForm and API infrastructure for embedded, governed applications and agentic workflowsBest use caseFeedback, NPS, CSAT, product surveys, link surveys, in-app micro-surveysRegulated intake, customer-facing product forms, portals, workflow forms, schema-driven applications, and agentic workflow interfacesForm modelSurvey flows and question types for response collectionJSON schemas that define UI, validation, submission structure, and backend APIsAPI modelPublic Client API for survey interactions and Management API for surveys, contacts, responses, and webhooksForm and resource paths generate schema and submission endpointsEmbeddingWebsite, app, email, and link survey deliveryRenderer and builder embedded directly into customer-controlled applicationsGovernance centerSelf-hosting, privacy, survey data control, open-core packagingProject, form, and submission permissions; roles, actions, audit patterns, stages, and deployment boundariesBest buyerProduct, growth, customer experience, and feedback teams that need open-source surveysDevelopment teams building form-heavy products, portals, and enterprise workflowsWrong fit warningNot designed to be the form/API layer for every application workflowNot the lightest answer for simple surveys or one-off feedback forms**What Formbricks is good at**
Formbricks deserves a fair reading. Its official docs describe it as an open-source platform for collecting and analyzing feedback from customers, users, and employees through targeted surveys.
That is a real product category.
If your team needs NPS surveys, CSAT surveys, product feedback, onboarding feedback, churn surveys, website surveys, in-app micro-surveys, or link-based surveys, Formbricks is built for that motion. Its homepage frames the product around privacy-first experience management, feedback collection across websites and apps, and self-hosting when a team wants more control over data.
Its open-source form builder page also makes the category clear: unlimited forms, unlimited responses, open-source survey building, conditional logic, multi-language surveys, integrations, hidden fields, partial submissions, single-use links, and custom domains.
That matters because the Typeform-alternative search is not only about technical architecture. Many buyers really do want a better survey tool: more generous limits, more privacy control, self-hosting, open-source code, and enough product polish for feedback collection.
Formbricks has a strong claim there.
The question is what happens when the form is not mainly a survey.
## **What Form.io is good at**
Form.io is strongest when the form is not just a feedback surface, but part of the application contract. Its value shows up when a team needs JSON-defined forms, generated APIs, submission records, validation, permissions, workflow actions, audit patterns, and self-hosted deployment to stay aligned.
That includes regulated intake, customer portals, tenant-managed SaaS forms, healthcare and financial workflows, government services, insurance claims, and internal processes where the submitted record needs to remain explainable over time.
It also matters for agentic workflows. If an AI agent or human-in-the-loop workflow needs to ask for data, validate fields, route submissions, require confirmation, or operate inside an enterprise governance boundary, the form layer needs to be more than a survey delivery tool. Form.io gives developers a governed form and API layer that can become part of that workflow infrastructure.
So the Form.io category should appear early in the decision: it is not the survey tool in this comparison. It is the form infrastructure layer when forms, submissions, APIs, and workflow behavior need to be owned by the application.
## **What changes when a survey becomes application infrastructure**
A survey collects feedback. Application infrastructure carries business process.
That line gets blurry at first. A customer feedback form can become a support workflow. A product survey can feed account health. A compliance questionnaire can become an auditable record. A tenant-specific intake form can become a feature inside a SaaS platform. A public-facing form can become the first step in a case management workflow.
At that point, the evaluation changes.
The buyer is no longer asking only whether the tool can collect a response. The buyer is asking:
- Who owns the schema?
- What validates the submission?
- Which API receives and exposes the data?
- Can the form be embedded inside our product?
- Can customers build or modify their own forms inside our app?
- Can roles and permissions apply at the form and submission level?
- Can the same form move through development, test, and production?
- Can historical submissions remain explainable after form definitions change?
Those are Form.io questions.
Form.io’s [drag-and-drop form builder and APIs](https://form.io/features/drag-and-drop-form-builder-apis/) page describes the builder as a JSON schema editor that defines form UI, validation, the data model, and REST API endpoints together. That is the architectural difference.
Formbricks is strong when the workflow is survey-led. Form.io is strong when the form is a contract between the user interface, submitted data, backend API, permissions, and downstream process.
## **Survey flows vs schema contracts**
Formbricks is optimized around survey delivery. Its own Typeform-alternative page describes link surveys, in-app micro-surveys, pop-up surveys, Dockerized self-hosting, an open API, and open-source customization.
That is useful when the main asset is a survey.
Form.io starts from a different object: the form schema. Every Form.io form is a JSON document that defines the title, path, display mode, components, validation, conditional logic, and submission data shape.
That schema can render in an application, accept submissions, validate data, and create predictable API behavior. The form is not only a front-end artifact. It is the source of truth that connects rendering, validation, submission storage, and backend endpoints.
This matters when multiple systems need to trust the same form definition.
If the form is only a feedback survey, a survey-first platform is usually enough. If the form is a reusable business object across applications, tenants, workflows, and environments, the schema needs to carry more responsibility.
That is where Form.io’s model becomes more valuable.
## **API and data model comparison**
Formbricks has APIs, and the comparison should say that clearly. Its REST API documentation describes two API surfaces: a Public Client API for frontend survey interactions and a Management API for backend management tasks. The exposed methods include displays, responses, contacts, surveys, action classes, contact attributes, and webhooks.
That API surface fits a survey and feedback product.
Form.io’s API model is different because the form path and schema define the submission API itself. The [Forms from JSON](https://form.io/features/form-from-json-schema/) documentation explains that a form path can create endpoints for retrieving the schema and creating, listing, reading, updating, and deleting submissions.
That changes the center of gravity.
In Formbricks, the API helps manage and operate surveys. In Form.io, the form can define part of the application data layer.
For feedback collection, Formbricks’ model is sensible. For application intake, regulated submissions, onboarding flows, service requests, claims, eligibility workflows, or tenant-managed forms, Form.io’s generated form/submission API model is usually the more direct fit.
## **Embedding and white-labeling**
Formbricks can reach users in useful places: websites, apps, email, pop-ups, and links. That is exactly what a survey platform should do. For customer experience teams, that flexibility matters because feedback is most useful when it appears at the right moment in the product journey.
Form.io uses embedding for a different purpose.
The [Form.io open-source page](https://form.io/open-source/) explains that forms are rendered from JSON using Form.io renderers for frameworks such as Vanilla JavaScript, Angular, React, and Vue. The [Enterprise Form Builder Module](https://form.io/product-announcement/enterprise-form-builder-module/) goes further: it lets teams embed a customizable, white-labeled form-building interface directly into their own applications.
That is not the same as embedding a survey.
It means a SaaS platform, healthcare product, government portal, insurance system, or internal enterprise app can expose governed form creation to its users without sending those users into a separate form product. The application still controls navigation, authentication, permissions, branding, allowed components, data model, and workflow behavior.
That is a major distinction for platform teams.
If you want to ask users for feedback, Formbricks may be the cleaner answer. If your customers need to build and manage forms inside your product, Form.io fits the architecture more directly.
## **Self-hosting, licensing, security, and governance**
Do not reduce this comparison to “self-hosted vs not self-hosted.” Formbricks is a legitimate self-hosted option. Its self-hosting docs describe cloud hosting, free self-hosting, self-hosting with an Enterprise Edition license, Docker setup, one-click setup, migration, configuration, and integrations.
Formbricks’ license docs also give useful detail. The core source code is AGPLv3, while larger-team and enterprise functionality lives under a separate enterprise license. The Community Edition includes self-hosting for commercial purposes, unlimited surveys, unlimited responses, unlimited users, API access, SDKs, website and app surveys, webhooks, multi-language surveys, and integrations. Enterprise features include items such as teams and access roles, audit logs, SSO, two-factor authentication, contact management, quota management, and prioritized support, depending on the license configuration.
That is a strong open-source story, but buyers need to understand the packaging.
Open source and self-hosting are valuable. They are not the same thing as complete application governance.
GitHub’s 2025 Octoverse report shows why this nuance matters. It says 63% of all repositories are public or open source, while 81.5% of contributions happen in private repositories ([GitHub Octoverse 2025](https://github.blog/news-insights/octoverse/octoverse-a-new-developer-joins-github-every-second-as-ai-leads-typescript-to-1/)). Modern software teams often depend on open source while doing most operational work inside private, governed systems.
Form.io’s self-hosted model is built for that private operational side. Its [self-hosted forms for enterprise](https://form.io/features/self-hosted-forms-for-enterprise/) page describes Form.io as deployable infrastructure that can run in AWS, Azure, Google Cloud, private data centers, or local Docker-based environments. It also describes separate components such as Enterprise Server, PDF Server, Developer Portal, renderer libraries, deployment environments, file storage, database requirements, and dev/test/prod patterns.
The key point is not that Form.io is self-hosted and Formbricks is not. Both can be self-hosted.
The key point is what is governed inside that boundary.
Formbricks governs surveys, feedback, contacts, responses, and experience-management workflows. Form.io governs forms, resources, submissions, generated APIs, roles, permissions, actions, environments, and form lifecycle.
Those are different control surfaces.
## **Pricing basis and scale predictability**
Formbricks has a strong Community Edition story for survey teams: AGPLv3 core access, free self-hosting, unlimited surveys, unlimited users, and unlimited responses. Teams evaluating Enterprise Edition should verify response, feature, workspace, support, and private-fork requirements directly against the current license table.
Form.io’s pricing story is different.
The point is not that Form.io is cheaper in every scenario. The point is that the buying model is designed around configured form/API infrastructure. Form.io’s [configuration-based pricing](https://form.io/configuration-based-pricing/) page lists unlimited API calls, unlimited submissions, unlimited developers and form builders, and unlimited forms and resources in relevant enterprise configurations.
That difference matters when forms become a platform feature.
If every tenant, customer, department, agency, or product line can create forms, usage can grow in ways that are hard to forecast. A per-response survey model may be fine for customer feedback. A configuration-based infrastructure model may be a better fit when submissions, forms, builders, tenants, and APIs are part of the product architecture.
The buyer should ask what is scaling.
If survey responses are scaling, Formbricks may fit. If application forms, submitted records, generated endpoints, customer form builders, and environments are scaling, Form.io deserves closer evaluation.
## **Customer proof: when form infrastructure scale becomes real**
Form infrastructure arguments can sound abstract until the volume shows up.
Form.io’s public case-study pages describe a publicplan GmbH implementation supporting more than 400 services and 1,000+ forms, and a Safety Mojo implementation that Form.io says saved 6-12 months of development time. Those are Form.io-published examples, so they should be read as customer proof rather than independent analyst validation. The Safety Mojo page also includes the customer proof line, “Form.io cleans up all the dirty work and does it for you” ([publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/), [Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)).
Those examples point to the real Form.io use case.
The hard part at that scale is not drawing a field. It is keeping the form, schema, submission record, API behavior, permissions, environment boundary, and downstream workflow aligned as requirements change.
IBM’s 2025 Cost of a Data Breach report puts the global average breach cost at $4.4 million and says 63% of organizations lacked AI governance policies ([IBM Cost of a Data Breach 2025](https://www.ibm.com/reports/data-breach)). That is not a form-specific statistic, and it should not be treated as one. It is a reminder that data workflows and governance boundaries are not minor implementation details when forms collect sensitive or operationally important data.
For teams handling simple feedback, that level of infrastructure may be unnecessary. For teams building regulated intake, customer portals, financial workflows, healthcare workflows, insurance claims, government services, or multi-tenant form platforms, it is often the main issue.
## **When Formbricks is the better choice**
Formbricks is likely the better fit when your team needs:
- a self-hosted Typeform alternative
- product feedback surveys
- NPS, CSAT, CES, onboarding, churn, or market research surveys
- in-app micro-surveys and website surveys
- open-source survey tooling with a clear cloud/self-host path
- privacy-first feedback collection
- a survey API for responses, contacts, and webhooks
- broad survey features without building a survey platform from scratch
In those cases, Form.io may be too much infrastructure. If the primary object is a survey and the output is feedback analysis, Formbricks is a natural choice.
## **When Form.io is the better choice**
Form.io is likely the better fit when your team needs:
- embedded forms inside a customer-facing application
- white-labeled form building inside your own product
- JSON-defined forms that drive rendering, validation, submissions, and APIs
- generated form APIs instead of hand-built backend endpoints for every form
- form, project, and submission permissions
- dev/test/prod form environments and SDLC-aware form promotion
- multi-tenant form workflows
- audit-relevant controls such as permissions, deployment boundaries, submission history, and security/compliance features
- configuration-based pricing for high-volume form infrastructure
- forms that support workflows beyond feedback collection
- governed form and submission context for agentic workflows
In those cases, the form is no longer just a question flow. It is a governed application layer.
## **The decision rule**
Choose Formbricks if the main job is collecting feedback through open-source, self-hosted surveys.
Choose Form.io if the main job is making forms, submissions, APIs, permissions, workflow behavior, and agentic workflow context part of your product or enterprise application infrastructure.
That is the real comparison.
Formbricks helps teams own survey and feedback collection. Form.io helps teams own the form layer when it becomes part of the architecture.
## **FAQ**
### **Is Formbricks a form builder?**
Yes, but it is better understood as an open-source survey and experience management platform. It can build forms and surveys, but its strongest fit is feedback collection across websites, apps, emails, and shared links.
### **Is Form.io a Formbricks alternative?**
Form.io can be an alternative when the buyer’s requirement is governed forms, generated APIs, embedded form rendering, self-hosted deployment, and application infrastructure. It is not a direct replacement for every survey, feedback, or experience-management use case Formbricks supports.
### **Which is better for a self-hosted Typeform alternative?**
Formbricks is usually the stronger fit for a self-hosted Typeform alternative. It is built around surveys, feedback collection, open-source access, and privacy-first response workflows.
### **Which is better for embedded forms?**
Form.io is usually the stronger fit when forms need to be embedded into a customer-facing product or enterprise application as a governed runtime. Formbricks can embed surveys, while Form.io is built around embeddable form rendering and embedded form building.
### **Can Formbricks be self-hosted?**
Yes. Formbricks documents free self-hosting and self-hosting with an Enterprise Edition license. Buyers should verify which features are included in Community Edition and which require Enterprise Edition.
### **Can Form.io be self-hosted?**
Yes. Form.io supports self-hosted deployment with API server environments, portal/authoring environments, renderer libraries, PDF Server options, customer-controlled databases, file storage choices, and common dev/test/prod deployment structures.
### **Does Formbricks have an API?**
Yes. Formbricks documents a Public Client API for frontend survey interactions and a Management API for backend management tasks such as surveys, contacts, responses, action classes, and webhooks.
### **Does Form.io generate APIs from forms?**
Yes. Form.io’s distinction is that form schemas and paths can directly define schema and submission endpoints, making the form itself part of the application API contract.
### **Which is better for regulated form workflows?**
Form.io is usually the better fit when the regulated workflow depends on form schemas, submission permissions, generated APIs, deployment boundaries, submission history, and long-term governance of form changes. Formbricks may still fit regulated feedback collection when a survey-first model is enough.
### **Which is better for customer-facing SaaS platforms?**
Form.io is usually the stronger fit when SaaS customers need to create or use forms inside your product experience, especially with white-labeling, tenant boundaries, permissions, and governed form behavior. Formbricks is stronger when the SaaS product mainly needs in-app feedback and customer surveys.
### **How should teams evaluate Formbricks vs Form.io?**
Start by deciding whether you are choosing a survey platform or a form infrastructure layer. Then compare deployment, embedding, API behavior, permissions, licensing, pricing basis, audit needs, and who will maintain the form model over time.
## **Build form infrastructure without turning every form into a custom project**
When forms become part of the application architecture, the right platform needs to do more than collect responses. It needs to keep schemas, submissions, APIs, permissions, and workflows aligned as the system grows.
[Try Form.io for free](https://form.io/try-formio-for-free/) if your team needs self-hosted form infrastructure that developers can embed, govern, and scale inside the applications you already own.
# Budibase vs Form.io: Internal Tools or Form Infrastructure?
[  ](https://form.io/budibase-formio-vs-budibase/)Organizations comparing self-hosted, open-source builders for internal tools and enterprise forms often put Budibase and Form.io in the same shortlist. Both speak to technical teams that want more control than lightweight SaaS form tools provide, but they solve different layers of the problem.
Budibase focuses on internal operations apps, agents, automations, and workflows around business data. Form.io is designed as application infrastructure for forms, APIs, workflows, and enterprise governance, including agentic workflow patterns where governed forms and submissions need to stay connected to permissions, validation, actions, and audit evidence.
That distinction matters before the feature checklist begins. The question is not whether both products can collect data. It is whether the form is a screen inside an internal app or a governed contract inside the application architecture.
## **Key takeaways**
- Budibase is best understood as an open-source operations platform for internal tools, agents, apps, automations, and connected data.
- Form.io is best understood as form-driven application infrastructure: JSON-defined forms, generated APIs, submission data, permissions, workflow actions, self-hosted deployment, and governed patterns for agentic workflows.
- Budibase is a credible choice for internal apps, request workflows, admin panels, and operational tools.
- Form.io is the better fit when forms need to be embedded in a product, reused across tenants, governed through submission-level permissions, exposed through APIs, managed as part of an enterprise SDLC, or used as structured context for agentic workflows.
- The main question is not "Which product has forms?" It is "What layer do your forms need to own?"
## **Quick comparison**
## **Decision area****Budibase****Form.io**Primary jobInternal operations platform for agents, apps, automations, workflows, and connected dataForm and API infrastructure for embedded, governed, form-driven applications and agentic workflowsForm modelForms are components inside Budibase apps, usually tied to tables, views, custom schemas, or app workflowsForms are JSON schemas that define UI, validation, submission structure, and backend APIsAPI modelPublic API gives access to apps, users, tables, and data through a RESTful APIEach form/resource path can generate REST endpoints for schemas and submissionsEmbeddingPublished apps can be embedded with iframes; enterprise microfrontend options existRenderer and builder can be embedded directly into customer-controlled applicationsGovernanceTenant roles, workspace roles, app roles, SSO, groups, and audit logs depending on planProject, form, and submission permissions; roles, actions, audit patterns, stages, and self-hosted environmentsBest buyerTeams building internal tools and operations workflows quicklyTeams standardizing forms, APIs, submissions, permissions, workflow behavior, and agentic workflow context as product infrastructureWrong fit warningLess ideal when the form layer must be a portable, governed contract outside an internal app surfaceNot a general internal-tools replacement for every dashboard, CRUD app, or admin panel**What Budibase is good at**
Budibase deserves a fair reading. Its own documentation describes it as an open-source platform for internal tools and workflow automation, used by more than 200,000 teams to automate workflows, handle requests, build internal tools, and connect systems using their own data, LLMs, and APIs.
That is a real category.
If your team needs to build an internal approval app, a data-entry screen, an admin panel, a request workflow, an operations dashboard, or an agent-assisted internal process, Budibase is built for that motion. It gives teams a visual app builder, data connections, automations, apps, agents, roles, and deployment options in one operations-oriented surface.
Budibase forms are part of that app-building model. The official forms documentation says forms are built from a Form component, Field group components, and Input components, with optional schemas tied to tables, views, relationships, or custom structures.
That is useful when the form is a screen inside an internal app.
The question is what happens when the form is no longer just a screen.
## **What Form.io is good at**
Form.io is strongest when forms, submissions, validation, permissions, APIs, and workflow actions need to become governed infrastructure rather than app components. The form definition can become a JSON contract that drives rendering, submission shape, validation rules, backend endpoints, and downstream handoffs.
That makes Form.io a better fit for customer-facing forms, regulated intake, tenant-managed SaaS form builders, healthcare and financial workflows, government services, insurance claims, and enterprise processes where the form record needs to stay governed after submission.
It also matters for agentic workflows. When AI-assisted or runtime agents need to collect structured data, validate inputs, trigger actions, or require human confirmation inside enterprise guardrails, the form layer needs stable schemas, permissions, and audit patterns. Form.io is built for that form and workflow infrastructure layer.
So the Form.io category should appear early in the decision: it is not the general internal app builder in this comparison. It is the governed form infrastructure layer when forms, APIs, submissions, and workflow behavior need to be owned by the application architecture.
## **What changes when forms become infrastructure**
Many teams start with a simple internal form and end up with application infrastructure.
The intake form becomes a case creation workflow. The customer form becomes a white-labeled feature inside a SaaS product. The compliance form becomes a regulated submission record. The public-sector form becomes one of hundreds of services that must follow the same standards. The healthcare or financial-services form becomes part of a workflow where validation, access, auditability, and downstream APIs matter as much as the UI.
That is the point where the Budibase vs Form.io decision gets sharper.
Form.io's form builder is not only a visual form editor. The Form.io documentation says the builder creates a JSON schema representation of the form, and that schema is used to dynamically render the form and automatically generate the REST API that supports it ([Form.io form building docs](https://help.form.io/userguide/forms/form-building)).
That is the architectural difference.
In Budibase, forms help users interact with data inside apps. In Form.io, the form schema can become the contract that defines the rendered UI, validation rules, submitted data shape, API endpoints, permissions, and downstream workflow behavior.
For teams whose forms are application infrastructure, that difference is not small.
## **Forms inside apps vs forms as contracts**
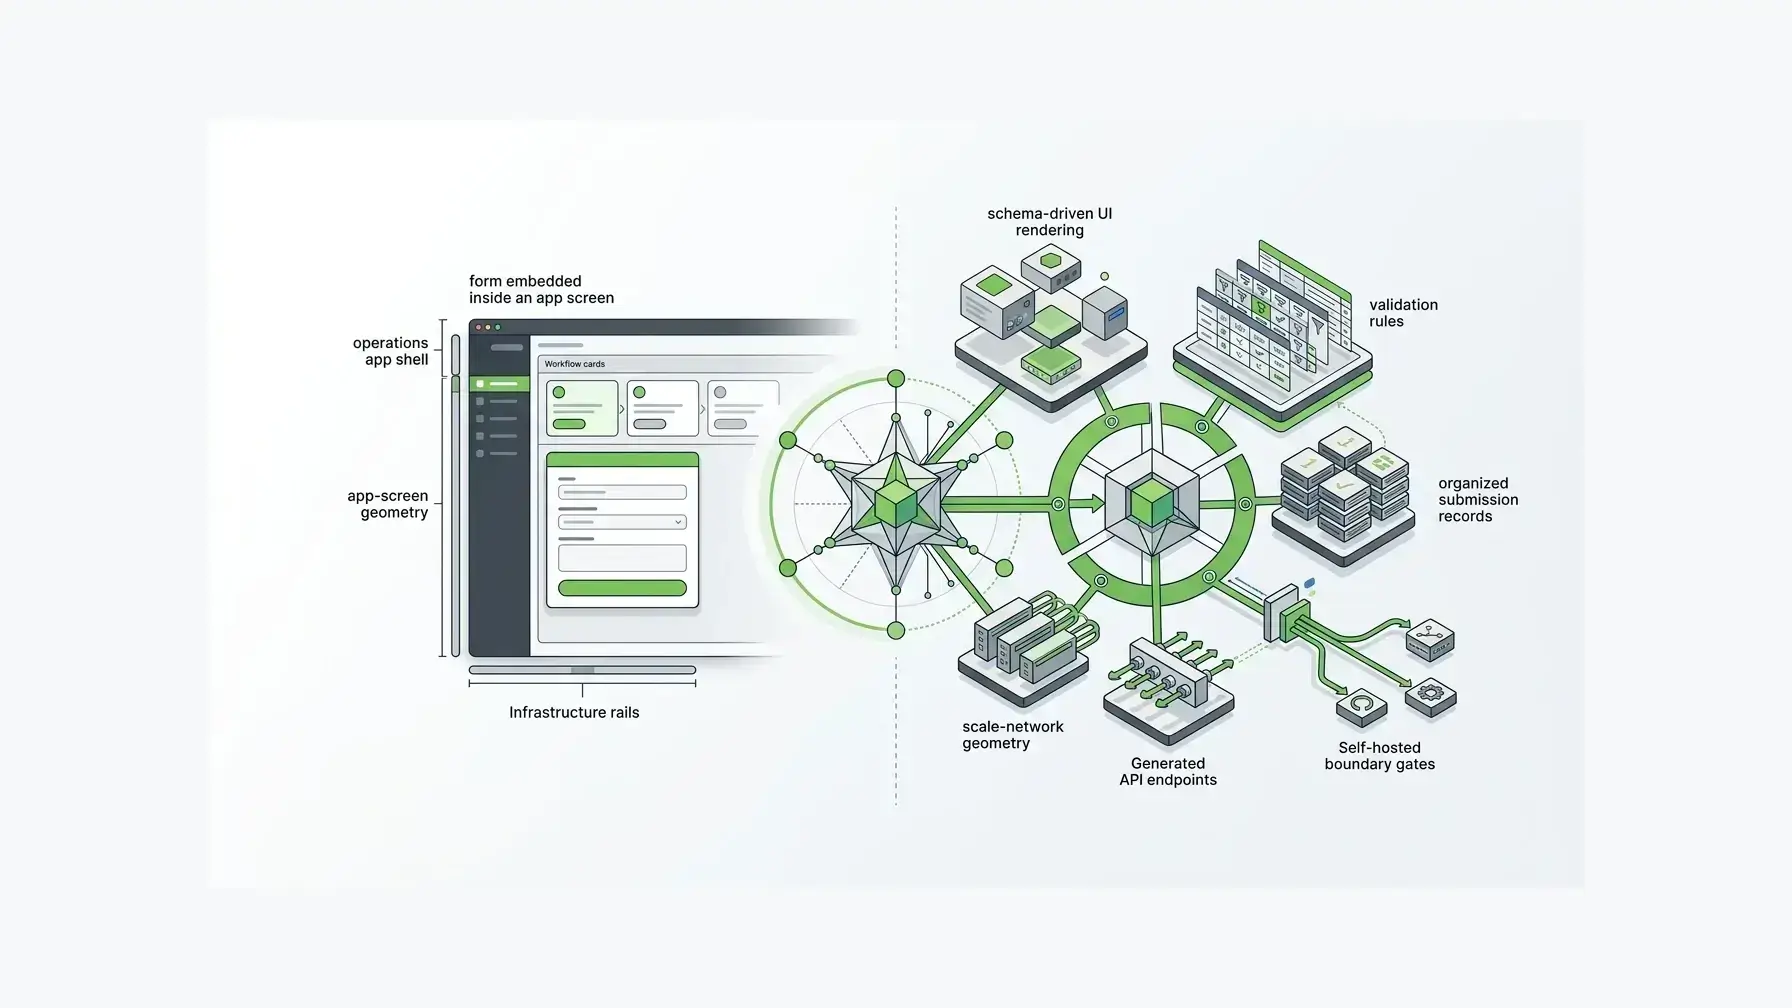Budibase is strongest when you want a visual way to assemble apps around data and process. Its forms can create and update data, use schemas, and participate in workflows. For internal teams, that can be exactly right.
Form.io is stronger when the form definition itself needs to travel across systems.
Every Form.io form is a structured JSON definition. Form.io's JSON-schema forms documentation explains that a form schema can define the form title, path, type, display mode, components, validation, conditional logic, and submission data shape. It also explains that a form path creates endpoints such as schema retrieval and submission create/list/read/update/delete operations ([Forms from JSON](https://form.io/features/form-from-json-schema/)).
That matters when multiple applications, teams, tenants, or agents need to rely on the same form contract.
If a form is only a UI on top of a table, the surrounding system still needs to decide how validation is enforced, how submissions are stored, how APIs behave, how permissions apply, and how downstream services consume the data. If the form is a governed schema with APIs and submissions attached, more of that behavior has one source of truth.
That is why Form.io often resonates with teams that have outgrown simple form building. They are not trying to draw fields faster. They are trying to keep the form, data model, API behavior, permissions, and workflow triggers aligned as requirements change.
## **API and data model comparison**
Budibase has an API, and that should be acknowledged clearly. Its public API documentation says the API provides access to applications, users, tables, and data through a RESTful API and an OpenAPI 3.0 specification.
That makes sense for an internal operations platform. You can integrate with the Budibase environment, work with tables and records, and connect Budibase to broader business systems.
Form.io's API model is more specific to form infrastructure. The form schema defines the path and the submission endpoints that support that form. Form.io's drag-and-drop builder and API documentation explains that saving a form registers endpoints for creating, listing, reading, updating, and deleting submissions, with validation enforced from the schema ([drag-and-drop form builder APIs](https://form.io/features/drag-and-drop-form-builder-apis/)).
That is a different center of gravity.
Budibase helps you build apps around data. Form.io helps you define the form and submission layer that creates, validates, stores, and exposes that data in the first place.
For an internal app, either model may work. For a customer-facing product, regulated intake workflow, or multi-tenant form platform, the form-defined API model can be the safer foundation.
## **Embedding and white-labeling**
Budibase supports embedding, but the default model is app embedding. Its embedded app documentation describes embedding a published Budibase app in an iframe, with access considerations for public screens, allowed domains, and authenticated embedded users. Budibase also documents an enterprise microfrontend option for non-iframe embedding in specific licensed scenarios.
That can be useful when the thing you want to embed is an app.
Form.io is built for a different embedding requirement: embedding form rendering and form building inside the application your team already owns. The open-source `formio.js` renderer and SDK can render JSON schema forms inside an application and communicate with Form.io APIs ([Form.io JavaScript renderer](https://github.com/formio/formio.js)). The [Enterprise Form Builder Module](https://form.io/enterprise-form-builder-module/) lets teams expose white-labeled, preconfigured form building inside their own product while controlling components, guardrails, structured data, APIs, permissions, and workflow behavior.
That distinction is important for SaaS platforms, government service portals, healthcare products, and other systems where customers or internal teams need self-service form creation without leaving the product experience.
If you want to embed a whole operational app, Budibase may fit. If you want to embed governed form creation and rendering as part of your own product architecture, Form.io is the more direct match.
## **Self-hosting, security, and governance**
Do not reduce this comparison to "self-hosted vs not self-hosted." Budibase is a legitimate self-hosted option. Its hosting docs describe Budibase Cloud and self-hosted installation paths, including Docker, Kubernetes, and DigitalOcean. Its security docs say the self-hosted version can be deployed inside your own network, on your own servers, with control over how data is secured and without data needing to leave your VPC.
That is real.
The stronger Form.io argument is not that Budibase lacks deployment control. It is that Form.io's control is organized around form infrastructure.
Form.io's self-hosted deployment documentation describes API server environments, portal/authoring environments, Docker-based deployment, and common dev/test/prod structures ([Form.io self-hosted deployment docs](https://help.form.io/deployments/deployment-guide.md)). Its roles and permissions documentation separates access across project, form, and submission scopes, with permissions governing form definitions and submission data ([Form.io roles and permissions docs](https://help.form.io/developers/roles-and-permissions.md)).
That is the level of detail serious form infrastructure often needs.
Open source is also not a substitute for governance by itself. GitHub's 2025 Octoverse report says 63% of all repositories are open source or public, while 81.5% of contributions happen in private repositories, showing how public software and private enterprise work now depend on each other ([GitHub Octoverse 2025](https://github.blog/news-insights/octoverse/octoverse-a-new-developer-joins-github-every-second-as-ai-leads-typescript-to-1/)). Black Duck's 2026 OSSRA analysis found that 87% of audited codebases contained at least one vulnerability and 78% contained high-risk vulnerabilities, which is why open-source adoption still needs supply-chain governance ([Black Duck 2026 OSSRA](https://www.blackduck.com/blog/open-source-trends-ossra-report.html)). Gartner also predicts that by 2027, 70% of organizations with platform teams will include GenAI capabilities in internal developer platforms, increasing the need for reusable guardrails around generated and internal applications ([Gartner software engineering trends](https://www.gartner.com/en/newsroom/press-releases/2025-07-01-gartner-identifies-the-top-strategic-trends-in-software-engineering-for-2025-and-beyond)).
The practical lesson is simple: open source and self-hosting are valuable, but enterprise teams still need clear controls over data, roles, changes, workflows, and audit evidence.
Budibase has governance features such as tenant roles, workspace app roles, SSO, user groups, and audit logs. Its audit log docs say audit logs track events across a Budibase installation, and also show an upgrade path for free-tier users who need audit logs. That is not a criticism. It is a reminder to verify packaging against the controls your team actually needs.
For Form.io buyers, the governance question is more specific: who can change a form definition, who can submit, who can read submissions, which action fires after submission, which environment owns the schema, and which historical submission was governed by which form state?
Those are form-infrastructure questions.
## **Pricing basis: free tier vs scale predictability**
Budibase has a strong pricing story for many teams. Its pricing page includes a free open-source self-hosted plan, and higher tiers add capabilities such as more logs, custom branding, backups, SSO, user groups, SCIM, audit logs, priority support, and air-gapped deployment options.
For internal tools, that can be compelling.
Form.io's pricing story is different. The point is not that it is cheaper in every scenario. The point is that it is priced around self-hosted form/API configuration rather than usage meters. Form.io's configuration-based pricing page lists unlimited API calls, unlimited submissions, unlimited developers and form builders, and unlimited forms and resources in relevant configurations, and it frames the buying model around projects, API/PDF environments, and enterprise add-ons ([Form.io configuration-based pricing](https://form.io/configuration-based-pricing/)).
That difference matters when forms are high-volume, public-facing, embedded, or tenant-driven.
If every customer, office, agency, or product team can create forms, usage can become difficult to predict. A pricing model that avoids per-form, per-submission, per-end-user, per-developer, and per-API-call charges can make more sense when forms are infrastructure rather than a handful of internal apps.
## **Customer proof: when this becomes real**
Form infrastructure arguments can sound abstract until the scale shows up.
A Form.io public-sector case study for publicplan GmbH describes support for over 400 services and 1,000+ forms under strict standards and a short timeline ([publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)). Another Form.io-hosted customer proof point describes a long-time platform user running multiple production applications with a Form.io backend and saying, "Form.io cleans up all the dirty work and does it for you" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)).
Those examples point to the same idea: when forms multiply across services, products, departments, or customers, the hard part is not dragging fields onto a page. The hard part is keeping the form layer governed, reusable, API-backed, and operationally stable.
That is the Form.io case.
## **When Budibase is the better choice**
Budibase is likely the better fit when your team needs:
- internal tools for operations, support, HR, IT, finance, or admin workflows
- agent-assisted internal request handling
- dashboards, admin panels, and CRUD apps over business data
- a visual app builder for teams that want to ship internal workflows quickly
- open-source self-hosting for internal app delivery
- automations and app screens in one operations platform
In those cases, Form.io may be too specialized. If the form is just one component inside a broader internal app, Budibase can be the simpler answer.
## **When Form.io is the better choice**
Form.io is likely the better fit when your team needs:
- embedded forms inside a customer-facing application
- white-labeled form building inside your own product
- JSON-defined forms that can drive rendering, validation, submissions, and APIs
- generated form APIs instead of hand-built backend endpoints for every form
- submission-level permissions and form-specific access control
- dev/test/prod form environments and SDLC-aware form promotion
- multi-tenant form workflows
- compliance-oriented audit patterns
- no per-submission, per-form, per-end-user, or per-API-call pricing surprise
- governed form and submission context for agentic workflows
In those cases, the form is no longer a UI component. It is a governed application layer.
## **The decision rule**
Choose Budibase if the main job is building internal operational apps around data, approvals, automations, and agents.
Choose Form.io if the main job is making forms, submissions, APIs, permissions, workflow behavior, and agentic workflow context part of your product or enterprise application infrastructure.
That is the real comparison.
Budibase helps teams build operational applications faster. Form.io helps teams keep form-driven systems governed when the forms themselves become the architecture.
## **FAQ**
### **Is Budibase a form builder?**
Budibase includes form-building capabilities, but it is better understood as an internal operations platform for apps, agents, automations, workflows, and connected data. Forms are one important part of that app-building model.
### **Is Form.io a Budibase alternative?**
Form.io can be an alternative when the specific requirement is governed forms, submissions, generated APIs, embedded form rendering, and self-hosted form infrastructure. It is not a general replacement for every internal app or dashboard use case Budibase supports.
### **Which is better for internal tools?**
Budibase is usually the stronger fit for broad internal tools, admin panels, request workflows, dashboards, and operations apps. Form.io is more specialized around the form and API layer.
### **Which is better for embedded forms?**
Form.io is usually the stronger fit when forms need to be embedded into a customer-facing product or internal application as a governed runtime. Budibase can embed apps, but Form.io is built around embeddable form rendering and embedded form building.
### **Can Budibase be self-hosted?**
Yes. Budibase supports self-hosting and documents deployment paths such as Docker, Kubernetes, and DigitalOcean. Buyers should still verify which governance, audit, SSO, SCIM, support, and air-gapped features are included in the plan they intend to use.
### **Can Form.io be self-hosted?**
Yes. Form.io supports self-hosted deployment with API server environments, portal/authoring environments, Docker-based deployment, customer-controlled databases, and common dev/test/prod structures.
### **Does Budibase generate APIs from forms?**
Budibase has a public API for apps, users, tables, and data. Form.io's distinction is that form schemas and paths can directly define form and submission endpoints, making the form itself part of the API contract.
### **Which is better for regulated form workflows?**
Form.io is usually the better fit when the regulated workflow depends on form schemas, submission permissions, generated APIs, deployment boundaries, audit patterns, and long-term governance of form changes. Budibase may still fit internal regulated workflows when the app-builder model is enough.
### **Which is better for customer-facing SaaS platforms?**
Form.io is usually the stronger fit when SaaS customers need to create or use forms inside your product experience, especially with white-labeling, tenant boundaries, and governed form behavior. Budibase is stronger when the goal is to build internal apps for your own team.
### **How should teams evaluate Budibase vs Form.io?**
Start by deciding whether you are choosing an internal app builder or a form infrastructure layer. Then compare deployment, embedding, API behavior, permissions, pricing basis, audit needs, and who will maintain the form model over time.
## **Build form infrastructure without turning every form into a custom project**
When forms become part of the application architecture, the right platform needs to do more than render fields. It needs to keep schemas, submissions, APIs, permissions, and workflows aligned as the system grows.
[Try Form.io for free](https://form.io/try-formio-for-free/) if your team needs self-hosted form infrastructure that developers can embed, govern, and scale inside the applications you already own.
# HIPAA-Compliant Form Builder: What Healthcare SaaS Teams Should Evaluate
## [  ](https://form.io/hipaa-compliant-form-builder-healthcare-saas-platforms/)**Key Takeaways**
- A HIPAA-compliant form builder is not compliant because it has a healthcare template or a lock icon.
- If a vendor creates, receives, maintains, or transmits ePHI for a covered entity or business associate, the BAA and operational responsibility boundary matter.
- Hosted HIPAA form builders can be a good fit for simple intake, consent, appointment, or website forms.
- Healthcare SaaS teams usually need more than a hosted form link: APIs, embedded rendering, role-aware access, audit logs, revision history, and deployment control.
- Form.io is strongest when HIPAA-governed forms are part of application infrastructure rather than a standalone intake tool.
## **What "HIPAA-Compliant Form Builder" Actually Means**
The phrase "HIPAA-compliant form builder" is useful shorthand, but it can hide the real decision.
HIPAA compliance is not a feature that one vendor turns on for the whole organization. It is a legal, contractual, administrative, technical, and operational responsibility. The form builder can support that responsibility. It cannot replace it.
The U.S. Department of Health and Human Services explains that when a covered entity or business associate uses a cloud service to create, receive, maintain, or transmit ePHI, the cloud service provider is generally a business associate and the parties need a HIPAA-compliant business associate agreement. [HHS also notes](https://www.hhs.gov/hipaa/for-professionals/special-topics/health-information-technology/cloud-computing/index.html) that this can still be true even when the provider stores only encrypted ePHI and does not hold the decryption key.
That point matters for online forms.
If a form collects PHI, the risk does not stop at the submit button. The data may be stored, emailed, exported, routed through webhooks, copied into a CRM, written to a database, attached to a PDF, shown in an admin portal, or sent to downstream systems. A HIPAA-ready form tool has to be evaluated across that whole path.
The [HHS Security Rule](https://www.hhs.gov/hipaa/for-professionals/security/index.html) frames the obligation around administrative, physical, and technical safeguards for the confidentiality, integrity, and availability of ePHI. In plain terms: the form is only one surface. The system around the form has to be governed too.
The risk is not theoretical. IBM's 2025 Cost of a Data Breach report puts the global average breach cost at [$4.4 million](https://www.ibm.com/reports/data-breach?app=true). That is not a healthcare-form-specific number, but it gives the right scale for the decision: a form that collects sensitive health data is not a minor website feature when the surrounding workflow is weak.
## **The Quick Decision: Practice Intake Tool Or Healthcare SaaS Infrastructure?**
Most buyers searching for a HIPAA-compliant form builder fall into one of two groups.
The first group needs a faster way to collect patient information. A clinic, therapy practice, dental office, or small healthcare provider may need intake forms, consent forms, appointment requests, file uploads, and e-signatures. A hosted HIPAA-enabled form builder can work well here if the vendor signs the right BAA, the account is configured correctly, and the workflow keeps PHI inside approved systems.
The second group is building a healthcare product. That buyer does not only need a form. It needs form capability inside an application.
For healthcare SaaS teams, forms may power onboarding, eligibility, clinical screening, referrals, patient-reported outcomes, provider workflows, prior authorization, records updates, care-team routing, and follow-up check-ins. A [third-party digital health article from Light-it](https://lightit.io/blog/5-ways-to-apply-hipaa-compliant-form-builders-to-your-digital-health-product/) describes HIPAA-compliant forms as part of ongoing product workflows such as patient intake, assessments, appointment scheduling, regular check-ins, and feedback surveys. That is a different problem than publishing a secure contact form on a website.
The distinction is simple:
**Buyer situation****Better fit**One practice needs intake forms and patient packetsHosted HIPAA-enabled form builderA healthcare SaaS product needs forms inside its appEmbedded form infrastructureA team needs patient data routed to internal systemsAPI-first form platformA team must keep PHI inside its own environmentSelf-hosted form infrastructureA product needs tenant-specific forms and permissionsWhite-label or multi-tenant form infrastructureThe mistake is treating these as the same purchase.
## **The Requirements Checklist**
Before comparing logos, healthcare teams should define the control boundary.
### **BAA Scope**
A BAA is not a marketing badge. It establishes the permitted uses and disclosures of PHI, requires appropriate safeguards, covers reporting obligations, addresses subcontractors, and should align with the actual workflow. [HHS sample BAA guidance](https://www.hhs.gov/hipaa/for-professionals/covered-entities/sample-business-associate-agreement-provisions/index.html) says these contracts should clarify and limit how a business associate may use or disclose PHI and require safeguards to prevent unauthorized use or disclosure.
The practical question is: which vendor is creating, receiving, maintaining, or transmitting ePHI?
If the form builder stores submissions, handles uploaded files, sends notifications containing PHI, or passes data to another system, the BAA and subcontractor chain need to match that reality.
### **Where PHI Is Stored**
Data location is not a minor implementation detail. It determines who administers the database, where backups live, which security controls apply, who can access logs, what happens at termination, and how incident response works.
For a simple hosted form workflow, vendor-managed storage may be acceptable. For a healthcare SaaS product, the team may need submissions in its own database, cloud account, region, network, or compliant infrastructure boundary.
This is one reason self-hosting matters. It does not make an application HIPAA compliant by itself. It gives the customer more control over where PHI lives and which controls surround it.
### **Access Control And Identity**
HIPAA-governed forms usually need more than a shared admin login.
Ask who can view submissions, edit forms, export data, upload files, change permissions, configure webhooks, or see audit logs. Then map those permissions to real roles: patient, provider, customer admin, internal support, implementation partner, compliance reviewer, and developer.
For SaaS products, this gets harder. One customer's admin should not see another customer's submissions. A support user may need temporary access. A provider may need access to only assigned patients. A form builder may need schema-editing rights without PHI access.
The form system has to support those boundaries instead of forcing the application to patch them later.
### **Audit Logs And Revision History**
The highest-risk part of a healthcare form often starts after submission.
What changed? Who changed it? Which version of the form captured the original data? Did a webhook run? Did an email action send? Did the submitted value get edited later? Can the team reconstruct the record if an auditor asks?
Generic form builders often focus on collection. Healthcare SaaS teams need evidence.
Form.io's Security Module is built around this kind of evidence. Its [secure forms and compliance readiness documentation](https://form.io/features/secure-forms-compliance-readiness/) describes advanced audit logging, action logs, form revisions, submission revision logs, submission collections, and container security scanning. The important distinction is that form revisions track changes to the form schema, while submission revisions track changes to submitted data.
That distinction sounds small. It is not.
A historical submission is not only the answers a patient gave. It is the form version, validation rules, field labels, conditional logic, workflow context, and submission state that governed the data at the time.
### **APIs And Integration Control**
Healthcare forms rarely stay inside the form tool.
An intake form may need to create a patient profile, update a resource, trigger a referral workflow, generate a PDF, route a task to a care team, or feed an internal dashboard. A screening form may need validation, conditional follow-up, file uploads, and downstream review. A provider form may need to connect with legacy systems or internal case management.
If the form builder only gives you CSV exports or a fragile integration layer, the application team inherits the risk.
Form.io's [concepts documentation](https://help.form.io/start/form.io-concepts) explains that as a form is built, Form.io constructs the JSON schema and defines a REST API endpoint. Submissions are API-accessible, owned by users for permission enforcement, portable, and revision-trackable with the Security & Compliance package. That is the infrastructure argument: the form definition, submitted data, API, and access model belong in the same system.
### **Tenant And Customer Boundaries**
Healthcare SaaS teams often serve many customers from one product. That means the form layer may need tenant-aware configuration, customer-specific forms, white-labeled experiences, separate roles, different workflows, and different data retention expectations.
This is where "HIPAA form builder" searches become too small. The issue is not only whether one form can collect PHI. It is whether a platform can support repeated, governed form workflows across customers without collapsing into one-off custom code.
## **Common HIPAA Form Builder Categories**
The market is easier to understand when you separate platform types.
**Category****Best fit****Strength****Gap**Hosted HIPAA form builderPractices and clinics that need intake, consent, and website formsFast setup, templates, vendor-managed hostingLimited architecture and data-boundary controlHealthcare intake platformPatient intake, appointment, and engagement workflowsHealthcare-specific UX and workflowsMay be too narrow for broader SaaS infrastructureEnterprise form/workflow platformLarger teams with governed workflowsMore controls and integrationsOften still vendor-hosted or workflow-product centeredSelf-hosted form infrastructureHealthcare SaaS and regulated product teamsDeployment control, APIs, data ownership, auditabilityRequires technical ownershipCustom buildUnique workflows with no acceptable platform fitMaximum controlExpensive to build, secure, test, document, and maintainThere is no universal winner. There is only the right layer for the job.
## **Where Form.io Fits For Healthcare SaaS**
Form.io is not the lightest way to publish a HIPAA-ready website form. It is a stronger fit when forms are part of healthcare application infrastructure.
That usually means the team needs some combination of embedded forms, generated APIs, custom roles, submission storage, workflow actions, form revisions, submission revisions, audit logs, file/PDF handling, and customer-controlled deployment.
Form.io's [self-hosted forms documentation](https://form.io/features/self-hosted-forms-for-enterprise/) says the platform can run in AWS, Azure, Google Cloud, private data centers, or Docker-based environments, with submission data stored in the customer's MongoDB instance and security boundary. The same page is careful about the boundary: self-hosted deployment enables compliance control, but the customer still needs proper access controls, encryption, audit logging, network security, and the rest of the compliance program.
That honesty is useful.
Healthcare SaaS teams do not need another vendor promising that complexity disappears. They need a platform that gives them the right control surfaces: forms, resources, generated APIs, submissions, actions, [roles and permissions](https://form.io/features/forms-for-teams/), revisions, and audit evidence.
Form.io's [healthcare forms page](https://form.io/industries/healthcare-forms/) points to use cases such as patient registration, records, appointments, routing inquiries, notifications, [conditional logic](https://form.io/features/form-conditional-logic-form-validation/), mobile-responsive forms, offline mode, form revisions, autosave, accessibility, and the Security Module. The better strategic reading is not "Form.io makes healthcare simple." It is that Form.io gives healthcare teams a form infrastructure layer they can govern inside their own architecture.
The [CHESS Health case study](https://form.io/how-a-flexible-form-solution-helped-get-to-market-in-6-weeks-instead-of-6-months/) is a useful proof point. Form.io describes a healthcare technology company managing EMRs, EHRs, interoperability, strict security and compliance requirements, sensitive data in its own environment, legacy integrations, and the need to get to market faster. The case headline says CHESS Health got to market in 6 weeks instead of 6 months. That is the category fit: not a simple intake form, but a healthcare product workflow that needed speed without giving up architectural control.
There is also a buyer sentiment signal from [Trustpilot](https://www.trustpilot.com/review/form.io), where one reviewer called Form.io "really great software, both for integration and standalone." The quote is broad, but it matches the central buying reason for this article: the form layer has to work as part of a larger system.
## **When A Hosted HIPAA Form Builder Is Enough**
A hosted HIPAA form builder may be the better answer when the workflow is simple and the organization accepts the vendor-managed model.
That can include:
- Patient intake forms for one practice
- Consent forms
- Appointment request forms
- Simple file uploads
- Basic medical history forms
- Feedback surveys
- Website-embedded forms
- Staff-created forms with limited integration needs
In these cases, speed matters. Templates matter. A no-code builder matters. A signed BAA, encrypted submissions, access controls, and a clean admin experience may be enough.
The important word is "enough."
If a workflow starts simple but will later need custom identity, tenant-specific configuration, deeper APIs, application-owned submission records, role-aware workflows, and evidence-grade revision history, the cheapest or fastest hosted option can become expensive later.
## **When Healthcare SaaS Teams Should Avoid Standalone Form Tools**
Standalone form tools become risky when the form is part of the product's core workflow.
Watch for these signals:
- PHI must remain inside your own cloud, database, or approved deployment boundary.
- Forms need to be embedded directly into your product experience.
- Customers need their own form configuration, roles, branding, or workflows.
- Submissions need to become application records, not just entries in a vendor dashboard.
- The product needs generated APIs, webhooks, resources, permissions, and workflow actions.
- Historical records need to resolve to the form version that captured them.
- Support, operations, providers, and customer admins need different access rules.
- Exports, notifications, analytics, and AI tools must not create uncontrolled PHI copies.
These are not edge cases for healthcare SaaS. They are ordinary product requirements.
The wrong tool can still pass the first demo. The problem appears later, when the team needs to prove who accessed PHI, why a submission changed, whether a field existed at the time of capture, where a file was stored, or why one tenant's workflow affected another.
That is the moment when "just use a form builder" stops being a plan.
## **Evaluation Table**
##  **Evaluation question****Why it matters****What to look for**Will the vendor sign the right BAA?PHI handling needs a contractual boundaryBAA scope, subcontractors, permitted uses, breach/security incident termsWhere is PHI stored?Data location shapes risk and responsibilityCustomer-controlled database, approved region, backup and termination termsCan access map to real roles?Healthcare workflows are role-sensitiveRBAC, SSO/MFA options, admin separation, own-vs-all submission accessAre form changes versioned?Historical records need contextForm revisions, schema history, promotion/stage controlsAre submission changes versioned?Modified PHI needs accountabilitySubmission revisions, who/when/what logs, revert or history viewsAre actions auditable?Integrations are common failure pointsAction logs for emails, webhooks, resource saves, and workflow stepsDoes the platform generate APIs?SaaS products need system integrationREST APIs, submission endpoints, resources, webhooksCan forms be embedded and white-labeled?Healthcare SaaS forms live inside productsRenderer libraries, embedded builder, brand controlCan the platform be self-hosted?Some teams need customer-controlled infrastructureDocker, cloud/on-prem deployment, environment variables, customer databaseDoes the vendor overclaim compliance?Overclaiming creates riskClear shared-responsibility language and technical-control boundaries**What Not To Assume**
Do not assume a healthcare template makes a workflow compliant.
Do not assume encryption solves the whole problem. HHS cloud guidance is clear that encryption alone does not remove business associate obligations when a provider maintains ePHI.
Do not assume a BAA covers every downstream action. If submissions are emailed to the wrong inbox, copied into a non-approved CRM, exported to spreadsheets, or passed through an unreviewed automation, the form builder's feature list is not the whole risk picture.
Do not assume self-hosting removes responsibility. It increases control. It also increases the customer's obligation to configure and operate the environment correctly.
Do not assume a standalone form tool will scale into product infrastructure. Sometimes it will. Often it will not.
## **FAQ**
### **Is A Form Builder HIPAA Compliant If It Signs A BAA?**
No. A BAA is necessary in many PHI workflows, but it is not the whole compliance answer. The organization still needs appropriate safeguards, policies, configuration, access control, risk analysis, monitoring, and incident-response processes.
### **Can Healthcare Teams Use Google Forms For PHI?**
Do not use a general form workflow for PHI unless the entire vendor relationship, configuration, storage model, access controls, and BAA requirements are approved for that use. For most healthcare SaaS teams, the safer default is to use a platform designed for regulated data workflows.
### **What Features Should HIPAA-Compliant Forms Have?**
At minimum, evaluate BAA support, encryption, access control, audit logs, secure storage, user management, file handling, retention/deletion, and integration behavior. For healthcare SaaS, also evaluate APIs, embedding, tenant boundaries, revision history, and deployment control.
### **Do Healthcare SaaS Teams Need Self-Hosted Forms?**
Not always. But self-hosting becomes important when PHI must stay inside the customer's environment, when the form layer needs to align with internal security controls, or when product architecture requires direct control over database, network, logging, and deployment boundaries.
### **Does Self-Hosting Make A Form Platform HIPAA Compliant?**
No. Self-hosting enables more control over infrastructure and data boundaries. Compliance still depends on how the environment is configured, monitored, documented, and governed.
### **Can Form.io Be Used For HIPAA Workflows?**
Form.io provides healthcare-oriented form infrastructure and security/compliance capabilities that can support HIPAA-governed workflows in customer-controlled environments. The customer's organization remains responsible for its HIPAA compliance program, configuration, policies, and deployment controls.
### **Does Form.io Certify My Application As HIPAA Compliant?**
No. Form.io's own compliance-readiness language is clear that the platform provides technical capabilities that support regulated deployments; it does not certify a customer's application or organization for HIPAA.
### **Why Do Audit Logs Matter For HIPAA Forms?**
Audit logs help answer who accessed or changed data, when it happened, what entity was affected, and which workflow action ran. For healthcare SaaS teams, that evidence can matter as much as the original form submission.
### **Should PHI Be Stored In A Third-Party Form Vendor Account?**
It depends on the workflow, BAA, risk analysis, and organizational policy. For simple intake forms, vendor-managed storage may be acceptable. For healthcare SaaS platforms, application-owned or customer-controlled storage may be a better fit.
### **What Should I Ask Before Collecting PHI Through An Online Form?**
Ask where PHI is stored, who can access it, which BAA covers it, whether uploads and notifications are protected, how audit logs work, how long data is retained, how submissions are deleted or exported, and what happens when the form changes.
## **Build HIPAA-Governed Form Infrastructure With Form.io**
If your healthcare product only needs a simple intake form, choose the fastest HIPAA-enabled tool that satisfies your compliance review.
If your forms define product workflows, API contracts, submissions, permissions, audit evidence, and data boundaries, choose infrastructure that respects that complexity from the start.
[Try Form.io for healthcare SaaS form infrastructure](/try-formio-for-free/).
# When Your Forms Don’t Match Your Design System Part 2
[  ](https://form.io/when-your-forms-dont-match-your-design-system-part-2/)In [Part 1](/when-your-forms-dont-match-your-design-system-part-1/), we established the design system compliance problem. Now let’s solve it for 98% of cases using class overrides alone.
Class names let you replace the CSS classes on your form components without touching the HTML structure. This is faster, less fragile, and easier to maintain than template-level customization. Start with this method in every case, and only reach for template overrides if you can’t accomplish your design goals with classes alone.
### **What Is the Class Names Method?**
Form.io templates are built from components, and each component has named parts: `input`, `label`, `button`, and so on. Class names let you define exactly which CSS classes apply to each part. The HTML structure stays the same; only the classes change. Because you’re working at the class level, this approach works with any CSS framework, whether you’re using Tailwind, Bootstrap, or something entirely your own, so you’re never locked into a particular toolchain.
### **Before You Start**
This guide assumes you already have a working Form.io application using the `@formio/js` renderer. To add the Standard Template, install it from npm:
```
npm install @formio/standard-template
```
**Note:** The Standard Template is a new and actively evolving package. Check the[ GitHub repository](https://github.com/formio/standard-template) for the latest version and API details before adopting it in production.
### **The Structure**
Here’s what a theme definition looks like:
```
import { standardTemplate } from '@formio/standard-template';
import type { TemplateClasses } from '@formio/standard-template';
const myTheme: TemplateClasses = {
// Component definitions go here
};
Formio.use(standardTemplate('my-custom-theme', myTheme));
```
Each component you want to customize gets an entry, and each entry defines classes for different contexts (`form` mode versus `html` display mode) and for the different parts of that component. Once you’ve seen one component defined, the rest follow the same shape.
### **Building a Complete Theme**
Let’s build a complete theme from scratch using Tailwind classes, transforming a basic contact form to match a modern design system. We’ll add one piece at a time.
#### **Our goal:**
- Minimal, underline-style input fields with an accent focus state
- Small, uppercase labels in the accent color
- A gradient pill button with hover effects
- Comfortable spacing between fields
#### **Step 1: Input Fields**
```
const myTheme: TemplateClasses = {
input: {
form: {
input: [
'block',
'w-full',
'px-0',
'py-2.5',
'text-base',
'text-slate-800',
'bg-transparent',
'border-0',
'border-b-2',
'border-slate-300',
'focus:outline-none',
'focus:border-violet-600',
'placeholder:text-slate-400',
'transition-colors',
'duration-200'
]
}
}
};
```
Pause on the shape of that definition, because every other component follows it:
- `input` (the outer key) is the component type: text fields, email fields, and so on
- `form` is the context (edit mode; there’s also html for read-only display)
- `input` (the inner key) is the specific element within that component
- The array contains all the Tailwind classes applied to that element
The result is an underline-style input: no box, no background, just a bottom border that shifts to violet when the field has focus.
#### **Step 2: Add Labels**
```
const myTheme: TemplateClasses = {
label: {
form: {
label: [
'block',
'text-xs',
'font-bold',
'uppercase',
'tracking-wider',
'text-violet-600',
'mb-2'
]
}
},
input: {
// ...input classes from Step 1
}
};
```
Labels now have their own styling: small, bold, uppercase, with letter-spacing and the accent color picking up the same violet as the input focus state. This sits alongside the input definition rather than inside it, because labels and inputs are independent components.
#### **Step 3: Add Buttons**
```
const myTheme: TemplateClasses = {
button: {
form: {
button: [
'w-full',
'px-6',
'py-3',
'text-sm',
'font-bold',
'uppercase',
'tracking-wider',
'text-white',
'bg-gradient-to-br',
'from-violet-600',
'to-violet-700',
'rounded-full',
'shadow-lg',
'shadow-violet-600/30',
'cursor-pointer',
'transition',
'duration-150',
'hover:opacity-90',
'hover:-translate-y-px',
'disabled:opacity-50',
'disabled:cursor-not-allowed'
]
}
},
label: {
// ...label classes from Step 2
},
input: {
// ...input classes from Step 1
}
};
```
The button becomes a full-width gradient pill: violet gradient background, a soft glow shadow, a subtle lift on hover, and proper disabled states. Notice the pattern: each component is self-contained, and adding a new one never disturbs the others.
#### **Step 4: Add Field Spacing**
```
const myTheme: TemplateClasses = {
component: {
form: {
component: [
'mb-6'
]
}
},
button: {
// ...button classes from Step 3
},
label: {
// ...label classes from Step 2
},
input: {
// ...input classes from Step 1
}
};
```
The `component` entry wraps every field in the form, so a single `mb-6` here gives each field comfortable breathing room below it. That’s the last piece of the theme.
### **The Complete Theme**
Here’s the full theme definition:
```
import { standardTemplate } from '@formio/standard-template';
import type { TemplateClasses } from '@formio/standard-template';
const myTheme: TemplateClasses = {
label: {
form: {
label: [
'block',
'text-xs',
'font-bold',
'uppercase',
'tracking-wider',
'text-violet-600',
'mb-2'
]
}
},
input: {
form: {
input: [
'block',
'w-full',
'px-0',
'py-2.5',
'text-base',
'text-slate-800',
'bg-transparent',
'border-0',
'border-b-2',
'border-slate-300',
'focus:outline-none',
'focus:border-violet-600',
'placeholder:text-slate-400',
'transition-colors',
'duration-200'
]
}
},
button: {
form: {
button: [
'w-full',
'px-6',
'py-3',
'text-sm',
'font-bold',
'uppercase',
'tracking-wider',
'text-white',
'bg-gradient-to-br',
'from-violet-600',
'to-violet-700',
'rounded-full',
'shadow-lg',
'shadow-violet-600/30',
'cursor-pointer',
'transition',
'duration-150',
'hover:opacity-90',
'hover:-translate-y-px',
'disabled:opacity-50',
'disabled:cursor-not-allowed'
]
}
},
component: {
form: {
component: [
'mb-6'
]
}
}
};
// Apply it globally
Formio.use(standardTemplate('my-custom-theme', myTheme));
```
Apply this once when your application initializes, and every form in your application will use the styling.
### **Before:**
### **After:**
### **Next Steps**
You now have everything you need to style Form.io forms to match your design system using class overrides. From here, the work is mostly a matter of breadth. The same pattern extends to every other component:
- **Radio buttons and checkboxes:** `radio`, `checkbox`
- **Select dropdowns:** `select`
- **Text areas:** `textarea`
- **Error and help text:** `errorLabel`, `helpBlock`
- **Field containers:** `component`, `field`
In every case you define classes for the component type and its parts, exactly as we did above. A textarea, for example, would take the same underline treatment as the inputs, plus `resize-y` and a `min-h-20` so users can expand it comfortably.
As your themes grow, it helps to pull them into their own modules so you can reuse them across projects:
```
// themes/tailwind-modern.ts
export const tailwindModern: TemplateClasses = {
// Your theme definition
};
// app.ts
import { tailwindModern } from './themes/tailwind-modern';
Formio.use(standardTemplate('tailwind-modern', tailwindModern));
```
Do this consistently and you end up with a library of themes you can share across your organization and maintain as part of your design system.
### **Additional Resources**
- [**Standard Template Playground**](https://apps.form.io/standard-template/): Interactive examples of different themes and styling approaches
- [**GitHub Repository**](https://github.com/formio/standard-template): Inspect the code and learn more about what you can target with CSS
# When Your Forms Don’t Match Your Design System Part 1
[  ](https://form.io/when-your-forms-dont-match-your-design-system-part-1/)Your design team just shipped an updated component library. New focus rings, refined spacing, updated color tokens. Engineering updates the React components, the dashboard layouts, and the navigation. Everything looks cohesive.
Then someone opens a form.
Form.io has been powering your dynamic forms beautifully. It handles complex conditional logic, multi-step workflows, and validation rules that would take many engineering hours to build from scratch. The form builder itself is invaluable: non-technical team members can create and modify forms without engineering involvement.
But visually, those forms still use the Bootstrap classes and markup they shipped with. Now there’s a mismatch. The rest of your application has evolved, and the forms haven’t.
This isn’t a Form.io problem. It’s a sign of success. Your product has matured to the point where your design system requirements go beyond any form builder’s defaults.
## **Why This Happens**
Form.io ships with professional, well-designed templates based on Bootstrap, and that’s exactly what you want when you’re getting started. These defaults handle everything: inputs, buttons, radio groups, validation messages, error states. They’re accessible, well-tested, and work across browsers. For many teams, they’re perfect and require no customization at all.
But as your product matures, specific visual requirements tend to surface. Maybe your design system has standardized on Tailwind rather than Bootstrap. Maybe you’ve built up custom brand colors, spacing scales, and typography, or your design team has defined particular interaction patterns. And at some point, “close enough” stops being good enough. You need the forms to match the rest of your application pixel-for-pixel. That’s the moment you need to customize Form.io’s visual layer while keeping everything else that makes it valuable.
## **What Teams Try Today**
Before Standard Template When teams hit this point in their product evolution, they usually reach for one of four approaches. Each comes with real trade-offs.
1. **Convince design to accept the form builder’s defaults.** Sometimes that works for internal tools, but for a customer-facing product with established brand guidelines, it’s usually a non-starter.
2. **Write custom CSS that overrides the defaults.** This works until it doesn’t: you can change colors and spacing, but you can’t restructure HTML with CSS, future updates might break your overrides, and maintenance gets expensive.
3. **Rebuild the component templates from the ground up.** You could use the default Form.io Bootstrap 5 template as a guide for writing your own. That gives you complete control, but now you’re maintaining even more code. It’s technically possible, but operationally expensive.
4. **Build a custom form system from scratch.** The most drastic option. Do this and you throw away Form.io’s conditional logic, validation rules, and visual builder, everything that made it valuable in the first place. It’s rarely justified. You chose Form.io for a reason.
What most teams actually want is something none of those quite delivers: keep Form.io’s powerful form logic and builder interface, but adapt the visual layer to match their design system.
## **The Standard Template**
After Standard Template The Standard Template introduces a customization system that works *with* Form.io’s existing architecture instead of against it. Its core mechanism is **Style Map**: you replace the CSS classes on existing HTML elements without changing the underlying structure. It works with any CSS framework, whether that’s Tailwind, Bootstrap, or a fully custom design system, and it’s fast to implement and easy to maintain. With the Standard Template, you’re configuring Form.io’s rendering layer, not fighting it.
This approach makes sense when you have an established design system with specific requirements, several forms that need to stay visually consistent, and a product where design system compliance matters, and you want all of that without giving up Form.io’s form logic and builder.
Just as important is knowing when you *don’t* need it. If Form.io’s default Bootstrap theme already works for you, if you only have a form or two, if your forms are internal tools where strict visual consistency isn’t a concern, or if you’re just getting started and should be optimizing for speed over pixel-perfection, then reaching for customization only creates work. Form.io’s defaults are professionally designed and serve most use cases well. Don’t make work for yourself unless you have a clear requirement.
## **Wrapping Up**
Adopting the Standard Template gives you the best of both worlds: Form.io’s powerful form capabilities with your design system’s visual consistency. Once it’s in place, your forms match your design system’s colors, spacing, and typography, while non-technical users keep building and modifying forms in the Form.io builder exactly as before. All of Form.io’s logic, validation, conditionals, and calculations keep working, your maintenance burden shrinks to a set of class definitions and the occasional template override, and new Form.io features and updates apply without conflicts.
The Standard Template is now available with the [release of Form.io 9.8.0](/release-notes/formio-enterprise-9-8-0-and-pdf-server-5-14-0/).
In [Part 2](/when-your-forms-dont-match-your-design-system-part-2/), I’ll show you how class overrides work with concrete examples. You’ll build a complete Tailwind theme from scratch without touching a single line of HTML.
# MCP Server List: What Regulated Enterprise Developers Should Actually Use
[  ](https://form.io/mcp-server-list-regulated-enterprise-developers/)You can find an MCP server list in seconds. That is not the hard part. The hard part is deciding which servers deserve access to your source code, cloud accounts, tickets, documentation, test environments, and production-adjacent business data.
For regulated enterprise developers, the question is not "which MCP servers are popular?" It is "which MCP servers can we trust inside a governed workflow?"
## **The quick answer**
Start with the official MCP Registry, then filter by control surface.
For regulated enterprise development, the strongest shortlist usually includes:
**MCP surface****Best fit****Enterprise question**Official MCP RegistryDiscovery and metadataIs this server officially published, namespace-authenticated, and still current?GitHub MCP ServerRepos, pull requests, issues, Actions, security findingsCan the agent work inside the same SDLC boundary developers already use?GitLab MCP ServerGitLab.com, self-managed GitLab, Duo workflowsDoes it respect the deployment model and permissions your GitLab instance already enforces?AWS MCP ServersCloud architecture, docs, API operationsAre IAM, least privilege, CloudWatch metrics, and CloudTrail evidence understood before use?Azure MCP ServerAzure resources, Entra ID-backed cloud workflowsDoes the server inherit the identity and guardrail model your Azure teams already use?Atlassian Rovo MCP ServerJira, Confluence, CompassDoes the agent see only what the user has permission to see?Playwright MCPBrowser automation and UI testingAre unsafe direct-code tools disabled unless the client is trusted?Sentry MCPDebugging and observabilityCan the agent inspect errors without turning observability into an unbounded data pipe?Docker MCP toolingLocal gateway, catalog, containerized MCP operationsCan servers be packaged and scoped consistently across teams?Form.io MCP ServerForms, resources, actions, APIs, and schema-driven application infrastructureCan the agent build against governed form and API patterns instead of improvising them?That is the useful MCP server list for regulated teams: not a popularity contest, but a map of which systems an agent can touch, how it authenticates, what it can change, and where the audit evidence lands.
## **What an MCP server list can and cannot tell you**
MCP, or Model Context Protocol, gives AI clients a standard way to connect to external tools and data. An MCP server is the bridge between the agent and a system such as GitHub, AWS, Jira, a browser, a database, or a domain platform such as Form.io.
An MCP server list helps with discovery. It does not prove that a server belongs in your enterprise agent environment.
That distinction matters because the official MCP Registry itself is a metadata layer. The registry documentation describes it as the official centralized repository for publicly accessible MCP server metadata, while also noting that it is still in preview and does not support private servers. It supports discovery, namespace authentication, installation metadata, and REST API access. It is not a substitute for enterprise security review.
That is the first mistake many teams make. They treat discovery as approval.
For a developer testing locally, that may be tolerable. For a regulated team, it is a weak control. A server that reads public docs is not in the same risk category as a server that can open pull requests, read customer tickets, execute cloud API calls, or inspect production error traces.
The list is the beginning. The trust decision comes after.
## **The regulated-enterprise filter**
Before you add a server to Claude Code, Cursor, VS Code, Windsurf, or another MCP client, ask six questions.
### **Who maintains it?**
Prefer official or vendor-maintained servers when the system is critical. A community server can be useful, but enterprise teams need a clear owner, release trail, issue history, and support path.
This is why GitHub, GitLab, AWS, Azure, Atlassian, Playwright, Docker, Sentry, and Form.io deserve separate treatment from generic directories. They are not just "available MCP servers." They are maintained by, or directly tied to, the systems they expose.
### **What identity model does it inherit?**
A lower-risk server is usually one that inherits the identity and permission model already governing the system.
[GitLab's MCP docs](https://docs.gitlab.com/user/gitlab_duo/model_context_protocol/mcp_server/), for example, describe OAuth registration and HTTP transport options, and they support GitLab.com, Self-Managed, and Dedicated environments. [Atlassian's remote MCP server](https://support.atlassian.com/atlassian-rovo-mcp-server/docs/getting-started-with-the-atlassian-remote-mcp-server/) uses OAuth 2.1 and respects Jira, Confluence, and Compass permissions. [Azure MCP Server](https://learn.microsoft.com/en-us/azure/developer/azure-mcp-server/overview) uses Microsoft Entra ID through Azure Identity.
That matters more than convenience. If the server works around identity, it works around governance.
### **What can it mutate?**
Read-only access is one risk. Write access is another. Production mutation is another.
A server that searches docs can still leak context. A server that changes infrastructure, submits forms, opens tickets, or modifies code can create operational state. Treat those differently.
The [MCP security guidance](https://modelcontextprotocol.io/specification/2025-06-18/basic/security_best_practices) calls out risks such as confused deputy behavior, token passthrough, SSRF, session hijacking, local server compromise, and the need to minimize scopes. Those are not abstract security concerns. They are what happens when an agent can act through a server whose authority is broader than the user's intent.
### **Where are logs written?**
Regulated teams need evidence. If an agent uses a server to retrieve context, change an issue, call an API, or update a form definition, the team needs to know where that action is logged.
AWS is a useful benchmark here. AWS announced the [AWS MCP Server general availability](https://aws.amazon.com/about-aws/whats-new/2026/05/aws-mcp-server/) on May 6, 2026, describing IAM-based guardrails, Amazon CloudWatch metrics, and AWS CloudTrail logging. That does not make every AWS MCP use case automatically approved, but it does give enterprise teams a familiar evidence model.
### **What data crosses the boundary?**
Some MCP servers expose local files. Some expose SaaS data. Some connect to cloud accounts. Some connect to internal systems. Some domain-specific servers, such as the Form.io AI toolset, connect to a customer's self-hosted environment.
The boundary is the point.
Form.io describes its MCP Server as connecting to a customer's self-hosted Form.io deployment so AI coding agents can work with forms, resources, actions, and APIs without moving that governed surface outside the enterprise boundary. That is a different posture from a generic public directory listing.
### **Is this build-time or runtime?**
Do not collapse every agentic tool into one bucket.
MCP servers are usually build-time or operator-time connectors. They help coding agents and assistants read context, call tools, scaffold work, or interact with systems.
Runtime agent governance is different. Form.io's [Universal Agent Gateway](https://form.io/uag/) belongs in that adjacent category. UAG is not the same thing as the Form.io MCP Server. The MCP Server helps AI coding agents build against Form.io patterns. UAG governs production agent workflows at runtime.
Regulated teams need both concepts, but they should not confuse them.
## **The MCP servers worth knowing**
### **1. Official MCP Registry**
Use the official registry as the starting point, not the finish line.
The [official registry](https://modelcontextprotocol.io/registry/about) is valuable because it gives teams a canonical discovery surface for public MCP servers. It supports server metadata, namespace authentication, REST API discovery, package references, and standardized installation information.
For enterprise teams, the important detail is the limit. The registry is public. It is still in preview. It is not where private enterprise servers should live. It also does not remove the need to review code, packages, transport, authentication, scopes, and data handling.
Use it to find servers. Do not use it as your approval workflow.
### **2. GitHub MCP Server**
The [GitHub MCP Server](https://github.com/github/github-mcp-server) belongs in many enterprise developer shortlists because GitHub is where source code, issues, pull requests, Actions, security findings, and review state already live for many teams.
That makes it powerful. It also makes it sensitive.
A coding agent that can inspect a repo, summarize issues, open a pull request, or reason over security findings is operating close to the SDLC evidence trail. That can be a good thing when the team scopes access properly. It can be a problem when every repo is available by default.
Use GitHub MCP when the agent needs to work inside the same development boundary developers already use. Scope it to the repositories and operations needed for the task.
### **3. GitLab MCP Server**
GitLab deserves its own place because many regulated organizations use self-managed GitLab or GitLab Dedicated rather than a purely public SaaS setup.
The official GitLab MCP documentation supports GitLab.com, Self-Managed, and Dedicated environments. It also warns that users are responsible for guarding against prompt injection and should use MCP tools only with trusted GitLab objects.
That warning is useful. It says the quiet part plainly: permission inheritance is not the whole security model. If an agent reads hostile issue content, merge request comments, or documentation, those objects can become part of the instruction stream.
Use GitLab MCP where GitLab is already the system of record for code and planning, but pair it with prompt-injection hygiene and object-scope limits.
### **4. AWS MCP Servers**
AWS MCP belongs in the list because cloud infrastructure is where agent mistakes become expensive.
AWS has multiple MCP surfaces, including [AWS Labs servers](https://github.com/awslabs/mcp/) and the generally available [AWS MCP Server](https://aws.amazon.com/blogs/aws/the-aws-mcp-server-is-now-generally-available/). The managed server is especially relevant to enterprise teams because AWS describes IAM guardrails, SigV4-style authenticated access through the Agent Toolkit, CloudWatch metrics, CloudTrail logging, AWS Knowledge MCP, AWS API MCP capabilities, and access to more than 15,000 AWS APIs.
That is exactly why the risk bar is high.
An agent that can ask AWS docs questions is one thing. An agent that can call AWS APIs is another. The minimum viable control is least-privilege IAM, environment separation, and CloudTrail visibility. Without those, cloud MCP access is too broad for regulated workflows.
Use AWS MCP for documentation, architecture support, and tightly scoped operations. Do not give a general coding agent broad cloud authority just because the server exists.
### **5. Azure MCP Server**
Azure MCP is important for teams whose cloud control plane already sits under Microsoft identity.
Microsoft's Azure MCP Server documentation describes integration with Azure resources, developer tools such as VS Code and GitHub Copilot, and authentication through Azure Identity. For enterprise teams, the key phrase is not "Azure resources." It is identity inheritance.
If the server can operate through Entra ID-backed access patterns and the same Azure permissions teams already govern, it fits better than a standalone connector with its own unmanaged secrets.
Use Azure MCP where the team already has mature Azure role design, environment separation, and resource governance.
### **6. Atlassian Rovo MCP Server**
Jira and Confluence are where a lot of enterprise work actually lives: requirements, tickets, runbooks, decisions, incident notes, acceptance criteria, and stakeholder context.
Atlassian's Rovo MCP Server documentation describes OAuth 2.1, support for Jira, Confluence, and Compass, permission inheritance, and IP allowlisting behavior in Atlassian Cloud.
That makes it a strong context server, especially for coding agents that need product intent or implementation history.
The risk is also obvious. Tickets and docs often contain sensitive business context, customer details, credentials copied where they should not be, and architectural notes. Permission inheritance helps, but it does not classify the content for you.
Use Atlassian MCP for project and documentation context, with clear limits on what spaces, projects, and user scopes are exposed.
### **7. Playwright MCP**
Playwright MCP is one of the most useful developer servers because it gives agents a structured way to interact with web pages and browser workflows.
The [Playwright MCP docs](https://playwright.dev/docs/getting-started-mcp) describe use of accessibility snapshots rather than screenshots or pixel-based interaction. That is the right foundation for repeatable browser automation.
But the same documentation also warns that direct Playwright code execution is effectively remote code execution and should only be enabled for trusted MCP clients.
That is the regulated-enterprise lesson in miniature. A tool can be both useful and unsafe if enabled in the wrong mode.
Use Playwright MCP for testing, QA, browser workflows, and UI validation. Disable unsafe direct-code tools unless the client and execution environment are trusted.
### **8. Sentry MCP**
The [Sentry MCP Server](https://github.com/getsentry/sentry-mcp) belongs in the operational layer. It helps agents inspect errors, traces, issues, and debugging context.
That can compress the time between "the build failed" and "the actual production error is understood." It also exposes operational data that may include request context, user metadata, stack traces, and environment details.
For regulated teams, observability MCP should be scoped like production support access, not like a convenience plugin.
Use Sentry MCP when the agent is doing debugging or remediation work, and restrict the projects, environments, and data fields that should be visible.
### **9. Docker MCP tooling**
[Docker's MCP tooling](https://docs.docker.com/reference/cli/docker/mcp/) is less about one business system and more about packaging, gateway behavior, and local developer operations.
That makes it useful for standardization. Enterprise teams do not want every developer hand-rolling MCP server installation and transport decisions in a different local config file.
Use Docker MCP tooling to make server setup more repeatable, especially when you need a catalog or gateway-style operating model across teams.
### **10. Form.io MCP Server**
Form.io belongs in this MCP server list because regulated applications often begin at the data-capture layer: forms, resources, validation rules, submission records, workflow actions, APIs, permissions, revisions, and audit evidence.
That is the layer where generic coding agents can create drift fastest.
One team builds a React form. Another builds a different submission API. A third adds an agent workflow. Each piece works. None of them share the same governance contract.
The [Form.io AI toolset](https://form.io/ai/) exists to push the agent toward the governed path at build time. The Form.io MCP Server connects AI coding agents to a customer's self-hosted Form.io deployment so they can read, create, and scaffold forms, resources, actions, and APIs from the same platform primitives. Form.io Skills guide the agent toward platform-specific patterns. The Agentic Coding Plugin brings that MCP Server and skill library into the developer's coding environment.
That makes Form.io different from a generic connector.
It is not just giving an agent another data source. It is giving the agent a governed application primitive: schemas that can produce interfaces, APIs, validation behavior, submissions, permissions, and workflow hooks from the same definition.
For teams using Form.io as [schema-driven application infrastructure](https://form.io/platform/), this is the right kind of MCP server: one that makes the governed path easier than building around it.
That value shows up in customer language too. In a [Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/), a long-time Form.io platform user put it plainly: "Form.io cleans up all the dirty work and does it for you." The surrounding case study frames that value as months of development time saved on a next-generation application launch.
## **How to decide what belongs in your agent context**
The fastest way to create MCP sprawl is to install every useful server globally.
Do not do that.
Treat MCP servers like permissions. Most should be project-specific, task-specific, or environment-specific.
Use this sequence:
1. Start with read-only discovery.
2. Prefer official or vendor-maintained servers.
3. Scope by project, repo, workspace, tenant, or environment.
4. Keep mutation tools disabled until the workflow needs them.
5. Separate local development access from production access.
6. Route secrets through existing identity systems where possible.
7. Log agent actions in the system of record.
8. Review prompt-injection exposure when the server reads user-authored content.
9. Revoke unused servers.
That may sound slower than "install the top 20 MCP servers." It is not slower when you count remediation.
A regulated team that cannot explain which server had which permission at which point in a workflow does not have an MCP strategy. It has a collection of shortcuts.
## **Why domain-specific MCP matters**
Generic MCP servers are good at giving agents access to tools. Domain-specific MCP servers are better when the agent needs to create governed artifacts.
That difference is especially important for forms and workflow data.
A generic file server can read a schema file. A GitHub server can modify code. A browser server can test a form. None of those, by itself, tells the agent what a valid governed form workflow should look like inside the enterprise.
Form.io's MCP Server does.
The reason is architectural. Form.io is not only a form renderer. Its [drag-and-drop form builder and API model](https://form.io/features/drag-and-drop-form-builder-apis/) treats form definitions as JSON-backed application infrastructure. Forms can produce APIs. Submission data is managed separately from Form JSON. Form revisions and submission management matter because historical state and current state are not always the same thing.
That is why the Form.io MCP Server matters for regulated developers. It helps the coding agent build with the same primitives the platform governs: forms, resources, actions, APIs, roles, group permissions, server-side actions, [form revision history](https://form.io/features/form-revisions-form-json-schema/), and [complete audit trails](https://form.io/features/log-forms-complete-audit-trail/).
That does not mean Form.io replaces GitHub, GitLab, AWS, Azure, Playwright, Sentry, or Atlassian. It means Form.io occupies a different layer: the form and workflow infrastructure layer where business data enters the system and becomes governed submission state.
## **What proof should enterprise teams look for?**
Popularity is weak proof.
Stars, upvotes, and directory rank tell you that a server is visible. They do not tell you whether the server is appropriate for regulated work.
Better proof looks like this:
- Official or vendor-maintained source.
- Clear authentication model.
- Clear transport model.
- Least-privilege configuration.
- Permission inheritance from the system of record.
- Audit logging for meaningful actions.
- Environment separation.
- Versioned releases.
- Security guidance.
- Support for private or self-managed deployment where needed.
The production-readiness gap is real. A [2026 research paper on production MCP](https://arxiv.org/abs/2603.13417) reports more than 10,000 active MCP servers and 97 million monthly SDK downloads, while also arguing that production MCP still needs stronger identity propagation, adaptive tool budgeting, structured error semantics, and observability.
That is the point. MCP adoption is moving faster than MCP governance.
The answer is not to wait. The answer is to be precise.
Use servers that inherit controls you already trust. Scope them narrowly. Prefer domain-specific servers when the agent is creating governed artifacts. Treat runtime agent governance as a separate layer from coding-time MCP.
## **Key takeaways**
- An MCP server list helps you discover options, but it does not approve them for regulated use.
- Official and vendor-maintained servers should carry more weight than generic directory entries.
- Evaluate each server by identity, permissions, audit evidence, transport, data boundary, and mutation risk.
- GitHub, GitLab, AWS, Azure, Atlassian, Playwright, Sentry, Docker, and Form.io each occupy different control surfaces.
- Form.io's MCP Server is a build-time path into governed form and API infrastructure; UAG is the separate runtime governance layer.
## **FAQ**
### **What is an MCP server list?**
An MCP server list is a directory, registry, repository, or article that helps developers find Model Context Protocol servers. The best starting point is the official MCP Registry, but regulated teams should treat any list as discovery rather than approval.
### **What is the safest way to find MCP servers?**
Start with official sources: the official MCP Registry, vendor documentation, vendor-maintained GitHub repositories, and your own internal registry for private servers. Avoid installing servers only because they appear in a public directory or social post.
### **Are MCP servers secure?**
MCP servers are not automatically secure or unsafe. Security depends on the server's code, maintainer, transport, authentication model, tool scope, permissions, data access, and execution environment. The MCP security guidance specifically calls out risks such as confused deputy behavior, token passthrough, SSRF, session hijacking, local compromise, and scope minimization.
### **Should regulated teams use community MCP servers?**
Sometimes, but not casually. A community server can be useful for low-risk local workflows, prototypes, or read-only tasks. For sensitive systems, prefer official or vendor-maintained servers, or run an internal review before adding the server to an enterprise agent environment.
### **Which MCP servers are best for developers?**
A practical regulated-enterprise list usually starts with GitHub or GitLab for SDLC work, Playwright for browser testing, AWS or Azure for cloud workflows, Atlassian for ticket and documentation context, Sentry for debugging, Docker for packaging and gateway patterns, and Form.io for governed form/API infrastructure.
### **What is the difference between an MCP registry and an MCP server?**
An MCP registry helps you discover servers and their metadata. An MCP server is the actual connector that exposes tools, data, or actions to an MCP client. A registry is not a security review, and it does not mean the server is safe for your environment.
### **How does Form.io fit into an MCP server list?**
Form.io fits when the agent needs to work with governed form and workflow infrastructure. The Form.io MCP Server gives AI coding agents access to Form.io forms, resources, actions, and APIs inside the customer's deployment boundary, while Form.io Skills guide the agent toward platform-specific implementation patterns.
### **Is Form.io UAG an MCP server?**
No. Form.io's MCP Server is build-time infrastructure for AI coding agents. UAG is runtime governance for production agent workflows. They belong in the same agentic architecture conversation, but they are not the same component.
### **Should MCP servers be installed globally?**
Usually no. Global installation encourages overbroad access. Regulated teams should scope MCP servers by project, workspace, environment, repository, tenant, or task. Mutation tools should be enabled only when the workflow requires them.
### **What should an enterprise MCP policy include?**
At minimum, it should define approved server sources, identity requirements, permission scopes, logging expectations, data-boundary rules, prompt-injection handling, environment separation, and a removal process for unused or deprecated servers.
### **When should a team build its own MCP server?**
Build your own MCP server when the system is internal, private, highly regulated, domain-specific, or poorly represented by public servers. Private systems should not be forced into public registries just to make them usable by agents.
## **Build Governed Form And API Workflows With Form.io**
If your team needs AI coding agents to build against governed forms, generated APIs, submission records, permissions, revisions, and self-hosted infrastructure, [try Form.io for governed form and API workflows](/try-formio-for-free/).
# AI Governance Platform: Agentic Workflow Governance Layers Compared
[  ](https://form.io/ai-governance-platform-agentic-workflow-governance-layers-compared/)AI governance platform searches hide several different problems under one phrase. A policy registry is not runtime tool-call control. A process engine is not schema-driven data access. If agents can read data, invoke tools, submit records, and trigger workflows, governance has to live where the agent acts. This comparison names the layer before judging the tool.
## **The AI Governance Gap Is Now Operational**
Most AI governance conversations started with model risk, policy documentation, and compliance review. Those still matter.
But agentic workflows add a sharper question: what happens when the AI system can do something?
Grant Thornton's 2026 AI Impact Survey found that 78% of senior business leaders lacked full confidence that their organization could pass an independent AI governance audit within 90 days. The same survey said 46% of leaders believed AI underperformed because controls and compliance were not working ([Grant Thornton](https://www.grantthornton.com/insights/press-releases/2026/april/grant-thornton-survey-on-ai-proof-gap)).
That is not just a board-level policy problem. It is an infrastructure problem.
Gartner's 2025 strategic technology trends report predicted that by 2028, at least 15% of day-to-day work decisions would be made autonomously through agentic AI, up from 0% in 2024 ([Gartner](https://www.gartner.com/en/newsroom/press-releases/2024-10-21-gartner-identifies-the-top-10-strategic-technology-trends-for-2025)). If even a small share of ordinary operational decisions moves through agents, governance has to follow the action, not only the policy record.
If an agent can approve a request, update a record, route a case, draft a decision, trigger an integration, or submit structured data into a system of record, the organization needs more than a governance statement. It needs an execution path that can answer:
- What was the agent allowed to do?
- Which identity or role gave it that permission?
- What schema, validation rule, or process state constrained the action?
- Was a human required to approve it?
- What audit evidence exists after the action?
An AI governance platform can help with policy, inventory, and risk. An agentic workflow needs that, plus runtime controls at the exact layer where the agent touches the business system.
## **Five Governance Layers To Compare**
The phrase "AI governance platform" is too broad unless you name the layer.
For agentic workflows, the main layers are:
**Governance layer****What it governs****Example fit**AI policy and risk governanceAI inventory, use cases, risk tiering, compliance evidence, board reportingCredo AI, OneTrust, IBM watsonx.governance, classic GRC-style AI governance suitesRuntime agent governanceTool calls, resource access, inter-agent messages, action-level policy enforcementMicrosoft Agent Governance ToolkitProcess orchestration governanceBPMN, case state, human tasks, SLAs, process audit trails, exception handlingCamunda 8.9, Flowable 2025.1, Appian process workflowsPlatform-native agent governanceAgents built and managed inside a specific app/process platformAppian Agent StudioSchema/API/data-access governanceThe forms, fields, validation rules, submissions, APIs, roles, and actions an agent uses to do workForm.io Universal Agent GatewayThese layers can overlap. They can also coexist.
A bank might use Microsoft Entra for agent identities, Microsoft Agent Governance Toolkit for action-level policy, Camunda for cross-system process orchestration, and Form.io UAG for governed access to intake forms, validation, submissions, and downstream workflow actions.
The mistake is treating those as interchangeable.
## **Quick Comparison**
## **Platform or toolkit****Governance center of gravity****Strongest fit****Watch the boundary**Form.io UAGSchema, form, API, submission, RBAC, and action governance exposed to agents through MCPAgents that need governed access to forms, submissions, validation, and workflow infrastructureNot a generic AI GRC dashboard or full BPMN engineAppian Agent StudioAgents embedded inside Appian's process/application platformTeams already building workflows in AppianStrong inside Appian's platform boundary; less about portable schema/API ownershipCamunda 8.9BPMN-based agentic orchestration, human tasks, process state, audit logs, MCP/A2ATeams that govern work through explicit process modelsGovernance starts at orchestration; the data-capture/schema layer may still live elsewhereFlowable 2025.1Agent engine beside BPMN/CMMN/DMN, agent exchange tracking, case/process controlDynamic case work and process automation with first-class agentsStrong process layer; still needs source-of-truth data contractsMicrosoft AGTRuntime policy enforcement, identity, sandboxing, OWASP agentic risk controlsDevelopers adding action-level governance to agent frameworksA toolkit, not a business workflow or forms infrastructure platform**Form.io UAG: When The Governed Schema Should Become Agent Context**
Form.io's Universal Agent Gateway is strongest when the agent has to operate through a governed form and workflow layer instead of a loose collection of prompts, tools, and credentials.
Form.io's core argument starts below the agent. In Form.io, Form JSON is the schema created by the form builder. The Form.io documentation says that schema is used to render forms inside applications, generate REST API interfaces on the server, and host the form schema at the embed URL ([Form.io Form JSON documentation](https://help.form.io/userguide/forms/form-building/form-json)).
That matters because an agent needs structured context.
An agent does not need a vague prompt saying "collect the right onboarding details." It needs to know which fields exist, which fields are required, what validation rules apply, how submissions are shaped, which actions can run, and what permissions apply to the current actor.
Form.io UAG turns that existing application infrastructure into the agent surface. The UAG page explains that agents can authenticate through existing Form.io auth and SSO, inherit enterprise RBAC, retrieve and route secure data inside the private network, and execute actions governed by Form.io Actions and audit trails ([Form.io UAG](https://form.io/uag/)).
That is a specific kind of governance. It is not "AI governance" as a board dashboard. It is governance at the layer where forms, APIs, submissions, validation, and workflow actions already meet.
This is why Form.io should not be framed as simply another AI agent platform. Form.io's AI page describes UAG as the runtime governance layer for production agentic workflows, while the MCP Server, Skills, and Agentic Coding Plugin support build-time development ([Form.io AI](https://form.io/ai/)). That separation is important. Build-time agents need patterns for creating software. Runtime agents need permissioned, logged access to production workflow surfaces.
The customer proof is not AI-specific yet, so it should be used carefully. But it does show why this infrastructure layer matters. In one Form.io public-sector case study, publicplan supported more than 400 digital public-sector services and 1,000+ forms while meeting strict standards and a short timeline ([Form.io publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)). In another Form.io banking case study, an international banking deployment served 5,000 banking groups and recovered 50% of the team's capacity ([Form.io banking case study](https://form.io/case-studies/how-many-technologies-can-actually-support-the-business-process-transformation-of-serving-5000-banking-groups/)).
Those are not UAG deployment claims. They are infrastructure claims. They show why a governed forms/API/submission layer is valuable before agents arrive. UAG extends that same layer to agents.
### **Strongest Fit**
Form.io UAG is the strongest fit when:
- forms are part of the application contract, not just hosted collection pages
- agents need to understand field structure, validation rules, submission shape, and workflow actions
- the customer needs self-hosted or private-network control
- RBAC, auth, audit trails, and form revisions are already part of the governance model
- the team wants humans and agents operating through the same governed schema layer
Form.io is not the right answer if the buyer only needs a general AI policy registry. It is the right answer when the agent's work touches form-driven application infrastructure.
## **Appian Agent Studio: When Agents Belong Inside The Appian Process Platform**
Appian's governance story is platform-native.
Agent Studio is built for teams that already use Appian to design applications, workflows, data fabric patterns, and enterprise processes. Appian's 25.4 release material frames Agent Studio as a guided way to create enterprise AI agents and drag them into business processes. Appian also says agents embedded in processes can use guardrails, tools, data, and human review inside the process context (Appian Agent Studio release material).
That is a clear fit when Appian is already the process application platform.
The governance center is not the open schema/API layer. It is the Appian platform boundary. Agents live inside the Appian design and process model, use Appian objects and tools, and inherit governance from the Appian environment.
That can be exactly what an Appian customer wants. It is less compelling when a team needs agent access to application-owned forms, APIs, validation rules, submissions, and deployment boundaries outside Appian.
### **Strongest Fit**
Appian Agent Studio fits when:
- the business process already lives in Appian
- low-code process design is the center of gravity
- agents need to operate inside Appian's app/process/data fabric layer
- the organization wants human review and process guardrails inside the same platform
The Form.io contrast is not "Appian cannot govern agents." It can govern them inside its platform. The Form.io distinction is that governance starts at the schema and form infrastructure layer agents use to collect, validate, submit, and route data.
## **Camunda 8.9: When BPMN Orchestration Is The Governance Backbone**
Camunda approaches agentic governance from the process orchestration layer.
In its 8.9 release, Camunda frames agentic orchestration as coordinating AI agents, knowledge workers, tools, and systems across end-to-end business processes. The release emphasizes deterministic process logic, global user task listeners, centralized audit logs, MCP access to running clusters, and A2A support for multi-agent communication (Camunda 8.9 release material).
That is a strong governance story for teams that already model work as BPMN.
The useful distinction is this: Camunda governs the flow of work. It controls process state, human tasks, incidents, retries, escalation, and the audit trail around the process. That is different from governing the form schema, validation logic, submission payload, or field-level context an agent uses before it reaches a process step.
In many architectures, both layers matter.
A government service workflow might use Form.io to collect and validate service request data through self-hosted forms and generated APIs, then use Camunda to orchestrate downstream case routing, approvals, exceptions, and cross-system work. The agent should respect both layers.
### **Strongest Fit**
Camunda fits when:
- BPMN is already the operating language for process governance
- the organization needs explicit process state and incident handling
- agents participate in workflows with human tasks and deterministic rules
- auditability needs to follow the end-to-end process path
Form.io fits earlier in the path: where the agent needs governed access to the structured data, forms, validation rules, and APIs that feed the process.
## **Flowable 2025.1: When Case And Process Work Need First-Class Agents**
Flowable's 2025.1 release puts agents beside BPMN and CMMN rather than treating them as external helpers.
Flowable says the release adds an agent engine alongside its BPMN and CMMN automation engines, with internal agent types such as utility, document, knowledge, and orchestrator agents. It also describes agent exchange tracking as a way to store AI interactions for traceability and audit support (Flowable 2025.1 release material).
That makes Flowable a serious process/case governance comparison.
Its strongest fit is dynamic work: cases, documents, human judgment, process variation, and AI-assisted decisions that need to stay inside a process/case model. If a case state determines what an agent can and cannot do, Flowable's governance center makes sense.
The Form.io distinction is again layer ownership.
Flowable can govern the case or process. Form.io can govern the structured form and submission layer that feeds the case. In agentic workflows, those are connected but not identical.
### **Strongest Fit**
Flowable fits when:
- work is case-heavy and may not follow one fixed process path
- AI agents need to operate inside CMMN/BPMN-style orchestration
- traceability of agent exchanges matters
- the organization wants an agent engine inside the process platform
Form.io fits when the agent's most important constraint is the governed schema, validation, permission, submission, and action surface around data intake and form-driven workflows.
## **Microsoft Agent Governance Toolkit: When Developers Need Runtime Action Controls**
Microsoft Agent Governance Toolkit is the most developer-centered entry in this comparison.
Microsoft introduced AGT as an open-source runtime security governance project for autonomous AI agents. The announcement says the toolkit is designed to work with existing frameworks and includes deterministic policy enforcement, identity, sandboxing, reliability controls, and mapping to OWASP agentic AI risks ([Microsoft open-source announcement](https://opensource.microsoft.com/blog/2026/04/02/introducing-the-agent-governance-toolkit-open-source-runtime-security-for-ai-agents/)).
That layer matters because agents can misuse tools even when the surrounding workflow looks well designed.
Microsoft's later Agent Framework guidance makes the layer even clearer: Agent Framework handles build and orchestration, while Agent Governance Toolkit handles govern and audit. It evaluates tool calls, resource access, and inter-agent messages against policy before execution ([Microsoft Agent Framework and AGT](https://devblogs.microsoft.com/agent-framework/governance-at-the-speed-of-agents-microsoft-agent-framework-and-agent-governance-toolkit-better-together/)).
That is not the same job as Form.io UAG.
AGT helps govern the agent's actions at runtime. Form.io UAG gives agents governed access to Form.io's form, submission, schema, API, RBAC, and action layer. In some architectures, AGT could sit beside or around an agent framework, while UAG provides the business-specific tools and context the agent is allowed to use.
### **Strongest Fit**
Microsoft AGT fits when:
- developers need action-level policy checks inside an agent framework
- tool-call misuse, goal hijacking, rogue agents, or inter-agent trust are the main concern
- the team wants an open-source runtime governance toolkit
- the application/workflow platform is already chosen elsewhere
Form.io fits when the agent needs a governed business surface for form-driven work, not only a policy wrapper around tool calls.
## **How To Choose The Right Governance Layer**
The useful question is not "which AI governance platform should we buy?"
The useful question is: where can the agent create the most risk?
### **If The Risk Is AI Inventory And Compliance Evidence**
Start with a classic AI governance platform.
This is the layer for model inventory, use-case approvals, risk tiers, policy mapping, regulatory documentation, monitoring, and executive accountability. It matters most when the organization cannot answer which AI systems exist, who owns them, what risk category they fall into, or what evidence supports approval.
Form.io does not replace that layer.
### **If The Risk Is Tool-Call Misuse**
Look at runtime agent governance.
This is where Microsoft Agent Governance Toolkit is relevant. It helps evaluate actions before execution and provides runtime security controls for autonomous agent frameworks.
Form.io can supply governed business tools and context; AGT can help enforce broader action-layer policies.
### **If The Risk Is Process Visibility**
Look at process orchestration.
Camunda, Flowable, and Appian are stronger when the work has to be governed as a process or case: state, sequence, incidents, handoffs, human review, SLAs, escalation, and full process auditability.
Form.io can still matter if the workflow starts with governed forms, submissions, and APIs.
### **If The Risk Is Data, Schema, And API Drift**
This is where Form.io belongs.
If humans use one form definition, APIs use another contract, agents use a prompt-based tool description, and workflow actions use yet another set of assumptions, governance will drift. The agent may still complete the task. The organization may not be able to prove that the task followed the governed path.
Form.io's stronger argument is that the same Form JSON and platform layer can define the form, the validation, the generated API surface, the submission shape, permissions, and the runtime agent context.
That starts with deployment control. A [self-hosted Form.io](https://form.io/features/self-hosted-forms-for-enterprise/) environment lets the form and submission layer live inside the customer's own infrastructure boundary.
It also starts with the form contract itself. The [drag-and-drop form builder with APIs](https://form.io/features/drag-and-drop-form-builder-apis/) is not only a visual authoring surface; it produces structured definitions that can become application interfaces.
Governance then depends on behavior, not just fields. [Conditional logic and validation](https://form.io/features/form-conditional-logic-form-validation/) help define what data is acceptable before a workflow or agent acts on it.
Finally, the work has to map to people and roles. [Teams and permissions](https://form.io/features/forms-for-teams/) belong in the same architecture conversation because agent access should inherit the same governance model that controls human access.
## **Where Form.io Fits**
Form.io is not trying to be every layer of AI governance.
That is a strength, not a weakness.
Form.io is strongest when forms are application infrastructure: the schema, user interface, generated API, validation model, submission record, permission boundary, and workflow trigger are connected. When agents enter that environment, the agent should not get a separate shadow contract. It should operate through the same governed layer as the application.
That is the UAG argument.
If your organization only needs an AI policy dashboard, choose an AI governance suite. If it needs action-level runtime policy enforcement across agent frameworks, evaluate a toolkit like Microsoft AGT. If it needs process orchestration, evaluate Camunda, Flowable, or Appian.
If the agent needs governed access to forms, fields, submissions, APIs, validation rules, permissions, and workflow actions inside a customer-controlled deployment, Form.io should be in the conversation.
## **Key Takeaways**
- AI governance platform is too broad unless you name the layer.
- Agentic workflows need governance where agents act, not only where policies are documented.
- Form.io UAG governs the schema/API/form/submission/action layer for production agents.
- Appian, Camunda, and Flowable govern agents through process or case platforms.
- Microsoft AGT governs runtime tool calls and action policies.
- The strongest architecture can combine layers instead of forcing one product to do every job.
- Form.io's strongest claim is not generic AI governance. It is governed application infrastructure for agents working through forms, APIs, validation, submissions, permissions, and actions.
## **FAQ**
### **What Is An AI Governance Platform?**
An AI governance platform helps organizations manage AI risk, policy, accountability, compliance evidence, monitoring, and operational controls. In classic enterprise usage, it often includes AI inventory, use-case approvals, risk classification, policy mapping, audit evidence, and reporting.
For agentic workflows, the term needs more precision. A platform that governs model risk is not automatically the same as a tool that governs agent actions, process state, form submissions, or API access.
### **What Is Agentic Workflow Governance?**
Agentic workflow governance is the set of controls that determines what an AI agent can do inside a business process. It covers tool access, data access, identity, permissions, validation, human review, logging, audit trails, exception handling, and policy enforcement.
The key difference is action. A chatbot that answers a question needs content safety. An agent that updates a submission or triggers a workflow needs execution governance.
### **Is Form.io UAG An AI Governance Platform?**
Form.io UAG is most accurately understood as a runtime governance layer for agents operating through Form.io infrastructure. It is not a general AI GRC dashboard.
UAG gives agents governed access to the Form.io layer: forms, field definitions, validation, submissions, actions, auth, RBAC, and application workflow context. That makes it highly relevant to agentic workflow governance, especially when forms and APIs are part of the customer-controlled application stack.
### **How Is Form.io UAG Different From Microsoft Agent Governance Toolkit?**
Microsoft Agent Governance Toolkit focuses on runtime policy enforcement for agent actions: tool calls, resource access, identity, sandboxing, and auditability around the agent framework.
Form.io UAG focuses on the business surface the agent uses when work involves forms, submissions, validation, APIs, and workflow actions. AGT can help govern the agent's behavior. UAG gives the agent a governed Form.io context to operate through.
### **How Is Form.io UAG Different From Process Engines?**
Process engines such as Camunda and Flowable govern processes and cases. They are strong when the main governance problem is end-to-end orchestration: state, sequence, human tasks, incidents, escalation, and process audit trails.
Form.io governs the form and data infrastructure layer. It is stronger when the main governance problem is schema, validation, submissions, permissions, APIs, and form-driven workflow actions. Many enterprise architectures can use both layers.
### **When Should A Team Use A Classic AI Governance Suite Instead?**
Use a classic AI governance suite when the main problem is enterprise oversight: AI inventory, use-case approvals, risk scoring, regulatory mapping, model monitoring, audit evidence, and board-level accountability.
Use Form.io UAG when the main problem is operational: agents need governed access to forms, submissions, validation, APIs, and workflow actions. The two layers can complement each other.
### **Why Does Schema Matter For Agent Governance?**
Agents need structured context. A schema tells the agent what fields exist, which data is required, what validation rules apply, how submissions are shaped, and which actions are meaningful.
When the same schema drives human forms, APIs, validation, and agent context, the organization reduces drift. The agent is less likely to operate from stale prompt instructions or a parallel tool definition that no longer matches the application.
### **Can Form.io Replace A Process Engine?**
No. Form.io should not be framed as a full process engine replacement.
Form.io is infrastructure for forms, APIs, submissions, validation, permissions, and workflow-related actions. If the organization needs full BPMN or case orchestration, a process engine may still be appropriate. Form.io's role is to make the form and data capture layer governed enough for humans, developers, systems, and agents to use safely.
## **Build Governed Agentic Workflows With Form.io**
If your agents need to work through forms, submissions, APIs, validation rules, permissions, and workflow actions inside your own deployment boundary, start with the governed infrastructure layer.
[Try Form.io for governed agentic workflow infrastructure](/try-formio-for-free/).
[ Share](https://www.facebook.com/sharer/sharer.php?u=https://form.io/ai-governance-platform-agentic-workflow-governance-layers-compared/%2F&src=sdkpreparse)#### Webinars
# [](https://form.io/webinars/agentic-coding-for-the-enterprise/)[Agentic Coding for the Enterprise (LIVE Demo: Form.io Agentic Coding Toolset)](https://form.io/webinars/agentic-coding-for-the-enterprise/)
# Date: Wednesday, August 19, 2026 Time: Central [](https://form.io/webinars/enable-self-service-forms-in-your-application/)[Enable Self-Service Forms in Your Application (LIVE Demo: Form.io’s Enterprise Form Builder Module)](https://form.io/webinars/enable-self-service-forms-in-your-application/)
# Date: Thursday, June 25, 2026 Time: 11:00 pm Central [](https://form.io/webinars/byo-css-the-new-standard-for-white-labeling-form-io/)[BYO-CSS: The New Standard for White Labeling Form.io](https://form.io/webinars/byo-css-the-new-standard-for-white-labeling-form-io/)
Date: Thursday, March 26, 2026 Time: 11:00 am Central #### Recent Posts
# [](https://form.io/web-form-builder-apis-self-hosted-control/)[Web Form Builder: When Online Forms Need APIs, Workflows, and Self-Hosted Control](https://form.io/web-form-builder-apis-self-hosted-control/)
# August 5, 2026 [](https://form.io/e-signature-software-self-hosted-form-workflows/)[E Signature Software for Self-Hosted Form Workflows: DocuSign Alternatives for Enterprise Control](https://form.io/e-signature-software-self-hosted-form-workflows/)
# July 21, 2026 [](https://form.io/json-schema-validator-tools-production-apps/)[JSON Schema Validator Tools for Production Apps](https://form.io/json-schema-validator-tools-production-apps/)
# July 20, 2026 [](https://form.io/embedded-forms-b2b-saas-white-label-comparison/)[Embedded Forms for B2B SaaS: The White-Label Form Builder Comparison](https://form.io/embedded-forms-b2b-saas-white-label-comparison/)
# July 17, 2026 [](https://form.io/claims-management-software-insurance-form-builders/)[Claims Management Software Starts With The Forms That Feed It](https://form.io/claims-management-software-insurance-form-builders/)
# July 16, 2026 [](https://form.io/kyc-onboarding-software-financial-services-form-platforms/)[KYC Onboarding Software for Financial Services: Forms, APIs, and Audit-Ready Intake](https://form.io/kyc-onboarding-software-financial-services-form-platforms/)
July 15, 2026 #### Recent Case Studies
# [](https://form.io/case-studies/from-60-pages-to-a-single-click/)[From 60 Pages to a Single Click: How Form.io Powered a Government Agency’s Digitization](https://form.io/case-studies/from-60-pages-to-a-single-click/)
# June 15, 2026 [](https://form.io/case-studies/from-six-week-release-cycles-to-same-day-form-changes-patagonia-health/)[From Six-Week Release Cycles To Same-Day Form Changes – Patagonia Health](https://form.io/case-studies/from-six-week-release-cycles-to-same-day-form-changes-patagonia-health/)
# June 15, 2026 [](https://form.io/case-studies/accelerated-development-time-line-by-two-years/)[Accelerated Development Timeline By Two Years](https://form.io/case-studies/accelerated-development-time-line-by-two-years/)
# May 7, 2025 [](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)[The Digital Transformation Of Supporting New Services For The German Public Sector—On Repeat](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)
December 2, 2024 #### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# Self Hosted Form Builder: Enterprise Forms and APIs Deployed in Your Environment
*Published:* 2026-07-14
*Author:* Veronika Druck
*URL:* https://form.io/self-hosted-form-builder-enterprise-forms-apis-deployed-in-your-environment/
*Description:* A technical buyer guide to self-hosted enterprise form infrastructure, explaining how Form.io deploys forms, APIs, submissions, permissions, and workflow controls inside the customer's environment.
[  ](https://form.io/audit-trail-software-enterprise-form-builders-with-native-sdlc/)Audit trail software sounds simple until the record being audited is not just a file, invoice, login, or database row.
Enterprise forms change. Submitted data changes. Validation rules change. Permissions change. Workflow actions fire. APIs read and update the same records that users see in the interface.
For regulated form workflows, the question is not only "Do we have logs?" It is "Can we prove what happened, who did it, what version of the form governed it, and whether the workflow moved through the right control path?"
## **What audit trail software has to prove**
Audit trail software creates a chronological record of activity inside a system.
At minimum, that record should help answer:
- Who performed the action?
- What changed?
- When did it happen?
- Which object, record, form, user, or system was affected?
- What context explains the change?
- Can the record be reviewed later without reconstructing it from guesswork?
That matters because audit trails are not only for after-the-fact compliance reviews. They are also useful for security monitoring, troubleshooting, workflow accountability, and incident investigation.
NIST's log management guidance treats logging as part of a broader cybersecurity evidence system. The draft [NIST SP 800-92 Rev. 1 Cybersecurity Log Management Planning Guide](https://csrc.nist.gov/pubs/sp/800/92/r1/ipd) treats logging as part of a broader cybersecurity evidence system.
Regulated systems make the point even more concrete. [21 CFR 11.10](https://www.law.cornell.edu/cfr/text/21/11.10) requires procedures and controls for closed systems that include secure, computer-generated, time-stamped audit trails for actions that create, modify, or delete electronic records, and it says record changes must not obscure previously recorded information. HIPAA's technical safeguards similarly include [audit controls](https://www.law.cornell.edu/cfr/text/45/164.312) for information systems that contain or use electronic protected health information.
That is the right starting point. Logs are evidence.
But enterprise form workflows need a more specific kind of evidence.
If a claims intake form changes, a patient referral submission is corrected, a public-sector application moves from draft to review, or an embedded customer form is updated through an API, a generic event log may not be enough. The system needs to preserve the relationship between the action and the form infrastructure that governed it.
## **Why enterprise forms need a different audit model**
A form in an enterprise application is not just a page.
It can be:
- a user interface
- a JSON schema
- a validation contract
- a submission model
- a generated API
- a workflow trigger
- a permission boundary
- a document-generation source
- a long-term record
That is why auditability gets harder when forms become application infrastructure.
A simple audit log might show that a user updated a record at 2:14 PM. That is useful, but it does not answer every question an auditor, compliance team, or engineering lead may ask later.
For example:
- Which form version was active when the user submitted the record?
- Did the form have the same required fields then that it has now?
- Was the submitted value changed after capture?
- Was there a documented reason for the change?
- Did a webhook, email, approval action, or downstream integration fire?
- Did the change happen in development, staging, or production?
- Did the API update follow the same permission rules as the portal update?
Those are form-infrastructure questions, not just logging questions.
IBM's 2025 [Cost of a Data Breach Report](https://www.ibm.com/reports/data-breach) puts the global average breach cost at $4.4 million and reports that 63% of organizations lacked AI governance policies. That statistic is not form-specific, but it gives the right scale for the decision. When sensitive data workflows are hard to trace, the risk is not cosmetic.
For enterprise forms, the audit model has to cover both sides of the system: the form definition and the submitted data.
## **The four audit layers enterprise form builders should support**
Most form tools can tell you that a submission exists.
Enterprise form infrastructure needs to tell a deeper story.
### **1. System activity and access logs**
The first layer is the system-level audit log.
This is the record of access, authentication, API requests, data reads, data writes, and other platform activity. It answers questions like:
- Who viewed this submission?
- Who authenticated?
- Which API request changed the record?
- Which project, form, or user was involved?
- Did a request fail?
- Can related events be correlated?
Form.io's [audit logging documentation](https://help.form.io/dev/audit-logging) describes a system-level audit log format with date, event, UUID, project ID, session ID, user ID, and event-specific context. The docs also state that audit logs output to standard out for the Docker container and can be routed into a log aggregation system.
Another note: high-volume system logs should not necessarily store complete submission payloads inside every event. Sensitive form values may need a different audit mechanism than API access events.
The right audit design separates broad activity logging from field-level revision history, then lets teams correlate the two when they need to investigate.
### **2. Form revisions**
The second layer is form revision history.
Enterprise forms change over time. Teams add fields, remove fields, rename fields, update validation rules, change conditional logic, revise consent text, and adjust workflow requirements.
If the form changes after a record is submitted, the system still needs to explain what the form looked like when the record was captured.
Form.io's [Form Revisions documentation](https://help.form.io/userguide/forms/form-revisions) is built for that problem. Form Revisions let teams preserve form versions as forms evolve and can display submission data in the form revision that captured it. The revision interface also exposes who made a revision, when the revision was made, the revision number, and revision notes.
That distinction is central to auditability.
If an auditor reviews a historical submission, the question is not only "What data is in the record now?" It is also "What fields, labels, rules, and structure governed the user when the record was created?"
Without form revision history, teams often have to reconstruct that context from release notes, screenshots, old code, or database backups. That is fragile.
### **3. Submission revisions**
The third layer is submission revision history.
This is the field-level history of changes to submitted data after initial capture.
A submitted form might be corrected by a staff member. A patient record might need an updated value. A claims workflow might need a revised amount. A government service application might need a supporting detail added after review.
In those cases, the system needs to preserve the previous state, the new state, the user who made the change, the time of the change, and any revision note explaining why the change happened.
Form.io's [Submissions documentation](https://help.form.io/userguide/submissions) describes Submission Revisions as an audit logging capability that tracks who updated a submission, when the change was made, and notes associated with the update. The documentation also says the PDF change log can include the revision ID, updating user, date and time, revision note, and list of revision changes.
That is the difference between editing a record and governing a record.
An edit changes the current value. A revision trail preserves the accountable history behind that value.
### **4. Stage, action, and deployment history**
The fourth layer is the SDLC layer.
For enterprise form teams, auditability is not limited to runtime activity. It also includes how form definitions, resources, roles, and actions move through development, staging, and production.
Form.io's [Stages documentation](https://help.form.io/userguide/projects/stages) describes stages as a way to isolate project forms and resources for form management between different environments. The same documentation frames a typical enterprise workflow around Live, Authoring, QA/Test, and Development stages.
That matters because regulated teams often need controlled promotion.
They need a place to build and test form changes before production. They need to know which form version moved forward. They need to avoid ad hoc edits that change production behavior without review. This should not be inflated into a claim that Form.io replaces a full CI/CD or release-management system for all application code. The narrower point is still valuable: form configuration has its own lifecycle, and enterprise teams need a controlled way to manage it.
Audit trail software that ignores the lifecycle layer misses a major part of the form governance problem.
## **A practical comparison framework**
The right audit trail software depends on what kind of system you are auditing.
**Category****Best fit****What it proves****Where it can fall short for enterprise forms**Generic audit log toolingBroad system activity, application events, operational monitoringWho did what, when, and where across systemsUsually does not understand form schema versions or submission-level change historyCompliance audit management toolsPolicy controls, audit programs, evidence management, compliance workflowsWhether controls exist and evidence was collectedOften manages audit process, not the runtime form record itselfAccounting or finance audit trail toolsFinancial transactions, invoices, approvals, accounting changesTransaction history and financial accountabilityUsually narrow to finance workflowsBasic form builders with logsSimple submissions, admin edits, response exportsBasic submission history and account activityMay not preserve form schema history, API-level activity, or stage promotionCustom-built audit trailHighly specific internal applicationsWhatever the team designs and maintainsExpensive to build, test, secure, document, and keep consistent across formsForm infrastructure with native audit controlsRegulated form workflows, embedded forms, generated APIs, long-lived submissionsSystem activity, form revisions, submission revisions, permissions, actions, and stage movementRequires technical ownership and a clear governance modelThe key is fit.
If your team only needs a basic activity log for a contact form, enterprise form infrastructure is probably too much. If your team is managing high-value workflows where form definitions and submitted data both matter, the audit model needs to be native to the form platform.
## **Where Form.io fits**
Form.io is strongest when the form is part of the application infrastructure.
That usually means a team needs some mix of [self-hosted form deployment](/features/self-hosted-forms-for-enterprise/), embedded forms, generated APIs, permissions, workflow actions, form revisions, submission revisions, audit logging, and environment promotion.
The reason is architectural.
Form.io forms and resources are JSON-driven definitions that can render user interfaces, generate APIs, validate submissions, store submitted data, and participate in roles, permissions, actions, stages, and revisions.
That makes auditability part of the same system that owns the form workflow.
[The Security Module](/features/secure-forms-compliance-readiness/) bundles advanced audit logging, action logs, form revisions, submission revision logs, submission collections, and container security scanning. The [complete audit trail feature](/features/log-forms-complete-audit-trail/) separates system-wide audit logs from field-level submission revisions, which is the right separation for high-volume enterprise workflows. The [Form Revisions feature](/features/form-revisions-form-json-schema/) preserves form JSON schema versions so historical submissions can remain explainable as forms evolve.
Form.io also matters when APIs are part of the record. A form workflow may be updated through the portal, an embedded application, or a generated API. The buyer should not have to accept one audit posture for the UI and another for API-driven operations.
That is why generated APIs are relevant to audit trail software. Form.io's [form API model](/features/form-api/) lets teams treat forms and resources as API-connected infrastructure, not isolated web pages. Permissions, submissions, and actions then sit closer to the form data model.
This is also where customer proof matters. [G2's Form.io review page](https://www.g2.com/products/form-io/reviews) describes the platform as deployable into on-premise or private cloud environments, giving customers control of submission data. One enterprise reviewer summarized the practical product experience this way: "Form.io is an intuitive, developer-friendly framework that provides excellent data management." That is not an audit claim by itself. It is buyer proof for the control-and-customization posture that makes audit-heavy form infrastructure worth evaluating.
## **When simple audit logging is enough**
Not every workflow needs all of this.
Simple audit logging may be enough when:
- The form is short-lived.
- Submitted data is low risk.
- Responses are rarely edited after capture.
- The form schema rarely changes.
- The form is not embedded into a regulated application.
- There is no need for DEV/STAGE/PROD promotion.
- Exports are enough for downstream systems.
- The audit question is limited to account activity or submission timestamps.
In those cases, a lighter form builder, basic form backend, or general application log may be a better fit.
The mistake is keeping that model after the workflow becomes infrastructure.
Once forms drive eligibility, claims, intake, onboarding, financial review, patient workflows, public-sector services, insurance applications, or internal approvals, the audit trail has to explain more than "a record changed."
It has to explain the governed context around the change.
## **Evaluation checklist for audit trail software in form workflows**
Use these questions before choosing a form platform for an audit-heavy workflow.
### **Does the platform track system-level activity?**
Look for access events, authentication events, API requests, data reads, data writes, request correlation, and log export options.
### **Does it preserve form schema versions?**
If a field, validation rule, label, or conditional path changes, the platform should preserve enough form history to explain historical submissions.
### **Does it preserve submitted-data history?**
Submission revisions should show who changed a value, when it changed, what changed, and why.
### **Can historical submissions render against the original form version?**
This matters when auditors, legal teams, or operations teams need to understand what a user actually saw at capture time.
### **Are workflow actions included in the governance model?**
Actions such as emails, webhooks, approvals, PDF generation, and save-to-resource operations can affect the record. They should not be invisible.
### **Can forms move through controlled stages?**
Enterprise teams need a way to test, version, and promote forms, resources, roles, and actions without treating production as the editing surface.
### **Do permissions apply close to the form and submission model?**
[Form permissions](/features/form-permissions/) matter because different people may be allowed to create, read, update, delete, approve, or export different records.
### **Can the platform run inside the required deployment boundary?**
Self-hosting does not automatically make a system compliant. It does let the customer place the form platform inside the environment, monitoring, identity, logging, and operational controls the organization already governs.
### **Are forms still usable for builders and developers?**
Audit controls only help if the team can still build and maintain the workflow. A usable [form builder](/features/form-builder/) and a clear [JSON-powered form model](/features/json-powered-forms/) reduce the temptation to route around governance.
## **Key takeaways**
- Audit trail software is not only a logging feature when forms become application infrastructure.
- Enterprise form workflows need evidence across system activity, form revisions, submission revisions, workflow actions, permissions, and stage promotion.
- Generic logs can show that something happened. Form infrastructure should show what version of the form governed the record when it happened.
- Form.io fits best when the form schema, generated API, submitted data, and governance controls need to stay connected.
- The right buyer is not looking for the lightest form tool. They are looking for a form platform that can defend the record later.
## **FAQ**
### **What is audit trail software?**
Audit trail software records system activity in chronological order so teams can review who performed an action, what changed, when it happened, and which record or system was affected.
### **Why do enterprise forms need audit trails?**
Enterprise forms often collect data that drives decisions, approvals, compliance records, customer onboarding, claims, patient workflows, government services, or financial review. If the record changes later, the organization needs evidence of what happened.
### **What is the difference between an audit log and a submission revision?**
An audit log records system-level activity such as access, authentication, API requests, and data modification events. A submission revision preserves field-level history for a specific submitted record.
### **What is the difference between form revisions and submission revisions?**
Form revisions track changes to the form schema: fields, validation rules, conditional logic, layout, and related form structure. Submission revisions track changes to submitted data after capture.
### **Why does form versioning matter for audit trails?**
Form versioning helps explain historical records. If a submission was captured under an older form version, the team may need to review the exact schema, fields, labels, and validation rules that governed that submission.
### **Does self-hosting make audit trail software compliant?**
No. Self-hosting gives the organization more control over deployment, data, logs, identity, monitoring, and infrastructure. Compliance still depends on configuration, policy, controls, documentation, and review.
### **Should audit trail software store every field value in every log?**
Not always. High-volume system logs can become expensive and sensitive if they store full payloads in every event. A better model often separates system audit logs from field-level submission revisions.
### **What should regulated teams look for in form audit trails?**
They should look for system audit logs, form revisions, submission revisions, permissions, workflow/action evidence, stage promotion, exportable evidence, and deployment control.
### **Can generic log management replace native form revision history?**
Generic log management can help centralize and review system events, but it usually does not understand form schema versions, submission rendering, or field-level form data history unless the application sends that context deliberately.
### **When is Form.io a good fit for audit-heavy forms?**
Form.io is a good fit when forms are part of a larger application workflow and the team needs [form workflows](/features/form-workflows/), generated APIs, permissions, revisions, submission history, and customer-controlled deployment.
### **When is Form.io probably too much?**
Form.io may be more platform than needed for a simple contact form, survey, or lead-capture page where the data is low risk and the audit requirement is limited to basic timestamps or account activity.
## **Build audit-ready form infrastructure with Form.io**
# Web Form Builder: When Online Forms Need APIs, Workflows, and Self-Hosted Control
[  ](https://form.io/web-form-builder-apis-self-hosted-control/)A web form builder sounds like a simple category until the form becomes part of a real application. A contact form, signup form, or feedback survey can live in a lightweight tool. A regulated intake process, embedded customer workflow, or API-connected business process needs more than fields on a page.
That is where the buying question changes.
## **What a Web Form Builder Should Do**
A web form builder is software for creating forms users can complete in a browser. At the basic level, it should let a team create fields, set required answers, publish a form, collect submissions, and send the data somewhere useful.
For many teams, that is enough.
Zapier's long-running online form builder list shows how the broad market is usually framed: quick form creation, automation, advanced logic, conversational form experiences, AI-assisted building, Excel sync, approval flows, and reporting options ([Zapier](https://zapier.com/blog/best-online-form-builder-software/)). That is the default expectation buyers bring to the phrase.
The problem is that "web form builder" covers several different jobs:
- a marketing team collecting leads
- an operations team routing internal requests
- a product team embedding forms inside a SaaS application
- a healthcare, insurance, finance, or government team collecting sensitive data
- a development team using forms as part of an API-backed workflow
Those jobs should not be evaluated with the same checklist.
If the form is only a standalone page, the most important questions are speed, templates, design, notifications, and basic integrations. If the form is part of application infrastructure, the questions become more serious: who owns the schema, where does submission data live, what APIs exist, how validation runs, what happens after submit, and whether the platform can operate inside the customer's environment.
## **When a Simple Web Form Builder Is Enough**
A simple web form builder is a good fit when the form is low-risk, isolated, and easy to replace.
Use a lightweight tool when:
- the form collects basic marketing or event information
- submissions can live in the vendor's hosted system
- exporting to a spreadsheet is acceptable
- the workflow after submission is simple
- there are no unusual data residency or deployment requirements
- the form is not deeply embedded in a product experience
- developers do not need to treat the form as an API-backed component
In that world, the best tool is often the fastest tool your team will actually use. A simple builder can be the right decision for a campaign, a workshop signup, a small survey, or a basic internal request.
The mistake is keeping that same mental model after the requirements change.
## **Where Web Form Builders Start To Break Down**
Web forms become harder when the submission is not the end of the process.
A user submits an intake form. Then the data has to create a case, trigger a review, update a CRM, route to a queue, generate a PDF, notify a downstream system, enforce role-based access, or become part of a customer-facing application.
At that point, the form has a second job. It is no longer just collecting answers. It is becoming the front door to a process.
The breakdown usually shows up in five places.
### **The Data Model Lives Somewhere Else**
Many web form builders make it easy to create fields, but the real application data model lives outside the form tool. That creates drift. A field is required in the form but optional in the backend. A dropdown changes in the builder but not in the API. A validation rule exists in the browser but not server-side.
This is small until the form becomes important.
Then every disconnected rule becomes a place where bad data can enter the system.
### **Integrations Become Workflow Logic**
Basic integrations are helpful. They send a notification, create a spreadsheet row, add a CRM contact, or post to a collaboration tool.
But integration is not the same as workflow ownership.
Enterprise forms often need conditional routing, retries, identity context, external IDs, error handling, and clean handoff to other systems. Form.io's webhook documentation, for example, treats a submission as a payload that can call an external API, map response IDs back to the submission, and optionally wait for the webhook response before continuing actions ([Form.io webhook actions docs](https://help.form.io/form-building/actions/webhook-actions)).
That is a different requirement than "send this form to a spreadsheet."
### **Security And Compliance Become Architecture Questions**
The more sensitive the data, the less acceptable it is to treat the form builder as a detached SaaS box.
IBM's 2025 Cost of a Data Breach Report puts the global average breach cost at USD 4.4 million ([IBM](https://www.ibm.com/reports/data-breach)). That statistic should not be used to scare every team away from hosted tools. It should remind buyers that data capture is part of the security boundary.
For sensitive forms, the evaluation should include:
- where submissions are stored
- who administers the environment
- how access is controlled
- how data moves between systems
- how logs, evidence, and audit needs are handled
- whether the form platform can live inside the organization's deployment model
Self-hosting does not automatically make a system compliant. It gives the organization more control over the environment where compliance controls are implemented and reviewed.
### **Product Teams Need Embedding, Not Just Publishing**
Publishing a hosted form is not the same as embedding a form builder into a product.
If a B2B SaaS team wants customers to create or manage their own forms inside the application, the builder has to respect the product's authentication, permissions, tenant boundaries, styling, and data model. That is closer to an embedded product capability than a public web form.
This is why Form.io's [Enterprise Form Builder Module](https://form.io/features/enterprise-form-builder-module/) matters for platform teams. The point is not only that a user can drag fields onto a canvas. The point is that a company can provide a white-labeled, pre-wired form-building experience inside its own application.
### **Developers Need A Stable Contract**
Developers can work around almost anything once. The cost shows up when every new form requires custom backend glue.
A stronger web form builder for application teams should create a stable contract between the form, the submission record, the API, validation, permissions, and downstream systems.
Form.io's own project documentation says that when a new form is created, a REST API is automatically generated to serve as the backend for the form and for other systems that need to create submissions ([Form.io project docs](https://help.form.io/admin/projects/creating-a-project)). That is the key architectural distinction: the form is not only a UI artifact. It is part of the API surface.
## **A Web Form Builder Evaluation Checklist**
Before choosing a web form builder, separate the easy questions from the questions that determine long-term fit.
Evaluation AreaLightweight Form NeedInfrastructure-Grade Form NeedBuilderDrag-and-drop fields, templates, brandingConfigurable builder, reusable schemas, controlled componentsDataHosted submissions and exportsStructured submission records with API accessWorkflowNotifications and simple integrationsWebhooks, Actions, retries, external IDs, routingValidationClient-side rules and required fieldsSchema-linked validation across UI and server pathsEmbeddingPublic link or iframeNative application embedding and white-label controlDeploymentVendor-hosted SaaSHosted, private cloud, on-premises, or local deployment optionsGovernanceAdmin settingsRoles, permissions, stages, evidence, and environment controlFitCampaigns, surveys, simple intakeProduct workflows, regulated intake, internal systems, multi-tenant SaaSThis checklist prevents a common buying mistake: choosing the easiest form tool for the first version, then rebuilding the entire intake layer once the forms become operationally important.
## **Why APIs Change The Category**
APIs change a web form builder from a page-building tool into an application component.
Without APIs, the form is mostly a destination. Users go there, submit data, and the team exports or forwards the result.
With APIs, the form can become part of the system:
- applications can create and read submissions
- forms can populate fields from external data
- downstream systems can consume structured payloads
- teams can build reporting, review, and workflow layers on top of submission records
- developers can integrate forms into products without treating each one as a one-off project
Form.io's [data integration tools](https://form.io/features/data-integration-tools-for-enterprise-forms/) positioning makes this point directly: forms, resources, submissions, and projects are accessible through REST APIs. The practical value is not just "there is an API." It is that the form builder, schema, submission data, and integration surface are part of the same model.
That matters when teams are building internal tools, partner portals, insurance workflows, healthcare intake, public-sector services, or SaaS onboarding flows.
The user sees a web form. The architecture sees a contract.
## **Why Deployment And Data Control Matter**
Deployment is one of the clearest dividing lines between a simple web form builder and enterprise form infrastructure.
If the form is low-risk, vendor-hosted SaaS is usually fine. If the form handles regulated data, internal process data, customer application data, or data that has to move through controlled systems, deployment becomes part of the buying decision.
Form.io's deployment documentation says the platform can be installed in cloud environments, on-premise data centers, or local machines, and that enterprise deployments can use multi-environment architecture across private cloud or on-prem environments ([Form.io deployment overview](https://help.form.io/deploy/deployment-overview)). Its on-premises deployment documentation frames on-prem as relevant when infrastructure, compliance, or data-security requirements call for that model ([Form.io on-premises deployment docs](https://help.form.io/deploy/on-premises-deployment)).
This does not make Form.io the right fit for every form.
It makes Form.io relevant when the form layer has to live where the rest of the application lives.
For teams with strict environment rules, that is often the real requirement hiding underneath the phrase "web form builder." They are not only asking for a form canvas. They are asking whether the form system can respect their data boundary, deployment model, access controls, and integration paths.
## **Where Form.io Fits**
Form.io is a stronger fit when the form is part of an application, not just a standalone collection page.
The core difference is that Form.io combines a [drag-and-drop form builder with APIs](https://form.io/features/drag-and-drop-form-builder-apis/). Teams can design forms visually while keeping the underlying structure available as JSON and exposed through generated REST APIs.
That combination is useful when:
- developers need forms embedded in a product
- business users need controlled form authoring
- submissions need to be available through APIs
- workflows need webhooks or server-side actions
- the organization needs self-hosted or on-premises deployment
- forms need to share a governance model with the surrounding application
Form.io is not the best answer when a team only needs a quick public survey or a simple contact form. That buyer should choose the fastest lightweight tool that fits the job.
But when a web form builder has to support real application infrastructure, the decision changes. The value is not only the builder UI. It is the connection between form schema, submission data, generated APIs, deployment control, and workflow actions.
Customer language points to the same distinction. A Trustpilot reviewer described Form.io as useful "for integration and standalone" work ([Trustpilot](https://www.trustpilot.com/review/form.io)). A Form.io case study customer put the infrastructure burden more bluntly: Form.io "cleans up all the dirty work" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)).
That is the real category line.
A basic web form builder helps a team make a form. Form.io is for teams that need the form to become a governed part of the application.
## **Key Takeaways**
- A web form builder can mean anything from a simple contact form to an embedded application workflow.
- Lightweight tools are a good fit when forms are low-risk, standalone, and easy to replace.
- Enterprise teams should evaluate APIs, validation, submissions, workflow actions, permissions, and deployment control.
- Form.io fits when the form layer needs to operate as controlled application infrastructure, not just a hosted form page.
- Self-hosting is not a compliance shortcut; it is a control model for teams that need to own the environment.
## **FAQ**
### **What Is A Web Form Builder?**
A web form builder is software for creating forms that users complete in a browser. Basic builders focus on fields, templates, publishing, notifications, and exports. More advanced builders support APIs, workflows, permissions, embedding, and controlled deployment.
### **What Is The Difference Between A Web Form Builder And An Online Form Builder?**
The terms often overlap. "Online form builder" usually points to hosted SaaS tools for creating and publishing forms quickly. "Web form builder" can mean the same thing, but it is also used by product and development teams looking for embeddable form-building inside a web application.
### **When Is A Basic Form Builder Enough?**
A basic form builder is enough when the form is low-risk, standalone, and does not need deep integration with internal systems. Examples include event registration, simple lead capture, small surveys, and basic internal requests.
### **When Does A Web Form Builder Need APIs?**
A web form builder needs APIs when other systems must create, read, update, route, or report on submissions. APIs matter when forms are part of a product, portal, approval workflow, regulated intake process, or internal system of record.
### **Why Does Form Schema Matter?**
The schema defines the form's structure and behavior. In a schema-driven model, the same definition can support rendering, validation, submissions, APIs, workflow actions, and governance. That reduces drift between what the user sees and what the backend expects.
### **Can A Web Form Builder Be Self-Hosted?**
Some web form builders are hosted-only. Form.io supports self-hosted deployment models, including cloud, on-premises, and local environments according to its deployment documentation. That matters when the organization needs control over hosting, network boundaries, data storage, and operational review.
### **Is Self-Hosting The Same As Compliance?**
No. Self-hosting gives the customer more control over the environment, but compliance still depends on configuration, policies, controls, monitoring, documentation, and the broader system boundary. The value is control, not a shortcut around responsibility.
### **Why Would A SaaS Product Need An Embedded Form Builder?**
A SaaS product may need customers or internal teams to create forms inside the product itself. In that case, the builder has to respect tenant boundaries, authentication, permissions, styling, and data storage. A public form link is not enough.
### **How Is Form.io Different From A Simple Form Tool?**
Form.io is built for teams that need forms, submission data, generated APIs, workflow actions, and deployment control together. It can still provide a drag-and-drop builder, but the stronger reason to use it is when forms need to operate inside application infrastructure.
## **Build Web Forms That Fit Your Application Architecture**
# E Signature Software for Self-Hosted Form Workflows: DocuSign Alternatives for Enterprise Control
[  ](https://form.io/e-signature-software-self-hosted-form-workflows/)E signature software is usually evaluated as a document workflow tool: send a PDF, collect a signature, store an audit trail, and move on.
That is enough for many contracts. It is not enough when the signature is attached to regulated intake, eligibility data, consent records, financial applications, healthcare workflows, or other form submissions that must stay inside your application boundary.
The better question is not only, "Can this document be signed?" It is, "Can we defend the signed record later, with the data, schema, context, and audit trail intact?"
## **What E Signature Software Usually Solves**
Most e signature software helps teams replace wet signatures with an electronic signing process. The standard workflow is familiar: upload a document, place signature fields, route it to signers, authenticate the signer, collect consent, and retain a completed envelope.
That category is large because the paper problem is large. [Grand View Research estimated](https://www.grandviewresearch.com/industry-analysis/digital-signature-market-report) the global digital signature market at USD 6.9 billion in 2025 and projected a 43.9% CAGR from 2026 to 2033.
But market size does not tell you which architecture fits your use case.
Standalone signing platforms are strongest when the signed artifact is the document itself: contracts, sales agreements, HR forms, procurement packets, vendor agreements, and legal paperwork. In those cases, the system of record is often the completed document package.
Form-driven applications are different. The signed evidence may need to stay attached to a submission record, user identity, form version, field values, workflow state, API transaction, and downstream system update.
That is where a normal e-signature checklist starts to miss the real buyer risk.
## **Why DocuSign Alternatives Become Relevant**
DocuSign is the name many buyers know first. Adobe, Dropbox Sign, PandaDoc, Zoho Sign, OneSpan, and other tools also belong in the traditional e-signature conversation.
Those tools can be the right choice when your team mainly needs a document-signing workflow. The mistake is assuming that the best document-signing platform is automatically the best signing architecture for application data.
Teams start looking for DocuSign alternatives when one or more constraints appears:
- signature data must stay inside a private cloud, VPC, on-premise, or controlled deployment boundary
- the signed record begins as structured form data, not a static PDF
- signer consent needs to connect to the exact fields and submission context that were signed
- APIs, webhooks, roles, permissions, and audit history matter as much as the visual signature
- pricing or operations become hard to forecast when signatures scale across many workflows
For these teams, the word "alternative" does not simply mean cheaper. It means architecturally different.
## **The Enterprise Evaluation Criteria**
Before choosing e signature software, separate legal acceptance from operational evidence.
The U.S. [ESIGN Act](https://uscode.house.gov/view.xhtml?edition=prelim&path=%2Fprelim%40title15%2Fchapter96) says electronic signatures and records generally cannot be denied legal effect solely because they are electronic. It also points to record retention: electronic records must remain accurate, accessible, and reproducible for later reference.
That retention point matters. A signature event is only as useful as the record your team can reproduce when someone asks what was signed, by whom, under which form version, with which field values, and under which business process.
Evaluate each platform across six criteria.
**Criterion****Why it matters**Deployment controlDetermines where sensitive data, signature proof, and operational evidence live.Record modelShows whether the signed artifact is a PDF envelope, a submission record, or both.Audit trailCaptures the evidence needed to defend the transaction later.API accessDetermines whether signatures can participate in application workflows.Identity and access controlsConnects signing to the right user, role, tenant, or workflow boundary.Pricing modelDetermines whether cost scales predictably across high-volume workflows.The wrong platform can still collect a signature. The problem appears later, when the team needs to prove what the signature means inside the larger system.
## **Where Self-Hosted Form Workflows Change The Question**
Self-hosted form workflows change the center of gravity.
Instead of asking, "Which e-signature vendor should host this envelope?" the team asks, "How do we keep the signed record inside the same infrastructure that owns the form, data, APIs, permissions, and audit history?"
That shift matters for regulated teams, embedded SaaS products, government contractors, healthcare platforms, insurance workflows, financial services onboarding, and internal enterprise portals.
The signature is not a decorative mark. It is a control point in the data lifecycle.
NIST's [digital signature project](https://csrc.nist.gov/projects/digital-signatures) frames digital signatures around generation, verification, and data protection. That distinction is useful for buyers: a visible signature image is not the same thing as verifiable proof that the protected data and context have not changed.
In a form workflow, the strongest signature system should answer questions like:
- Which form version captured the data?
- Which fields were protected by the signature?
- Did the data change after signing?
- Can the application verify the signature through an API?
- Does the signed record remain inside the customer's environment?
- Can the team reproduce the record without depending on a third-party envelope as the only source of truth?
Those are infrastructure questions, not just signing questions.
## **How Form.io E-Sign+ Fits**
[Form.io E-Sign+](/features/cryptographic-e-signatures-for-form-data/) is built for a narrower, more controlled version of the e-signature problem: cryptographically secure signatures associated with Form.io submission data inside the customer's own environment.
That is a different posture than a standalone document-signing workflow.
With Form.io, the [form schema and submission data](/form-json-schema-vs-submission/), generated APIs, permissions, workflow actions, and deployment boundary are already part of the application infrastructure. E-Sign+ extends that infrastructure by letting teams verify signed submission data and context rather than treating the signature as only a PDF-layer event.
The [product documentation](https://help.form.io/dev/integrations/e-sign%2B) describes E-Sign+ as tied to submission data, usable through native submission IDs, and decoupled from PDFs. It can protect selected fields, all form data, and/or submission properties, depending on configuration.
That makes Form.io a strong fit when the signature needs to travel with application data.
Form.io's broader customer proof reinforces the infrastructure value. One customer quote on [Form.io's homepage](https://form.io/) says, "Speed to market using Form.io worked fantastically well," because the team did not have to spend most of its time building its own solution. Another proof point describes cutting data-processing workload by 50%.
Those quotes are not E-Sign+ specific. They do show the larger pattern: Form.io is strongest when teams need to stop rebuilding form, data, API, and workflow plumbing from scratch.
## **E Signature Software Comparison**
**Best fit****Typical tools****Watch the tradeoff**Standard document signingDocuSign, Adobe Acrobat Sign, Dropbox Sign, PandaDoc, Zoho SignStrong for envelopes and documents, but not always ideal when signed evidence must remain attached to application-owned submission data.Developer signing APIsAPI-first signing platformsFlexible for document workflows, but your team still owns the surrounding form schema, data model, and governance path.Self-hosted form signing infrastructureForm.io E-Sign+Strong fit when forms, submissions, APIs, permissions, and signature verification need to stay in the customer's controlled environment.The point is not that every team should leave document-signing platforms. Many should not.
The point is that e signature software has to match the record you are actually signing.
If the record is a contract document, a document-signing tool may be enough. If the record is a governed application submission, the signature belongs closer to the form infrastructure.
## **Key Takeaways**
- E signature software is a broad category, but enterprise form workflows need more than a signed PDF.
- Legal validity is only one part of the evaluation. Record retention, reproducibility, and context matter.
- DocuSign alternatives become relevant when teams need deployment control, API access, data ownership, or application-level signature proof.
- Form.io E-Sign+ fits teams that need cryptographic signature verification tied to submission data inside their own environment.
- The stronger question is not "Which tool signs documents fastest?" It is "Which system protects the signed record your application actually depends on?"
## **FAQ**
### **What Is E Signature Software?**
E signature software lets people sign electronic records or documents without printing and scanning paper. In business workflows, it usually includes signer routing, authentication, consent capture, audit history, completed document storage, and API or integration options.
### **Is E Signature Software Legally Binding?**
Electronic signatures can be legally valid in many contexts, including under the U.S. ESIGN Act and [EU eIDAS rules](https://ec.europa.eu/digital-building-blocks/sites/spaces/DIGITAL/pages/467109069/What%2Bis%2BeSignature). Buyers should still review the specific transaction type, jurisdiction, identity process, consent language, retention rules, and audit evidence with legal counsel.
### **What Is The Best DocuSign Alternative?**
The best DocuSign alternative depends on the job. If the job is standard document signing, a standalone signing platform may fit. If the job is signing structured form submissions inside a controlled application, Form.io E-Sign+ is worth evaluating because the signature proof stays closer to the form data and API workflow.
### **When Should A Team Choose Self-Hosted E Signature Software?**
A team should consider self-hosted signing infrastructure when sensitive submission data, regulatory obligations, customer architecture, data residency, or private deployment requirements make third-party-hosted signing workflows difficult to justify.
### **How Is Form.io E-Sign+ Different From A PDF Signature Tool?**
Form.io E-Sign+ is designed around submission-linked signature proof. PDFs can still be part of a workflow, but the stronger distinction is that E-Sign+ can verify signed form data and context inside the customer's own [self-hosted Form.io environment](/enterprise-self-hosting/).
### **Does Form.io Replace DocuSign?**
Not for every use case. DocuSign is a strong document-signing platform. Form.io is a stronger fit when signatures are part of a governed form workflow, embedded application, or self-hosted data pipeline where submission context matters.
### **What Should Enterprises Look For In E Signature Software?**
Enterprises should evaluate deployment control, signer identity, audit trail quality, API access, retention and reproducibility, [configuration-based pricing](/configuration-based-pricing/), integration fit, and whether the signed record is a document envelope or application data.
### **Can E Signature Software Work With APIs?**
Yes. Many signing platforms provide APIs, but the important question is what the API controls. For form-driven applications, APIs should connect signatures to submission records, permissions, workflow state, and downstream systems.
### **Why Does Signature Context Matter?**
Signature context matters because a signature without the surrounding record can be hard to defend. Teams may need to know the form version, field values, signer identity, submission ID, timestamp, protected fields, and whether anything changed after signing.
### **How Does Form.io Help With Controlled Form Workflows?**
Form.io gives teams [form management infrastructure](/form-management-software/) for forms, submissions, generated APIs, permissions, workflow actions, and self-hosted deployment. E-Sign+ extends that model by connecting signature verification to submission data instead of treating signing as a disconnected document event.
## **Build Signature Proof Into Your Form Infrastructure**
If your team needs signatures that stay attached to governed form data, application APIs, and your own deployment boundary, [try Form.io for self-hosted form workflows](/try-formio-for-free/).
# JSON Schema Validator Tools for Production Apps
[  ](https://form.io/json-schema-validator-tools-production-apps/)Searches for **json schema validator** often start with a simple need: check whether this JSON payload matches this schema.
That is useful. It is also only the first layer.
In a production app, a schema may validate API requests, generate a form, drive documentation, define a submission shape, feed an AI tool, or become part of a governed application contract. The right tool depends on which job the schema has to do.
## **Key takeaways**
- A JSON Schema validator checks whether JSON data conforms to a declared structure, types, required fields, constraints, and references.
- Online validators are useful for quick checks, but production teams usually need runtime libraries, CI checks, API contract tooling, or form infrastructure.
- Ajv, Python `jsonschema`, and Java validators solve the library problem. They do not own form authoring, submissions, permissions, or deployment governance.
- Form generators turn schema into UI, but the backend still has to store, secure, expose, and govern submitted data.
- Form.io fits when schema needs to become form and API infrastructure: builder, renderer, submissions, generated APIs, permissions, workflow actions, revisions, and customer-controlled deployment.
## **Quick answer: which JSON Schema validator tool should you use?**
Use an online validator when you need to test a small schema and sample payload quickly.
Use Ajv when your JavaScript or TypeScript application needs fast JSON Schema validation in Node.js, the browser, an API gateway, or a build process.
Use Python `jsonschema` when your Python services need to validate instances against JSON Schema drafts and report validation errors in application code.
Use a Java validator such as NetworkNT when JSON Schema validation belongs in a JVM service, API layer, or request/response validation path.
Use Spectral or a schema lifecycle tool when the problem is not one payload, but API governance, linting, bundling, testing, and CI.
Use RJSF, JSON Forms, or SurveyJS when the goal is to generate a form interface from structured schema.
Use Form.io when the schema must become production form infrastructure: a human-facing form, submission record, generated REST API, workflow surface, permission boundary, and governed deployment model.
## **What a JSON Schema validator actually proves**
JSON syntax validation and JSON Schema validation are different jobs.
A JSON syntax validator answers: is this valid JSON?
A JSON Schema validator answers: does this valid JSON match the structure and rules the application expects?
That can include object shape, required fields, string formats, numeric ranges, enum values, array constraints, nested objects, and references to other schema definitions.
The official JSON Schema site describes JSON Schema as the vocabulary that enables JSON data consistency, validity, and interoperability at scale ([JSON Schema](https://json-schema.org/)). The specification hub also separates JSON Schema Core from JSON Schema Validation, where validation defines the keywords used to assert whether data is valid ([JSON Schema specification](https://json-schema.org/specification)).
That distinction matters because many production failures are not syntax failures. They are contract failures.
The payload is valid JSON, but it is missing the field the downstream service expects. The field exists, but the type changed. The UI allowed a value that the backend rejects. The API docs say one thing, but the runtime accepts another. The schema was copied into three services, and now nobody knows which version is authoritative.
A validator can catch part of that. It cannot, by itself, decide where schema ownership lives.
## **The five tool layers behind the search**
The search result page for `json schema validator` looks crowded because people use the same phrase for several different jobs.
**Tool layer****Best fit****What it proves or creates****What the team still owns**Online validatorQuick testing and debuggingA sample JSON instance matches a schemaProduction runtime, security, CI, versioningRuntime validatorAPI requests, service boundaries, app codePayloads satisfy schema rules in a language/runtimeUI, storage, workflows, governanceAPI contract toolingOpenAPI, linting, docs, API style rulesAPI definitions follow a contract and style rulesForm authoring, submissions, application stateForm generatorRendering forms from schemaA schema can produce a user-facing formBackend APIs, permissions, data lifecycleForm/API infrastructureProduction forms, APIs, submissions, workflowsSchema governs form UX, submission shape, generated APIs, and data handlingProduct fit, deployment ownership, policy configurationThe mistake is asking, "What is the best JSON Schema validator?" without asking, "What part of the system needs validation?"
## **Online validators are useful, but limited**
Online validators are useful for quick checks. They help developers paste in a schema, paste in sample JSON, and see errors immediately.
That is often exactly what the searcher wants.
But online validators should not become the production validation strategy. They are poor places for sensitive payloads. They do not enforce validation in your application. They do not live in CI. They do not control what happens after data is accepted.
Use them like a scratchpad.
For production, validation needs to move into the system path: application code, API gateway, test suite, CI pipeline, schema registry, form builder, or platform boundary.
## **Runtime validators: Ajv, Python, Java, and the application path**
Runtime validators belong where your application receives, transforms, or emits JSON.
Ajv is the obvious JavaScript and TypeScript example. Its documentation says it supports JSON Schema draft-04, draft-06, draft-07, draft 2019-09, draft 2020-12, and JSON Type Definition ([Ajv schema language guide](https://ajv.js.org/guide/schema-language.html)). Snyk's package database currently lists Ajv at more than 272 million weekly npm downloads, which shows how deeply validation libraries can sit inside the JavaScript ecosystem ([Snyk Ajv package page](https://security.snyk.io/package/npm/ajv)).
Python teams commonly reach for `jsonschema`, whose documentation shows the simple `validate` function and the validator classes behind it ([Python jsonschema validation docs](https://python-jsonschema.readthedocs.io/en/stable/validate/)).
Java teams may use NetworkNT's JSON Schema Validator, which describes support for multiple drafts and OpenAPI 3 request/response validation ([NetworkNT JSON Schema Validator](https://github.com/networknt/json-schema-validator)).
These tools are important because validation should happen where the system can reject bad data before it spreads.
The practical checklist is straightforward:
- Confirm which JSON Schema draft or dialect your validator supports.
- Reuse compiled validators where the library recommends it.
- Decide whether validation should fail fast or collect all errors.
- Make error messages useful enough for logs, developers, or users.
- Treat `$ref`, remote references, and bundled schemas as design choices, not incidental details.
- Benchmark against your actual schemas and payload sizes if validation runs in a hot path.
Runtime validators are the right answer when the job is validation.
They are not the whole answer when the same schema also needs to create forms, APIs, permissions, workflows, submission records, and audit evidence.
## **API contract tools: where JSON Schema meets OpenAPI**
For API teams, JSON Schema often appears through OpenAPI.
The OpenAPI Initiative's 3.1 release announcement says OpenAPI Schema Objects are now fully compatible with JSON Schema draft 2020-12 ([OpenAPI 3.1 release](https://www.openapis.org/blog/2021/02/18/openapi-specification-3-1-released)). That matters because the schema can become part of request validation, response validation, documentation, mock servers, SDK generation, and contract testing.
This is where tools such as Spectral fit. Spectral is a JSON/YAML linter designed with OpenAPI, AsyncAPI, and JSON Schema in mind ([Spectral](https://stoplight.io/open-source/spectral)). A validator asks whether data satisfies a schema. A linter can ask whether an API definition follows a team rule.
That is a different level of governance.
For production apps, the better question is not "Can we validate this object?" It is:
- Can we keep the API contract and implementation aligned?
- Can we catch drift in CI before release?
- Can we enforce style and security rules across many APIs?
- Can generated docs, mocks, clients, and tests inherit the same contract?
That is where JSON Schema starts becoming part of operational discipline.
## **Schema lifecycle tools: keep schemas from becoming loose files**
When schemas are shared across teams, a single validator is not enough.
Schema files need formatting, linting, testing, bundling, versioning, and promotion through environments. The official JSON Schema tools page shows how broad the ecosystem has become, including validators, documentation generators, schema-to-code tools, schema-to-web-UI tools, benchmarks, and compliance reports ([JSON Schema tools](https://json-schema.org/tools)).
Sourcemeta's JSON Schema CLI is a good example of the production-lifecycle layer. Its repository describes a CLI for maintaining schema repositories and ensuring quality during local development and CI/CD, including formatting, linting, testing, and bundling ([Sourcemeta JSON Schema CLI](https://github.com/sourcemeta/jsonschema)).
This layer matters when a schema is not a one-off file. It is a source artifact.
If multiple services, teams, or applications depend on it, schema changes need review. References need to resolve. Tests need to run. Breaking changes need to be understood before they reach production.
That is the point where teams stop treating JSON Schema as an isolated validator input and start treating it as part of the application contract.
## **Form generators: when schema becomes UI**
Some teams search for a JSON Schema validator and really need a form generator.
RJSF, for example, is a React component capable of building HTML forms out of JSON Schema. JSON Forms is another JSON Schema-based form renderer with data binding, validation, and rule-based visibility.
These tools are useful when a team wants schema to reduce repetitive form UI work.
But a form generator still leaves major production questions open:
- Where are submissions stored?
- Which API receives the data?
- How are permissions enforced?
- How are form changes versioned?
- How do non-developers safely edit forms?
- How does the schema move between dev, test, and production?
- What happens when the form becomes part of a regulated workflow?
A React JSON Schema form can render fields. That does not make it a form platform.
This is the line Form.io crosses.
## **Where Form.io fits**
Form.io belongs in this conversation only after the lower layers are clear.
It is not a replacement for Ajv, Python `jsonschema`, the JSON Schema specification, or OpenAPI tooling.
Form.io is the better fit when schema needs to become form and API infrastructure.
Form.io's Form JSON documentation says Form JSON defines the structure, appearance, and functionality of a form, and that the schema is used for rendering forms, generating REST API interfaces, and hosting the form schema for embedding ([Form.io Form JSON docs](https://help.form.io/form-building/form-json)).
Its feature documentation also explains that the builder outputs JSON schemas rather than static HTML, and that the same schema defines the UI, validation rules, data model, and REST API endpoints ([drag-and-drop form builder and APIs](https://form.io/features/drag-and-drop-form-builder-apis/)).
That is the infrastructure difference.
A validator can say, "This payload is valid."
A form generator can say, "This schema can render a form."
Form.io can connect the form definition, rendered experience, submission data, generated API, permission model, workflow actions, revisions, and deployment boundary.
That includes the operational pieces validators do not try to own: [self-hosted form deployment](https://form.io/features/self-hosted-forms-for-enterprise/), [form revisions](https://form.io/features/form-revisions-form-json-schema), [complete audit trails](https://form.io/features/log-forms-complete-audit-trail/), [secure forms compliance readiness](https://form.io/features/secure-forms-compliance-readiness/), and [fillable PDF workflows](https://form.io/features/fillable-pdf-forms) when the submitted record also needs document output.
That matters for teams building customer portals, healthcare intake, insurance claims, government services, financial onboarding, internal approval workflows, and B2B SaaS products where forms are part of the application architecture.
There is also customer proof behind this pattern. G2's indexed Form.io reviews include a State of Ohio pandemic-response example where Form.io was used to stand up forms, store and present data through an API, and feed analytics dashboards. The same reviewer called the model "easy to manage" across hundreds of websites ([G2 Form.io reviews](https://www.g2.com/products/form-io/reviews)).
Form.io's own customer proof makes the same point from the build-vs-buy side. Edify.ai said speed to market with Form.io "worked fantastically well" and that the team could focus development time on proprietary work instead ([Form.io customer proof](https://form.io/)).
The honest framing is this:
Use a JSON Schema validator when validation is the job.
Use Form.io when the schema needs to become a governed form, API, and submission system.
## **A production checklist for choosing JSON Schema tools**
Before choosing a tool, answer these questions.
### **1. Where does validation happen?**
Validation may belong in the browser, backend service, API gateway, test suite, CI pipeline, ETL job, or form platform.
One schema may need several validators in different places. That is normal. The risk is when each surface evolves its own slightly different rules.
### **2. Which schema version do you support?**
JSON Schema draft support is not trivia. Draft-07, 2019-09, and 2020-12 do not behave identically.
Pin the version. Document it. Make sure your tooling supports it before using draft-specific keywords in production.
### **3. Who owns schema changes?**
If schemas define production behavior, they need ownership.
A change to a field, type, required value, nested object, or reference may affect UI, API behavior, stored submissions, integrations, reports, and historical records.
### **4. Is the schema only validating data, or generating behavior?**
If the schema only validates API payloads, a runtime library may be enough.
If the schema renders forms, generates APIs, controls submissions, and drives workflow behavior, the decision belongs at the platform layer.
### **5. What happens after validation passes?**
This is the question most validator pages skip.
Where does the data go? Who can see it? Can it be edited? Is there revision history? Does it trigger a webhook? Can the workflow be audited? Can the platform run inside your environment?
If those questions matter, you are no longer only choosing a JSON Schema validator.
## **Key takeaways**
JSON Schema validators are necessary tools, but the phrase hides several different jobs.
Online validators help with quick checks. Runtime validators enforce contracts in code. API tooling keeps definitions consistent. Schema lifecycle tools keep shared schemas maintainable. Form generators turn schema into UI.
Form.io is for the next layer: production forms and APIs governed by schema, with submissions, permissions, workflows, revisions, and deployment control attached.
That is the practical distinction. Do not make a validator carry the full application burden. Use the validator where validation belongs, and choose infrastructure when the schema becomes infrastructure.
## **FAQ**
### **What is a JSON Schema validator?**
A JSON Schema validator checks whether JSON data conforms to rules described in a JSON Schema. Those rules can define object structure, required fields, data types, arrays, enums, numeric limits, string formats, and references to other schemas.
### **Is JSON validation the same as JSON Schema validation?**
No. JSON validation usually means checking whether the text is valid JSON syntax. JSON Schema validation checks whether valid JSON data matches an expected schema.
### **What is the best JSON Schema validator for JavaScript?**
Ajv is one of the default choices for JavaScript and TypeScript teams. It supports multiple JSON Schema drafts and is widely used across Node.js and browser environments.
### **What is the best JSON Schema validator for Python?**
Python teams commonly use the `jsonschema` package. It implements JSON Schema validation and provides validator classes, error handling, and draft-aware behavior.
### **Can JSON Schema generate forms?**
Yes, some tools can render forms from JSON Schema. RJSF and JSON Forms are common examples. The important distinction is that rendering a form does not automatically provide backend APIs, submission storage, permissions, or workflow governance.
### **Does OpenAPI use JSON Schema?**
OpenAPI 3.1 aligns its Schema Object with JSON Schema draft 2020-12. That makes JSON Schema more important for API contracts, documentation, request and response validation, and API tooling.
### **Should I paste sensitive data into an online JSON Schema validator?**
For sensitive production data, avoid it. Online validators are useful for examples and debugging, but regulated or customer data should be validated inside tools and environments your team controls.
### **What should production teams check before choosing a validator?**
Check draft support, runtime support, error quality, performance, custom formats, `$ref` handling, CI integration, schema bundling, and how schema changes are governed over time.
### **Is Form.io a JSON Schema validator?**
Form.io is not best understood as a standalone JSON Schema validator. It is a schema-driven form and API platform. It uses schema to help govern forms, submissions, generated APIs, permissions, workflows, and deployment control.
### **When should a team use Form.io instead of only a validator library?**
Use Form.io when the schema needs to operate a production form workflow, not just validate a payload. That includes embedded forms, submission records, generated REST APIs, permissions, workflow actions, revisions, and self-hosted deployment.
### **Can Form.io work alongside validators like Ajv?**
Yes. A production architecture can use validation libraries at service boundaries while using Form.io for the form, API, submission, and workflow layer. The key is deciding which system owns each contract.
If your schema needs to do more than validate JSON, [try Form.io for free](/try-formio-for-free/) and see how forms, APIs, submissions, and workflow controls can live on one foundation.
# Embedded Forms for B2B SaaS: The White-Label Form Builder Comparison
[  ](https://form.io/embedded-forms-b2b-saas-white-label-comparison/)Embedded forms are easy to misunderstand.
For a marketing team, an embedded form might mean a signup widget pasted into a page. For a B2B SaaS platform, it can mean something much heavier: a branded form experience inside the product, customer-managed form creation, tenant-specific permissions, API-backed submissions, and workflow rules that cannot drift from the rest of the application.
That is the difference this comparison is about.
## **Embedded forms become product infrastructure**
An embedded form is a form rendered inside a webpage or application, usually through an iframe, script, SDK, component, or framework integration.
That definition is useful, but too broad. It puts a newsletter signup form and a customer-facing SaaS form builder in the same bucket.
B2B SaaS teams need a sharper distinction:
- Embedded form: a finished form appears inside your website or app.
- Embedded form builder: your users or admins can create and edit forms inside your product.
- White-label form infrastructure: the forms, builder, submissions, APIs, branding, roles, tenant boundaries, and workflow behavior all operate as part of your product.
That last category is where Form.io belongs. The [Form.io Enterprise Form Builder Module](https://form.io/enterprise-form-builder-module/) is built to embed a white-labeled form builder inside an application while the platform owner keeps control over components, data model, permissions, and workflow behavior.
## **Quick comparison**
**Option****Best fit****Main strength****Main tradeoff**Form.ioB2B SaaS teams that need embedded forms, embedded form building, APIs, tenant-aware control, and deployment flexibilityForms behave like governed application infrastructureMore platform than a simple marketing form team needsJotformHosted enterprise teams that want template-rich no-code form building and broad business workflowsFast, familiar hosted form creationStrongest when the form system can remain vendor-hosted and account-centeredFeatheryProduct teams that want polished embedded form UX and a white-label editor experienceStrong product-form experience and editor customizationTeams still need to evaluate backend governance, deployment, and data ownership depthSurveyJSJavaScript teams that want form libraries and a builder they can wire into their own stackDeveloper control inside front-end applicationsMore assembly work around storage, APIs, permissions, and operationsFormsortTeams building branded conversion flowsManaged branded flows with conversion focusNarrower fit when forms become governed product infrastructure123FormBuilder / similar toolsTeams that primarily need branded hosted forms and account-level white labelingFamiliar form-builder packagingWhite label often centers on branding more than application architectureThe right choice depends less on the phrase "embedded forms" and more on what the embedded form has to own.
## **The SaaS evaluation checklist**
If customers only need to submit a contact form, almost any credible form builder can work.
If customers need to create forms inside your application, the checklist changes:
- Can the finished form be embedded cleanly?
- Can the builder itself be embedded?
- Can vendor branding be removed from the form, builder, emails, URLs, and exports?
- Can each tenant have separate forms, submissions, themes, permissions, and workflows?
- Can you restrict which components, validation rules, logic, and publishing actions customers can use?
- Are submissions available through APIs, not only exports or webhooks?
- Where does submission data live?
- Can the form layer run inside the deployment boundary your customers require?
- Are revisions, access controls, and audit evidence part of the model?
- Does the pricing model still work when every customer creates forms?
Those questions are not cosmetic. They are architecture questions.
[Postman's 2025 State of the API report](https://voyager.postman.com/doc/postman-state-of-the-api-report-2025.pdf) found that 82% of organizations had adopted some level of API-first approach. That matters because embedded forms in a SaaS product are not just pixels. They create records, trigger workflows, and pass data to the rest of the application.
## **Where Form.io fits**
Form.io is the strongest fit when embedded forms need to behave like part of the product infrastructure.
The [Form.io form embedding documentation](https://help.form.io/dev/form-embedding) covers quick inline embedding, JavaScript embedding, iframe fallback, builder embedding, and framework embedding. That gives teams a practical path from simple rendering to deeper application integration.
But the more important distinction is what sits behind the embed.
Form.io forms are JSON-driven definitions connected to rendering, validation, submissions, APIs, permissions, and workflow behavior. The [drag-and-drop form builder with APIs](https://form.io/features/drag-and-drop-form-builder-apis/) is not only a UI for arranging fields. It is part of a system where form definitions can become application contracts.
That matters for SaaS platforms where customers need their own forms, variations, permissions, and branded experiences. The [Form.io homepage](https://form.io/) explicitly frames white-label SaaS use around form, API, and data management under the platform's brand or the customer's brand. It also describes multi-tenant child-project patterns for separating forms, data, and form building.
For more controlled environments, the [self-hosted Form.io deployment model](https://form.io/features/self-hosted-forms-for-enterprise/) matters because the form layer can live closer to the customer's infrastructure boundary instead of becoming an external data silo.
## **White label is more than branding**
Most white-label form pages talk about logos, colors, custom domains, badge removal, and branded emails.
Those are real requirements. They are not enough.
In a B2B SaaS product, white label also means the form capability has to respect the product's operating model. A tenant should not see another tenant's forms. A customer admin should not publish components that break downstream processing. A support team should be able to diagnose what changed. A developer should know how submissions map into APIs and workflows.
This is where a light embed starts to strain.
OWASP's API Security Top 10 puts [broken object-level authorization](https://owasp.org/API-Security/editions/2023/en/0xa1-broken-object-level-authorization/) first. That is a useful reminder for SaaS form architecture: if embedded forms create or expose customer records through APIs, authorization has to be object-aware and tenant-aware. Front-end hiding is not governance.
The same logic applies to validation and workflow behavior. The [conditional logic and validation features](https://form.io/features/form-conditional-logic-form-validation/) matter because the form should enforce rules before bad data becomes an API or workflow problem.
## **When a simpler embedded form is enough**
Use a simpler hosted embed when the form is not central to the product.
That includes:
- newsletter signup
- marketing lead capture
- event registration
- contact and support requests
- one-off surveys
- public feedback forms
- low-risk forms that can live in an external form account
In those cases, a hosted form builder with templates, brand settings, and a quick embed code may be the best decision. Jotform, Formsort, 123FormBuilder, and similar tools can be strong fits when speed and convenience are the main job.
The mistake is keeping that architecture after forms become a customer-facing product capability.
## **When embedded form infrastructure is needed**
Embedded form infrastructure becomes important when the form is part of how your SaaS product works.
Examples include:
- customer onboarding flows that differ by tenant
- partner and vendor portals
- regulated intake workflows
- customer-managed form libraries
- embedded application builders
- productized approval flows
- internal workflow forms exposed to external customers
- multi-office or multi-group customer operations
In these cases, forms need lifecycle control. NIST's [Secure Software Development Framework](https://csrc.nist.gov/pubs/sp/800/218/final) treats security practices as part of the software development lifecycle, which is the right lens for embedded form capability that ships inside a SaaS product. The form builder is no longer an outside utility. It is part of the product surface.
Data risk also changes the decision. [Thales' 2025 Cloud Security Study](https://cpl.thalesgroup.com/cloud-security-research) reported that 54% of cloud data is sensitive and that only 8% of respondents encrypt 80% or more of cloud data. That does not mean every embedded form needs self-hosting. It does mean SaaS teams should know where form data lives, who can access it, how it is encrypted, and how it moves through APIs.
## **Customer proof: white-label forms as a business model**
The white-label use case is not theoretical for Form.io.
In Form.io's Bursting Silver case study, the company describes how a regulatory-industry platform [white-labeled Form.io](https://form.io/case-studies/from-facing-the-risk-of-losing-an-entire-industry-to-generating-millions-and-having-new-clients-call-them/) to support its industry, sign dozens of new clients, and increase revenue by 25%.
That proof point matters because it connects embedded forms to a business model, not just a UI decision. When forms are a capability customers use inside your product, the form layer can influence retention, onboarding, service load, expansion, and product differentiation.
## **The decision framework**
Choose a simple embedded form when the form is a page element.
Choose a hosted enterprise form builder when business users need fast form creation and the external vendor account model is acceptable.
Choose a JavaScript form library when your team wants front-end control and is ready to build the backend, storage, permissions, and operational layer around it.
Choose Form.io when the form capability needs to become part of your product architecture: embedded rendering, embedded building, customer self-service, white-label experience, structured schemas, generated APIs, permissions, validation, workflow behavior, and deployment control.
That is the real difference.
Embedded forms are not automatically infrastructure. But in B2B SaaS, they often become infrastructure faster than teams expect.
## **Key takeaways**
- Embedded forms can mean a simple widget, an embedded form builder, or full white-label form infrastructure.
- SaaS teams should evaluate builder embedding, tenant separation, data ownership, APIs, permissions, workflow behavior, and deployment model.
- Competitors can be good fits for hosted no-code forms, polished product forms, developer libraries, or branded conversion flows.
- Form.io is strongest when the form layer needs to stay connected to schemas, APIs, submissions, permissions, and workflows inside the product architecture.
- A simple embed is enough for low-risk marketing forms. It is not enough when customers need to build and govern forms inside your SaaS.
## **FAQ**
### **What are embedded forms?**
Embedded forms are forms rendered inside a webpage or application through an iframe, script, SDK, component, or framework integration. The user completes the form without leaving the surrounding site or product experience.
### **What is an embedded form builder?**
An embedded form builder is a builder or editor exposed inside your application so users can create or change forms without going to a separate vendor dashboard.
### **What does white-label mean for forms?**
At minimum, white label usually means custom branding, colors, domains, and removal of vendor badges. For SaaS platforms, it should also include builder experience, tenant separation, emails, exports, permissions, and workflow behavior.
### **Can customers create their own forms inside a SaaS product?**
Yes, if the platform supports embedded form building. The important question is whether customers can do that inside guardrails your product controls.
### **Are iframe embedded forms enough?**
Sometimes. Iframes can be practical for low-risk or simple use cases. They are often weaker when the form needs deep styling, app authentication, event handling, tenant-aware permissions, or tight workflow integration.
### **Which embedded form builder is best for multi-tenant SaaS?**
Form.io is a strong fit when multi-tenant SaaS teams need white-labeled form creation, APIs, permissions, structured submissions, workflow behavior, and deployment control. Simpler tools may fit when the requirement is only branded form capture.
### **Do embedded forms create security risks?**
They can if teams treat them as front-end widgets while the data becomes sensitive application data. The right controls depend on authorization, validation, tenant separation, encryption, auditability, and where submissions are stored.
### **When should I choose Form.io over a simpler form builder?**
Choose Form.io when forms are part of the application infrastructure: customers create forms, submissions feed APIs, permissions matter, workflows depend on form data, and the deployment boundary is important.
### **Can Form.io replace my whole application backend?**
No. Form.io is infrastructure for forms, APIs, submissions, validation, permissions, and workflow-related actions. Your application still needs its own product logic, user experience, integrations, and surrounding architecture.
## **Build embedded forms that behave like your product**
If your SaaS customers only need a form on a page, keep it simple.
If they need governed, branded, customer-managed forms inside your product, start with infrastructure that can carry the form, data, API, and workflow model together.
[Try Form.io for white-label embedded form infrastructure](/try-formio-for-free/).
# Claims Management Software Starts With The Forms That Feed It
[  ](https://form.io/claims-management-software-insurance-form-builders/)Claims management software comparisons usually start with the core claims system.
That makes sense. Carriers, TPAs, MGAs, adjusters, and self-insured organizations need systems for assignment, reserves, adjudication, payments, subrogation, reporting, and closure.
But many claims problems start earlier.
They start at the first notice of loss. They start when a claimant uploads the wrong document, an adjuster captures incomplete field notes, an agent enters policy data twice, or a regulatory form has to be recreated from unstructured intake data.
Before a claim can be managed, the data has to be captured.
That is why insurance teams should evaluate the form infrastructure behind the claims workflow, not only the claims platform itself.
## **Key Takeaways**
- Claims management software and claims form infrastructure solve different layers of the same workflow.
- Full claims systems manage the claim lifecycle. Form infrastructure governs intake, validation, files, submissions, APIs, PDFs, permissions, and handoff.
- Claim handling is a high-risk customer and regulator touchpoint, so weak intake creates downstream cost.
- Form.io is not a full claims-core replacement. It is a strong fit when insurance forms need to become embedded, API-backed, self-hosted workflow infrastructure.
- The right evaluation question is not only "which claims system?" It is also "what form layer feeds and extends the claims system?"
## **What Claims Management Software Usually Means**
In most buyer guides, claims management software means a system that supports the claims lifecycle from first notice of loss through settlement and closure.
The category usually includes:
- FNOL and claims intake
- claim assignment and triage
- document and image management
- policy lookup
- investigation and adjudication
- reserve management
- payments and settlement
- regulatory reporting
- analytics and dashboards
- customer status updates
- closure and audit history
That is why systems like Guidewire ClaimCenter, Duck Creek Claims, Riskonnect, FINEOS, VCA, BriteCore, Snapsheet, and other claims platforms dominate the search results for **claims management software**.
They are solving a large operational problem.
Form.io should not be framed as a replacement for those systems when the buyer needs a full claims core. If your team needs end-to-end claims adjudication, reserve management, litigation tracking, payment workflows, subrogation, CAT-scale claims operations, or deep P&C suite functionality, a claims management platform is the right category to evaluate.
But claims systems do not remove the need for form infrastructure.
They often create more of it.
## **Why Claims Intake Is An Infrastructure Problem**
Claims are where the insurer's promise becomes visible.
The customer does not experience the claims system as a data model or an admin workflow. They experience it as a form, a file upload, a status update, an estimate, a call, a missing document request, or a delay.
That is why digital claims workflows have real retention stakes. J.D. Power's 2025 U.S. Claims Digital Experience Study reported that insurers deliver adequate digital updates only 22% of the time. Insurance Journal's coverage of the study also reported that 52% of auto and homeowners customers who rate their digital claim experience as "poor" or "just OK" are likely to leave or not renew, compared with 4% of customers who rate the experience as "excellent" or "perfect" ([Yahoo Finance syndication of J.D. Power release](https://finance.yahoo.com/news/fully-digital-claims-processing-drives-120000409.html), [Insurance Journal](https://www.insurancejournal.com/news/national/2025/12/09/850297.htm)).
Weak intake also shows up in complaint patterns. The NAIC says delays, denials, and unsatisfactory settlements are among common reasons consumers file complaints, and that consumers are asked to gather supporting documents, photographs, correspondence, phone logs, and detailed accounts when filing complaints ([NAIC](https://content.naic.org/article/how-file-complaint-and-research-complaints-against-insurance-carriers)). A ValuePenguin analysis of NAIC closed complaint data reported that claim handling accounted for 65.2% of closed insurance complaints in 2024, with delays and unsatisfactory settlements or offers as the top claim-handling complaint types ([ValuePenguin](https://www.valuepenguin.com/most-common-insurance-complaints)).
Those numbers do not prove a form platform fixes claims operations by itself.
They prove the stakes.
If claims data enters the workflow through weak forms, disconnected uploads, duplicated manual entry, unclear validation, or inconsistent status paths, the claims system inherits that mess.
## **The Claims Workflow Surfaces That Depend On Forms**
Insurance forms are not only contact forms.
In a claims environment, forms show up across the workflow:
- policyholder FNOL forms
- agent and broker claim submission forms
- adjuster field reports
- inspection and damage assessment forms
- photo, video, and document upload flows
- repair estimate collection
- medical record and proof-of-loss intake
- third-party claimant forms
- loss run request forms
- policy application and endorsement forms
- regulatory filing packets
- PDF outputs for records, signatures, reviews, or state-specific requirements
Some of these forms are customer-facing. Some are internal. Some are embedded in portals. Some are mobile. Some still need to map back to exact PDF-style layouts because insurance operations have not escaped document reality.
That is the layer where form infrastructure matters.
A claim can move through a core system, but the surrounding form layer still has to answer practical questions:
- Who can submit this form?
- Which fields are required for this claim type?
- Can the claimant save and resume?
- Can an adjuster collect data offline?
- Can photos and documents be attached securely?
- Does the submitted data become structured JSON, or does someone retype it later?
- Can the submission feed an API, webhook, claims core, document repository, or analytics pipeline?
- Can the same data produce a PDF output when a regulator, carrier, or partner still needs one?
- Can changes to the form and submission be audited?
Those are not cosmetic questions. They are workflow architecture.
## **What To Evaluate In The Claims Form Layer**
A serious claims-intake form layer should be evaluated on more than field layout.
### **Conditional Logic**
Insurance workflows vary by claim type, line of business, state, channel, and role.
A property claim does not ask the same questions as a cyber liability claim. A claimant portal does not need the same view as an adjuster workflow. A policyholder should not see every internal field an examiner needs.
The form layer should support conditional logic, role-specific screens, and dynamic form paths without forcing every variation into custom code.
### **Validation Before Handoff**
The worst time to discover bad data is after it reaches the claims system.
Claims forms should validate required fields, dates, policy identifiers, file requirements, numeric values, and conditional dependencies before submission. They should reduce preventable downstream rework without pretending every claim is simple.
### **File And Evidence Capture**
Claims intake often depends on documents and media: photos, estimates, police reports, medical documents, invoices, inspection records, correspondence, and proof-of-loss materials.
The form layer should treat uploads as part of the submission record, not as an afterthought in a shared inbox.
### **Generated APIs And System Handoff**
Claims data rarely stays in one place.
It may need to feed a claims core, policy system, CRM, document management platform, analytics warehouse, notification workflow, payment process, or regulatory reporting path.
That is why static forms are not enough. The form layer should expose structured submission data through APIs and integration patterns that developers can control. For Form.io, that includes [drag-and-drop forms with generated APIs](https://form.io/features/drag-and-drop-form-builder-apis/) rather than forms that stop at display and email notification.
### **Permissions And Submission Access**
Insurance workflows are role-sensitive.
Policyholders, agents, adjusters, claim supervisors, legal teams, compliance teams, and admins should not all see the same data. A useful form platform needs access control around forms and submissions, not just a login screen in front of everything.
### **Auditability**
Claims records can become evidence.
If a form changes, a submission is edited, a file is replaced, or a workflow action fires, teams need to understand what changed, who changed it, and when. Auditability is not decoration in regulated workflows.
That is why a claims form layer should include a [complete audit trail for form changes and submissions](https://form.io/features/log-forms-complete-audit-trail/), especially when operational records may later be reviewed by legal, compliance, or regulator-facing teams.
### **PDF And Regulatory Output**
Insurance still runs on documents.
NAIC's SERFF industry training page describes electronic rate and form filing as including form submittal, document management, and review access, while supporting compliance with consumer protection requirements ([NAIC SERFF](https://content.naic.org/node/10174)). That does not mean every claims form feeds SERFF. It does mean "forms" in insurance often exist inside regulated document and review workflows.
Good form infrastructure should let teams collect structured data through modern web forms while still producing PDF outputs when official, partner, regulatory, or legacy processes require them.
That can include [custom PDF templates](https://form.io/features/pdf-forms-pdf-template-designer/) and [fillable PDF forms](https://form.io/features/fillable-pdf-forms/) when the workflow has to preserve document fidelity without giving up structured submission data.
## **Where Form.io Fits**
Form.io fits when the forms around claims management need to become application infrastructure.
That does not mean Form.io is a claims adjudication engine. It does not calculate reserves, run a full claims core, or replace every specialized insurance platform.
It means Form.io can support the form, API, submission, PDF, and workflow layer that surrounds those systems.
Form.io's public insurance PDF page speaks directly to this type of insurance workflow: outputting submissions to PDF, turning PDFs into embeddable dynamic forms, tracking changes to fields and forms, auto-populating repeated data, autosaving unfinished forms, collecting offline, and using mobile-responsive forms ([Form.io insurance PDF forms](https://form.io/industries/pdf-forms-for-insurance/)).
The official Form.io documentation also describes two PDF paths: PDF output from webform submissions and PDF-first forms where teams upload a PDF and place interactive fields on top of it. PDF Plus adds PDF-first experiences with pixel-perfect PDF backgrounds and JSON-driven overlays, while PDF Basic supports printing and downloading webform submissions as PDFs ([Form.io docs](https://help.form.io/form.io-concepts.md?ask=How%20does%20Form.io%20support%20PDF%20forms%20and%20PDF%20output%20from%20webform%20submissions%3F)).
That matters for insurance because the buyer often needs both:
- modern, embedded, API-backed data capture
- document-style outputs that still match policy, claims, underwriting, or regulatory expectations
Form.io also matters when teams need forms and APIs together. The platform is designed around JSON-defined forms, submissions, generated APIs, permissions, workflow actions, and customer-controlled deployment. For insurance teams, that can support workflows such as:
- embedded FNOL forms inside a policyholder portal
- agent-facing application and claims intake
- adjuster inspection forms with file uploads
- internal review forms for claims operations
- self-hosted data capture for sensitive records
- structured submission APIs into existing claims or policy systems
- PDF outputs for claim packets, confirmations, or document-heavy workflows
This is the useful distinction:
Claims management software manages the claim.
Form.io can govern the form infrastructure that captures and moves the data the claim depends on.
## **Comparison: What To Ask Before Choosing The Form Layer**
## **Evaluation question****Why it matters****What to look for**Can the form handle different claim types?Claims vary by line, state, product, and roleConditional logic, reusable components, role-specific flowsCan users upload documents and photos?Evidence is often the claim recordSecure file upload, file metadata, submission associationDoes the form validate data before submission?Bad intake data creates downstream reworkRequired fields, conditional validation, typed data, calculated valuesDoes submission data have an API?Claims data must move into other systemsREST APIs, webhooks, JSON submissions, developer-controlled handoffCan permissions be scoped?Insurance workflows are role-sensitiveForm and submission permissions, own-vs-all access, admin boundariesCan changes be audited?Claims and regulated forms need evidenceChange history, audit logs, revision-aware workflowsCan web submissions become PDFs?Insurance still needs documentsPDF output, PDF templates, PDF-first forms, existing PDF conversionCan it be embedded?Claims intake lives inside portals and productsEmbeddable renderer, embedded builder, white-label controlsCan it be self-hosted?Some insurance data must stay inside controlled environmentsCustomer-controlled deployment, database, file storage, network boundary**When A Full Claims Management Platform Is The Better Fit**
Use a full claims management platform when the core problem is managing the claim lifecycle itself.
That includes:
- claim assignment and triage
- reserve management
- adjudication workflows
- payments and settlement
- subrogation and recovery
- litigation management
- catastrophe scale handling
- repair network workflows
- claims analytics
- policy and billing suite integration
- specialized P&C, health, life, or workers' compensation claim operations
This is where platforms like Guidewire, Duck Creek, Riskonnect, FINEOS, VCA, BriteCore, Snapsheet, and other insurance-specific systems belong in the evaluation.
Trying to force a form infrastructure platform to behave like a complete claims core would be the wrong move.
But it is equally risky to assume the claims core solves every form problem around it.
Many carriers already have core systems. The friction is in the portals, supplemental forms, customer-facing intake, partner workflows, document packets, regulatory outputs, and integration surfaces around those systems.
That is where a dedicated form infrastructure layer can make sense.
## **When To Evaluate Form Infrastructure Separately**
Evaluate the form layer separately when any of these are true:
- Your claims core works, but customer or agent intake is weak.
- You need embedded forms in a portal, app, or white-labeled product.
- Claims data must feed multiple downstream systems.
- Different teams need to create or modify forms without breaking the architecture.
- Documents and PDFs are still part of the official workflow.
- You need structured APIs instead of manual re-entry.
- You need submission-level permissions and audit evidence.
- You need to self-host the form and submission layer.
- You need offline or mobile-responsive collection.
- You need a repeatable way to turn form changes into governed application behavior.
This is the buyer Form.io should speak to.
Not the buyer looking for the quickest online form.
Not the buyer who wants to replace every claims system overnight.
The buyer whose forms have become infrastructure.
## **Customer Proof: Insurance Forms Are Operational Systems**
Form.io has public insurance-adjacent proof through E-Risk Services, LLC, described in a Form.io case study as a specialty-lines underwriting subsidiary of Nationwide Insurance Company. The case study says E-Risk built a CRM in two months instead of two years ([Form.io case study](https://form.io/case-studies/building-a-crm-took-2-months-instead-of-2-years/)).
That proof point should be used carefully. It is a Form.io-hosted case study, not an independent Nationwide-hosted validation of the timeline.
But it is still relevant because E-Risk's public Nationwide page shows the real insurance surfaces around specialty lines: product pages, applications and forms, policy forms, loss run requests, expiring policy requests, underwriting contact paths, quoting, and servicing ([Nationwide E-Risk](https://www.nationwide.com/excessandsurplus/e-risk/)).
That is the practical pattern.
Insurance teams do not only need one claims screen. They need many controlled data-capture and document workflows around underwriting, servicing, claims, renewals, requests, and regulated communications.
Form infrastructure is how those workflows stay usable without becoming disconnected spreadsheets, PDF piles, email chains, and one-off portals.
The customer language from another Form.io-hosted case study is useful here because it describes the same infrastructure burden in plain terms. In the Safety Mojo case study, a long-time Form.io platform user said, "Form.io cleans up all the dirty work and does it for you" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)). That quote is not insurance-specific, but it fits the architectural point: forms become expensive when every team has to rebuild the form, data, API, and workflow plumbing separately.
## **The Decision Rule**
Choose a claims management platform when the main requirement is claims-core operation.
Choose Form.io when the main requirement is governed form infrastructure around insurance workflows.
That means forms that can render in your application, collect structured data, validate submissions, handle files, expose APIs, support permissions, produce PDFs, and live inside your deployment boundary.
For teams with stricter data-control requirements, [self-hosted enterprise forms](https://form.io/features/self-hosted-forms-for-enterprise/) can keep the form, submission, and file-handling layer inside the environment the organization controls.
For insurance teams, this distinction matters because "claims management software" is not one decision.
It is at least two:
1\. What system manages the claim lifecycle? 2. What infrastructure captures, governs, and moves the data that feeds it?
Most comparisons answer only the first question.
The second question is where Form.io belongs.
## **FAQ**
### **What Is Claims Management Software?**
Claims management software helps insurance teams manage claims from intake through assignment, investigation, adjudication, settlement, reporting, and closure. It often includes FNOL, document management, workflow automation, payments, analytics, and compliance features.
### **Is Form.io Claims Management Software?**
Form.io is not a full claims management platform or claims-core system. It is form and API infrastructure that can support the intake, submission, document, PDF, permission, and integration layer around claims workflows.
### **Can Form.io Replace Guidewire Or Duck Creek?**
Not when the requirement is a full claims core. Guidewire, Duck Creek, and similar systems are built for end-to-end claims operations. Form.io is a better fit when teams need governed forms, APIs, submissions, PDFs, and embedded intake around those systems.
### **What Is FNOL Software?**
FNOL software supports first notice of loss: the initial claim report. A strong FNOL workflow captures structured claim data, claimant details, incident information, documents, photos, and routing data so the claim can move into the right downstream process.
### **Why Do Insurance Claims Workflows Need Better Forms?**
Claims workflows depend on accurate intake. If forms collect incomplete data, miss required documents, fail to validate fields, or force manual re-entry, the claims process slows down and customer experience suffers.
### **Can Claims Forms Collect Photos And Documents?**
Yes, but the important question is how those files are stored, associated with submissions, permissioned, and handed off. Claims evidence should be part of the structured submission workflow, not a loose email attachment.
### **How Do PDF Forms Fit Insurance Claims?**
Many insurance workflows still require PDF-style outputs, forms, packets, or official documents. A modern form layer should collect structured web data while still supporting PDF output or PDF-first forms when the workflow requires document fidelity.
### **What Should Insurers Evaluate In Claims Intake Software?**
Evaluate conditional logic, validation, file uploads, submission APIs, permissions, audit logs, embedded rendering, PDF output, mobile/offline support, and deployment control. The form layer should support the claims architecture, not just display fields.
### **Do Claims Workflows Need Self-Hosted Forms?**
Not always. Self-hosting matters when sensitive claims data, regulatory expectations, customer requirements, or enterprise architecture require the form and submission layer to run inside a controlled environment.
### **How Can Forms Connect To Claims Management Systems?**
Forms can connect through APIs, webhooks, submission exports, custom integrations, document workflows, or middleware. The important requirement is structured, validated submission data that downstream systems can consume reliably.
## **Build Claims Intake Infrastructure With Form.io**
If your team needs a full claims-core platform, evaluate claims management systems directly.
If your team needs better claims intake, embedded insurance forms, PDF outputs, generated APIs, controlled submissions, and customer-hosted form infrastructure, evaluate the form layer separately.
[Try Form.io for insurance form infrastructure](https://form.io/try-formio-for-free/).
# KYC Onboarding Software for Financial Services: Forms, APIs, and Audit-Ready Intake
[  ](https://form.io/kyc-onboarding-software-financial-services-form-platforms/)KYC onboarding software is usually evaluated as an identity verification purchase.
That is only part of the system.
Banks, fintechs, lenders, and other financial-services teams still have to collect customer data, route exceptions, connect verification providers, preserve evidence, and keep sensitive workflows under control. The right question is not only which KYC provider to buy. It is what intake infrastructure the provider connects to.
## **Key Takeaways**
- KYC onboarding software includes identity checks, but the surrounding intake layer matters just as much.
- Dedicated KYC vendors are strongest for document verification, sanctions screening, adverse media, KYB data, biometrics, and verification coverage.
- Form.io is a better fit for the application infrastructure around those checks: embedded forms, structured submissions, generated APIs, permissions, workflows, revisions, audit trails, and customer-controlled deployment.
- Financial-services teams should evaluate who owns the schema, submission record, API handoff, audit evidence, and change-control path.
- The strongest architecture often combines a KYC verification vendor with a governed form platform that controls intake inside the customer's own product and environment.
## **What KYC Onboarding Software Has To Handle**
KYC onboarding is not a simple signup form with a document upload bolted on.
In financial services, onboarding can involve customer identity, beneficial ownership, business entity details, risk indicators, attestations, document evidence, sanctions and PEP checks, adverse media review, manual exception handling, approvals, and ongoing updates.
The fraud pressure behind those workflows is real. The Federal Trade Commission reported that consumers lost more than $12.5 billion to fraud in 2024, a 25% increase from the prior year ([FTC](https://www.ftc.gov/news-events/news/press-releases/2025/03/new-ftc-data-show-big-jump-reported-losses-fraud-125-billion-2024)). That number does not prove any one onboarding product prevents fraud. It does show why financial-services teams treat identity, intake, and evidence workflows as risk infrastructure.
For covered financial institutions, customer due diligence also extends beyond one-time identity capture. FinCEN describes CDD as policies and procedures that identify and verify customers and beneficial owners, understand customer relationships for risk profiling, and support ongoing monitoring and customer-information updates ([FinCEN](https://www.fincen.gov/news/news-releases/fincen-reminds-financial-institutions-cdd-rule-becomes-effective-today)). FinCEN's 2026 exceptive relief narrowed repeat beneficial-owner verification at every new account opening, but preserved initial verification, risk-based updates, and ongoing monitoring obligations ([FinCEN](https://www.fincen.gov/news/news-releases/fincen-issues-exceptive-relief-streamline-customer-due-diligence-requirements)). Digital identity guidance makes the same point from another angle: NIST SP 800-63A-4 defines identity proofing and enrollment requirements across three identity assurance levels, with evidence, validation, and verification expectations that affect onboarding design ([NIST SP 800-63A-4](https://csrc.nist.gov/pubs/sp/800/63/a/4/final)). FFIEC authentication guidance also emphasizes layered security and stronger controls than single-factor authentication for financial institution services and systems ([FFIEC authentication guidance](https://www.ffiec.gov/news/press-releases/2021/pr-08-11)).
That is the operating reality KYC onboarding software has to support.
It has to help the organization answer:
- What information do we need for this customer type?
- Which evidence is required for this product, jurisdiction, or risk profile?
- Which verification provider or internal service should receive the data?
- Who reviews exceptions?
- Which decisions and changes need to be retained?
- Where does the submission record live?
- How do we update customer information later without losing history?
Those are not only compliance questions. They are application architecture questions.
## **The Three Layers Of KYC Onboarding Software**
Most KYC software pages collapse three different layers into one category.
That makes comparison harder than it needs to be.
### **1. KYC Verification And Data Providers**
This is the layer buyers usually think of first.
KYC verification providers handle identity document verification, database checks, liveness or biometric checks, sanctions screening, PEP screening, adverse media, fraud signals, KYB data, business registry checks, and beneficial ownership data.
If your main problem is global identity coverage, document authenticity, fraud detection, sanctions data, or KYB intelligence, this is the category you should evaluate.
Form.io does not replace that layer.
### **2. Client Lifecycle And Case Workflow Platforms**
Some financial institutions need a broader client lifecycle management system.
That can include onboarding cases, risk scoring, relationship-manager queues, remediation workflows, periodic refresh, monitoring, approvals, dashboards, and enterprise reporting.
If the primary buyer need is a complete CLM suite for a large financial institution, a specialized onboarding or CLM platform may be the right center of gravity.
Form.io does not claim to be a full AML case-management system.
### **3. Form And Application Infrastructure**
This is the layer many comparisons understate.
Before a verification service can check anything, the organization has to collect the right data, validate it, structure it, submit it, secure it, route it, and keep the record. That work often happens in forms embedded inside account-opening flows, borrower portals, investor onboarding flows, agent portals, internal review tools, and customer update workflows.
This is where Form.io belongs.
Form.io is not the sanctions database, fraud network, or identity bureau. It is the schema-driven form and API infrastructure that can sit around those systems when the customer needs to own the intake experience and the data path.
## **Why Static Forms Break KYC Workflows**
Static forms are comfortable until the onboarding workflow branches.
A retail deposit account does not collect the same evidence as a commercial lending application. A sole proprietor does not require the same entity structure as a multi-owner company. A low-risk domestic customer does not follow the same path as a higher-risk customer, foreign entity, trust, money-services business, or politically exposed person.
KYC onboarding software often has to branch by:
- individual versus business customer
- account or product type
- jurisdiction
- entity structure
- risk level
- ownership profile
- required documents
- missing or inconsistent information
- applicant role
- reviewer role
- periodic refresh or customer update
If those branches live in hard-coded forms, spreadsheets, PDFs, or ad hoc portal logic, the onboarding workflow becomes brittle. Compliance teams cannot change requirements cleanly. Developers cannot route data consistently. Reviewers inherit partial records. Customers get asked for the wrong information.
The stronger model is a governed intake schema: the form defines the data structure, validation, conditional logic, submission record, API handoff, and change path.
That is the Form.io argument.
## **What A KYC Intake Layer Should Provide**
The form layer behind KYC onboarding software should be evaluated as infrastructure, not as a decorative front end.
### **Dynamic Forms And Validation**
KYC intake should adapt to the customer, product, jurisdiction, entity type, and risk profile.
The platform should support [conditional logic and validation](https://form.io/features/form-conditional-logic-form-validation/), reusable components, calculated values, required evidence, document upload fields, consent language, and validation rules. The goal is not to make a long form look nicer. The goal is to collect the right information before the workflow reaches verification, review, or downstream systems.
### **Structured Submission Records**
For KYC, a submitted form is not just a message.
It is a record of what was asked, what was provided, which files were attached, what metadata came with the submission, and what later changed. Submission data needs to remain accessible for internal systems, reviewers, reports, and audit workflows.
Form.io's documentation describes forms as the structure that collects, validates, and stores user data, while the same form structure defines a backend API for managing and accessing submitted data ([Form.io docs](https://help.form.io/userguide/forms)). That structure matters when KYC data needs to move beyond a form inbox.
### **API Handoff To Verification And Core Systems**
KYC onboarding almost always depends on other systems.
Data may need to move into identity verification providers, sanctions or PEP screening services, CRM, core banking, lending systems, document management, case management, data warehouses, notification tools, and compliance reporting.
For Form.io, the strongest claim is architectural: every form, resource, submission, and project is accessible through a REST API, with predictable endpoints and submission paths that developers can connect to other systems ([data integration tools](https://form.io/features/data-integration-tools-for-enterprise-forms/)). Webhook actions can also send submission payloads to external endpoints when events occur.
That does not mean Form.io ships every KYC vendor integration out of the box.
It means teams can build the intake and handoff layer around the verification tools they choose.
### **Role-Based Access**
KYC data is role-sensitive.
Applicants, authorized representatives, relationship managers, compliance analysts, operations staff, auditors, developers, and administrators should not all see or edit the same data.
The intake layer should support [role and submission permissions](https://help.form.io/developers/roles-and-permissions.md) around forms, submissions, admin surfaces, and review workflows. This matters because KYC onboarding often blends customer-facing and internal workflows. One weak permission model can turn a controlled process into an overexposed one.
### **Revisions And Audit Logs**
Regulated onboarding workflows need history.
If a customer updates business ownership details, a reviewer changes a risk classification, a required field is added, or an administrator modifies access, the organization needs to know what happened.
Form.io describes two complementary logging systems: Submission Revisions for field-level submission changes and Server Audit Logging for system activity such as form access, authentication, and API-level data modifications ([audit trail capabilities](https://form.io/features/log-forms-complete-audit-trail/)). Those capabilities fit KYC intake because the evidence trail is part of the workflow, not an afterthought.
Availability and configuration still matter. Teams should confirm which modules, settings, and license terms apply before making compliance commitments.
### **Deployment And Data Boundary Control**
KYC onboarding touches sensitive personal and business information.
Some financial-services teams can use hosted tools without issue. Others need stricter control over environment, authentication, database, file storage, network access, logging, and vendor exposure.
That is where [self-hosted forms](https://form.io/features/self-hosted-forms-for-enterprise/) or customer-controlled deployment becomes part of the buying decision. Form.io is strongest when the intake layer needs to live inside the customer's architecture rather than as a disconnected third-party form surface.
## **How Form.io Fits Beside KYC Verification Vendors**
The right architecture is often not Form.io instead of a KYC vendor.
It is Form.io around the KYC vendor.
A financial-services team might use Form.io to build an [embedded onboarding flow](https://form.io/features/drag-and-drop-form-builder-apis/) that collects customer and entity data, validates required fields, captures documents, stores submissions, applies role-based access, and exposes the submission through APIs. The same workflow can then call identity verification, document verification, sanctions screening, fraud, CRM, or core system services.
That division of responsibility is clearer and more credible:
**Layer****What It Does****Typical Fit**KYC verification providerIdentity proofing, document checks, sanctions or PEP screening, KYB data, fraud signalsUse when verification intelligence and coverage are the core needCLM or onboarding suiteCases, queues, lifecycle workflows, risk review, remediation, dashboardsUse when the institution needs a broad onboarding operating systemForm.io intake infrastructureEmbedded forms, structured submissions, generated APIs, permissions, revisions, audit trails, workflow handoff, self-hosted deploymentUse when the team needs to own the intake layer inside its product and systemsThis distinction also keeps the compliance claim honest.
Form.io can support regulated KYC onboarding controls. It does not make an organization compliant by itself. It does not replace AML policy, compliance staff, model validation, legal review, sanctions data, transaction monitoring, or the specialized identity providers that verify people and businesses.
It gives teams the form/application layer those systems need to receive clean, structured, governed intake data.
## **KYC Onboarding Software Evaluation Checklist**
When evaluating KYC onboarding software, ask who owns each part of the workflow.
**Evaluation question****Why it matters****What to check**Who owns the intake schema?KYC requirements change by customer type, product, jurisdiction, and risk profileForm definitions, reusable components, conditional logic, validation, versioningCan the workflow collect documents and evidence?Verification and review often depend on file evidenceSecure uploads, metadata, submission association, downstream accessDoes the submission have an API?KYC data needs to move into verification, CRM, case, banking, lending, and reporting systemsREST APIs, webhooks, JSON submissions, authentication, retry/error patternsCan permissions be scoped by role?Applicants, reviewers, admins, and auditors need different accessForm permissions, submission permissions, own/all access, SSO role mappingIs the workflow auditable?Reviewers need to understand changes and decisionsSubmission revisions, form revisions, audit logs, timestamps, user identity, notesCan the system support ongoing updates?KYC and CDD are not always one-time eventsCustomer refresh flows, changed-information capture, reviewer routing, historical recordsCan the intake live inside your product?Customer onboarding often belongs inside a portal or applicationEmbedded renderer, white-label controls, developer-owned front endCan the environment be controlled?Some teams need strict data boundary and infrastructure controlSelf-hosted or customer-controlled deployment, database/storage options, logging integrationDoes the product overclaim compliance?Software supports controls; it does not replace legal obligationsClear scope, configuration details, module requirements, evidence of controlsThe checklist helps separate a strong verification tool from a strong intake platform.
Some buyers need both.
## **When A Dedicated KYC Vendor Is The Better Fit**
Use a dedicated KYC vendor when the primary need is verification intelligence.
That includes:
- identity document verification
- biometric or liveness checks
- sanctions, PEP, and adverse media screening
- KYB data and business registry checks
- beneficial ownership data services
- fraud network signals
- country-specific document coverage
- transaction monitoring or AML case management
Those are specialized capabilities. A form platform should not pretend to replace them.
The same is true for a full client lifecycle suite. If the institution needs enterprise case management, risk scoring, remediation workflows, onboarding dashboards, periodic refresh operations, and compliance-team queues in one packaged system, a CLM platform may be the better center of gravity.
Form.io becomes more relevant when the organization already has or plans to choose those systems, but still needs to own the form layer that feeds them.
## **Where Form.io Is The Better Fit**
Form.io is the better fit when the KYC onboarding workflow is also a product, integration, and governance problem.
That usually means:
- onboarding forms need to be embedded inside a customer portal or internal product
- the data model needs to be controlled by the application team
- submissions need to become API-accessible records
- KYC providers need to be called from the workflow rather than own the whole experience
- permissions need to be scoped across applicants, reviewers, admins, and service accounts
- form and submission changes need revision history
- audit logs need to feed operational or compliance tooling
- sensitive intake data needs to remain in customer-controlled infrastructure
- teams need one governed form layer across multiple onboarding use cases
That is the buyer who should evaluate Form.io as part of a KYC onboarding software stack.
A Trustpilot reviewer called Form.io a "powerful embedded form builder" and wrote that it was "seamlessly built into our B2B application" ([Trustpilot](https://www.trustpilot.com/review/form.io)). That is a small proof point, but it points at the right fit: Form.io is strongest when developers and regulated teams need data management, integration, and control around forms, not just a hosted questionnaire.
## **Bottom Line**
KYC onboarding software is not one product category.
It is a stack.
Verification vendors help confirm identity, screen risk, and supply data. CLM platforms help manage onboarding cases and lifecycle operations. Form infrastructure governs the intake layer: what gets asked, how it is validated, where the submission lives, which systems receive it, who can access it, and what evidence remains when the process changes.
For financial-services teams, that layer deserves its own evaluation.
If the problem is buying verification coverage, choose a KYC provider. If the problem is owning regulated intake across products, portals, APIs, reviewers, audit trails, and customer-controlled infrastructure, evaluate Form.io as the form/application infrastructure around the KYC workflow.
## **FAQ**
### **What is KYC onboarding software?**
KYC onboarding software helps financial-services teams collect customer information, verify identity, assess risk, route exceptions, and preserve records during account opening or customer onboarding. The category can include identity verification tools, KYB providers, CLM platforms, and form/application infrastructure. Buyers should separate those layers before comparing vendors.
### **Is Form.io a KYC verification provider?**
No. Form.io is not an identity verification bureau, sanctions database, biometric provider, AML case-management system, or KYB data provider. It can provide the embedded form, submission, API, permissions, and workflow infrastructure around those services.
### **Where does Form.io fit in a KYC onboarding stack?**
Form.io fits at the intake and application-infrastructure layer. Teams can use it to build embedded onboarding forms, collect structured data, manage submissions, connect APIs and webhooks, scope access, preserve revisions, and deploy in customer-controlled environments. Dedicated verification vendors can still handle identity checks and screening.
### **Why are forms important in KYC onboarding?**
The form layer determines what information is collected, how it is validated, how it is stored, and how it moves into downstream systems. Weak forms create incomplete data, manual rework, inconsistent review paths, and poor audit evidence. In KYC workflows, form design is also data architecture.
### **What should financial-services teams look for in KYC intake software?**
Look for dynamic forms, conditional logic, document upload support, structured submissions, API access, webhooks, role-based permissions, revision history, audit logging, authentication integration, and deployment control. Also confirm what the product does not do, especially around legal compliance, AML policy, sanctions data, and identity verification.
### **Can Form.io help with beneficial ownership collection?**
Form.io can help teams build intake workflows that collect business entity and beneficial ownership information, validate required fields, store submissions, and route data to review or verification systems. It does not determine the legal obligation by itself. Teams should map fields and processes to current regulatory counsel and compliance requirements.
### **Can Form.io connect to KYC or AML vendors?**
Yes, Form.io is built for API-connected form workflows. Forms and submissions can be exposed through REST APIs, and webhook actions can send submission data to external systems. Teams still need to implement and govern the specific integration with their chosen KYC, AML, CRM, banking, or case-management systems.
### **Does Form.io make a financial institution compliant?**
No software makes a financial institution compliant on its own. Form.io can support regulated onboarding controls through structured intake, permissions, APIs, revisions, audit logging, and customer-controlled deployment. Compliance still depends on policy, configuration, monitoring, staff judgment, legal review, and the broader control environment.
### **When should a team choose a full KYC platform instead of Form.io?**
Choose a full KYC platform when the main need is identity verification coverage, fraud signals, sanctions screening, KYB datasets, adverse media, transaction monitoring, or packaged case workflows. Choose Form.io when the main need is to own the embedded intake layer and connect it to those specialized services.
### **Is self-hosting important for KYC onboarding software?**
It depends on the organization's risk posture, architecture, and regulatory environment. Some teams can use hosted KYC products. Others need more control over data, authentication, file storage, logging, network boundaries, and deployment. Form.io is relevant when customer-controlled infrastructure is part of the requirement.
### **How should teams start evaluating Form.io for KYC onboarding?**
Start by mapping the intake workflow: customer types, fields, documents, verification calls, exception paths, reviewer roles, submission records, audit needs, and downstream systems. Then evaluate whether Form.io can provide the governed form and API layer around the verification tools the organization already uses or plans to adopt.
[Build controlled onboarding workflows](/try-formio-for-free/) with Form.io.
# Typeform Alternatives for Self-Hosted and Regulated Teams
[  ](https://form.io/typeform-alternatives-self-hosted-compliance-bound/)Most searches for **typeform alternatives** start with a simple frustration: response limits, pricing, branding, or the one-question-at-a-time format.
Those are real reasons to compare tools. But they are not the whole decision.
If your forms collect regulated data, live inside a customer portal, support tenant-specific workflows, or need to connect directly to your application APIs, the better question is not "Which tool costs less than Typeform?" It is "Which layer of the system should own this form?"
## **Key takeaways**
- Typeform is strong for polished conversational forms, surveys, quizzes, and lead capture.
- Many Typeform alternatives compete on price, free response limits, design flexibility, or survey features.
- Self-hosted alternatives matter when the buyer needs more control over where response data lives.
- Compliance-bound teams need more than a form UX: they need permissions, auditability, deployment control, data routing, and clear responsibility boundaries.
- Form.io is a better fit when forms become embedded, API-backed application infrastructure rather than standalone surveys.
## **Quick comparison: which Typeform alternative fits the job?**
## **Scenario****Better-fit category****Examples to evaluate**Marketing forms, lead capture, quizzes, landing pagesPresentation-first form buildersTypeform, Tally, Fillout, JotformProduct feedback, NPS, CSAT, in-app surveysSurvey and feedback platformsFormbricks, SurveyMonkey, Qualtrics, SurveySparrowOpen-source or privacy-first survey collectionSelf-hosted survey toolsFormbricks, LimeSurvey, HeyForm, OpnFormRegulated intake, portals, claims, onboarding, internal workflowsForm infrastructureForm.ioCustomer-facing SaaS form buildingEmbedded and white-labeled form infrastructureForm.ioForms that need generated APIs and submission permissionsSchema-driven form/API platformsForm.io**Why teams look for Typeform alternatives**
Typeform has a clear job. It helps teams create polished, conversational forms without building a custom form experience from scratch. For many marketing, survey, quiz, and customer-feedback workflows, that is enough.
But the market around Typeform alternatives has grown because buyers often hit one of five limits.
First, pricing and response limits can become frustrating. Tally positions itself directly against Typeform by emphasizing unlimited forms and responses on its free plan, while Typeform's free plan is limited to 10 monthly responses in Tally's comparison.
Second, some teams want more layout flexibility. Fillout argues that Typeform is recognizable and polished, but more opinionated, while Fillout gives teams multi-page forms with more control over page structure and integrations.
Third, privacy and self-hosting are becoming a separate buying category. Formbricks frames itself as an open-source Typeform alternative with a self-hosted Community Edition for teams that want more control over data ownership.
Fourth, regulated teams need clearer data boundaries. Typeform publishes security, data-handling, and compliance guidance, including a compliance article stating that Typeform can provide a BAA for customers on its Enterprise plan. Its help center also documents that Typeform data is hosted on AWS, with main servers in Virginia and EU data hosting available for Enterprise and Growth Custom customers.
Fifth, some teams discover that the form is not really a survey anymore. It is intake. It is workflow. It is a record. It is a customer-facing feature. It is part of the application.
That fifth case is where Form.io belongs in the conversation.
## **The three types of Typeform alternatives**
The mistake is treating all Typeform alternatives as one category.
They are not.
### **1. Presentation-first form builders**
These tools compete with Typeform on form creation speed, design, free tiers, templates, payment collection, embeddability, and basic automation.
They are often the right answer when the form is a marketing asset or a lightweight business workflow. If the team needs a better-looking contact form, a free survey, a quiz, a registration form, or a lead-capture flow, a presentation-first tool may be enough.
This category is where Tally, Fillout, Jotform, Paperform, and similar tools usually compete.
The tradeoff is that the form usually remains a standalone tool. It may integrate with the rest of the stack, but it does not become the infrastructure layer that governs submissions, permissions, APIs, tenants, and deployment environments.
### **2. Privacy-first survey and feedback platforms**
These tools compete on self-hosting, open-source access, feedback workflows, product surveys, NPS, CSAT, in-app micro-surveys, and user research.
Formbricks is a good example. Its Typeform-alternative page emphasizes open source, self-hosting, link surveys, in-app micro-surveys, pop-up surveys, Dockerized deployment, and an open API.
That is a strong fit when the main object is feedback.
But feedback is not the same as application intake. A survey platform may own responses, contacts, segments, and feedback analytics. It may not be designed to become the form/API layer inside a regulated portal, insurance claim workflow, government service, or B2B SaaS product.
### **3. Form infrastructure platforms**
This is the category most Typeform-alternative lists miss.
Form infrastructure is for teams whose forms need to do more than collect answers. These forms need to render inside an application, validate structured data, create submission records, expose APIs, route data to internal systems, respect permissions, survive audits, and remain under the customer's deployment control.
That is the Form.io case.
Form.io describes itself as a self-hosted developer productivity platform for building forms, APIs, and workflows. Its "How Form.io Works" page explains that the drag-and-drop builder creates forms and APIs together, that every form and resource has an automatically generated REST API, and that the platform can be embedded in the customer's own environment ([How Form.io Works](https://form.io/how-it-works/)).
When the buyer needs that layer, Typeform alternatives should not be judged only by design, templates, or monthly response caps.
## **Where self-hosting changes the decision**
Self-hosting is not automatically required. Plenty of teams are better served by a managed SaaS form tool.
But self-hosting changes the evaluation when forms collect sensitive data, connect to internal systems, support regulated workflows, or sit inside a product your team owns.
IBM's 2025 Cost of a Data Breach report puts the global average cost of a data breach at $4.4 million ([IBM Cost of a Data Breach 2025](https://www.ibm.com/reports/data-breach)). That is not a form-builder statistic, and it should not be used that way. It is a reminder that data collection boundaries have real financial and operational consequences.
Data-control expectations are also moving into mainstream architecture decisions. BARC's 2026 data sovereignty survey found that 76% of respondents expect data sovereignty to become more important, which helps explain why "where does this form data live?" is no longer a niche legal question ([BARC data sovereignty survey](https://barc.com/news/data-sovereignty-2026-survey/)).
Verizon's 2026 DBIR summary says 31% of breaches now start with software vulnerabilities and 48% involve ransomware ([Verizon DBIR 2026](https://www.verizon.com/business/resources/reports/dbir/)). Again, that does not mean a form tool causes the risk. It means buyers should care about where software runs, how it is patched, how access works, and who controls the data path.
For a lightweight survey, a hosted form tool can be perfectly reasonable.
For regulated intake, the questions change:
- Where is submission data stored?
- Can the platform run in our environment?
- Can fields be encrypted where needed?
- Can permissions apply to submissions, not just workspace users?
- Can audit logs show what happened?
- Can dev/test/prod environments support controlled changes?
- Can forms connect to our APIs without routing sensitive data through unnecessary third parties?
Those are infrastructure questions.
## **Why Form.io is different from most Typeform alternatives**
Form.io is not trying to be a prettier Typeform clone.
That matters.
Form.io is built around the idea that a form can be a governed schema. The form definition can drive rendering, validation, submitted data shape, generated API endpoints, permissions, and workflow actions.
The practical difference shows up in four places.
### **Forms and APIs are connected**
In Typeform and many alternatives, the form is mainly a collection surface. You can export data, trigger integrations, or connect webhooks, but the form itself is not usually the application data layer.
Form.io's model is different. Its builder and platform center on JSON-powered forms and APIs. Form.io's own product documentation says every form and resource has an automatically generated REST API associated with it.
That is useful when every new form would otherwise require engineering work to create endpoints, validation, storage, and integration behavior.
### **Deployment can stay inside your environment**
Typeform and many alternatives are hosted SaaS products. Some newer alternatives offer self-hosting, especially in the open-source survey category.
Form.io's self-hosted story is more infrastructure-oriented. Its configuration-based pricing page describes API server environments, enterprise projects, PDF server options, dev/test/prod configurations, self-hosted databases, and security compliance features in API Plus configurations ([Form.io configuration-based pricing](https://form.io/configuration-based-pricing/)). Its self-hosted enterprise forms page also frames the Developer Portal, forms, projects, permissions, and submissions as running inside the customer's own environment ([self-hosted forms for enterprise](https://form.io/features/self-hosted-forms-for-enterprise/)).
That is a better match when the buyer is not allowed to treat form data as a casual SaaS export.
### **Governance is tied to the form layer**
Regulated forms often need more than account-level access control. Teams may need form-level permissions, submission-level access, field-level encryption, revision history, action logs, submission revision logs, and audit evidence.
Form.io's security-compliance materials describe advanced audit logging, action logs, form revisions, submission revision logs, submission collections, field-level encryption, and container security scanning as part of its security module and API Plus feature set ([Form.io secure forms compliance readiness](https://form.io/features/secure-forms-compliance-readiness/)).
That is also how broader security frameworks talk about control. NIST SP 800-53 treats security and privacy controls as part of organization-wide risk management, not as isolated software checkboxes ([NIST SP 800-53 Rev. 5](https://csrc.nist.gov/pubs/sp/800/53/r5/upd1/final)).
That does not mean every Form.io buyer needs every module. It does mean the platform is designed for teams that need those questions answered at the form infrastructure layer.
### **Embedded form building is a platform feature**
Some Typeform alternatives let you embed a form. That is not the same as embedding a governed form-building capability inside your own product.
Form.io can support teams that need form rendering and form building inside their application experience, including white-labeled and tenant-aware scenarios. Its Enterprise Form Builder Module is positioned for exposing a customized form-building experience inside the customer's own application ([Enterprise Form Builder Module](https://form.io/enterprise-form-builder-module/)).
That is where Form.io becomes relevant to SaaS platforms, government portals, healthcare products, insurance workflows, and financial services onboarding.
## **A practical shortlist of Typeform alternatives**
### **Choose Typeform when presentation matters most**
Typeform still makes sense when the primary goal is polished conversational UX, surveys, quizzes, lead capture, and a familiar visual form-building experience. If the form is not regulated, not deeply embedded, and not part of your product architecture, Typeform may be enough.
### **Choose Tally when free limits are the issue**
Tally is a strong fit when the buyer wants a simpler and more generous free form builder. Its comparison page emphasizes unlimited forms, unlimited responses, conditional logic, file uploads, payments, and API access on lower-cost or free tiers.
### **Choose Fillout when the issue is flexibility**
Fillout is worth evaluating when the buyer wants modern form building, stronger free response limits, database-style integrations, multi-page forms, and more layout flexibility than Typeform's one-question-at-a-time format.
### **Choose Formbricks when the job is self-hosted surveys**
Formbricks is a strong fit when the buyer wants open-source, self-hosted surveys, product feedback, NPS, CSAT, website surveys, or in-app micro-surveys. It is especially relevant when the team wants a privacy-first Typeform alternative but still thinks in survey and feedback terms.
### **Choose Form.io when forms become infrastructure**
Form.io is the better fit when the buyer needs forms to become part of the application stack: embedded rendering, generated APIs, submission storage, permissions, actions, security/compliance modules, self-hosted deployment, and controlled form lifecycle.
A Form.io customer proof point from Safety Mojo captures the reason this matters: "Form.io cleans up all the dirty work and does it for you" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)). On G2, another reviewer points to "the level of customization that can go into every form" ([Form.io reviews on G2](https://www.g2.com/products/form-io/reviews)). That is the value when the dirty work is not just building a form, but keeping forms, data, APIs, and workflow behavior aligned.
The scale proof points point in the same direction. Form.io's publicplan case study describes support for more than 400 services and 1,000+ forms in a German public-sector context, while the TauRes case study reports an estimated 50% reduction in data-processing workload after standardizing acquisition workflows around Form.io ([publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/), [TauRes case study](https://form.io/case-studies/taures-case-study-data-acquisition-and-analysis/)).
## **Decision framework**
Ask these questions before choosing a Typeform alternative:
**Question****If yes, look at**Do we mainly need a better free plan or lower-cost form builder?Tally, Fillout, JotformDo we mainly need surveys, NPS, CSAT, or product feedback?Formbricks, SurveyMonkey, QualtricsDo we need open-source or self-hosted survey collection?Formbricks, LimeSurvey, HeyFormDo forms need to live inside our application or portal?Form.ioDo submissions need generated APIs, permissions, and audit-relevant controls?Form.ioDo customers or tenants need to build forms inside our product?Form.ioDo we need a simple marketing form this week?Typeform or a presentation-first alternativeThe strongest decision comes from naming the job.
If the job is presentation, choose a presentation-first tool.
If the job is feedback, choose a survey platform.
If the job is governed application intake, choose form infrastructure.
## **FAQ**
### **Which Typeform alternative should you choose?**
There is no single universal Typeform alternative. Tally and Fillout are strong for lower-cost form building, Formbricks is strong for open-source and self-hosted surveys, and Form.io is stronger when forms need to become embedded, API-backed application infrastructure.
### **Is there a self-hosted Typeform alternative?**
Yes. Formbricks is a strong self-hosted survey alternative. Form.io is also self-hosted, but it solves a different problem: governed forms, generated APIs, submissions, permissions, and workflow behavior inside customer-controlled environments.
### **Is Typeform good for regulated data collection?**
Typeform publishes security and compliance materials and says it can provide a BAA for Enterprise customers in relevant HIPAA contexts. Regulated teams should still verify hosting, data residency, contractual scope, retention, access control, audit, and integration requirements before choosing any hosted form tool.
### **When is Form.io a Typeform alternative?**
Form.io is a Typeform alternative when the real requirement is not just a nice form experience, but embedded forms, self-hosted deployment, generated APIs, submission records, permissions, and governed workflow infrastructure.
### **Is Form.io a survey tool?**
Form.io can collect survey-like data, but it is better understood as a form and API platform. It is usually a stronger fit for application forms, portals, regulated intake, workflow forms, and customer-facing form infrastructure than for simple standalone surveys.
### **Which Typeform alternative fits product feedback?**
Formbricks is worth evaluating for product feedback, in-app micro-surveys, NPS, CSAT, and privacy-first survey workflows. It is designed around feedback collection rather than general form infrastructure.
### **Which Typeform alternative fits embedded forms?**
Form.io is usually the better fit when forms need to be embedded into a customer-facing application and governed as part of the product architecture rather than embedded as standalone survey widgets.
### **Which Typeform alternative fits compliance-bound workflows?**
It depends on the compliance requirement. A hosted tool may be enough for low-risk workflows with the right contracts and settings. For stricter control over deployment, storage, APIs, permissions, and audit evidence, Form.io is often the more relevant category fit.
### **Can Form.io replace Typeform?**
Form.io can replace Typeform when the organization needs self-hosted, embedded, API-backed form infrastructure. It may be too much platform for a simple marketing survey, quiz, or event-registration form.
### **What should developers compare before choosing?**
Developers should compare hosting model, schema ownership, API behavior, validation, permissions, submission storage, audit needs, SDK/rendering model, deployment environments, and whether the form needs to live inside an application users already trust.
## **Final recommendation**
For simple campaigns and surveys, choose the form tool that gets the job done with the least operational burden.
For feedback programs, choose a survey platform with the right data and research workflow.
For regulated intake, embedded portals, tenant-aware SaaS forms, and form-driven application workflows, evaluate Form.io as infrastructure, not as another prettier form builder.
The distinction matters because a form is sometimes just a form. But when the data, API, permissions, workflow, and deployment boundary all depend on it, the form has become part of the architecture.
[Try Form.io for free](https://form.io/try-formio-for-free/) to see how self-hosted forms, generated APIs, and governed submission workflows fit inside your application environment.
# Jotform Alternative for Regulated Teams: When Hosted Forms Are Not Enough
[  ](https://form.io/alternatives-to-jotform-regulated-industries/)Jotform is a strong hosted form builder when the job is to create a form quickly.
That is not the same as choosing form infrastructure for regulated work.
If your forms collect sensitive data, drive downstream decisions, live inside a product, or need to satisfy audit and security teams, the real question is not only which builder is easiest. It is which platform gives you enough control after the form is submitted.
## **The Short Version**
Most Jotform alternative lists compare templates, pricing, free plans, conditional logic, integrations, and form design.
Those things matter. They just do not settle the decision for regulated teams.
If your use case is a marketing form, event registration form, internal survey, or lightweight intake workflow, a hosted builder may be the right answer. If your use case is healthcare intake, government services, insurance claims, financial onboarding, customer portals, or embedded SaaS workflows, you need to evaluate a different layer.
For those teams, a serious Jotform alternative should be judged by:
- where the platform runs
- who controls submission data
- how authentication and permissions work
- whether forms generate APIs
- whether form and submission changes are auditable
- whether the form builder can be embedded and white-labeled
- whether the platform can fit into the systems you already govern
That is where Form.io belongs in the conversation.
Form.io is not the fastest option for a one-off hosted form. It is the stronger fit when forms become part of application infrastructure.
## **Why Most Jotform Alternative Lists Miss the Regulated Buyer**
Most search results for `jotform alternative` are written for broad software shoppers.
They usually ask familiar questions:
- Which tool is cheaper?
- Which one has better templates?
- Which one is easier for a nontechnical team?
- Which one has the most integrations?
- Which one has the cleanest form design?
That comparison is useful for simple workflows. It is incomplete for regulated ones.
A hospital intake workflow, public-sector application, insurance claim, KYC onboarding flow, or embedded customer portal cannot be evaluated only by front-end form features. The submitted data becomes part of a larger system. It may need to be retained, corrected, audited, routed, exported, approved, signed, versioned, or tied to a specific policy decision.
That moves the decision out of the form-builder category and into the architecture layer.
The right question becomes: can the form platform respect the control surface around the form?
## **The Real Buying Question: Hosted Builder or Controlled Infrastructure?**
There are two different jobs hiding behind the same keyword.
The first job is form creation. A team needs to publish a polished form, collect responses, and send data somewhere useful. Hosted builders are good at this. They reduce setup time, give nontechnical users a friendly workspace, and make common forms easy to ship.
The second job is governed data collection. A team needs forms to run inside a larger application boundary, use existing authentication, expose durable APIs, preserve record history, and support audit evidence when something changes.
Those are not the same job.
The first job rewards speed. The second rewards control.
That does not make hosted builders bad. It means regulated teams need to know when the category changes.
## **Where Hosted Form Builders Work Well**
A hosted form builder can be the right choice when the workflow is narrow and the organization accepts the vendor-managed model.
Use a hosted builder when:
- the form is standalone
- the data does not need to stay inside your own environment
- the workflow can live in the vendor's dashboard
- standard integrations are enough
- nontechnical creation matters more than developer control
- the form does not need to become part of a product or governed application
This is why broad Jotform alternative lists often recommend tools like Typeform, Google Forms, Tally, Fillout, Cognito Forms, Formstack, FormAssembly, or other hosted builders. For simple forms, those recommendations can make sense.
Regulated teams should be more careful.
The moment the form sits inside a controlled business process, the tool has to answer questions that template libraries cannot answer.
## **Where Regulated Teams Need More Than a Hosted Builder**
Regulated workflows usually fail at the edges.
The form itself looks fine. The problem appears after submission.
Who can see the data? Which system owns the record? What happens when the form schema changes? Can a historical submission still be understood against the form version that captured it? Did the webhook fire? Who changed the claim amount, diagnosis note, eligibility field, or approval status? Can the organization prove it later?
These are ordinary questions in healthcare, government, finance, education, insurance, and other regulated settings.
They also map directly to formal control programs. NIST SP 800-53 Rev. 5 organizes security and privacy controls across families such as [Access Control, Audit and Accountability, Identification and Authentication, Incident Response, Risk Assessment, and System and Communications Protection](https://csrc.nist.gov/pubs/sp/800/53/r5/upd1/final). HHS says the [HIPAA Security Rule](https://www.hhs.gov/hipaa/for-professionals/security/laws-regulations/index.html) establishes national standards for electronic protected health information and requires administrative, physical, and technical safeguards. A form platform used in regulated work does not sit outside those concerns. It becomes one of the places those concerns show up.
IBM's 2025 Cost of a Data Breach report gives the risk scale. IBM reports a [global average breach cost of $4.4 million](https://www.ibm.com/reports/data-breach), and also reports that 63% of organizations lacked AI governance policies to manage AI or prevent shadow AI. Verizon's [2026 Data Breach Investigations Report](https://www.verizon.com/business/resources/reports/dbir/) adds another useful warning: software vulnerabilities now start 31% of breaches, which is why regulated teams should evaluate the form platform as software infrastructure, not only as a form-design surface.
Forms are one of those systems.
## **What a Regulated Jotform Alternative Should Prove**
A regulated team should not start with "Which form builder is easiest?"
Start with the control requirements.
### **Deployment Boundary**
Where does the platform run?
For some teams, vendor-managed SaaS is acceptable. For others, sensitive data must remain inside a private cloud, on-premise environment, government-approved network, customer-controlled database, or specific regional boundary.
That is one of Form.io's clearest differences. Form.io's [self-hosted forms for enterprise](/features/self-hosted-forms-for-enterprise/) model is built so the platform can deploy inside environments the customer controls. The same core surfaces, including form builder, REST API generation, submission handling, and renderer libraries, can run within the customer's infrastructure.
This matters because deployment is not just an IT preference. It shapes data residency, incident response, logging, backup strategy, access review, and compliance ownership.
### **Data Ownership and Submission Control**
The form response is not just a row in a vendor dashboard.
For regulated teams, a submission may become a patient record, claim record, case file, intake record, eligibility input, identity artifact, or workflow event. The platform needs to fit the system that owns that record.
Form.io's architecture stores forms, resources, submissions, users, and project data as JSON documents in the customer's MongoDB or MongoDB-compatible database. That document model is part of why Form.io can treat form definitions and submission records as application data rather than isolated form entries.
If your team needs application-owned data, this distinction matters more than builder polish.
### **Authentication and Permissions**
Regulated forms rarely have one kind of user.
A healthcare intake flow may involve patients, providers, administrators, support staff, and compliance reviewers. A government service workflow may involve applicants, case workers, supervisors, auditors, and external systems. A SaaS product may need tenant admins, end users, implementation teams, and internal support roles.
The platform has to respect those boundaries.
Form.io's [roles and permissions](/features/forms-for-teams/) model is built around controlling who can create forms, view submissions, modify data, manage projects, and interact with APIs. That matters when the same form infrastructure supports different departments, customers, tenants, or workflow stages.
For regulated teams, permissions are not an admin convenience. They are part of the evidence trail.
### **Generated APIs**
Many hosted form tools expose APIs. That does not mean the form is the API contract.
The stronger architecture is schema-driven: the same definition that renders the form also defines the submission structure and API behavior around it. Form.io's [form from JSON](/features/form-from-json/) model gives teams a JSON-based form definition that can render interfaces and support generated APIs from the same source.
This is useful when forms feed applications, not just spreadsheets.
It lets developers treat forms as governed application surfaces: forms, resources, submissions, validation, webhooks, and workflow actions can be reasoned about together instead of being scattered across a visual builder, a separate API layer, and custom glue code.
### **Audit Trails and Revisions**
Regulated teams need to know more than whether a form was submitted.
They need to know what changed.
Form.io's [complete audit trail](/features/log-forms-complete-audit-trail/) capabilities distinguish between submission revisions and server audit logging. Submission revisions track field-level changes to submitted data. Server audit logging captures system activity such as authentication, form access, API requests, and data modification events.
That distinction matters. An auditor may need to know that a submission was created by one user, modified by another, and later viewed through a specific role or project context. A support team may need to know whether a webhook ran. A compliance team may need to know which form revision captured a historical record.
For financial services, this is not an abstract preference. The [FTC Safeguards Rule](https://www.ecfr.gov/current/title-16/chapter-I/subchapter-C/part-314) requires financial institutions to monitor and log authorized-user activity and detect unauthorized access, use, or tampering with customer information. It also creates retention and change-management expectations around customer information systems.
Form.io's [secure forms compliance readiness](/features/secure-forms-compliance-readiness/) capabilities also include advanced audit logging, action logs, form revisions, submission revision logs, submission collections, and container security scanning as part of the Security Module.
That is a different category of answer than "the form has an activity log."
### **Embedded and White-Labeled Use**
Many regulated forms do not belong on a third-party hosted page.
They belong inside a patient portal, citizen service portal, claims application, financial onboarding flow, education system, or B2B SaaS product.
That creates two requirements at once: the form needs to feel native to the product, and the form data needs to move through the product's security and workflow model.
Form.io is designed for embedded use. Developers can render forms inside their own applications, use the platform's APIs, and let business users modify schemas after the application is in place. For software teams, this is often the useful compromise: developers own the system boundary, while business teams can still manage many form changes without reopening every application ticket.
## **Comparison Table: Jotform Alternative Categories**
**Category****Best fit****Strength****Risk for regulated teams**Hosted no-code form builderSimple forms, surveys, registration, marketing captureFast setup and low technical burdenData and workflow live primarily in the vendor-managed modelHosted enterprise form suiteBusiness teams that need more compliance features and admin controlBetter security, SSO, compliance options, supportMay still be separate from the customer's application infrastructureIndustry-specific form toolNarrow healthcare, education, legal, or government workflowsBetter fit for one vertical's common use casesCan be too narrow for cross-department or product-embedded workflowsCustom-built formsUnique internal systems with strong engineering ownershipMaximum controlExpensive to build, secure, document, version, and maintainSelf-hosted form infrastructureRegulated teams where forms are part of real applicationsDeployment control, APIs, permissions, revisions, audit evidence, embedded useRequires technical ownershipThe last row is where Form.io fits.
It is not the right answer for every team looking for a Jotform alternative. It is the right answer when the team has outgrown the assumption that forms are standalone assets.
## **Why Form.io Is Different From a Normal Form Builder**
Form.io is easier to understand when you stop treating it as a lighter or heavier version of a hosted form builder.
It is infrastructure for forms and the APIs around them.
The visual builder creates schemas. The renderer turns those schemas into forms inside applications. The API server manages forms, resources, submissions, permissions, projects, and actions. The self-hosted deployment model lets the customer run that infrastructure inside their own environment.
That is why Form.io's own guidance is direct about fit. In Form.io's article on [why teams should not use Form.io without a developer team](https://form.io/why-you-shouldnt-use-formio-if-you-dont-have-a-dev-team/), the product is framed as infrastructure software for software developers building custom applications, not a simple form builder for nontechnical users. In other words, it is the wrong choice if a marketing team needs a simple form live this afternoon, and the better choice if a software team needs forms to behave like governed application infrastructure.
That honesty is valuable.
The buyer who only wants speed should not be pushed into infrastructure. The buyer who needs control should not be pushed into convenience software that will fail later.
## **Proof That This Is a Real Deployment Problem**
This is not theoretical positioning.
Form.io's public case-study library includes publicplan GmbH, where the project supported [more than 400 public-sector services and 1,000+ forms](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/) with strict standards and a short timeline. That kind of workload is not a normal contact-form problem. It is a repeatable public-service infrastructure problem.
The same pattern shows up in customer sentiment. A Trustpilot reviewer described Form.io as useful for both integration and standalone use and praised support when users get stuck ([Trustpilot](https://www.trustpilot.com/review/form.io)). The wording is simple, but the integration point is doing real work. Regulated teams are rarely buying a form in isolation. They are buying a form layer that has to connect to the rest of the system.
## **When Form.io Is the Wrong Jotform Alternative**
Form.io is not the right replacement if the team wants the fastest possible hosted form with the least technical setup.
Choose a simpler hosted builder when:
- the form is temporary
- the data is low risk
- the workflow is not part of a product
- the team does not have developers available
- vendor-managed hosting is acceptable
- the organization does not need custom API, identity, or audit architecture
That is not a failure case. It is buyer fit.
For simple forms, infrastructure can be too much.
## **When Form.io Is the Right Jotform Alternative**
Form.io becomes the stronger answer when the form is part of the system.
That usually means one or more of these conditions is true:
- submission data must stay inside a controlled environment
- forms are embedded in a customer-facing application
- different users need different permissions
- submissions need to become application records
- the team needs APIs generated from form definitions
- changes to forms and submissions need revision history
- workflows depend on webhooks, actions, approvals, or integrations
- the organization needs audit evidence after submission
- the platform must support multiple teams, tenants, projects, or environments
These are the use cases where "easy form builder" becomes too small a category.
For those teams, Form.io's advantage is not that it hides complexity. It is that it gives the team places to put the complexity where it belongs: deployment, schema, API, permissions, revisions, audit logs, workflow actions, and application integration.
## **Key Takeaways**
- A broad Jotform alternative list is useful for simple form-building needs.
- Regulated teams need to evaluate deployment boundary, data ownership, permissions, APIs, auditability, and embedded use.
- Hosted builders can work when the form is standalone and vendor-managed storage is acceptable.
- Form.io is strongest when forms become application infrastructure inside customer-controlled environments.
- The right choice depends less on builder polish and more on what must happen after the form is submitted.
## **FAQ**
### **What is the best Jotform alternative for regulated teams?**
The best Jotform alternative depends on the control requirements. If the team only needs a hosted form with better pricing or templates, a simpler hosted builder may be enough. If the team needs self-hosting, APIs, permissions, audit trails, revisions, and embedded application workflows, Form.io is a stronger fit.
### **Is Form.io easier to use than Jotform?**
Not for simple hosted forms. Jotform is easier for nontechnical teams that need to create and publish forms quickly. Form.io is built for teams that need developer control, application integration, self-hosted deployment, generated APIs, and governance around forms and submissions.
### **When should a team avoid Form.io?**
Avoid Form.io when the form is simple, standalone, low risk, and needs to be created by a nontechnical user without developer involvement. Form.io expects technical ownership, especially for self-hosted deployments and production application integration.
### **Why would a regulated team outgrow a hosted form builder?**
Hosted form builders can become limiting when the workflow needs controlled data residency, internal authentication, custom permissions, API-driven records, audit logs, revision history, or direct embedding inside a product or portal. Those needs turn the form into part of the application architecture.
### **Does Form.io support self-hosted forms?**
Yes. Form.io can be deployed in customer-controlled environments, including cloud, private data center, and Docker-based deployments. That gives teams more control over where form infrastructure runs and how submission data fits their existing security boundary.
### **Does Form.io generate APIs from forms?**
Yes. Form.io's schema-driven model uses form and resource definitions to support REST API behavior around submissions, validation, resources, permissions, and workflow actions. That makes it useful when forms are interfaces into application data, not just hosted pages.
### **Is Form.io HIPAA compliant?**
Form.io provides technical capabilities that can support HIPAA-governed workflows in customer-controlled environments, but the customer remains responsible for its compliance program, configuration, policies, deployment controls, and business associate requirements.
### **Does a BAA make a form workflow compliant?**
No. HHS explains that [business associate contracts](https://www.hhs.gov/hipaa/for-professionals/covered-entities/sample-business-associate-agreement-provisions/index.html) define permitted uses, safeguards, breach reporting, access, amendment, accounting, subcontractor, and termination obligations. A BAA matters, but compliance also depends on how the workflow is configured, secured, monitored, and governed.
### **Why do audit trails matter for form submissions?**
Audit trails help answer who accessed data, who changed it, what changed, when it changed, and which workflow action ran. For regulated teams, that evidence can matter as much as the original submission.
### **Can Form.io be embedded inside a SaaS product?**
Yes. Form.io is designed for embedded application use. Developers can render forms inside their own applications, connect them to Form.io APIs, and let authorized business users manage form schemas after the product infrastructure is in place.
### **What should I ask before choosing a Jotform alternative?**
Ask where data is stored, who controls deployment, how permissions work, whether APIs are generated from the form schema, how revisions are handled, whether audit logs are available, and whether the form can live inside your own application or portal.
## **Build Regulated Form Infrastructure With Form.io**
If you only need a quick hosted form, choose the simplest tool that satisfies the job.
If your forms define application workflows, submission records, permissions, APIs, audit evidence, and deployment boundaries, choose infrastructure that respects that reality.
[Try Form.io for regulated form infrastructure](/try-formio-for-free/).
# Formbricks vs Form.io: Survey Tool or Form Infrastructure?
[  ](https://form.io/formbricks-formio-vs-formbricks-self-hosted-typeform-alternative/)Organizations looking for a self-hosted alternative to Typeform or a privacy-first feedback platform often compare Formbricks and Form.io. Both have open-source and self-hosted evaluation paths, but they solve fundamentally different problems.
Formbricks focuses on surveys, experience management, and product feedback. Form.io is designed as application infrastructure for forms, APIs, workflows, and enterprise governance, including agentic workflow patterns where governed forms and submissions need to stay connected to permissions, validation, actions, and audit evidence.
That distinction matters before the feature checklist begins. The question is not whether both products can build forms. It is whether the form is mainly a survey or part of the application architecture.
## **Key takeaways**
- Formbricks is best understood as an open-source experience management and survey platform for link surveys, website surveys, in-app surveys, email surveys, and customer feedback workflows.
- Form.io is best understood as form-driven application infrastructure: JSON-defined forms, generated APIs, submission data, permissions, workflow actions, self-hosted deployment, and governed patterns for agentic workflows.
- Formbricks is a credible choice when the buyer wants a self-hosted Typeform alternative or privacy-first feedback tool.
- Form.io is the better fit when forms need to be embedded in a product, reused across tenants, governed through submission-level permissions, exposed through APIs, managed across enterprise environments, or used as structured context for agentic workflows.
- The main question is not “Which one is open source?” It is “Does your form need to collect feedback, or does it need to become part of the application architecture?”
## **Quick comparison**
The comparison below summarizes the product jobs documented in Formbricks’ platform, API, self-hosting, and licensing docs and Form.io’s JSON schema, generated API, self-hosting, and embedded builder pages.
## **Decision area****Formbricks****Form.io**Primary jobOpen-source surveys and experience managementForm and API infrastructure for embedded, governed applications and agentic workflowsBest use caseFeedback, NPS, CSAT, product surveys, link surveys, in-app micro-surveysRegulated intake, customer-facing product forms, portals, workflow forms, schema-driven applications, and agentic workflow interfacesForm modelSurvey flows and question types for response collectionJSON schemas that define UI, validation, submission structure, and backend APIsAPI modelPublic Client API for survey interactions and Management API for surveys, contacts, responses, and webhooksForm and resource paths generate schema and submission endpointsEmbeddingWebsite, app, email, and link survey deliveryRenderer and builder embedded directly into customer-controlled applicationsGovernance centerSelf-hosting, privacy, survey data control, open-core packagingProject, form, and submission permissions; roles, actions, audit patterns, stages, and deployment boundariesBest buyerProduct, growth, customer experience, and feedback teams that need open-source surveysDevelopment teams building form-heavy products, portals, and enterprise workflowsWrong fit warningNot designed to be the form/API layer for every application workflowNot the lightest answer for simple surveys or one-off feedback forms**What Formbricks is good at**
Formbricks deserves a fair reading. Its official docs describe it as an open-source platform for collecting and analyzing feedback from customers, users, and employees through targeted surveys.
That is a real product category.
If your team needs NPS surveys, CSAT surveys, product feedback, onboarding feedback, churn surveys, website surveys, in-app micro-surveys, or link-based surveys, Formbricks is built for that motion. Its homepage frames the product around privacy-first experience management, feedback collection across websites and apps, and self-hosting when a team wants more control over data.
Its open-source form builder page also makes the category clear: unlimited forms, unlimited responses, open-source survey building, conditional logic, multi-language surveys, integrations, hidden fields, partial submissions, single-use links, and custom domains.
That matters because the Typeform-alternative search is not only about technical architecture. Many buyers really do want a better survey tool: more generous limits, more privacy control, self-hosting, open-source code, and enough product polish for feedback collection.
Formbricks has a strong claim there.
The question is what happens when the form is not mainly a survey.
## **What Form.io is good at**
Form.io is strongest when the form is not just a feedback surface, but part of the application contract. Its value shows up when a team needs JSON-defined forms, generated APIs, submission records, validation, permissions, workflow actions, audit patterns, and self-hosted deployment to stay aligned.
That includes regulated intake, customer portals, tenant-managed SaaS forms, healthcare and financial workflows, government services, insurance claims, and internal processes where the submitted record needs to remain explainable over time.
It also matters for agentic workflows. If an AI agent or human-in-the-loop workflow needs to ask for data, validate fields, route submissions, require confirmation, or operate inside an enterprise governance boundary, the form layer needs to be more than a survey delivery tool. Form.io gives developers a governed form and API layer that can become part of that workflow infrastructure.
So the Form.io category should appear early in the decision: it is not the survey tool in this comparison. It is the form infrastructure layer when forms, submissions, APIs, and workflow behavior need to be owned by the application.
## **What changes when a survey becomes application infrastructure**
A survey collects feedback. Application infrastructure carries business process.
That line gets blurry at first. A customer feedback form can become a support workflow. A product survey can feed account health. A compliance questionnaire can become an auditable record. A tenant-specific intake form can become a feature inside a SaaS platform. A public-facing form can become the first step in a case management workflow.
At that point, the evaluation changes.
The buyer is no longer asking only whether the tool can collect a response. The buyer is asking:
- Who owns the schema?
- What validates the submission?
- Which API receives and exposes the data?
- Can the form be embedded inside our product?
- Can customers build or modify their own forms inside our app?
- Can roles and permissions apply at the form and submission level?
- Can the same form move through development, test, and production?
- Can historical submissions remain explainable after form definitions change?
Those are Form.io questions.
Form.io’s [drag-and-drop form builder and APIs](https://form.io/features/drag-and-drop-form-builder-apis/) page describes the builder as a JSON schema editor that defines form UI, validation, the data model, and REST API endpoints together. That is the architectural difference.
Formbricks is strong when the workflow is survey-led. Form.io is strong when the form is a contract between the user interface, submitted data, backend API, permissions, and downstream process.
## **Survey flows vs schema contracts**
Formbricks is optimized around survey delivery. Its own Typeform-alternative page describes link surveys, in-app micro-surveys, pop-up surveys, Dockerized self-hosting, an open API, and open-source customization.
That is useful when the main asset is a survey.
Form.io starts from a different object: the form schema. Every Form.io form is a JSON document that defines the title, path, display mode, components, validation, conditional logic, and submission data shape.
That schema can render in an application, accept submissions, validate data, and create predictable API behavior. The form is not only a front-end artifact. It is the source of truth that connects rendering, validation, submission storage, and backend endpoints.
This matters when multiple systems need to trust the same form definition.
If the form is only a feedback survey, a survey-first platform is usually enough. If the form is a reusable business object across applications, tenants, workflows, and environments, the schema needs to carry more responsibility.
That is where Form.io’s model becomes more valuable.
## **API and data model comparison**
Formbricks has APIs, and the comparison should say that clearly. Its REST API documentation describes two API surfaces: a Public Client API for frontend survey interactions and a Management API for backend management tasks. The exposed methods include displays, responses, contacts, surveys, action classes, contact attributes, and webhooks.
That API surface fits a survey and feedback product.
Form.io’s API model is different because the form path and schema define the submission API itself. The [Forms from JSON](https://form.io/features/form-from-json-schema/) documentation explains that a form path can create endpoints for retrieving the schema and creating, listing, reading, updating, and deleting submissions.
That changes the center of gravity.
In Formbricks, the API helps manage and operate surveys. In Form.io, the form can define part of the application data layer.
For feedback collection, Formbricks’ model is sensible. For application intake, regulated submissions, onboarding flows, service requests, claims, eligibility workflows, or tenant-managed forms, Form.io’s generated form/submission API model is usually the more direct fit.
## **Embedding and white-labeling**
Formbricks can reach users in useful places: websites, apps, email, pop-ups, and links. That is exactly what a survey platform should do. For customer experience teams, that flexibility matters because feedback is most useful when it appears at the right moment in the product journey.
Form.io uses embedding for a different purpose.
The [Form.io open-source page](https://form.io/open-source/) explains that forms are rendered from JSON using Form.io renderers for frameworks such as Vanilla JavaScript, Angular, React, and Vue. The [Enterprise Form Builder Module](https://form.io/product-announcement/enterprise-form-builder-module/) goes further: it lets teams embed a customizable, white-labeled form-building interface directly into their own applications.
That is not the same as embedding a survey.
It means a SaaS platform, healthcare product, government portal, insurance system, or internal enterprise app can expose governed form creation to its users without sending those users into a separate form product. The application still controls navigation, authentication, permissions, branding, allowed components, data model, and workflow behavior.
That is a major distinction for platform teams.
If you want to ask users for feedback, Formbricks may be the cleaner answer. If your customers need to build and manage forms inside your product, Form.io fits the architecture more directly.
## **Self-hosting, licensing, security, and governance**
Do not reduce this comparison to “self-hosted vs not self-hosted.” Formbricks is a legitimate self-hosted option. Its self-hosting docs describe cloud hosting, free self-hosting, self-hosting with an Enterprise Edition license, Docker setup, one-click setup, migration, configuration, and integrations.
Formbricks’ license docs also give useful detail. The core source code is AGPLv3, while larger-team and enterprise functionality lives under a separate enterprise license. The Community Edition includes self-hosting for commercial purposes, unlimited surveys, unlimited responses, unlimited users, API access, SDKs, website and app surveys, webhooks, multi-language surveys, and integrations. Enterprise features include items such as teams and access roles, audit logs, SSO, two-factor authentication, contact management, quota management, and prioritized support, depending on the license configuration.
That is a strong open-source story, but buyers need to understand the packaging.
Open source and self-hosting are valuable. They are not the same thing as complete application governance.
GitHub’s 2025 Octoverse report shows why this nuance matters. It says 63% of all repositories are public or open source, while 81.5% of contributions happen in private repositories ([GitHub Octoverse 2025](https://github.blog/news-insights/octoverse/octoverse-a-new-developer-joins-github-every-second-as-ai-leads-typescript-to-1/)). Modern software teams often depend on open source while doing most operational work inside private, governed systems.
Form.io’s self-hosted model is built for that private operational side. Its [self-hosted forms for enterprise](https://form.io/features/self-hosted-forms-for-enterprise/) page describes Form.io as deployable infrastructure that can run in AWS, Azure, Google Cloud, private data centers, or local Docker-based environments. It also describes separate components such as Enterprise Server, PDF Server, Developer Portal, renderer libraries, deployment environments, file storage, database requirements, and dev/test/prod patterns.
The key point is not that Form.io is self-hosted and Formbricks is not. Both can be self-hosted.
The key point is what is governed inside that boundary.
Formbricks governs surveys, feedback, contacts, responses, and experience-management workflows. Form.io governs forms, resources, submissions, generated APIs, roles, permissions, actions, environments, and form lifecycle.
Those are different control surfaces.
## **Pricing basis and scale predictability**
Formbricks has a strong Community Edition story for survey teams: AGPLv3 core access, free self-hosting, unlimited surveys, unlimited users, and unlimited responses. Teams evaluating Enterprise Edition should verify response, feature, workspace, support, and private-fork requirements directly against the current license table.
Form.io’s pricing story is different.
The point is not that Form.io is cheaper in every scenario. The point is that the buying model is designed around configured form/API infrastructure. Form.io’s [configuration-based pricing](https://form.io/configuration-based-pricing/) page lists unlimited API calls, unlimited submissions, unlimited developers and form builders, and unlimited forms and resources in relevant enterprise configurations.
That difference matters when forms become a platform feature.
If every tenant, customer, department, agency, or product line can create forms, usage can grow in ways that are hard to forecast. A per-response survey model may be fine for customer feedback. A configuration-based infrastructure model may be a better fit when submissions, forms, builders, tenants, and APIs are part of the product architecture.
The buyer should ask what is scaling.
If survey responses are scaling, Formbricks may fit. If application forms, submitted records, generated endpoints, customer form builders, and environments are scaling, Form.io deserves closer evaluation.
## **Customer proof: when form infrastructure scale becomes real**
Form infrastructure arguments can sound abstract until the volume shows up.
Form.io’s public case-study pages describe a publicplan GmbH implementation supporting more than 400 services and 1,000+ forms, and a Safety Mojo implementation that Form.io says saved 6-12 months of development time. Those are Form.io-published examples, so they should be read as customer proof rather than independent analyst validation. The Safety Mojo page also includes the customer proof line, “Form.io cleans up all the dirty work and does it for you” ([publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/), [Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)).
Those examples point to the real Form.io use case.
The hard part at that scale is not drawing a field. It is keeping the form, schema, submission record, API behavior, permissions, environment boundary, and downstream workflow aligned as requirements change.
IBM’s 2025 Cost of a Data Breach report puts the global average breach cost at $4.4 million and says 63% of organizations lacked AI governance policies ([IBM Cost of a Data Breach 2025](https://www.ibm.com/reports/data-breach)). That is not a form-specific statistic, and it should not be treated as one. It is a reminder that data workflows and governance boundaries are not minor implementation details when forms collect sensitive or operationally important data.
For teams handling simple feedback, that level of infrastructure may be unnecessary. For teams building regulated intake, customer portals, financial workflows, healthcare workflows, insurance claims, government services, or multi-tenant form platforms, it is often the main issue.
## **When Formbricks is the better choice**
Formbricks is likely the better fit when your team needs:
- a self-hosted Typeform alternative
- product feedback surveys
- NPS, CSAT, CES, onboarding, churn, or market research surveys
- in-app micro-surveys and website surveys
- open-source survey tooling with a clear cloud/self-host path
- privacy-first feedback collection
- a survey API for responses, contacts, and webhooks
- broad survey features without building a survey platform from scratch
In those cases, Form.io may be too much infrastructure. If the primary object is a survey and the output is feedback analysis, Formbricks is a natural choice.
## **When Form.io is the better choice**
Form.io is likely the better fit when your team needs:
- embedded forms inside a customer-facing application
- white-labeled form building inside your own product
- JSON-defined forms that drive rendering, validation, submissions, and APIs
- generated form APIs instead of hand-built backend endpoints for every form
- form, project, and submission permissions
- dev/test/prod form environments and SDLC-aware form promotion
- multi-tenant form workflows
- audit-relevant controls such as permissions, deployment boundaries, submission history, and security/compliance features
- configuration-based pricing for high-volume form infrastructure
- forms that support workflows beyond feedback collection
- governed form and submission context for agentic workflows
In those cases, the form is no longer just a question flow. It is a governed application layer.
## **The decision rule**
Choose Formbricks if the main job is collecting feedback through open-source, self-hosted surveys.
Choose Form.io if the main job is making forms, submissions, APIs, permissions, workflow behavior, and agentic workflow context part of your product or enterprise application infrastructure.
That is the real comparison.
Formbricks helps teams own survey and feedback collection. Form.io helps teams own the form layer when it becomes part of the architecture.
## **FAQ**
### **Is Formbricks a form builder?**
Yes, but it is better understood as an open-source survey and experience management platform. It can build forms and surveys, but its strongest fit is feedback collection across websites, apps, emails, and shared links.
### **Is Form.io a Formbricks alternative?**
Form.io can be an alternative when the buyer’s requirement is governed forms, generated APIs, embedded form rendering, self-hosted deployment, and application infrastructure. It is not a direct replacement for every survey, feedback, or experience-management use case Formbricks supports.
### **Which is better for a self-hosted Typeform alternative?**
Formbricks is usually the stronger fit for a self-hosted Typeform alternative. It is built around surveys, feedback collection, open-source access, and privacy-first response workflows.
### **Which is better for embedded forms?**
Form.io is usually the stronger fit when forms need to be embedded into a customer-facing product or enterprise application as a governed runtime. Formbricks can embed surveys, while Form.io is built around embeddable form rendering and embedded form building.
### **Can Formbricks be self-hosted?**
Yes. Formbricks documents free self-hosting and self-hosting with an Enterprise Edition license. Buyers should verify which features are included in Community Edition and which require Enterprise Edition.
### **Can Form.io be self-hosted?**
Yes. Form.io supports self-hosted deployment with API server environments, portal/authoring environments, renderer libraries, PDF Server options, customer-controlled databases, file storage choices, and common dev/test/prod deployment structures.
### **Does Formbricks have an API?**
Yes. Formbricks documents a Public Client API for frontend survey interactions and a Management API for backend management tasks such as surveys, contacts, responses, action classes, and webhooks.
### **Does Form.io generate APIs from forms?**
Yes. Form.io’s distinction is that form schemas and paths can directly define schema and submission endpoints, making the form itself part of the application API contract.
### **Which is better for regulated form workflows?**
Form.io is usually the better fit when the regulated workflow depends on form schemas, submission permissions, generated APIs, deployment boundaries, submission history, and long-term governance of form changes. Formbricks may still fit regulated feedback collection when a survey-first model is enough.
### **Which is better for customer-facing SaaS platforms?**
Form.io is usually the stronger fit when SaaS customers need to create or use forms inside your product experience, especially with white-labeling, tenant boundaries, permissions, and governed form behavior. Formbricks is stronger when the SaaS product mainly needs in-app feedback and customer surveys.
### **How should teams evaluate Formbricks vs Form.io?**
Start by deciding whether you are choosing a survey platform or a form infrastructure layer. Then compare deployment, embedding, API behavior, permissions, licensing, pricing basis, audit needs, and who will maintain the form model over time.
## **Build form infrastructure without turning every form into a custom project**
When forms become part of the application architecture, the right platform needs to do more than collect responses. It needs to keep schemas, submissions, APIs, permissions, and workflows aligned as the system grows.
[Try Form.io for free](https://form.io/try-formio-for-free/) if your team needs self-hosted form infrastructure that developers can embed, govern, and scale inside the applications you already own.
# Budibase vs Form.io: Internal Tools or Form Infrastructure?
[  ](https://form.io/budibase-formio-vs-budibase/)Organizations comparing self-hosted, open-source builders for internal tools and enterprise forms often put Budibase and Form.io in the same shortlist. Both speak to technical teams that want more control than lightweight SaaS form tools provide, but they solve different layers of the problem.
Budibase focuses on internal operations apps, agents, automations, and workflows around business data. Form.io is designed as application infrastructure for forms, APIs, workflows, and enterprise governance, including agentic workflow patterns where governed forms and submissions need to stay connected to permissions, validation, actions, and audit evidence.
That distinction matters before the feature checklist begins. The question is not whether both products can collect data. It is whether the form is a screen inside an internal app or a governed contract inside the application architecture.
## **Key takeaways**
- Budibase is best understood as an open-source operations platform for internal tools, agents, apps, automations, and connected data.
- Form.io is best understood as form-driven application infrastructure: JSON-defined forms, generated APIs, submission data, permissions, workflow actions, self-hosted deployment, and governed patterns for agentic workflows.
- Budibase is a credible choice for internal apps, request workflows, admin panels, and operational tools.
- Form.io is the better fit when forms need to be embedded in a product, reused across tenants, governed through submission-level permissions, exposed through APIs, managed as part of an enterprise SDLC, or used as structured context for agentic workflows.
- The main question is not "Which product has forms?" It is "What layer do your forms need to own?"
## **Quick comparison**
## **Decision area****Budibase****Form.io**Primary jobInternal operations platform for agents, apps, automations, workflows, and connected dataForm and API infrastructure for embedded, governed, form-driven applications and agentic workflowsForm modelForms are components inside Budibase apps, usually tied to tables, views, custom schemas, or app workflowsForms are JSON schemas that define UI, validation, submission structure, and backend APIsAPI modelPublic API gives access to apps, users, tables, and data through a RESTful APIEach form/resource path can generate REST endpoints for schemas and submissionsEmbeddingPublished apps can be embedded with iframes; enterprise microfrontend options existRenderer and builder can be embedded directly into customer-controlled applicationsGovernanceTenant roles, workspace roles, app roles, SSO, groups, and audit logs depending on planProject, form, and submission permissions; roles, actions, audit patterns, stages, and self-hosted environmentsBest buyerTeams building internal tools and operations workflows quicklyTeams standardizing forms, APIs, submissions, permissions, workflow behavior, and agentic workflow context as product infrastructureWrong fit warningLess ideal when the form layer must be a portable, governed contract outside an internal app surfaceNot a general internal-tools replacement for every dashboard, CRUD app, or admin panel**What Budibase is good at**
Budibase deserves a fair reading. Its own documentation describes it as an open-source platform for internal tools and workflow automation, used by more than 200,000 teams to automate workflows, handle requests, build internal tools, and connect systems using their own data, LLMs, and APIs.
That is a real category.
If your team needs to build an internal approval app, a data-entry screen, an admin panel, a request workflow, an operations dashboard, or an agent-assisted internal process, Budibase is built for that motion. It gives teams a visual app builder, data connections, automations, apps, agents, roles, and deployment options in one operations-oriented surface.
Budibase forms are part of that app-building model. The official forms documentation says forms are built from a Form component, Field group components, and Input components, with optional schemas tied to tables, views, relationships, or custom structures.
That is useful when the form is a screen inside an internal app.
The question is what happens when the form is no longer just a screen.
## **What Form.io is good at**
Form.io is strongest when forms, submissions, validation, permissions, APIs, and workflow actions need to become governed infrastructure rather than app components. The form definition can become a JSON contract that drives rendering, submission shape, validation rules, backend endpoints, and downstream handoffs.
That makes Form.io a better fit for customer-facing forms, regulated intake, tenant-managed SaaS form builders, healthcare and financial workflows, government services, insurance claims, and enterprise processes where the form record needs to stay governed after submission.
It also matters for agentic workflows. When AI-assisted or runtime agents need to collect structured data, validate inputs, trigger actions, or require human confirmation inside enterprise guardrails, the form layer needs stable schemas, permissions, and audit patterns. Form.io is built for that form and workflow infrastructure layer.
So the Form.io category should appear early in the decision: it is not the general internal app builder in this comparison. It is the governed form infrastructure layer when forms, APIs, submissions, and workflow behavior need to be owned by the application architecture.
## **What changes when forms become infrastructure**
Many teams start with a simple internal form and end up with application infrastructure.
The intake form becomes a case creation workflow. The customer form becomes a white-labeled feature inside a SaaS product. The compliance form becomes a regulated submission record. The public-sector form becomes one of hundreds of services that must follow the same standards. The healthcare or financial-services form becomes part of a workflow where validation, access, auditability, and downstream APIs matter as much as the UI.
That is the point where the Budibase vs Form.io decision gets sharper.
Form.io's form builder is not only a visual form editor. The Form.io documentation says the builder creates a JSON schema representation of the form, and that schema is used to dynamically render the form and automatically generate the REST API that supports it ([Form.io form building docs](https://help.form.io/userguide/forms/form-building)).
That is the architectural difference.
In Budibase, forms help users interact with data inside apps. In Form.io, the form schema can become the contract that defines the rendered UI, validation rules, submitted data shape, API endpoints, permissions, and downstream workflow behavior.
For teams whose forms are application infrastructure, that difference is not small.
## **Forms inside apps vs forms as contracts**
Budibase is strongest when you want a visual way to assemble apps around data and process. Its forms can create and update data, use schemas, and participate in workflows. For internal teams, that can be exactly right.
Form.io is stronger when the form definition itself needs to travel across systems.
Every Form.io form is a structured JSON definition. Form.io's JSON-schema forms documentation explains that a form schema can define the form title, path, type, display mode, components, validation, conditional logic, and submission data shape. It also explains that a form path creates endpoints such as schema retrieval and submission create/list/read/update/delete operations ([Forms from JSON](https://form.io/features/form-from-json-schema/)).
That matters when multiple applications, teams, tenants, or agents need to rely on the same form contract.
If a form is only a UI on top of a table, the surrounding system still needs to decide how validation is enforced, how submissions are stored, how APIs behave, how permissions apply, and how downstream services consume the data. If the form is a governed schema with APIs and submissions attached, more of that behavior has one source of truth.
That is why Form.io often resonates with teams that have outgrown simple form building. They are not trying to draw fields faster. They are trying to keep the form, data model, API behavior, permissions, and workflow triggers aligned as requirements change.
## **API and data model comparison**
Budibase has an API, and that should be acknowledged clearly. Its public API documentation says the API provides access to applications, users, tables, and data through a RESTful API and an OpenAPI 3.0 specification.
That makes sense for an internal operations platform. You can integrate with the Budibase environment, work with tables and records, and connect Budibase to broader business systems.
Form.io's API model is more specific to form infrastructure. The form schema defines the path and the submission endpoints that support that form. Form.io's drag-and-drop builder and API documentation explains that saving a form registers endpoints for creating, listing, reading, updating, and deleting submissions, with validation enforced from the schema ([drag-and-drop form builder APIs](https://form.io/features/drag-and-drop-form-builder-apis/)).
That is a different center of gravity.
Budibase helps you build apps around data. Form.io helps you define the form and submission layer that creates, validates, stores, and exposes that data in the first place.
For an internal app, either model may work. For a customer-facing product, regulated intake workflow, or multi-tenant form platform, the form-defined API model can be the safer foundation.
## **Embedding and white-labeling**
Budibase supports embedding, but the default model is app embedding. Its embedded app documentation describes embedding a published Budibase app in an iframe, with access considerations for public screens, allowed domains, and authenticated embedded users. Budibase also documents an enterprise microfrontend option for non-iframe embedding in specific licensed scenarios.
That can be useful when the thing you want to embed is an app.
Form.io is built for a different embedding requirement: embedding form rendering and form building inside the application your team already owns. The open-source `formio.js` renderer and SDK can render JSON schema forms inside an application and communicate with Form.io APIs ([Form.io JavaScript renderer](https://github.com/formio/formio.js)). The [Enterprise Form Builder Module](https://form.io/enterprise-form-builder-module/) lets teams expose white-labeled, preconfigured form building inside their own product while controlling components, guardrails, structured data, APIs, permissions, and workflow behavior.
That distinction is important for SaaS platforms, government service portals, healthcare products, and other systems where customers or internal teams need self-service form creation without leaving the product experience.
If you want to embed a whole operational app, Budibase may fit. If you want to embed governed form creation and rendering as part of your own product architecture, Form.io is the more direct match.
## **Self-hosting, security, and governance**
Do not reduce this comparison to "self-hosted vs not self-hosted." Budibase is a legitimate self-hosted option. Its hosting docs describe Budibase Cloud and self-hosted installation paths, including Docker, Kubernetes, and DigitalOcean. Its security docs say the self-hosted version can be deployed inside your own network, on your own servers, with control over how data is secured and without data needing to leave your VPC.
That is real.
The stronger Form.io argument is not that Budibase lacks deployment control. It is that Form.io's control is organized around form infrastructure.
Form.io's self-hosted deployment documentation describes API server environments, portal/authoring environments, Docker-based deployment, and common dev/test/prod structures ([Form.io self-hosted deployment docs](https://help.form.io/deployments/deployment-guide.md)). Its roles and permissions documentation separates access across project, form, and submission scopes, with permissions governing form definitions and submission data ([Form.io roles and permissions docs](https://help.form.io/developers/roles-and-permissions.md)).
That is the level of detail serious form infrastructure often needs.
Open source is also not a substitute for governance by itself. GitHub's 2025 Octoverse report says 63% of all repositories are open source or public, while 81.5% of contributions happen in private repositories, showing how public software and private enterprise work now depend on each other ([GitHub Octoverse 2025](https://github.blog/news-insights/octoverse/octoverse-a-new-developer-joins-github-every-second-as-ai-leads-typescript-to-1/)). Black Duck's 2026 OSSRA analysis found that 87% of audited codebases contained at least one vulnerability and 78% contained high-risk vulnerabilities, which is why open-source adoption still needs supply-chain governance ([Black Duck 2026 OSSRA](https://www.blackduck.com/blog/open-source-trends-ossra-report.html)). Gartner also predicts that by 2027, 70% of organizations with platform teams will include GenAI capabilities in internal developer platforms, increasing the need for reusable guardrails around generated and internal applications ([Gartner software engineering trends](https://www.gartner.com/en/newsroom/press-releases/2025-07-01-gartner-identifies-the-top-strategic-trends-in-software-engineering-for-2025-and-beyond)).
The practical lesson is simple: open source and self-hosting are valuable, but enterprise teams still need clear controls over data, roles, changes, workflows, and audit evidence.
Budibase has governance features such as tenant roles, workspace app roles, SSO, user groups, and audit logs. Its audit log docs say audit logs track events across a Budibase installation, and also show an upgrade path for free-tier users who need audit logs. That is not a criticism. It is a reminder to verify packaging against the controls your team actually needs.
For Form.io buyers, the governance question is more specific: who can change a form definition, who can submit, who can read submissions, which action fires after submission, which environment owns the schema, and which historical submission was governed by which form state?
Those are form-infrastructure questions.
## **Pricing basis: free tier vs scale predictability**
Budibase has a strong pricing story for many teams. Its pricing page includes a free open-source self-hosted plan, and higher tiers add capabilities such as more logs, custom branding, backups, SSO, user groups, SCIM, audit logs, priority support, and air-gapped deployment options.
For internal tools, that can be compelling.
Form.io's pricing story is different. The point is not that it is cheaper in every scenario. The point is that it is priced around self-hosted form/API configuration rather than usage meters. Form.io's configuration-based pricing page lists unlimited API calls, unlimited submissions, unlimited developers and form builders, and unlimited forms and resources in relevant configurations, and it frames the buying model around projects, API/PDF environments, and enterprise add-ons ([Form.io configuration-based pricing](https://form.io/configuration-based-pricing/)).
That difference matters when forms are high-volume, public-facing, embedded, or tenant-driven.
If every customer, office, agency, or product team can create forms, usage can become difficult to predict. A pricing model that avoids per-form, per-submission, per-end-user, per-developer, and per-API-call charges can make more sense when forms are infrastructure rather than a handful of internal apps.
## **Customer proof: when this becomes real**
Form infrastructure arguments can sound abstract until the scale shows up.
A Form.io public-sector case study for publicplan GmbH describes support for over 400 services and 1,000+ forms under strict standards and a short timeline ([publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)). Another Form.io-hosted customer proof point describes a long-time platform user running multiple production applications with a Form.io backend and saying, "Form.io cleans up all the dirty work and does it for you" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)).
Those examples point to the same idea: when forms multiply across services, products, departments, or customers, the hard part is not dragging fields onto a page. The hard part is keeping the form layer governed, reusable, API-backed, and operationally stable.
That is the Form.io case.
## **When Budibase is the better choice**
Budibase is likely the better fit when your team needs:
- internal tools for operations, support, HR, IT, finance, or admin workflows
- agent-assisted internal request handling
- dashboards, admin panels, and CRUD apps over business data
- a visual app builder for teams that want to ship internal workflows quickly
- open-source self-hosting for internal app delivery
- automations and app screens in one operations platform
In those cases, Form.io may be too specialized. If the form is just one component inside a broader internal app, Budibase can be the simpler answer.
## **When Form.io is the better choice**
Form.io is likely the better fit when your team needs:
- embedded forms inside a customer-facing application
- white-labeled form building inside your own product
- JSON-defined forms that can drive rendering, validation, submissions, and APIs
- generated form APIs instead of hand-built backend endpoints for every form
- submission-level permissions and form-specific access control
- dev/test/prod form environments and SDLC-aware form promotion
- multi-tenant form workflows
- compliance-oriented audit patterns
- no per-submission, per-form, per-end-user, or per-API-call pricing surprise
- governed form and submission context for agentic workflows
In those cases, the form is no longer a UI component. It is a governed application layer.
## **The decision rule**
Choose Budibase if the main job is building internal operational apps around data, approvals, automations, and agents.
Choose Form.io if the main job is making forms, submissions, APIs, permissions, workflow behavior, and agentic workflow context part of your product or enterprise application infrastructure.
That is the real comparison.
Budibase helps teams build operational applications faster. Form.io helps teams keep form-driven systems governed when the forms themselves become the architecture.
## **FAQ**
### **Is Budibase a form builder?**
Budibase includes form-building capabilities, but it is better understood as an internal operations platform for apps, agents, automations, workflows, and connected data. Forms are one important part of that app-building model.
### **Is Form.io a Budibase alternative?**
Form.io can be an alternative when the specific requirement is governed forms, submissions, generated APIs, embedded form rendering, and self-hosted form infrastructure. It is not a general replacement for every internal app or dashboard use case Budibase supports.
### **Which is better for internal tools?**
Budibase is usually the stronger fit for broad internal tools, admin panels, request workflows, dashboards, and operations apps. Form.io is more specialized around the form and API layer.
### **Which is better for embedded forms?**
Form.io is usually the stronger fit when forms need to be embedded into a customer-facing product or internal application as a governed runtime. Budibase can embed apps, but Form.io is built around embeddable form rendering and embedded form building.
### **Can Budibase be self-hosted?**
Yes. Budibase supports self-hosting and documents deployment paths such as Docker, Kubernetes, and DigitalOcean. Buyers should still verify which governance, audit, SSO, SCIM, support, and air-gapped features are included in the plan they intend to use.
### **Can Form.io be self-hosted?**
Yes. Form.io supports self-hosted deployment with API server environments, portal/authoring environments, Docker-based deployment, customer-controlled databases, and common dev/test/prod structures.
### **Does Budibase generate APIs from forms?**
Budibase has a public API for apps, users, tables, and data. Form.io's distinction is that form schemas and paths can directly define form and submission endpoints, making the form itself part of the API contract.
### **Which is better for regulated form workflows?**
Form.io is usually the better fit when the regulated workflow depends on form schemas, submission permissions, generated APIs, deployment boundaries, audit patterns, and long-term governance of form changes. Budibase may still fit internal regulated workflows when the app-builder model is enough.
### **Which is better for customer-facing SaaS platforms?**
Form.io is usually the stronger fit when SaaS customers need to create or use forms inside your product experience, especially with white-labeling, tenant boundaries, and governed form behavior. Budibase is stronger when the goal is to build internal apps for your own team.
### **How should teams evaluate Budibase vs Form.io?**
Start by deciding whether you are choosing an internal app builder or a form infrastructure layer. Then compare deployment, embedding, API behavior, permissions, pricing basis, audit needs, and who will maintain the form model over time.
## **Build form infrastructure without turning every form into a custom project**
When forms become part of the application architecture, the right platform needs to do more than render fields. It needs to keep schemas, submissions, APIs, permissions, and workflows aligned as the system grows.
[Try Form.io for free](https://form.io/try-formio-for-free/) if your team needs self-hosted form infrastructure that developers can embed, govern, and scale inside the applications you already own.
# HIPAA-Compliant Form Builder: What Healthcare SaaS Teams Should Evaluate
## [  ](https://form.io/hipaa-compliant-form-builder-healthcare-saas-platforms/)**Key Takeaways**
- A HIPAA-compliant form builder is not compliant because it has a healthcare template or a lock icon.
- If a vendor creates, receives, maintains, or transmits ePHI for a covered entity or business associate, the BAA and operational responsibility boundary matter.
- Hosted HIPAA form builders can be a good fit for simple intake, consent, appointment, or website forms.
- Healthcare SaaS teams usually need more than a hosted form link: APIs, embedded rendering, role-aware access, audit logs, revision history, and deployment control.
- Form.io is strongest when HIPAA-governed forms are part of application infrastructure rather than a standalone intake tool.
## **What "HIPAA-Compliant Form Builder" Actually Means**
The phrase "HIPAA-compliant form builder" is useful shorthand, but it can hide the real decision.
HIPAA compliance is not a feature that one vendor turns on for the whole organization. It is a legal, contractual, administrative, technical, and operational responsibility. The form builder can support that responsibility. It cannot replace it.
The U.S. Department of Health and Human Services explains that when a covered entity or business associate uses a cloud service to create, receive, maintain, or transmit ePHI, the cloud service provider is generally a business associate and the parties need a HIPAA-compliant business associate agreement. [HHS also notes](https://www.hhs.gov/hipaa/for-professionals/special-topics/health-information-technology/cloud-computing/index.html) that this can still be true even when the provider stores only encrypted ePHI and does not hold the decryption key.
That point matters for online forms.
If a form collects PHI, the risk does not stop at the submit button. The data may be stored, emailed, exported, routed through webhooks, copied into a CRM, written to a database, attached to a PDF, shown in an admin portal, or sent to downstream systems. A HIPAA-ready form tool has to be evaluated across that whole path.
The [HHS Security Rule](https://www.hhs.gov/hipaa/for-professionals/security/index.html) frames the obligation around administrative, physical, and technical safeguards for the confidentiality, integrity, and availability of ePHI. In plain terms: the form is only one surface. The system around the form has to be governed too.
The risk is not theoretical. IBM's 2025 Cost of a Data Breach report puts the global average breach cost at [$4.4 million](https://www.ibm.com/reports/data-breach?app=true). That is not a healthcare-form-specific number, but it gives the right scale for the decision: a form that collects sensitive health data is not a minor website feature when the surrounding workflow is weak.
## **The Quick Decision: Practice Intake Tool Or Healthcare SaaS Infrastructure?**
Most buyers searching for a HIPAA-compliant form builder fall into one of two groups.
The first group needs a faster way to collect patient information. A clinic, therapy practice, dental office, or small healthcare provider may need intake forms, consent forms, appointment requests, file uploads, and e-signatures. A hosted HIPAA-enabled form builder can work well here if the vendor signs the right BAA, the account is configured correctly, and the workflow keeps PHI inside approved systems.
The second group is building a healthcare product. That buyer does not only need a form. It needs form capability inside an application.
For healthcare SaaS teams, forms may power onboarding, eligibility, clinical screening, referrals, patient-reported outcomes, provider workflows, prior authorization, records updates, care-team routing, and follow-up check-ins. A [third-party digital health article from Light-it](https://lightit.io/blog/5-ways-to-apply-hipaa-compliant-form-builders-to-your-digital-health-product/) describes HIPAA-compliant forms as part of ongoing product workflows such as patient intake, assessments, appointment scheduling, regular check-ins, and feedback surveys. That is a different problem than publishing a secure contact form on a website.
The distinction is simple:
**Buyer situation****Better fit**One practice needs intake forms and patient packetsHosted HIPAA-enabled form builderA healthcare SaaS product needs forms inside its appEmbedded form infrastructureA team needs patient data routed to internal systemsAPI-first form platformA team must keep PHI inside its own environmentSelf-hosted form infrastructureA product needs tenant-specific forms and permissionsWhite-label or multi-tenant form infrastructureThe mistake is treating these as the same purchase.
## **The Requirements Checklist**
Before comparing logos, healthcare teams should define the control boundary.
### **BAA Scope**
A BAA is not a marketing badge. It establishes the permitted uses and disclosures of PHI, requires appropriate safeguards, covers reporting obligations, addresses subcontractors, and should align with the actual workflow. [HHS sample BAA guidance](https://www.hhs.gov/hipaa/for-professionals/covered-entities/sample-business-associate-agreement-provisions/index.html) says these contracts should clarify and limit how a business associate may use or disclose PHI and require safeguards to prevent unauthorized use or disclosure.
The practical question is: which vendor is creating, receiving, maintaining, or transmitting ePHI?
If the form builder stores submissions, handles uploaded files, sends notifications containing PHI, or passes data to another system, the BAA and subcontractor chain need to match that reality.
### **Where PHI Is Stored**
Data location is not a minor implementation detail. It determines who administers the database, where backups live, which security controls apply, who can access logs, what happens at termination, and how incident response works.
For a simple hosted form workflow, vendor-managed storage may be acceptable. For a healthcare SaaS product, the team may need submissions in its own database, cloud account, region, network, or compliant infrastructure boundary.
This is one reason self-hosting matters. It does not make an application HIPAA compliant by itself. It gives the customer more control over where PHI lives and which controls surround it.
### **Access Control And Identity**
HIPAA-governed forms usually need more than a shared admin login.
Ask who can view submissions, edit forms, export data, upload files, change permissions, configure webhooks, or see audit logs. Then map those permissions to real roles: patient, provider, customer admin, internal support, implementation partner, compliance reviewer, and developer.
For SaaS products, this gets harder. One customer's admin should not see another customer's submissions. A support user may need temporary access. A provider may need access to only assigned patients. A form builder may need schema-editing rights without PHI access.
The form system has to support those boundaries instead of forcing the application to patch them later.
### **Audit Logs And Revision History**
The highest-risk part of a healthcare form often starts after submission.
What changed? Who changed it? Which version of the form captured the original data? Did a webhook run? Did an email action send? Did the submitted value get edited later? Can the team reconstruct the record if an auditor asks?
Generic form builders often focus on collection. Healthcare SaaS teams need evidence.
Form.io's Security Module is built around this kind of evidence. Its [secure forms and compliance readiness documentation](https://form.io/features/secure-forms-compliance-readiness/) describes advanced audit logging, action logs, form revisions, submission revision logs, submission collections, and container security scanning. The important distinction is that form revisions track changes to the form schema, while submission revisions track changes to submitted data.
That distinction sounds small. It is not.
A historical submission is not only the answers a patient gave. It is the form version, validation rules, field labels, conditional logic, workflow context, and submission state that governed the data at the time.
### **APIs And Integration Control**
Healthcare forms rarely stay inside the form tool.
An intake form may need to create a patient profile, update a resource, trigger a referral workflow, generate a PDF, route a task to a care team, or feed an internal dashboard. A screening form may need validation, conditional follow-up, file uploads, and downstream review. A provider form may need to connect with legacy systems or internal case management.
If the form builder only gives you CSV exports or a fragile integration layer, the application team inherits the risk.
Form.io's [concepts documentation](https://help.form.io/start/form.io-concepts) explains that as a form is built, Form.io constructs the JSON schema and defines a REST API endpoint. Submissions are API-accessible, owned by users for permission enforcement, portable, and revision-trackable with the Security & Compliance package. That is the infrastructure argument: the form definition, submitted data, API, and access model belong in the same system.
### **Tenant And Customer Boundaries**
Healthcare SaaS teams often serve many customers from one product. That means the form layer may need tenant-aware configuration, customer-specific forms, white-labeled experiences, separate roles, different workflows, and different data retention expectations.
This is where "HIPAA form builder" searches become too small. The issue is not only whether one form can collect PHI. It is whether a platform can support repeated, governed form workflows across customers without collapsing into one-off custom code.
## **Common HIPAA Form Builder Categories**
The market is easier to understand when you separate platform types.
**Category****Best fit****Strength****Gap**Hosted HIPAA form builderPractices and clinics that need intake, consent, and website formsFast setup, templates, vendor-managed hostingLimited architecture and data-boundary controlHealthcare intake platformPatient intake, appointment, and engagement workflowsHealthcare-specific UX and workflowsMay be too narrow for broader SaaS infrastructureEnterprise form/workflow platformLarger teams with governed workflowsMore controls and integrationsOften still vendor-hosted or workflow-product centeredSelf-hosted form infrastructureHealthcare SaaS and regulated product teamsDeployment control, APIs, data ownership, auditabilityRequires technical ownershipCustom buildUnique workflows with no acceptable platform fitMaximum controlExpensive to build, secure, test, document, and maintainThere is no universal winner. There is only the right layer for the job.
## **Where Form.io Fits For Healthcare SaaS**
Form.io is not the lightest way to publish a HIPAA-ready website form. It is a stronger fit when forms are part of healthcare application infrastructure.
That usually means the team needs some combination of embedded forms, generated APIs, custom roles, submission storage, workflow actions, form revisions, submission revisions, audit logs, file/PDF handling, and customer-controlled deployment.
Form.io's [self-hosted forms documentation](https://form.io/features/self-hosted-forms-for-enterprise/) says the platform can run in AWS, Azure, Google Cloud, private data centers, or Docker-based environments, with submission data stored in the customer's MongoDB instance and security boundary. The same page is careful about the boundary: self-hosted deployment enables compliance control, but the customer still needs proper access controls, encryption, audit logging, network security, and the rest of the compliance program.
That honesty is useful.
Healthcare SaaS teams do not need another vendor promising that complexity disappears. They need a platform that gives them the right control surfaces: forms, resources, generated APIs, submissions, actions, [roles and permissions](https://form.io/features/forms-for-teams/), revisions, and audit evidence.
Form.io's [healthcare forms page](https://form.io/industries/healthcare-forms/) points to use cases such as patient registration, records, appointments, routing inquiries, notifications, [conditional logic](https://form.io/features/form-conditional-logic-form-validation/), mobile-responsive forms, offline mode, form revisions, autosave, accessibility, and the Security Module. The better strategic reading is not "Form.io makes healthcare simple." It is that Form.io gives healthcare teams a form infrastructure layer they can govern inside their own architecture.
The [CHESS Health case study](https://form.io/how-a-flexible-form-solution-helped-get-to-market-in-6-weeks-instead-of-6-months/) is a useful proof point. Form.io describes a healthcare technology company managing EMRs, EHRs, interoperability, strict security and compliance requirements, sensitive data in its own environment, legacy integrations, and the need to get to market faster. The case headline says CHESS Health got to market in 6 weeks instead of 6 months. That is the category fit: not a simple intake form, but a healthcare product workflow that needed speed without giving up architectural control.
There is also a buyer sentiment signal from [Trustpilot](https://www.trustpilot.com/review/form.io), where one reviewer called Form.io "really great software, both for integration and standalone." The quote is broad, but it matches the central buying reason for this article: the form layer has to work as part of a larger system.
## **When A Hosted HIPAA Form Builder Is Enough**
A hosted HIPAA form builder may be the better answer when the workflow is simple and the organization accepts the vendor-managed model.
That can include:
- Patient intake forms for one practice
- Consent forms
- Appointment request forms
- Simple file uploads
- Basic medical history forms
- Feedback surveys
- Website-embedded forms
- Staff-created forms with limited integration needs
In these cases, speed matters. Templates matter. A no-code builder matters. A signed BAA, encrypted submissions, access controls, and a clean admin experience may be enough.
The important word is "enough."
If a workflow starts simple but will later need custom identity, tenant-specific configuration, deeper APIs, application-owned submission records, role-aware workflows, and evidence-grade revision history, the cheapest or fastest hosted option can become expensive later.
## **When Healthcare SaaS Teams Should Avoid Standalone Form Tools**
Standalone form tools become risky when the form is part of the product's core workflow.
Watch for these signals:
- PHI must remain inside your own cloud, database, or approved deployment boundary.
- Forms need to be embedded directly into your product experience.
- Customers need their own form configuration, roles, branding, or workflows.
- Submissions need to become application records, not just entries in a vendor dashboard.
- The product needs generated APIs, webhooks, resources, permissions, and workflow actions.
- Historical records need to resolve to the form version that captured them.
- Support, operations, providers, and customer admins need different access rules.
- Exports, notifications, analytics, and AI tools must not create uncontrolled PHI copies.
These are not edge cases for healthcare SaaS. They are ordinary product requirements.
The wrong tool can still pass the first demo. The problem appears later, when the team needs to prove who accessed PHI, why a submission changed, whether a field existed at the time of capture, where a file was stored, or why one tenant's workflow affected another.
That is the moment when "just use a form builder" stops being a plan.
## **Evaluation Table**
##  **Evaluation question****Why it matters****What to look for**Will the vendor sign the right BAA?PHI handling needs a contractual boundaryBAA scope, subcontractors, permitted uses, breach/security incident termsWhere is PHI stored?Data location shapes risk and responsibilityCustomer-controlled database, approved region, backup and termination termsCan access map to real roles?Healthcare workflows are role-sensitiveRBAC, SSO/MFA options, admin separation, own-vs-all submission accessAre form changes versioned?Historical records need contextForm revisions, schema history, promotion/stage controlsAre submission changes versioned?Modified PHI needs accountabilitySubmission revisions, who/when/what logs, revert or history viewsAre actions auditable?Integrations are common failure pointsAction logs for emails, webhooks, resource saves, and workflow stepsDoes the platform generate APIs?SaaS products need system integrationREST APIs, submission endpoints, resources, webhooksCan forms be embedded and white-labeled?Healthcare SaaS forms live inside productsRenderer libraries, embedded builder, brand controlCan the platform be self-hosted?Some teams need customer-controlled infrastructureDocker, cloud/on-prem deployment, environment variables, customer databaseDoes the vendor overclaim compliance?Overclaiming creates riskClear shared-responsibility language and technical-control boundaries**What Not To Assume**
Do not assume a healthcare template makes a workflow compliant.
Do not assume encryption solves the whole problem. HHS cloud guidance is clear that encryption alone does not remove business associate obligations when a provider maintains ePHI.
Do not assume a BAA covers every downstream action. If submissions are emailed to the wrong inbox, copied into a non-approved CRM, exported to spreadsheets, or passed through an unreviewed automation, the form builder's feature list is not the whole risk picture.
Do not assume self-hosting removes responsibility. It increases control. It also increases the customer's obligation to configure and operate the environment correctly.
Do not assume a standalone form tool will scale into product infrastructure. Sometimes it will. Often it will not.
## **FAQ**
### **Is A Form Builder HIPAA Compliant If It Signs A BAA?**
No. A BAA is necessary in many PHI workflows, but it is not the whole compliance answer. The organization still needs appropriate safeguards, policies, configuration, access control, risk analysis, monitoring, and incident-response processes.
### **Can Healthcare Teams Use Google Forms For PHI?**
Do not use a general form workflow for PHI unless the entire vendor relationship, configuration, storage model, access controls, and BAA requirements are approved for that use. For most healthcare SaaS teams, the safer default is to use a platform designed for regulated data workflows.
### **What Features Should HIPAA-Compliant Forms Have?**
At minimum, evaluate BAA support, encryption, access control, audit logs, secure storage, user management, file handling, retention/deletion, and integration behavior. For healthcare SaaS, also evaluate APIs, embedding, tenant boundaries, revision history, and deployment control.
### **Do Healthcare SaaS Teams Need Self-Hosted Forms?**
Not always. But self-hosting becomes important when PHI must stay inside the customer's environment, when the form layer needs to align with internal security controls, or when product architecture requires direct control over database, network, logging, and deployment boundaries.
### **Does Self-Hosting Make A Form Platform HIPAA Compliant?**
No. Self-hosting enables more control over infrastructure and data boundaries. Compliance still depends on how the environment is configured, monitored, documented, and governed.
### **Can Form.io Be Used For HIPAA Workflows?**
Form.io provides healthcare-oriented form infrastructure and security/compliance capabilities that can support HIPAA-governed workflows in customer-controlled environments. The customer's organization remains responsible for its HIPAA compliance program, configuration, policies, and deployment controls.
### **Does Form.io Certify My Application As HIPAA Compliant?**
No. Form.io's own compliance-readiness language is clear that the platform provides technical capabilities that support regulated deployments; it does not certify a customer's application or organization for HIPAA.
### **Why Do Audit Logs Matter For HIPAA Forms?**
Audit logs help answer who accessed or changed data, when it happened, what entity was affected, and which workflow action ran. For healthcare SaaS teams, that evidence can matter as much as the original form submission.
### **Should PHI Be Stored In A Third-Party Form Vendor Account?**
It depends on the workflow, BAA, risk analysis, and organizational policy. For simple intake forms, vendor-managed storage may be acceptable. For healthcare SaaS platforms, application-owned or customer-controlled storage may be a better fit.
### **What Should I Ask Before Collecting PHI Through An Online Form?**
Ask where PHI is stored, who can access it, which BAA covers it, whether uploads and notifications are protected, how audit logs work, how long data is retained, how submissions are deleted or exported, and what happens when the form changes.
## **Build HIPAA-Governed Form Infrastructure With Form.io**
If your healthcare product only needs a simple intake form, choose the fastest HIPAA-enabled tool that satisfies your compliance review.
If your forms define product workflows, API contracts, submissions, permissions, audit evidence, and data boundaries, choose infrastructure that respects that complexity from the start.
[Try Form.io for healthcare SaaS form infrastructure](/try-formio-for-free/).
# When Your Forms Don’t Match Your Design System Part 2
[  ](https://form.io/when-your-forms-dont-match-your-design-system-part-2/)In [Part 1](/when-your-forms-dont-match-your-design-system-part-1/), we established the design system compliance problem. Now let’s solve it for 98% of cases using class overrides alone.
Class names let you replace the CSS classes on your form components without touching the HTML structure. This is faster, less fragile, and easier to maintain than template-level customization. Start with this method in every case, and only reach for template overrides if you can’t accomplish your design goals with classes alone.
### **What Is the Class Names Method?**
Form.io templates are built from components, and each component has named parts: `input`, `label`, `button`, and so on. Class names let you define exactly which CSS classes apply to each part. The HTML structure stays the same; only the classes change. Because you’re working at the class level, this approach works with any CSS framework, whether you’re using Tailwind, Bootstrap, or something entirely your own, so you’re never locked into a particular toolchain.
### **Before You Start**
This guide assumes you already have a working Form.io application using the `@formio/js` renderer. To add the Standard Template, install it from npm:
```
npm install @formio/standard-template
```
**Note:** The Standard Template is a new and actively evolving package. Check the[ GitHub repository](https://github.com/formio/standard-template) for the latest version and API details before adopting it in production.
### **The Structure**
Here’s what a theme definition looks like:
```
import { standardTemplate } from '@formio/standard-template';
import type { TemplateClasses } from '@formio/standard-template';
const myTheme: TemplateClasses = {
// Component definitions go here
};
Formio.use(standardTemplate('my-custom-theme', myTheme));
```
Each component you want to customize gets an entry, and each entry defines classes for different contexts (`form` mode versus `html` display mode) and for the different parts of that component. Once you’ve seen one component defined, the rest follow the same shape.
### **Building a Complete Theme**
Let’s build a complete theme from scratch using Tailwind classes, transforming a basic contact form to match a modern design system. We’ll add one piece at a time.
#### **Our goal:**
- Minimal, underline-style input fields with an accent focus state
- Small, uppercase labels in the accent color
- A gradient pill button with hover effects
- Comfortable spacing between fields
#### **Step 1: Input Fields**
```
const myTheme: TemplateClasses = {
input: {
form: {
input: [
'block',
'w-full',
'px-0',
'py-2.5',
'text-base',
'text-slate-800',
'bg-transparent',
'border-0',
'border-b-2',
'border-slate-300',
'focus:outline-none',
'focus:border-violet-600',
'placeholder:text-slate-400',
'transition-colors',
'duration-200'
]
}
}
};
```
Pause on the shape of that definition, because every other component follows it:
- `input` (the outer key) is the component type: text fields, email fields, and so on
- `form` is the context (edit mode; there’s also html for read-only display)
- `input` (the inner key) is the specific element within that component
- The array contains all the Tailwind classes applied to that element
The result is an underline-style input: no box, no background, just a bottom border that shifts to violet when the field has focus.
#### **Step 2: Add Labels**
```
const myTheme: TemplateClasses = {
label: {
form: {
label: [
'block',
'text-xs',
'font-bold',
'uppercase',
'tracking-wider',
'text-violet-600',
'mb-2'
]
}
},
input: {
// ...input classes from Step 1
}
};
```
Labels now have their own styling: small, bold, uppercase, with letter-spacing and the accent color picking up the same violet as the input focus state. This sits alongside the input definition rather than inside it, because labels and inputs are independent components.
#### **Step 3: Add Buttons**
```
const myTheme: TemplateClasses = {
button: {
form: {
button: [
'w-full',
'px-6',
'py-3',
'text-sm',
'font-bold',
'uppercase',
'tracking-wider',
'text-white',
'bg-gradient-to-br',
'from-violet-600',
'to-violet-700',
'rounded-full',
'shadow-lg',
'shadow-violet-600/30',
'cursor-pointer',
'transition',
'duration-150',
'hover:opacity-90',
'hover:-translate-y-px',
'disabled:opacity-50',
'disabled:cursor-not-allowed'
]
}
},
label: {
// ...label classes from Step 2
},
input: {
// ...input classes from Step 1
}
};
```
The button becomes a full-width gradient pill: violet gradient background, a soft glow shadow, a subtle lift on hover, and proper disabled states. Notice the pattern: each component is self-contained, and adding a new one never disturbs the others.
#### **Step 4: Add Field Spacing**
```
const myTheme: TemplateClasses = {
component: {
form: {
component: [
'mb-6'
]
}
},
button: {
// ...button classes from Step 3
},
label: {
// ...label classes from Step 2
},
input: {
// ...input classes from Step 1
}
};
```
The `component` entry wraps every field in the form, so a single `mb-6` here gives each field comfortable breathing room below it. That’s the last piece of the theme.
### **The Complete Theme**
Here’s the full theme definition:
```
import { standardTemplate } from '@formio/standard-template';
import type { TemplateClasses } from '@formio/standard-template';
const myTheme: TemplateClasses = {
label: {
form: {
label: [
'block',
'text-xs',
'font-bold',
'uppercase',
'tracking-wider',
'text-violet-600',
'mb-2'
]
}
},
input: {
form: {
input: [
'block',
'w-full',
'px-0',
'py-2.5',
'text-base',
'text-slate-800',
'bg-transparent',
'border-0',
'border-b-2',
'border-slate-300',
'focus:outline-none',
'focus:border-violet-600',
'placeholder:text-slate-400',
'transition-colors',
'duration-200'
]
}
},
button: {
form: {
button: [
'w-full',
'px-6',
'py-3',
'text-sm',
'font-bold',
'uppercase',
'tracking-wider',
'text-white',
'bg-gradient-to-br',
'from-violet-600',
'to-violet-700',
'rounded-full',
'shadow-lg',
'shadow-violet-600/30',
'cursor-pointer',
'transition',
'duration-150',
'hover:opacity-90',
'hover:-translate-y-px',
'disabled:opacity-50',
'disabled:cursor-not-allowed'
]
}
},
component: {
form: {
component: [
'mb-6'
]
}
}
};
// Apply it globally
Formio.use(standardTemplate('my-custom-theme', myTheme));
```
Apply this once when your application initializes, and every form in your application will use the styling.
### **Before:**
### **After:**
### **Next Steps**
You now have everything you need to style Form.io forms to match your design system using class overrides. From here, the work is mostly a matter of breadth. The same pattern extends to every other component:
- **Radio buttons and checkboxes:** `radio`, `checkbox`
- **Select dropdowns:** `select`
- **Text areas:** `textarea`
- **Error and help text:** `errorLabel`, `helpBlock`
- **Field containers:** `component`, `field`
In every case you define classes for the component type and its parts, exactly as we did above. A textarea, for example, would take the same underline treatment as the inputs, plus `resize-y` and a `min-h-20` so users can expand it comfortably.
As your themes grow, it helps to pull them into their own modules so you can reuse them across projects:
```
// themes/tailwind-modern.ts
export const tailwindModern: TemplateClasses = {
// Your theme definition
};
// app.ts
import { tailwindModern } from './themes/tailwind-modern';
Formio.use(standardTemplate('tailwind-modern', tailwindModern));
```
Do this consistently and you end up with a library of themes you can share across your organization and maintain as part of your design system.
### **Additional Resources**
- [**Standard Template Playground**](https://apps.form.io/standard-template/): Interactive examples of different themes and styling approaches
- [**GitHub Repository**](https://github.com/formio/standard-template): Inspect the code and learn more about what you can target with CSS
# When Your Forms Don’t Match Your Design System Part 1
[  ](https://form.io/when-your-forms-dont-match-your-design-system-part-1/)Your design team just shipped an updated component library. New focus rings, refined spacing, updated color tokens. Engineering updates the React components, the dashboard layouts, and the navigation. Everything looks cohesive.
Then someone opens a form.
Form.io has been powering your dynamic forms beautifully. It handles complex conditional logic, multi-step workflows, and validation rules that would take many engineering hours to build from scratch. The form builder itself is invaluable: non-technical team members can create and modify forms without engineering involvement.
But visually, those forms still use the Bootstrap classes and markup they shipped with. Now there’s a mismatch. The rest of your application has evolved, and the forms haven’t.
This isn’t a Form.io problem. It’s a sign of success. Your product has matured to the point where your design system requirements go beyond any form builder’s defaults.
## **Why This Happens**
Form.io ships with professional, well-designed templates based on Bootstrap, and that’s exactly what you want when you’re getting started. These defaults handle everything: inputs, buttons, radio groups, validation messages, error states. They’re accessible, well-tested, and work across browsers. For many teams, they’re perfect and require no customization at all.
But as your product matures, specific visual requirements tend to surface. Maybe your design system has standardized on Tailwind rather than Bootstrap. Maybe you’ve built up custom brand colors, spacing scales, and typography, or your design team has defined particular interaction patterns. And at some point, “close enough” stops being good enough. You need the forms to match the rest of your application pixel-for-pixel. That’s the moment you need to customize Form.io’s visual layer while keeping everything else that makes it valuable.
## **What Teams Try Today**
Before Standard Template When teams hit this point in their product evolution, they usually reach for one of four approaches. Each comes with real trade-offs.
1. **Convince design to accept the form builder’s defaults.** Sometimes that works for internal tools, but for a customer-facing product with established brand guidelines, it’s usually a non-starter.
2. **Write custom CSS that overrides the defaults.** This works until it doesn’t: you can change colors and spacing, but you can’t restructure HTML with CSS, future updates might break your overrides, and maintenance gets expensive.
3. **Rebuild the component templates from the ground up.** You could use the default Form.io Bootstrap 5 template as a guide for writing your own. That gives you complete control, but now you’re maintaining even more code. It’s technically possible, but operationally expensive.
4. **Build a custom form system from scratch.** The most drastic option. Do this and you throw away Form.io’s conditional logic, validation rules, and visual builder, everything that made it valuable in the first place. It’s rarely justified. You chose Form.io for a reason.
What most teams actually want is something none of those quite delivers: keep Form.io’s powerful form logic and builder interface, but adapt the visual layer to match their design system.
## **The Standard Template**
After Standard Template The Standard Template introduces a customization system that works *with* Form.io’s existing architecture instead of against it. Its core mechanism is **Style Map**: you replace the CSS classes on existing HTML elements without changing the underlying structure. It works with any CSS framework, whether that’s Tailwind, Bootstrap, or a fully custom design system, and it’s fast to implement and easy to maintain. With the Standard Template, you’re configuring Form.io’s rendering layer, not fighting it.
This approach makes sense when you have an established design system with specific requirements, several forms that need to stay visually consistent, and a product where design system compliance matters, and you want all of that without giving up Form.io’s form logic and builder.
Just as important is knowing when you *don’t* need it. If Form.io’s default Bootstrap theme already works for you, if you only have a form or two, if your forms are internal tools where strict visual consistency isn’t a concern, or if you’re just getting started and should be optimizing for speed over pixel-perfection, then reaching for customization only creates work. Form.io’s defaults are professionally designed and serve most use cases well. Don’t make work for yourself unless you have a clear requirement.
## **Wrapping Up**
Adopting the Standard Template gives you the best of both worlds: Form.io’s powerful form capabilities with your design system’s visual consistency. Once it’s in place, your forms match your design system’s colors, spacing, and typography, while non-technical users keep building and modifying forms in the Form.io builder exactly as before. All of Form.io’s logic, validation, conditionals, and calculations keep working, your maintenance burden shrinks to a set of class definitions and the occasional template override, and new Form.io features and updates apply without conflicts.
The Standard Template is now available with the [release of Form.io 9.8.0](/release-notes/formio-enterprise-9-8-0-and-pdf-server-5-14-0/).
In [Part 2](/when-your-forms-dont-match-your-design-system-part-2/), I’ll show you how class overrides work with concrete examples. You’ll build a complete Tailwind theme from scratch without touching a single line of HTML.
# MCP Server List: What Regulated Enterprise Developers Should Actually Use
[  ](https://form.io/mcp-server-list-regulated-enterprise-developers/)You can find an MCP server list in seconds. That is not the hard part. The hard part is deciding which servers deserve access to your source code, cloud accounts, tickets, documentation, test environments, and production-adjacent business data.
For regulated enterprise developers, the question is not "which MCP servers are popular?" It is "which MCP servers can we trust inside a governed workflow?"
## **The quick answer**
Start with the official MCP Registry, then filter by control surface.
For regulated enterprise development, the strongest shortlist usually includes:
**MCP surface****Best fit****Enterprise question**Official MCP RegistryDiscovery and metadataIs this server officially published, namespace-authenticated, and still current?GitHub MCP ServerRepos, pull requests, issues, Actions, security findingsCan the agent work inside the same SDLC boundary developers already use?GitLab MCP ServerGitLab.com, self-managed GitLab, Duo workflowsDoes it respect the deployment model and permissions your GitLab instance already enforces?AWS MCP ServersCloud architecture, docs, API operationsAre IAM, least privilege, CloudWatch metrics, and CloudTrail evidence understood before use?Azure MCP ServerAzure resources, Entra ID-backed cloud workflowsDoes the server inherit the identity and guardrail model your Azure teams already use?Atlassian Rovo MCP ServerJira, Confluence, CompassDoes the agent see only what the user has permission to see?Playwright MCPBrowser automation and UI testingAre unsafe direct-code tools disabled unless the client is trusted?Sentry MCPDebugging and observabilityCan the agent inspect errors without turning observability into an unbounded data pipe?Docker MCP toolingLocal gateway, catalog, containerized MCP operationsCan servers be packaged and scoped consistently across teams?Form.io MCP ServerForms, resources, actions, APIs, and schema-driven application infrastructureCan the agent build against governed form and API patterns instead of improvising them?That is the useful MCP server list for regulated teams: not a popularity contest, but a map of which systems an agent can touch, how it authenticates, what it can change, and where the audit evidence lands.
## **What an MCP server list can and cannot tell you**
MCP, or Model Context Protocol, gives AI clients a standard way to connect to external tools and data. An MCP server is the bridge between the agent and a system such as GitHub, AWS, Jira, a browser, a database, or a domain platform such as Form.io.
An MCP server list helps with discovery. It does not prove that a server belongs in your enterprise agent environment.
That distinction matters because the official MCP Registry itself is a metadata layer. The registry documentation describes it as the official centralized repository for publicly accessible MCP server metadata, while also noting that it is still in preview and does not support private servers. It supports discovery, namespace authentication, installation metadata, and REST API access. It is not a substitute for enterprise security review.
That is the first mistake many teams make. They treat discovery as approval.
For a developer testing locally, that may be tolerable. For a regulated team, it is a weak control. A server that reads public docs is not in the same risk category as a server that can open pull requests, read customer tickets, execute cloud API calls, or inspect production error traces.
The list is the beginning. The trust decision comes after.
## **The regulated-enterprise filter**
Before you add a server to Claude Code, Cursor, VS Code, Windsurf, or another MCP client, ask six questions.
### **Who maintains it?**
Prefer official or vendor-maintained servers when the system is critical. A community server can be useful, but enterprise teams need a clear owner, release trail, issue history, and support path.
This is why GitHub, GitLab, AWS, Azure, Atlassian, Playwright, Docker, Sentry, and Form.io deserve separate treatment from generic directories. They are not just "available MCP servers." They are maintained by, or directly tied to, the systems they expose.
### **What identity model does it inherit?**
A lower-risk server is usually one that inherits the identity and permission model already governing the system.
[GitLab's MCP docs](https://docs.gitlab.com/user/gitlab_duo/model_context_protocol/mcp_server/), for example, describe OAuth registration and HTTP transport options, and they support GitLab.com, Self-Managed, and Dedicated environments. [Atlassian's remote MCP server](https://support.atlassian.com/atlassian-rovo-mcp-server/docs/getting-started-with-the-atlassian-remote-mcp-server/) uses OAuth 2.1 and respects Jira, Confluence, and Compass permissions. [Azure MCP Server](https://learn.microsoft.com/en-us/azure/developer/azure-mcp-server/overview) uses Microsoft Entra ID through Azure Identity.
That matters more than convenience. If the server works around identity, it works around governance.
### **What can it mutate?**
Read-only access is one risk. Write access is another. Production mutation is another.
A server that searches docs can still leak context. A server that changes infrastructure, submits forms, opens tickets, or modifies code can create operational state. Treat those differently.
The [MCP security guidance](https://modelcontextprotocol.io/specification/2025-06-18/basic/security_best_practices) calls out risks such as confused deputy behavior, token passthrough, SSRF, session hijacking, local server compromise, and the need to minimize scopes. Those are not abstract security concerns. They are what happens when an agent can act through a server whose authority is broader than the user's intent.
### **Where are logs written?**
Regulated teams need evidence. If an agent uses a server to retrieve context, change an issue, call an API, or update a form definition, the team needs to know where that action is logged.
AWS is a useful benchmark here. AWS announced the [AWS MCP Server general availability](https://aws.amazon.com/about-aws/whats-new/2026/05/aws-mcp-server/) on May 6, 2026, describing IAM-based guardrails, Amazon CloudWatch metrics, and AWS CloudTrail logging. That does not make every AWS MCP use case automatically approved, but it does give enterprise teams a familiar evidence model.
### **What data crosses the boundary?**
Some MCP servers expose local files. Some expose SaaS data. Some connect to cloud accounts. Some connect to internal systems. Some domain-specific servers, such as the Form.io AI toolset, connect to a customer's self-hosted environment.
The boundary is the point.
Form.io describes its MCP Server as connecting to a customer's self-hosted Form.io deployment so AI coding agents can work with forms, resources, actions, and APIs without moving that governed surface outside the enterprise boundary. That is a different posture from a generic public directory listing.
### **Is this build-time or runtime?**
Do not collapse every agentic tool into one bucket.
MCP servers are usually build-time or operator-time connectors. They help coding agents and assistants read context, call tools, scaffold work, or interact with systems.
Runtime agent governance is different. Form.io's [Universal Agent Gateway](https://form.io/uag/) belongs in that adjacent category. UAG is not the same thing as the Form.io MCP Server. The MCP Server helps AI coding agents build against Form.io patterns. UAG governs production agent workflows at runtime.
Regulated teams need both concepts, but they should not confuse them.
## **The MCP servers worth knowing**
### **1. Official MCP Registry**
Use the official registry as the starting point, not the finish line.
The [official registry](https://modelcontextprotocol.io/registry/about) is valuable because it gives teams a canonical discovery surface for public MCP servers. It supports server metadata, namespace authentication, REST API discovery, package references, and standardized installation information.
For enterprise teams, the important detail is the limit. The registry is public. It is still in preview. It is not where private enterprise servers should live. It also does not remove the need to review code, packages, transport, authentication, scopes, and data handling.
Use it to find servers. Do not use it as your approval workflow.
### **2. GitHub MCP Server**
The [GitHub MCP Server](https://github.com/github/github-mcp-server) belongs in many enterprise developer shortlists because GitHub is where source code, issues, pull requests, Actions, security findings, and review state already live for many teams.
That makes it powerful. It also makes it sensitive.
A coding agent that can inspect a repo, summarize issues, open a pull request, or reason over security findings is operating close to the SDLC evidence trail. That can be a good thing when the team scopes access properly. It can be a problem when every repo is available by default.
Use GitHub MCP when the agent needs to work inside the same development boundary developers already use. Scope it to the repositories and operations needed for the task.
### **3. GitLab MCP Server**
GitLab deserves its own place because many regulated organizations use self-managed GitLab or GitLab Dedicated rather than a purely public SaaS setup.
The official GitLab MCP documentation supports GitLab.com, Self-Managed, and Dedicated environments. It also warns that users are responsible for guarding against prompt injection and should use MCP tools only with trusted GitLab objects.
That warning is useful. It says the quiet part plainly: permission inheritance is not the whole security model. If an agent reads hostile issue content, merge request comments, or documentation, those objects can become part of the instruction stream.
Use GitLab MCP where GitLab is already the system of record for code and planning, but pair it with prompt-injection hygiene and object-scope limits.
### **4. AWS MCP Servers**
AWS MCP belongs in the list because cloud infrastructure is where agent mistakes become expensive.
AWS has multiple MCP surfaces, including [AWS Labs servers](https://github.com/awslabs/mcp/) and the generally available [AWS MCP Server](https://aws.amazon.com/blogs/aws/the-aws-mcp-server-is-now-generally-available/). The managed server is especially relevant to enterprise teams because AWS describes IAM guardrails, SigV4-style authenticated access through the Agent Toolkit, CloudWatch metrics, CloudTrail logging, AWS Knowledge MCP, AWS API MCP capabilities, and access to more than 15,000 AWS APIs.
That is exactly why the risk bar is high.
An agent that can ask AWS docs questions is one thing. An agent that can call AWS APIs is another. The minimum viable control is least-privilege IAM, environment separation, and CloudTrail visibility. Without those, cloud MCP access is too broad for regulated workflows.
Use AWS MCP for documentation, architecture support, and tightly scoped operations. Do not give a general coding agent broad cloud authority just because the server exists.
### **5. Azure MCP Server**
Azure MCP is important for teams whose cloud control plane already sits under Microsoft identity.
Microsoft's Azure MCP Server documentation describes integration with Azure resources, developer tools such as VS Code and GitHub Copilot, and authentication through Azure Identity. For enterprise teams, the key phrase is not "Azure resources." It is identity inheritance.
If the server can operate through Entra ID-backed access patterns and the same Azure permissions teams already govern, it fits better than a standalone connector with its own unmanaged secrets.
Use Azure MCP where the team already has mature Azure role design, environment separation, and resource governance.
### **6. Atlassian Rovo MCP Server**
Jira and Confluence are where a lot of enterprise work actually lives: requirements, tickets, runbooks, decisions, incident notes, acceptance criteria, and stakeholder context.
Atlassian's Rovo MCP Server documentation describes OAuth 2.1, support for Jira, Confluence, and Compass, permission inheritance, and IP allowlisting behavior in Atlassian Cloud.
That makes it a strong context server, especially for coding agents that need product intent or implementation history.
The risk is also obvious. Tickets and docs often contain sensitive business context, customer details, credentials copied where they should not be, and architectural notes. Permission inheritance helps, but it does not classify the content for you.
Use Atlassian MCP for project and documentation context, with clear limits on what spaces, projects, and user scopes are exposed.
### **7. Playwright MCP**
Playwright MCP is one of the most useful developer servers because it gives agents a structured way to interact with web pages and browser workflows.
The [Playwright MCP docs](https://playwright.dev/docs/getting-started-mcp) describe use of accessibility snapshots rather than screenshots or pixel-based interaction. That is the right foundation for repeatable browser automation.
But the same documentation also warns that direct Playwright code execution is effectively remote code execution and should only be enabled for trusted MCP clients.
That is the regulated-enterprise lesson in miniature. A tool can be both useful and unsafe if enabled in the wrong mode.
Use Playwright MCP for testing, QA, browser workflows, and UI validation. Disable unsafe direct-code tools unless the client and execution environment are trusted.
### **8. Sentry MCP**
The [Sentry MCP Server](https://github.com/getsentry/sentry-mcp) belongs in the operational layer. It helps agents inspect errors, traces, issues, and debugging context.
That can compress the time between "the build failed" and "the actual production error is understood." It also exposes operational data that may include request context, user metadata, stack traces, and environment details.
For regulated teams, observability MCP should be scoped like production support access, not like a convenience plugin.
Use Sentry MCP when the agent is doing debugging or remediation work, and restrict the projects, environments, and data fields that should be visible.
### **9. Docker MCP tooling**
[Docker's MCP tooling](https://docs.docker.com/reference/cli/docker/mcp/) is less about one business system and more about packaging, gateway behavior, and local developer operations.
That makes it useful for standardization. Enterprise teams do not want every developer hand-rolling MCP server installation and transport decisions in a different local config file.
Use Docker MCP tooling to make server setup more repeatable, especially when you need a catalog or gateway-style operating model across teams.
### **10. Form.io MCP Server**
Form.io belongs in this MCP server list because regulated applications often begin at the data-capture layer: forms, resources, validation rules, submission records, workflow actions, APIs, permissions, revisions, and audit evidence.
That is the layer where generic coding agents can create drift fastest.
One team builds a React form. Another builds a different submission API. A third adds an agent workflow. Each piece works. None of them share the same governance contract.
The [Form.io AI toolset](https://form.io/ai/) exists to push the agent toward the governed path at build time. The Form.io MCP Server connects AI coding agents to a customer's self-hosted Form.io deployment so they can read, create, and scaffold forms, resources, actions, and APIs from the same platform primitives. Form.io Skills guide the agent toward platform-specific patterns. The Agentic Coding Plugin brings that MCP Server and skill library into the developer's coding environment.
That makes Form.io different from a generic connector.
It is not just giving an agent another data source. It is giving the agent a governed application primitive: schemas that can produce interfaces, APIs, validation behavior, submissions, permissions, and workflow hooks from the same definition.
For teams using Form.io as [schema-driven application infrastructure](https://form.io/platform/), this is the right kind of MCP server: one that makes the governed path easier than building around it.
That value shows up in customer language too. In a [Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/), a long-time Form.io platform user put it plainly: "Form.io cleans up all the dirty work and does it for you." The surrounding case study frames that value as months of development time saved on a next-generation application launch.
## **How to decide what belongs in your agent context**
The fastest way to create MCP sprawl is to install every useful server globally.
Do not do that.
Treat MCP servers like permissions. Most should be project-specific, task-specific, or environment-specific.
Use this sequence:
1. Start with read-only discovery.
2. Prefer official or vendor-maintained servers.
3. Scope by project, repo, workspace, tenant, or environment.
4. Keep mutation tools disabled until the workflow needs them.
5. Separate local development access from production access.
6. Route secrets through existing identity systems where possible.
7. Log agent actions in the system of record.
8. Review prompt-injection exposure when the server reads user-authored content.
9. Revoke unused servers.
That may sound slower than "install the top 20 MCP servers." It is not slower when you count remediation.
A regulated team that cannot explain which server had which permission at which point in a workflow does not have an MCP strategy. It has a collection of shortcuts.
## **Why domain-specific MCP matters**
Generic MCP servers are good at giving agents access to tools. Domain-specific MCP servers are better when the agent needs to create governed artifacts.
That difference is especially important for forms and workflow data.
A generic file server can read a schema file. A GitHub server can modify code. A browser server can test a form. None of those, by itself, tells the agent what a valid governed form workflow should look like inside the enterprise.
Form.io's MCP Server does.
The reason is architectural. Form.io is not only a form renderer. Its [drag-and-drop form builder and API model](https://form.io/features/drag-and-drop-form-builder-apis/) treats form definitions as JSON-backed application infrastructure. Forms can produce APIs. Submission data is managed separately from Form JSON. Form revisions and submission management matter because historical state and current state are not always the same thing.
That is why the Form.io MCP Server matters for regulated developers. It helps the coding agent build with the same primitives the platform governs: forms, resources, actions, APIs, roles, group permissions, server-side actions, [form revision history](https://form.io/features/form-revisions-form-json-schema/), and [complete audit trails](https://form.io/features/log-forms-complete-audit-trail/).
That does not mean Form.io replaces GitHub, GitLab, AWS, Azure, Playwright, Sentry, or Atlassian. It means Form.io occupies a different layer: the form and workflow infrastructure layer where business data enters the system and becomes governed submission state.
## **What proof should enterprise teams look for?**
Popularity is weak proof.
Stars, upvotes, and directory rank tell you that a server is visible. They do not tell you whether the server is appropriate for regulated work.
Better proof looks like this:
- Official or vendor-maintained source.
- Clear authentication model.
- Clear transport model.
- Least-privilege configuration.
- Permission inheritance from the system of record.
- Audit logging for meaningful actions.
- Environment separation.
- Versioned releases.
- Security guidance.
- Support for private or self-managed deployment where needed.
The production-readiness gap is real. A [2026 research paper on production MCP](https://arxiv.org/abs/2603.13417) reports more than 10,000 active MCP servers and 97 million monthly SDK downloads, while also arguing that production MCP still needs stronger identity propagation, adaptive tool budgeting, structured error semantics, and observability.
That is the point. MCP adoption is moving faster than MCP governance.
The answer is not to wait. The answer is to be precise.
Use servers that inherit controls you already trust. Scope them narrowly. Prefer domain-specific servers when the agent is creating governed artifacts. Treat runtime agent governance as a separate layer from coding-time MCP.
## **Key takeaways**
- An MCP server list helps you discover options, but it does not approve them for regulated use.
- Official and vendor-maintained servers should carry more weight than generic directory entries.
- Evaluate each server by identity, permissions, audit evidence, transport, data boundary, and mutation risk.
- GitHub, GitLab, AWS, Azure, Atlassian, Playwright, Sentry, Docker, and Form.io each occupy different control surfaces.
- Form.io's MCP Server is a build-time path into governed form and API infrastructure; UAG is the separate runtime governance layer.
## **FAQ**
### **What is an MCP server list?**
An MCP server list is a directory, registry, repository, or article that helps developers find Model Context Protocol servers. The best starting point is the official MCP Registry, but regulated teams should treat any list as discovery rather than approval.
### **What is the safest way to find MCP servers?**
Start with official sources: the official MCP Registry, vendor documentation, vendor-maintained GitHub repositories, and your own internal registry for private servers. Avoid installing servers only because they appear in a public directory or social post.
### **Are MCP servers secure?**
MCP servers are not automatically secure or unsafe. Security depends on the server's code, maintainer, transport, authentication model, tool scope, permissions, data access, and execution environment. The MCP security guidance specifically calls out risks such as confused deputy behavior, token passthrough, SSRF, session hijacking, local compromise, and scope minimization.
### **Should regulated teams use community MCP servers?**
Sometimes, but not casually. A community server can be useful for low-risk local workflows, prototypes, or read-only tasks. For sensitive systems, prefer official or vendor-maintained servers, or run an internal review before adding the server to an enterprise agent environment.
### **Which MCP servers are best for developers?**
A practical regulated-enterprise list usually starts with GitHub or GitLab for SDLC work, Playwright for browser testing, AWS or Azure for cloud workflows, Atlassian for ticket and documentation context, Sentry for debugging, Docker for packaging and gateway patterns, and Form.io for governed form/API infrastructure.
### **What is the difference between an MCP registry and an MCP server?**
An MCP registry helps you discover servers and their metadata. An MCP server is the actual connector that exposes tools, data, or actions to an MCP client. A registry is not a security review, and it does not mean the server is safe for your environment.
### **How does Form.io fit into an MCP server list?**
Form.io fits when the agent needs to work with governed form and workflow infrastructure. The Form.io MCP Server gives AI coding agents access to Form.io forms, resources, actions, and APIs inside the customer's deployment boundary, while Form.io Skills guide the agent toward platform-specific implementation patterns.
### **Is Form.io UAG an MCP server?**
No. Form.io's MCP Server is build-time infrastructure for AI coding agents. UAG is runtime governance for production agent workflows. They belong in the same agentic architecture conversation, but they are not the same component.
### **Should MCP servers be installed globally?**
Usually no. Global installation encourages overbroad access. Regulated teams should scope MCP servers by project, workspace, environment, repository, tenant, or task. Mutation tools should be enabled only when the workflow requires them.
### **What should an enterprise MCP policy include?**
At minimum, it should define approved server sources, identity requirements, permission scopes, logging expectations, data-boundary rules, prompt-injection handling, environment separation, and a removal process for unused or deprecated servers.
### **When should a team build its own MCP server?**
Build your own MCP server when the system is internal, private, highly regulated, domain-specific, or poorly represented by public servers. Private systems should not be forced into public registries just to make them usable by agents.
## **Build Governed Form And API Workflows With Form.io**
If your team needs AI coding agents to build against governed forms, generated APIs, submission records, permissions, revisions, and self-hosted infrastructure, [try Form.io for governed form and API workflows](/try-formio-for-free/).
# AI Governance Platform: Agentic Workflow Governance Layers Compared
[  ](https://form.io/ai-governance-platform-agentic-workflow-governance-layers-compared/)AI governance platform searches hide several different problems under one phrase. A policy registry is not runtime tool-call control. A process engine is not schema-driven data access. If agents can read data, invoke tools, submit records, and trigger workflows, governance has to live where the agent acts. This comparison names the layer before judging the tool.
## **The AI Governance Gap Is Now Operational**
Most AI governance conversations started with model risk, policy documentation, and compliance review. Those still matter.
But agentic workflows add a sharper question: what happens when the AI system can do something?
Grant Thornton's 2026 AI Impact Survey found that 78% of senior business leaders lacked full confidence that their organization could pass an independent AI governance audit within 90 days. The same survey said 46% of leaders believed AI underperformed because controls and compliance were not working ([Grant Thornton](https://www.grantthornton.com/insights/press-releases/2026/april/grant-thornton-survey-on-ai-proof-gap)).
That is not just a board-level policy problem. It is an infrastructure problem.
Gartner's 2025 strategic technology trends report predicted that by 2028, at least 15% of day-to-day work decisions would be made autonomously through agentic AI, up from 0% in 2024 ([Gartner](https://www.gartner.com/en/newsroom/press-releases/2024-10-21-gartner-identifies-the-top-10-strategic-technology-trends-for-2025)). If even a small share of ordinary operational decisions moves through agents, governance has to follow the action, not only the policy record.
If an agent can approve a request, update a record, route a case, draft a decision, trigger an integration, or submit structured data into a system of record, the organization needs more than a governance statement. It needs an execution path that can answer:
- What was the agent allowed to do?
- Which identity or role gave it that permission?
- What schema, validation rule, or process state constrained the action?
- Was a human required to approve it?
- What audit evidence exists after the action?
An AI governance platform can help with policy, inventory, and risk. An agentic workflow needs that, plus runtime controls at the exact layer where the agent touches the business system.
## **Five Governance Layers To Compare**
The phrase "AI governance platform" is too broad unless you name the layer.
For agentic workflows, the main layers are:
**Governance layer****What it governs****Example fit**AI policy and risk governanceAI inventory, use cases, risk tiering, compliance evidence, board reportingCredo AI, OneTrust, IBM watsonx.governance, classic GRC-style AI governance suitesRuntime agent governanceTool calls, resource access, inter-agent messages, action-level policy enforcementMicrosoft Agent Governance ToolkitProcess orchestration governanceBPMN, case state, human tasks, SLAs, process audit trails, exception handlingCamunda 8.9, Flowable 2025.1, Appian process workflowsPlatform-native agent governanceAgents built and managed inside a specific app/process platformAppian Agent StudioSchema/API/data-access governanceThe forms, fields, validation rules, submissions, APIs, roles, and actions an agent uses to do workForm.io Universal Agent GatewayThese layers can overlap. They can also coexist.
A bank might use Microsoft Entra for agent identities, Microsoft Agent Governance Toolkit for action-level policy, Camunda for cross-system process orchestration, and Form.io UAG for governed access to intake forms, validation, submissions, and downstream workflow actions.
The mistake is treating those as interchangeable.
## **Quick Comparison**
## **Platform or toolkit****Governance center of gravity****Strongest fit****Watch the boundary**Form.io UAGSchema, form, API, submission, RBAC, and action governance exposed to agents through MCPAgents that need governed access to forms, submissions, validation, and workflow infrastructureNot a generic AI GRC dashboard or full BPMN engineAppian Agent StudioAgents embedded inside Appian's process/application platformTeams already building workflows in AppianStrong inside Appian's platform boundary; less about portable schema/API ownershipCamunda 8.9BPMN-based agentic orchestration, human tasks, process state, audit logs, MCP/A2ATeams that govern work through explicit process modelsGovernance starts at orchestration; the data-capture/schema layer may still live elsewhereFlowable 2025.1Agent engine beside BPMN/CMMN/DMN, agent exchange tracking, case/process controlDynamic case work and process automation with first-class agentsStrong process layer; still needs source-of-truth data contractsMicrosoft AGTRuntime policy enforcement, identity, sandboxing, OWASP agentic risk controlsDevelopers adding action-level governance to agent frameworksA toolkit, not a business workflow or forms infrastructure platform**Form.io UAG: When The Governed Schema Should Become Agent Context**
Form.io's Universal Agent Gateway is strongest when the agent has to operate through a governed form and workflow layer instead of a loose collection of prompts, tools, and credentials.
Form.io's core argument starts below the agent. In Form.io, Form JSON is the schema created by the form builder. The Form.io documentation says that schema is used to render forms inside applications, generate REST API interfaces on the server, and host the form schema at the embed URL ([Form.io Form JSON documentation](https://help.form.io/userguide/forms/form-building/form-json)).
That matters because an agent needs structured context.
An agent does not need a vague prompt saying "collect the right onboarding details." It needs to know which fields exist, which fields are required, what validation rules apply, how submissions are shaped, which actions can run, and what permissions apply to the current actor.
Form.io UAG turns that existing application infrastructure into the agent surface. The UAG page explains that agents can authenticate through existing Form.io auth and SSO, inherit enterprise RBAC, retrieve and route secure data inside the private network, and execute actions governed by Form.io Actions and audit trails ([Form.io UAG](https://form.io/uag/)).
That is a specific kind of governance. It is not "AI governance" as a board dashboard. It is governance at the layer where forms, APIs, submissions, validation, and workflow actions already meet.
This is why Form.io should not be framed as simply another AI agent platform. Form.io's AI page describes UAG as the runtime governance layer for production agentic workflows, while the MCP Server, Skills, and Agentic Coding Plugin support build-time development ([Form.io AI](https://form.io/ai/)). That separation is important. Build-time agents need patterns for creating software. Runtime agents need permissioned, logged access to production workflow surfaces.
The customer proof is not AI-specific yet, so it should be used carefully. But it does show why this infrastructure layer matters. In one Form.io public-sector case study, publicplan supported more than 400 digital public-sector services and 1,000+ forms while meeting strict standards and a short timeline ([Form.io publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)). In another Form.io banking case study, an international banking deployment served 5,000 banking groups and recovered 50% of the team's capacity ([Form.io banking case study](https://form.io/case-studies/how-many-technologies-can-actually-support-the-business-process-transformation-of-serving-5000-banking-groups/)).
Those are not UAG deployment claims. They are infrastructure claims. They show why a governed forms/API/submission layer is valuable before agents arrive. UAG extends that same layer to agents.
### **Strongest Fit**
Form.io UAG is the strongest fit when:
- forms are part of the application contract, not just hosted collection pages
- agents need to understand field structure, validation rules, submission shape, and workflow actions
- the customer needs self-hosted or private-network control
- RBAC, auth, audit trails, and form revisions are already part of the governance model
- the team wants humans and agents operating through the same governed schema layer
Form.io is not the right answer if the buyer only needs a general AI policy registry. It is the right answer when the agent's work touches form-driven application infrastructure.
## **Appian Agent Studio: When Agents Belong Inside The Appian Process Platform**
Appian's governance story is platform-native.
Agent Studio is built for teams that already use Appian to design applications, workflows, data fabric patterns, and enterprise processes. Appian's 25.4 release material frames Agent Studio as a guided way to create enterprise AI agents and drag them into business processes. Appian also says agents embedded in processes can use guardrails, tools, data, and human review inside the process context (Appian Agent Studio release material).
That is a clear fit when Appian is already the process application platform.
The governance center is not the open schema/API layer. It is the Appian platform boundary. Agents live inside the Appian design and process model, use Appian objects and tools, and inherit governance from the Appian environment.
That can be exactly what an Appian customer wants. It is less compelling when a team needs agent access to application-owned forms, APIs, validation rules, submissions, and deployment boundaries outside Appian.
### **Strongest Fit**
Appian Agent Studio fits when:
- the business process already lives in Appian
- low-code process design is the center of gravity
- agents need to operate inside Appian's app/process/data fabric layer
- the organization wants human review and process guardrails inside the same platform
The Form.io contrast is not "Appian cannot govern agents." It can govern them inside its platform. The Form.io distinction is that governance starts at the schema and form infrastructure layer agents use to collect, validate, submit, and route data.
## **Camunda 8.9: When BPMN Orchestration Is The Governance Backbone**
Camunda approaches agentic governance from the process orchestration layer.
In its 8.9 release, Camunda frames agentic orchestration as coordinating AI agents, knowledge workers, tools, and systems across end-to-end business processes. The release emphasizes deterministic process logic, global user task listeners, centralized audit logs, MCP access to running clusters, and A2A support for multi-agent communication (Camunda 8.9 release material).
That is a strong governance story for teams that already model work as BPMN.
The useful distinction is this: Camunda governs the flow of work. It controls process state, human tasks, incidents, retries, escalation, and the audit trail around the process. That is different from governing the form schema, validation logic, submission payload, or field-level context an agent uses before it reaches a process step.
In many architectures, both layers matter.
A government service workflow might use Form.io to collect and validate service request data through self-hosted forms and generated APIs, then use Camunda to orchestrate downstream case routing, approvals, exceptions, and cross-system work. The agent should respect both layers.
### **Strongest Fit**
Camunda fits when:
- BPMN is already the operating language for process governance
- the organization needs explicit process state and incident handling
- agents participate in workflows with human tasks and deterministic rules
- auditability needs to follow the end-to-end process path
Form.io fits earlier in the path: where the agent needs governed access to the structured data, forms, validation rules, and APIs that feed the process.
## **Flowable 2025.1: When Case And Process Work Need First-Class Agents**
Flowable's 2025.1 release puts agents beside BPMN and CMMN rather than treating them as external helpers.
Flowable says the release adds an agent engine alongside its BPMN and CMMN automation engines, with internal agent types such as utility, document, knowledge, and orchestrator agents. It also describes agent exchange tracking as a way to store AI interactions for traceability and audit support (Flowable 2025.1 release material).
That makes Flowable a serious process/case governance comparison.
Its strongest fit is dynamic work: cases, documents, human judgment, process variation, and AI-assisted decisions that need to stay inside a process/case model. If a case state determines what an agent can and cannot do, Flowable's governance center makes sense.
The Form.io distinction is again layer ownership.
Flowable can govern the case or process. Form.io can govern the structured form and submission layer that feeds the case. In agentic workflows, those are connected but not identical.
### **Strongest Fit**
Flowable fits when:
- work is case-heavy and may not follow one fixed process path
- AI agents need to operate inside CMMN/BPMN-style orchestration
- traceability of agent exchanges matters
- the organization wants an agent engine inside the process platform
Form.io fits when the agent's most important constraint is the governed schema, validation, permission, submission, and action surface around data intake and form-driven workflows.
## **Microsoft Agent Governance Toolkit: When Developers Need Runtime Action Controls**
Microsoft Agent Governance Toolkit is the most developer-centered entry in this comparison.
Microsoft introduced AGT as an open-source runtime security governance project for autonomous AI agents. The announcement says the toolkit is designed to work with existing frameworks and includes deterministic policy enforcement, identity, sandboxing, reliability controls, and mapping to OWASP agentic AI risks ([Microsoft open-source announcement](https://opensource.microsoft.com/blog/2026/04/02/introducing-the-agent-governance-toolkit-open-source-runtime-security-for-ai-agents/)).
That layer matters because agents can misuse tools even when the surrounding workflow looks well designed.
Microsoft's later Agent Framework guidance makes the layer even clearer: Agent Framework handles build and orchestration, while Agent Governance Toolkit handles govern and audit. It evaluates tool calls, resource access, and inter-agent messages against policy before execution ([Microsoft Agent Framework and AGT](https://devblogs.microsoft.com/agent-framework/governance-at-the-speed-of-agents-microsoft-agent-framework-and-agent-governance-toolkit-better-together/)).
That is not the same job as Form.io UAG.
AGT helps govern the agent's actions at runtime. Form.io UAG gives agents governed access to Form.io's form, submission, schema, API, RBAC, and action layer. In some architectures, AGT could sit beside or around an agent framework, while UAG provides the business-specific tools and context the agent is allowed to use.
### **Strongest Fit**
Microsoft AGT fits when:
- developers need action-level policy checks inside an agent framework
- tool-call misuse, goal hijacking, rogue agents, or inter-agent trust are the main concern
- the team wants an open-source runtime governance toolkit
- the application/workflow platform is already chosen elsewhere
Form.io fits when the agent needs a governed business surface for form-driven work, not only a policy wrapper around tool calls.
## **How To Choose The Right Governance Layer**
The useful question is not "which AI governance platform should we buy?"
The useful question is: where can the agent create the most risk?
### **If The Risk Is AI Inventory And Compliance Evidence**
Start with a classic AI governance platform.
This is the layer for model inventory, use-case approvals, risk tiers, policy mapping, regulatory documentation, monitoring, and executive accountability. It matters most when the organization cannot answer which AI systems exist, who owns them, what risk category they fall into, or what evidence supports approval.
Form.io does not replace that layer.
### **If The Risk Is Tool-Call Misuse**
Look at runtime agent governance.
This is where Microsoft Agent Governance Toolkit is relevant. It helps evaluate actions before execution and provides runtime security controls for autonomous agent frameworks.
Form.io can supply governed business tools and context; AGT can help enforce broader action-layer policies.
### **If The Risk Is Process Visibility**
Look at process orchestration.
Camunda, Flowable, and Appian are stronger when the work has to be governed as a process or case: state, sequence, incidents, handoffs, human review, SLAs, escalation, and full process auditability.
Form.io can still matter if the workflow starts with governed forms, submissions, and APIs.
### **If The Risk Is Data, Schema, And API Drift**
This is where Form.io belongs.
If humans use one form definition, APIs use another contract, agents use a prompt-based tool description, and workflow actions use yet another set of assumptions, governance will drift. The agent may still complete the task. The organization may not be able to prove that the task followed the governed path.
Form.io's stronger argument is that the same Form JSON and platform layer can define the form, the validation, the generated API surface, the submission shape, permissions, and the runtime agent context.
That starts with deployment control. A [self-hosted Form.io](https://form.io/features/self-hosted-forms-for-enterprise/) environment lets the form and submission layer live inside the customer's own infrastructure boundary.
It also starts with the form contract itself. The [drag-and-drop form builder with APIs](https://form.io/features/drag-and-drop-form-builder-apis/) is not only a visual authoring surface; it produces structured definitions that can become application interfaces.
Governance then depends on behavior, not just fields. [Conditional logic and validation](https://form.io/features/form-conditional-logic-form-validation/) help define what data is acceptable before a workflow or agent acts on it.
Finally, the work has to map to people and roles. [Teams and permissions](https://form.io/features/forms-for-teams/) belong in the same architecture conversation because agent access should inherit the same governance model that controls human access.
## **Where Form.io Fits**
Form.io is not trying to be every layer of AI governance.
That is a strength, not a weakness.
Form.io is strongest when forms are application infrastructure: the schema, user interface, generated API, validation model, submission record, permission boundary, and workflow trigger are connected. When agents enter that environment, the agent should not get a separate shadow contract. It should operate through the same governed layer as the application.
That is the UAG argument.
If your organization only needs an AI policy dashboard, choose an AI governance suite. If it needs action-level runtime policy enforcement across agent frameworks, evaluate a toolkit like Microsoft AGT. If it needs process orchestration, evaluate Camunda, Flowable, or Appian.
If the agent needs governed access to forms, fields, submissions, APIs, validation rules, permissions, and workflow actions inside a customer-controlled deployment, Form.io should be in the conversation.
## **Key Takeaways**
- AI governance platform is too broad unless you name the layer.
- Agentic workflows need governance where agents act, not only where policies are documented.
- Form.io UAG governs the schema/API/form/submission/action layer for production agents.
- Appian, Camunda, and Flowable govern agents through process or case platforms.
- Microsoft AGT governs runtime tool calls and action policies.
- The strongest architecture can combine layers instead of forcing one product to do every job.
- Form.io's strongest claim is not generic AI governance. It is governed application infrastructure for agents working through forms, APIs, validation, submissions, permissions, and actions.
## **FAQ**
### **What Is An AI Governance Platform?**
An AI governance platform helps organizations manage AI risk, policy, accountability, compliance evidence, monitoring, and operational controls. In classic enterprise usage, it often includes AI inventory, use-case approvals, risk classification, policy mapping, audit evidence, and reporting.
For agentic workflows, the term needs more precision. A platform that governs model risk is not automatically the same as a tool that governs agent actions, process state, form submissions, or API access.
### **What Is Agentic Workflow Governance?**
Agentic workflow governance is the set of controls that determines what an AI agent can do inside a business process. It covers tool access, data access, identity, permissions, validation, human review, logging, audit trails, exception handling, and policy enforcement.
The key difference is action. A chatbot that answers a question needs content safety. An agent that updates a submission or triggers a workflow needs execution governance.
### **Is Form.io UAG An AI Governance Platform?**
Form.io UAG is most accurately understood as a runtime governance layer for agents operating through Form.io infrastructure. It is not a general AI GRC dashboard.
UAG gives agents governed access to the Form.io layer: forms, field definitions, validation, submissions, actions, auth, RBAC, and application workflow context. That makes it highly relevant to agentic workflow governance, especially when forms and APIs are part of the customer-controlled application stack.
### **How Is Form.io UAG Different From Microsoft Agent Governance Toolkit?**
Microsoft Agent Governance Toolkit focuses on runtime policy enforcement for agent actions: tool calls, resource access, identity, sandboxing, and auditability around the agent framework.
Form.io UAG focuses on the business surface the agent uses when work involves forms, submissions, validation, APIs, and workflow actions. AGT can help govern the agent's behavior. UAG gives the agent a governed Form.io context to operate through.
### **How Is Form.io UAG Different From Process Engines?**
Process engines such as Camunda and Flowable govern processes and cases. They are strong when the main governance problem is end-to-end orchestration: state, sequence, human tasks, incidents, escalation, and process audit trails.
Form.io governs the form and data infrastructure layer. It is stronger when the main governance problem is schema, validation, submissions, permissions, APIs, and form-driven workflow actions. Many enterprise architectures can use both layers.
### **When Should A Team Use A Classic AI Governance Suite Instead?**
Use a classic AI governance suite when the main problem is enterprise oversight: AI inventory, use-case approvals, risk scoring, regulatory mapping, model monitoring, audit evidence, and board-level accountability.
Use Form.io UAG when the main problem is operational: agents need governed access to forms, submissions, validation, APIs, and workflow actions. The two layers can complement each other.
### **Why Does Schema Matter For Agent Governance?**
Agents need structured context. A schema tells the agent what fields exist, which data is required, what validation rules apply, how submissions are shaped, and which actions are meaningful.
When the same schema drives human forms, APIs, validation, and agent context, the organization reduces drift. The agent is less likely to operate from stale prompt instructions or a parallel tool definition that no longer matches the application.
### **Can Form.io Replace A Process Engine?**
No. Form.io should not be framed as a full process engine replacement.
Form.io is infrastructure for forms, APIs, submissions, validation, permissions, and workflow-related actions. If the organization needs full BPMN or case orchestration, a process engine may still be appropriate. Form.io's role is to make the form and data capture layer governed enough for humans, developers, systems, and agents to use safely.
## **Build Governed Agentic Workflows With Form.io**
If your agents need to work through forms, submissions, APIs, validation rules, permissions, and workflow actions inside your own deployment boundary, start with the governed infrastructure layer.
[Try Form.io for governed agentic workflow infrastructure](/try-formio-for-free/).
[ Share](https://www.facebook.com/sharer/sharer.php?u=https://form.io/ai-governance-platform-agentic-workflow-governance-layers-compared/%2F&src=sdkpreparse)#### Webinars
# [](https://form.io/webinars/agentic-coding-for-the-enterprise/)[Agentic Coding for the Enterprise (LIVE Demo: Form.io Agentic Coding Toolset)](https://form.io/webinars/agentic-coding-for-the-enterprise/)
# Date: Wednesday, August 19, 2026 Time: Central [](https://form.io/webinars/enable-self-service-forms-in-your-application/)[Enable Self-Service Forms in Your Application (LIVE Demo: Form.io’s Enterprise Form Builder Module)](https://form.io/webinars/enable-self-service-forms-in-your-application/)
# Date: Thursday, June 25, 2026 Time: 11:00 pm Central [](https://form.io/webinars/byo-css-the-new-standard-for-white-labeling-form-io/)[BYO-CSS: The New Standard for White Labeling Form.io](https://form.io/webinars/byo-css-the-new-standard-for-white-labeling-form-io/)
Date: Thursday, March 26, 2026 Time: 11:00 am Central #### Recent Posts
# [](https://form.io/web-form-builder-apis-self-hosted-control/)[Web Form Builder: When Online Forms Need APIs, Workflows, and Self-Hosted Control](https://form.io/web-form-builder-apis-self-hosted-control/)
# August 5, 2026 [](https://form.io/e-signature-software-self-hosted-form-workflows/)[E Signature Software for Self-Hosted Form Workflows: DocuSign Alternatives for Enterprise Control](https://form.io/e-signature-software-self-hosted-form-workflows/)
# July 21, 2026 [](https://form.io/json-schema-validator-tools-production-apps/)[JSON Schema Validator Tools for Production Apps](https://form.io/json-schema-validator-tools-production-apps/)
# July 20, 2026 [](https://form.io/embedded-forms-b2b-saas-white-label-comparison/)[Embedded Forms for B2B SaaS: The White-Label Form Builder Comparison](https://form.io/embedded-forms-b2b-saas-white-label-comparison/)
# July 17, 2026 [](https://form.io/claims-management-software-insurance-form-builders/)[Claims Management Software Starts With The Forms That Feed It](https://form.io/claims-management-software-insurance-form-builders/)
# July 16, 2026 [](https://form.io/kyc-onboarding-software-financial-services-form-platforms/)[KYC Onboarding Software for Financial Services: Forms, APIs, and Audit-Ready Intake](https://form.io/kyc-onboarding-software-financial-services-form-platforms/)
July 15, 2026 #### Recent Case Studies
# [](https://form.io/case-studies/from-60-pages-to-a-single-click/)[From 60 Pages to a Single Click: How Form.io Powered a Government Agency’s Digitization](https://form.io/case-studies/from-60-pages-to-a-single-click/)
# June 15, 2026 [](https://form.io/case-studies/from-six-week-release-cycles-to-same-day-form-changes-patagonia-health/)[From Six-Week Release Cycles To Same-Day Form Changes – Patagonia Health](https://form.io/case-studies/from-six-week-release-cycles-to-same-day-form-changes-patagonia-health/)
# June 15, 2026 [](https://form.io/case-studies/accelerated-development-time-line-by-two-years/)[Accelerated Development Timeline By Two Years](https://form.io/case-studies/accelerated-development-time-line-by-two-years/)
# May 7, 2025 [](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)[The Digital Transformation Of Supporting New Services For The German Public Sector—On Repeat](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)
December 2, 2024 #### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# Approval Workflow Software for Multi-Step Forms: Find the Best Workflow Forms Tool
*Published:* 2026-07-09
*Author:* Veronika Druck
*URL:* https://form.io/approval-workflow-software-multi-step-forms/
*Description:* While Formstack and Jotform handle basic routing, Form.io is positioned for enterprise teams that need self-hosted, developer-configurable, multi-step approval workflows without usage-based pricing.
[  ](https://form.io/audit-trail-software-enterprise-form-builders-with-native-sdlc/)Audit trail software sounds simple until the record being audited is not just a file, invoice, login, or database row.
Enterprise forms change. Submitted data changes. Validation rules change. Permissions change. Workflow actions fire. APIs read and update the same records that users see in the interface.
For regulated form workflows, the question is not only "Do we have logs?" It is "Can we prove what happened, who did it, what version of the form governed it, and whether the workflow moved through the right control path?"
## **What audit trail software has to prove**
Audit trail software creates a chronological record of activity inside a system.
At minimum, that record should help answer:
- Who performed the action?
- What changed?
- When did it happen?
- Which object, record, form, user, or system was affected?
- What context explains the change?
- Can the record be reviewed later without reconstructing it from guesswork?
That matters because audit trails are not only for after-the-fact compliance reviews. They are also useful for security monitoring, troubleshooting, workflow accountability, and incident investigation.
NIST's log management guidance treats logging as part of a broader cybersecurity evidence system. The draft [NIST SP 800-92 Rev. 1 Cybersecurity Log Management Planning Guide](https://csrc.nist.gov/pubs/sp/800/92/r1/ipd) treats logging as part of a broader cybersecurity evidence system.
Regulated systems make the point even more concrete. [21 CFR 11.10](https://www.law.cornell.edu/cfr/text/21/11.10) requires procedures and controls for closed systems that include secure, computer-generated, time-stamped audit trails for actions that create, modify, or delete electronic records, and it says record changes must not obscure previously recorded information. HIPAA's technical safeguards similarly include [audit controls](https://www.law.cornell.edu/cfr/text/45/164.312) for information systems that contain or use electronic protected health information.
That is the right starting point. Logs are evidence.
But enterprise form workflows need a more specific kind of evidence.
If a claims intake form changes, a patient referral submission is corrected, a public-sector application moves from draft to review, or an embedded customer form is updated through an API, a generic event log may not be enough. The system needs to preserve the relationship between the action and the form infrastructure that governed it.
## **Why enterprise forms need a different audit model**
A form in an enterprise application is not just a page.
It can be:
- a user interface
- a JSON schema
- a validation contract
- a submission model
- a generated API
- a workflow trigger
- a permission boundary
- a document-generation source
- a long-term record
That is why auditability gets harder when forms become application infrastructure.
A simple audit log might show that a user updated a record at 2:14 PM. That is useful, but it does not answer every question an auditor, compliance team, or engineering lead may ask later.
For example:
- Which form version was active when the user submitted the record?
- Did the form have the same required fields then that it has now?
- Was the submitted value changed after capture?
- Was there a documented reason for the change?
- Did a webhook, email, approval action, or downstream integration fire?
- Did the change happen in development, staging, or production?
- Did the API update follow the same permission rules as the portal update?
Those are form-infrastructure questions, not just logging questions.
IBM's 2025 [Cost of a Data Breach Report](https://www.ibm.com/reports/data-breach) puts the global average breach cost at $4.4 million and reports that 63% of organizations lacked AI governance policies. That statistic is not form-specific, but it gives the right scale for the decision. When sensitive data workflows are hard to trace, the risk is not cosmetic.
For enterprise forms, the audit model has to cover both sides of the system: the form definition and the submitted data.
## **The four audit layers enterprise form builders should support**
Most form tools can tell you that a submission exists.
Enterprise form infrastructure needs to tell a deeper story.
### **1. System activity and access logs**
The first layer is the system-level audit log.
This is the record of access, authentication, API requests, data reads, data writes, and other platform activity. It answers questions like:
- Who viewed this submission?
- Who authenticated?
- Which API request changed the record?
- Which project, form, or user was involved?
- Did a request fail?
- Can related events be correlated?
Form.io's [audit logging documentation](https://help.form.io/dev/audit-logging) describes a system-level audit log format with date, event, UUID, project ID, session ID, user ID, and event-specific context. The docs also state that audit logs output to standard out for the Docker container and can be routed into a log aggregation system.
Another note: high-volume system logs should not necessarily store complete submission payloads inside every event. Sensitive form values may need a different audit mechanism than API access events.
The right audit design separates broad activity logging from field-level revision history, then lets teams correlate the two when they need to investigate.
### **2. Form revisions**
The second layer is form revision history.
Enterprise forms change over time. Teams add fields, remove fields, rename fields, update validation rules, change conditional logic, revise consent text, and adjust workflow requirements.
If the form changes after a record is submitted, the system still needs to explain what the form looked like when the record was captured.
Form.io's [Form Revisions documentation](https://help.form.io/userguide/forms/form-revisions) is built for that problem. Form Revisions let teams preserve form versions as forms evolve and can display submission data in the form revision that captured it. The revision interface also exposes who made a revision, when the revision was made, the revision number, and revision notes.
That distinction is central to auditability.
If an auditor reviews a historical submission, the question is not only "What data is in the record now?" It is also "What fields, labels, rules, and structure governed the user when the record was created?"
Without form revision history, teams often have to reconstruct that context from release notes, screenshots, old code, or database backups. That is fragile.
### **3. Submission revisions**
The third layer is submission revision history.
This is the field-level history of changes to submitted data after initial capture.
A submitted form might be corrected by a staff member. A patient record might need an updated value. A claims workflow might need a revised amount. A government service application might need a supporting detail added after review.
In those cases, the system needs to preserve the previous state, the new state, the user who made the change, the time of the change, and any revision note explaining why the change happened.
Form.io's [Submissions documentation](https://help.form.io/userguide/submissions) describes Submission Revisions as an audit logging capability that tracks who updated a submission, when the change was made, and notes associated with the update. The documentation also says the PDF change log can include the revision ID, updating user, date and time, revision note, and list of revision changes.
That is the difference between editing a record and governing a record.
An edit changes the current value. A revision trail preserves the accountable history behind that value.
### **4. Stage, action, and deployment history**
The fourth layer is the SDLC layer.
For enterprise form teams, auditability is not limited to runtime activity. It also includes how form definitions, resources, roles, and actions move through development, staging, and production.
Form.io's [Stages documentation](https://help.form.io/userguide/projects/stages) describes stages as a way to isolate project forms and resources for form management between different environments. The same documentation frames a typical enterprise workflow around Live, Authoring, QA/Test, and Development stages.
That matters because regulated teams often need controlled promotion.
They need a place to build and test form changes before production. They need to know which form version moved forward. They need to avoid ad hoc edits that change production behavior without review. This should not be inflated into a claim that Form.io replaces a full CI/CD or release-management system for all application code. The narrower point is still valuable: form configuration has its own lifecycle, and enterprise teams need a controlled way to manage it.
Audit trail software that ignores the lifecycle layer misses a major part of the form governance problem.
## **A practical comparison framework**
The right audit trail software depends on what kind of system you are auditing.
**Category****Best fit****What it proves****Where it can fall short for enterprise forms**Generic audit log toolingBroad system activity, application events, operational monitoringWho did what, when, and where across systemsUsually does not understand form schema versions or submission-level change historyCompliance audit management toolsPolicy controls, audit programs, evidence management, compliance workflowsWhether controls exist and evidence was collectedOften manages audit process, not the runtime form record itselfAccounting or finance audit trail toolsFinancial transactions, invoices, approvals, accounting changesTransaction history and financial accountabilityUsually narrow to finance workflowsBasic form builders with logsSimple submissions, admin edits, response exportsBasic submission history and account activityMay not preserve form schema history, API-level activity, or stage promotionCustom-built audit trailHighly specific internal applicationsWhatever the team designs and maintainsExpensive to build, test, secure, document, and keep consistent across formsForm infrastructure with native audit controlsRegulated form workflows, embedded forms, generated APIs, long-lived submissionsSystem activity, form revisions, submission revisions, permissions, actions, and stage movementRequires technical ownership and a clear governance modelThe key is fit.
If your team only needs a basic activity log for a contact form, enterprise form infrastructure is probably too much. If your team is managing high-value workflows where form definitions and submitted data both matter, the audit model needs to be native to the form platform.
## **Where Form.io fits**
Form.io is strongest when the form is part of the application infrastructure.
That usually means a team needs some mix of [self-hosted form deployment](/features/self-hosted-forms-for-enterprise/), embedded forms, generated APIs, permissions, workflow actions, form revisions, submission revisions, audit logging, and environment promotion.
The reason is architectural.
Form.io forms and resources are JSON-driven definitions that can render user interfaces, generate APIs, validate submissions, store submitted data, and participate in roles, permissions, actions, stages, and revisions.
That makes auditability part of the same system that owns the form workflow.
[The Security Module](/features/secure-forms-compliance-readiness/) bundles advanced audit logging, action logs, form revisions, submission revision logs, submission collections, and container security scanning. The [complete audit trail feature](/features/log-forms-complete-audit-trail/) separates system-wide audit logs from field-level submission revisions, which is the right separation for high-volume enterprise workflows. The [Form Revisions feature](/features/form-revisions-form-json-schema/) preserves form JSON schema versions so historical submissions can remain explainable as forms evolve.
Form.io also matters when APIs are part of the record. A form workflow may be updated through the portal, an embedded application, or a generated API. The buyer should not have to accept one audit posture for the UI and another for API-driven operations.
That is why generated APIs are relevant to audit trail software. Form.io's [form API model](/features/form-api/) lets teams treat forms and resources as API-connected infrastructure, not isolated web pages. Permissions, submissions, and actions then sit closer to the form data model.
This is also where customer proof matters. [G2's Form.io review page](https://www.g2.com/products/form-io/reviews) describes the platform as deployable into on-premise or private cloud environments, giving customers control of submission data. One enterprise reviewer summarized the practical product experience this way: "Form.io is an intuitive, developer-friendly framework that provides excellent data management." That is not an audit claim by itself. It is buyer proof for the control-and-customization posture that makes audit-heavy form infrastructure worth evaluating.
## **When simple audit logging is enough**
Not every workflow needs all of this.
Simple audit logging may be enough when:
- The form is short-lived.
- Submitted data is low risk.
- Responses are rarely edited after capture.
- The form schema rarely changes.
- The form is not embedded into a regulated application.
- There is no need for DEV/STAGE/PROD promotion.
- Exports are enough for downstream systems.
- The audit question is limited to account activity or submission timestamps.
In those cases, a lighter form builder, basic form backend, or general application log may be a better fit.
The mistake is keeping that model after the workflow becomes infrastructure.
Once forms drive eligibility, claims, intake, onboarding, financial review, patient workflows, public-sector services, insurance applications, or internal approvals, the audit trail has to explain more than "a record changed."
It has to explain the governed context around the change.
## **Evaluation checklist for audit trail software in form workflows**
Use these questions before choosing a form platform for an audit-heavy workflow.
### **Does the platform track system-level activity?**
Look for access events, authentication events, API requests, data reads, data writes, request correlation, and log export options.
### **Does it preserve form schema versions?**
If a field, validation rule, label, or conditional path changes, the platform should preserve enough form history to explain historical submissions.
### **Does it preserve submitted-data history?**
Submission revisions should show who changed a value, when it changed, what changed, and why.
### **Can historical submissions render against the original form version?**
This matters when auditors, legal teams, or operations teams need to understand what a user actually saw at capture time.
### **Are workflow actions included in the governance model?**
Actions such as emails, webhooks, approvals, PDF generation, and save-to-resource operations can affect the record. They should not be invisible.
### **Can forms move through controlled stages?**
Enterprise teams need a way to test, version, and promote forms, resources, roles, and actions without treating production as the editing surface.
### **Do permissions apply close to the form and submission model?**
[Form permissions](/features/form-permissions/) matter because different people may be allowed to create, read, update, delete, approve, or export different records.
### **Can the platform run inside the required deployment boundary?**
Self-hosting does not automatically make a system compliant. It does let the customer place the form platform inside the environment, monitoring, identity, logging, and operational controls the organization already governs.
### **Are forms still usable for builders and developers?**
Audit controls only help if the team can still build and maintain the workflow. A usable [form builder](/features/form-builder/) and a clear [JSON-powered form model](/features/json-powered-forms/) reduce the temptation to route around governance.
## **Key takeaways**
- Audit trail software is not only a logging feature when forms become application infrastructure.
- Enterprise form workflows need evidence across system activity, form revisions, submission revisions, workflow actions, permissions, and stage promotion.
- Generic logs can show that something happened. Form infrastructure should show what version of the form governed the record when it happened.
- Form.io fits best when the form schema, generated API, submitted data, and governance controls need to stay connected.
- The right buyer is not looking for the lightest form tool. They are looking for a form platform that can defend the record later.
## **FAQ**
### **What is audit trail software?**
Audit trail software records system activity in chronological order so teams can review who performed an action, what changed, when it happened, and which record or system was affected.
### **Why do enterprise forms need audit trails?**
Enterprise forms often collect data that drives decisions, approvals, compliance records, customer onboarding, claims, patient workflows, government services, or financial review. If the record changes later, the organization needs evidence of what happened.
### **What is the difference between an audit log and a submission revision?**
An audit log records system-level activity such as access, authentication, API requests, and data modification events. A submission revision preserves field-level history for a specific submitted record.
### **What is the difference between form revisions and submission revisions?**
Form revisions track changes to the form schema: fields, validation rules, conditional logic, layout, and related form structure. Submission revisions track changes to submitted data after capture.
### **Why does form versioning matter for audit trails?**
Form versioning helps explain historical records. If a submission was captured under an older form version, the team may need to review the exact schema, fields, labels, and validation rules that governed that submission.
### **Does self-hosting make audit trail software compliant?**
No. Self-hosting gives the organization more control over deployment, data, logs, identity, monitoring, and infrastructure. Compliance still depends on configuration, policy, controls, documentation, and review.
### **Should audit trail software store every field value in every log?**
Not always. High-volume system logs can become expensive and sensitive if they store full payloads in every event. A better model often separates system audit logs from field-level submission revisions.
### **What should regulated teams look for in form audit trails?**
They should look for system audit logs, form revisions, submission revisions, permissions, workflow/action evidence, stage promotion, exportable evidence, and deployment control.
### **Can generic log management replace native form revision history?**
Generic log management can help centralize and review system events, but it usually does not understand form schema versions, submission rendering, or field-level form data history unless the application sends that context deliberately.
### **When is Form.io a good fit for audit-heavy forms?**
Form.io is a good fit when forms are part of a larger application workflow and the team needs [form workflows](/features/form-workflows/), generated APIs, permissions, revisions, submission history, and customer-controlled deployment.
### **When is Form.io probably too much?**
Form.io may be more platform than needed for a simple contact form, survey, or lead-capture page where the data is low risk and the audit requirement is limited to basic timestamps or account activity.
## **Build audit-ready form infrastructure with Form.io**
# Web Form Builder: When Online Forms Need APIs, Workflows, and Self-Hosted Control
[  ](https://form.io/web-form-builder-apis-self-hosted-control/)A web form builder sounds like a simple category until the form becomes part of a real application. A contact form, signup form, or feedback survey can live in a lightweight tool. A regulated intake process, embedded customer workflow, or API-connected business process needs more than fields on a page.
That is where the buying question changes.
## **What a Web Form Builder Should Do**
A web form builder is software for creating forms users can complete in a browser. At the basic level, it should let a team create fields, set required answers, publish a form, collect submissions, and send the data somewhere useful.
For many teams, that is enough.
Zapier's long-running online form builder list shows how the broad market is usually framed: quick form creation, automation, advanced logic, conversational form experiences, AI-assisted building, Excel sync, approval flows, and reporting options ([Zapier](https://zapier.com/blog/best-online-form-builder-software/)). That is the default expectation buyers bring to the phrase.
The problem is that "web form builder" covers several different jobs:
- a marketing team collecting leads
- an operations team routing internal requests
- a product team embedding forms inside a SaaS application
- a healthcare, insurance, finance, or government team collecting sensitive data
- a development team using forms as part of an API-backed workflow
Those jobs should not be evaluated with the same checklist.
If the form is only a standalone page, the most important questions are speed, templates, design, notifications, and basic integrations. If the form is part of application infrastructure, the questions become more serious: who owns the schema, where does submission data live, what APIs exist, how validation runs, what happens after submit, and whether the platform can operate inside the customer's environment.
## **When a Simple Web Form Builder Is Enough**
A simple web form builder is a good fit when the form is low-risk, isolated, and easy to replace.
Use a lightweight tool when:
- the form collects basic marketing or event information
- submissions can live in the vendor's hosted system
- exporting to a spreadsheet is acceptable
- the workflow after submission is simple
- there are no unusual data residency or deployment requirements
- the form is not deeply embedded in a product experience
- developers do not need to treat the form as an API-backed component
In that world, the best tool is often the fastest tool your team will actually use. A simple builder can be the right decision for a campaign, a workshop signup, a small survey, or a basic internal request.
The mistake is keeping that same mental model after the requirements change.
## **Where Web Form Builders Start To Break Down**
Web forms become harder when the submission is not the end of the process.
A user submits an intake form. Then the data has to create a case, trigger a review, update a CRM, route to a queue, generate a PDF, notify a downstream system, enforce role-based access, or become part of a customer-facing application.
At that point, the form has a second job. It is no longer just collecting answers. It is becoming the front door to a process.
The breakdown usually shows up in five places.
### **The Data Model Lives Somewhere Else**
Many web form builders make it easy to create fields, but the real application data model lives outside the form tool. That creates drift. A field is required in the form but optional in the backend. A dropdown changes in the builder but not in the API. A validation rule exists in the browser but not server-side.
This is small until the form becomes important.
Then every disconnected rule becomes a place where bad data can enter the system.
### **Integrations Become Workflow Logic**
Basic integrations are helpful. They send a notification, create a spreadsheet row, add a CRM contact, or post to a collaboration tool.
But integration is not the same as workflow ownership.
Enterprise forms often need conditional routing, retries, identity context, external IDs, error handling, and clean handoff to other systems. Form.io's webhook documentation, for example, treats a submission as a payload that can call an external API, map response IDs back to the submission, and optionally wait for the webhook response before continuing actions ([Form.io webhook actions docs](https://help.form.io/form-building/actions/webhook-actions)).
That is a different requirement than "send this form to a spreadsheet."
### **Security And Compliance Become Architecture Questions**
The more sensitive the data, the less acceptable it is to treat the form builder as a detached SaaS box.
IBM's 2025 Cost of a Data Breach Report puts the global average breach cost at USD 4.4 million ([IBM](https://www.ibm.com/reports/data-breach)). That statistic should not be used to scare every team away from hosted tools. It should remind buyers that data capture is part of the security boundary.
For sensitive forms, the evaluation should include:
- where submissions are stored
- who administers the environment
- how access is controlled
- how data moves between systems
- how logs, evidence, and audit needs are handled
- whether the form platform can live inside the organization's deployment model
Self-hosting does not automatically make a system compliant. It gives the organization more control over the environment where compliance controls are implemented and reviewed.
### **Product Teams Need Embedding, Not Just Publishing**
Publishing a hosted form is not the same as embedding a form builder into a product.
If a B2B SaaS team wants customers to create or manage their own forms inside the application, the builder has to respect the product's authentication, permissions, tenant boundaries, styling, and data model. That is closer to an embedded product capability than a public web form.
This is why Form.io's [Enterprise Form Builder Module](https://form.io/features/enterprise-form-builder-module/) matters for platform teams. The point is not only that a user can drag fields onto a canvas. The point is that a company can provide a white-labeled, pre-wired form-building experience inside its own application.
### **Developers Need A Stable Contract**
Developers can work around almost anything once. The cost shows up when every new form requires custom backend glue.
A stronger web form builder for application teams should create a stable contract between the form, the submission record, the API, validation, permissions, and downstream systems.
Form.io's own project documentation says that when a new form is created, a REST API is automatically generated to serve as the backend for the form and for other systems that need to create submissions ([Form.io project docs](https://help.form.io/admin/projects/creating-a-project)). That is the key architectural distinction: the form is not only a UI artifact. It is part of the API surface.
## **A Web Form Builder Evaluation Checklist**
Before choosing a web form builder, separate the easy questions from the questions that determine long-term fit.
Evaluation AreaLightweight Form NeedInfrastructure-Grade Form NeedBuilderDrag-and-drop fields, templates, brandingConfigurable builder, reusable schemas, controlled componentsDataHosted submissions and exportsStructured submission records with API accessWorkflowNotifications and simple integrationsWebhooks, Actions, retries, external IDs, routingValidationClient-side rules and required fieldsSchema-linked validation across UI and server pathsEmbeddingPublic link or iframeNative application embedding and white-label controlDeploymentVendor-hosted SaaSHosted, private cloud, on-premises, or local deployment optionsGovernanceAdmin settingsRoles, permissions, stages, evidence, and environment controlFitCampaigns, surveys, simple intakeProduct workflows, regulated intake, internal systems, multi-tenant SaaSThis checklist prevents a common buying mistake: choosing the easiest form tool for the first version, then rebuilding the entire intake layer once the forms become operationally important.
## **Why APIs Change The Category**
APIs change a web form builder from a page-building tool into an application component.
Without APIs, the form is mostly a destination. Users go there, submit data, and the team exports or forwards the result.
With APIs, the form can become part of the system:
- applications can create and read submissions
- forms can populate fields from external data
- downstream systems can consume structured payloads
- teams can build reporting, review, and workflow layers on top of submission records
- developers can integrate forms into products without treating each one as a one-off project
Form.io's [data integration tools](https://form.io/features/data-integration-tools-for-enterprise-forms/) positioning makes this point directly: forms, resources, submissions, and projects are accessible through REST APIs. The practical value is not just "there is an API." It is that the form builder, schema, submission data, and integration surface are part of the same model.
That matters when teams are building internal tools, partner portals, insurance workflows, healthcare intake, public-sector services, or SaaS onboarding flows.
The user sees a web form. The architecture sees a contract.
## **Why Deployment And Data Control Matter**
Deployment is one of the clearest dividing lines between a simple web form builder and enterprise form infrastructure.
If the form is low-risk, vendor-hosted SaaS is usually fine. If the form handles regulated data, internal process data, customer application data, or data that has to move through controlled systems, deployment becomes part of the buying decision.
Form.io's deployment documentation says the platform can be installed in cloud environments, on-premise data centers, or local machines, and that enterprise deployments can use multi-environment architecture across private cloud or on-prem environments ([Form.io deployment overview](https://help.form.io/deploy/deployment-overview)). Its on-premises deployment documentation frames on-prem as relevant when infrastructure, compliance, or data-security requirements call for that model ([Form.io on-premises deployment docs](https://help.form.io/deploy/on-premises-deployment)).
This does not make Form.io the right fit for every form.
It makes Form.io relevant when the form layer has to live where the rest of the application lives.
For teams with strict environment rules, that is often the real requirement hiding underneath the phrase "web form builder." They are not only asking for a form canvas. They are asking whether the form system can respect their data boundary, deployment model, access controls, and integration paths.
## **Where Form.io Fits**
Form.io is a stronger fit when the form is part of an application, not just a standalone collection page.
The core difference is that Form.io combines a [drag-and-drop form builder with APIs](https://form.io/features/drag-and-drop-form-builder-apis/). Teams can design forms visually while keeping the underlying structure available as JSON and exposed through generated REST APIs.
That combination is useful when:
- developers need forms embedded in a product
- business users need controlled form authoring
- submissions need to be available through APIs
- workflows need webhooks or server-side actions
- the organization needs self-hosted or on-premises deployment
- forms need to share a governance model with the surrounding application
Form.io is not the best answer when a team only needs a quick public survey or a simple contact form. That buyer should choose the fastest lightweight tool that fits the job.
But when a web form builder has to support real application infrastructure, the decision changes. The value is not only the builder UI. It is the connection between form schema, submission data, generated APIs, deployment control, and workflow actions.
Customer language points to the same distinction. A Trustpilot reviewer described Form.io as useful "for integration and standalone" work ([Trustpilot](https://www.trustpilot.com/review/form.io)). A Form.io case study customer put the infrastructure burden more bluntly: Form.io "cleans up all the dirty work" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)).
That is the real category line.
A basic web form builder helps a team make a form. Form.io is for teams that need the form to become a governed part of the application.
## **Key Takeaways**
- A web form builder can mean anything from a simple contact form to an embedded application workflow.
- Lightweight tools are a good fit when forms are low-risk, standalone, and easy to replace.
- Enterprise teams should evaluate APIs, validation, submissions, workflow actions, permissions, and deployment control.
- Form.io fits when the form layer needs to operate as controlled application infrastructure, not just a hosted form page.
- Self-hosting is not a compliance shortcut; it is a control model for teams that need to own the environment.
## **FAQ**
### **What Is A Web Form Builder?**
A web form builder is software for creating forms that users complete in a browser. Basic builders focus on fields, templates, publishing, notifications, and exports. More advanced builders support APIs, workflows, permissions, embedding, and controlled deployment.
### **What Is The Difference Between A Web Form Builder And An Online Form Builder?**
The terms often overlap. "Online form builder" usually points to hosted SaaS tools for creating and publishing forms quickly. "Web form builder" can mean the same thing, but it is also used by product and development teams looking for embeddable form-building inside a web application.
### **When Is A Basic Form Builder Enough?**
A basic form builder is enough when the form is low-risk, standalone, and does not need deep integration with internal systems. Examples include event registration, simple lead capture, small surveys, and basic internal requests.
### **When Does A Web Form Builder Need APIs?**
A web form builder needs APIs when other systems must create, read, update, route, or report on submissions. APIs matter when forms are part of a product, portal, approval workflow, regulated intake process, or internal system of record.
### **Why Does Form Schema Matter?**
The schema defines the form's structure and behavior. In a schema-driven model, the same definition can support rendering, validation, submissions, APIs, workflow actions, and governance. That reduces drift between what the user sees and what the backend expects.
### **Can A Web Form Builder Be Self-Hosted?**
Some web form builders are hosted-only. Form.io supports self-hosted deployment models, including cloud, on-premises, and local environments according to its deployment documentation. That matters when the organization needs control over hosting, network boundaries, data storage, and operational review.
### **Is Self-Hosting The Same As Compliance?**
No. Self-hosting gives the customer more control over the environment, but compliance still depends on configuration, policies, controls, monitoring, documentation, and the broader system boundary. The value is control, not a shortcut around responsibility.
### **Why Would A SaaS Product Need An Embedded Form Builder?**
A SaaS product may need customers or internal teams to create forms inside the product itself. In that case, the builder has to respect tenant boundaries, authentication, permissions, styling, and data storage. A public form link is not enough.
### **How Is Form.io Different From A Simple Form Tool?**
Form.io is built for teams that need forms, submission data, generated APIs, workflow actions, and deployment control together. It can still provide a drag-and-drop builder, but the stronger reason to use it is when forms need to operate inside application infrastructure.
## **Build Web Forms That Fit Your Application Architecture**
# E Signature Software for Self-Hosted Form Workflows: DocuSign Alternatives for Enterprise Control
[  ](https://form.io/e-signature-software-self-hosted-form-workflows/)E signature software is usually evaluated as a document workflow tool: send a PDF, collect a signature, store an audit trail, and move on.
That is enough for many contracts. It is not enough when the signature is attached to regulated intake, eligibility data, consent records, financial applications, healthcare workflows, or other form submissions that must stay inside your application boundary.
The better question is not only, "Can this document be signed?" It is, "Can we defend the signed record later, with the data, schema, context, and audit trail intact?"
## **What E Signature Software Usually Solves**
Most e signature software helps teams replace wet signatures with an electronic signing process. The standard workflow is familiar: upload a document, place signature fields, route it to signers, authenticate the signer, collect consent, and retain a completed envelope.
That category is large because the paper problem is large. [Grand View Research estimated](https://www.grandviewresearch.com/industry-analysis/digital-signature-market-report) the global digital signature market at USD 6.9 billion in 2025 and projected a 43.9% CAGR from 2026 to 2033.
But market size does not tell you which architecture fits your use case.
Standalone signing platforms are strongest when the signed artifact is the document itself: contracts, sales agreements, HR forms, procurement packets, vendor agreements, and legal paperwork. In those cases, the system of record is often the completed document package.
Form-driven applications are different. The signed evidence may need to stay attached to a submission record, user identity, form version, field values, workflow state, API transaction, and downstream system update.
That is where a normal e-signature checklist starts to miss the real buyer risk.
## **Why DocuSign Alternatives Become Relevant**
DocuSign is the name many buyers know first. Adobe, Dropbox Sign, PandaDoc, Zoho Sign, OneSpan, and other tools also belong in the traditional e-signature conversation.
Those tools can be the right choice when your team mainly needs a document-signing workflow. The mistake is assuming that the best document-signing platform is automatically the best signing architecture for application data.
Teams start looking for DocuSign alternatives when one or more constraints appears:
- signature data must stay inside a private cloud, VPC, on-premise, or controlled deployment boundary
- the signed record begins as structured form data, not a static PDF
- signer consent needs to connect to the exact fields and submission context that were signed
- APIs, webhooks, roles, permissions, and audit history matter as much as the visual signature
- pricing or operations become hard to forecast when signatures scale across many workflows
For these teams, the word "alternative" does not simply mean cheaper. It means architecturally different.
## **The Enterprise Evaluation Criteria**
Before choosing e signature software, separate legal acceptance from operational evidence.
The U.S. [ESIGN Act](https://uscode.house.gov/view.xhtml?edition=prelim&path=%2Fprelim%40title15%2Fchapter96) says electronic signatures and records generally cannot be denied legal effect solely because they are electronic. It also points to record retention: electronic records must remain accurate, accessible, and reproducible for later reference.
That retention point matters. A signature event is only as useful as the record your team can reproduce when someone asks what was signed, by whom, under which form version, with which field values, and under which business process.
Evaluate each platform across six criteria.
**Criterion****Why it matters**Deployment controlDetermines where sensitive data, signature proof, and operational evidence live.Record modelShows whether the signed artifact is a PDF envelope, a submission record, or both.Audit trailCaptures the evidence needed to defend the transaction later.API accessDetermines whether signatures can participate in application workflows.Identity and access controlsConnects signing to the right user, role, tenant, or workflow boundary.Pricing modelDetermines whether cost scales predictably across high-volume workflows.The wrong platform can still collect a signature. The problem appears later, when the team needs to prove what the signature means inside the larger system.
## **Where Self-Hosted Form Workflows Change The Question**
Self-hosted form workflows change the center of gravity.
Instead of asking, "Which e-signature vendor should host this envelope?" the team asks, "How do we keep the signed record inside the same infrastructure that owns the form, data, APIs, permissions, and audit history?"
That shift matters for regulated teams, embedded SaaS products, government contractors, healthcare platforms, insurance workflows, financial services onboarding, and internal enterprise portals.
The signature is not a decorative mark. It is a control point in the data lifecycle.
NIST's [digital signature project](https://csrc.nist.gov/projects/digital-signatures) frames digital signatures around generation, verification, and data protection. That distinction is useful for buyers: a visible signature image is not the same thing as verifiable proof that the protected data and context have not changed.
In a form workflow, the strongest signature system should answer questions like:
- Which form version captured the data?
- Which fields were protected by the signature?
- Did the data change after signing?
- Can the application verify the signature through an API?
- Does the signed record remain inside the customer's environment?
- Can the team reproduce the record without depending on a third-party envelope as the only source of truth?
Those are infrastructure questions, not just signing questions.
## **How Form.io E-Sign+ Fits**
[Form.io E-Sign+](/features/cryptographic-e-signatures-for-form-data/) is built for a narrower, more controlled version of the e-signature problem: cryptographically secure signatures associated with Form.io submission data inside the customer's own environment.
That is a different posture than a standalone document-signing workflow.
With Form.io, the [form schema and submission data](/form-json-schema-vs-submission/), generated APIs, permissions, workflow actions, and deployment boundary are already part of the application infrastructure. E-Sign+ extends that infrastructure by letting teams verify signed submission data and context rather than treating the signature as only a PDF-layer event.
The [product documentation](https://help.form.io/dev/integrations/e-sign%2B) describes E-Sign+ as tied to submission data, usable through native submission IDs, and decoupled from PDFs. It can protect selected fields, all form data, and/or submission properties, depending on configuration.
That makes Form.io a strong fit when the signature needs to travel with application data.
Form.io's broader customer proof reinforces the infrastructure value. One customer quote on [Form.io's homepage](https://form.io/) says, "Speed to market using Form.io worked fantastically well," because the team did not have to spend most of its time building its own solution. Another proof point describes cutting data-processing workload by 50%.
Those quotes are not E-Sign+ specific. They do show the larger pattern: Form.io is strongest when teams need to stop rebuilding form, data, API, and workflow plumbing from scratch.
## **E Signature Software Comparison**
**Best fit****Typical tools****Watch the tradeoff**Standard document signingDocuSign, Adobe Acrobat Sign, Dropbox Sign, PandaDoc, Zoho SignStrong for envelopes and documents, but not always ideal when signed evidence must remain attached to application-owned submission data.Developer signing APIsAPI-first signing platformsFlexible for document workflows, but your team still owns the surrounding form schema, data model, and governance path.Self-hosted form signing infrastructureForm.io E-Sign+Strong fit when forms, submissions, APIs, permissions, and signature verification need to stay in the customer's controlled environment.The point is not that every team should leave document-signing platforms. Many should not.
The point is that e signature software has to match the record you are actually signing.
If the record is a contract document, a document-signing tool may be enough. If the record is a governed application submission, the signature belongs closer to the form infrastructure.
## **Key Takeaways**
- E signature software is a broad category, but enterprise form workflows need more than a signed PDF.
- Legal validity is only one part of the evaluation. Record retention, reproducibility, and context matter.
- DocuSign alternatives become relevant when teams need deployment control, API access, data ownership, or application-level signature proof.
- Form.io E-Sign+ fits teams that need cryptographic signature verification tied to submission data inside their own environment.
- The stronger question is not "Which tool signs documents fastest?" It is "Which system protects the signed record your application actually depends on?"
## **FAQ**
### **What Is E Signature Software?**
E signature software lets people sign electronic records or documents without printing and scanning paper. In business workflows, it usually includes signer routing, authentication, consent capture, audit history, completed document storage, and API or integration options.
### **Is E Signature Software Legally Binding?**
Electronic signatures can be legally valid in many contexts, including under the U.S. ESIGN Act and [EU eIDAS rules](https://ec.europa.eu/digital-building-blocks/sites/spaces/DIGITAL/pages/467109069/What%2Bis%2BeSignature). Buyers should still review the specific transaction type, jurisdiction, identity process, consent language, retention rules, and audit evidence with legal counsel.
### **What Is The Best DocuSign Alternative?**
The best DocuSign alternative depends on the job. If the job is standard document signing, a standalone signing platform may fit. If the job is signing structured form submissions inside a controlled application, Form.io E-Sign+ is worth evaluating because the signature proof stays closer to the form data and API workflow.
### **When Should A Team Choose Self-Hosted E Signature Software?**
A team should consider self-hosted signing infrastructure when sensitive submission data, regulatory obligations, customer architecture, data residency, or private deployment requirements make third-party-hosted signing workflows difficult to justify.
### **How Is Form.io E-Sign+ Different From A PDF Signature Tool?**
Form.io E-Sign+ is designed around submission-linked signature proof. PDFs can still be part of a workflow, but the stronger distinction is that E-Sign+ can verify signed form data and context inside the customer's own [self-hosted Form.io environment](/enterprise-self-hosting/).
### **Does Form.io Replace DocuSign?**
Not for every use case. DocuSign is a strong document-signing platform. Form.io is a stronger fit when signatures are part of a governed form workflow, embedded application, or self-hosted data pipeline where submission context matters.
### **What Should Enterprises Look For In E Signature Software?**
Enterprises should evaluate deployment control, signer identity, audit trail quality, API access, retention and reproducibility, [configuration-based pricing](/configuration-based-pricing/), integration fit, and whether the signed record is a document envelope or application data.
### **Can E Signature Software Work With APIs?**
Yes. Many signing platforms provide APIs, but the important question is what the API controls. For form-driven applications, APIs should connect signatures to submission records, permissions, workflow state, and downstream systems.
### **Why Does Signature Context Matter?**
Signature context matters because a signature without the surrounding record can be hard to defend. Teams may need to know the form version, field values, signer identity, submission ID, timestamp, protected fields, and whether anything changed after signing.
### **How Does Form.io Help With Controlled Form Workflows?**
Form.io gives teams [form management infrastructure](/form-management-software/) for forms, submissions, generated APIs, permissions, workflow actions, and self-hosted deployment. E-Sign+ extends that model by connecting signature verification to submission data instead of treating signing as a disconnected document event.
## **Build Signature Proof Into Your Form Infrastructure**
If your team needs signatures that stay attached to governed form data, application APIs, and your own deployment boundary, [try Form.io for self-hosted form workflows](/try-formio-for-free/).
# JSON Schema Validator Tools for Production Apps
[  ](https://form.io/json-schema-validator-tools-production-apps/)Searches for **json schema validator** often start with a simple need: check whether this JSON payload matches this schema.
That is useful. It is also only the first layer.
In a production app, a schema may validate API requests, generate a form, drive documentation, define a submission shape, feed an AI tool, or become part of a governed application contract. The right tool depends on which job the schema has to do.
## **Key takeaways**
- A JSON Schema validator checks whether JSON data conforms to a declared structure, types, required fields, constraints, and references.
- Online validators are useful for quick checks, but production teams usually need runtime libraries, CI checks, API contract tooling, or form infrastructure.
- Ajv, Python `jsonschema`, and Java validators solve the library problem. They do not own form authoring, submissions, permissions, or deployment governance.
- Form generators turn schema into UI, but the backend still has to store, secure, expose, and govern submitted data.
- Form.io fits when schema needs to become form and API infrastructure: builder, renderer, submissions, generated APIs, permissions, workflow actions, revisions, and customer-controlled deployment.
## **Quick answer: which JSON Schema validator tool should you use?**
Use an online validator when you need to test a small schema and sample payload quickly.
Use Ajv when your JavaScript or TypeScript application needs fast JSON Schema validation in Node.js, the browser, an API gateway, or a build process.
Use Python `jsonschema` when your Python services need to validate instances against JSON Schema drafts and report validation errors in application code.
Use a Java validator such as NetworkNT when JSON Schema validation belongs in a JVM service, API layer, or request/response validation path.
Use Spectral or a schema lifecycle tool when the problem is not one payload, but API governance, linting, bundling, testing, and CI.
Use RJSF, JSON Forms, or SurveyJS when the goal is to generate a form interface from structured schema.
Use Form.io when the schema must become production form infrastructure: a human-facing form, submission record, generated REST API, workflow surface, permission boundary, and governed deployment model.
## **What a JSON Schema validator actually proves**
JSON syntax validation and JSON Schema validation are different jobs.
A JSON syntax validator answers: is this valid JSON?
A JSON Schema validator answers: does this valid JSON match the structure and rules the application expects?
That can include object shape, required fields, string formats, numeric ranges, enum values, array constraints, nested objects, and references to other schema definitions.
The official JSON Schema site describes JSON Schema as the vocabulary that enables JSON data consistency, validity, and interoperability at scale ([JSON Schema](https://json-schema.org/)). The specification hub also separates JSON Schema Core from JSON Schema Validation, where validation defines the keywords used to assert whether data is valid ([JSON Schema specification](https://json-schema.org/specification)).
That distinction matters because many production failures are not syntax failures. They are contract failures.
The payload is valid JSON, but it is missing the field the downstream service expects. The field exists, but the type changed. The UI allowed a value that the backend rejects. The API docs say one thing, but the runtime accepts another. The schema was copied into three services, and now nobody knows which version is authoritative.
A validator can catch part of that. It cannot, by itself, decide where schema ownership lives.
## **The five tool layers behind the search**
The search result page for `json schema validator` looks crowded because people use the same phrase for several different jobs.
**Tool layer****Best fit****What it proves or creates****What the team still owns**Online validatorQuick testing and debuggingA sample JSON instance matches a schemaProduction runtime, security, CI, versioningRuntime validatorAPI requests, service boundaries, app codePayloads satisfy schema rules in a language/runtimeUI, storage, workflows, governanceAPI contract toolingOpenAPI, linting, docs, API style rulesAPI definitions follow a contract and style rulesForm authoring, submissions, application stateForm generatorRendering forms from schemaA schema can produce a user-facing formBackend APIs, permissions, data lifecycleForm/API infrastructureProduction forms, APIs, submissions, workflowsSchema governs form UX, submission shape, generated APIs, and data handlingProduct fit, deployment ownership, policy configurationThe mistake is asking, "What is the best JSON Schema validator?" without asking, "What part of the system needs validation?"
## **Online validators are useful, but limited**
Online validators are useful for quick checks. They help developers paste in a schema, paste in sample JSON, and see errors immediately.
That is often exactly what the searcher wants.
But online validators should not become the production validation strategy. They are poor places for sensitive payloads. They do not enforce validation in your application. They do not live in CI. They do not control what happens after data is accepted.
Use them like a scratchpad.
For production, validation needs to move into the system path: application code, API gateway, test suite, CI pipeline, schema registry, form builder, or platform boundary.
## **Runtime validators: Ajv, Python, Java, and the application path**
Runtime validators belong where your application receives, transforms, or emits JSON.
Ajv is the obvious JavaScript and TypeScript example. Its documentation says it supports JSON Schema draft-04, draft-06, draft-07, draft 2019-09, draft 2020-12, and JSON Type Definition ([Ajv schema language guide](https://ajv.js.org/guide/schema-language.html)). Snyk's package database currently lists Ajv at more than 272 million weekly npm downloads, which shows how deeply validation libraries can sit inside the JavaScript ecosystem ([Snyk Ajv package page](https://security.snyk.io/package/npm/ajv)).
Python teams commonly reach for `jsonschema`, whose documentation shows the simple `validate` function and the validator classes behind it ([Python jsonschema validation docs](https://python-jsonschema.readthedocs.io/en/stable/validate/)).
Java teams may use NetworkNT's JSON Schema Validator, which describes support for multiple drafts and OpenAPI 3 request/response validation ([NetworkNT JSON Schema Validator](https://github.com/networknt/json-schema-validator)).
These tools are important because validation should happen where the system can reject bad data before it spreads.
The practical checklist is straightforward:
- Confirm which JSON Schema draft or dialect your validator supports.
- Reuse compiled validators where the library recommends it.
- Decide whether validation should fail fast or collect all errors.
- Make error messages useful enough for logs, developers, or users.
- Treat `$ref`, remote references, and bundled schemas as design choices, not incidental details.
- Benchmark against your actual schemas and payload sizes if validation runs in a hot path.
Runtime validators are the right answer when the job is validation.
They are not the whole answer when the same schema also needs to create forms, APIs, permissions, workflows, submission records, and audit evidence.
## **API contract tools: where JSON Schema meets OpenAPI**
For API teams, JSON Schema often appears through OpenAPI.
The OpenAPI Initiative's 3.1 release announcement says OpenAPI Schema Objects are now fully compatible with JSON Schema draft 2020-12 ([OpenAPI 3.1 release](https://www.openapis.org/blog/2021/02/18/openapi-specification-3-1-released)). That matters because the schema can become part of request validation, response validation, documentation, mock servers, SDK generation, and contract testing.
This is where tools such as Spectral fit. Spectral is a JSON/YAML linter designed with OpenAPI, AsyncAPI, and JSON Schema in mind ([Spectral](https://stoplight.io/open-source/spectral)). A validator asks whether data satisfies a schema. A linter can ask whether an API definition follows a team rule.
That is a different level of governance.
For production apps, the better question is not "Can we validate this object?" It is:
- Can we keep the API contract and implementation aligned?
- Can we catch drift in CI before release?
- Can we enforce style and security rules across many APIs?
- Can generated docs, mocks, clients, and tests inherit the same contract?
That is where JSON Schema starts becoming part of operational discipline.
## **Schema lifecycle tools: keep schemas from becoming loose files**
When schemas are shared across teams, a single validator is not enough.
Schema files need formatting, linting, testing, bundling, versioning, and promotion through environments. The official JSON Schema tools page shows how broad the ecosystem has become, including validators, documentation generators, schema-to-code tools, schema-to-web-UI tools, benchmarks, and compliance reports ([JSON Schema tools](https://json-schema.org/tools)).
Sourcemeta's JSON Schema CLI is a good example of the production-lifecycle layer. Its repository describes a CLI for maintaining schema repositories and ensuring quality during local development and CI/CD, including formatting, linting, testing, and bundling ([Sourcemeta JSON Schema CLI](https://github.com/sourcemeta/jsonschema)).
This layer matters when a schema is not a one-off file. It is a source artifact.
If multiple services, teams, or applications depend on it, schema changes need review. References need to resolve. Tests need to run. Breaking changes need to be understood before they reach production.
That is the point where teams stop treating JSON Schema as an isolated validator input and start treating it as part of the application contract.
## **Form generators: when schema becomes UI**
Some teams search for a JSON Schema validator and really need a form generator.
RJSF, for example, is a React component capable of building HTML forms out of JSON Schema. JSON Forms is another JSON Schema-based form renderer with data binding, validation, and rule-based visibility.
These tools are useful when a team wants schema to reduce repetitive form UI work.
But a form generator still leaves major production questions open:
- Where are submissions stored?
- Which API receives the data?
- How are permissions enforced?
- How are form changes versioned?
- How do non-developers safely edit forms?
- How does the schema move between dev, test, and production?
- What happens when the form becomes part of a regulated workflow?
A React JSON Schema form can render fields. That does not make it a form platform.
This is the line Form.io crosses.
## **Where Form.io fits**
Form.io belongs in this conversation only after the lower layers are clear.
It is not a replacement for Ajv, Python `jsonschema`, the JSON Schema specification, or OpenAPI tooling.
Form.io is the better fit when schema needs to become form and API infrastructure.
Form.io's Form JSON documentation says Form JSON defines the structure, appearance, and functionality of a form, and that the schema is used for rendering forms, generating REST API interfaces, and hosting the form schema for embedding ([Form.io Form JSON docs](https://help.form.io/form-building/form-json)).
Its feature documentation also explains that the builder outputs JSON schemas rather than static HTML, and that the same schema defines the UI, validation rules, data model, and REST API endpoints ([drag-and-drop form builder and APIs](https://form.io/features/drag-and-drop-form-builder-apis/)).
That is the infrastructure difference.
A validator can say, "This payload is valid."
A form generator can say, "This schema can render a form."
Form.io can connect the form definition, rendered experience, submission data, generated API, permission model, workflow actions, revisions, and deployment boundary.
That includes the operational pieces validators do not try to own: [self-hosted form deployment](https://form.io/features/self-hosted-forms-for-enterprise/), [form revisions](https://form.io/features/form-revisions-form-json-schema), [complete audit trails](https://form.io/features/log-forms-complete-audit-trail/), [secure forms compliance readiness](https://form.io/features/secure-forms-compliance-readiness/), and [fillable PDF workflows](https://form.io/features/fillable-pdf-forms) when the submitted record also needs document output.
That matters for teams building customer portals, healthcare intake, insurance claims, government services, financial onboarding, internal approval workflows, and B2B SaaS products where forms are part of the application architecture.
There is also customer proof behind this pattern. G2's indexed Form.io reviews include a State of Ohio pandemic-response example where Form.io was used to stand up forms, store and present data through an API, and feed analytics dashboards. The same reviewer called the model "easy to manage" across hundreds of websites ([G2 Form.io reviews](https://www.g2.com/products/form-io/reviews)).
Form.io's own customer proof makes the same point from the build-vs-buy side. Edify.ai said speed to market with Form.io "worked fantastically well" and that the team could focus development time on proprietary work instead ([Form.io customer proof](https://form.io/)).
The honest framing is this:
Use a JSON Schema validator when validation is the job.
Use Form.io when the schema needs to become a governed form, API, and submission system.
## **A production checklist for choosing JSON Schema tools**
Before choosing a tool, answer these questions.
### **1. Where does validation happen?**
Validation may belong in the browser, backend service, API gateway, test suite, CI pipeline, ETL job, or form platform.
One schema may need several validators in different places. That is normal. The risk is when each surface evolves its own slightly different rules.
### **2. Which schema version do you support?**
JSON Schema draft support is not trivia. Draft-07, 2019-09, and 2020-12 do not behave identically.
Pin the version. Document it. Make sure your tooling supports it before using draft-specific keywords in production.
### **3. Who owns schema changes?**
If schemas define production behavior, they need ownership.
A change to a field, type, required value, nested object, or reference may affect UI, API behavior, stored submissions, integrations, reports, and historical records.
### **4. Is the schema only validating data, or generating behavior?**
If the schema only validates API payloads, a runtime library may be enough.
If the schema renders forms, generates APIs, controls submissions, and drives workflow behavior, the decision belongs at the platform layer.
### **5. What happens after validation passes?**
This is the question most validator pages skip.
Where does the data go? Who can see it? Can it be edited? Is there revision history? Does it trigger a webhook? Can the workflow be audited? Can the platform run inside your environment?
If those questions matter, you are no longer only choosing a JSON Schema validator.
## **Key takeaways**
JSON Schema validators are necessary tools, but the phrase hides several different jobs.
Online validators help with quick checks. Runtime validators enforce contracts in code. API tooling keeps definitions consistent. Schema lifecycle tools keep shared schemas maintainable. Form generators turn schema into UI.
Form.io is for the next layer: production forms and APIs governed by schema, with submissions, permissions, workflows, revisions, and deployment control attached.
That is the practical distinction. Do not make a validator carry the full application burden. Use the validator where validation belongs, and choose infrastructure when the schema becomes infrastructure.
## **FAQ**
### **What is a JSON Schema validator?**
A JSON Schema validator checks whether JSON data conforms to rules described in a JSON Schema. Those rules can define object structure, required fields, data types, arrays, enums, numeric limits, string formats, and references to other schemas.
### **Is JSON validation the same as JSON Schema validation?**
No. JSON validation usually means checking whether the text is valid JSON syntax. JSON Schema validation checks whether valid JSON data matches an expected schema.
### **What is the best JSON Schema validator for JavaScript?**
Ajv is one of the default choices for JavaScript and TypeScript teams. It supports multiple JSON Schema drafts and is widely used across Node.js and browser environments.
### **What is the best JSON Schema validator for Python?**
Python teams commonly use the `jsonschema` package. It implements JSON Schema validation and provides validator classes, error handling, and draft-aware behavior.
### **Can JSON Schema generate forms?**
Yes, some tools can render forms from JSON Schema. RJSF and JSON Forms are common examples. The important distinction is that rendering a form does not automatically provide backend APIs, submission storage, permissions, or workflow governance.
### **Does OpenAPI use JSON Schema?**
OpenAPI 3.1 aligns its Schema Object with JSON Schema draft 2020-12. That makes JSON Schema more important for API contracts, documentation, request and response validation, and API tooling.
### **Should I paste sensitive data into an online JSON Schema validator?**
For sensitive production data, avoid it. Online validators are useful for examples and debugging, but regulated or customer data should be validated inside tools and environments your team controls.
### **What should production teams check before choosing a validator?**
Check draft support, runtime support, error quality, performance, custom formats, `$ref` handling, CI integration, schema bundling, and how schema changes are governed over time.
### **Is Form.io a JSON Schema validator?**
Form.io is not best understood as a standalone JSON Schema validator. It is a schema-driven form and API platform. It uses schema to help govern forms, submissions, generated APIs, permissions, workflows, and deployment control.
### **When should a team use Form.io instead of only a validator library?**
Use Form.io when the schema needs to operate a production form workflow, not just validate a payload. That includes embedded forms, submission records, generated REST APIs, permissions, workflow actions, revisions, and self-hosted deployment.
### **Can Form.io work alongside validators like Ajv?**
Yes. A production architecture can use validation libraries at service boundaries while using Form.io for the form, API, submission, and workflow layer. The key is deciding which system owns each contract.
If your schema needs to do more than validate JSON, [try Form.io for free](/try-formio-for-free/) and see how forms, APIs, submissions, and workflow controls can live on one foundation.
# Embedded Forms for B2B SaaS: The White-Label Form Builder Comparison
[  ](https://form.io/embedded-forms-b2b-saas-white-label-comparison/)Embedded forms are easy to misunderstand.
For a marketing team, an embedded form might mean a signup widget pasted into a page. For a B2B SaaS platform, it can mean something much heavier: a branded form experience inside the product, customer-managed form creation, tenant-specific permissions, API-backed submissions, and workflow rules that cannot drift from the rest of the application.
That is the difference this comparison is about.
## **Embedded forms become product infrastructure**
An embedded form is a form rendered inside a webpage or application, usually through an iframe, script, SDK, component, or framework integration.
That definition is useful, but too broad. It puts a newsletter signup form and a customer-facing SaaS form builder in the same bucket.
B2B SaaS teams need a sharper distinction:
- Embedded form: a finished form appears inside your website or app.
- Embedded form builder: your users or admins can create and edit forms inside your product.
- White-label form infrastructure: the forms, builder, submissions, APIs, branding, roles, tenant boundaries, and workflow behavior all operate as part of your product.
That last category is where Form.io belongs. The [Form.io Enterprise Form Builder Module](https://form.io/enterprise-form-builder-module/) is built to embed a white-labeled form builder inside an application while the platform owner keeps control over components, data model, permissions, and workflow behavior.
## **Quick comparison**
**Option****Best fit****Main strength****Main tradeoff**Form.ioB2B SaaS teams that need embedded forms, embedded form building, APIs, tenant-aware control, and deployment flexibilityForms behave like governed application infrastructureMore platform than a simple marketing form team needsJotformHosted enterprise teams that want template-rich no-code form building and broad business workflowsFast, familiar hosted form creationStrongest when the form system can remain vendor-hosted and account-centeredFeatheryProduct teams that want polished embedded form UX and a white-label editor experienceStrong product-form experience and editor customizationTeams still need to evaluate backend governance, deployment, and data ownership depthSurveyJSJavaScript teams that want form libraries and a builder they can wire into their own stackDeveloper control inside front-end applicationsMore assembly work around storage, APIs, permissions, and operationsFormsortTeams building branded conversion flowsManaged branded flows with conversion focusNarrower fit when forms become governed product infrastructure123FormBuilder / similar toolsTeams that primarily need branded hosted forms and account-level white labelingFamiliar form-builder packagingWhite label often centers on branding more than application architectureThe right choice depends less on the phrase "embedded forms" and more on what the embedded form has to own.
## **The SaaS evaluation checklist**
If customers only need to submit a contact form, almost any credible form builder can work.
If customers need to create forms inside your application, the checklist changes:
- Can the finished form be embedded cleanly?
- Can the builder itself be embedded?
- Can vendor branding be removed from the form, builder, emails, URLs, and exports?
- Can each tenant have separate forms, submissions, themes, permissions, and workflows?
- Can you restrict which components, validation rules, logic, and publishing actions customers can use?
- Are submissions available through APIs, not only exports or webhooks?
- Where does submission data live?
- Can the form layer run inside the deployment boundary your customers require?
- Are revisions, access controls, and audit evidence part of the model?
- Does the pricing model still work when every customer creates forms?
Those questions are not cosmetic. They are architecture questions.
[Postman's 2025 State of the API report](https://voyager.postman.com/doc/postman-state-of-the-api-report-2025.pdf) found that 82% of organizations had adopted some level of API-first approach. That matters because embedded forms in a SaaS product are not just pixels. They create records, trigger workflows, and pass data to the rest of the application.
## **Where Form.io fits**
Form.io is the strongest fit when embedded forms need to behave like part of the product infrastructure.
The [Form.io form embedding documentation](https://help.form.io/dev/form-embedding) covers quick inline embedding, JavaScript embedding, iframe fallback, builder embedding, and framework embedding. That gives teams a practical path from simple rendering to deeper application integration.
But the more important distinction is what sits behind the embed.
Form.io forms are JSON-driven definitions connected to rendering, validation, submissions, APIs, permissions, and workflow behavior. The [drag-and-drop form builder with APIs](https://form.io/features/drag-and-drop-form-builder-apis/) is not only a UI for arranging fields. It is part of a system where form definitions can become application contracts.
That matters for SaaS platforms where customers need their own forms, variations, permissions, and branded experiences. The [Form.io homepage](https://form.io/) explicitly frames white-label SaaS use around form, API, and data management under the platform's brand or the customer's brand. It also describes multi-tenant child-project patterns for separating forms, data, and form building.
For more controlled environments, the [self-hosted Form.io deployment model](https://form.io/features/self-hosted-forms-for-enterprise/) matters because the form layer can live closer to the customer's infrastructure boundary instead of becoming an external data silo.
## **White label is more than branding**
Most white-label form pages talk about logos, colors, custom domains, badge removal, and branded emails.
Those are real requirements. They are not enough.
In a B2B SaaS product, white label also means the form capability has to respect the product's operating model. A tenant should not see another tenant's forms. A customer admin should not publish components that break downstream processing. A support team should be able to diagnose what changed. A developer should know how submissions map into APIs and workflows.
This is where a light embed starts to strain.
OWASP's API Security Top 10 puts [broken object-level authorization](https://owasp.org/API-Security/editions/2023/en/0xa1-broken-object-level-authorization/) first. That is a useful reminder for SaaS form architecture: if embedded forms create or expose customer records through APIs, authorization has to be object-aware and tenant-aware. Front-end hiding is not governance.
The same logic applies to validation and workflow behavior. The [conditional logic and validation features](https://form.io/features/form-conditional-logic-form-validation/) matter because the form should enforce rules before bad data becomes an API or workflow problem.
## **When a simpler embedded form is enough**
Use a simpler hosted embed when the form is not central to the product.
That includes:
- newsletter signup
- marketing lead capture
- event registration
- contact and support requests
- one-off surveys
- public feedback forms
- low-risk forms that can live in an external form account
In those cases, a hosted form builder with templates, brand settings, and a quick embed code may be the best decision. Jotform, Formsort, 123FormBuilder, and similar tools can be strong fits when speed and convenience are the main job.
The mistake is keeping that architecture after forms become a customer-facing product capability.
## **When embedded form infrastructure is needed**
Embedded form infrastructure becomes important when the form is part of how your SaaS product works.
Examples include:
- customer onboarding flows that differ by tenant
- partner and vendor portals
- regulated intake workflows
- customer-managed form libraries
- embedded application builders
- productized approval flows
- internal workflow forms exposed to external customers
- multi-office or multi-group customer operations
In these cases, forms need lifecycle control. NIST's [Secure Software Development Framework](https://csrc.nist.gov/pubs/sp/800/218/final) treats security practices as part of the software development lifecycle, which is the right lens for embedded form capability that ships inside a SaaS product. The form builder is no longer an outside utility. It is part of the product surface.
Data risk also changes the decision. [Thales' 2025 Cloud Security Study](https://cpl.thalesgroup.com/cloud-security-research) reported that 54% of cloud data is sensitive and that only 8% of respondents encrypt 80% or more of cloud data. That does not mean every embedded form needs self-hosting. It does mean SaaS teams should know where form data lives, who can access it, how it is encrypted, and how it moves through APIs.
## **Customer proof: white-label forms as a business model**
The white-label use case is not theoretical for Form.io.
In Form.io's Bursting Silver case study, the company describes how a regulatory-industry platform [white-labeled Form.io](https://form.io/case-studies/from-facing-the-risk-of-losing-an-entire-industry-to-generating-millions-and-having-new-clients-call-them/) to support its industry, sign dozens of new clients, and increase revenue by 25%.
That proof point matters because it connects embedded forms to a business model, not just a UI decision. When forms are a capability customers use inside your product, the form layer can influence retention, onboarding, service load, expansion, and product differentiation.
## **The decision framework**
Choose a simple embedded form when the form is a page element.
Choose a hosted enterprise form builder when business users need fast form creation and the external vendor account model is acceptable.
Choose a JavaScript form library when your team wants front-end control and is ready to build the backend, storage, permissions, and operational layer around it.
Choose Form.io when the form capability needs to become part of your product architecture: embedded rendering, embedded building, customer self-service, white-label experience, structured schemas, generated APIs, permissions, validation, workflow behavior, and deployment control.
That is the real difference.
Embedded forms are not automatically infrastructure. But in B2B SaaS, they often become infrastructure faster than teams expect.
## **Key takeaways**
- Embedded forms can mean a simple widget, an embedded form builder, or full white-label form infrastructure.
- SaaS teams should evaluate builder embedding, tenant separation, data ownership, APIs, permissions, workflow behavior, and deployment model.
- Competitors can be good fits for hosted no-code forms, polished product forms, developer libraries, or branded conversion flows.
- Form.io is strongest when the form layer needs to stay connected to schemas, APIs, submissions, permissions, and workflows inside the product architecture.
- A simple embed is enough for low-risk marketing forms. It is not enough when customers need to build and govern forms inside your SaaS.
## **FAQ**
### **What are embedded forms?**
Embedded forms are forms rendered inside a webpage or application through an iframe, script, SDK, component, or framework integration. The user completes the form without leaving the surrounding site or product experience.
### **What is an embedded form builder?**
An embedded form builder is a builder or editor exposed inside your application so users can create or change forms without going to a separate vendor dashboard.
### **What does white-label mean for forms?**
At minimum, white label usually means custom branding, colors, domains, and removal of vendor badges. For SaaS platforms, it should also include builder experience, tenant separation, emails, exports, permissions, and workflow behavior.
### **Can customers create their own forms inside a SaaS product?**
Yes, if the platform supports embedded form building. The important question is whether customers can do that inside guardrails your product controls.
### **Are iframe embedded forms enough?**
Sometimes. Iframes can be practical for low-risk or simple use cases. They are often weaker when the form needs deep styling, app authentication, event handling, tenant-aware permissions, or tight workflow integration.
### **Which embedded form builder is best for multi-tenant SaaS?**
Form.io is a strong fit when multi-tenant SaaS teams need white-labeled form creation, APIs, permissions, structured submissions, workflow behavior, and deployment control. Simpler tools may fit when the requirement is only branded form capture.
### **Do embedded forms create security risks?**
They can if teams treat them as front-end widgets while the data becomes sensitive application data. The right controls depend on authorization, validation, tenant separation, encryption, auditability, and where submissions are stored.
### **When should I choose Form.io over a simpler form builder?**
Choose Form.io when forms are part of the application infrastructure: customers create forms, submissions feed APIs, permissions matter, workflows depend on form data, and the deployment boundary is important.
### **Can Form.io replace my whole application backend?**
No. Form.io is infrastructure for forms, APIs, submissions, validation, permissions, and workflow-related actions. Your application still needs its own product logic, user experience, integrations, and surrounding architecture.
## **Build embedded forms that behave like your product**
If your SaaS customers only need a form on a page, keep it simple.
If they need governed, branded, customer-managed forms inside your product, start with infrastructure that can carry the form, data, API, and workflow model together.
[Try Form.io for white-label embedded form infrastructure](/try-formio-for-free/).
# Claims Management Software Starts With The Forms That Feed It
[  ](https://form.io/claims-management-software-insurance-form-builders/)Claims management software comparisons usually start with the core claims system.
That makes sense. Carriers, TPAs, MGAs, adjusters, and self-insured organizations need systems for assignment, reserves, adjudication, payments, subrogation, reporting, and closure.
But many claims problems start earlier.
They start at the first notice of loss. They start when a claimant uploads the wrong document, an adjuster captures incomplete field notes, an agent enters policy data twice, or a regulatory form has to be recreated from unstructured intake data.
Before a claim can be managed, the data has to be captured.
That is why insurance teams should evaluate the form infrastructure behind the claims workflow, not only the claims platform itself.
## **Key Takeaways**
- Claims management software and claims form infrastructure solve different layers of the same workflow.
- Full claims systems manage the claim lifecycle. Form infrastructure governs intake, validation, files, submissions, APIs, PDFs, permissions, and handoff.
- Claim handling is a high-risk customer and regulator touchpoint, so weak intake creates downstream cost.
- Form.io is not a full claims-core replacement. It is a strong fit when insurance forms need to become embedded, API-backed, self-hosted workflow infrastructure.
- The right evaluation question is not only "which claims system?" It is also "what form layer feeds and extends the claims system?"
## **What Claims Management Software Usually Means**
In most buyer guides, claims management software means a system that supports the claims lifecycle from first notice of loss through settlement and closure.
The category usually includes:
- FNOL and claims intake
- claim assignment and triage
- document and image management
- policy lookup
- investigation and adjudication
- reserve management
- payments and settlement
- regulatory reporting
- analytics and dashboards
- customer status updates
- closure and audit history
That is why systems like Guidewire ClaimCenter, Duck Creek Claims, Riskonnect, FINEOS, VCA, BriteCore, Snapsheet, and other claims platforms dominate the search results for **claims management software**.
They are solving a large operational problem.
Form.io should not be framed as a replacement for those systems when the buyer needs a full claims core. If your team needs end-to-end claims adjudication, reserve management, litigation tracking, payment workflows, subrogation, CAT-scale claims operations, or deep P&C suite functionality, a claims management platform is the right category to evaluate.
But claims systems do not remove the need for form infrastructure.
They often create more of it.
## **Why Claims Intake Is An Infrastructure Problem**
Claims are where the insurer's promise becomes visible.
The customer does not experience the claims system as a data model or an admin workflow. They experience it as a form, a file upload, a status update, an estimate, a call, a missing document request, or a delay.
That is why digital claims workflows have real retention stakes. J.D. Power's 2025 U.S. Claims Digital Experience Study reported that insurers deliver adequate digital updates only 22% of the time. Insurance Journal's coverage of the study also reported that 52% of auto and homeowners customers who rate their digital claim experience as "poor" or "just OK" are likely to leave or not renew, compared with 4% of customers who rate the experience as "excellent" or "perfect" ([Yahoo Finance syndication of J.D. Power release](https://finance.yahoo.com/news/fully-digital-claims-processing-drives-120000409.html), [Insurance Journal](https://www.insurancejournal.com/news/national/2025/12/09/850297.htm)).
Weak intake also shows up in complaint patterns. The NAIC says delays, denials, and unsatisfactory settlements are among common reasons consumers file complaints, and that consumers are asked to gather supporting documents, photographs, correspondence, phone logs, and detailed accounts when filing complaints ([NAIC](https://content.naic.org/article/how-file-complaint-and-research-complaints-against-insurance-carriers)). A ValuePenguin analysis of NAIC closed complaint data reported that claim handling accounted for 65.2% of closed insurance complaints in 2024, with delays and unsatisfactory settlements or offers as the top claim-handling complaint types ([ValuePenguin](https://www.valuepenguin.com/most-common-insurance-complaints)).
Those numbers do not prove a form platform fixes claims operations by itself.
They prove the stakes.
If claims data enters the workflow through weak forms, disconnected uploads, duplicated manual entry, unclear validation, or inconsistent status paths, the claims system inherits that mess.
## **The Claims Workflow Surfaces That Depend On Forms**
Insurance forms are not only contact forms.
In a claims environment, forms show up across the workflow:
- policyholder FNOL forms
- agent and broker claim submission forms
- adjuster field reports
- inspection and damage assessment forms
- photo, video, and document upload flows
- repair estimate collection
- medical record and proof-of-loss intake
- third-party claimant forms
- loss run request forms
- policy application and endorsement forms
- regulatory filing packets
- PDF outputs for records, signatures, reviews, or state-specific requirements
Some of these forms are customer-facing. Some are internal. Some are embedded in portals. Some are mobile. Some still need to map back to exact PDF-style layouts because insurance operations have not escaped document reality.
That is the layer where form infrastructure matters.
A claim can move through a core system, but the surrounding form layer still has to answer practical questions:
- Who can submit this form?
- Which fields are required for this claim type?
- Can the claimant save and resume?
- Can an adjuster collect data offline?
- Can photos and documents be attached securely?
- Does the submitted data become structured JSON, or does someone retype it later?
- Can the submission feed an API, webhook, claims core, document repository, or analytics pipeline?
- Can the same data produce a PDF output when a regulator, carrier, or partner still needs one?
- Can changes to the form and submission be audited?
Those are not cosmetic questions. They are workflow architecture.
## **What To Evaluate In The Claims Form Layer**
A serious claims-intake form layer should be evaluated on more than field layout.
### **Conditional Logic**
Insurance workflows vary by claim type, line of business, state, channel, and role.
A property claim does not ask the same questions as a cyber liability claim. A claimant portal does not need the same view as an adjuster workflow. A policyholder should not see every internal field an examiner needs.
The form layer should support conditional logic, role-specific screens, and dynamic form paths without forcing every variation into custom code.
### **Validation Before Handoff**
The worst time to discover bad data is after it reaches the claims system.
Claims forms should validate required fields, dates, policy identifiers, file requirements, numeric values, and conditional dependencies before submission. They should reduce preventable downstream rework without pretending every claim is simple.
### **File And Evidence Capture**
Claims intake often depends on documents and media: photos, estimates, police reports, medical documents, invoices, inspection records, correspondence, and proof-of-loss materials.
The form layer should treat uploads as part of the submission record, not as an afterthought in a shared inbox.
### **Generated APIs And System Handoff**
Claims data rarely stays in one place.
It may need to feed a claims core, policy system, CRM, document management platform, analytics warehouse, notification workflow, payment process, or regulatory reporting path.
That is why static forms are not enough. The form layer should expose structured submission data through APIs and integration patterns that developers can control. For Form.io, that includes [drag-and-drop forms with generated APIs](https://form.io/features/drag-and-drop-form-builder-apis/) rather than forms that stop at display and email notification.
### **Permissions And Submission Access**
Insurance workflows are role-sensitive.
Policyholders, agents, adjusters, claim supervisors, legal teams, compliance teams, and admins should not all see the same data. A useful form platform needs access control around forms and submissions, not just a login screen in front of everything.
### **Auditability**
Claims records can become evidence.
If a form changes, a submission is edited, a file is replaced, or a workflow action fires, teams need to understand what changed, who changed it, and when. Auditability is not decoration in regulated workflows.
That is why a claims form layer should include a [complete audit trail for form changes and submissions](https://form.io/features/log-forms-complete-audit-trail/), especially when operational records may later be reviewed by legal, compliance, or regulator-facing teams.
### **PDF And Regulatory Output**
Insurance still runs on documents.
NAIC's SERFF industry training page describes electronic rate and form filing as including form submittal, document management, and review access, while supporting compliance with consumer protection requirements ([NAIC SERFF](https://content.naic.org/node/10174)). That does not mean every claims form feeds SERFF. It does mean "forms" in insurance often exist inside regulated document and review workflows.
Good form infrastructure should let teams collect structured data through modern web forms while still producing PDF outputs when official, partner, regulatory, or legacy processes require them.
That can include [custom PDF templates](https://form.io/features/pdf-forms-pdf-template-designer/) and [fillable PDF forms](https://form.io/features/fillable-pdf-forms/) when the workflow has to preserve document fidelity without giving up structured submission data.
## **Where Form.io Fits**
Form.io fits when the forms around claims management need to become application infrastructure.
That does not mean Form.io is a claims adjudication engine. It does not calculate reserves, run a full claims core, or replace every specialized insurance platform.
It means Form.io can support the form, API, submission, PDF, and workflow layer that surrounds those systems.
Form.io's public insurance PDF page speaks directly to this type of insurance workflow: outputting submissions to PDF, turning PDFs into embeddable dynamic forms, tracking changes to fields and forms, auto-populating repeated data, autosaving unfinished forms, collecting offline, and using mobile-responsive forms ([Form.io insurance PDF forms](https://form.io/industries/pdf-forms-for-insurance/)).
The official Form.io documentation also describes two PDF paths: PDF output from webform submissions and PDF-first forms where teams upload a PDF and place interactive fields on top of it. PDF Plus adds PDF-first experiences with pixel-perfect PDF backgrounds and JSON-driven overlays, while PDF Basic supports printing and downloading webform submissions as PDFs ([Form.io docs](https://help.form.io/form.io-concepts.md?ask=How%20does%20Form.io%20support%20PDF%20forms%20and%20PDF%20output%20from%20webform%20submissions%3F)).
That matters for insurance because the buyer often needs both:
- modern, embedded, API-backed data capture
- document-style outputs that still match policy, claims, underwriting, or regulatory expectations
Form.io also matters when teams need forms and APIs together. The platform is designed around JSON-defined forms, submissions, generated APIs, permissions, workflow actions, and customer-controlled deployment. For insurance teams, that can support workflows such as:
- embedded FNOL forms inside a policyholder portal
- agent-facing application and claims intake
- adjuster inspection forms with file uploads
- internal review forms for claims operations
- self-hosted data capture for sensitive records
- structured submission APIs into existing claims or policy systems
- PDF outputs for claim packets, confirmations, or document-heavy workflows
This is the useful distinction:
Claims management software manages the claim.
Form.io can govern the form infrastructure that captures and moves the data the claim depends on.
## **Comparison: What To Ask Before Choosing The Form Layer**
## **Evaluation question****Why it matters****What to look for**Can the form handle different claim types?Claims vary by line, state, product, and roleConditional logic, reusable components, role-specific flowsCan users upload documents and photos?Evidence is often the claim recordSecure file upload, file metadata, submission associationDoes the form validate data before submission?Bad intake data creates downstream reworkRequired fields, conditional validation, typed data, calculated valuesDoes submission data have an API?Claims data must move into other systemsREST APIs, webhooks, JSON submissions, developer-controlled handoffCan permissions be scoped?Insurance workflows are role-sensitiveForm and submission permissions, own-vs-all access, admin boundariesCan changes be audited?Claims and regulated forms need evidenceChange history, audit logs, revision-aware workflowsCan web submissions become PDFs?Insurance still needs documentsPDF output, PDF templates, PDF-first forms, existing PDF conversionCan it be embedded?Claims intake lives inside portals and productsEmbeddable renderer, embedded builder, white-label controlsCan it be self-hosted?Some insurance data must stay inside controlled environmentsCustomer-controlled deployment, database, file storage, network boundary**When A Full Claims Management Platform Is The Better Fit**
Use a full claims management platform when the core problem is managing the claim lifecycle itself.
That includes:
- claim assignment and triage
- reserve management
- adjudication workflows
- payments and settlement
- subrogation and recovery
- litigation management
- catastrophe scale handling
- repair network workflows
- claims analytics
- policy and billing suite integration
- specialized P&C, health, life, or workers' compensation claim operations
This is where platforms like Guidewire, Duck Creek, Riskonnect, FINEOS, VCA, BriteCore, Snapsheet, and other insurance-specific systems belong in the evaluation.
Trying to force a form infrastructure platform to behave like a complete claims core would be the wrong move.
But it is equally risky to assume the claims core solves every form problem around it.
Many carriers already have core systems. The friction is in the portals, supplemental forms, customer-facing intake, partner workflows, document packets, regulatory outputs, and integration surfaces around those systems.
That is where a dedicated form infrastructure layer can make sense.
## **When To Evaluate Form Infrastructure Separately**
Evaluate the form layer separately when any of these are true:
- Your claims core works, but customer or agent intake is weak.
- You need embedded forms in a portal, app, or white-labeled product.
- Claims data must feed multiple downstream systems.
- Different teams need to create or modify forms without breaking the architecture.
- Documents and PDFs are still part of the official workflow.
- You need structured APIs instead of manual re-entry.
- You need submission-level permissions and audit evidence.
- You need to self-host the form and submission layer.
- You need offline or mobile-responsive collection.
- You need a repeatable way to turn form changes into governed application behavior.
This is the buyer Form.io should speak to.
Not the buyer looking for the quickest online form.
Not the buyer who wants to replace every claims system overnight.
The buyer whose forms have become infrastructure.
## **Customer Proof: Insurance Forms Are Operational Systems**
Form.io has public insurance-adjacent proof through E-Risk Services, LLC, described in a Form.io case study as a specialty-lines underwriting subsidiary of Nationwide Insurance Company. The case study says E-Risk built a CRM in two months instead of two years ([Form.io case study](https://form.io/case-studies/building-a-crm-took-2-months-instead-of-2-years/)).
That proof point should be used carefully. It is a Form.io-hosted case study, not an independent Nationwide-hosted validation of the timeline.
But it is still relevant because E-Risk's public Nationwide page shows the real insurance surfaces around specialty lines: product pages, applications and forms, policy forms, loss run requests, expiring policy requests, underwriting contact paths, quoting, and servicing ([Nationwide E-Risk](https://www.nationwide.com/excessandsurplus/e-risk/)).
That is the practical pattern.
Insurance teams do not only need one claims screen. They need many controlled data-capture and document workflows around underwriting, servicing, claims, renewals, requests, and regulated communications.
Form infrastructure is how those workflows stay usable without becoming disconnected spreadsheets, PDF piles, email chains, and one-off portals.
The customer language from another Form.io-hosted case study is useful here because it describes the same infrastructure burden in plain terms. In the Safety Mojo case study, a long-time Form.io platform user said, "Form.io cleans up all the dirty work and does it for you" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)). That quote is not insurance-specific, but it fits the architectural point: forms become expensive when every team has to rebuild the form, data, API, and workflow plumbing separately.
## **The Decision Rule**
Choose a claims management platform when the main requirement is claims-core operation.
Choose Form.io when the main requirement is governed form infrastructure around insurance workflows.
That means forms that can render in your application, collect structured data, validate submissions, handle files, expose APIs, support permissions, produce PDFs, and live inside your deployment boundary.
For teams with stricter data-control requirements, [self-hosted enterprise forms](https://form.io/features/self-hosted-forms-for-enterprise/) can keep the form, submission, and file-handling layer inside the environment the organization controls.
For insurance teams, this distinction matters because "claims management software" is not one decision.
It is at least two:
1\. What system manages the claim lifecycle? 2. What infrastructure captures, governs, and moves the data that feeds it?
Most comparisons answer only the first question.
The second question is where Form.io belongs.
## **FAQ**
### **What Is Claims Management Software?**
Claims management software helps insurance teams manage claims from intake through assignment, investigation, adjudication, settlement, reporting, and closure. It often includes FNOL, document management, workflow automation, payments, analytics, and compliance features.
### **Is Form.io Claims Management Software?**
Form.io is not a full claims management platform or claims-core system. It is form and API infrastructure that can support the intake, submission, document, PDF, permission, and integration layer around claims workflows.
### **Can Form.io Replace Guidewire Or Duck Creek?**
Not when the requirement is a full claims core. Guidewire, Duck Creek, and similar systems are built for end-to-end claims operations. Form.io is a better fit when teams need governed forms, APIs, submissions, PDFs, and embedded intake around those systems.
### **What Is FNOL Software?**
FNOL software supports first notice of loss: the initial claim report. A strong FNOL workflow captures structured claim data, claimant details, incident information, documents, photos, and routing data so the claim can move into the right downstream process.
### **Why Do Insurance Claims Workflows Need Better Forms?**
Claims workflows depend on accurate intake. If forms collect incomplete data, miss required documents, fail to validate fields, or force manual re-entry, the claims process slows down and customer experience suffers.
### **Can Claims Forms Collect Photos And Documents?**
Yes, but the important question is how those files are stored, associated with submissions, permissioned, and handed off. Claims evidence should be part of the structured submission workflow, not a loose email attachment.
### **How Do PDF Forms Fit Insurance Claims?**
Many insurance workflows still require PDF-style outputs, forms, packets, or official documents. A modern form layer should collect structured web data while still supporting PDF output or PDF-first forms when the workflow requires document fidelity.
### **What Should Insurers Evaluate In Claims Intake Software?**
Evaluate conditional logic, validation, file uploads, submission APIs, permissions, audit logs, embedded rendering, PDF output, mobile/offline support, and deployment control. The form layer should support the claims architecture, not just display fields.
### **Do Claims Workflows Need Self-Hosted Forms?**
Not always. Self-hosting matters when sensitive claims data, regulatory expectations, customer requirements, or enterprise architecture require the form and submission layer to run inside a controlled environment.
### **How Can Forms Connect To Claims Management Systems?**
Forms can connect through APIs, webhooks, submission exports, custom integrations, document workflows, or middleware. The important requirement is structured, validated submission data that downstream systems can consume reliably.
## **Build Claims Intake Infrastructure With Form.io**
If your team needs a full claims-core platform, evaluate claims management systems directly.
If your team needs better claims intake, embedded insurance forms, PDF outputs, generated APIs, controlled submissions, and customer-hosted form infrastructure, evaluate the form layer separately.
[Try Form.io for insurance form infrastructure](https://form.io/try-formio-for-free/).
# KYC Onboarding Software for Financial Services: Forms, APIs, and Audit-Ready Intake
[  ](https://form.io/kyc-onboarding-software-financial-services-form-platforms/)KYC onboarding software is usually evaluated as an identity verification purchase.
That is only part of the system.
Banks, fintechs, lenders, and other financial-services teams still have to collect customer data, route exceptions, connect verification providers, preserve evidence, and keep sensitive workflows under control. The right question is not only which KYC provider to buy. It is what intake infrastructure the provider connects to.
## **Key Takeaways**
- KYC onboarding software includes identity checks, but the surrounding intake layer matters just as much.
- Dedicated KYC vendors are strongest for document verification, sanctions screening, adverse media, KYB data, biometrics, and verification coverage.
- Form.io is a better fit for the application infrastructure around those checks: embedded forms, structured submissions, generated APIs, permissions, workflows, revisions, audit trails, and customer-controlled deployment.
- Financial-services teams should evaluate who owns the schema, submission record, API handoff, audit evidence, and change-control path.
- The strongest architecture often combines a KYC verification vendor with a governed form platform that controls intake inside the customer's own product and environment.
## **What KYC Onboarding Software Has To Handle**
KYC onboarding is not a simple signup form with a document upload bolted on.
In financial services, onboarding can involve customer identity, beneficial ownership, business entity details, risk indicators, attestations, document evidence, sanctions and PEP checks, adverse media review, manual exception handling, approvals, and ongoing updates.
The fraud pressure behind those workflows is real. The Federal Trade Commission reported that consumers lost more than $12.5 billion to fraud in 2024, a 25% increase from the prior year ([FTC](https://www.ftc.gov/news-events/news/press-releases/2025/03/new-ftc-data-show-big-jump-reported-losses-fraud-125-billion-2024)). That number does not prove any one onboarding product prevents fraud. It does show why financial-services teams treat identity, intake, and evidence workflows as risk infrastructure.
For covered financial institutions, customer due diligence also extends beyond one-time identity capture. FinCEN describes CDD as policies and procedures that identify and verify customers and beneficial owners, understand customer relationships for risk profiling, and support ongoing monitoring and customer-information updates ([FinCEN](https://www.fincen.gov/news/news-releases/fincen-reminds-financial-institutions-cdd-rule-becomes-effective-today)). FinCEN's 2026 exceptive relief narrowed repeat beneficial-owner verification at every new account opening, but preserved initial verification, risk-based updates, and ongoing monitoring obligations ([FinCEN](https://www.fincen.gov/news/news-releases/fincen-issues-exceptive-relief-streamline-customer-due-diligence-requirements)). Digital identity guidance makes the same point from another angle: NIST SP 800-63A-4 defines identity proofing and enrollment requirements across three identity assurance levels, with evidence, validation, and verification expectations that affect onboarding design ([NIST SP 800-63A-4](https://csrc.nist.gov/pubs/sp/800/63/a/4/final)). FFIEC authentication guidance also emphasizes layered security and stronger controls than single-factor authentication for financial institution services and systems ([FFIEC authentication guidance](https://www.ffiec.gov/news/press-releases/2021/pr-08-11)).
That is the operating reality KYC onboarding software has to support.
It has to help the organization answer:
- What information do we need for this customer type?
- Which evidence is required for this product, jurisdiction, or risk profile?
- Which verification provider or internal service should receive the data?
- Who reviews exceptions?
- Which decisions and changes need to be retained?
- Where does the submission record live?
- How do we update customer information later without losing history?
Those are not only compliance questions. They are application architecture questions.
## **The Three Layers Of KYC Onboarding Software**
Most KYC software pages collapse three different layers into one category.
That makes comparison harder than it needs to be.
### **1. KYC Verification And Data Providers**
This is the layer buyers usually think of first.
KYC verification providers handle identity document verification, database checks, liveness or biometric checks, sanctions screening, PEP screening, adverse media, fraud signals, KYB data, business registry checks, and beneficial ownership data.
If your main problem is global identity coverage, document authenticity, fraud detection, sanctions data, or KYB intelligence, this is the category you should evaluate.
Form.io does not replace that layer.
### **2. Client Lifecycle And Case Workflow Platforms**
Some financial institutions need a broader client lifecycle management system.
That can include onboarding cases, risk scoring, relationship-manager queues, remediation workflows, periodic refresh, monitoring, approvals, dashboards, and enterprise reporting.
If the primary buyer need is a complete CLM suite for a large financial institution, a specialized onboarding or CLM platform may be the right center of gravity.
Form.io does not claim to be a full AML case-management system.
### **3. Form And Application Infrastructure**
This is the layer many comparisons understate.
Before a verification service can check anything, the organization has to collect the right data, validate it, structure it, submit it, secure it, route it, and keep the record. That work often happens in forms embedded inside account-opening flows, borrower portals, investor onboarding flows, agent portals, internal review tools, and customer update workflows.
This is where Form.io belongs.
Form.io is not the sanctions database, fraud network, or identity bureau. It is the schema-driven form and API infrastructure that can sit around those systems when the customer needs to own the intake experience and the data path.
## **Why Static Forms Break KYC Workflows**
Static forms are comfortable until the onboarding workflow branches.
A retail deposit account does not collect the same evidence as a commercial lending application. A sole proprietor does not require the same entity structure as a multi-owner company. A low-risk domestic customer does not follow the same path as a higher-risk customer, foreign entity, trust, money-services business, or politically exposed person.
KYC onboarding software often has to branch by:
- individual versus business customer
- account or product type
- jurisdiction
- entity structure
- risk level
- ownership profile
- required documents
- missing or inconsistent information
- applicant role
- reviewer role
- periodic refresh or customer update
If those branches live in hard-coded forms, spreadsheets, PDFs, or ad hoc portal logic, the onboarding workflow becomes brittle. Compliance teams cannot change requirements cleanly. Developers cannot route data consistently. Reviewers inherit partial records. Customers get asked for the wrong information.
The stronger model is a governed intake schema: the form defines the data structure, validation, conditional logic, submission record, API handoff, and change path.
That is the Form.io argument.
## **What A KYC Intake Layer Should Provide**
The form layer behind KYC onboarding software should be evaluated as infrastructure, not as a decorative front end.
### **Dynamic Forms And Validation**
KYC intake should adapt to the customer, product, jurisdiction, entity type, and risk profile.
The platform should support [conditional logic and validation](https://form.io/features/form-conditional-logic-form-validation/), reusable components, calculated values, required evidence, document upload fields, consent language, and validation rules. The goal is not to make a long form look nicer. The goal is to collect the right information before the workflow reaches verification, review, or downstream systems.
### **Structured Submission Records**
For KYC, a submitted form is not just a message.
It is a record of what was asked, what was provided, which files were attached, what metadata came with the submission, and what later changed. Submission data needs to remain accessible for internal systems, reviewers, reports, and audit workflows.
Form.io's documentation describes forms as the structure that collects, validates, and stores user data, while the same form structure defines a backend API for managing and accessing submitted data ([Form.io docs](https://help.form.io/userguide/forms)). That structure matters when KYC data needs to move beyond a form inbox.
### **API Handoff To Verification And Core Systems**
KYC onboarding almost always depends on other systems.
Data may need to move into identity verification providers, sanctions or PEP screening services, CRM, core banking, lending systems, document management, case management, data warehouses, notification tools, and compliance reporting.
For Form.io, the strongest claim is architectural: every form, resource, submission, and project is accessible through a REST API, with predictable endpoints and submission paths that developers can connect to other systems ([data integration tools](https://form.io/features/data-integration-tools-for-enterprise-forms/)). Webhook actions can also send submission payloads to external endpoints when events occur.
That does not mean Form.io ships every KYC vendor integration out of the box.
It means teams can build the intake and handoff layer around the verification tools they choose.
### **Role-Based Access**
KYC data is role-sensitive.
Applicants, authorized representatives, relationship managers, compliance analysts, operations staff, auditors, developers, and administrators should not all see or edit the same data.
The intake layer should support [role and submission permissions](https://help.form.io/developers/roles-and-permissions.md) around forms, submissions, admin surfaces, and review workflows. This matters because KYC onboarding often blends customer-facing and internal workflows. One weak permission model can turn a controlled process into an overexposed one.
### **Revisions And Audit Logs**
Regulated onboarding workflows need history.
If a customer updates business ownership details, a reviewer changes a risk classification, a required field is added, or an administrator modifies access, the organization needs to know what happened.
Form.io describes two complementary logging systems: Submission Revisions for field-level submission changes and Server Audit Logging for system activity such as form access, authentication, and API-level data modifications ([audit trail capabilities](https://form.io/features/log-forms-complete-audit-trail/)). Those capabilities fit KYC intake because the evidence trail is part of the workflow, not an afterthought.
Availability and configuration still matter. Teams should confirm which modules, settings, and license terms apply before making compliance commitments.
### **Deployment And Data Boundary Control**
KYC onboarding touches sensitive personal and business information.
Some financial-services teams can use hosted tools without issue. Others need stricter control over environment, authentication, database, file storage, network access, logging, and vendor exposure.
That is where [self-hosted forms](https://form.io/features/self-hosted-forms-for-enterprise/) or customer-controlled deployment becomes part of the buying decision. Form.io is strongest when the intake layer needs to live inside the customer's architecture rather than as a disconnected third-party form surface.
## **How Form.io Fits Beside KYC Verification Vendors**
The right architecture is often not Form.io instead of a KYC vendor.
It is Form.io around the KYC vendor.
A financial-services team might use Form.io to build an [embedded onboarding flow](https://form.io/features/drag-and-drop-form-builder-apis/) that collects customer and entity data, validates required fields, captures documents, stores submissions, applies role-based access, and exposes the submission through APIs. The same workflow can then call identity verification, document verification, sanctions screening, fraud, CRM, or core system services.
That division of responsibility is clearer and more credible:
**Layer****What It Does****Typical Fit**KYC verification providerIdentity proofing, document checks, sanctions or PEP screening, KYB data, fraud signalsUse when verification intelligence and coverage are the core needCLM or onboarding suiteCases, queues, lifecycle workflows, risk review, remediation, dashboardsUse when the institution needs a broad onboarding operating systemForm.io intake infrastructureEmbedded forms, structured submissions, generated APIs, permissions, revisions, audit trails, workflow handoff, self-hosted deploymentUse when the team needs to own the intake layer inside its product and systemsThis distinction also keeps the compliance claim honest.
Form.io can support regulated KYC onboarding controls. It does not make an organization compliant by itself. It does not replace AML policy, compliance staff, model validation, legal review, sanctions data, transaction monitoring, or the specialized identity providers that verify people and businesses.
It gives teams the form/application layer those systems need to receive clean, structured, governed intake data.
## **KYC Onboarding Software Evaluation Checklist**
When evaluating KYC onboarding software, ask who owns each part of the workflow.
**Evaluation question****Why it matters****What to check**Who owns the intake schema?KYC requirements change by customer type, product, jurisdiction, and risk profileForm definitions, reusable components, conditional logic, validation, versioningCan the workflow collect documents and evidence?Verification and review often depend on file evidenceSecure uploads, metadata, submission association, downstream accessDoes the submission have an API?KYC data needs to move into verification, CRM, case, banking, lending, and reporting systemsREST APIs, webhooks, JSON submissions, authentication, retry/error patternsCan permissions be scoped by role?Applicants, reviewers, admins, and auditors need different accessForm permissions, submission permissions, own/all access, SSO role mappingIs the workflow auditable?Reviewers need to understand changes and decisionsSubmission revisions, form revisions, audit logs, timestamps, user identity, notesCan the system support ongoing updates?KYC and CDD are not always one-time eventsCustomer refresh flows, changed-information capture, reviewer routing, historical recordsCan the intake live inside your product?Customer onboarding often belongs inside a portal or applicationEmbedded renderer, white-label controls, developer-owned front endCan the environment be controlled?Some teams need strict data boundary and infrastructure controlSelf-hosted or customer-controlled deployment, database/storage options, logging integrationDoes the product overclaim compliance?Software supports controls; it does not replace legal obligationsClear scope, configuration details, module requirements, evidence of controlsThe checklist helps separate a strong verification tool from a strong intake platform.
Some buyers need both.
## **When A Dedicated KYC Vendor Is The Better Fit**
Use a dedicated KYC vendor when the primary need is verification intelligence.
That includes:
- identity document verification
- biometric or liveness checks
- sanctions, PEP, and adverse media screening
- KYB data and business registry checks
- beneficial ownership data services
- fraud network signals
- country-specific document coverage
- transaction monitoring or AML case management
Those are specialized capabilities. A form platform should not pretend to replace them.
The same is true for a full client lifecycle suite. If the institution needs enterprise case management, risk scoring, remediation workflows, onboarding dashboards, periodic refresh operations, and compliance-team queues in one packaged system, a CLM platform may be the better center of gravity.
Form.io becomes more relevant when the organization already has or plans to choose those systems, but still needs to own the form layer that feeds them.
## **Where Form.io Is The Better Fit**
Form.io is the better fit when the KYC onboarding workflow is also a product, integration, and governance problem.
That usually means:
- onboarding forms need to be embedded inside a customer portal or internal product
- the data model needs to be controlled by the application team
- submissions need to become API-accessible records
- KYC providers need to be called from the workflow rather than own the whole experience
- permissions need to be scoped across applicants, reviewers, admins, and service accounts
- form and submission changes need revision history
- audit logs need to feed operational or compliance tooling
- sensitive intake data needs to remain in customer-controlled infrastructure
- teams need one governed form layer across multiple onboarding use cases
That is the buyer who should evaluate Form.io as part of a KYC onboarding software stack.
A Trustpilot reviewer called Form.io a "powerful embedded form builder" and wrote that it was "seamlessly built into our B2B application" ([Trustpilot](https://www.trustpilot.com/review/form.io)). That is a small proof point, but it points at the right fit: Form.io is strongest when developers and regulated teams need data management, integration, and control around forms, not just a hosted questionnaire.
## **Bottom Line**
KYC onboarding software is not one product category.
It is a stack.
Verification vendors help confirm identity, screen risk, and supply data. CLM platforms help manage onboarding cases and lifecycle operations. Form infrastructure governs the intake layer: what gets asked, how it is validated, where the submission lives, which systems receive it, who can access it, and what evidence remains when the process changes.
For financial-services teams, that layer deserves its own evaluation.
If the problem is buying verification coverage, choose a KYC provider. If the problem is owning regulated intake across products, portals, APIs, reviewers, audit trails, and customer-controlled infrastructure, evaluate Form.io as the form/application infrastructure around the KYC workflow.
## **FAQ**
### **What is KYC onboarding software?**
KYC onboarding software helps financial-services teams collect customer information, verify identity, assess risk, route exceptions, and preserve records during account opening or customer onboarding. The category can include identity verification tools, KYB providers, CLM platforms, and form/application infrastructure. Buyers should separate those layers before comparing vendors.
### **Is Form.io a KYC verification provider?**
No. Form.io is not an identity verification bureau, sanctions database, biometric provider, AML case-management system, or KYB data provider. It can provide the embedded form, submission, API, permissions, and workflow infrastructure around those services.
### **Where does Form.io fit in a KYC onboarding stack?**
Form.io fits at the intake and application-infrastructure layer. Teams can use it to build embedded onboarding forms, collect structured data, manage submissions, connect APIs and webhooks, scope access, preserve revisions, and deploy in customer-controlled environments. Dedicated verification vendors can still handle identity checks and screening.
### **Why are forms important in KYC onboarding?**
The form layer determines what information is collected, how it is validated, how it is stored, and how it moves into downstream systems. Weak forms create incomplete data, manual rework, inconsistent review paths, and poor audit evidence. In KYC workflows, form design is also data architecture.
### **What should financial-services teams look for in KYC intake software?**
Look for dynamic forms, conditional logic, document upload support, structured submissions, API access, webhooks, role-based permissions, revision history, audit logging, authentication integration, and deployment control. Also confirm what the product does not do, especially around legal compliance, AML policy, sanctions data, and identity verification.
### **Can Form.io help with beneficial ownership collection?**
Form.io can help teams build intake workflows that collect business entity and beneficial ownership information, validate required fields, store submissions, and route data to review or verification systems. It does not determine the legal obligation by itself. Teams should map fields and processes to current regulatory counsel and compliance requirements.
### **Can Form.io connect to KYC or AML vendors?**
Yes, Form.io is built for API-connected form workflows. Forms and submissions can be exposed through REST APIs, and webhook actions can send submission data to external systems. Teams still need to implement and govern the specific integration with their chosen KYC, AML, CRM, banking, or case-management systems.
### **Does Form.io make a financial institution compliant?**
No software makes a financial institution compliant on its own. Form.io can support regulated onboarding controls through structured intake, permissions, APIs, revisions, audit logging, and customer-controlled deployment. Compliance still depends on policy, configuration, monitoring, staff judgment, legal review, and the broader control environment.
### **When should a team choose a full KYC platform instead of Form.io?**
Choose a full KYC platform when the main need is identity verification coverage, fraud signals, sanctions screening, KYB datasets, adverse media, transaction monitoring, or packaged case workflows. Choose Form.io when the main need is to own the embedded intake layer and connect it to those specialized services.
### **Is self-hosting important for KYC onboarding software?**
It depends on the organization's risk posture, architecture, and regulatory environment. Some teams can use hosted KYC products. Others need more control over data, authentication, file storage, logging, network boundaries, and deployment. Form.io is relevant when customer-controlled infrastructure is part of the requirement.
### **How should teams start evaluating Form.io for KYC onboarding?**
Start by mapping the intake workflow: customer types, fields, documents, verification calls, exception paths, reviewer roles, submission records, audit needs, and downstream systems. Then evaluate whether Form.io can provide the governed form and API layer around the verification tools the organization already uses or plans to adopt.
[Build controlled onboarding workflows](/try-formio-for-free/) with Form.io.
# Typeform Alternatives for Self-Hosted and Regulated Teams
[  ](https://form.io/typeform-alternatives-self-hosted-compliance-bound/)Most searches for **typeform alternatives** start with a simple frustration: response limits, pricing, branding, or the one-question-at-a-time format.
Those are real reasons to compare tools. But they are not the whole decision.
If your forms collect regulated data, live inside a customer portal, support tenant-specific workflows, or need to connect directly to your application APIs, the better question is not "Which tool costs less than Typeform?" It is "Which layer of the system should own this form?"
## **Key takeaways**
- Typeform is strong for polished conversational forms, surveys, quizzes, and lead capture.
- Many Typeform alternatives compete on price, free response limits, design flexibility, or survey features.
- Self-hosted alternatives matter when the buyer needs more control over where response data lives.
- Compliance-bound teams need more than a form UX: they need permissions, auditability, deployment control, data routing, and clear responsibility boundaries.
- Form.io is a better fit when forms become embedded, API-backed application infrastructure rather than standalone surveys.
## **Quick comparison: which Typeform alternative fits the job?**
## **Scenario****Better-fit category****Examples to evaluate**Marketing forms, lead capture, quizzes, landing pagesPresentation-first form buildersTypeform, Tally, Fillout, JotformProduct feedback, NPS, CSAT, in-app surveysSurvey and feedback platformsFormbricks, SurveyMonkey, Qualtrics, SurveySparrowOpen-source or privacy-first survey collectionSelf-hosted survey toolsFormbricks, LimeSurvey, HeyForm, OpnFormRegulated intake, portals, claims, onboarding, internal workflowsForm infrastructureForm.ioCustomer-facing SaaS form buildingEmbedded and white-labeled form infrastructureForm.ioForms that need generated APIs and submission permissionsSchema-driven form/API platformsForm.io**Why teams look for Typeform alternatives**
Typeform has a clear job. It helps teams create polished, conversational forms without building a custom form experience from scratch. For many marketing, survey, quiz, and customer-feedback workflows, that is enough.
But the market around Typeform alternatives has grown because buyers often hit one of five limits.
First, pricing and response limits can become frustrating. Tally positions itself directly against Typeform by emphasizing unlimited forms and responses on its free plan, while Typeform's free plan is limited to 10 monthly responses in Tally's comparison.
Second, some teams want more layout flexibility. Fillout argues that Typeform is recognizable and polished, but more opinionated, while Fillout gives teams multi-page forms with more control over page structure and integrations.
Third, privacy and self-hosting are becoming a separate buying category. Formbricks frames itself as an open-source Typeform alternative with a self-hosted Community Edition for teams that want more control over data ownership.
Fourth, regulated teams need clearer data boundaries. Typeform publishes security, data-handling, and compliance guidance, including a compliance article stating that Typeform can provide a BAA for customers on its Enterprise plan. Its help center also documents that Typeform data is hosted on AWS, with main servers in Virginia and EU data hosting available for Enterprise and Growth Custom customers.
Fifth, some teams discover that the form is not really a survey anymore. It is intake. It is workflow. It is a record. It is a customer-facing feature. It is part of the application.
That fifth case is where Form.io belongs in the conversation.
## **The three types of Typeform alternatives**
The mistake is treating all Typeform alternatives as one category.
They are not.
### **1. Presentation-first form builders**
These tools compete with Typeform on form creation speed, design, free tiers, templates, payment collection, embeddability, and basic automation.
They are often the right answer when the form is a marketing asset or a lightweight business workflow. If the team needs a better-looking contact form, a free survey, a quiz, a registration form, or a lead-capture flow, a presentation-first tool may be enough.
This category is where Tally, Fillout, Jotform, Paperform, and similar tools usually compete.
The tradeoff is that the form usually remains a standalone tool. It may integrate with the rest of the stack, but it does not become the infrastructure layer that governs submissions, permissions, APIs, tenants, and deployment environments.
### **2. Privacy-first survey and feedback platforms**
These tools compete on self-hosting, open-source access, feedback workflows, product surveys, NPS, CSAT, in-app micro-surveys, and user research.
Formbricks is a good example. Its Typeform-alternative page emphasizes open source, self-hosting, link surveys, in-app micro-surveys, pop-up surveys, Dockerized deployment, and an open API.
That is a strong fit when the main object is feedback.
But feedback is not the same as application intake. A survey platform may own responses, contacts, segments, and feedback analytics. It may not be designed to become the form/API layer inside a regulated portal, insurance claim workflow, government service, or B2B SaaS product.
### **3. Form infrastructure platforms**
This is the category most Typeform-alternative lists miss.
Form infrastructure is for teams whose forms need to do more than collect answers. These forms need to render inside an application, validate structured data, create submission records, expose APIs, route data to internal systems, respect permissions, survive audits, and remain under the customer's deployment control.
That is the Form.io case.
Form.io describes itself as a self-hosted developer productivity platform for building forms, APIs, and workflows. Its "How Form.io Works" page explains that the drag-and-drop builder creates forms and APIs together, that every form and resource has an automatically generated REST API, and that the platform can be embedded in the customer's own environment ([How Form.io Works](https://form.io/how-it-works/)).
When the buyer needs that layer, Typeform alternatives should not be judged only by design, templates, or monthly response caps.
## **Where self-hosting changes the decision**
Self-hosting is not automatically required. Plenty of teams are better served by a managed SaaS form tool.
But self-hosting changes the evaluation when forms collect sensitive data, connect to internal systems, support regulated workflows, or sit inside a product your team owns.
IBM's 2025 Cost of a Data Breach report puts the global average cost of a data breach at $4.4 million ([IBM Cost of a Data Breach 2025](https://www.ibm.com/reports/data-breach)). That is not a form-builder statistic, and it should not be used that way. It is a reminder that data collection boundaries have real financial and operational consequences.
Data-control expectations are also moving into mainstream architecture decisions. BARC's 2026 data sovereignty survey found that 76% of respondents expect data sovereignty to become more important, which helps explain why "where does this form data live?" is no longer a niche legal question ([BARC data sovereignty survey](https://barc.com/news/data-sovereignty-2026-survey/)).
Verizon's 2026 DBIR summary says 31% of breaches now start with software vulnerabilities and 48% involve ransomware ([Verizon DBIR 2026](https://www.verizon.com/business/resources/reports/dbir/)). Again, that does not mean a form tool causes the risk. It means buyers should care about where software runs, how it is patched, how access works, and who controls the data path.
For a lightweight survey, a hosted form tool can be perfectly reasonable.
For regulated intake, the questions change:
- Where is submission data stored?
- Can the platform run in our environment?
- Can fields be encrypted where needed?
- Can permissions apply to submissions, not just workspace users?
- Can audit logs show what happened?
- Can dev/test/prod environments support controlled changes?
- Can forms connect to our APIs without routing sensitive data through unnecessary third parties?
Those are infrastructure questions.
## **Why Form.io is different from most Typeform alternatives**
Form.io is not trying to be a prettier Typeform clone.
That matters.
Form.io is built around the idea that a form can be a governed schema. The form definition can drive rendering, validation, submitted data shape, generated API endpoints, permissions, and workflow actions.
The practical difference shows up in four places.
### **Forms and APIs are connected**
In Typeform and many alternatives, the form is mainly a collection surface. You can export data, trigger integrations, or connect webhooks, but the form itself is not usually the application data layer.
Form.io's model is different. Its builder and platform center on JSON-powered forms and APIs. Form.io's own product documentation says every form and resource has an automatically generated REST API associated with it.
That is useful when every new form would otherwise require engineering work to create endpoints, validation, storage, and integration behavior.
### **Deployment can stay inside your environment**
Typeform and many alternatives are hosted SaaS products. Some newer alternatives offer self-hosting, especially in the open-source survey category.
Form.io's self-hosted story is more infrastructure-oriented. Its configuration-based pricing page describes API server environments, enterprise projects, PDF server options, dev/test/prod configurations, self-hosted databases, and security compliance features in API Plus configurations ([Form.io configuration-based pricing](https://form.io/configuration-based-pricing/)). Its self-hosted enterprise forms page also frames the Developer Portal, forms, projects, permissions, and submissions as running inside the customer's own environment ([self-hosted forms for enterprise](https://form.io/features/self-hosted-forms-for-enterprise/)).
That is a better match when the buyer is not allowed to treat form data as a casual SaaS export.
### **Governance is tied to the form layer**
Regulated forms often need more than account-level access control. Teams may need form-level permissions, submission-level access, field-level encryption, revision history, action logs, submission revision logs, and audit evidence.
Form.io's security-compliance materials describe advanced audit logging, action logs, form revisions, submission revision logs, submission collections, field-level encryption, and container security scanning as part of its security module and API Plus feature set ([Form.io secure forms compliance readiness](https://form.io/features/secure-forms-compliance-readiness/)).
That is also how broader security frameworks talk about control. NIST SP 800-53 treats security and privacy controls as part of organization-wide risk management, not as isolated software checkboxes ([NIST SP 800-53 Rev. 5](https://csrc.nist.gov/pubs/sp/800/53/r5/upd1/final)).
That does not mean every Form.io buyer needs every module. It does mean the platform is designed for teams that need those questions answered at the form infrastructure layer.
### **Embedded form building is a platform feature**
Some Typeform alternatives let you embed a form. That is not the same as embedding a governed form-building capability inside your own product.
Form.io can support teams that need form rendering and form building inside their application experience, including white-labeled and tenant-aware scenarios. Its Enterprise Form Builder Module is positioned for exposing a customized form-building experience inside the customer's own application ([Enterprise Form Builder Module](https://form.io/enterprise-form-builder-module/)).
That is where Form.io becomes relevant to SaaS platforms, government portals, healthcare products, insurance workflows, and financial services onboarding.
## **A practical shortlist of Typeform alternatives**
### **Choose Typeform when presentation matters most**
Typeform still makes sense when the primary goal is polished conversational UX, surveys, quizzes, lead capture, and a familiar visual form-building experience. If the form is not regulated, not deeply embedded, and not part of your product architecture, Typeform may be enough.
### **Choose Tally when free limits are the issue**
Tally is a strong fit when the buyer wants a simpler and more generous free form builder. Its comparison page emphasizes unlimited forms, unlimited responses, conditional logic, file uploads, payments, and API access on lower-cost or free tiers.
### **Choose Fillout when the issue is flexibility**
Fillout is worth evaluating when the buyer wants modern form building, stronger free response limits, database-style integrations, multi-page forms, and more layout flexibility than Typeform's one-question-at-a-time format.
### **Choose Formbricks when the job is self-hosted surveys**
Formbricks is a strong fit when the buyer wants open-source, self-hosted surveys, product feedback, NPS, CSAT, website surveys, or in-app micro-surveys. It is especially relevant when the team wants a privacy-first Typeform alternative but still thinks in survey and feedback terms.
### **Choose Form.io when forms become infrastructure**
Form.io is the better fit when the buyer needs forms to become part of the application stack: embedded rendering, generated APIs, submission storage, permissions, actions, security/compliance modules, self-hosted deployment, and controlled form lifecycle.
A Form.io customer proof point from Safety Mojo captures the reason this matters: "Form.io cleans up all the dirty work and does it for you" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)). On G2, another reviewer points to "the level of customization that can go into every form" ([Form.io reviews on G2](https://www.g2.com/products/form-io/reviews)). That is the value when the dirty work is not just building a form, but keeping forms, data, APIs, and workflow behavior aligned.
The scale proof points point in the same direction. Form.io's publicplan case study describes support for more than 400 services and 1,000+ forms in a German public-sector context, while the TauRes case study reports an estimated 50% reduction in data-processing workload after standardizing acquisition workflows around Form.io ([publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/), [TauRes case study](https://form.io/case-studies/taures-case-study-data-acquisition-and-analysis/)).
## **Decision framework**
Ask these questions before choosing a Typeform alternative:
**Question****If yes, look at**Do we mainly need a better free plan or lower-cost form builder?Tally, Fillout, JotformDo we mainly need surveys, NPS, CSAT, or product feedback?Formbricks, SurveyMonkey, QualtricsDo we need open-source or self-hosted survey collection?Formbricks, LimeSurvey, HeyFormDo forms need to live inside our application or portal?Form.ioDo submissions need generated APIs, permissions, and audit-relevant controls?Form.ioDo customers or tenants need to build forms inside our product?Form.ioDo we need a simple marketing form this week?Typeform or a presentation-first alternativeThe strongest decision comes from naming the job.
If the job is presentation, choose a presentation-first tool.
If the job is feedback, choose a survey platform.
If the job is governed application intake, choose form infrastructure.
## **FAQ**
### **Which Typeform alternative should you choose?**
There is no single universal Typeform alternative. Tally and Fillout are strong for lower-cost form building, Formbricks is strong for open-source and self-hosted surveys, and Form.io is stronger when forms need to become embedded, API-backed application infrastructure.
### **Is there a self-hosted Typeform alternative?**
Yes. Formbricks is a strong self-hosted survey alternative. Form.io is also self-hosted, but it solves a different problem: governed forms, generated APIs, submissions, permissions, and workflow behavior inside customer-controlled environments.
### **Is Typeform good for regulated data collection?**
Typeform publishes security and compliance materials and says it can provide a BAA for Enterprise customers in relevant HIPAA contexts. Regulated teams should still verify hosting, data residency, contractual scope, retention, access control, audit, and integration requirements before choosing any hosted form tool.
### **When is Form.io a Typeform alternative?**
Form.io is a Typeform alternative when the real requirement is not just a nice form experience, but embedded forms, self-hosted deployment, generated APIs, submission records, permissions, and governed workflow infrastructure.
### **Is Form.io a survey tool?**
Form.io can collect survey-like data, but it is better understood as a form and API platform. It is usually a stronger fit for application forms, portals, regulated intake, workflow forms, and customer-facing form infrastructure than for simple standalone surveys.
### **Which Typeform alternative fits product feedback?**
Formbricks is worth evaluating for product feedback, in-app micro-surveys, NPS, CSAT, and privacy-first survey workflows. It is designed around feedback collection rather than general form infrastructure.
### **Which Typeform alternative fits embedded forms?**
Form.io is usually the better fit when forms need to be embedded into a customer-facing application and governed as part of the product architecture rather than embedded as standalone survey widgets.
### **Which Typeform alternative fits compliance-bound workflows?**
It depends on the compliance requirement. A hosted tool may be enough for low-risk workflows with the right contracts and settings. For stricter control over deployment, storage, APIs, permissions, and audit evidence, Form.io is often the more relevant category fit.
### **Can Form.io replace Typeform?**
Form.io can replace Typeform when the organization needs self-hosted, embedded, API-backed form infrastructure. It may be too much platform for a simple marketing survey, quiz, or event-registration form.
### **What should developers compare before choosing?**
Developers should compare hosting model, schema ownership, API behavior, validation, permissions, submission storage, audit needs, SDK/rendering model, deployment environments, and whether the form needs to live inside an application users already trust.
## **Final recommendation**
For simple campaigns and surveys, choose the form tool that gets the job done with the least operational burden.
For feedback programs, choose a survey platform with the right data and research workflow.
For regulated intake, embedded portals, tenant-aware SaaS forms, and form-driven application workflows, evaluate Form.io as infrastructure, not as another prettier form builder.
The distinction matters because a form is sometimes just a form. But when the data, API, permissions, workflow, and deployment boundary all depend on it, the form has become part of the architecture.
[Try Form.io for free](https://form.io/try-formio-for-free/) to see how self-hosted forms, generated APIs, and governed submission workflows fit inside your application environment.
# Jotform Alternative for Regulated Teams: When Hosted Forms Are Not Enough
[  ](https://form.io/alternatives-to-jotform-regulated-industries/)Jotform is a strong hosted form builder when the job is to create a form quickly.
That is not the same as choosing form infrastructure for regulated work.
If your forms collect sensitive data, drive downstream decisions, live inside a product, or need to satisfy audit and security teams, the real question is not only which builder is easiest. It is which platform gives you enough control after the form is submitted.
## **The Short Version**
Most Jotform alternative lists compare templates, pricing, free plans, conditional logic, integrations, and form design.
Those things matter. They just do not settle the decision for regulated teams.
If your use case is a marketing form, event registration form, internal survey, or lightweight intake workflow, a hosted builder may be the right answer. If your use case is healthcare intake, government services, insurance claims, financial onboarding, customer portals, or embedded SaaS workflows, you need to evaluate a different layer.
For those teams, a serious Jotform alternative should be judged by:
- where the platform runs
- who controls submission data
- how authentication and permissions work
- whether forms generate APIs
- whether form and submission changes are auditable
- whether the form builder can be embedded and white-labeled
- whether the platform can fit into the systems you already govern
That is where Form.io belongs in the conversation.
Form.io is not the fastest option for a one-off hosted form. It is the stronger fit when forms become part of application infrastructure.
## **Why Most Jotform Alternative Lists Miss the Regulated Buyer**
Most search results for `jotform alternative` are written for broad software shoppers.
They usually ask familiar questions:
- Which tool is cheaper?
- Which one has better templates?
- Which one is easier for a nontechnical team?
- Which one has the most integrations?
- Which one has the cleanest form design?
That comparison is useful for simple workflows. It is incomplete for regulated ones.
A hospital intake workflow, public-sector application, insurance claim, KYC onboarding flow, or embedded customer portal cannot be evaluated only by front-end form features. The submitted data becomes part of a larger system. It may need to be retained, corrected, audited, routed, exported, approved, signed, versioned, or tied to a specific policy decision.
That moves the decision out of the form-builder category and into the architecture layer.
The right question becomes: can the form platform respect the control surface around the form?
## **The Real Buying Question: Hosted Builder or Controlled Infrastructure?**
There are two different jobs hiding behind the same keyword.
The first job is form creation. A team needs to publish a polished form, collect responses, and send data somewhere useful. Hosted builders are good at this. They reduce setup time, give nontechnical users a friendly workspace, and make common forms easy to ship.
The second job is governed data collection. A team needs forms to run inside a larger application boundary, use existing authentication, expose durable APIs, preserve record history, and support audit evidence when something changes.
Those are not the same job.
The first job rewards speed. The second rewards control.
That does not make hosted builders bad. It means regulated teams need to know when the category changes.
## **Where Hosted Form Builders Work Well**
A hosted form builder can be the right choice when the workflow is narrow and the organization accepts the vendor-managed model.
Use a hosted builder when:
- the form is standalone
- the data does not need to stay inside your own environment
- the workflow can live in the vendor's dashboard
- standard integrations are enough
- nontechnical creation matters more than developer control
- the form does not need to become part of a product or governed application
This is why broad Jotform alternative lists often recommend tools like Typeform, Google Forms, Tally, Fillout, Cognito Forms, Formstack, FormAssembly, or other hosted builders. For simple forms, those recommendations can make sense.
Regulated teams should be more careful.
The moment the form sits inside a controlled business process, the tool has to answer questions that template libraries cannot answer.
## **Where Regulated Teams Need More Than a Hosted Builder**
Regulated workflows usually fail at the edges.
The form itself looks fine. The problem appears after submission.
Who can see the data? Which system owns the record? What happens when the form schema changes? Can a historical submission still be understood against the form version that captured it? Did the webhook fire? Who changed the claim amount, diagnosis note, eligibility field, or approval status? Can the organization prove it later?
These are ordinary questions in healthcare, government, finance, education, insurance, and other regulated settings.
They also map directly to formal control programs. NIST SP 800-53 Rev. 5 organizes security and privacy controls across families such as [Access Control, Audit and Accountability, Identification and Authentication, Incident Response, Risk Assessment, and System and Communications Protection](https://csrc.nist.gov/pubs/sp/800/53/r5/upd1/final). HHS says the [HIPAA Security Rule](https://www.hhs.gov/hipaa/for-professionals/security/laws-regulations/index.html) establishes national standards for electronic protected health information and requires administrative, physical, and technical safeguards. A form platform used in regulated work does not sit outside those concerns. It becomes one of the places those concerns show up.
IBM's 2025 Cost of a Data Breach report gives the risk scale. IBM reports a [global average breach cost of $4.4 million](https://www.ibm.com/reports/data-breach), and also reports that 63% of organizations lacked AI governance policies to manage AI or prevent shadow AI. Verizon's [2026 Data Breach Investigations Report](https://www.verizon.com/business/resources/reports/dbir/) adds another useful warning: software vulnerabilities now start 31% of breaches, which is why regulated teams should evaluate the form platform as software infrastructure, not only as a form-design surface.
Forms are one of those systems.
## **What a Regulated Jotform Alternative Should Prove**
A regulated team should not start with "Which form builder is easiest?"
Start with the control requirements.
### **Deployment Boundary**
Where does the platform run?
For some teams, vendor-managed SaaS is acceptable. For others, sensitive data must remain inside a private cloud, on-premise environment, government-approved network, customer-controlled database, or specific regional boundary.
That is one of Form.io's clearest differences. Form.io's [self-hosted forms for enterprise](/features/self-hosted-forms-for-enterprise/) model is built so the platform can deploy inside environments the customer controls. The same core surfaces, including form builder, REST API generation, submission handling, and renderer libraries, can run within the customer's infrastructure.
This matters because deployment is not just an IT preference. It shapes data residency, incident response, logging, backup strategy, access review, and compliance ownership.
### **Data Ownership and Submission Control**
The form response is not just a row in a vendor dashboard.
For regulated teams, a submission may become a patient record, claim record, case file, intake record, eligibility input, identity artifact, or workflow event. The platform needs to fit the system that owns that record.
Form.io's architecture stores forms, resources, submissions, users, and project data as JSON documents in the customer's MongoDB or MongoDB-compatible database. That document model is part of why Form.io can treat form definitions and submission records as application data rather than isolated form entries.
If your team needs application-owned data, this distinction matters more than builder polish.
### **Authentication and Permissions**
Regulated forms rarely have one kind of user.
A healthcare intake flow may involve patients, providers, administrators, support staff, and compliance reviewers. A government service workflow may involve applicants, case workers, supervisors, auditors, and external systems. A SaaS product may need tenant admins, end users, implementation teams, and internal support roles.
The platform has to respect those boundaries.
Form.io's [roles and permissions](/features/forms-for-teams/) model is built around controlling who can create forms, view submissions, modify data, manage projects, and interact with APIs. That matters when the same form infrastructure supports different departments, customers, tenants, or workflow stages.
For regulated teams, permissions are not an admin convenience. They are part of the evidence trail.
### **Generated APIs**
Many hosted form tools expose APIs. That does not mean the form is the API contract.
The stronger architecture is schema-driven: the same definition that renders the form also defines the submission structure and API behavior around it. Form.io's [form from JSON](/features/form-from-json/) model gives teams a JSON-based form definition that can render interfaces and support generated APIs from the same source.
This is useful when forms feed applications, not just spreadsheets.
It lets developers treat forms as governed application surfaces: forms, resources, submissions, validation, webhooks, and workflow actions can be reasoned about together instead of being scattered across a visual builder, a separate API layer, and custom glue code.
### **Audit Trails and Revisions**
Regulated teams need to know more than whether a form was submitted.
They need to know what changed.
Form.io's [complete audit trail](/features/log-forms-complete-audit-trail/) capabilities distinguish between submission revisions and server audit logging. Submission revisions track field-level changes to submitted data. Server audit logging captures system activity such as authentication, form access, API requests, and data modification events.
That distinction matters. An auditor may need to know that a submission was created by one user, modified by another, and later viewed through a specific role or project context. A support team may need to know whether a webhook ran. A compliance team may need to know which form revision captured a historical record.
For financial services, this is not an abstract preference. The [FTC Safeguards Rule](https://www.ecfr.gov/current/title-16/chapter-I/subchapter-C/part-314) requires financial institutions to monitor and log authorized-user activity and detect unauthorized access, use, or tampering with customer information. It also creates retention and change-management expectations around customer information systems.
Form.io's [secure forms compliance readiness](/features/secure-forms-compliance-readiness/) capabilities also include advanced audit logging, action logs, form revisions, submission revision logs, submission collections, and container security scanning as part of the Security Module.
That is a different category of answer than "the form has an activity log."
### **Embedded and White-Labeled Use**
Many regulated forms do not belong on a third-party hosted page.
They belong inside a patient portal, citizen service portal, claims application, financial onboarding flow, education system, or B2B SaaS product.
That creates two requirements at once: the form needs to feel native to the product, and the form data needs to move through the product's security and workflow model.
Form.io is designed for embedded use. Developers can render forms inside their own applications, use the platform's APIs, and let business users modify schemas after the application is in place. For software teams, this is often the useful compromise: developers own the system boundary, while business teams can still manage many form changes without reopening every application ticket.
## **Comparison Table: Jotform Alternative Categories**
**Category****Best fit****Strength****Risk for regulated teams**Hosted no-code form builderSimple forms, surveys, registration, marketing captureFast setup and low technical burdenData and workflow live primarily in the vendor-managed modelHosted enterprise form suiteBusiness teams that need more compliance features and admin controlBetter security, SSO, compliance options, supportMay still be separate from the customer's application infrastructureIndustry-specific form toolNarrow healthcare, education, legal, or government workflowsBetter fit for one vertical's common use casesCan be too narrow for cross-department or product-embedded workflowsCustom-built formsUnique internal systems with strong engineering ownershipMaximum controlExpensive to build, secure, document, version, and maintainSelf-hosted form infrastructureRegulated teams where forms are part of real applicationsDeployment control, APIs, permissions, revisions, audit evidence, embedded useRequires technical ownershipThe last row is where Form.io fits.
It is not the right answer for every team looking for a Jotform alternative. It is the right answer when the team has outgrown the assumption that forms are standalone assets.
## **Why Form.io Is Different From a Normal Form Builder**
Form.io is easier to understand when you stop treating it as a lighter or heavier version of a hosted form builder.
It is infrastructure for forms and the APIs around them.
The visual builder creates schemas. The renderer turns those schemas into forms inside applications. The API server manages forms, resources, submissions, permissions, projects, and actions. The self-hosted deployment model lets the customer run that infrastructure inside their own environment.
That is why Form.io's own guidance is direct about fit. In Form.io's article on [why teams should not use Form.io without a developer team](https://form.io/why-you-shouldnt-use-formio-if-you-dont-have-a-dev-team/), the product is framed as infrastructure software for software developers building custom applications, not a simple form builder for nontechnical users. In other words, it is the wrong choice if a marketing team needs a simple form live this afternoon, and the better choice if a software team needs forms to behave like governed application infrastructure.
That honesty is valuable.
The buyer who only wants speed should not be pushed into infrastructure. The buyer who needs control should not be pushed into convenience software that will fail later.
## **Proof That This Is a Real Deployment Problem**
This is not theoretical positioning.
Form.io's public case-study library includes publicplan GmbH, where the project supported [more than 400 public-sector services and 1,000+ forms](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/) with strict standards and a short timeline. That kind of workload is not a normal contact-form problem. It is a repeatable public-service infrastructure problem.
The same pattern shows up in customer sentiment. A Trustpilot reviewer described Form.io as useful for both integration and standalone use and praised support when users get stuck ([Trustpilot](https://www.trustpilot.com/review/form.io)). The wording is simple, but the integration point is doing real work. Regulated teams are rarely buying a form in isolation. They are buying a form layer that has to connect to the rest of the system.
## **When Form.io Is the Wrong Jotform Alternative**
Form.io is not the right replacement if the team wants the fastest possible hosted form with the least technical setup.
Choose a simpler hosted builder when:
- the form is temporary
- the data is low risk
- the workflow is not part of a product
- the team does not have developers available
- vendor-managed hosting is acceptable
- the organization does not need custom API, identity, or audit architecture
That is not a failure case. It is buyer fit.
For simple forms, infrastructure can be too much.
## **When Form.io Is the Right Jotform Alternative**
Form.io becomes the stronger answer when the form is part of the system.
That usually means one or more of these conditions is true:
- submission data must stay inside a controlled environment
- forms are embedded in a customer-facing application
- different users need different permissions
- submissions need to become application records
- the team needs APIs generated from form definitions
- changes to forms and submissions need revision history
- workflows depend on webhooks, actions, approvals, or integrations
- the organization needs audit evidence after submission
- the platform must support multiple teams, tenants, projects, or environments
These are the use cases where "easy form builder" becomes too small a category.
For those teams, Form.io's advantage is not that it hides complexity. It is that it gives the team places to put the complexity where it belongs: deployment, schema, API, permissions, revisions, audit logs, workflow actions, and application integration.
## **Key Takeaways**
- A broad Jotform alternative list is useful for simple form-building needs.
- Regulated teams need to evaluate deployment boundary, data ownership, permissions, APIs, auditability, and embedded use.
- Hosted builders can work when the form is standalone and vendor-managed storage is acceptable.
- Form.io is strongest when forms become application infrastructure inside customer-controlled environments.
- The right choice depends less on builder polish and more on what must happen after the form is submitted.
## **FAQ**
### **What is the best Jotform alternative for regulated teams?**
The best Jotform alternative depends on the control requirements. If the team only needs a hosted form with better pricing or templates, a simpler hosted builder may be enough. If the team needs self-hosting, APIs, permissions, audit trails, revisions, and embedded application workflows, Form.io is a stronger fit.
### **Is Form.io easier to use than Jotform?**
Not for simple hosted forms. Jotform is easier for nontechnical teams that need to create and publish forms quickly. Form.io is built for teams that need developer control, application integration, self-hosted deployment, generated APIs, and governance around forms and submissions.
### **When should a team avoid Form.io?**
Avoid Form.io when the form is simple, standalone, low risk, and needs to be created by a nontechnical user without developer involvement. Form.io expects technical ownership, especially for self-hosted deployments and production application integration.
### **Why would a regulated team outgrow a hosted form builder?**
Hosted form builders can become limiting when the workflow needs controlled data residency, internal authentication, custom permissions, API-driven records, audit logs, revision history, or direct embedding inside a product or portal. Those needs turn the form into part of the application architecture.
### **Does Form.io support self-hosted forms?**
Yes. Form.io can be deployed in customer-controlled environments, including cloud, private data center, and Docker-based deployments. That gives teams more control over where form infrastructure runs and how submission data fits their existing security boundary.
### **Does Form.io generate APIs from forms?**
Yes. Form.io's schema-driven model uses form and resource definitions to support REST API behavior around submissions, validation, resources, permissions, and workflow actions. That makes it useful when forms are interfaces into application data, not just hosted pages.
### **Is Form.io HIPAA compliant?**
Form.io provides technical capabilities that can support HIPAA-governed workflows in customer-controlled environments, but the customer remains responsible for its compliance program, configuration, policies, deployment controls, and business associate requirements.
### **Does a BAA make a form workflow compliant?**
No. HHS explains that [business associate contracts](https://www.hhs.gov/hipaa/for-professionals/covered-entities/sample-business-associate-agreement-provisions/index.html) define permitted uses, safeguards, breach reporting, access, amendment, accounting, subcontractor, and termination obligations. A BAA matters, but compliance also depends on how the workflow is configured, secured, monitored, and governed.
### **Why do audit trails matter for form submissions?**
Audit trails help answer who accessed data, who changed it, what changed, when it changed, and which workflow action ran. For regulated teams, that evidence can matter as much as the original submission.
### **Can Form.io be embedded inside a SaaS product?**
Yes. Form.io is designed for embedded application use. Developers can render forms inside their own applications, connect them to Form.io APIs, and let authorized business users manage form schemas after the product infrastructure is in place.
### **What should I ask before choosing a Jotform alternative?**
Ask where data is stored, who controls deployment, how permissions work, whether APIs are generated from the form schema, how revisions are handled, whether audit logs are available, and whether the form can live inside your own application or portal.
## **Build Regulated Form Infrastructure With Form.io**
If you only need a quick hosted form, choose the simplest tool that satisfies the job.
If your forms define application workflows, submission records, permissions, APIs, audit evidence, and deployment boundaries, choose infrastructure that respects that reality.
[Try Form.io for regulated form infrastructure](/try-formio-for-free/).
# Formbricks vs Form.io: Survey Tool or Form Infrastructure?
[  ](https://form.io/formbricks-formio-vs-formbricks-self-hosted-typeform-alternative/)Organizations looking for a self-hosted alternative to Typeform or a privacy-first feedback platform often compare Formbricks and Form.io. Both have open-source and self-hosted evaluation paths, but they solve fundamentally different problems.
Formbricks focuses on surveys, experience management, and product feedback. Form.io is designed as application infrastructure for forms, APIs, workflows, and enterprise governance, including agentic workflow patterns where governed forms and submissions need to stay connected to permissions, validation, actions, and audit evidence.
That distinction matters before the feature checklist begins. The question is not whether both products can build forms. It is whether the form is mainly a survey or part of the application architecture.
## **Key takeaways**
- Formbricks is best understood as an open-source experience management and survey platform for link surveys, website surveys, in-app surveys, email surveys, and customer feedback workflows.
- Form.io is best understood as form-driven application infrastructure: JSON-defined forms, generated APIs, submission data, permissions, workflow actions, self-hosted deployment, and governed patterns for agentic workflows.
- Formbricks is a credible choice when the buyer wants a self-hosted Typeform alternative or privacy-first feedback tool.
- Form.io is the better fit when forms need to be embedded in a product, reused across tenants, governed through submission-level permissions, exposed through APIs, managed across enterprise environments, or used as structured context for agentic workflows.
- The main question is not “Which one is open source?” It is “Does your form need to collect feedback, or does it need to become part of the application architecture?”
## **Quick comparison**
The comparison below summarizes the product jobs documented in Formbricks’ platform, API, self-hosting, and licensing docs and Form.io’s JSON schema, generated API, self-hosting, and embedded builder pages.
## **Decision area****Formbricks****Form.io**Primary jobOpen-source surveys and experience managementForm and API infrastructure for embedded, governed applications and agentic workflowsBest use caseFeedback, NPS, CSAT, product surveys, link surveys, in-app micro-surveysRegulated intake, customer-facing product forms, portals, workflow forms, schema-driven applications, and agentic workflow interfacesForm modelSurvey flows and question types for response collectionJSON schemas that define UI, validation, submission structure, and backend APIsAPI modelPublic Client API for survey interactions and Management API for surveys, contacts, responses, and webhooksForm and resource paths generate schema and submission endpointsEmbeddingWebsite, app, email, and link survey deliveryRenderer and builder embedded directly into customer-controlled applicationsGovernance centerSelf-hosting, privacy, survey data control, open-core packagingProject, form, and submission permissions; roles, actions, audit patterns, stages, and deployment boundariesBest buyerProduct, growth, customer experience, and feedback teams that need open-source surveysDevelopment teams building form-heavy products, portals, and enterprise workflowsWrong fit warningNot designed to be the form/API layer for every application workflowNot the lightest answer for simple surveys or one-off feedback forms**What Formbricks is good at**
Formbricks deserves a fair reading. Its official docs describe it as an open-source platform for collecting and analyzing feedback from customers, users, and employees through targeted surveys.
That is a real product category.
If your team needs NPS surveys, CSAT surveys, product feedback, onboarding feedback, churn surveys, website surveys, in-app micro-surveys, or link-based surveys, Formbricks is built for that motion. Its homepage frames the product around privacy-first experience management, feedback collection across websites and apps, and self-hosting when a team wants more control over data.
Its open-source form builder page also makes the category clear: unlimited forms, unlimited responses, open-source survey building, conditional logic, multi-language surveys, integrations, hidden fields, partial submissions, single-use links, and custom domains.
That matters because the Typeform-alternative search is not only about technical architecture. Many buyers really do want a better survey tool: more generous limits, more privacy control, self-hosting, open-source code, and enough product polish for feedback collection.
Formbricks has a strong claim there.
The question is what happens when the form is not mainly a survey.
## **What Form.io is good at**
Form.io is strongest when the form is not just a feedback surface, but part of the application contract. Its value shows up when a team needs JSON-defined forms, generated APIs, submission records, validation, permissions, workflow actions, audit patterns, and self-hosted deployment to stay aligned.
That includes regulated intake, customer portals, tenant-managed SaaS forms, healthcare and financial workflows, government services, insurance claims, and internal processes where the submitted record needs to remain explainable over time.
It also matters for agentic workflows. If an AI agent or human-in-the-loop workflow needs to ask for data, validate fields, route submissions, require confirmation, or operate inside an enterprise governance boundary, the form layer needs to be more than a survey delivery tool. Form.io gives developers a governed form and API layer that can become part of that workflow infrastructure.
So the Form.io category should appear early in the decision: it is not the survey tool in this comparison. It is the form infrastructure layer when forms, submissions, APIs, and workflow behavior need to be owned by the application.
## **What changes when a survey becomes application infrastructure**
A survey collects feedback. Application infrastructure carries business process.
That line gets blurry at first. A customer feedback form can become a support workflow. A product survey can feed account health. A compliance questionnaire can become an auditable record. A tenant-specific intake form can become a feature inside a SaaS platform. A public-facing form can become the first step in a case management workflow.
At that point, the evaluation changes.
The buyer is no longer asking only whether the tool can collect a response. The buyer is asking:
- Who owns the schema?
- What validates the submission?
- Which API receives and exposes the data?
- Can the form be embedded inside our product?
- Can customers build or modify their own forms inside our app?
- Can roles and permissions apply at the form and submission level?
- Can the same form move through development, test, and production?
- Can historical submissions remain explainable after form definitions change?
Those are Form.io questions.
Form.io’s [drag-and-drop form builder and APIs](https://form.io/features/drag-and-drop-form-builder-apis/) page describes the builder as a JSON schema editor that defines form UI, validation, the data model, and REST API endpoints together. That is the architectural difference.
Formbricks is strong when the workflow is survey-led. Form.io is strong when the form is a contract between the user interface, submitted data, backend API, permissions, and downstream process.
## **Survey flows vs schema contracts**
Formbricks is optimized around survey delivery. Its own Typeform-alternative page describes link surveys, in-app micro-surveys, pop-up surveys, Dockerized self-hosting, an open API, and open-source customization.
That is useful when the main asset is a survey.
Form.io starts from a different object: the form schema. Every Form.io form is a JSON document that defines the title, path, display mode, components, validation, conditional logic, and submission data shape.
That schema can render in an application, accept submissions, validate data, and create predictable API behavior. The form is not only a front-end artifact. It is the source of truth that connects rendering, validation, submission storage, and backend endpoints.
This matters when multiple systems need to trust the same form definition.
If the form is only a feedback survey, a survey-first platform is usually enough. If the form is a reusable business object across applications, tenants, workflows, and environments, the schema needs to carry more responsibility.
That is where Form.io’s model becomes more valuable.
## **API and data model comparison**
Formbricks has APIs, and the comparison should say that clearly. Its REST API documentation describes two API surfaces: a Public Client API for frontend survey interactions and a Management API for backend management tasks. The exposed methods include displays, responses, contacts, surveys, action classes, contact attributes, and webhooks.
That API surface fits a survey and feedback product.
Form.io’s API model is different because the form path and schema define the submission API itself. The [Forms from JSON](https://form.io/features/form-from-json-schema/) documentation explains that a form path can create endpoints for retrieving the schema and creating, listing, reading, updating, and deleting submissions.
That changes the center of gravity.
In Formbricks, the API helps manage and operate surveys. In Form.io, the form can define part of the application data layer.
For feedback collection, Formbricks’ model is sensible. For application intake, regulated submissions, onboarding flows, service requests, claims, eligibility workflows, or tenant-managed forms, Form.io’s generated form/submission API model is usually the more direct fit.
## **Embedding and white-labeling**
Formbricks can reach users in useful places: websites, apps, email, pop-ups, and links. That is exactly what a survey platform should do. For customer experience teams, that flexibility matters because feedback is most useful when it appears at the right moment in the product journey.
Form.io uses embedding for a different purpose.
The [Form.io open-source page](https://form.io/open-source/) explains that forms are rendered from JSON using Form.io renderers for frameworks such as Vanilla JavaScript, Angular, React, and Vue. The [Enterprise Form Builder Module](https://form.io/product-announcement/enterprise-form-builder-module/) goes further: it lets teams embed a customizable, white-labeled form-building interface directly into their own applications.
That is not the same as embedding a survey.
It means a SaaS platform, healthcare product, government portal, insurance system, or internal enterprise app can expose governed form creation to its users without sending those users into a separate form product. The application still controls navigation, authentication, permissions, branding, allowed components, data model, and workflow behavior.
That is a major distinction for platform teams.
If you want to ask users for feedback, Formbricks may be the cleaner answer. If your customers need to build and manage forms inside your product, Form.io fits the architecture more directly.
## **Self-hosting, licensing, security, and governance**
Do not reduce this comparison to “self-hosted vs not self-hosted.” Formbricks is a legitimate self-hosted option. Its self-hosting docs describe cloud hosting, free self-hosting, self-hosting with an Enterprise Edition license, Docker setup, one-click setup, migration, configuration, and integrations.
Formbricks’ license docs also give useful detail. The core source code is AGPLv3, while larger-team and enterprise functionality lives under a separate enterprise license. The Community Edition includes self-hosting for commercial purposes, unlimited surveys, unlimited responses, unlimited users, API access, SDKs, website and app surveys, webhooks, multi-language surveys, and integrations. Enterprise features include items such as teams and access roles, audit logs, SSO, two-factor authentication, contact management, quota management, and prioritized support, depending on the license configuration.
That is a strong open-source story, but buyers need to understand the packaging.
Open source and self-hosting are valuable. They are not the same thing as complete application governance.
GitHub’s 2025 Octoverse report shows why this nuance matters. It says 63% of all repositories are public or open source, while 81.5% of contributions happen in private repositories ([GitHub Octoverse 2025](https://github.blog/news-insights/octoverse/octoverse-a-new-developer-joins-github-every-second-as-ai-leads-typescript-to-1/)). Modern software teams often depend on open source while doing most operational work inside private, governed systems.
Form.io’s self-hosted model is built for that private operational side. Its [self-hosted forms for enterprise](https://form.io/features/self-hosted-forms-for-enterprise/) page describes Form.io as deployable infrastructure that can run in AWS, Azure, Google Cloud, private data centers, or local Docker-based environments. It also describes separate components such as Enterprise Server, PDF Server, Developer Portal, renderer libraries, deployment environments, file storage, database requirements, and dev/test/prod patterns.
The key point is not that Form.io is self-hosted and Formbricks is not. Both can be self-hosted.
The key point is what is governed inside that boundary.
Formbricks governs surveys, feedback, contacts, responses, and experience-management workflows. Form.io governs forms, resources, submissions, generated APIs, roles, permissions, actions, environments, and form lifecycle.
Those are different control surfaces.
## **Pricing basis and scale predictability**
Formbricks has a strong Community Edition story for survey teams: AGPLv3 core access, free self-hosting, unlimited surveys, unlimited users, and unlimited responses. Teams evaluating Enterprise Edition should verify response, feature, workspace, support, and private-fork requirements directly against the current license table.
Form.io’s pricing story is different.
The point is not that Form.io is cheaper in every scenario. The point is that the buying model is designed around configured form/API infrastructure. Form.io’s [configuration-based pricing](https://form.io/configuration-based-pricing/) page lists unlimited API calls, unlimited submissions, unlimited developers and form builders, and unlimited forms and resources in relevant enterprise configurations.
That difference matters when forms become a platform feature.
If every tenant, customer, department, agency, or product line can create forms, usage can grow in ways that are hard to forecast. A per-response survey model may be fine for customer feedback. A configuration-based infrastructure model may be a better fit when submissions, forms, builders, tenants, and APIs are part of the product architecture.
The buyer should ask what is scaling.
If survey responses are scaling, Formbricks may fit. If application forms, submitted records, generated endpoints, customer form builders, and environments are scaling, Form.io deserves closer evaluation.
## **Customer proof: when form infrastructure scale becomes real**
Form infrastructure arguments can sound abstract until the volume shows up.
Form.io’s public case-study pages describe a publicplan GmbH implementation supporting more than 400 services and 1,000+ forms, and a Safety Mojo implementation that Form.io says saved 6-12 months of development time. Those are Form.io-published examples, so they should be read as customer proof rather than independent analyst validation. The Safety Mojo page also includes the customer proof line, “Form.io cleans up all the dirty work and does it for you” ([publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/), [Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)).
Those examples point to the real Form.io use case.
The hard part at that scale is not drawing a field. It is keeping the form, schema, submission record, API behavior, permissions, environment boundary, and downstream workflow aligned as requirements change.
IBM’s 2025 Cost of a Data Breach report puts the global average breach cost at $4.4 million and says 63% of organizations lacked AI governance policies ([IBM Cost of a Data Breach 2025](https://www.ibm.com/reports/data-breach)). That is not a form-specific statistic, and it should not be treated as one. It is a reminder that data workflows and governance boundaries are not minor implementation details when forms collect sensitive or operationally important data.
For teams handling simple feedback, that level of infrastructure may be unnecessary. For teams building regulated intake, customer portals, financial workflows, healthcare workflows, insurance claims, government services, or multi-tenant form platforms, it is often the main issue.
## **When Formbricks is the better choice**
Formbricks is likely the better fit when your team needs:
- a self-hosted Typeform alternative
- product feedback surveys
- NPS, CSAT, CES, onboarding, churn, or market research surveys
- in-app micro-surveys and website surveys
- open-source survey tooling with a clear cloud/self-host path
- privacy-first feedback collection
- a survey API for responses, contacts, and webhooks
- broad survey features without building a survey platform from scratch
In those cases, Form.io may be too much infrastructure. If the primary object is a survey and the output is feedback analysis, Formbricks is a natural choice.
## **When Form.io is the better choice**
Form.io is likely the better fit when your team needs:
- embedded forms inside a customer-facing application
- white-labeled form building inside your own product
- JSON-defined forms that drive rendering, validation, submissions, and APIs
- generated form APIs instead of hand-built backend endpoints for every form
- form, project, and submission permissions
- dev/test/prod form environments and SDLC-aware form promotion
- multi-tenant form workflows
- audit-relevant controls such as permissions, deployment boundaries, submission history, and security/compliance features
- configuration-based pricing for high-volume form infrastructure
- forms that support workflows beyond feedback collection
- governed form and submission context for agentic workflows
In those cases, the form is no longer just a question flow. It is a governed application layer.
## **The decision rule**
Choose Formbricks if the main job is collecting feedback through open-source, self-hosted surveys.
Choose Form.io if the main job is making forms, submissions, APIs, permissions, workflow behavior, and agentic workflow context part of your product or enterprise application infrastructure.
That is the real comparison.
Formbricks helps teams own survey and feedback collection. Form.io helps teams own the form layer when it becomes part of the architecture.
## **FAQ**
### **Is Formbricks a form builder?**
Yes, but it is better understood as an open-source survey and experience management platform. It can build forms and surveys, but its strongest fit is feedback collection across websites, apps, emails, and shared links.
### **Is Form.io a Formbricks alternative?**
Form.io can be an alternative when the buyer’s requirement is governed forms, generated APIs, embedded form rendering, self-hosted deployment, and application infrastructure. It is not a direct replacement for every survey, feedback, or experience-management use case Formbricks supports.
### **Which is better for a self-hosted Typeform alternative?**
Formbricks is usually the stronger fit for a self-hosted Typeform alternative. It is built around surveys, feedback collection, open-source access, and privacy-first response workflows.
### **Which is better for embedded forms?**
Form.io is usually the stronger fit when forms need to be embedded into a customer-facing product or enterprise application as a governed runtime. Formbricks can embed surveys, while Form.io is built around embeddable form rendering and embedded form building.
### **Can Formbricks be self-hosted?**
Yes. Formbricks documents free self-hosting and self-hosting with an Enterprise Edition license. Buyers should verify which features are included in Community Edition and which require Enterprise Edition.
### **Can Form.io be self-hosted?**
Yes. Form.io supports self-hosted deployment with API server environments, portal/authoring environments, renderer libraries, PDF Server options, customer-controlled databases, file storage choices, and common dev/test/prod deployment structures.
### **Does Formbricks have an API?**
Yes. Formbricks documents a Public Client API for frontend survey interactions and a Management API for backend management tasks such as surveys, contacts, responses, action classes, and webhooks.
### **Does Form.io generate APIs from forms?**
Yes. Form.io’s distinction is that form schemas and paths can directly define schema and submission endpoints, making the form itself part of the application API contract.
### **Which is better for regulated form workflows?**
Form.io is usually the better fit when the regulated workflow depends on form schemas, submission permissions, generated APIs, deployment boundaries, submission history, and long-term governance of form changes. Formbricks may still fit regulated feedback collection when a survey-first model is enough.
### **Which is better for customer-facing SaaS platforms?**
Form.io is usually the stronger fit when SaaS customers need to create or use forms inside your product experience, especially with white-labeling, tenant boundaries, permissions, and governed form behavior. Formbricks is stronger when the SaaS product mainly needs in-app feedback and customer surveys.
### **How should teams evaluate Formbricks vs Form.io?**
Start by deciding whether you are choosing a survey platform or a form infrastructure layer. Then compare deployment, embedding, API behavior, permissions, licensing, pricing basis, audit needs, and who will maintain the form model over time.
## **Build form infrastructure without turning every form into a custom project**
When forms become part of the application architecture, the right platform needs to do more than collect responses. It needs to keep schemas, submissions, APIs, permissions, and workflows aligned as the system grows.
[Try Form.io for free](https://form.io/try-formio-for-free/) if your team needs self-hosted form infrastructure that developers can embed, govern, and scale inside the applications you already own.
# Budibase vs Form.io: Internal Tools or Form Infrastructure?
[  ](https://form.io/budibase-formio-vs-budibase/)Organizations comparing self-hosted, open-source builders for internal tools and enterprise forms often put Budibase and Form.io in the same shortlist. Both speak to technical teams that want more control than lightweight SaaS form tools provide, but they solve different layers of the problem.
Budibase focuses on internal operations apps, agents, automations, and workflows around business data. Form.io is designed as application infrastructure for forms, APIs, workflows, and enterprise governance, including agentic workflow patterns where governed forms and submissions need to stay connected to permissions, validation, actions, and audit evidence.
That distinction matters before the feature checklist begins. The question is not whether both products can collect data. It is whether the form is a screen inside an internal app or a governed contract inside the application architecture.
## **Key takeaways**
- Budibase is best understood as an open-source operations platform for internal tools, agents, apps, automations, and connected data.
- Form.io is best understood as form-driven application infrastructure: JSON-defined forms, generated APIs, submission data, permissions, workflow actions, self-hosted deployment, and governed patterns for agentic workflows.
- Budibase is a credible choice for internal apps, request workflows, admin panels, and operational tools.
- Form.io is the better fit when forms need to be embedded in a product, reused across tenants, governed through submission-level permissions, exposed through APIs, managed as part of an enterprise SDLC, or used as structured context for agentic workflows.
- The main question is not "Which product has forms?" It is "What layer do your forms need to own?"
## **Quick comparison**
## **Decision area****Budibase****Form.io**Primary jobInternal operations platform for agents, apps, automations, workflows, and connected dataForm and API infrastructure for embedded, governed, form-driven applications and agentic workflowsForm modelForms are components inside Budibase apps, usually tied to tables, views, custom schemas, or app workflowsForms are JSON schemas that define UI, validation, submission structure, and backend APIsAPI modelPublic API gives access to apps, users, tables, and data through a RESTful APIEach form/resource path can generate REST endpoints for schemas and submissionsEmbeddingPublished apps can be embedded with iframes; enterprise microfrontend options existRenderer and builder can be embedded directly into customer-controlled applicationsGovernanceTenant roles, workspace roles, app roles, SSO, groups, and audit logs depending on planProject, form, and submission permissions; roles, actions, audit patterns, stages, and self-hosted environmentsBest buyerTeams building internal tools and operations workflows quicklyTeams standardizing forms, APIs, submissions, permissions, workflow behavior, and agentic workflow context as product infrastructureWrong fit warningLess ideal when the form layer must be a portable, governed contract outside an internal app surfaceNot a general internal-tools replacement for every dashboard, CRUD app, or admin panel**What Budibase is good at**
Budibase deserves a fair reading. Its own documentation describes it as an open-source platform for internal tools and workflow automation, used by more than 200,000 teams to automate workflows, handle requests, build internal tools, and connect systems using their own data, LLMs, and APIs.
That is a real category.
If your team needs to build an internal approval app, a data-entry screen, an admin panel, a request workflow, an operations dashboard, or an agent-assisted internal process, Budibase is built for that motion. It gives teams a visual app builder, data connections, automations, apps, agents, roles, and deployment options in one operations-oriented surface.
Budibase forms are part of that app-building model. The official forms documentation says forms are built from a Form component, Field group components, and Input components, with optional schemas tied to tables, views, relationships, or custom structures.
That is useful when the form is a screen inside an internal app.
The question is what happens when the form is no longer just a screen.
## **What Form.io is good at**
Form.io is strongest when forms, submissions, validation, permissions, APIs, and workflow actions need to become governed infrastructure rather than app components. The form definition can become a JSON contract that drives rendering, submission shape, validation rules, backend endpoints, and downstream handoffs.
That makes Form.io a better fit for customer-facing forms, regulated intake, tenant-managed SaaS form builders, healthcare and financial workflows, government services, insurance claims, and enterprise processes where the form record needs to stay governed after submission.
It also matters for agentic workflows. When AI-assisted or runtime agents need to collect structured data, validate inputs, trigger actions, or require human confirmation inside enterprise guardrails, the form layer needs stable schemas, permissions, and audit patterns. Form.io is built for that form and workflow infrastructure layer.
So the Form.io category should appear early in the decision: it is not the general internal app builder in this comparison. It is the governed form infrastructure layer when forms, APIs, submissions, and workflow behavior need to be owned by the application architecture.
## **What changes when forms become infrastructure**
Many teams start with a simple internal form and end up with application infrastructure.
The intake form becomes a case creation workflow. The customer form becomes a white-labeled feature inside a SaaS product. The compliance form becomes a regulated submission record. The public-sector form becomes one of hundreds of services that must follow the same standards. The healthcare or financial-services form becomes part of a workflow where validation, access, auditability, and downstream APIs matter as much as the UI.
That is the point where the Budibase vs Form.io decision gets sharper.
Form.io's form builder is not only a visual form editor. The Form.io documentation says the builder creates a JSON schema representation of the form, and that schema is used to dynamically render the form and automatically generate the REST API that supports it ([Form.io form building docs](https://help.form.io/userguide/forms/form-building)).
That is the architectural difference.
In Budibase, forms help users interact with data inside apps. In Form.io, the form schema can become the contract that defines the rendered UI, validation rules, submitted data shape, API endpoints, permissions, and downstream workflow behavior.
For teams whose forms are application infrastructure, that difference is not small.
## **Forms inside apps vs forms as contracts**
Budibase is strongest when you want a visual way to assemble apps around data and process. Its forms can create and update data, use schemas, and participate in workflows. For internal teams, that can be exactly right.
Form.io is stronger when the form definition itself needs to travel across systems.
Every Form.io form is a structured JSON definition. Form.io's JSON-schema forms documentation explains that a form schema can define the form title, path, type, display mode, components, validation, conditional logic, and submission data shape. It also explains that a form path creates endpoints such as schema retrieval and submission create/list/read/update/delete operations ([Forms from JSON](https://form.io/features/form-from-json-schema/)).
That matters when multiple applications, teams, tenants, or agents need to rely on the same form contract.
If a form is only a UI on top of a table, the surrounding system still needs to decide how validation is enforced, how submissions are stored, how APIs behave, how permissions apply, and how downstream services consume the data. If the form is a governed schema with APIs and submissions attached, more of that behavior has one source of truth.
That is why Form.io often resonates with teams that have outgrown simple form building. They are not trying to draw fields faster. They are trying to keep the form, data model, API behavior, permissions, and workflow triggers aligned as requirements change.
## **API and data model comparison**
Budibase has an API, and that should be acknowledged clearly. Its public API documentation says the API provides access to applications, users, tables, and data through a RESTful API and an OpenAPI 3.0 specification.
That makes sense for an internal operations platform. You can integrate with the Budibase environment, work with tables and records, and connect Budibase to broader business systems.
Form.io's API model is more specific to form infrastructure. The form schema defines the path and the submission endpoints that support that form. Form.io's drag-and-drop builder and API documentation explains that saving a form registers endpoints for creating, listing, reading, updating, and deleting submissions, with validation enforced from the schema ([drag-and-drop form builder APIs](https://form.io/features/drag-and-drop-form-builder-apis/)).
That is a different center of gravity.
Budibase helps you build apps around data. Form.io helps you define the form and submission layer that creates, validates, stores, and exposes that data in the first place.
For an internal app, either model may work. For a customer-facing product, regulated intake workflow, or multi-tenant form platform, the form-defined API model can be the safer foundation.
## **Embedding and white-labeling**
Budibase supports embedding, but the default model is app embedding. Its embedded app documentation describes embedding a published Budibase app in an iframe, with access considerations for public screens, allowed domains, and authenticated embedded users. Budibase also documents an enterprise microfrontend option for non-iframe embedding in specific licensed scenarios.
That can be useful when the thing you want to embed is an app.
Form.io is built for a different embedding requirement: embedding form rendering and form building inside the application your team already owns. The open-source `formio.js` renderer and SDK can render JSON schema forms inside an application and communicate with Form.io APIs ([Form.io JavaScript renderer](https://github.com/formio/formio.js)). The [Enterprise Form Builder Module](https://form.io/enterprise-form-builder-module/) lets teams expose white-labeled, preconfigured form building inside their own product while controlling components, guardrails, structured data, APIs, permissions, and workflow behavior.
That distinction is important for SaaS platforms, government service portals, healthcare products, and other systems where customers or internal teams need self-service form creation without leaving the product experience.
If you want to embed a whole operational app, Budibase may fit. If you want to embed governed form creation and rendering as part of your own product architecture, Form.io is the more direct match.
## **Self-hosting, security, and governance**
Do not reduce this comparison to "self-hosted vs not self-hosted." Budibase is a legitimate self-hosted option. Its hosting docs describe Budibase Cloud and self-hosted installation paths, including Docker, Kubernetes, and DigitalOcean. Its security docs say the self-hosted version can be deployed inside your own network, on your own servers, with control over how data is secured and without data needing to leave your VPC.
That is real.
The stronger Form.io argument is not that Budibase lacks deployment control. It is that Form.io's control is organized around form infrastructure.
Form.io's self-hosted deployment documentation describes API server environments, portal/authoring environments, Docker-based deployment, and common dev/test/prod structures ([Form.io self-hosted deployment docs](https://help.form.io/deployments/deployment-guide.md)). Its roles and permissions documentation separates access across project, form, and submission scopes, with permissions governing form definitions and submission data ([Form.io roles and permissions docs](https://help.form.io/developers/roles-and-permissions.md)).
That is the level of detail serious form infrastructure often needs.
Open source is also not a substitute for governance by itself. GitHub's 2025 Octoverse report says 63% of all repositories are open source or public, while 81.5% of contributions happen in private repositories, showing how public software and private enterprise work now depend on each other ([GitHub Octoverse 2025](https://github.blog/news-insights/octoverse/octoverse-a-new-developer-joins-github-every-second-as-ai-leads-typescript-to-1/)). Black Duck's 2026 OSSRA analysis found that 87% of audited codebases contained at least one vulnerability and 78% contained high-risk vulnerabilities, which is why open-source adoption still needs supply-chain governance ([Black Duck 2026 OSSRA](https://www.blackduck.com/blog/open-source-trends-ossra-report.html)). Gartner also predicts that by 2027, 70% of organizations with platform teams will include GenAI capabilities in internal developer platforms, increasing the need for reusable guardrails around generated and internal applications ([Gartner software engineering trends](https://www.gartner.com/en/newsroom/press-releases/2025-07-01-gartner-identifies-the-top-strategic-trends-in-software-engineering-for-2025-and-beyond)).
The practical lesson is simple: open source and self-hosting are valuable, but enterprise teams still need clear controls over data, roles, changes, workflows, and audit evidence.
Budibase has governance features such as tenant roles, workspace app roles, SSO, user groups, and audit logs. Its audit log docs say audit logs track events across a Budibase installation, and also show an upgrade path for free-tier users who need audit logs. That is not a criticism. It is a reminder to verify packaging against the controls your team actually needs.
For Form.io buyers, the governance question is more specific: who can change a form definition, who can submit, who can read submissions, which action fires after submission, which environment owns the schema, and which historical submission was governed by which form state?
Those are form-infrastructure questions.
## **Pricing basis: free tier vs scale predictability**
Budibase has a strong pricing story for many teams. Its pricing page includes a free open-source self-hosted plan, and higher tiers add capabilities such as more logs, custom branding, backups, SSO, user groups, SCIM, audit logs, priority support, and air-gapped deployment options.
For internal tools, that can be compelling.
Form.io's pricing story is different. The point is not that it is cheaper in every scenario. The point is that it is priced around self-hosted form/API configuration rather than usage meters. Form.io's configuration-based pricing page lists unlimited API calls, unlimited submissions, unlimited developers and form builders, and unlimited forms and resources in relevant configurations, and it frames the buying model around projects, API/PDF environments, and enterprise add-ons ([Form.io configuration-based pricing](https://form.io/configuration-based-pricing/)).
That difference matters when forms are high-volume, public-facing, embedded, or tenant-driven.
If every customer, office, agency, or product team can create forms, usage can become difficult to predict. A pricing model that avoids per-form, per-submission, per-end-user, per-developer, and per-API-call charges can make more sense when forms are infrastructure rather than a handful of internal apps.
## **Customer proof: when this becomes real**
Form infrastructure arguments can sound abstract until the scale shows up.
A Form.io public-sector case study for publicplan GmbH describes support for over 400 services and 1,000+ forms under strict standards and a short timeline ([publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)). Another Form.io-hosted customer proof point describes a long-time platform user running multiple production applications with a Form.io backend and saying, "Form.io cleans up all the dirty work and does it for you" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)).
Those examples point to the same idea: when forms multiply across services, products, departments, or customers, the hard part is not dragging fields onto a page. The hard part is keeping the form layer governed, reusable, API-backed, and operationally stable.
That is the Form.io case.
## **When Budibase is the better choice**
Budibase is likely the better fit when your team needs:
- internal tools for operations, support, HR, IT, finance, or admin workflows
- agent-assisted internal request handling
- dashboards, admin panels, and CRUD apps over business data
- a visual app builder for teams that want to ship internal workflows quickly
- open-source self-hosting for internal app delivery
- automations and app screens in one operations platform
In those cases, Form.io may be too specialized. If the form is just one component inside a broader internal app, Budibase can be the simpler answer.
## **When Form.io is the better choice**
Form.io is likely the better fit when your team needs:
- embedded forms inside a customer-facing application
- white-labeled form building inside your own product
- JSON-defined forms that can drive rendering, validation, submissions, and APIs
- generated form APIs instead of hand-built backend endpoints for every form
- submission-level permissions and form-specific access control
- dev/test/prod form environments and SDLC-aware form promotion
- multi-tenant form workflows
- compliance-oriented audit patterns
- no per-submission, per-form, per-end-user, or per-API-call pricing surprise
- governed form and submission context for agentic workflows
In those cases, the form is no longer a UI component. It is a governed application layer.
## **The decision rule**
Choose Budibase if the main job is building internal operational apps around data, approvals, automations, and agents.
Choose Form.io if the main job is making forms, submissions, APIs, permissions, workflow behavior, and agentic workflow context part of your product or enterprise application infrastructure.
That is the real comparison.
Budibase helps teams build operational applications faster. Form.io helps teams keep form-driven systems governed when the forms themselves become the architecture.
## **FAQ**
### **Is Budibase a form builder?**
Budibase includes form-building capabilities, but it is better understood as an internal operations platform for apps, agents, automations, workflows, and connected data. Forms are one important part of that app-building model.
### **Is Form.io a Budibase alternative?**
Form.io can be an alternative when the specific requirement is governed forms, submissions, generated APIs, embedded form rendering, and self-hosted form infrastructure. It is not a general replacement for every internal app or dashboard use case Budibase supports.
### **Which is better for internal tools?**
Budibase is usually the stronger fit for broad internal tools, admin panels, request workflows, dashboards, and operations apps. Form.io is more specialized around the form and API layer.
### **Which is better for embedded forms?**
Form.io is usually the stronger fit when forms need to be embedded into a customer-facing product or internal application as a governed runtime. Budibase can embed apps, but Form.io is built around embeddable form rendering and embedded form building.
### **Can Budibase be self-hosted?**
Yes. Budibase supports self-hosting and documents deployment paths such as Docker, Kubernetes, and DigitalOcean. Buyers should still verify which governance, audit, SSO, SCIM, support, and air-gapped features are included in the plan they intend to use.
### **Can Form.io be self-hosted?**
Yes. Form.io supports self-hosted deployment with API server environments, portal/authoring environments, Docker-based deployment, customer-controlled databases, and common dev/test/prod structures.
### **Does Budibase generate APIs from forms?**
Budibase has a public API for apps, users, tables, and data. Form.io's distinction is that form schemas and paths can directly define form and submission endpoints, making the form itself part of the API contract.
### **Which is better for regulated form workflows?**
Form.io is usually the better fit when the regulated workflow depends on form schemas, submission permissions, generated APIs, deployment boundaries, audit patterns, and long-term governance of form changes. Budibase may still fit internal regulated workflows when the app-builder model is enough.
### **Which is better for customer-facing SaaS platforms?**
Form.io is usually the stronger fit when SaaS customers need to create or use forms inside your product experience, especially with white-labeling, tenant boundaries, and governed form behavior. Budibase is stronger when the goal is to build internal apps for your own team.
### **How should teams evaluate Budibase vs Form.io?**
Start by deciding whether you are choosing an internal app builder or a form infrastructure layer. Then compare deployment, embedding, API behavior, permissions, pricing basis, audit needs, and who will maintain the form model over time.
## **Build form infrastructure without turning every form into a custom project**
When forms become part of the application architecture, the right platform needs to do more than render fields. It needs to keep schemas, submissions, APIs, permissions, and workflows aligned as the system grows.
[Try Form.io for free](https://form.io/try-formio-for-free/) if your team needs self-hosted form infrastructure that developers can embed, govern, and scale inside the applications you already own.
# HIPAA-Compliant Form Builder: What Healthcare SaaS Teams Should Evaluate
## [  ](https://form.io/hipaa-compliant-form-builder-healthcare-saas-platforms/)**Key Takeaways**
- A HIPAA-compliant form builder is not compliant because it has a healthcare template or a lock icon.
- If a vendor creates, receives, maintains, or transmits ePHI for a covered entity or business associate, the BAA and operational responsibility boundary matter.
- Hosted HIPAA form builders can be a good fit for simple intake, consent, appointment, or website forms.
- Healthcare SaaS teams usually need more than a hosted form link: APIs, embedded rendering, role-aware access, audit logs, revision history, and deployment control.
- Form.io is strongest when HIPAA-governed forms are part of application infrastructure rather than a standalone intake tool.
## **What "HIPAA-Compliant Form Builder" Actually Means**
The phrase "HIPAA-compliant form builder" is useful shorthand, but it can hide the real decision.
HIPAA compliance is not a feature that one vendor turns on for the whole organization. It is a legal, contractual, administrative, technical, and operational responsibility. The form builder can support that responsibility. It cannot replace it.
The U.S. Department of Health and Human Services explains that when a covered entity or business associate uses a cloud service to create, receive, maintain, or transmit ePHI, the cloud service provider is generally a business associate and the parties need a HIPAA-compliant business associate agreement. [HHS also notes](https://www.hhs.gov/hipaa/for-professionals/special-topics/health-information-technology/cloud-computing/index.html) that this can still be true even when the provider stores only encrypted ePHI and does not hold the decryption key.
That point matters for online forms.
If a form collects PHI, the risk does not stop at the submit button. The data may be stored, emailed, exported, routed through webhooks, copied into a CRM, written to a database, attached to a PDF, shown in an admin portal, or sent to downstream systems. A HIPAA-ready form tool has to be evaluated across that whole path.
The [HHS Security Rule](https://www.hhs.gov/hipaa/for-professionals/security/index.html) frames the obligation around administrative, physical, and technical safeguards for the confidentiality, integrity, and availability of ePHI. In plain terms: the form is only one surface. The system around the form has to be governed too.
The risk is not theoretical. IBM's 2025 Cost of a Data Breach report puts the global average breach cost at [$4.4 million](https://www.ibm.com/reports/data-breach?app=true). That is not a healthcare-form-specific number, but it gives the right scale for the decision: a form that collects sensitive health data is not a minor website feature when the surrounding workflow is weak.
## **The Quick Decision: Practice Intake Tool Or Healthcare SaaS Infrastructure?**
Most buyers searching for a HIPAA-compliant form builder fall into one of two groups.
The first group needs a faster way to collect patient information. A clinic, therapy practice, dental office, or small healthcare provider may need intake forms, consent forms, appointment requests, file uploads, and e-signatures. A hosted HIPAA-enabled form builder can work well here if the vendor signs the right BAA, the account is configured correctly, and the workflow keeps PHI inside approved systems.
The second group is building a healthcare product. That buyer does not only need a form. It needs form capability inside an application.
For healthcare SaaS teams, forms may power onboarding, eligibility, clinical screening, referrals, patient-reported outcomes, provider workflows, prior authorization, records updates, care-team routing, and follow-up check-ins. A [third-party digital health article from Light-it](https://lightit.io/blog/5-ways-to-apply-hipaa-compliant-form-builders-to-your-digital-health-product/) describes HIPAA-compliant forms as part of ongoing product workflows such as patient intake, assessments, appointment scheduling, regular check-ins, and feedback surveys. That is a different problem than publishing a secure contact form on a website.
The distinction is simple:
**Buyer situation****Better fit**One practice needs intake forms and patient packetsHosted HIPAA-enabled form builderA healthcare SaaS product needs forms inside its appEmbedded form infrastructureA team needs patient data routed to internal systemsAPI-first form platformA team must keep PHI inside its own environmentSelf-hosted form infrastructureA product needs tenant-specific forms and permissionsWhite-label or multi-tenant form infrastructureThe mistake is treating these as the same purchase.
## **The Requirements Checklist**
Before comparing logos, healthcare teams should define the control boundary.
### **BAA Scope**
A BAA is not a marketing badge. It establishes the permitted uses and disclosures of PHI, requires appropriate safeguards, covers reporting obligations, addresses subcontractors, and should align with the actual workflow. [HHS sample BAA guidance](https://www.hhs.gov/hipaa/for-professionals/covered-entities/sample-business-associate-agreement-provisions/index.html) says these contracts should clarify and limit how a business associate may use or disclose PHI and require safeguards to prevent unauthorized use or disclosure.
The practical question is: which vendor is creating, receiving, maintaining, or transmitting ePHI?
If the form builder stores submissions, handles uploaded files, sends notifications containing PHI, or passes data to another system, the BAA and subcontractor chain need to match that reality.
### **Where PHI Is Stored**
Data location is not a minor implementation detail. It determines who administers the database, where backups live, which security controls apply, who can access logs, what happens at termination, and how incident response works.
For a simple hosted form workflow, vendor-managed storage may be acceptable. For a healthcare SaaS product, the team may need submissions in its own database, cloud account, region, network, or compliant infrastructure boundary.
This is one reason self-hosting matters. It does not make an application HIPAA compliant by itself. It gives the customer more control over where PHI lives and which controls surround it.
### **Access Control And Identity**
HIPAA-governed forms usually need more than a shared admin login.
Ask who can view submissions, edit forms, export data, upload files, change permissions, configure webhooks, or see audit logs. Then map those permissions to real roles: patient, provider, customer admin, internal support, implementation partner, compliance reviewer, and developer.
For SaaS products, this gets harder. One customer's admin should not see another customer's submissions. A support user may need temporary access. A provider may need access to only assigned patients. A form builder may need schema-editing rights without PHI access.
The form system has to support those boundaries instead of forcing the application to patch them later.
### **Audit Logs And Revision History**
The highest-risk part of a healthcare form often starts after submission.
What changed? Who changed it? Which version of the form captured the original data? Did a webhook run? Did an email action send? Did the submitted value get edited later? Can the team reconstruct the record if an auditor asks?
Generic form builders often focus on collection. Healthcare SaaS teams need evidence.
Form.io's Security Module is built around this kind of evidence. Its [secure forms and compliance readiness documentation](https://form.io/features/secure-forms-compliance-readiness/) describes advanced audit logging, action logs, form revisions, submission revision logs, submission collections, and container security scanning. The important distinction is that form revisions track changes to the form schema, while submission revisions track changes to submitted data.
That distinction sounds small. It is not.
A historical submission is not only the answers a patient gave. It is the form version, validation rules, field labels, conditional logic, workflow context, and submission state that governed the data at the time.
### **APIs And Integration Control**
Healthcare forms rarely stay inside the form tool.
An intake form may need to create a patient profile, update a resource, trigger a referral workflow, generate a PDF, route a task to a care team, or feed an internal dashboard. A screening form may need validation, conditional follow-up, file uploads, and downstream review. A provider form may need to connect with legacy systems or internal case management.
If the form builder only gives you CSV exports or a fragile integration layer, the application team inherits the risk.
Form.io's [concepts documentation](https://help.form.io/start/form.io-concepts) explains that as a form is built, Form.io constructs the JSON schema and defines a REST API endpoint. Submissions are API-accessible, owned by users for permission enforcement, portable, and revision-trackable with the Security & Compliance package. That is the infrastructure argument: the form definition, submitted data, API, and access model belong in the same system.
### **Tenant And Customer Boundaries**
Healthcare SaaS teams often serve many customers from one product. That means the form layer may need tenant-aware configuration, customer-specific forms, white-labeled experiences, separate roles, different workflows, and different data retention expectations.
This is where "HIPAA form builder" searches become too small. The issue is not only whether one form can collect PHI. It is whether a platform can support repeated, governed form workflows across customers without collapsing into one-off custom code.
## **Common HIPAA Form Builder Categories**
The market is easier to understand when you separate platform types.
**Category****Best fit****Strength****Gap**Hosted HIPAA form builderPractices and clinics that need intake, consent, and website formsFast setup, templates, vendor-managed hostingLimited architecture and data-boundary controlHealthcare intake platformPatient intake, appointment, and engagement workflowsHealthcare-specific UX and workflowsMay be too narrow for broader SaaS infrastructureEnterprise form/workflow platformLarger teams with governed workflowsMore controls and integrationsOften still vendor-hosted or workflow-product centeredSelf-hosted form infrastructureHealthcare SaaS and regulated product teamsDeployment control, APIs, data ownership, auditabilityRequires technical ownershipCustom buildUnique workflows with no acceptable platform fitMaximum controlExpensive to build, secure, test, document, and maintainThere is no universal winner. There is only the right layer for the job.
## **Where Form.io Fits For Healthcare SaaS**
Form.io is not the lightest way to publish a HIPAA-ready website form. It is a stronger fit when forms are part of healthcare application infrastructure.
That usually means the team needs some combination of embedded forms, generated APIs, custom roles, submission storage, workflow actions, form revisions, submission revisions, audit logs, file/PDF handling, and customer-controlled deployment.
Form.io's [self-hosted forms documentation](https://form.io/features/self-hosted-forms-for-enterprise/) says the platform can run in AWS, Azure, Google Cloud, private data centers, or Docker-based environments, with submission data stored in the customer's MongoDB instance and security boundary. The same page is careful about the boundary: self-hosted deployment enables compliance control, but the customer still needs proper access controls, encryption, audit logging, network security, and the rest of the compliance program.
That honesty is useful.
Healthcare SaaS teams do not need another vendor promising that complexity disappears. They need a platform that gives them the right control surfaces: forms, resources, generated APIs, submissions, actions, [roles and permissions](https://form.io/features/forms-for-teams/), revisions, and audit evidence.
Form.io's [healthcare forms page](https://form.io/industries/healthcare-forms/) points to use cases such as patient registration, records, appointments, routing inquiries, notifications, [conditional logic](https://form.io/features/form-conditional-logic-form-validation/), mobile-responsive forms, offline mode, form revisions, autosave, accessibility, and the Security Module. The better strategic reading is not "Form.io makes healthcare simple." It is that Form.io gives healthcare teams a form infrastructure layer they can govern inside their own architecture.
The [CHESS Health case study](https://form.io/how-a-flexible-form-solution-helped-get-to-market-in-6-weeks-instead-of-6-months/) is a useful proof point. Form.io describes a healthcare technology company managing EMRs, EHRs, interoperability, strict security and compliance requirements, sensitive data in its own environment, legacy integrations, and the need to get to market faster. The case headline says CHESS Health got to market in 6 weeks instead of 6 months. That is the category fit: not a simple intake form, but a healthcare product workflow that needed speed without giving up architectural control.
There is also a buyer sentiment signal from [Trustpilot](https://www.trustpilot.com/review/form.io), where one reviewer called Form.io "really great software, both for integration and standalone." The quote is broad, but it matches the central buying reason for this article: the form layer has to work as part of a larger system.
## **When A Hosted HIPAA Form Builder Is Enough**
A hosted HIPAA form builder may be the better answer when the workflow is simple and the organization accepts the vendor-managed model.
That can include:
- Patient intake forms for one practice
- Consent forms
- Appointment request forms
- Simple file uploads
- Basic medical history forms
- Feedback surveys
- Website-embedded forms
- Staff-created forms with limited integration needs
In these cases, speed matters. Templates matter. A no-code builder matters. A signed BAA, encrypted submissions, access controls, and a clean admin experience may be enough.
The important word is "enough."
If a workflow starts simple but will later need custom identity, tenant-specific configuration, deeper APIs, application-owned submission records, role-aware workflows, and evidence-grade revision history, the cheapest or fastest hosted option can become expensive later.
## **When Healthcare SaaS Teams Should Avoid Standalone Form Tools**
Standalone form tools become risky when the form is part of the product's core workflow.
Watch for these signals:
- PHI must remain inside your own cloud, database, or approved deployment boundary.
- Forms need to be embedded directly into your product experience.
- Customers need their own form configuration, roles, branding, or workflows.
- Submissions need to become application records, not just entries in a vendor dashboard.
- The product needs generated APIs, webhooks, resources, permissions, and workflow actions.
- Historical records need to resolve to the form version that captured them.
- Support, operations, providers, and customer admins need different access rules.
- Exports, notifications, analytics, and AI tools must not create uncontrolled PHI copies.
These are not edge cases for healthcare SaaS. They are ordinary product requirements.
The wrong tool can still pass the first demo. The problem appears later, when the team needs to prove who accessed PHI, why a submission changed, whether a field existed at the time of capture, where a file was stored, or why one tenant's workflow affected another.
That is the moment when "just use a form builder" stops being a plan.
## **Evaluation Table**
##  **Evaluation question****Why it matters****What to look for**Will the vendor sign the right BAA?PHI handling needs a contractual boundaryBAA scope, subcontractors, permitted uses, breach/security incident termsWhere is PHI stored?Data location shapes risk and responsibilityCustomer-controlled database, approved region, backup and termination termsCan access map to real roles?Healthcare workflows are role-sensitiveRBAC, SSO/MFA options, admin separation, own-vs-all submission accessAre form changes versioned?Historical records need contextForm revisions, schema history, promotion/stage controlsAre submission changes versioned?Modified PHI needs accountabilitySubmission revisions, who/when/what logs, revert or history viewsAre actions auditable?Integrations are common failure pointsAction logs for emails, webhooks, resource saves, and workflow stepsDoes the platform generate APIs?SaaS products need system integrationREST APIs, submission endpoints, resources, webhooksCan forms be embedded and white-labeled?Healthcare SaaS forms live inside productsRenderer libraries, embedded builder, brand controlCan the platform be self-hosted?Some teams need customer-controlled infrastructureDocker, cloud/on-prem deployment, environment variables, customer databaseDoes the vendor overclaim compliance?Overclaiming creates riskClear shared-responsibility language and technical-control boundaries**What Not To Assume**
Do not assume a healthcare template makes a workflow compliant.
Do not assume encryption solves the whole problem. HHS cloud guidance is clear that encryption alone does not remove business associate obligations when a provider maintains ePHI.
Do not assume a BAA covers every downstream action. If submissions are emailed to the wrong inbox, copied into a non-approved CRM, exported to spreadsheets, or passed through an unreviewed automation, the form builder's feature list is not the whole risk picture.
Do not assume self-hosting removes responsibility. It increases control. It also increases the customer's obligation to configure and operate the environment correctly.
Do not assume a standalone form tool will scale into product infrastructure. Sometimes it will. Often it will not.
## **FAQ**
### **Is A Form Builder HIPAA Compliant If It Signs A BAA?**
No. A BAA is necessary in many PHI workflows, but it is not the whole compliance answer. The organization still needs appropriate safeguards, policies, configuration, access control, risk analysis, monitoring, and incident-response processes.
### **Can Healthcare Teams Use Google Forms For PHI?**
Do not use a general form workflow for PHI unless the entire vendor relationship, configuration, storage model, access controls, and BAA requirements are approved for that use. For most healthcare SaaS teams, the safer default is to use a platform designed for regulated data workflows.
### **What Features Should HIPAA-Compliant Forms Have?**
At minimum, evaluate BAA support, encryption, access control, audit logs, secure storage, user management, file handling, retention/deletion, and integration behavior. For healthcare SaaS, also evaluate APIs, embedding, tenant boundaries, revision history, and deployment control.
### **Do Healthcare SaaS Teams Need Self-Hosted Forms?**
Not always. But self-hosting becomes important when PHI must stay inside the customer's environment, when the form layer needs to align with internal security controls, or when product architecture requires direct control over database, network, logging, and deployment boundaries.
### **Does Self-Hosting Make A Form Platform HIPAA Compliant?**
No. Self-hosting enables more control over infrastructure and data boundaries. Compliance still depends on how the environment is configured, monitored, documented, and governed.
### **Can Form.io Be Used For HIPAA Workflows?**
Form.io provides healthcare-oriented form infrastructure and security/compliance capabilities that can support HIPAA-governed workflows in customer-controlled environments. The customer's organization remains responsible for its HIPAA compliance program, configuration, policies, and deployment controls.
### **Does Form.io Certify My Application As HIPAA Compliant?**
No. Form.io's own compliance-readiness language is clear that the platform provides technical capabilities that support regulated deployments; it does not certify a customer's application or organization for HIPAA.
### **Why Do Audit Logs Matter For HIPAA Forms?**
Audit logs help answer who accessed or changed data, when it happened, what entity was affected, and which workflow action ran. For healthcare SaaS teams, that evidence can matter as much as the original form submission.
### **Should PHI Be Stored In A Third-Party Form Vendor Account?**
It depends on the workflow, BAA, risk analysis, and organizational policy. For simple intake forms, vendor-managed storage may be acceptable. For healthcare SaaS platforms, application-owned or customer-controlled storage may be a better fit.
### **What Should I Ask Before Collecting PHI Through An Online Form?**
Ask where PHI is stored, who can access it, which BAA covers it, whether uploads and notifications are protected, how audit logs work, how long data is retained, how submissions are deleted or exported, and what happens when the form changes.
## **Build HIPAA-Governed Form Infrastructure With Form.io**
If your healthcare product only needs a simple intake form, choose the fastest HIPAA-enabled tool that satisfies your compliance review.
If your forms define product workflows, API contracts, submissions, permissions, audit evidence, and data boundaries, choose infrastructure that respects that complexity from the start.
[Try Form.io for healthcare SaaS form infrastructure](/try-formio-for-free/).
# When Your Forms Don’t Match Your Design System Part 2
[  ](https://form.io/when-your-forms-dont-match-your-design-system-part-2/)In [Part 1](/when-your-forms-dont-match-your-design-system-part-1/), we established the design system compliance problem. Now let’s solve it for 98% of cases using class overrides alone.
Class names let you replace the CSS classes on your form components without touching the HTML structure. This is faster, less fragile, and easier to maintain than template-level customization. Start with this method in every case, and only reach for template overrides if you can’t accomplish your design goals with classes alone.
### **What Is the Class Names Method?**
Form.io templates are built from components, and each component has named parts: `input`, `label`, `button`, and so on. Class names let you define exactly which CSS classes apply to each part. The HTML structure stays the same; only the classes change. Because you’re working at the class level, this approach works with any CSS framework, whether you’re using Tailwind, Bootstrap, or something entirely your own, so you’re never locked into a particular toolchain.
### **Before You Start**
This guide assumes you already have a working Form.io application using the `@formio/js` renderer. To add the Standard Template, install it from npm:
```
npm install @formio/standard-template
```
**Note:** The Standard Template is a new and actively evolving package. Check the[ GitHub repository](https://github.com/formio/standard-template) for the latest version and API details before adopting it in production.
### **The Structure**
Here’s what a theme definition looks like:
```
import { standardTemplate } from '@formio/standard-template';
import type { TemplateClasses } from '@formio/standard-template';
const myTheme: TemplateClasses = {
// Component definitions go here
};
Formio.use(standardTemplate('my-custom-theme', myTheme));
```
Each component you want to customize gets an entry, and each entry defines classes for different contexts (`form` mode versus `html` display mode) and for the different parts of that component. Once you’ve seen one component defined, the rest follow the same shape.
### **Building a Complete Theme**
Let’s build a complete theme from scratch using Tailwind classes, transforming a basic contact form to match a modern design system. We’ll add one piece at a time.
#### **Our goal:**
- Minimal, underline-style input fields with an accent focus state
- Small, uppercase labels in the accent color
- A gradient pill button with hover effects
- Comfortable spacing between fields
#### **Step 1: Input Fields**
```
const myTheme: TemplateClasses = {
input: {
form: {
input: [
'block',
'w-full',
'px-0',
'py-2.5',
'text-base',
'text-slate-800',
'bg-transparent',
'border-0',
'border-b-2',
'border-slate-300',
'focus:outline-none',
'focus:border-violet-600',
'placeholder:text-slate-400',
'transition-colors',
'duration-200'
]
}
}
};
```
Pause on the shape of that definition, because every other component follows it:
- `input` (the outer key) is the component type: text fields, email fields, and so on
- `form` is the context (edit mode; there’s also html for read-only display)
- `input` (the inner key) is the specific element within that component
- The array contains all the Tailwind classes applied to that element
The result is an underline-style input: no box, no background, just a bottom border that shifts to violet when the field has focus.
#### **Step 2: Add Labels**
```
const myTheme: TemplateClasses = {
label: {
form: {
label: [
'block',
'text-xs',
'font-bold',
'uppercase',
'tracking-wider',
'text-violet-600',
'mb-2'
]
}
},
input: {
// ...input classes from Step 1
}
};
```
Labels now have their own styling: small, bold, uppercase, with letter-spacing and the accent color picking up the same violet as the input focus state. This sits alongside the input definition rather than inside it, because labels and inputs are independent components.
#### **Step 3: Add Buttons**
```
const myTheme: TemplateClasses = {
button: {
form: {
button: [
'w-full',
'px-6',
'py-3',
'text-sm',
'font-bold',
'uppercase',
'tracking-wider',
'text-white',
'bg-gradient-to-br',
'from-violet-600',
'to-violet-700',
'rounded-full',
'shadow-lg',
'shadow-violet-600/30',
'cursor-pointer',
'transition',
'duration-150',
'hover:opacity-90',
'hover:-translate-y-px',
'disabled:opacity-50',
'disabled:cursor-not-allowed'
]
}
},
label: {
// ...label classes from Step 2
},
input: {
// ...input classes from Step 1
}
};
```
The button becomes a full-width gradient pill: violet gradient background, a soft glow shadow, a subtle lift on hover, and proper disabled states. Notice the pattern: each component is self-contained, and adding a new one never disturbs the others.
#### **Step 4: Add Field Spacing**
```
const myTheme: TemplateClasses = {
component: {
form: {
component: [
'mb-6'
]
}
},
button: {
// ...button classes from Step 3
},
label: {
// ...label classes from Step 2
},
input: {
// ...input classes from Step 1
}
};
```
The `component` entry wraps every field in the form, so a single `mb-6` here gives each field comfortable breathing room below it. That’s the last piece of the theme.
### **The Complete Theme**
Here’s the full theme definition:
```
import { standardTemplate } from '@formio/standard-template';
import type { TemplateClasses } from '@formio/standard-template';
const myTheme: TemplateClasses = {
label: {
form: {
label: [
'block',
'text-xs',
'font-bold',
'uppercase',
'tracking-wider',
'text-violet-600',
'mb-2'
]
}
},
input: {
form: {
input: [
'block',
'w-full',
'px-0',
'py-2.5',
'text-base',
'text-slate-800',
'bg-transparent',
'border-0',
'border-b-2',
'border-slate-300',
'focus:outline-none',
'focus:border-violet-600',
'placeholder:text-slate-400',
'transition-colors',
'duration-200'
]
}
},
button: {
form: {
button: [
'w-full',
'px-6',
'py-3',
'text-sm',
'font-bold',
'uppercase',
'tracking-wider',
'text-white',
'bg-gradient-to-br',
'from-violet-600',
'to-violet-700',
'rounded-full',
'shadow-lg',
'shadow-violet-600/30',
'cursor-pointer',
'transition',
'duration-150',
'hover:opacity-90',
'hover:-translate-y-px',
'disabled:opacity-50',
'disabled:cursor-not-allowed'
]
}
},
component: {
form: {
component: [
'mb-6'
]
}
}
};
// Apply it globally
Formio.use(standardTemplate('my-custom-theme', myTheme));
```
Apply this once when your application initializes, and every form in your application will use the styling.
### **Before:**
### **After:**
### **Next Steps**
You now have everything you need to style Form.io forms to match your design system using class overrides. From here, the work is mostly a matter of breadth. The same pattern extends to every other component:
- **Radio buttons and checkboxes:** `radio`, `checkbox`
- **Select dropdowns:** `select`
- **Text areas:** `textarea`
- **Error and help text:** `errorLabel`, `helpBlock`
- **Field containers:** `component`, `field`
In every case you define classes for the component type and its parts, exactly as we did above. A textarea, for example, would take the same underline treatment as the inputs, plus `resize-y` and a `min-h-20` so users can expand it comfortably.
As your themes grow, it helps to pull them into their own modules so you can reuse them across projects:
```
// themes/tailwind-modern.ts
export const tailwindModern: TemplateClasses = {
// Your theme definition
};
// app.ts
import { tailwindModern } from './themes/tailwind-modern';
Formio.use(standardTemplate('tailwind-modern', tailwindModern));
```
Do this consistently and you end up with a library of themes you can share across your organization and maintain as part of your design system.
### **Additional Resources**
- [**Standard Template Playground**](https://apps.form.io/standard-template/): Interactive examples of different themes and styling approaches
- [**GitHub Repository**](https://github.com/formio/standard-template): Inspect the code and learn more about what you can target with CSS
# When Your Forms Don’t Match Your Design System Part 1
[  ](https://form.io/when-your-forms-dont-match-your-design-system-part-1/)Your design team just shipped an updated component library. New focus rings, refined spacing, updated color tokens. Engineering updates the React components, the dashboard layouts, and the navigation. Everything looks cohesive.
Then someone opens a form.
Form.io has been powering your dynamic forms beautifully. It handles complex conditional logic, multi-step workflows, and validation rules that would take many engineering hours to build from scratch. The form builder itself is invaluable: non-technical team members can create and modify forms without engineering involvement.
But visually, those forms still use the Bootstrap classes and markup they shipped with. Now there’s a mismatch. The rest of your application has evolved, and the forms haven’t.
This isn’t a Form.io problem. It’s a sign of success. Your product has matured to the point where your design system requirements go beyond any form builder’s defaults.
## **Why This Happens**
Form.io ships with professional, well-designed templates based on Bootstrap, and that’s exactly what you want when you’re getting started. These defaults handle everything: inputs, buttons, radio groups, validation messages, error states. They’re accessible, well-tested, and work across browsers. For many teams, they’re perfect and require no customization at all.
But as your product matures, specific visual requirements tend to surface. Maybe your design system has standardized on Tailwind rather than Bootstrap. Maybe you’ve built up custom brand colors, spacing scales, and typography, or your design team has defined particular interaction patterns. And at some point, “close enough” stops being good enough. You need the forms to match the rest of your application pixel-for-pixel. That’s the moment you need to customize Form.io’s visual layer while keeping everything else that makes it valuable.
## **What Teams Try Today**
Before Standard Template When teams hit this point in their product evolution, they usually reach for one of four approaches. Each comes with real trade-offs.
1. **Convince design to accept the form builder’s defaults.** Sometimes that works for internal tools, but for a customer-facing product with established brand guidelines, it’s usually a non-starter.
2. **Write custom CSS that overrides the defaults.** This works until it doesn’t: you can change colors and spacing, but you can’t restructure HTML with CSS, future updates might break your overrides, and maintenance gets expensive.
3. **Rebuild the component templates from the ground up.** You could use the default Form.io Bootstrap 5 template as a guide for writing your own. That gives you complete control, but now you’re maintaining even more code. It’s technically possible, but operationally expensive.
4. **Build a custom form system from scratch.** The most drastic option. Do this and you throw away Form.io’s conditional logic, validation rules, and visual builder, everything that made it valuable in the first place. It’s rarely justified. You chose Form.io for a reason.
What most teams actually want is something none of those quite delivers: keep Form.io’s powerful form logic and builder interface, but adapt the visual layer to match their design system.
## **The Standard Template**
After Standard Template The Standard Template introduces a customization system that works *with* Form.io’s existing architecture instead of against it. Its core mechanism is **Style Map**: you replace the CSS classes on existing HTML elements without changing the underlying structure. It works with any CSS framework, whether that’s Tailwind, Bootstrap, or a fully custom design system, and it’s fast to implement and easy to maintain. With the Standard Template, you’re configuring Form.io’s rendering layer, not fighting it.
This approach makes sense when you have an established design system with specific requirements, several forms that need to stay visually consistent, and a product where design system compliance matters, and you want all of that without giving up Form.io’s form logic and builder.
Just as important is knowing when you *don’t* need it. If Form.io’s default Bootstrap theme already works for you, if you only have a form or two, if your forms are internal tools where strict visual consistency isn’t a concern, or if you’re just getting started and should be optimizing for speed over pixel-perfection, then reaching for customization only creates work. Form.io’s defaults are professionally designed and serve most use cases well. Don’t make work for yourself unless you have a clear requirement.
## **Wrapping Up**
Adopting the Standard Template gives you the best of both worlds: Form.io’s powerful form capabilities with your design system’s visual consistency. Once it’s in place, your forms match your design system’s colors, spacing, and typography, while non-technical users keep building and modifying forms in the Form.io builder exactly as before. All of Form.io’s logic, validation, conditionals, and calculations keep working, your maintenance burden shrinks to a set of class definitions and the occasional template override, and new Form.io features and updates apply without conflicts.
The Standard Template is now available with the [release of Form.io 9.8.0](/release-notes/formio-enterprise-9-8-0-and-pdf-server-5-14-0/).
In [Part 2](/when-your-forms-dont-match-your-design-system-part-2/), I’ll show you how class overrides work with concrete examples. You’ll build a complete Tailwind theme from scratch without touching a single line of HTML.
# MCP Server List: What Regulated Enterprise Developers Should Actually Use
[  ](https://form.io/mcp-server-list-regulated-enterprise-developers/)You can find an MCP server list in seconds. That is not the hard part. The hard part is deciding which servers deserve access to your source code, cloud accounts, tickets, documentation, test environments, and production-adjacent business data.
For regulated enterprise developers, the question is not "which MCP servers are popular?" It is "which MCP servers can we trust inside a governed workflow?"
## **The quick answer**
Start with the official MCP Registry, then filter by control surface.
For regulated enterprise development, the strongest shortlist usually includes:
**MCP surface****Best fit****Enterprise question**Official MCP RegistryDiscovery and metadataIs this server officially published, namespace-authenticated, and still current?GitHub MCP ServerRepos, pull requests, issues, Actions, security findingsCan the agent work inside the same SDLC boundary developers already use?GitLab MCP ServerGitLab.com, self-managed GitLab, Duo workflowsDoes it respect the deployment model and permissions your GitLab instance already enforces?AWS MCP ServersCloud architecture, docs, API operationsAre IAM, least privilege, CloudWatch metrics, and CloudTrail evidence understood before use?Azure MCP ServerAzure resources, Entra ID-backed cloud workflowsDoes the server inherit the identity and guardrail model your Azure teams already use?Atlassian Rovo MCP ServerJira, Confluence, CompassDoes the agent see only what the user has permission to see?Playwright MCPBrowser automation and UI testingAre unsafe direct-code tools disabled unless the client is trusted?Sentry MCPDebugging and observabilityCan the agent inspect errors without turning observability into an unbounded data pipe?Docker MCP toolingLocal gateway, catalog, containerized MCP operationsCan servers be packaged and scoped consistently across teams?Form.io MCP ServerForms, resources, actions, APIs, and schema-driven application infrastructureCan the agent build against governed form and API patterns instead of improvising them?That is the useful MCP server list for regulated teams: not a popularity contest, but a map of which systems an agent can touch, how it authenticates, what it can change, and where the audit evidence lands.
## **What an MCP server list can and cannot tell you**
MCP, or Model Context Protocol, gives AI clients a standard way to connect to external tools and data. An MCP server is the bridge between the agent and a system such as GitHub, AWS, Jira, a browser, a database, or a domain platform such as Form.io.
An MCP server list helps with discovery. It does not prove that a server belongs in your enterprise agent environment.
That distinction matters because the official MCP Registry itself is a metadata layer. The registry documentation describes it as the official centralized repository for publicly accessible MCP server metadata, while also noting that it is still in preview and does not support private servers. It supports discovery, namespace authentication, installation metadata, and REST API access. It is not a substitute for enterprise security review.
That is the first mistake many teams make. They treat discovery as approval.
For a developer testing locally, that may be tolerable. For a regulated team, it is a weak control. A server that reads public docs is not in the same risk category as a server that can open pull requests, read customer tickets, execute cloud API calls, or inspect production error traces.
The list is the beginning. The trust decision comes after.
## **The regulated-enterprise filter**
Before you add a server to Claude Code, Cursor, VS Code, Windsurf, or another MCP client, ask six questions.
### **Who maintains it?**
Prefer official or vendor-maintained servers when the system is critical. A community server can be useful, but enterprise teams need a clear owner, release trail, issue history, and support path.
This is why GitHub, GitLab, AWS, Azure, Atlassian, Playwright, Docker, Sentry, and Form.io deserve separate treatment from generic directories. They are not just "available MCP servers." They are maintained by, or directly tied to, the systems they expose.
### **What identity model does it inherit?**
A lower-risk server is usually one that inherits the identity and permission model already governing the system.
[GitLab's MCP docs](https://docs.gitlab.com/user/gitlab_duo/model_context_protocol/mcp_server/), for example, describe OAuth registration and HTTP transport options, and they support GitLab.com, Self-Managed, and Dedicated environments. [Atlassian's remote MCP server](https://support.atlassian.com/atlassian-rovo-mcp-server/docs/getting-started-with-the-atlassian-remote-mcp-server/) uses OAuth 2.1 and respects Jira, Confluence, and Compass permissions. [Azure MCP Server](https://learn.microsoft.com/en-us/azure/developer/azure-mcp-server/overview) uses Microsoft Entra ID through Azure Identity.
That matters more than convenience. If the server works around identity, it works around governance.
### **What can it mutate?**
Read-only access is one risk. Write access is another. Production mutation is another.
A server that searches docs can still leak context. A server that changes infrastructure, submits forms, opens tickets, or modifies code can create operational state. Treat those differently.
The [MCP security guidance](https://modelcontextprotocol.io/specification/2025-06-18/basic/security_best_practices) calls out risks such as confused deputy behavior, token passthrough, SSRF, session hijacking, local server compromise, and the need to minimize scopes. Those are not abstract security concerns. They are what happens when an agent can act through a server whose authority is broader than the user's intent.
### **Where are logs written?**
Regulated teams need evidence. If an agent uses a server to retrieve context, change an issue, call an API, or update a form definition, the team needs to know where that action is logged.
AWS is a useful benchmark here. AWS announced the [AWS MCP Server general availability](https://aws.amazon.com/about-aws/whats-new/2026/05/aws-mcp-server/) on May 6, 2026, describing IAM-based guardrails, Amazon CloudWatch metrics, and AWS CloudTrail logging. That does not make every AWS MCP use case automatically approved, but it does give enterprise teams a familiar evidence model.
### **What data crosses the boundary?**
Some MCP servers expose local files. Some expose SaaS data. Some connect to cloud accounts. Some connect to internal systems. Some domain-specific servers, such as the Form.io AI toolset, connect to a customer's self-hosted environment.
The boundary is the point.
Form.io describes its MCP Server as connecting to a customer's self-hosted Form.io deployment so AI coding agents can work with forms, resources, actions, and APIs without moving that governed surface outside the enterprise boundary. That is a different posture from a generic public directory listing.
### **Is this build-time or runtime?**
Do not collapse every agentic tool into one bucket.
MCP servers are usually build-time or operator-time connectors. They help coding agents and assistants read context, call tools, scaffold work, or interact with systems.
Runtime agent governance is different. Form.io's [Universal Agent Gateway](https://form.io/uag/) belongs in that adjacent category. UAG is not the same thing as the Form.io MCP Server. The MCP Server helps AI coding agents build against Form.io patterns. UAG governs production agent workflows at runtime.
Regulated teams need both concepts, but they should not confuse them.
## **The MCP servers worth knowing**
### **1. Official MCP Registry**
Use the official registry as the starting point, not the finish line.
The [official registry](https://modelcontextprotocol.io/registry/about) is valuable because it gives teams a canonical discovery surface for public MCP servers. It supports server metadata, namespace authentication, REST API discovery, package references, and standardized installation information.
For enterprise teams, the important detail is the limit. The registry is public. It is still in preview. It is not where private enterprise servers should live. It also does not remove the need to review code, packages, transport, authentication, scopes, and data handling.
Use it to find servers. Do not use it as your approval workflow.
### **2. GitHub MCP Server**
The [GitHub MCP Server](https://github.com/github/github-mcp-server) belongs in many enterprise developer shortlists because GitHub is where source code, issues, pull requests, Actions, security findings, and review state already live for many teams.
That makes it powerful. It also makes it sensitive.
A coding agent that can inspect a repo, summarize issues, open a pull request, or reason over security findings is operating close to the SDLC evidence trail. That can be a good thing when the team scopes access properly. It can be a problem when every repo is available by default.
Use GitHub MCP when the agent needs to work inside the same development boundary developers already use. Scope it to the repositories and operations needed for the task.
### **3. GitLab MCP Server**
GitLab deserves its own place because many regulated organizations use self-managed GitLab or GitLab Dedicated rather than a purely public SaaS setup.
The official GitLab MCP documentation supports GitLab.com, Self-Managed, and Dedicated environments. It also warns that users are responsible for guarding against prompt injection and should use MCP tools only with trusted GitLab objects.
That warning is useful. It says the quiet part plainly: permission inheritance is not the whole security model. If an agent reads hostile issue content, merge request comments, or documentation, those objects can become part of the instruction stream.
Use GitLab MCP where GitLab is already the system of record for code and planning, but pair it with prompt-injection hygiene and object-scope limits.
### **4. AWS MCP Servers**
AWS MCP belongs in the list because cloud infrastructure is where agent mistakes become expensive.
AWS has multiple MCP surfaces, including [AWS Labs servers](https://github.com/awslabs/mcp/) and the generally available [AWS MCP Server](https://aws.amazon.com/blogs/aws/the-aws-mcp-server-is-now-generally-available/). The managed server is especially relevant to enterprise teams because AWS describes IAM guardrails, SigV4-style authenticated access through the Agent Toolkit, CloudWatch metrics, CloudTrail logging, AWS Knowledge MCP, AWS API MCP capabilities, and access to more than 15,000 AWS APIs.
That is exactly why the risk bar is high.
An agent that can ask AWS docs questions is one thing. An agent that can call AWS APIs is another. The minimum viable control is least-privilege IAM, environment separation, and CloudTrail visibility. Without those, cloud MCP access is too broad for regulated workflows.
Use AWS MCP for documentation, architecture support, and tightly scoped operations. Do not give a general coding agent broad cloud authority just because the server exists.
### **5. Azure MCP Server**
Azure MCP is important for teams whose cloud control plane already sits under Microsoft identity.
Microsoft's Azure MCP Server documentation describes integration with Azure resources, developer tools such as VS Code and GitHub Copilot, and authentication through Azure Identity. For enterprise teams, the key phrase is not "Azure resources." It is identity inheritance.
If the server can operate through Entra ID-backed access patterns and the same Azure permissions teams already govern, it fits better than a standalone connector with its own unmanaged secrets.
Use Azure MCP where the team already has mature Azure role design, environment separation, and resource governance.
### **6. Atlassian Rovo MCP Server**
Jira and Confluence are where a lot of enterprise work actually lives: requirements, tickets, runbooks, decisions, incident notes, acceptance criteria, and stakeholder context.
Atlassian's Rovo MCP Server documentation describes OAuth 2.1, support for Jira, Confluence, and Compass, permission inheritance, and IP allowlisting behavior in Atlassian Cloud.
That makes it a strong context server, especially for coding agents that need product intent or implementation history.
The risk is also obvious. Tickets and docs often contain sensitive business context, customer details, credentials copied where they should not be, and architectural notes. Permission inheritance helps, but it does not classify the content for you.
Use Atlassian MCP for project and documentation context, with clear limits on what spaces, projects, and user scopes are exposed.
### **7. Playwright MCP**
Playwright MCP is one of the most useful developer servers because it gives agents a structured way to interact with web pages and browser workflows.
The [Playwright MCP docs](https://playwright.dev/docs/getting-started-mcp) describe use of accessibility snapshots rather than screenshots or pixel-based interaction. That is the right foundation for repeatable browser automation.
But the same documentation also warns that direct Playwright code execution is effectively remote code execution and should only be enabled for trusted MCP clients.
That is the regulated-enterprise lesson in miniature. A tool can be both useful and unsafe if enabled in the wrong mode.
Use Playwright MCP for testing, QA, browser workflows, and UI validation. Disable unsafe direct-code tools unless the client and execution environment are trusted.
### **8. Sentry MCP**
The [Sentry MCP Server](https://github.com/getsentry/sentry-mcp) belongs in the operational layer. It helps agents inspect errors, traces, issues, and debugging context.
That can compress the time between "the build failed" and "the actual production error is understood." It also exposes operational data that may include request context, user metadata, stack traces, and environment details.
For regulated teams, observability MCP should be scoped like production support access, not like a convenience plugin.
Use Sentry MCP when the agent is doing debugging or remediation work, and restrict the projects, environments, and data fields that should be visible.
### **9. Docker MCP tooling**
[Docker's MCP tooling](https://docs.docker.com/reference/cli/docker/mcp/) is less about one business system and more about packaging, gateway behavior, and local developer operations.
That makes it useful for standardization. Enterprise teams do not want every developer hand-rolling MCP server installation and transport decisions in a different local config file.
Use Docker MCP tooling to make server setup more repeatable, especially when you need a catalog or gateway-style operating model across teams.
### **10. Form.io MCP Server**
Form.io belongs in this MCP server list because regulated applications often begin at the data-capture layer: forms, resources, validation rules, submission records, workflow actions, APIs, permissions, revisions, and audit evidence.
That is the layer where generic coding agents can create drift fastest.
One team builds a React form. Another builds a different submission API. A third adds an agent workflow. Each piece works. None of them share the same governance contract.
The [Form.io AI toolset](https://form.io/ai/) exists to push the agent toward the governed path at build time. The Form.io MCP Server connects AI coding agents to a customer's self-hosted Form.io deployment so they can read, create, and scaffold forms, resources, actions, and APIs from the same platform primitives. Form.io Skills guide the agent toward platform-specific patterns. The Agentic Coding Plugin brings that MCP Server and skill library into the developer's coding environment.
That makes Form.io different from a generic connector.
It is not just giving an agent another data source. It is giving the agent a governed application primitive: schemas that can produce interfaces, APIs, validation behavior, submissions, permissions, and workflow hooks from the same definition.
For teams using Form.io as [schema-driven application infrastructure](https://form.io/platform/), this is the right kind of MCP server: one that makes the governed path easier than building around it.
That value shows up in customer language too. In a [Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/), a long-time Form.io platform user put it plainly: "Form.io cleans up all the dirty work and does it for you." The surrounding case study frames that value as months of development time saved on a next-generation application launch.
## **How to decide what belongs in your agent context**
The fastest way to create MCP sprawl is to install every useful server globally.
Do not do that.
Treat MCP servers like permissions. Most should be project-specific, task-specific, or environment-specific.
Use this sequence:
1. Start with read-only discovery.
2. Prefer official or vendor-maintained servers.
3. Scope by project, repo, workspace, tenant, or environment.
4. Keep mutation tools disabled until the workflow needs them.
5. Separate local development access from production access.
6. Route secrets through existing identity systems where possible.
7. Log agent actions in the system of record.
8. Review prompt-injection exposure when the server reads user-authored content.
9. Revoke unused servers.
That may sound slower than "install the top 20 MCP servers." It is not slower when you count remediation.
A regulated team that cannot explain which server had which permission at which point in a workflow does not have an MCP strategy. It has a collection of shortcuts.
## **Why domain-specific MCP matters**
Generic MCP servers are good at giving agents access to tools. Domain-specific MCP servers are better when the agent needs to create governed artifacts.
That difference is especially important for forms and workflow data.
A generic file server can read a schema file. A GitHub server can modify code. A browser server can test a form. None of those, by itself, tells the agent what a valid governed form workflow should look like inside the enterprise.
Form.io's MCP Server does.
The reason is architectural. Form.io is not only a form renderer. Its [drag-and-drop form builder and API model](https://form.io/features/drag-and-drop-form-builder-apis/) treats form definitions as JSON-backed application infrastructure. Forms can produce APIs. Submission data is managed separately from Form JSON. Form revisions and submission management matter because historical state and current state are not always the same thing.
That is why the Form.io MCP Server matters for regulated developers. It helps the coding agent build with the same primitives the platform governs: forms, resources, actions, APIs, roles, group permissions, server-side actions, [form revision history](https://form.io/features/form-revisions-form-json-schema/), and [complete audit trails](https://form.io/features/log-forms-complete-audit-trail/).
That does not mean Form.io replaces GitHub, GitLab, AWS, Azure, Playwright, Sentry, or Atlassian. It means Form.io occupies a different layer: the form and workflow infrastructure layer where business data enters the system and becomes governed submission state.
## **What proof should enterprise teams look for?**
Popularity is weak proof.
Stars, upvotes, and directory rank tell you that a server is visible. They do not tell you whether the server is appropriate for regulated work.
Better proof looks like this:
- Official or vendor-maintained source.
- Clear authentication model.
- Clear transport model.
- Least-privilege configuration.
- Permission inheritance from the system of record.
- Audit logging for meaningful actions.
- Environment separation.
- Versioned releases.
- Security guidance.
- Support for private or self-managed deployment where needed.
The production-readiness gap is real. A [2026 research paper on production MCP](https://arxiv.org/abs/2603.13417) reports more than 10,000 active MCP servers and 97 million monthly SDK downloads, while also arguing that production MCP still needs stronger identity propagation, adaptive tool budgeting, structured error semantics, and observability.
That is the point. MCP adoption is moving faster than MCP governance.
The answer is not to wait. The answer is to be precise.
Use servers that inherit controls you already trust. Scope them narrowly. Prefer domain-specific servers when the agent is creating governed artifacts. Treat runtime agent governance as a separate layer from coding-time MCP.
## **Key takeaways**
- An MCP server list helps you discover options, but it does not approve them for regulated use.
- Official and vendor-maintained servers should carry more weight than generic directory entries.
- Evaluate each server by identity, permissions, audit evidence, transport, data boundary, and mutation risk.
- GitHub, GitLab, AWS, Azure, Atlassian, Playwright, Sentry, Docker, and Form.io each occupy different control surfaces.
- Form.io's MCP Server is a build-time path into governed form and API infrastructure; UAG is the separate runtime governance layer.
## **FAQ**
### **What is an MCP server list?**
An MCP server list is a directory, registry, repository, or article that helps developers find Model Context Protocol servers. The best starting point is the official MCP Registry, but regulated teams should treat any list as discovery rather than approval.
### **What is the safest way to find MCP servers?**
Start with official sources: the official MCP Registry, vendor documentation, vendor-maintained GitHub repositories, and your own internal registry for private servers. Avoid installing servers only because they appear in a public directory or social post.
### **Are MCP servers secure?**
MCP servers are not automatically secure or unsafe. Security depends on the server's code, maintainer, transport, authentication model, tool scope, permissions, data access, and execution environment. The MCP security guidance specifically calls out risks such as confused deputy behavior, token passthrough, SSRF, session hijacking, local compromise, and scope minimization.
### **Should regulated teams use community MCP servers?**
Sometimes, but not casually. A community server can be useful for low-risk local workflows, prototypes, or read-only tasks. For sensitive systems, prefer official or vendor-maintained servers, or run an internal review before adding the server to an enterprise agent environment.
### **Which MCP servers are best for developers?**
A practical regulated-enterprise list usually starts with GitHub or GitLab for SDLC work, Playwright for browser testing, AWS or Azure for cloud workflows, Atlassian for ticket and documentation context, Sentry for debugging, Docker for packaging and gateway patterns, and Form.io for governed form/API infrastructure.
### **What is the difference between an MCP registry and an MCP server?**
An MCP registry helps you discover servers and their metadata. An MCP server is the actual connector that exposes tools, data, or actions to an MCP client. A registry is not a security review, and it does not mean the server is safe for your environment.
### **How does Form.io fit into an MCP server list?**
Form.io fits when the agent needs to work with governed form and workflow infrastructure. The Form.io MCP Server gives AI coding agents access to Form.io forms, resources, actions, and APIs inside the customer's deployment boundary, while Form.io Skills guide the agent toward platform-specific implementation patterns.
### **Is Form.io UAG an MCP server?**
No. Form.io's MCP Server is build-time infrastructure for AI coding agents. UAG is runtime governance for production agent workflows. They belong in the same agentic architecture conversation, but they are not the same component.
### **Should MCP servers be installed globally?**
Usually no. Global installation encourages overbroad access. Regulated teams should scope MCP servers by project, workspace, environment, repository, tenant, or task. Mutation tools should be enabled only when the workflow requires them.
### **What should an enterprise MCP policy include?**
At minimum, it should define approved server sources, identity requirements, permission scopes, logging expectations, data-boundary rules, prompt-injection handling, environment separation, and a removal process for unused or deprecated servers.
### **When should a team build its own MCP server?**
Build your own MCP server when the system is internal, private, highly regulated, domain-specific, or poorly represented by public servers. Private systems should not be forced into public registries just to make them usable by agents.
## **Build Governed Form And API Workflows With Form.io**
If your team needs AI coding agents to build against governed forms, generated APIs, submission records, permissions, revisions, and self-hosted infrastructure, [try Form.io for governed form and API workflows](/try-formio-for-free/).
# AI Governance Platform: Agentic Workflow Governance Layers Compared
[  ](https://form.io/ai-governance-platform-agentic-workflow-governance-layers-compared/)AI governance platform searches hide several different problems under one phrase. A policy registry is not runtime tool-call control. A process engine is not schema-driven data access. If agents can read data, invoke tools, submit records, and trigger workflows, governance has to live where the agent acts. This comparison names the layer before judging the tool.
## **The AI Governance Gap Is Now Operational**
Most AI governance conversations started with model risk, policy documentation, and compliance review. Those still matter.
But agentic workflows add a sharper question: what happens when the AI system can do something?
Grant Thornton's 2026 AI Impact Survey found that 78% of senior business leaders lacked full confidence that their organization could pass an independent AI governance audit within 90 days. The same survey said 46% of leaders believed AI underperformed because controls and compliance were not working ([Grant Thornton](https://www.grantthornton.com/insights/press-releases/2026/april/grant-thornton-survey-on-ai-proof-gap)).
That is not just a board-level policy problem. It is an infrastructure problem.
Gartner's 2025 strategic technology trends report predicted that by 2028, at least 15% of day-to-day work decisions would be made autonomously through agentic AI, up from 0% in 2024 ([Gartner](https://www.gartner.com/en/newsroom/press-releases/2024-10-21-gartner-identifies-the-top-10-strategic-technology-trends-for-2025)). If even a small share of ordinary operational decisions moves through agents, governance has to follow the action, not only the policy record.
If an agent can approve a request, update a record, route a case, draft a decision, trigger an integration, or submit structured data into a system of record, the organization needs more than a governance statement. It needs an execution path that can answer:
- What was the agent allowed to do?
- Which identity or role gave it that permission?
- What schema, validation rule, or process state constrained the action?
- Was a human required to approve it?
- What audit evidence exists after the action?
An AI governance platform can help with policy, inventory, and risk. An agentic workflow needs that, plus runtime controls at the exact layer where the agent touches the business system.
## **Five Governance Layers To Compare**
The phrase "AI governance platform" is too broad unless you name the layer.
For agentic workflows, the main layers are:
**Governance layer****What it governs****Example fit**AI policy and risk governanceAI inventory, use cases, risk tiering, compliance evidence, board reportingCredo AI, OneTrust, IBM watsonx.governance, classic GRC-style AI governance suitesRuntime agent governanceTool calls, resource access, inter-agent messages, action-level policy enforcementMicrosoft Agent Governance ToolkitProcess orchestration governanceBPMN, case state, human tasks, SLAs, process audit trails, exception handlingCamunda 8.9, Flowable 2025.1, Appian process workflowsPlatform-native agent governanceAgents built and managed inside a specific app/process platformAppian Agent StudioSchema/API/data-access governanceThe forms, fields, validation rules, submissions, APIs, roles, and actions an agent uses to do workForm.io Universal Agent GatewayThese layers can overlap. They can also coexist.
A bank might use Microsoft Entra for agent identities, Microsoft Agent Governance Toolkit for action-level policy, Camunda for cross-system process orchestration, and Form.io UAG for governed access to intake forms, validation, submissions, and downstream workflow actions.
The mistake is treating those as interchangeable.
## **Quick Comparison**
## **Platform or toolkit****Governance center of gravity****Strongest fit****Watch the boundary**Form.io UAGSchema, form, API, submission, RBAC, and action governance exposed to agents through MCPAgents that need governed access to forms, submissions, validation, and workflow infrastructureNot a generic AI GRC dashboard or full BPMN engineAppian Agent StudioAgents embedded inside Appian's process/application platformTeams already building workflows in AppianStrong inside Appian's platform boundary; less about portable schema/API ownershipCamunda 8.9BPMN-based agentic orchestration, human tasks, process state, audit logs, MCP/A2ATeams that govern work through explicit process modelsGovernance starts at orchestration; the data-capture/schema layer may still live elsewhereFlowable 2025.1Agent engine beside BPMN/CMMN/DMN, agent exchange tracking, case/process controlDynamic case work and process automation with first-class agentsStrong process layer; still needs source-of-truth data contractsMicrosoft AGTRuntime policy enforcement, identity, sandboxing, OWASP agentic risk controlsDevelopers adding action-level governance to agent frameworksA toolkit, not a business workflow or forms infrastructure platform**Form.io UAG: When The Governed Schema Should Become Agent Context**
Form.io's Universal Agent Gateway is strongest when the agent has to operate through a governed form and workflow layer instead of a loose collection of prompts, tools, and credentials.
Form.io's core argument starts below the agent. In Form.io, Form JSON is the schema created by the form builder. The Form.io documentation says that schema is used to render forms inside applications, generate REST API interfaces on the server, and host the form schema at the embed URL ([Form.io Form JSON documentation](https://help.form.io/userguide/forms/form-building/form-json)).
That matters because an agent needs structured context.
An agent does not need a vague prompt saying "collect the right onboarding details." It needs to know which fields exist, which fields are required, what validation rules apply, how submissions are shaped, which actions can run, and what permissions apply to the current actor.
Form.io UAG turns that existing application infrastructure into the agent surface. The UAG page explains that agents can authenticate through existing Form.io auth and SSO, inherit enterprise RBAC, retrieve and route secure data inside the private network, and execute actions governed by Form.io Actions and audit trails ([Form.io UAG](https://form.io/uag/)).
That is a specific kind of governance. It is not "AI governance" as a board dashboard. It is governance at the layer where forms, APIs, submissions, validation, and workflow actions already meet.
This is why Form.io should not be framed as simply another AI agent platform. Form.io's AI page describes UAG as the runtime governance layer for production agentic workflows, while the MCP Server, Skills, and Agentic Coding Plugin support build-time development ([Form.io AI](https://form.io/ai/)). That separation is important. Build-time agents need patterns for creating software. Runtime agents need permissioned, logged access to production workflow surfaces.
The customer proof is not AI-specific yet, so it should be used carefully. But it does show why this infrastructure layer matters. In one Form.io public-sector case study, publicplan supported more than 400 digital public-sector services and 1,000+ forms while meeting strict standards and a short timeline ([Form.io publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)). In another Form.io banking case study, an international banking deployment served 5,000 banking groups and recovered 50% of the team's capacity ([Form.io banking case study](https://form.io/case-studies/how-many-technologies-can-actually-support-the-business-process-transformation-of-serving-5000-banking-groups/)).
Those are not UAG deployment claims. They are infrastructure claims. They show why a governed forms/API/submission layer is valuable before agents arrive. UAG extends that same layer to agents.
### **Strongest Fit**
Form.io UAG is the strongest fit when:
- forms are part of the application contract, not just hosted collection pages
- agents need to understand field structure, validation rules, submission shape, and workflow actions
- the customer needs self-hosted or private-network control
- RBAC, auth, audit trails, and form revisions are already part of the governance model
- the team wants humans and agents operating through the same governed schema layer
Form.io is not the right answer if the buyer only needs a general AI policy registry. It is the right answer when the agent's work touches form-driven application infrastructure.
## **Appian Agent Studio: When Agents Belong Inside The Appian Process Platform**
Appian's governance story is platform-native.
Agent Studio is built for teams that already use Appian to design applications, workflows, data fabric patterns, and enterprise processes. Appian's 25.4 release material frames Agent Studio as a guided way to create enterprise AI agents and drag them into business processes. Appian also says agents embedded in processes can use guardrails, tools, data, and human review inside the process context (Appian Agent Studio release material).
That is a clear fit when Appian is already the process application platform.
The governance center is not the open schema/API layer. It is the Appian platform boundary. Agents live inside the Appian design and process model, use Appian objects and tools, and inherit governance from the Appian environment.
That can be exactly what an Appian customer wants. It is less compelling when a team needs agent access to application-owned forms, APIs, validation rules, submissions, and deployment boundaries outside Appian.
### **Strongest Fit**
Appian Agent Studio fits when:
- the business process already lives in Appian
- low-code process design is the center of gravity
- agents need to operate inside Appian's app/process/data fabric layer
- the organization wants human review and process guardrails inside the same platform
The Form.io contrast is not "Appian cannot govern agents." It can govern them inside its platform. The Form.io distinction is that governance starts at the schema and form infrastructure layer agents use to collect, validate, submit, and route data.
## **Camunda 8.9: When BPMN Orchestration Is The Governance Backbone**
Camunda approaches agentic governance from the process orchestration layer.
In its 8.9 release, Camunda frames agentic orchestration as coordinating AI agents, knowledge workers, tools, and systems across end-to-end business processes. The release emphasizes deterministic process logic, global user task listeners, centralized audit logs, MCP access to running clusters, and A2A support for multi-agent communication (Camunda 8.9 release material).
That is a strong governance story for teams that already model work as BPMN.
The useful distinction is this: Camunda governs the flow of work. It controls process state, human tasks, incidents, retries, escalation, and the audit trail around the process. That is different from governing the form schema, validation logic, submission payload, or field-level context an agent uses before it reaches a process step.
In many architectures, both layers matter.
A government service workflow might use Form.io to collect and validate service request data through self-hosted forms and generated APIs, then use Camunda to orchestrate downstream case routing, approvals, exceptions, and cross-system work. The agent should respect both layers.
### **Strongest Fit**
Camunda fits when:
- BPMN is already the operating language for process governance
- the organization needs explicit process state and incident handling
- agents participate in workflows with human tasks and deterministic rules
- auditability needs to follow the end-to-end process path
Form.io fits earlier in the path: where the agent needs governed access to the structured data, forms, validation rules, and APIs that feed the process.
## **Flowable 2025.1: When Case And Process Work Need First-Class Agents**
Flowable's 2025.1 release puts agents beside BPMN and CMMN rather than treating them as external helpers.
Flowable says the release adds an agent engine alongside its BPMN and CMMN automation engines, with internal agent types such as utility, document, knowledge, and orchestrator agents. It also describes agent exchange tracking as a way to store AI interactions for traceability and audit support (Flowable 2025.1 release material).
That makes Flowable a serious process/case governance comparison.
Its strongest fit is dynamic work: cases, documents, human judgment, process variation, and AI-assisted decisions that need to stay inside a process/case model. If a case state determines what an agent can and cannot do, Flowable's governance center makes sense.
The Form.io distinction is again layer ownership.
Flowable can govern the case or process. Form.io can govern the structured form and submission layer that feeds the case. In agentic workflows, those are connected but not identical.
### **Strongest Fit**
Flowable fits when:
- work is case-heavy and may not follow one fixed process path
- AI agents need to operate inside CMMN/BPMN-style orchestration
- traceability of agent exchanges matters
- the organization wants an agent engine inside the process platform
Form.io fits when the agent's most important constraint is the governed schema, validation, permission, submission, and action surface around data intake and form-driven workflows.
## **Microsoft Agent Governance Toolkit: When Developers Need Runtime Action Controls**
Microsoft Agent Governance Toolkit is the most developer-centered entry in this comparison.
Microsoft introduced AGT as an open-source runtime security governance project for autonomous AI agents. The announcement says the toolkit is designed to work with existing frameworks and includes deterministic policy enforcement, identity, sandboxing, reliability controls, and mapping to OWASP agentic AI risks ([Microsoft open-source announcement](https://opensource.microsoft.com/blog/2026/04/02/introducing-the-agent-governance-toolkit-open-source-runtime-security-for-ai-agents/)).
That layer matters because agents can misuse tools even when the surrounding workflow looks well designed.
Microsoft's later Agent Framework guidance makes the layer even clearer: Agent Framework handles build and orchestration, while Agent Governance Toolkit handles govern and audit. It evaluates tool calls, resource access, and inter-agent messages against policy before execution ([Microsoft Agent Framework and AGT](https://devblogs.microsoft.com/agent-framework/governance-at-the-speed-of-agents-microsoft-agent-framework-and-agent-governance-toolkit-better-together/)).
That is not the same job as Form.io UAG.
AGT helps govern the agent's actions at runtime. Form.io UAG gives agents governed access to Form.io's form, submission, schema, API, RBAC, and action layer. In some architectures, AGT could sit beside or around an agent framework, while UAG provides the business-specific tools and context the agent is allowed to use.
### **Strongest Fit**
Microsoft AGT fits when:
- developers need action-level policy checks inside an agent framework
- tool-call misuse, goal hijacking, rogue agents, or inter-agent trust are the main concern
- the team wants an open-source runtime governance toolkit
- the application/workflow platform is already chosen elsewhere
Form.io fits when the agent needs a governed business surface for form-driven work, not only a policy wrapper around tool calls.
## **How To Choose The Right Governance Layer**
The useful question is not "which AI governance platform should we buy?"
The useful question is: where can the agent create the most risk?
### **If The Risk Is AI Inventory And Compliance Evidence**
Start with a classic AI governance platform.
This is the layer for model inventory, use-case approvals, risk tiers, policy mapping, regulatory documentation, monitoring, and executive accountability. It matters most when the organization cannot answer which AI systems exist, who owns them, what risk category they fall into, or what evidence supports approval.
Form.io does not replace that layer.
### **If The Risk Is Tool-Call Misuse**
Look at runtime agent governance.
This is where Microsoft Agent Governance Toolkit is relevant. It helps evaluate actions before execution and provides runtime security controls for autonomous agent frameworks.
Form.io can supply governed business tools and context; AGT can help enforce broader action-layer policies.
### **If The Risk Is Process Visibility**
Look at process orchestration.
Camunda, Flowable, and Appian are stronger when the work has to be governed as a process or case: state, sequence, incidents, handoffs, human review, SLAs, escalation, and full process auditability.
Form.io can still matter if the workflow starts with governed forms, submissions, and APIs.
### **If The Risk Is Data, Schema, And API Drift**
This is where Form.io belongs.
If humans use one form definition, APIs use another contract, agents use a prompt-based tool description, and workflow actions use yet another set of assumptions, governance will drift. The agent may still complete the task. The organization may not be able to prove that the task followed the governed path.
Form.io's stronger argument is that the same Form JSON and platform layer can define the form, the validation, the generated API surface, the submission shape, permissions, and the runtime agent context.
That starts with deployment control. A [self-hosted Form.io](https://form.io/features/self-hosted-forms-for-enterprise/) environment lets the form and submission layer live inside the customer's own infrastructure boundary.
It also starts with the form contract itself. The [drag-and-drop form builder with APIs](https://form.io/features/drag-and-drop-form-builder-apis/) is not only a visual authoring surface; it produces structured definitions that can become application interfaces.
Governance then depends on behavior, not just fields. [Conditional logic and validation](https://form.io/features/form-conditional-logic-form-validation/) help define what data is acceptable before a workflow or agent acts on it.
Finally, the work has to map to people and roles. [Teams and permissions](https://form.io/features/forms-for-teams/) belong in the same architecture conversation because agent access should inherit the same governance model that controls human access.
## **Where Form.io Fits**
Form.io is not trying to be every layer of AI governance.
That is a strength, not a weakness.
Form.io is strongest when forms are application infrastructure: the schema, user interface, generated API, validation model, submission record, permission boundary, and workflow trigger are connected. When agents enter that environment, the agent should not get a separate shadow contract. It should operate through the same governed layer as the application.
That is the UAG argument.
If your organization only needs an AI policy dashboard, choose an AI governance suite. If it needs action-level runtime policy enforcement across agent frameworks, evaluate a toolkit like Microsoft AGT. If it needs process orchestration, evaluate Camunda, Flowable, or Appian.
If the agent needs governed access to forms, fields, submissions, APIs, validation rules, permissions, and workflow actions inside a customer-controlled deployment, Form.io should be in the conversation.
## **Key Takeaways**
- AI governance platform is too broad unless you name the layer.
- Agentic workflows need governance where agents act, not only where policies are documented.
- Form.io UAG governs the schema/API/form/submission/action layer for production agents.
- Appian, Camunda, and Flowable govern agents through process or case platforms.
- Microsoft AGT governs runtime tool calls and action policies.
- The strongest architecture can combine layers instead of forcing one product to do every job.
- Form.io's strongest claim is not generic AI governance. It is governed application infrastructure for agents working through forms, APIs, validation, submissions, permissions, and actions.
## **FAQ**
### **What Is An AI Governance Platform?**
An AI governance platform helps organizations manage AI risk, policy, accountability, compliance evidence, monitoring, and operational controls. In classic enterprise usage, it often includes AI inventory, use-case approvals, risk classification, policy mapping, audit evidence, and reporting.
For agentic workflows, the term needs more precision. A platform that governs model risk is not automatically the same as a tool that governs agent actions, process state, form submissions, or API access.
### **What Is Agentic Workflow Governance?**
Agentic workflow governance is the set of controls that determines what an AI agent can do inside a business process. It covers tool access, data access, identity, permissions, validation, human review, logging, audit trails, exception handling, and policy enforcement.
The key difference is action. A chatbot that answers a question needs content safety. An agent that updates a submission or triggers a workflow needs execution governance.
### **Is Form.io UAG An AI Governance Platform?**
Form.io UAG is most accurately understood as a runtime governance layer for agents operating through Form.io infrastructure. It is not a general AI GRC dashboard.
UAG gives agents governed access to the Form.io layer: forms, field definitions, validation, submissions, actions, auth, RBAC, and application workflow context. That makes it highly relevant to agentic workflow governance, especially when forms and APIs are part of the customer-controlled application stack.
### **How Is Form.io UAG Different From Microsoft Agent Governance Toolkit?**
Microsoft Agent Governance Toolkit focuses on runtime policy enforcement for agent actions: tool calls, resource access, identity, sandboxing, and auditability around the agent framework.
Form.io UAG focuses on the business surface the agent uses when work involves forms, submissions, validation, APIs, and workflow actions. AGT can help govern the agent's behavior. UAG gives the agent a governed Form.io context to operate through.
### **How Is Form.io UAG Different From Process Engines?**
Process engines such as Camunda and Flowable govern processes and cases. They are strong when the main governance problem is end-to-end orchestration: state, sequence, human tasks, incidents, escalation, and process audit trails.
Form.io governs the form and data infrastructure layer. It is stronger when the main governance problem is schema, validation, submissions, permissions, APIs, and form-driven workflow actions. Many enterprise architectures can use both layers.
### **When Should A Team Use A Classic AI Governance Suite Instead?**
Use a classic AI governance suite when the main problem is enterprise oversight: AI inventory, use-case approvals, risk scoring, regulatory mapping, model monitoring, audit evidence, and board-level accountability.
Use Form.io UAG when the main problem is operational: agents need governed access to forms, submissions, validation, APIs, and workflow actions. The two layers can complement each other.
### **Why Does Schema Matter For Agent Governance?**
Agents need structured context. A schema tells the agent what fields exist, which data is required, what validation rules apply, how submissions are shaped, and which actions are meaningful.
When the same schema drives human forms, APIs, validation, and agent context, the organization reduces drift. The agent is less likely to operate from stale prompt instructions or a parallel tool definition that no longer matches the application.
### **Can Form.io Replace A Process Engine?**
No. Form.io should not be framed as a full process engine replacement.
Form.io is infrastructure for forms, APIs, submissions, validation, permissions, and workflow-related actions. If the organization needs full BPMN or case orchestration, a process engine may still be appropriate. Form.io's role is to make the form and data capture layer governed enough for humans, developers, systems, and agents to use safely.
## **Build Governed Agentic Workflows With Form.io**
If your agents need to work through forms, submissions, APIs, validation rules, permissions, and workflow actions inside your own deployment boundary, start with the governed infrastructure layer.
[Try Form.io for governed agentic workflow infrastructure](/try-formio-for-free/).
[ Share](https://www.facebook.com/sharer/sharer.php?u=https://form.io/ai-governance-platform-agentic-workflow-governance-layers-compared/%2F&src=sdkpreparse)#### Webinars
# [](https://form.io/webinars/agentic-coding-for-the-enterprise/)[Agentic Coding for the Enterprise (LIVE Demo: Form.io Agentic Coding Toolset)](https://form.io/webinars/agentic-coding-for-the-enterprise/)
# Date: Wednesday, August 19, 2026 Time: Central [](https://form.io/webinars/enable-self-service-forms-in-your-application/)[Enable Self-Service Forms in Your Application (LIVE Demo: Form.io’s Enterprise Form Builder Module)](https://form.io/webinars/enable-self-service-forms-in-your-application/)
# Date: Thursday, June 25, 2026 Time: 11:00 pm Central [](https://form.io/webinars/byo-css-the-new-standard-for-white-labeling-form-io/)[BYO-CSS: The New Standard for White Labeling Form.io](https://form.io/webinars/byo-css-the-new-standard-for-white-labeling-form-io/)
Date: Thursday, March 26, 2026 Time: 11:00 am Central #### Recent Posts
# [](https://form.io/web-form-builder-apis-self-hosted-control/)[Web Form Builder: When Online Forms Need APIs, Workflows, and Self-Hosted Control](https://form.io/web-form-builder-apis-self-hosted-control/)
# August 5, 2026 [](https://form.io/e-signature-software-self-hosted-form-workflows/)[E Signature Software for Self-Hosted Form Workflows: DocuSign Alternatives for Enterprise Control](https://form.io/e-signature-software-self-hosted-form-workflows/)
# July 21, 2026 [](https://form.io/json-schema-validator-tools-production-apps/)[JSON Schema Validator Tools for Production Apps](https://form.io/json-schema-validator-tools-production-apps/)
# July 20, 2026 [](https://form.io/embedded-forms-b2b-saas-white-label-comparison/)[Embedded Forms for B2B SaaS: The White-Label Form Builder Comparison](https://form.io/embedded-forms-b2b-saas-white-label-comparison/)
# July 17, 2026 [](https://form.io/claims-management-software-insurance-form-builders/)[Claims Management Software Starts With The Forms That Feed It](https://form.io/claims-management-software-insurance-form-builders/)
# July 16, 2026 [](https://form.io/kyc-onboarding-software-financial-services-form-platforms/)[KYC Onboarding Software for Financial Services: Forms, APIs, and Audit-Ready Intake](https://form.io/kyc-onboarding-software-financial-services-form-platforms/)
July 15, 2026 #### Recent Case Studies
# [](https://form.io/case-studies/from-60-pages-to-a-single-click/)[From 60 Pages to a Single Click: How Form.io Powered a Government Agency’s Digitization](https://form.io/case-studies/from-60-pages-to-a-single-click/)
# June 15, 2026 [](https://form.io/case-studies/from-six-week-release-cycles-to-same-day-form-changes-patagonia-health/)[From Six-Week Release Cycles To Same-Day Form Changes – Patagonia Health](https://form.io/case-studies/from-six-week-release-cycles-to-same-day-form-changes-patagonia-health/)
# June 15, 2026 [](https://form.io/case-studies/accelerated-development-time-line-by-two-years/)[Accelerated Development Timeline By Two Years](https://form.io/case-studies/accelerated-development-time-line-by-two-years/)
# May 7, 2025 [](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)[The Digital Transformation Of Supporting New Services For The German Public Sector—On Repeat](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)
December 2, 2024 #### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# E-Sign+ Digital Signatures
*Published:* 2026-05-12
*Author:* Form.io Wizard
*URL:* https://form.io/e-sign-plus/
*Description:* Enterprise digital signature page for E-Sign+, Form.io's module for cryptographic signatures on submission data inside self-hosted environments.
For enterprises that need signed data to stay inside their own environment
# E-Sign+: Cryptographic E-Signatures For Form Data You Control
## Form.io E-Sign+ lets teams capture and verify digital signatures directly against submission data, inside their own self-hosted environment, without handing sensitive workflows to a third-party e-signature platform or forcing every signature into a PDF process.
##  Digital Signature Infrastructure For Healthcare Financial Services Government Insurance Regulated Workflows Most E-Signature Workflows Still Treat Digital Work Like Paper
### When the signature depends on a document export, a vendor account, or a separate PDF workflow, your proof of agreement starts drifting away from the system where the real data lives.
### Without E-Sign+
- Sensitive form data may leave your security boundary just to complete a signature step.
- The signed proof is tied to a document artifact instead of the live submission record your application already uses.
- You have to trust a third-party system with the signature evidence, audit trail, and cryptographic proof.
### With Form.io E-Sign+
- The signature happens inside your own Form.io environment, against the submission data itself.
- Signed values are cryptographically verified, and changes invalidate the signature automatically.
- You keep control of the data, the signature record, the APIs, and the cryptographic key strategy.
## What E-Sign+ Actually Proves
### Not merely that someone drew or typed a signature. It proves that the signed data and its context have not changed since the moment of signing.
E-Sign+ creates a cryptographic signature for the selected submission data, form context, and configured submission properties. If the protected values change later, the signature no longer validates.
That distinction matters. In regulated workflows, the question is not only, “Was there a signature?” The harder question is, “Can we prove this is still the same data that was signed?”
Form.io answers that question at the data layer, where the submission already lives.
## Why Enterprises Use E-Sign+
### Because high-stakes signatures need more than a visual mark on a PDF. They need data integrity, ownership, auditability, and deployment control.
### Zero-Trust By Design
The signature process runs inside your application environment, so sensitive submission data and signature evidence do not need to move to an external provider.
### API-Driven Access
Signed data remains accessible through the native Form.io submission ID and APIs, keeping signatures connected to the application workflow.
### Decoupled From PDFs
Create immutable data snapshots inside your application without requiring a PDF-first process, while still exporting to PDF when the workflow requires it.
### Bring Your Own Keys
Use your own private keys, store them outside the deployment when needed, or integrate cryptographic operations through AWS KMS.
## Built For Signed Workflows Where Data Cannot Be In Question
### Especially when the signature is part of a larger form-driven process, not a standalone document transaction.
### Healthcare Consent And Intake
Capture consent against the exact patient data, disclosures, and form context inside the healthcare workflow your application already manages.
### Financial Approvals And Disclosures
Protect approvals, loan terms, underwriting decisions, disclosures, and internal sign-offs with tamper-evident validation.
### Government And Insurance Workflows
Keep applications, attestations, approvals, and regulated submissions inside the environment where governance and auditability are already enforced.
## Are You Going To Build Signature Infrastructure Yourself?
### The hard part is not putting a signature field on a form. It is proving, later, that the signed data, form definition, and relevant submission context are still intact.
That requires cryptographic signing, revision-aware submission handling, invalidation behavior, API access, key management, signature metadata, and a user-facing stamp that makes validity understandable.
E-Sign+ gives self-hosted Form.io customers a governed digital signature module without forcing the organization into disconnected document infrastructure.
### What E-Sign+ Helps You Avoid
- Exporting sensitive workflows into third-party e-signature platforms.
- Building and maintaining a custom cryptographic signature layer around your form workflows.
- Relying on signatures that look complete visually but do not prove the underlying submission data is unchanged.
## How E-Sign+ Works
### Configure what a signature protects, capture the signature inside the form, then let Form.io validate whether the protected data still matches.
1 ### Define
Select the component that acts as the signature and choose whether it protects specific fields, all form data, or selected submission properties.
2 ### Sign
Use a compatible field type, including text fields, checkboxes, dates, email fields, or a traditional signature component, to capture the signing action.
3 ### Verify
Display a configurable signature stamp and validate whether the signed values, form revision, and selected context remain unchanged.
## Keep Digital Signature Trust Inside Your Own Environment
### Use E-Sign+ when signed data, cryptographic proof, and auditability need to stay connected to the Form.io submissions, APIs, and deployment controls your organization already depends on.
## Form.io is Trusted By Enterprises Building Complex, Regulated, Form-Driven Applications
          #### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# Enterprise Form Builder Module
*Published:* 2026-04-09
*Author:* Form.io
*URL:* https://form.io/enterprise-form-builder-module/
*Description:* White-labeled embedded form building for products and internal platforms, giving users self-service form creation while teams keep control of data, rules, APIs, and workflow governance.
For enterprises that need self-service form building without losing control
# Embed Form Building Directly In Your App
## Give internal teams or customers a white-labeled, pre-configured form builder inside your application so they can build the forms they need without waiting on your team, while you keep the structured data, governance, and workflow integrity your platform depends on.
## 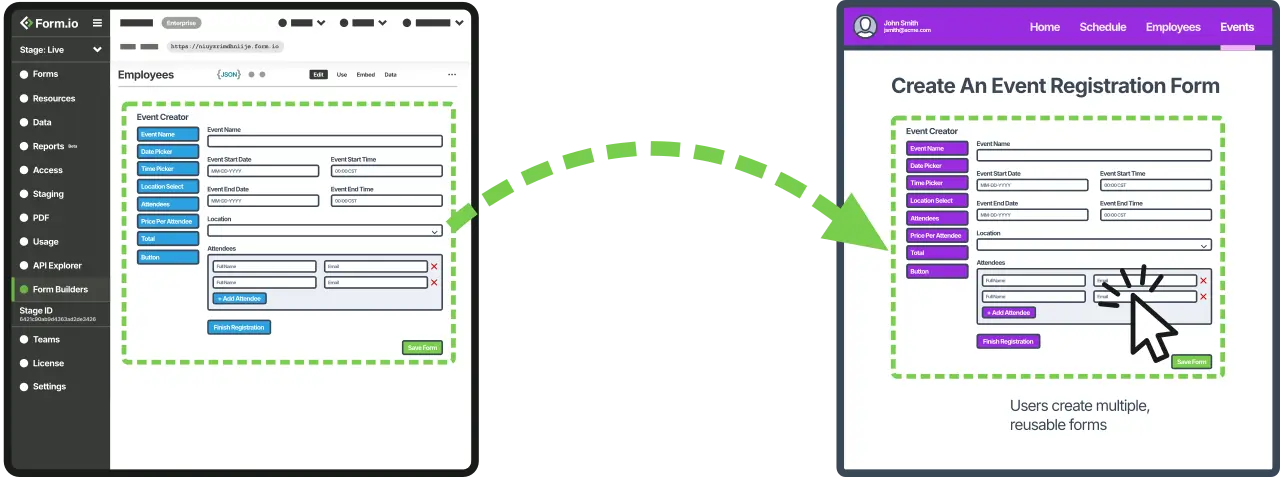 Self-Service Form Building For Customers Product Teams Customer Support Marketing Teams Operations If Form Building Stays A Developer Function, Your Customers Wait And Your Backlog Grows
### Every new form request becomes a ticket, a delay, and another round of manual configuration your team has to own.
### Without Embedded Form Building
- Your customers send requests every time they need a new form or a variation for a new office, team, or workflow.
- Your developers become the bottleneck for layout, branding, rules, routing, and release timing.
- Building your own form builder means also building permissions, validation, lifecycle management, and governance around it.
### With The Enterprise Form Builder Module
- Your customers can self-serve by building their own forms inside your application.
- You control the guardrails, data model, and workflow behavior while exposing only what your platform should allow.
- You scale software, not headcount, because form creation stops living in your support queue.
## What You Are Actually Embedding
### Not just a drag-and-drop UI. A governed, connected, white-labeled form building capability that lives inside your platform.
The Enterprise Form Builder Module lets you expose form building to your customers within your own application experience. That means your users get autonomy, but they do not get chaos.
You can pre-configure components, constrain what can be built, preserve your branding, and keep every form connected to the Form.io platform's structured data, APIs, permissions, and workflow behavior.
So instead of handing customers a disconnected builder, you embed a controlled extension of your product.
## Why Enterprises Use EFBM
### Because the goal is not just letting customers make forms. The goal is letting them manage their own workflows without breaking your platform.
### White-Labeled In Your Experience
Your customers never leave your product. The builder is exposed under your brand, inside your workflows, with the experience you want them to have.
### Pre-Configured Customer Autonomy
Let customers create what they need inside the boundaries you define, so self-service does not become a governance problem.
### Structured, AI-Ready Data
Forms are connected to JSON-driven data structures and APIs, which makes downstream automation, routing, and agent workflows far more reliable.
### Scale Software, Not People
Remove an entire class of repetitive support work from your team and turn form delivery into a product capability instead of an ongoing service burden.
## Built For Platform Companies Serving Complex Customers
### Especially when every customer, office, agency, or business unit needs some variation of the forms and workflows inside your application.
1 ### Customer-Facing Platforms
Your customers need to create and manage forms as part of the product experience, not by emailing your support team.
2 ### Multi-Office Or Multi-Group Operations
Each office, department, or tenant needs its own forms and process variations, but you still need one governed platform strategy.
3 ### Enterprise Workflow Applications
You need the forms, the data, and the workflow logic to stay connected because the forms are only the visible tip of the business process.
## Are You Going To Build This From Scratch?
### Because the hard part is not drawing a form on the screen. It is everything required to make embedded form building viable in an enterprise product.
White-labeling. Permissions. Component constraints. Validation. Structured data. Workflow routing. Governance. Auditability. Long-term maintainability.
The Enterprise Form Builder Module lets you expose a proven form building capability inside your application without taking on the cost, risk, and distraction of building the builder yourself.
### What the Enterprise Form Builder Helps You Avoid
- Building an embedded form builder as a standalone engineering project.
- Manually servicing endless requests for new forms, revisions, and workflow-specific variants.
- Creating disconnected forms that look flexible on the surface but break your data and process standards underneath.
## How Enterprises Use It
### Configure the capability once, expose it in your product, then let customers move faster inside guardrails you control.
1 ### Configure
Define the components, rules, branding, and workflow boundaries appropriate for your platform and your customers.
2 ### Embed
Expose the builder directly inside your application so form creation happens where the work already lives.
3 ### Scale
Let customers create what they need while your platform keeps the data structured, branded, governed, and connected.
## Turn Form Requests Into A Product Capability
### Embed a white-labeled form builder in your app so your customers can self-serve, your team can stop chasing tickets, and your platform can keep the structured data and workflow discipline enterprise buyers expect.
## Form.io is Trusted By Enterprises Building Complex, Regulated, Form-Driven Applications
          #### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# Form.io Universal Agent Gateway (UAG)
*Published:* 2025-11-19
*Author:* Form.io Wizard
*URL:* https://form.io/uag/
*Description:* pen-source, MIT-licensed MCP server. Turns the JSON schemas you already use for forms, APIs, and workflows into dynamic context, guardrails, and authenticated data access for AI agents in regulated enterprises — without retraining models or ripping out your stack.
## Form.io's Universal Agent Gateway (UAG) turns the JSON schemas you already use for forms, APIs, and workflows into dynamic context, guardrails, and data access for agents without retraining models or ripping out your stack.
## The Silent Failure Mode of Enterprise AI Agents
### The Top Concerns for Gen AI Among Enterprises In are Scalability & Performance, Security Regarding Sensitive Information, Integration Challenges, Ease of Use, Cost, and Data Transparency.\*
AI Agents in enterprises need to:
- Interface with existing production systems, legacy, new, and anything in between.
- Operate on real, governed data
- Respect RBAC and existing auth
- Follow actual business rules and human-in-the-loop workflows
But teams are hitting the same walls every time:
- Integration complexities: "Every time we connect an agent to a real system, we end up having to hand-wire one-off implementations."
- Security risk & governance: "We can't just copy all this data into a model or expose it over the open web."
- Operational Complexity: "Every use case needs its own agent, its own integration service, its own glue code."
- Context Chaos: "The model is smart, but it doesn't know our fields, our forms, our processes."
They DON'T have a model problem.
They DO have a context, control and integration problem.
It doesn't have to be this way.
\* "Accountable Acceleration: Gen AI Fast-Tracks Into The Enterprise." Wharton Human-AI Resaerch and GBK Collective, October 2025
## 3 Alternatives You Might Be Considering
### And Why They Hurt You
Most enterprises trying to solve the AI agent problem are faced with one of three unattractive paths:
1. Train Your Own Fleet of Task-Specific Models
- High cost, high complexity
- Every new workflow = new training + governance overhead
- Hard to keep aligned with constantly changing processes
2. Lock into a Monolithic "Do Everything" Agent Platform
- Vendor lock-in for your most strategic layer
- Opinionated stack that may clash with your existing architecture
- Limited control over how agents see and act on your data
3. Build Custom MCP Servers and Agent Services for Each Use Case
- Your best engineers become "plumbers"
- Every integration becomes a one-off snowflake
- Maintenance, security reviews, and compliance sprawl over time
What if there was a fourth path?
## The Form.io Universal Agent Gateway (UAG)
### The Bridge Between Enterprise AI and Enterprise Reality
Form.io has spent a decade helping enterprises standardize mission-critical workflows on JSON-driven forms, APIs, and RBAC.
The Universal Agent Gateway (UAG) takes that same JSON foundation and uses it to:
Enable agents to work inside your enterprise the same way your humans already do.  Instructing agents with the same JSON schemas that you use for forms, APIs, and workflows. With UAG:
- The same JSON definitions that power your forms, validations, APIs, and RBAC now define agent context, inputs, and outputs.
- Updating a form isn't just a UX change, it instantly updates what an agent knows and is allowed to do.
- Agents authenticate like users, inherit real RBAC, and are logged, governed, and auditable.
- All of this is packaged as a configurable MCP Server, released as MIT-licensed Open Source, and designed to plug into your existing Form.io projects.
You don't rebuild your enterprise for AI.
## You extend the system so you can standardize once on JSON-driven forms and APIs, then use UAG as the universal, open, self-hosted MCP layer connecting agents, humans, and systems. The Core Shift: From "Prompt Hacking" to JSON-Driven Agent Workflows
### Most organizations are trying to solve context with brittle workarounds:
- Prompt stuffing: giant, fragile prompts that break when the process changes.
- Massive retraining: expensive fine-tuning just to get models to understand your domain.
- Ad-hoc tools: custom MCP servers built per use case that your teams have to maintain forever.
UAG inverts the model:
1 Your JSON Schemas Become Agent Context When you've already configured:
- Form Definitions
- Validation rules
- Conditional logic
- Data models
- RBAC Policies
- Auth integration
- Form settings
- Data routing
UAG treats these as the binding set of rules for agents:
- Because a nurse doesn't want to read JSON, they want an intake form.
- An AI agent doesn't want raw spec docs, it wants structured JSON describing fields, rules, and constraints.
UAG is effectively a form renderer for AI agents. It interprets your Form.io JSON the way your applications do, and exposes it as dynamic, precise context through MCP tools.
- No duplication.
- No parallel "AI configuration" universe.
- No fragile prompt engineering.
2 Dynamic Context Updates Without Retraining With UAG:
- Update a form → update an agent's context.
- Add a field → add a constraint or capability.
- Publish a new version → instantly change agent behavior.
Change a form, change the agent. You don't retrain a model to add "Preferred Language" to an onboarding flow.
You update the form, and the agent, via UAG,knows:
- The field exists
- Its type, validation rules, masks, and required status
- Where to place it in the submission payload
This is the first time enterprises can iterate on agent logic the same way they iterate on forms.
3 Agents Get Real, Authenticated Access With Real RBAC With UAG, agents:
- Authenticate like any other user via your existing Form.io-based auth and SSO.
- Inherit your enterprise RBAC, not some shadow permission model
- Retrieve and route secure data dynamically, within your private network.
- Execute actions governed by your existing Form.io Actions and audit trails.
Every step is:
- Authenticated
- Authorized
- Logged
So instead of praying your "AI middle layer" behaves, you're operating inside a governed, auditable architecture you already trust.
4 Packaged as a Configurable MCP Server Instead of building your own agent-service per use case, UAG gives you:
- A turnkey MCP Server wired to your Form.io project
- Native authentication, RBAC, routing, and validation
- Native data model governance via your existing JSON schemas
- Extensible Actions and Modules to push/pull from any existing system (Snowflake, legacy databases, line-of-business apps, etc.)
Your developers work with skills and patterns they already know:
- JSON schemas
- Form.io server
- Actions and middleware
- Familiar self-hosted deployment
## So your teams can focus on designing workflows and guardrails, not reinventing yet another "AI integration layer." What This Looks Like in Practice
### It Doesn't Rely on Training Probabilities or Guesswork
A user OR an automated function sends a request to a UAG-enabled agent:
"Create a new customer: Joe Smith, CEO of ACME, with billing address in Dallas, and route him into your Tier 2 onboarding flow." What happens with UAG in the loop:
1. The agent calls UAG's tools to discover relevant forms and resources (e.g., Customer, Onboarding).
2. UAG returns the actual field definitions, requirements, and constraints from your Form.io project.
3. The agent uses that structured definition to assemble a valid submission object: not a guess.
4. UAG validates, sanitizes, and authorizes the data using the same pipeline your human forms go through.
5. UAG triggers your configured Actions/Modules to push data into your CRM, ERP, or any other system.
6. The whole interaction is logged and auditable, tied to the agent's authenticated identity.
## To the agent, it feels like a single, intelligent tool. To your enterprise, it feels like every guardrail you already trust and invested in is extended to AI. Why Form.io Is Uniquely Positioned to Solve This
### We're Not Just Jumping Into AI From the Sidelines
For years, enterprises across insurance, government, healthcare, banking, and large corporate IT have used Form.io to:
- Standardize form-based data collection
- Power mission-critical business process applications
- Enforce RBAC, validation, and data governance across complex workflows
- Self-host in highly regulated, security-sensitive environments
UAG is a direct extension of that proven foundation into the era of agentic AI:
- Same platform. Same JSON. Same governance.
- Now applied to AI agents as first-class actors.
## If You're Responsible for "Making AI Real," This Is For You
If you’re a CTO, Head of Platform, or senior engineering leader, you’re under pressure to:
- Turn AI from slides and demos into shipped systems
- Avoid another wave of technical debt and shadow platforms
- Protect the security, compliance, and trust you’ve spent a decade building
UAG is built to let you say “yes” to AI agents without saying “yes” to chaos:
- Agents can triage internal tickets, but only within governed forms and RBAC.
- Agents can initiate workflows across systems, but only through validated Actions you control.
- AI can scale process automation without you rebuilding your entire architecture.
Without starting over. Advance the the system you've already built into an AI-native future with a platform that's fully deployed in your enterprise environment.
 Standardize your AI integration strategy around one open-architected, self-hosted, extensible gateway instead of scattering risk and responsibility across vendors.
---
# Build AI Apps That Work For Your Enterprise
*Published:* 2025-07-16
*Author:* Form.io Wizard
*URL:* https://form.io/ai/
*Description:* Governed AI coding and runtime infrastructure for Form.io (http://form.io/) teams, connecting agents to self-hosted forms, APIs, schemas, skills, and production guardrails.
Agentic Coding Meets Form.io
# AI Speed with Enterprise Control: The Same Engine for 10 Years
## The Governed Agentic Coding Toolset.
Let your coding agents move at full speed inside a data layer that enforces your standards by default. The governance enterprises have run on for a decade, now extended to every prompt and every agent.
## Schedule a Call → [View on GitHub](https://github.com/formio/ai)  Trusted by Government Healthcare Insurance Financial Services Universal Agent Gateway (UAG) is part of this toolset. Need the runtime-specific overview? [Explore UAG here →](https://form.io/uag) The Governed Agentic Coding Toolset Four tools. One contract. Build-time through runtime.
Purpose-built infrastructure for enterprise teams using AI coding agents in self-hosted environments. Standardize what agents do in development and govern what they do in production.
### MCP Server
Connects AI coding agents directly to your self-hosted Form.io deployment. Governed access to read, create, and scaffold the full data layer: forms, resources, actions, and APIs without pushing data outside your security boundary.
### Skills
Platform-specific guidance that teaches AI agents how to build on Form.io instead of improvising from scratch. Standardized, compliance-ready patterns get applied by default, so teams stop re-teaching enterprise rules prompt by prompt.
### Agentic Coding Plugin
Brings the MCP Server and Skills into the developer's coding environment. The Form.io plugin for Claude Code lets agents trigger tools and apply patterns from prompt context, so applications get built inside the workflow instead of stitched across disconnected systems.
### Universal Agent Gateway (UAG)
The runtime governance layer for production agentic workflows. It operates independently from the build-time toolset, giving enterprises a governed runtime surface: dynamic context, guardrails, and data access for AI agents in production.
## [View the Form.io AI Repo →](https://github.com/formio/ai) The Agentic Shift For Twenty Years, Human Time Was the Brake on Chaos. AI Just Removed It.
Engineers used to build slowly. That slowness was frustrating, but it was also the window to catch the drift before three teams shipped **three incompatible data models.**
AI took the brake off and now the speed is real as well as the chaos arriving behind it. Enterprises that leaned on human pace as their de facto standardization layer are discovering they never had a standardization layer at all.
The old reflex was to slow it down, look at it, and make it match. But that doesn't fit inside the timeline of AI speed. The only answer is an architecture where the standard pattern is already **the easiest path.**
 Form.io sits above the agentic layer The JSON schema isn't generated by an agent, but instead governs them. Your developers, your AI tools, and your downstream systems all work from the same instruction set. That's what standardization looks like in the agentic era: a governed data layer every tool in the stack has to honor.
## Repeatability Is Architectural Repeatability Must Be a Property of the Infrastructure, Not Merely a Process.
A style guide, a code-review checklist, a center of excellence with a wiki page nobody reads... these produce the appearance of standards without the property of repeatability, because they depend on human attention to enforce.
And AI just made human attention the scarcest resource in the building.
**If repeatability requires anyone (or any agent) to remember to do the right thing, it's isn't repeatable. It's aspirational.**
## 10+ **Years solving this exact problem**governed, schema-driven data infrastructure for enterprises that can't afford the alternative 1 **JSON schema as the single source of truth**the form, the API, the validation, the submission, and the audit trail all read from one contract 2 **Places AI touches your stack**build-time, where agents generate code; and runtime, where agents act on data in motion  One Definition. Every Surface. The Pattern Doesn't Care Who (or What) Is Building.
JSON schema as the single source of truth. The same property that made it repeatable for human developers makes it repeatable for AI. Extending it to agents was a question of surface, not of redesign.
The form, the API, the validation rule, the submission record, the audit trail — all reading from the same contract. Change the contract once; everything downstream sees the change. No translation step. No reconciliation week.
01 ### Agents build against real infrastructure.
The MCP Server gives AI coding agents governed access to your live Form.io deployment of forms, resources, actions, and APIs instead of fabricated demo data. They build against the system you actually run.
02 ### Standardize once. Generate consistently.
Skills carry your platform patterns into every prompt. Consistency is enforced at the infrastructure level, not the prompt level, so the standard pattern is the easiest path every agent takes.
03 ### Self-hosted, out of the box.
FIPS compliance, RBAC, self-hosted deployment, FedRAMP-ready infrastructure. AI access stays inside your security boundary. The data never leaves your compliance envelope.
04 ### Governed at runtime, not just build-time.
UAG keeps autonomous workflows inside the same governance envelope as the human ones. Agents authenticate, inherit real RBAC, and act on validated data, logged and auditable, every time.
05 ### Build inside your coding workflow.
The Agentic Coding Plugin brings the MCP Server and Skills into Claude Code. Developers keep their preferred interface while gaining governed access to Form.io infrastructure and reusable delivery patterns.
06 ### Auditable by design.
Dynamic context derived from a living schema, not a static skill file that goes stale the moment the schema changes. Every agent action is governed and traceable by the same contract your humans follow.
## Build-Time Governance For When AI Velocity Is Outrunning Your Standards
Agentic coding can accelerate delivery. It can also multiply architectural drift when every team and every agent improvises a different path. Form.io makes the governed path the default one.
Ungoverned agentic coding - Five teams solve the same problem five different ways
- Each agent makes different assumptions about data models
- Ungoverned access to forms, resources, actions, and APIs
- Every prompt starts from scratch with no reusable patterns
- Faster code, no way to explain how it was generated
- Compliance defaults re-litigated on every project
Building with the Form.io toolset - One JSON schema governs the data layer across teams
- Agents read the real definition: types, rules, constraints
- Governed access inside your own security boundary
- Skills apply standardized, compliance-ready patterns by default
- Every generated surface uses the Form.io pattern
- Standardize once; agents build on the foundation
"Speed to market using Form.io worked fantastically well. We didn't have to spend 80% of our time building our own solution and instead could focus our dev time on things proprietary to us."
## — Edify.ai Schedule a Call → Runtime Governance For When AI Agents Move From Prompts Into Production
Build-time acceleration alone isn't enough. Production agentic workflows need their own governance layer when AI actions move from a developer's prompt into live enterprise operations.
What production AI agents require - Access to real, governed data vs copies in a model
- Respect for existing RBAC and authentication
- Adherence to actual business rules and workflows
- Auditability over what an agent saw, did, and routed
- Integration with legacy and new systems alike
- Governance the CISO will actually approve
What the Universal Agent Gateway delivers - Agents authenticate like users and inherit real RBAC
- Dynamic context from a living schema, not a stale spec
- Every action validated through the same pipeline as humans
- Every interaction logged, authorized, and auditable
- Push and pull from existing systems via configured actions
- Released as MIT-licensed, self-hosted open source
"Unmatched capability in its product class, particularly for complex use cases where complete ownership of your data is a must."
— Midnight Health [Get the Open Source UAG Repo →](https://github.com/formio/uag) A Decade in the Hardest Rooms We didn't jump into AI from the sidelines. For years, enterprises have standardized mission-critical workflows on Form.io in the environments where **a data silo is a compliance liability.**
## GovCIO Convergence Dept. of Justice, Ireland publicplan One360 Bursting Silver Contentstack SkyFlow Strategic Systems Liberty Fox Technologies Why This Fits Form.io The Architectural Answer Has Been in the Room the Whole Time.
The same open, JSON-based foundation that works for human developers gives enterprises a stronger foundation for AI-driven delivery.
The enterprises that built repeatable data infrastructure before the AI moment are the ones whose agents can do useful work now. The ones who didn't have two options: build the layer, or ship faster and reconcile harder.
Labor used to be the brake on chaos. That brake is gone. The replacement is an architectural property making the standard pattern the easiest path at build-time and runtime, for humans and agents alike.
Schedule a Call → #### One schema, more control
A single JSON schema governs data-collection UIs, validation, workflow actions, data models, and auto-generated APIs with RBAC.
#### Self-hosted by design
Delivered inside your own environment, so build-time and runtime governance stay inside your security boundary.
#### Infrastructure, not lock-in theater
Form.io doesn't replace your stack. It gives developers and agents a governed data and workflow layer that fits your existing systems.
#### Build-time plus runtime
MCP Server, Skills, and the Plugin support development. UAG governs agentic workflows in production. One contract underneath both.
Under the Hood The architectural principle that separates Form.io from everything else AI agents build on.
## The schema is central to the product.
Form.io is a self-hosted, JSON-schema-driven data and application composition platform. Every form, every API, every data route, every validation rule is defined in and governed by a single JSON definition living in your infrastructure, under your control, connected to your systems.
That schema is what makes Form.io repeatable. Configure it once for a regulated deployment: RBAC, FIPS compliance, multi-tenancy, agentic workflow hooks... and that configuration travels.
This is why enterprises in government, financial services, and healthcare adopt it: because it's the governed foundation their AI agents can finally do useful work on.
The schema governs everything Human input → API routing → AI agent actions → downstream systems. One instruction set. One source of truth.
## Ready to move at AI speed without losing control?
The same engine, proven for over a decade, now extended to AI. Let's talk.
Schedule a Call →
---
# Enterprise Self Hosting Of Form.io—When Should You?
*Published:* 2024-06-12
*Author:* Form.io Wizard
*URL:* https://form.io/enterprise-self-hosting/
*Description:* Form.io deployed entirely inside the customer's IT environment. Customers achieve their own FedRAMP, HIPAA, and other compliance certifications on top of the platform — compliance attaches to the customer environment, not to a SaaS vendor.
[  ](https://form.io/audit-trail-software-enterprise-form-builders-with-native-sdlc/)Audit trail software sounds simple until the record being audited is not just a file, invoice, login, or database row.
Enterprise forms change. Submitted data changes. Validation rules change. Permissions change. Workflow actions fire. APIs read and update the same records that users see in the interface.
For regulated form workflows, the question is not only "Do we have logs?" It is "Can we prove what happened, who did it, what version of the form governed it, and whether the workflow moved through the right control path?"
## **What audit trail software has to prove**
Audit trail software creates a chronological record of activity inside a system.
At minimum, that record should help answer:
- Who performed the action?
- What changed?
- When did it happen?
- Which object, record, form, user, or system was affected?
- What context explains the change?
- Can the record be reviewed later without reconstructing it from guesswork?
That matters because audit trails are not only for after-the-fact compliance reviews. They are also useful for security monitoring, troubleshooting, workflow accountability, and incident investigation.
NIST's log management guidance treats logging as part of a broader cybersecurity evidence system. The draft [NIST SP 800-92 Rev. 1 Cybersecurity Log Management Planning Guide](https://csrc.nist.gov/pubs/sp/800/92/r1/ipd) treats logging as part of a broader cybersecurity evidence system.
Regulated systems make the point even more concrete. [21 CFR 11.10](https://www.law.cornell.edu/cfr/text/21/11.10) requires procedures and controls for closed systems that include secure, computer-generated, time-stamped audit trails for actions that create, modify, or delete electronic records, and it says record changes must not obscure previously recorded information. HIPAA's technical safeguards similarly include [audit controls](https://www.law.cornell.edu/cfr/text/45/164.312) for information systems that contain or use electronic protected health information.
That is the right starting point. Logs are evidence.
But enterprise form workflows need a more specific kind of evidence.
If a claims intake form changes, a patient referral submission is corrected, a public-sector application moves from draft to review, or an embedded customer form is updated through an API, a generic event log may not be enough. The system needs to preserve the relationship between the action and the form infrastructure that governed it.
## **Why enterprise forms need a different audit model**
A form in an enterprise application is not just a page.
It can be:
- a user interface
- a JSON schema
- a validation contract
- a submission model
- a generated API
- a workflow trigger
- a permission boundary
- a document-generation source
- a long-term record
That is why auditability gets harder when forms become application infrastructure.
A simple audit log might show that a user updated a record at 2:14 PM. That is useful, but it does not answer every question an auditor, compliance team, or engineering lead may ask later.
For example:
- Which form version was active when the user submitted the record?
- Did the form have the same required fields then that it has now?
- Was the submitted value changed after capture?
- Was there a documented reason for the change?
- Did a webhook, email, approval action, or downstream integration fire?
- Did the change happen in development, staging, or production?
- Did the API update follow the same permission rules as the portal update?
Those are form-infrastructure questions, not just logging questions.
IBM's 2025 [Cost of a Data Breach Report](https://www.ibm.com/reports/data-breach) puts the global average breach cost at $4.4 million and reports that 63% of organizations lacked AI governance policies. That statistic is not form-specific, but it gives the right scale for the decision. When sensitive data workflows are hard to trace, the risk is not cosmetic.
For enterprise forms, the audit model has to cover both sides of the system: the form definition and the submitted data.
## **The four audit layers enterprise form builders should support**
Most form tools can tell you that a submission exists.
Enterprise form infrastructure needs to tell a deeper story.
### **1. System activity and access logs**
The first layer is the system-level audit log.
This is the record of access, authentication, API requests, data reads, data writes, and other platform activity. It answers questions like:
- Who viewed this submission?
- Who authenticated?
- Which API request changed the record?
- Which project, form, or user was involved?
- Did a request fail?
- Can related events be correlated?
Form.io's [audit logging documentation](https://help.form.io/dev/audit-logging) describes a system-level audit log format with date, event, UUID, project ID, session ID, user ID, and event-specific context. The docs also state that audit logs output to standard out for the Docker container and can be routed into a log aggregation system.
Another note: high-volume system logs should not necessarily store complete submission payloads inside every event. Sensitive form values may need a different audit mechanism than API access events.
The right audit design separates broad activity logging from field-level revision history, then lets teams correlate the two when they need to investigate.
### **2. Form revisions**
The second layer is form revision history.
Enterprise forms change over time. Teams add fields, remove fields, rename fields, update validation rules, change conditional logic, revise consent text, and adjust workflow requirements.
If the form changes after a record is submitted, the system still needs to explain what the form looked like when the record was captured.
Form.io's [Form Revisions documentation](https://help.form.io/userguide/forms/form-revisions) is built for that problem. Form Revisions let teams preserve form versions as forms evolve and can display submission data in the form revision that captured it. The revision interface also exposes who made a revision, when the revision was made, the revision number, and revision notes.
That distinction is central to auditability.
If an auditor reviews a historical submission, the question is not only "What data is in the record now?" It is also "What fields, labels, rules, and structure governed the user when the record was created?"
Without form revision history, teams often have to reconstruct that context from release notes, screenshots, old code, or database backups. That is fragile.
### **3. Submission revisions**
The third layer is submission revision history.
This is the field-level history of changes to submitted data after initial capture.
A submitted form might be corrected by a staff member. A patient record might need an updated value. A claims workflow might need a revised amount. A government service application might need a supporting detail added after review.
In those cases, the system needs to preserve the previous state, the new state, the user who made the change, the time of the change, and any revision note explaining why the change happened.
Form.io's [Submissions documentation](https://help.form.io/userguide/submissions) describes Submission Revisions as an audit logging capability that tracks who updated a submission, when the change was made, and notes associated with the update. The documentation also says the PDF change log can include the revision ID, updating user, date and time, revision note, and list of revision changes.
That is the difference between editing a record and governing a record.
An edit changes the current value. A revision trail preserves the accountable history behind that value.
### **4. Stage, action, and deployment history**
The fourth layer is the SDLC layer.
For enterprise form teams, auditability is not limited to runtime activity. It also includes how form definitions, resources, roles, and actions move through development, staging, and production.
Form.io's [Stages documentation](https://help.form.io/userguide/projects/stages) describes stages as a way to isolate project forms and resources for form management between different environments. The same documentation frames a typical enterprise workflow around Live, Authoring, QA/Test, and Development stages.
That matters because regulated teams often need controlled promotion.
They need a place to build and test form changes before production. They need to know which form version moved forward. They need to avoid ad hoc edits that change production behavior without review. This should not be inflated into a claim that Form.io replaces a full CI/CD or release-management system for all application code. The narrower point is still valuable: form configuration has its own lifecycle, and enterprise teams need a controlled way to manage it.
Audit trail software that ignores the lifecycle layer misses a major part of the form governance problem.
## **A practical comparison framework**
The right audit trail software depends on what kind of system you are auditing.
**Category****Best fit****What it proves****Where it can fall short for enterprise forms**Generic audit log toolingBroad system activity, application events, operational monitoringWho did what, when, and where across systemsUsually does not understand form schema versions or submission-level change historyCompliance audit management toolsPolicy controls, audit programs, evidence management, compliance workflowsWhether controls exist and evidence was collectedOften manages audit process, not the runtime form record itselfAccounting or finance audit trail toolsFinancial transactions, invoices, approvals, accounting changesTransaction history and financial accountabilityUsually narrow to finance workflowsBasic form builders with logsSimple submissions, admin edits, response exportsBasic submission history and account activityMay not preserve form schema history, API-level activity, or stage promotionCustom-built audit trailHighly specific internal applicationsWhatever the team designs and maintainsExpensive to build, test, secure, document, and keep consistent across formsForm infrastructure with native audit controlsRegulated form workflows, embedded forms, generated APIs, long-lived submissionsSystem activity, form revisions, submission revisions, permissions, actions, and stage movementRequires technical ownership and a clear governance modelThe key is fit.
If your team only needs a basic activity log for a contact form, enterprise form infrastructure is probably too much. If your team is managing high-value workflows where form definitions and submitted data both matter, the audit model needs to be native to the form platform.
## **Where Form.io fits**
Form.io is strongest when the form is part of the application infrastructure.
That usually means a team needs some mix of [self-hosted form deployment](/features/self-hosted-forms-for-enterprise/), embedded forms, generated APIs, permissions, workflow actions, form revisions, submission revisions, audit logging, and environment promotion.
The reason is architectural.
Form.io forms and resources are JSON-driven definitions that can render user interfaces, generate APIs, validate submissions, store submitted data, and participate in roles, permissions, actions, stages, and revisions.
That makes auditability part of the same system that owns the form workflow.
[The Security Module](/features/secure-forms-compliance-readiness/) bundles advanced audit logging, action logs, form revisions, submission revision logs, submission collections, and container security scanning. The [complete audit trail feature](/features/log-forms-complete-audit-trail/) separates system-wide audit logs from field-level submission revisions, which is the right separation for high-volume enterprise workflows. The [Form Revisions feature](/features/form-revisions-form-json-schema/) preserves form JSON schema versions so historical submissions can remain explainable as forms evolve.
Form.io also matters when APIs are part of the record. A form workflow may be updated through the portal, an embedded application, or a generated API. The buyer should not have to accept one audit posture for the UI and another for API-driven operations.
That is why generated APIs are relevant to audit trail software. Form.io's [form API model](/features/form-api/) lets teams treat forms and resources as API-connected infrastructure, not isolated web pages. Permissions, submissions, and actions then sit closer to the form data model.
This is also where customer proof matters. [G2's Form.io review page](https://www.g2.com/products/form-io/reviews) describes the platform as deployable into on-premise or private cloud environments, giving customers control of submission data. One enterprise reviewer summarized the practical product experience this way: "Form.io is an intuitive, developer-friendly framework that provides excellent data management." That is not an audit claim by itself. It is buyer proof for the control-and-customization posture that makes audit-heavy form infrastructure worth evaluating.
## **When simple audit logging is enough**
Not every workflow needs all of this.
Simple audit logging may be enough when:
- The form is short-lived.
- Submitted data is low risk.
- Responses are rarely edited after capture.
- The form schema rarely changes.
- The form is not embedded into a regulated application.
- There is no need for DEV/STAGE/PROD promotion.
- Exports are enough for downstream systems.
- The audit question is limited to account activity or submission timestamps.
In those cases, a lighter form builder, basic form backend, or general application log may be a better fit.
The mistake is keeping that model after the workflow becomes infrastructure.
Once forms drive eligibility, claims, intake, onboarding, financial review, patient workflows, public-sector services, insurance applications, or internal approvals, the audit trail has to explain more than "a record changed."
It has to explain the governed context around the change.
## **Evaluation checklist for audit trail software in form workflows**
Use these questions before choosing a form platform for an audit-heavy workflow.
### **Does the platform track system-level activity?**
Look for access events, authentication events, API requests, data reads, data writes, request correlation, and log export options.
### **Does it preserve form schema versions?**
If a field, validation rule, label, or conditional path changes, the platform should preserve enough form history to explain historical submissions.
### **Does it preserve submitted-data history?**
Submission revisions should show who changed a value, when it changed, what changed, and why.
### **Can historical submissions render against the original form version?**
This matters when auditors, legal teams, or operations teams need to understand what a user actually saw at capture time.
### **Are workflow actions included in the governance model?**
Actions such as emails, webhooks, approvals, PDF generation, and save-to-resource operations can affect the record. They should not be invisible.
### **Can forms move through controlled stages?**
Enterprise teams need a way to test, version, and promote forms, resources, roles, and actions without treating production as the editing surface.
### **Do permissions apply close to the form and submission model?**
[Form permissions](/features/form-permissions/) matter because different people may be allowed to create, read, update, delete, approve, or export different records.
### **Can the platform run inside the required deployment boundary?**
Self-hosting does not automatically make a system compliant. It does let the customer place the form platform inside the environment, monitoring, identity, logging, and operational controls the organization already governs.
### **Are forms still usable for builders and developers?**
Audit controls only help if the team can still build and maintain the workflow. A usable [form builder](/features/form-builder/) and a clear [JSON-powered form model](/features/json-powered-forms/) reduce the temptation to route around governance.
## **Key takeaways**
- Audit trail software is not only a logging feature when forms become application infrastructure.
- Enterprise form workflows need evidence across system activity, form revisions, submission revisions, workflow actions, permissions, and stage promotion.
- Generic logs can show that something happened. Form infrastructure should show what version of the form governed the record when it happened.
- Form.io fits best when the form schema, generated API, submitted data, and governance controls need to stay connected.
- The right buyer is not looking for the lightest form tool. They are looking for a form platform that can defend the record later.
## **FAQ**
### **What is audit trail software?**
Audit trail software records system activity in chronological order so teams can review who performed an action, what changed, when it happened, and which record or system was affected.
### **Why do enterprise forms need audit trails?**
Enterprise forms often collect data that drives decisions, approvals, compliance records, customer onboarding, claims, patient workflows, government services, or financial review. If the record changes later, the organization needs evidence of what happened.
### **What is the difference between an audit log and a submission revision?**
An audit log records system-level activity such as access, authentication, API requests, and data modification events. A submission revision preserves field-level history for a specific submitted record.
### **What is the difference between form revisions and submission revisions?**
Form revisions track changes to the form schema: fields, validation rules, conditional logic, layout, and related form structure. Submission revisions track changes to submitted data after capture.
### **Why does form versioning matter for audit trails?**
Form versioning helps explain historical records. If a submission was captured under an older form version, the team may need to review the exact schema, fields, labels, and validation rules that governed that submission.
### **Does self-hosting make audit trail software compliant?**
No. Self-hosting gives the organization more control over deployment, data, logs, identity, monitoring, and infrastructure. Compliance still depends on configuration, policy, controls, documentation, and review.
### **Should audit trail software store every field value in every log?**
Not always. High-volume system logs can become expensive and sensitive if they store full payloads in every event. A better model often separates system audit logs from field-level submission revisions.
### **What should regulated teams look for in form audit trails?**
They should look for system audit logs, form revisions, submission revisions, permissions, workflow/action evidence, stage promotion, exportable evidence, and deployment control.
### **Can generic log management replace native form revision history?**
Generic log management can help centralize and review system events, but it usually does not understand form schema versions, submission rendering, or field-level form data history unless the application sends that context deliberately.
### **When is Form.io a good fit for audit-heavy forms?**
Form.io is a good fit when forms are part of a larger application workflow and the team needs [form workflows](/features/form-workflows/), generated APIs, permissions, revisions, submission history, and customer-controlled deployment.
### **When is Form.io probably too much?**
Form.io may be more platform than needed for a simple contact form, survey, or lead-capture page where the data is low risk and the audit requirement is limited to basic timestamps or account activity.
## **Build audit-ready form infrastructure with Form.io**
# Web Form Builder: When Online Forms Need APIs, Workflows, and Self-Hosted Control
[  ](https://form.io/web-form-builder-apis-self-hosted-control/)A web form builder sounds like a simple category until the form becomes part of a real application. A contact form, signup form, or feedback survey can live in a lightweight tool. A regulated intake process, embedded customer workflow, or API-connected business process needs more than fields on a page.
That is where the buying question changes.
## **What a Web Form Builder Should Do**
A web form builder is software for creating forms users can complete in a browser. At the basic level, it should let a team create fields, set required answers, publish a form, collect submissions, and send the data somewhere useful.
For many teams, that is enough.
Zapier's long-running online form builder list shows how the broad market is usually framed: quick form creation, automation, advanced logic, conversational form experiences, AI-assisted building, Excel sync, approval flows, and reporting options ([Zapier](https://zapier.com/blog/best-online-form-builder-software/)). That is the default expectation buyers bring to the phrase.
The problem is that "web form builder" covers several different jobs:
- a marketing team collecting leads
- an operations team routing internal requests
- a product team embedding forms inside a SaaS application
- a healthcare, insurance, finance, or government team collecting sensitive data
- a development team using forms as part of an API-backed workflow
Those jobs should not be evaluated with the same checklist.
If the form is only a standalone page, the most important questions are speed, templates, design, notifications, and basic integrations. If the form is part of application infrastructure, the questions become more serious: who owns the schema, where does submission data live, what APIs exist, how validation runs, what happens after submit, and whether the platform can operate inside the customer's environment.
## **When a Simple Web Form Builder Is Enough**
A simple web form builder is a good fit when the form is low-risk, isolated, and easy to replace.
Use a lightweight tool when:
- the form collects basic marketing or event information
- submissions can live in the vendor's hosted system
- exporting to a spreadsheet is acceptable
- the workflow after submission is simple
- there are no unusual data residency or deployment requirements
- the form is not deeply embedded in a product experience
- developers do not need to treat the form as an API-backed component
In that world, the best tool is often the fastest tool your team will actually use. A simple builder can be the right decision for a campaign, a workshop signup, a small survey, or a basic internal request.
The mistake is keeping that same mental model after the requirements change.
## **Where Web Form Builders Start To Break Down**
Web forms become harder when the submission is not the end of the process.
A user submits an intake form. Then the data has to create a case, trigger a review, update a CRM, route to a queue, generate a PDF, notify a downstream system, enforce role-based access, or become part of a customer-facing application.
At that point, the form has a second job. It is no longer just collecting answers. It is becoming the front door to a process.
The breakdown usually shows up in five places.
### **The Data Model Lives Somewhere Else**
Many web form builders make it easy to create fields, but the real application data model lives outside the form tool. That creates drift. A field is required in the form but optional in the backend. A dropdown changes in the builder but not in the API. A validation rule exists in the browser but not server-side.
This is small until the form becomes important.
Then every disconnected rule becomes a place where bad data can enter the system.
### **Integrations Become Workflow Logic**
Basic integrations are helpful. They send a notification, create a spreadsheet row, add a CRM contact, or post to a collaboration tool.
But integration is not the same as workflow ownership.
Enterprise forms often need conditional routing, retries, identity context, external IDs, error handling, and clean handoff to other systems. Form.io's webhook documentation, for example, treats a submission as a payload that can call an external API, map response IDs back to the submission, and optionally wait for the webhook response before continuing actions ([Form.io webhook actions docs](https://help.form.io/form-building/actions/webhook-actions)).
That is a different requirement than "send this form to a spreadsheet."
### **Security And Compliance Become Architecture Questions**
The more sensitive the data, the less acceptable it is to treat the form builder as a detached SaaS box.
IBM's 2025 Cost of a Data Breach Report puts the global average breach cost at USD 4.4 million ([IBM](https://www.ibm.com/reports/data-breach)). That statistic should not be used to scare every team away from hosted tools. It should remind buyers that data capture is part of the security boundary.
For sensitive forms, the evaluation should include:
- where submissions are stored
- who administers the environment
- how access is controlled
- how data moves between systems
- how logs, evidence, and audit needs are handled
- whether the form platform can live inside the organization's deployment model
Self-hosting does not automatically make a system compliant. It gives the organization more control over the environment where compliance controls are implemented and reviewed.
### **Product Teams Need Embedding, Not Just Publishing**
Publishing a hosted form is not the same as embedding a form builder into a product.
If a B2B SaaS team wants customers to create or manage their own forms inside the application, the builder has to respect the product's authentication, permissions, tenant boundaries, styling, and data model. That is closer to an embedded product capability than a public web form.
This is why Form.io's [Enterprise Form Builder Module](https://form.io/features/enterprise-form-builder-module/) matters for platform teams. The point is not only that a user can drag fields onto a canvas. The point is that a company can provide a white-labeled, pre-wired form-building experience inside its own application.
### **Developers Need A Stable Contract**
Developers can work around almost anything once. The cost shows up when every new form requires custom backend glue.
A stronger web form builder for application teams should create a stable contract between the form, the submission record, the API, validation, permissions, and downstream systems.
Form.io's own project documentation says that when a new form is created, a REST API is automatically generated to serve as the backend for the form and for other systems that need to create submissions ([Form.io project docs](https://help.form.io/admin/projects/creating-a-project)). That is the key architectural distinction: the form is not only a UI artifact. It is part of the API surface.
## **A Web Form Builder Evaluation Checklist**
Before choosing a web form builder, separate the easy questions from the questions that determine long-term fit.
Evaluation AreaLightweight Form NeedInfrastructure-Grade Form NeedBuilderDrag-and-drop fields, templates, brandingConfigurable builder, reusable schemas, controlled componentsDataHosted submissions and exportsStructured submission records with API accessWorkflowNotifications and simple integrationsWebhooks, Actions, retries, external IDs, routingValidationClient-side rules and required fieldsSchema-linked validation across UI and server pathsEmbeddingPublic link or iframeNative application embedding and white-label controlDeploymentVendor-hosted SaaSHosted, private cloud, on-premises, or local deployment optionsGovernanceAdmin settingsRoles, permissions, stages, evidence, and environment controlFitCampaigns, surveys, simple intakeProduct workflows, regulated intake, internal systems, multi-tenant SaaSThis checklist prevents a common buying mistake: choosing the easiest form tool for the first version, then rebuilding the entire intake layer once the forms become operationally important.
## **Why APIs Change The Category**
APIs change a web form builder from a page-building tool into an application component.
Without APIs, the form is mostly a destination. Users go there, submit data, and the team exports or forwards the result.
With APIs, the form can become part of the system:
- applications can create and read submissions
- forms can populate fields from external data
- downstream systems can consume structured payloads
- teams can build reporting, review, and workflow layers on top of submission records
- developers can integrate forms into products without treating each one as a one-off project
Form.io's [data integration tools](https://form.io/features/data-integration-tools-for-enterprise-forms/) positioning makes this point directly: forms, resources, submissions, and projects are accessible through REST APIs. The practical value is not just "there is an API." It is that the form builder, schema, submission data, and integration surface are part of the same model.
That matters when teams are building internal tools, partner portals, insurance workflows, healthcare intake, public-sector services, or SaaS onboarding flows.
The user sees a web form. The architecture sees a contract.
## **Why Deployment And Data Control Matter**
Deployment is one of the clearest dividing lines between a simple web form builder and enterprise form infrastructure.
If the form is low-risk, vendor-hosted SaaS is usually fine. If the form handles regulated data, internal process data, customer application data, or data that has to move through controlled systems, deployment becomes part of the buying decision.
Form.io's deployment documentation says the platform can be installed in cloud environments, on-premise data centers, or local machines, and that enterprise deployments can use multi-environment architecture across private cloud or on-prem environments ([Form.io deployment overview](https://help.form.io/deploy/deployment-overview)). Its on-premises deployment documentation frames on-prem as relevant when infrastructure, compliance, or data-security requirements call for that model ([Form.io on-premises deployment docs](https://help.form.io/deploy/on-premises-deployment)).
This does not make Form.io the right fit for every form.
It makes Form.io relevant when the form layer has to live where the rest of the application lives.
For teams with strict environment rules, that is often the real requirement hiding underneath the phrase "web form builder." They are not only asking for a form canvas. They are asking whether the form system can respect their data boundary, deployment model, access controls, and integration paths.
## **Where Form.io Fits**
Form.io is a stronger fit when the form is part of an application, not just a standalone collection page.
The core difference is that Form.io combines a [drag-and-drop form builder with APIs](https://form.io/features/drag-and-drop-form-builder-apis/). Teams can design forms visually while keeping the underlying structure available as JSON and exposed through generated REST APIs.
That combination is useful when:
- developers need forms embedded in a product
- business users need controlled form authoring
- submissions need to be available through APIs
- workflows need webhooks or server-side actions
- the organization needs self-hosted or on-premises deployment
- forms need to share a governance model with the surrounding application
Form.io is not the best answer when a team only needs a quick public survey or a simple contact form. That buyer should choose the fastest lightweight tool that fits the job.
But when a web form builder has to support real application infrastructure, the decision changes. The value is not only the builder UI. It is the connection between form schema, submission data, generated APIs, deployment control, and workflow actions.
Customer language points to the same distinction. A Trustpilot reviewer described Form.io as useful "for integration and standalone" work ([Trustpilot](https://www.trustpilot.com/review/form.io)). A Form.io case study customer put the infrastructure burden more bluntly: Form.io "cleans up all the dirty work" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)).
That is the real category line.
A basic web form builder helps a team make a form. Form.io is for teams that need the form to become a governed part of the application.
## **Key Takeaways**
- A web form builder can mean anything from a simple contact form to an embedded application workflow.
- Lightweight tools are a good fit when forms are low-risk, standalone, and easy to replace.
- Enterprise teams should evaluate APIs, validation, submissions, workflow actions, permissions, and deployment control.
- Form.io fits when the form layer needs to operate as controlled application infrastructure, not just a hosted form page.
- Self-hosting is not a compliance shortcut; it is a control model for teams that need to own the environment.
## **FAQ**
### **What Is A Web Form Builder?**
A web form builder is software for creating forms that users complete in a browser. Basic builders focus on fields, templates, publishing, notifications, and exports. More advanced builders support APIs, workflows, permissions, embedding, and controlled deployment.
### **What Is The Difference Between A Web Form Builder And An Online Form Builder?**
The terms often overlap. "Online form builder" usually points to hosted SaaS tools for creating and publishing forms quickly. "Web form builder" can mean the same thing, but it is also used by product and development teams looking for embeddable form-building inside a web application.
### **When Is A Basic Form Builder Enough?**
A basic form builder is enough when the form is low-risk, standalone, and does not need deep integration with internal systems. Examples include event registration, simple lead capture, small surveys, and basic internal requests.
### **When Does A Web Form Builder Need APIs?**
A web form builder needs APIs when other systems must create, read, update, route, or report on submissions. APIs matter when forms are part of a product, portal, approval workflow, regulated intake process, or internal system of record.
### **Why Does Form Schema Matter?**
The schema defines the form's structure and behavior. In a schema-driven model, the same definition can support rendering, validation, submissions, APIs, workflow actions, and governance. That reduces drift between what the user sees and what the backend expects.
### **Can A Web Form Builder Be Self-Hosted?**
Some web form builders are hosted-only. Form.io supports self-hosted deployment models, including cloud, on-premises, and local environments according to its deployment documentation. That matters when the organization needs control over hosting, network boundaries, data storage, and operational review.
### **Is Self-Hosting The Same As Compliance?**
No. Self-hosting gives the customer more control over the environment, but compliance still depends on configuration, policies, controls, monitoring, documentation, and the broader system boundary. The value is control, not a shortcut around responsibility.
### **Why Would A SaaS Product Need An Embedded Form Builder?**
A SaaS product may need customers or internal teams to create forms inside the product itself. In that case, the builder has to respect tenant boundaries, authentication, permissions, styling, and data storage. A public form link is not enough.
### **How Is Form.io Different From A Simple Form Tool?**
Form.io is built for teams that need forms, submission data, generated APIs, workflow actions, and deployment control together. It can still provide a drag-and-drop builder, but the stronger reason to use it is when forms need to operate inside application infrastructure.
## **Build Web Forms That Fit Your Application Architecture**
# E Signature Software for Self-Hosted Form Workflows: DocuSign Alternatives for Enterprise Control
[  ](https://form.io/e-signature-software-self-hosted-form-workflows/)E signature software is usually evaluated as a document workflow tool: send a PDF, collect a signature, store an audit trail, and move on.
That is enough for many contracts. It is not enough when the signature is attached to regulated intake, eligibility data, consent records, financial applications, healthcare workflows, or other form submissions that must stay inside your application boundary.
The better question is not only, "Can this document be signed?" It is, "Can we defend the signed record later, with the data, schema, context, and audit trail intact?"
## **What E Signature Software Usually Solves**
Most e signature software helps teams replace wet signatures with an electronic signing process. The standard workflow is familiar: upload a document, place signature fields, route it to signers, authenticate the signer, collect consent, and retain a completed envelope.
That category is large because the paper problem is large. [Grand View Research estimated](https://www.grandviewresearch.com/industry-analysis/digital-signature-market-report) the global digital signature market at USD 6.9 billion in 2025 and projected a 43.9% CAGR from 2026 to 2033.
But market size does not tell you which architecture fits your use case.
Standalone signing platforms are strongest when the signed artifact is the document itself: contracts, sales agreements, HR forms, procurement packets, vendor agreements, and legal paperwork. In those cases, the system of record is often the completed document package.
Form-driven applications are different. The signed evidence may need to stay attached to a submission record, user identity, form version, field values, workflow state, API transaction, and downstream system update.
That is where a normal e-signature checklist starts to miss the real buyer risk.
## **Why DocuSign Alternatives Become Relevant**
DocuSign is the name many buyers know first. Adobe, Dropbox Sign, PandaDoc, Zoho Sign, OneSpan, and other tools also belong in the traditional e-signature conversation.
Those tools can be the right choice when your team mainly needs a document-signing workflow. The mistake is assuming that the best document-signing platform is automatically the best signing architecture for application data.
Teams start looking for DocuSign alternatives when one or more constraints appears:
- signature data must stay inside a private cloud, VPC, on-premise, or controlled deployment boundary
- the signed record begins as structured form data, not a static PDF
- signer consent needs to connect to the exact fields and submission context that were signed
- APIs, webhooks, roles, permissions, and audit history matter as much as the visual signature
- pricing or operations become hard to forecast when signatures scale across many workflows
For these teams, the word "alternative" does not simply mean cheaper. It means architecturally different.
## **The Enterprise Evaluation Criteria**
Before choosing e signature software, separate legal acceptance from operational evidence.
The U.S. [ESIGN Act](https://uscode.house.gov/view.xhtml?edition=prelim&path=%2Fprelim%40title15%2Fchapter96) says electronic signatures and records generally cannot be denied legal effect solely because they are electronic. It also points to record retention: electronic records must remain accurate, accessible, and reproducible for later reference.
That retention point matters. A signature event is only as useful as the record your team can reproduce when someone asks what was signed, by whom, under which form version, with which field values, and under which business process.
Evaluate each platform across six criteria.
**Criterion****Why it matters**Deployment controlDetermines where sensitive data, signature proof, and operational evidence live.Record modelShows whether the signed artifact is a PDF envelope, a submission record, or both.Audit trailCaptures the evidence needed to defend the transaction later.API accessDetermines whether signatures can participate in application workflows.Identity and access controlsConnects signing to the right user, role, tenant, or workflow boundary.Pricing modelDetermines whether cost scales predictably across high-volume workflows.The wrong platform can still collect a signature. The problem appears later, when the team needs to prove what the signature means inside the larger system.
## **Where Self-Hosted Form Workflows Change The Question**
Self-hosted form workflows change the center of gravity.
Instead of asking, "Which e-signature vendor should host this envelope?" the team asks, "How do we keep the signed record inside the same infrastructure that owns the form, data, APIs, permissions, and audit history?"
That shift matters for regulated teams, embedded SaaS products, government contractors, healthcare platforms, insurance workflows, financial services onboarding, and internal enterprise portals.
The signature is not a decorative mark. It is a control point in the data lifecycle.
NIST's [digital signature project](https://csrc.nist.gov/projects/digital-signatures) frames digital signatures around generation, verification, and data protection. That distinction is useful for buyers: a visible signature image is not the same thing as verifiable proof that the protected data and context have not changed.
In a form workflow, the strongest signature system should answer questions like:
- Which form version captured the data?
- Which fields were protected by the signature?
- Did the data change after signing?
- Can the application verify the signature through an API?
- Does the signed record remain inside the customer's environment?
- Can the team reproduce the record without depending on a third-party envelope as the only source of truth?
Those are infrastructure questions, not just signing questions.
## **How Form.io E-Sign+ Fits**
[Form.io E-Sign+](/features/cryptographic-e-signatures-for-form-data/) is built for a narrower, more controlled version of the e-signature problem: cryptographically secure signatures associated with Form.io submission data inside the customer's own environment.
That is a different posture than a standalone document-signing workflow.
With Form.io, the [form schema and submission data](/form-json-schema-vs-submission/), generated APIs, permissions, workflow actions, and deployment boundary are already part of the application infrastructure. E-Sign+ extends that infrastructure by letting teams verify signed submission data and context rather than treating the signature as only a PDF-layer event.
The [product documentation](https://help.form.io/dev/integrations/e-sign%2B) describes E-Sign+ as tied to submission data, usable through native submission IDs, and decoupled from PDFs. It can protect selected fields, all form data, and/or submission properties, depending on configuration.
That makes Form.io a strong fit when the signature needs to travel with application data.
Form.io's broader customer proof reinforces the infrastructure value. One customer quote on [Form.io's homepage](https://form.io/) says, "Speed to market using Form.io worked fantastically well," because the team did not have to spend most of its time building its own solution. Another proof point describes cutting data-processing workload by 50%.
Those quotes are not E-Sign+ specific. They do show the larger pattern: Form.io is strongest when teams need to stop rebuilding form, data, API, and workflow plumbing from scratch.
## **E Signature Software Comparison**
**Best fit****Typical tools****Watch the tradeoff**Standard document signingDocuSign, Adobe Acrobat Sign, Dropbox Sign, PandaDoc, Zoho SignStrong for envelopes and documents, but not always ideal when signed evidence must remain attached to application-owned submission data.Developer signing APIsAPI-first signing platformsFlexible for document workflows, but your team still owns the surrounding form schema, data model, and governance path.Self-hosted form signing infrastructureForm.io E-Sign+Strong fit when forms, submissions, APIs, permissions, and signature verification need to stay in the customer's controlled environment.The point is not that every team should leave document-signing platforms. Many should not.
The point is that e signature software has to match the record you are actually signing.
If the record is a contract document, a document-signing tool may be enough. If the record is a governed application submission, the signature belongs closer to the form infrastructure.
## **Key Takeaways**
- E signature software is a broad category, but enterprise form workflows need more than a signed PDF.
- Legal validity is only one part of the evaluation. Record retention, reproducibility, and context matter.
- DocuSign alternatives become relevant when teams need deployment control, API access, data ownership, or application-level signature proof.
- Form.io E-Sign+ fits teams that need cryptographic signature verification tied to submission data inside their own environment.
- The stronger question is not "Which tool signs documents fastest?" It is "Which system protects the signed record your application actually depends on?"
## **FAQ**
### **What Is E Signature Software?**
E signature software lets people sign electronic records or documents without printing and scanning paper. In business workflows, it usually includes signer routing, authentication, consent capture, audit history, completed document storage, and API or integration options.
### **Is E Signature Software Legally Binding?**
Electronic signatures can be legally valid in many contexts, including under the U.S. ESIGN Act and [EU eIDAS rules](https://ec.europa.eu/digital-building-blocks/sites/spaces/DIGITAL/pages/467109069/What%2Bis%2BeSignature). Buyers should still review the specific transaction type, jurisdiction, identity process, consent language, retention rules, and audit evidence with legal counsel.
### **What Is The Best DocuSign Alternative?**
The best DocuSign alternative depends on the job. If the job is standard document signing, a standalone signing platform may fit. If the job is signing structured form submissions inside a controlled application, Form.io E-Sign+ is worth evaluating because the signature proof stays closer to the form data and API workflow.
### **When Should A Team Choose Self-Hosted E Signature Software?**
A team should consider self-hosted signing infrastructure when sensitive submission data, regulatory obligations, customer architecture, data residency, or private deployment requirements make third-party-hosted signing workflows difficult to justify.
### **How Is Form.io E-Sign+ Different From A PDF Signature Tool?**
Form.io E-Sign+ is designed around submission-linked signature proof. PDFs can still be part of a workflow, but the stronger distinction is that E-Sign+ can verify signed form data and context inside the customer's own [self-hosted Form.io environment](/enterprise-self-hosting/).
### **Does Form.io Replace DocuSign?**
Not for every use case. DocuSign is a strong document-signing platform. Form.io is a stronger fit when signatures are part of a governed form workflow, embedded application, or self-hosted data pipeline where submission context matters.
### **What Should Enterprises Look For In E Signature Software?**
Enterprises should evaluate deployment control, signer identity, audit trail quality, API access, retention and reproducibility, [configuration-based pricing](/configuration-based-pricing/), integration fit, and whether the signed record is a document envelope or application data.
### **Can E Signature Software Work With APIs?**
Yes. Many signing platforms provide APIs, but the important question is what the API controls. For form-driven applications, APIs should connect signatures to submission records, permissions, workflow state, and downstream systems.
### **Why Does Signature Context Matter?**
Signature context matters because a signature without the surrounding record can be hard to defend. Teams may need to know the form version, field values, signer identity, submission ID, timestamp, protected fields, and whether anything changed after signing.
### **How Does Form.io Help With Controlled Form Workflows?**
Form.io gives teams [form management infrastructure](/form-management-software/) for forms, submissions, generated APIs, permissions, workflow actions, and self-hosted deployment. E-Sign+ extends that model by connecting signature verification to submission data instead of treating signing as a disconnected document event.
## **Build Signature Proof Into Your Form Infrastructure**
If your team needs signatures that stay attached to governed form data, application APIs, and your own deployment boundary, [try Form.io for self-hosted form workflows](/try-formio-for-free/).
# JSON Schema Validator Tools for Production Apps
[  ](https://form.io/json-schema-validator-tools-production-apps/)Searches for **json schema validator** often start with a simple need: check whether this JSON payload matches this schema.
That is useful. It is also only the first layer.
In a production app, a schema may validate API requests, generate a form, drive documentation, define a submission shape, feed an AI tool, or become part of a governed application contract. The right tool depends on which job the schema has to do.
## **Key takeaways**
- A JSON Schema validator checks whether JSON data conforms to a declared structure, types, required fields, constraints, and references.
- Online validators are useful for quick checks, but production teams usually need runtime libraries, CI checks, API contract tooling, or form infrastructure.
- Ajv, Python `jsonschema`, and Java validators solve the library problem. They do not own form authoring, submissions, permissions, or deployment governance.
- Form generators turn schema into UI, but the backend still has to store, secure, expose, and govern submitted data.
- Form.io fits when schema needs to become form and API infrastructure: builder, renderer, submissions, generated APIs, permissions, workflow actions, revisions, and customer-controlled deployment.
## **Quick answer: which JSON Schema validator tool should you use?**
Use an online validator when you need to test a small schema and sample payload quickly.
Use Ajv when your JavaScript or TypeScript application needs fast JSON Schema validation in Node.js, the browser, an API gateway, or a build process.
Use Python `jsonschema` when your Python services need to validate instances against JSON Schema drafts and report validation errors in application code.
Use a Java validator such as NetworkNT when JSON Schema validation belongs in a JVM service, API layer, or request/response validation path.
Use Spectral or a schema lifecycle tool when the problem is not one payload, but API governance, linting, bundling, testing, and CI.
Use RJSF, JSON Forms, or SurveyJS when the goal is to generate a form interface from structured schema.
Use Form.io when the schema must become production form infrastructure: a human-facing form, submission record, generated REST API, workflow surface, permission boundary, and governed deployment model.
## **What a JSON Schema validator actually proves**
JSON syntax validation and JSON Schema validation are different jobs.
A JSON syntax validator answers: is this valid JSON?
A JSON Schema validator answers: does this valid JSON match the structure and rules the application expects?
That can include object shape, required fields, string formats, numeric ranges, enum values, array constraints, nested objects, and references to other schema definitions.
The official JSON Schema site describes JSON Schema as the vocabulary that enables JSON data consistency, validity, and interoperability at scale ([JSON Schema](https://json-schema.org/)). The specification hub also separates JSON Schema Core from JSON Schema Validation, where validation defines the keywords used to assert whether data is valid ([JSON Schema specification](https://json-schema.org/specification)).
That distinction matters because many production failures are not syntax failures. They are contract failures.
The payload is valid JSON, but it is missing the field the downstream service expects. The field exists, but the type changed. The UI allowed a value that the backend rejects. The API docs say one thing, but the runtime accepts another. The schema was copied into three services, and now nobody knows which version is authoritative.
A validator can catch part of that. It cannot, by itself, decide where schema ownership lives.
## **The five tool layers behind the search**
The search result page for `json schema validator` looks crowded because people use the same phrase for several different jobs.
**Tool layer****Best fit****What it proves or creates****What the team still owns**Online validatorQuick testing and debuggingA sample JSON instance matches a schemaProduction runtime, security, CI, versioningRuntime validatorAPI requests, service boundaries, app codePayloads satisfy schema rules in a language/runtimeUI, storage, workflows, governanceAPI contract toolingOpenAPI, linting, docs, API style rulesAPI definitions follow a contract and style rulesForm authoring, submissions, application stateForm generatorRendering forms from schemaA schema can produce a user-facing formBackend APIs, permissions, data lifecycleForm/API infrastructureProduction forms, APIs, submissions, workflowsSchema governs form UX, submission shape, generated APIs, and data handlingProduct fit, deployment ownership, policy configurationThe mistake is asking, "What is the best JSON Schema validator?" without asking, "What part of the system needs validation?"
## **Online validators are useful, but limited**
Online validators are useful for quick checks. They help developers paste in a schema, paste in sample JSON, and see errors immediately.
That is often exactly what the searcher wants.
But online validators should not become the production validation strategy. They are poor places for sensitive payloads. They do not enforce validation in your application. They do not live in CI. They do not control what happens after data is accepted.
Use them like a scratchpad.
For production, validation needs to move into the system path: application code, API gateway, test suite, CI pipeline, schema registry, form builder, or platform boundary.
## **Runtime validators: Ajv, Python, Java, and the application path**
Runtime validators belong where your application receives, transforms, or emits JSON.
Ajv is the obvious JavaScript and TypeScript example. Its documentation says it supports JSON Schema draft-04, draft-06, draft-07, draft 2019-09, draft 2020-12, and JSON Type Definition ([Ajv schema language guide](https://ajv.js.org/guide/schema-language.html)). Snyk's package database currently lists Ajv at more than 272 million weekly npm downloads, which shows how deeply validation libraries can sit inside the JavaScript ecosystem ([Snyk Ajv package page](https://security.snyk.io/package/npm/ajv)).
Python teams commonly reach for `jsonschema`, whose documentation shows the simple `validate` function and the validator classes behind it ([Python jsonschema validation docs](https://python-jsonschema.readthedocs.io/en/stable/validate/)).
Java teams may use NetworkNT's JSON Schema Validator, which describes support for multiple drafts and OpenAPI 3 request/response validation ([NetworkNT JSON Schema Validator](https://github.com/networknt/json-schema-validator)).
These tools are important because validation should happen where the system can reject bad data before it spreads.
The practical checklist is straightforward:
- Confirm which JSON Schema draft or dialect your validator supports.
- Reuse compiled validators where the library recommends it.
- Decide whether validation should fail fast or collect all errors.
- Make error messages useful enough for logs, developers, or users.
- Treat `$ref`, remote references, and bundled schemas as design choices, not incidental details.
- Benchmark against your actual schemas and payload sizes if validation runs in a hot path.
Runtime validators are the right answer when the job is validation.
They are not the whole answer when the same schema also needs to create forms, APIs, permissions, workflows, submission records, and audit evidence.
## **API contract tools: where JSON Schema meets OpenAPI**
For API teams, JSON Schema often appears through OpenAPI.
The OpenAPI Initiative's 3.1 release announcement says OpenAPI Schema Objects are now fully compatible with JSON Schema draft 2020-12 ([OpenAPI 3.1 release](https://www.openapis.org/blog/2021/02/18/openapi-specification-3-1-released)). That matters because the schema can become part of request validation, response validation, documentation, mock servers, SDK generation, and contract testing.
This is where tools such as Spectral fit. Spectral is a JSON/YAML linter designed with OpenAPI, AsyncAPI, and JSON Schema in mind ([Spectral](https://stoplight.io/open-source/spectral)). A validator asks whether data satisfies a schema. A linter can ask whether an API definition follows a team rule.
That is a different level of governance.
For production apps, the better question is not "Can we validate this object?" It is:
- Can we keep the API contract and implementation aligned?
- Can we catch drift in CI before release?
- Can we enforce style and security rules across many APIs?
- Can generated docs, mocks, clients, and tests inherit the same contract?
That is where JSON Schema starts becoming part of operational discipline.
## **Schema lifecycle tools: keep schemas from becoming loose files**
When schemas are shared across teams, a single validator is not enough.
Schema files need formatting, linting, testing, bundling, versioning, and promotion through environments. The official JSON Schema tools page shows how broad the ecosystem has become, including validators, documentation generators, schema-to-code tools, schema-to-web-UI tools, benchmarks, and compliance reports ([JSON Schema tools](https://json-schema.org/tools)).
Sourcemeta's JSON Schema CLI is a good example of the production-lifecycle layer. Its repository describes a CLI for maintaining schema repositories and ensuring quality during local development and CI/CD, including formatting, linting, testing, and bundling ([Sourcemeta JSON Schema CLI](https://github.com/sourcemeta/jsonschema)).
This layer matters when a schema is not a one-off file. It is a source artifact.
If multiple services, teams, or applications depend on it, schema changes need review. References need to resolve. Tests need to run. Breaking changes need to be understood before they reach production.
That is the point where teams stop treating JSON Schema as an isolated validator input and start treating it as part of the application contract.
## **Form generators: when schema becomes UI**
Some teams search for a JSON Schema validator and really need a form generator.
RJSF, for example, is a React component capable of building HTML forms out of JSON Schema. JSON Forms is another JSON Schema-based form renderer with data binding, validation, and rule-based visibility.
These tools are useful when a team wants schema to reduce repetitive form UI work.
But a form generator still leaves major production questions open:
- Where are submissions stored?
- Which API receives the data?
- How are permissions enforced?
- How are form changes versioned?
- How do non-developers safely edit forms?
- How does the schema move between dev, test, and production?
- What happens when the form becomes part of a regulated workflow?
A React JSON Schema form can render fields. That does not make it a form platform.
This is the line Form.io crosses.
## **Where Form.io fits**
Form.io belongs in this conversation only after the lower layers are clear.
It is not a replacement for Ajv, Python `jsonschema`, the JSON Schema specification, or OpenAPI tooling.
Form.io is the better fit when schema needs to become form and API infrastructure.
Form.io's Form JSON documentation says Form JSON defines the structure, appearance, and functionality of a form, and that the schema is used for rendering forms, generating REST API interfaces, and hosting the form schema for embedding ([Form.io Form JSON docs](https://help.form.io/form-building/form-json)).
Its feature documentation also explains that the builder outputs JSON schemas rather than static HTML, and that the same schema defines the UI, validation rules, data model, and REST API endpoints ([drag-and-drop form builder and APIs](https://form.io/features/drag-and-drop-form-builder-apis/)).
That is the infrastructure difference.
A validator can say, "This payload is valid."
A form generator can say, "This schema can render a form."
Form.io can connect the form definition, rendered experience, submission data, generated API, permission model, workflow actions, revisions, and deployment boundary.
That includes the operational pieces validators do not try to own: [self-hosted form deployment](https://form.io/features/self-hosted-forms-for-enterprise/), [form revisions](https://form.io/features/form-revisions-form-json-schema), [complete audit trails](https://form.io/features/log-forms-complete-audit-trail/), [secure forms compliance readiness](https://form.io/features/secure-forms-compliance-readiness/), and [fillable PDF workflows](https://form.io/features/fillable-pdf-forms) when the submitted record also needs document output.
That matters for teams building customer portals, healthcare intake, insurance claims, government services, financial onboarding, internal approval workflows, and B2B SaaS products where forms are part of the application architecture.
There is also customer proof behind this pattern. G2's indexed Form.io reviews include a State of Ohio pandemic-response example where Form.io was used to stand up forms, store and present data through an API, and feed analytics dashboards. The same reviewer called the model "easy to manage" across hundreds of websites ([G2 Form.io reviews](https://www.g2.com/products/form-io/reviews)).
Form.io's own customer proof makes the same point from the build-vs-buy side. Edify.ai said speed to market with Form.io "worked fantastically well" and that the team could focus development time on proprietary work instead ([Form.io customer proof](https://form.io/)).
The honest framing is this:
Use a JSON Schema validator when validation is the job.
Use Form.io when the schema needs to become a governed form, API, and submission system.
## **A production checklist for choosing JSON Schema tools**
Before choosing a tool, answer these questions.
### **1. Where does validation happen?**
Validation may belong in the browser, backend service, API gateway, test suite, CI pipeline, ETL job, or form platform.
One schema may need several validators in different places. That is normal. The risk is when each surface evolves its own slightly different rules.
### **2. Which schema version do you support?**
JSON Schema draft support is not trivia. Draft-07, 2019-09, and 2020-12 do not behave identically.
Pin the version. Document it. Make sure your tooling supports it before using draft-specific keywords in production.
### **3. Who owns schema changes?**
If schemas define production behavior, they need ownership.
A change to a field, type, required value, nested object, or reference may affect UI, API behavior, stored submissions, integrations, reports, and historical records.
### **4. Is the schema only validating data, or generating behavior?**
If the schema only validates API payloads, a runtime library may be enough.
If the schema renders forms, generates APIs, controls submissions, and drives workflow behavior, the decision belongs at the platform layer.
### **5. What happens after validation passes?**
This is the question most validator pages skip.
Where does the data go? Who can see it? Can it be edited? Is there revision history? Does it trigger a webhook? Can the workflow be audited? Can the platform run inside your environment?
If those questions matter, you are no longer only choosing a JSON Schema validator.
## **Key takeaways**
JSON Schema validators are necessary tools, but the phrase hides several different jobs.
Online validators help with quick checks. Runtime validators enforce contracts in code. API tooling keeps definitions consistent. Schema lifecycle tools keep shared schemas maintainable. Form generators turn schema into UI.
Form.io is for the next layer: production forms and APIs governed by schema, with submissions, permissions, workflows, revisions, and deployment control attached.
That is the practical distinction. Do not make a validator carry the full application burden. Use the validator where validation belongs, and choose infrastructure when the schema becomes infrastructure.
## **FAQ**
### **What is a JSON Schema validator?**
A JSON Schema validator checks whether JSON data conforms to rules described in a JSON Schema. Those rules can define object structure, required fields, data types, arrays, enums, numeric limits, string formats, and references to other schemas.
### **Is JSON validation the same as JSON Schema validation?**
No. JSON validation usually means checking whether the text is valid JSON syntax. JSON Schema validation checks whether valid JSON data matches an expected schema.
### **What is the best JSON Schema validator for JavaScript?**
Ajv is one of the default choices for JavaScript and TypeScript teams. It supports multiple JSON Schema drafts and is widely used across Node.js and browser environments.
### **What is the best JSON Schema validator for Python?**
Python teams commonly use the `jsonschema` package. It implements JSON Schema validation and provides validator classes, error handling, and draft-aware behavior.
### **Can JSON Schema generate forms?**
Yes, some tools can render forms from JSON Schema. RJSF and JSON Forms are common examples. The important distinction is that rendering a form does not automatically provide backend APIs, submission storage, permissions, or workflow governance.
### **Does OpenAPI use JSON Schema?**
OpenAPI 3.1 aligns its Schema Object with JSON Schema draft 2020-12. That makes JSON Schema more important for API contracts, documentation, request and response validation, and API tooling.
### **Should I paste sensitive data into an online JSON Schema validator?**
For sensitive production data, avoid it. Online validators are useful for examples and debugging, but regulated or customer data should be validated inside tools and environments your team controls.
### **What should production teams check before choosing a validator?**
Check draft support, runtime support, error quality, performance, custom formats, `$ref` handling, CI integration, schema bundling, and how schema changes are governed over time.
### **Is Form.io a JSON Schema validator?**
Form.io is not best understood as a standalone JSON Schema validator. It is a schema-driven form and API platform. It uses schema to help govern forms, submissions, generated APIs, permissions, workflows, and deployment control.
### **When should a team use Form.io instead of only a validator library?**
Use Form.io when the schema needs to operate a production form workflow, not just validate a payload. That includes embedded forms, submission records, generated REST APIs, permissions, workflow actions, revisions, and self-hosted deployment.
### **Can Form.io work alongside validators like Ajv?**
Yes. A production architecture can use validation libraries at service boundaries while using Form.io for the form, API, submission, and workflow layer. The key is deciding which system owns each contract.
If your schema needs to do more than validate JSON, [try Form.io for free](/try-formio-for-free/) and see how forms, APIs, submissions, and workflow controls can live on one foundation.
# Embedded Forms for B2B SaaS: The White-Label Form Builder Comparison
[  ](https://form.io/embedded-forms-b2b-saas-white-label-comparison/)Embedded forms are easy to misunderstand.
For a marketing team, an embedded form might mean a signup widget pasted into a page. For a B2B SaaS platform, it can mean something much heavier: a branded form experience inside the product, customer-managed form creation, tenant-specific permissions, API-backed submissions, and workflow rules that cannot drift from the rest of the application.
That is the difference this comparison is about.
## **Embedded forms become product infrastructure**
An embedded form is a form rendered inside a webpage or application, usually through an iframe, script, SDK, component, or framework integration.
That definition is useful, but too broad. It puts a newsletter signup form and a customer-facing SaaS form builder in the same bucket.
B2B SaaS teams need a sharper distinction:
- Embedded form: a finished form appears inside your website or app.
- Embedded form builder: your users or admins can create and edit forms inside your product.
- White-label form infrastructure: the forms, builder, submissions, APIs, branding, roles, tenant boundaries, and workflow behavior all operate as part of your product.
That last category is where Form.io belongs. The [Form.io Enterprise Form Builder Module](https://form.io/enterprise-form-builder-module/) is built to embed a white-labeled form builder inside an application while the platform owner keeps control over components, data model, permissions, and workflow behavior.
## **Quick comparison**
**Option****Best fit****Main strength****Main tradeoff**Form.ioB2B SaaS teams that need embedded forms, embedded form building, APIs, tenant-aware control, and deployment flexibilityForms behave like governed application infrastructureMore platform than a simple marketing form team needsJotformHosted enterprise teams that want template-rich no-code form building and broad business workflowsFast, familiar hosted form creationStrongest when the form system can remain vendor-hosted and account-centeredFeatheryProduct teams that want polished embedded form UX and a white-label editor experienceStrong product-form experience and editor customizationTeams still need to evaluate backend governance, deployment, and data ownership depthSurveyJSJavaScript teams that want form libraries and a builder they can wire into their own stackDeveloper control inside front-end applicationsMore assembly work around storage, APIs, permissions, and operationsFormsortTeams building branded conversion flowsManaged branded flows with conversion focusNarrower fit when forms become governed product infrastructure123FormBuilder / similar toolsTeams that primarily need branded hosted forms and account-level white labelingFamiliar form-builder packagingWhite label often centers on branding more than application architectureThe right choice depends less on the phrase "embedded forms" and more on what the embedded form has to own.
## **The SaaS evaluation checklist**
If customers only need to submit a contact form, almost any credible form builder can work.
If customers need to create forms inside your application, the checklist changes:
- Can the finished form be embedded cleanly?
- Can the builder itself be embedded?
- Can vendor branding be removed from the form, builder, emails, URLs, and exports?
- Can each tenant have separate forms, submissions, themes, permissions, and workflows?
- Can you restrict which components, validation rules, logic, and publishing actions customers can use?
- Are submissions available through APIs, not only exports or webhooks?
- Where does submission data live?
- Can the form layer run inside the deployment boundary your customers require?
- Are revisions, access controls, and audit evidence part of the model?
- Does the pricing model still work when every customer creates forms?
Those questions are not cosmetic. They are architecture questions.
[Postman's 2025 State of the API report](https://voyager.postman.com/doc/postman-state-of-the-api-report-2025.pdf) found that 82% of organizations had adopted some level of API-first approach. That matters because embedded forms in a SaaS product are not just pixels. They create records, trigger workflows, and pass data to the rest of the application.
## **Where Form.io fits**
Form.io is the strongest fit when embedded forms need to behave like part of the product infrastructure.
The [Form.io form embedding documentation](https://help.form.io/dev/form-embedding) covers quick inline embedding, JavaScript embedding, iframe fallback, builder embedding, and framework embedding. That gives teams a practical path from simple rendering to deeper application integration.
But the more important distinction is what sits behind the embed.
Form.io forms are JSON-driven definitions connected to rendering, validation, submissions, APIs, permissions, and workflow behavior. The [drag-and-drop form builder with APIs](https://form.io/features/drag-and-drop-form-builder-apis/) is not only a UI for arranging fields. It is part of a system where form definitions can become application contracts.
That matters for SaaS platforms where customers need their own forms, variations, permissions, and branded experiences. The [Form.io homepage](https://form.io/) explicitly frames white-label SaaS use around form, API, and data management under the platform's brand or the customer's brand. It also describes multi-tenant child-project patterns for separating forms, data, and form building.
For more controlled environments, the [self-hosted Form.io deployment model](https://form.io/features/self-hosted-forms-for-enterprise/) matters because the form layer can live closer to the customer's infrastructure boundary instead of becoming an external data silo.
## **White label is more than branding**
Most white-label form pages talk about logos, colors, custom domains, badge removal, and branded emails.
Those are real requirements. They are not enough.
In a B2B SaaS product, white label also means the form capability has to respect the product's operating model. A tenant should not see another tenant's forms. A customer admin should not publish components that break downstream processing. A support team should be able to diagnose what changed. A developer should know how submissions map into APIs and workflows.
This is where a light embed starts to strain.
OWASP's API Security Top 10 puts [broken object-level authorization](https://owasp.org/API-Security/editions/2023/en/0xa1-broken-object-level-authorization/) first. That is a useful reminder for SaaS form architecture: if embedded forms create or expose customer records through APIs, authorization has to be object-aware and tenant-aware. Front-end hiding is not governance.
The same logic applies to validation and workflow behavior. The [conditional logic and validation features](https://form.io/features/form-conditional-logic-form-validation/) matter because the form should enforce rules before bad data becomes an API or workflow problem.
## **When a simpler embedded form is enough**
Use a simpler hosted embed when the form is not central to the product.
That includes:
- newsletter signup
- marketing lead capture
- event registration
- contact and support requests
- one-off surveys
- public feedback forms
- low-risk forms that can live in an external form account
In those cases, a hosted form builder with templates, brand settings, and a quick embed code may be the best decision. Jotform, Formsort, 123FormBuilder, and similar tools can be strong fits when speed and convenience are the main job.
The mistake is keeping that architecture after forms become a customer-facing product capability.
## **When embedded form infrastructure is needed**
Embedded form infrastructure becomes important when the form is part of how your SaaS product works.
Examples include:
- customer onboarding flows that differ by tenant
- partner and vendor portals
- regulated intake workflows
- customer-managed form libraries
- embedded application builders
- productized approval flows
- internal workflow forms exposed to external customers
- multi-office or multi-group customer operations
In these cases, forms need lifecycle control. NIST's [Secure Software Development Framework](https://csrc.nist.gov/pubs/sp/800/218/final) treats security practices as part of the software development lifecycle, which is the right lens for embedded form capability that ships inside a SaaS product. The form builder is no longer an outside utility. It is part of the product surface.
Data risk also changes the decision. [Thales' 2025 Cloud Security Study](https://cpl.thalesgroup.com/cloud-security-research) reported that 54% of cloud data is sensitive and that only 8% of respondents encrypt 80% or more of cloud data. That does not mean every embedded form needs self-hosting. It does mean SaaS teams should know where form data lives, who can access it, how it is encrypted, and how it moves through APIs.
## **Customer proof: white-label forms as a business model**
The white-label use case is not theoretical for Form.io.
In Form.io's Bursting Silver case study, the company describes how a regulatory-industry platform [white-labeled Form.io](https://form.io/case-studies/from-facing-the-risk-of-losing-an-entire-industry-to-generating-millions-and-having-new-clients-call-them/) to support its industry, sign dozens of new clients, and increase revenue by 25%.
That proof point matters because it connects embedded forms to a business model, not just a UI decision. When forms are a capability customers use inside your product, the form layer can influence retention, onboarding, service load, expansion, and product differentiation.
## **The decision framework**
Choose a simple embedded form when the form is a page element.
Choose a hosted enterprise form builder when business users need fast form creation and the external vendor account model is acceptable.
Choose a JavaScript form library when your team wants front-end control and is ready to build the backend, storage, permissions, and operational layer around it.
Choose Form.io when the form capability needs to become part of your product architecture: embedded rendering, embedded building, customer self-service, white-label experience, structured schemas, generated APIs, permissions, validation, workflow behavior, and deployment control.
That is the real difference.
Embedded forms are not automatically infrastructure. But in B2B SaaS, they often become infrastructure faster than teams expect.
## **Key takeaways**
- Embedded forms can mean a simple widget, an embedded form builder, or full white-label form infrastructure.
- SaaS teams should evaluate builder embedding, tenant separation, data ownership, APIs, permissions, workflow behavior, and deployment model.
- Competitors can be good fits for hosted no-code forms, polished product forms, developer libraries, or branded conversion flows.
- Form.io is strongest when the form layer needs to stay connected to schemas, APIs, submissions, permissions, and workflows inside the product architecture.
- A simple embed is enough for low-risk marketing forms. It is not enough when customers need to build and govern forms inside your SaaS.
## **FAQ**
### **What are embedded forms?**
Embedded forms are forms rendered inside a webpage or application through an iframe, script, SDK, component, or framework integration. The user completes the form without leaving the surrounding site or product experience.
### **What is an embedded form builder?**
An embedded form builder is a builder or editor exposed inside your application so users can create or change forms without going to a separate vendor dashboard.
### **What does white-label mean for forms?**
At minimum, white label usually means custom branding, colors, domains, and removal of vendor badges. For SaaS platforms, it should also include builder experience, tenant separation, emails, exports, permissions, and workflow behavior.
### **Can customers create their own forms inside a SaaS product?**
Yes, if the platform supports embedded form building. The important question is whether customers can do that inside guardrails your product controls.
### **Are iframe embedded forms enough?**
Sometimes. Iframes can be practical for low-risk or simple use cases. They are often weaker when the form needs deep styling, app authentication, event handling, tenant-aware permissions, or tight workflow integration.
### **Which embedded form builder is best for multi-tenant SaaS?**
Form.io is a strong fit when multi-tenant SaaS teams need white-labeled form creation, APIs, permissions, structured submissions, workflow behavior, and deployment control. Simpler tools may fit when the requirement is only branded form capture.
### **Do embedded forms create security risks?**
They can if teams treat them as front-end widgets while the data becomes sensitive application data. The right controls depend on authorization, validation, tenant separation, encryption, auditability, and where submissions are stored.
### **When should I choose Form.io over a simpler form builder?**
Choose Form.io when forms are part of the application infrastructure: customers create forms, submissions feed APIs, permissions matter, workflows depend on form data, and the deployment boundary is important.
### **Can Form.io replace my whole application backend?**
No. Form.io is infrastructure for forms, APIs, submissions, validation, permissions, and workflow-related actions. Your application still needs its own product logic, user experience, integrations, and surrounding architecture.
## **Build embedded forms that behave like your product**
If your SaaS customers only need a form on a page, keep it simple.
If they need governed, branded, customer-managed forms inside your product, start with infrastructure that can carry the form, data, API, and workflow model together.
[Try Form.io for white-label embedded form infrastructure](/try-formio-for-free/).
# Claims Management Software Starts With The Forms That Feed It
[  ](https://form.io/claims-management-software-insurance-form-builders/)Claims management software comparisons usually start with the core claims system.
That makes sense. Carriers, TPAs, MGAs, adjusters, and self-insured organizations need systems for assignment, reserves, adjudication, payments, subrogation, reporting, and closure.
But many claims problems start earlier.
They start at the first notice of loss. They start when a claimant uploads the wrong document, an adjuster captures incomplete field notes, an agent enters policy data twice, or a regulatory form has to be recreated from unstructured intake data.
Before a claim can be managed, the data has to be captured.
That is why insurance teams should evaluate the form infrastructure behind the claims workflow, not only the claims platform itself.
## **Key Takeaways**
- Claims management software and claims form infrastructure solve different layers of the same workflow.
- Full claims systems manage the claim lifecycle. Form infrastructure governs intake, validation, files, submissions, APIs, PDFs, permissions, and handoff.
- Claim handling is a high-risk customer and regulator touchpoint, so weak intake creates downstream cost.
- Form.io is not a full claims-core replacement. It is a strong fit when insurance forms need to become embedded, API-backed, self-hosted workflow infrastructure.
- The right evaluation question is not only "which claims system?" It is also "what form layer feeds and extends the claims system?"
## **What Claims Management Software Usually Means**
In most buyer guides, claims management software means a system that supports the claims lifecycle from first notice of loss through settlement and closure.
The category usually includes:
- FNOL and claims intake
- claim assignment and triage
- document and image management
- policy lookup
- investigation and adjudication
- reserve management
- payments and settlement
- regulatory reporting
- analytics and dashboards
- customer status updates
- closure and audit history
That is why systems like Guidewire ClaimCenter, Duck Creek Claims, Riskonnect, FINEOS, VCA, BriteCore, Snapsheet, and other claims platforms dominate the search results for **claims management software**.
They are solving a large operational problem.
Form.io should not be framed as a replacement for those systems when the buyer needs a full claims core. If your team needs end-to-end claims adjudication, reserve management, litigation tracking, payment workflows, subrogation, CAT-scale claims operations, or deep P&C suite functionality, a claims management platform is the right category to evaluate.
But claims systems do not remove the need for form infrastructure.
They often create more of it.
## **Why Claims Intake Is An Infrastructure Problem**
Claims are where the insurer's promise becomes visible.
The customer does not experience the claims system as a data model or an admin workflow. They experience it as a form, a file upload, a status update, an estimate, a call, a missing document request, or a delay.
That is why digital claims workflows have real retention stakes. J.D. Power's 2025 U.S. Claims Digital Experience Study reported that insurers deliver adequate digital updates only 22% of the time. Insurance Journal's coverage of the study also reported that 52% of auto and homeowners customers who rate their digital claim experience as "poor" or "just OK" are likely to leave or not renew, compared with 4% of customers who rate the experience as "excellent" or "perfect" ([Yahoo Finance syndication of J.D. Power release](https://finance.yahoo.com/news/fully-digital-claims-processing-drives-120000409.html), [Insurance Journal](https://www.insurancejournal.com/news/national/2025/12/09/850297.htm)).
Weak intake also shows up in complaint patterns. The NAIC says delays, denials, and unsatisfactory settlements are among common reasons consumers file complaints, and that consumers are asked to gather supporting documents, photographs, correspondence, phone logs, and detailed accounts when filing complaints ([NAIC](https://content.naic.org/article/how-file-complaint-and-research-complaints-against-insurance-carriers)). A ValuePenguin analysis of NAIC closed complaint data reported that claim handling accounted for 65.2% of closed insurance complaints in 2024, with delays and unsatisfactory settlements or offers as the top claim-handling complaint types ([ValuePenguin](https://www.valuepenguin.com/most-common-insurance-complaints)).
Those numbers do not prove a form platform fixes claims operations by itself.
They prove the stakes.
If claims data enters the workflow through weak forms, disconnected uploads, duplicated manual entry, unclear validation, or inconsistent status paths, the claims system inherits that mess.
## **The Claims Workflow Surfaces That Depend On Forms**
Insurance forms are not only contact forms.
In a claims environment, forms show up across the workflow:
- policyholder FNOL forms
- agent and broker claim submission forms
- adjuster field reports
- inspection and damage assessment forms
- photo, video, and document upload flows
- repair estimate collection
- medical record and proof-of-loss intake
- third-party claimant forms
- loss run request forms
- policy application and endorsement forms
- regulatory filing packets
- PDF outputs for records, signatures, reviews, or state-specific requirements
Some of these forms are customer-facing. Some are internal. Some are embedded in portals. Some are mobile. Some still need to map back to exact PDF-style layouts because insurance operations have not escaped document reality.
That is the layer where form infrastructure matters.
A claim can move through a core system, but the surrounding form layer still has to answer practical questions:
- Who can submit this form?
- Which fields are required for this claim type?
- Can the claimant save and resume?
- Can an adjuster collect data offline?
- Can photos and documents be attached securely?
- Does the submitted data become structured JSON, or does someone retype it later?
- Can the submission feed an API, webhook, claims core, document repository, or analytics pipeline?
- Can the same data produce a PDF output when a regulator, carrier, or partner still needs one?
- Can changes to the form and submission be audited?
Those are not cosmetic questions. They are workflow architecture.
## **What To Evaluate In The Claims Form Layer**
A serious claims-intake form layer should be evaluated on more than field layout.
### **Conditional Logic**
Insurance workflows vary by claim type, line of business, state, channel, and role.
A property claim does not ask the same questions as a cyber liability claim. A claimant portal does not need the same view as an adjuster workflow. A policyholder should not see every internal field an examiner needs.
The form layer should support conditional logic, role-specific screens, and dynamic form paths without forcing every variation into custom code.
### **Validation Before Handoff**
The worst time to discover bad data is after it reaches the claims system.
Claims forms should validate required fields, dates, policy identifiers, file requirements, numeric values, and conditional dependencies before submission. They should reduce preventable downstream rework without pretending every claim is simple.
### **File And Evidence Capture**
Claims intake often depends on documents and media: photos, estimates, police reports, medical documents, invoices, inspection records, correspondence, and proof-of-loss materials.
The form layer should treat uploads as part of the submission record, not as an afterthought in a shared inbox.
### **Generated APIs And System Handoff**
Claims data rarely stays in one place.
It may need to feed a claims core, policy system, CRM, document management platform, analytics warehouse, notification workflow, payment process, or regulatory reporting path.
That is why static forms are not enough. The form layer should expose structured submission data through APIs and integration patterns that developers can control. For Form.io, that includes [drag-and-drop forms with generated APIs](https://form.io/features/drag-and-drop-form-builder-apis/) rather than forms that stop at display and email notification.
### **Permissions And Submission Access**
Insurance workflows are role-sensitive.
Policyholders, agents, adjusters, claim supervisors, legal teams, compliance teams, and admins should not all see the same data. A useful form platform needs access control around forms and submissions, not just a login screen in front of everything.
### **Auditability**
Claims records can become evidence.
If a form changes, a submission is edited, a file is replaced, or a workflow action fires, teams need to understand what changed, who changed it, and when. Auditability is not decoration in regulated workflows.
That is why a claims form layer should include a [complete audit trail for form changes and submissions](https://form.io/features/log-forms-complete-audit-trail/), especially when operational records may later be reviewed by legal, compliance, or regulator-facing teams.
### **PDF And Regulatory Output**
Insurance still runs on documents.
NAIC's SERFF industry training page describes electronic rate and form filing as including form submittal, document management, and review access, while supporting compliance with consumer protection requirements ([NAIC SERFF](https://content.naic.org/node/10174)). That does not mean every claims form feeds SERFF. It does mean "forms" in insurance often exist inside regulated document and review workflows.
Good form infrastructure should let teams collect structured data through modern web forms while still producing PDF outputs when official, partner, regulatory, or legacy processes require them.
That can include [custom PDF templates](https://form.io/features/pdf-forms-pdf-template-designer/) and [fillable PDF forms](https://form.io/features/fillable-pdf-forms/) when the workflow has to preserve document fidelity without giving up structured submission data.
## **Where Form.io Fits**
Form.io fits when the forms around claims management need to become application infrastructure.
That does not mean Form.io is a claims adjudication engine. It does not calculate reserves, run a full claims core, or replace every specialized insurance platform.
It means Form.io can support the form, API, submission, PDF, and workflow layer that surrounds those systems.
Form.io's public insurance PDF page speaks directly to this type of insurance workflow: outputting submissions to PDF, turning PDFs into embeddable dynamic forms, tracking changes to fields and forms, auto-populating repeated data, autosaving unfinished forms, collecting offline, and using mobile-responsive forms ([Form.io insurance PDF forms](https://form.io/industries/pdf-forms-for-insurance/)).
The official Form.io documentation also describes two PDF paths: PDF output from webform submissions and PDF-first forms where teams upload a PDF and place interactive fields on top of it. PDF Plus adds PDF-first experiences with pixel-perfect PDF backgrounds and JSON-driven overlays, while PDF Basic supports printing and downloading webform submissions as PDFs ([Form.io docs](https://help.form.io/form.io-concepts.md?ask=How%20does%20Form.io%20support%20PDF%20forms%20and%20PDF%20output%20from%20webform%20submissions%3F)).
That matters for insurance because the buyer often needs both:
- modern, embedded, API-backed data capture
- document-style outputs that still match policy, claims, underwriting, or regulatory expectations
Form.io also matters when teams need forms and APIs together. The platform is designed around JSON-defined forms, submissions, generated APIs, permissions, workflow actions, and customer-controlled deployment. For insurance teams, that can support workflows such as:
- embedded FNOL forms inside a policyholder portal
- agent-facing application and claims intake
- adjuster inspection forms with file uploads
- internal review forms for claims operations
- self-hosted data capture for sensitive records
- structured submission APIs into existing claims or policy systems
- PDF outputs for claim packets, confirmations, or document-heavy workflows
This is the useful distinction:
Claims management software manages the claim.
Form.io can govern the form infrastructure that captures and moves the data the claim depends on.
## **Comparison: What To Ask Before Choosing The Form Layer**
## **Evaluation question****Why it matters****What to look for**Can the form handle different claim types?Claims vary by line, state, product, and roleConditional logic, reusable components, role-specific flowsCan users upload documents and photos?Evidence is often the claim recordSecure file upload, file metadata, submission associationDoes the form validate data before submission?Bad intake data creates downstream reworkRequired fields, conditional validation, typed data, calculated valuesDoes submission data have an API?Claims data must move into other systemsREST APIs, webhooks, JSON submissions, developer-controlled handoffCan permissions be scoped?Insurance workflows are role-sensitiveForm and submission permissions, own-vs-all access, admin boundariesCan changes be audited?Claims and regulated forms need evidenceChange history, audit logs, revision-aware workflowsCan web submissions become PDFs?Insurance still needs documentsPDF output, PDF templates, PDF-first forms, existing PDF conversionCan it be embedded?Claims intake lives inside portals and productsEmbeddable renderer, embedded builder, white-label controlsCan it be self-hosted?Some insurance data must stay inside controlled environmentsCustomer-controlled deployment, database, file storage, network boundary**When A Full Claims Management Platform Is The Better Fit**
Use a full claims management platform when the core problem is managing the claim lifecycle itself.
That includes:
- claim assignment and triage
- reserve management
- adjudication workflows
- payments and settlement
- subrogation and recovery
- litigation management
- catastrophe scale handling
- repair network workflows
- claims analytics
- policy and billing suite integration
- specialized P&C, health, life, or workers' compensation claim operations
This is where platforms like Guidewire, Duck Creek, Riskonnect, FINEOS, VCA, BriteCore, Snapsheet, and other insurance-specific systems belong in the evaluation.
Trying to force a form infrastructure platform to behave like a complete claims core would be the wrong move.
But it is equally risky to assume the claims core solves every form problem around it.
Many carriers already have core systems. The friction is in the portals, supplemental forms, customer-facing intake, partner workflows, document packets, regulatory outputs, and integration surfaces around those systems.
That is where a dedicated form infrastructure layer can make sense.
## **When To Evaluate Form Infrastructure Separately**
Evaluate the form layer separately when any of these are true:
- Your claims core works, but customer or agent intake is weak.
- You need embedded forms in a portal, app, or white-labeled product.
- Claims data must feed multiple downstream systems.
- Different teams need to create or modify forms without breaking the architecture.
- Documents and PDFs are still part of the official workflow.
- You need structured APIs instead of manual re-entry.
- You need submission-level permissions and audit evidence.
- You need to self-host the form and submission layer.
- You need offline or mobile-responsive collection.
- You need a repeatable way to turn form changes into governed application behavior.
This is the buyer Form.io should speak to.
Not the buyer looking for the quickest online form.
Not the buyer who wants to replace every claims system overnight.
The buyer whose forms have become infrastructure.
## **Customer Proof: Insurance Forms Are Operational Systems**
Form.io has public insurance-adjacent proof through E-Risk Services, LLC, described in a Form.io case study as a specialty-lines underwriting subsidiary of Nationwide Insurance Company. The case study says E-Risk built a CRM in two months instead of two years ([Form.io case study](https://form.io/case-studies/building-a-crm-took-2-months-instead-of-2-years/)).
That proof point should be used carefully. It is a Form.io-hosted case study, not an independent Nationwide-hosted validation of the timeline.
But it is still relevant because E-Risk's public Nationwide page shows the real insurance surfaces around specialty lines: product pages, applications and forms, policy forms, loss run requests, expiring policy requests, underwriting contact paths, quoting, and servicing ([Nationwide E-Risk](https://www.nationwide.com/excessandsurplus/e-risk/)).
That is the practical pattern.
Insurance teams do not only need one claims screen. They need many controlled data-capture and document workflows around underwriting, servicing, claims, renewals, requests, and regulated communications.
Form infrastructure is how those workflows stay usable without becoming disconnected spreadsheets, PDF piles, email chains, and one-off portals.
The customer language from another Form.io-hosted case study is useful here because it describes the same infrastructure burden in plain terms. In the Safety Mojo case study, a long-time Form.io platform user said, "Form.io cleans up all the dirty work and does it for you" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)). That quote is not insurance-specific, but it fits the architectural point: forms become expensive when every team has to rebuild the form, data, API, and workflow plumbing separately.
## **The Decision Rule**
Choose a claims management platform when the main requirement is claims-core operation.
Choose Form.io when the main requirement is governed form infrastructure around insurance workflows.
That means forms that can render in your application, collect structured data, validate submissions, handle files, expose APIs, support permissions, produce PDFs, and live inside your deployment boundary.
For teams with stricter data-control requirements, [self-hosted enterprise forms](https://form.io/features/self-hosted-forms-for-enterprise/) can keep the form, submission, and file-handling layer inside the environment the organization controls.
For insurance teams, this distinction matters because "claims management software" is not one decision.
It is at least two:
1\. What system manages the claim lifecycle? 2. What infrastructure captures, governs, and moves the data that feeds it?
Most comparisons answer only the first question.
The second question is where Form.io belongs.
## **FAQ**
### **What Is Claims Management Software?**
Claims management software helps insurance teams manage claims from intake through assignment, investigation, adjudication, settlement, reporting, and closure. It often includes FNOL, document management, workflow automation, payments, analytics, and compliance features.
### **Is Form.io Claims Management Software?**
Form.io is not a full claims management platform or claims-core system. It is form and API infrastructure that can support the intake, submission, document, PDF, permission, and integration layer around claims workflows.
### **Can Form.io Replace Guidewire Or Duck Creek?**
Not when the requirement is a full claims core. Guidewire, Duck Creek, and similar systems are built for end-to-end claims operations. Form.io is a better fit when teams need governed forms, APIs, submissions, PDFs, and embedded intake around those systems.
### **What Is FNOL Software?**
FNOL software supports first notice of loss: the initial claim report. A strong FNOL workflow captures structured claim data, claimant details, incident information, documents, photos, and routing data so the claim can move into the right downstream process.
### **Why Do Insurance Claims Workflows Need Better Forms?**
Claims workflows depend on accurate intake. If forms collect incomplete data, miss required documents, fail to validate fields, or force manual re-entry, the claims process slows down and customer experience suffers.
### **Can Claims Forms Collect Photos And Documents?**
Yes, but the important question is how those files are stored, associated with submissions, permissioned, and handed off. Claims evidence should be part of the structured submission workflow, not a loose email attachment.
### **How Do PDF Forms Fit Insurance Claims?**
Many insurance workflows still require PDF-style outputs, forms, packets, or official documents. A modern form layer should collect structured web data while still supporting PDF output or PDF-first forms when the workflow requires document fidelity.
### **What Should Insurers Evaluate In Claims Intake Software?**
Evaluate conditional logic, validation, file uploads, submission APIs, permissions, audit logs, embedded rendering, PDF output, mobile/offline support, and deployment control. The form layer should support the claims architecture, not just display fields.
### **Do Claims Workflows Need Self-Hosted Forms?**
Not always. Self-hosting matters when sensitive claims data, regulatory expectations, customer requirements, or enterprise architecture require the form and submission layer to run inside a controlled environment.
### **How Can Forms Connect To Claims Management Systems?**
Forms can connect through APIs, webhooks, submission exports, custom integrations, document workflows, or middleware. The important requirement is structured, validated submission data that downstream systems can consume reliably.
## **Build Claims Intake Infrastructure With Form.io**
If your team needs a full claims-core platform, evaluate claims management systems directly.
If your team needs better claims intake, embedded insurance forms, PDF outputs, generated APIs, controlled submissions, and customer-hosted form infrastructure, evaluate the form layer separately.
[Try Form.io for insurance form infrastructure](https://form.io/try-formio-for-free/).
# KYC Onboarding Software for Financial Services: Forms, APIs, and Audit-Ready Intake
[  ](https://form.io/kyc-onboarding-software-financial-services-form-platforms/)KYC onboarding software is usually evaluated as an identity verification purchase.
That is only part of the system.
Banks, fintechs, lenders, and other financial-services teams still have to collect customer data, route exceptions, connect verification providers, preserve evidence, and keep sensitive workflows under control. The right question is not only which KYC provider to buy. It is what intake infrastructure the provider connects to.
## **Key Takeaways**
- KYC onboarding software includes identity checks, but the surrounding intake layer matters just as much.
- Dedicated KYC vendors are strongest for document verification, sanctions screening, adverse media, KYB data, biometrics, and verification coverage.
- Form.io is a better fit for the application infrastructure around those checks: embedded forms, structured submissions, generated APIs, permissions, workflows, revisions, audit trails, and customer-controlled deployment.
- Financial-services teams should evaluate who owns the schema, submission record, API handoff, audit evidence, and change-control path.
- The strongest architecture often combines a KYC verification vendor with a governed form platform that controls intake inside the customer's own product and environment.
## **What KYC Onboarding Software Has To Handle**
KYC onboarding is not a simple signup form with a document upload bolted on.
In financial services, onboarding can involve customer identity, beneficial ownership, business entity details, risk indicators, attestations, document evidence, sanctions and PEP checks, adverse media review, manual exception handling, approvals, and ongoing updates.
The fraud pressure behind those workflows is real. The Federal Trade Commission reported that consumers lost more than $12.5 billion to fraud in 2024, a 25% increase from the prior year ([FTC](https://www.ftc.gov/news-events/news/press-releases/2025/03/new-ftc-data-show-big-jump-reported-losses-fraud-125-billion-2024)). That number does not prove any one onboarding product prevents fraud. It does show why financial-services teams treat identity, intake, and evidence workflows as risk infrastructure.
For covered financial institutions, customer due diligence also extends beyond one-time identity capture. FinCEN describes CDD as policies and procedures that identify and verify customers and beneficial owners, understand customer relationships for risk profiling, and support ongoing monitoring and customer-information updates ([FinCEN](https://www.fincen.gov/news/news-releases/fincen-reminds-financial-institutions-cdd-rule-becomes-effective-today)). FinCEN's 2026 exceptive relief narrowed repeat beneficial-owner verification at every new account opening, but preserved initial verification, risk-based updates, and ongoing monitoring obligations ([FinCEN](https://www.fincen.gov/news/news-releases/fincen-issues-exceptive-relief-streamline-customer-due-diligence-requirements)). Digital identity guidance makes the same point from another angle: NIST SP 800-63A-4 defines identity proofing and enrollment requirements across three identity assurance levels, with evidence, validation, and verification expectations that affect onboarding design ([NIST SP 800-63A-4](https://csrc.nist.gov/pubs/sp/800/63/a/4/final)). FFIEC authentication guidance also emphasizes layered security and stronger controls than single-factor authentication for financial institution services and systems ([FFIEC authentication guidance](https://www.ffiec.gov/news/press-releases/2021/pr-08-11)).
That is the operating reality KYC onboarding software has to support.
It has to help the organization answer:
- What information do we need for this customer type?
- Which evidence is required for this product, jurisdiction, or risk profile?
- Which verification provider or internal service should receive the data?
- Who reviews exceptions?
- Which decisions and changes need to be retained?
- Where does the submission record live?
- How do we update customer information later without losing history?
Those are not only compliance questions. They are application architecture questions.
## **The Three Layers Of KYC Onboarding Software**
Most KYC software pages collapse three different layers into one category.
That makes comparison harder than it needs to be.
### **1. KYC Verification And Data Providers**
This is the layer buyers usually think of first.
KYC verification providers handle identity document verification, database checks, liveness or biometric checks, sanctions screening, PEP screening, adverse media, fraud signals, KYB data, business registry checks, and beneficial ownership data.
If your main problem is global identity coverage, document authenticity, fraud detection, sanctions data, or KYB intelligence, this is the category you should evaluate.
Form.io does not replace that layer.
### **2. Client Lifecycle And Case Workflow Platforms**
Some financial institutions need a broader client lifecycle management system.
That can include onboarding cases, risk scoring, relationship-manager queues, remediation workflows, periodic refresh, monitoring, approvals, dashboards, and enterprise reporting.
If the primary buyer need is a complete CLM suite for a large financial institution, a specialized onboarding or CLM platform may be the right center of gravity.
Form.io does not claim to be a full AML case-management system.
### **3. Form And Application Infrastructure**
This is the layer many comparisons understate.
Before a verification service can check anything, the organization has to collect the right data, validate it, structure it, submit it, secure it, route it, and keep the record. That work often happens in forms embedded inside account-opening flows, borrower portals, investor onboarding flows, agent portals, internal review tools, and customer update workflows.
This is where Form.io belongs.
Form.io is not the sanctions database, fraud network, or identity bureau. It is the schema-driven form and API infrastructure that can sit around those systems when the customer needs to own the intake experience and the data path.
## **Why Static Forms Break KYC Workflows**
Static forms are comfortable until the onboarding workflow branches.
A retail deposit account does not collect the same evidence as a commercial lending application. A sole proprietor does not require the same entity structure as a multi-owner company. A low-risk domestic customer does not follow the same path as a higher-risk customer, foreign entity, trust, money-services business, or politically exposed person.
KYC onboarding software often has to branch by:
- individual versus business customer
- account or product type
- jurisdiction
- entity structure
- risk level
- ownership profile
- required documents
- missing or inconsistent information
- applicant role
- reviewer role
- periodic refresh or customer update
If those branches live in hard-coded forms, spreadsheets, PDFs, or ad hoc portal logic, the onboarding workflow becomes brittle. Compliance teams cannot change requirements cleanly. Developers cannot route data consistently. Reviewers inherit partial records. Customers get asked for the wrong information.
The stronger model is a governed intake schema: the form defines the data structure, validation, conditional logic, submission record, API handoff, and change path.
That is the Form.io argument.
## **What A KYC Intake Layer Should Provide**
The form layer behind KYC onboarding software should be evaluated as infrastructure, not as a decorative front end.
### **Dynamic Forms And Validation**
KYC intake should adapt to the customer, product, jurisdiction, entity type, and risk profile.
The platform should support [conditional logic and validation](https://form.io/features/form-conditional-logic-form-validation/), reusable components, calculated values, required evidence, document upload fields, consent language, and validation rules. The goal is not to make a long form look nicer. The goal is to collect the right information before the workflow reaches verification, review, or downstream systems.
### **Structured Submission Records**
For KYC, a submitted form is not just a message.
It is a record of what was asked, what was provided, which files were attached, what metadata came with the submission, and what later changed. Submission data needs to remain accessible for internal systems, reviewers, reports, and audit workflows.
Form.io's documentation describes forms as the structure that collects, validates, and stores user data, while the same form structure defines a backend API for managing and accessing submitted data ([Form.io docs](https://help.form.io/userguide/forms)). That structure matters when KYC data needs to move beyond a form inbox.
### **API Handoff To Verification And Core Systems**
KYC onboarding almost always depends on other systems.
Data may need to move into identity verification providers, sanctions or PEP screening services, CRM, core banking, lending systems, document management, case management, data warehouses, notification tools, and compliance reporting.
For Form.io, the strongest claim is architectural: every form, resource, submission, and project is accessible through a REST API, with predictable endpoints and submission paths that developers can connect to other systems ([data integration tools](https://form.io/features/data-integration-tools-for-enterprise-forms/)). Webhook actions can also send submission payloads to external endpoints when events occur.
That does not mean Form.io ships every KYC vendor integration out of the box.
It means teams can build the intake and handoff layer around the verification tools they choose.
### **Role-Based Access**
KYC data is role-sensitive.
Applicants, authorized representatives, relationship managers, compliance analysts, operations staff, auditors, developers, and administrators should not all see or edit the same data.
The intake layer should support [role and submission permissions](https://help.form.io/developers/roles-and-permissions.md) around forms, submissions, admin surfaces, and review workflows. This matters because KYC onboarding often blends customer-facing and internal workflows. One weak permission model can turn a controlled process into an overexposed one.
### **Revisions And Audit Logs**
Regulated onboarding workflows need history.
If a customer updates business ownership details, a reviewer changes a risk classification, a required field is added, or an administrator modifies access, the organization needs to know what happened.
Form.io describes two complementary logging systems: Submission Revisions for field-level submission changes and Server Audit Logging for system activity such as form access, authentication, and API-level data modifications ([audit trail capabilities](https://form.io/features/log-forms-complete-audit-trail/)). Those capabilities fit KYC intake because the evidence trail is part of the workflow, not an afterthought.
Availability and configuration still matter. Teams should confirm which modules, settings, and license terms apply before making compliance commitments.
### **Deployment And Data Boundary Control**
KYC onboarding touches sensitive personal and business information.
Some financial-services teams can use hosted tools without issue. Others need stricter control over environment, authentication, database, file storage, network access, logging, and vendor exposure.
That is where [self-hosted forms](https://form.io/features/self-hosted-forms-for-enterprise/) or customer-controlled deployment becomes part of the buying decision. Form.io is strongest when the intake layer needs to live inside the customer's architecture rather than as a disconnected third-party form surface.
## **How Form.io Fits Beside KYC Verification Vendors**
The right architecture is often not Form.io instead of a KYC vendor.
It is Form.io around the KYC vendor.
A financial-services team might use Form.io to build an [embedded onboarding flow](https://form.io/features/drag-and-drop-form-builder-apis/) that collects customer and entity data, validates required fields, captures documents, stores submissions, applies role-based access, and exposes the submission through APIs. The same workflow can then call identity verification, document verification, sanctions screening, fraud, CRM, or core system services.
That division of responsibility is clearer and more credible:
**Layer****What It Does****Typical Fit**KYC verification providerIdentity proofing, document checks, sanctions or PEP screening, KYB data, fraud signalsUse when verification intelligence and coverage are the core needCLM or onboarding suiteCases, queues, lifecycle workflows, risk review, remediation, dashboardsUse when the institution needs a broad onboarding operating systemForm.io intake infrastructureEmbedded forms, structured submissions, generated APIs, permissions, revisions, audit trails, workflow handoff, self-hosted deploymentUse when the team needs to own the intake layer inside its product and systemsThis distinction also keeps the compliance claim honest.
Form.io can support regulated KYC onboarding controls. It does not make an organization compliant by itself. It does not replace AML policy, compliance staff, model validation, legal review, sanctions data, transaction monitoring, or the specialized identity providers that verify people and businesses.
It gives teams the form/application layer those systems need to receive clean, structured, governed intake data.
## **KYC Onboarding Software Evaluation Checklist**
When evaluating KYC onboarding software, ask who owns each part of the workflow.
**Evaluation question****Why it matters****What to check**Who owns the intake schema?KYC requirements change by customer type, product, jurisdiction, and risk profileForm definitions, reusable components, conditional logic, validation, versioningCan the workflow collect documents and evidence?Verification and review often depend on file evidenceSecure uploads, metadata, submission association, downstream accessDoes the submission have an API?KYC data needs to move into verification, CRM, case, banking, lending, and reporting systemsREST APIs, webhooks, JSON submissions, authentication, retry/error patternsCan permissions be scoped by role?Applicants, reviewers, admins, and auditors need different accessForm permissions, submission permissions, own/all access, SSO role mappingIs the workflow auditable?Reviewers need to understand changes and decisionsSubmission revisions, form revisions, audit logs, timestamps, user identity, notesCan the system support ongoing updates?KYC and CDD are not always one-time eventsCustomer refresh flows, changed-information capture, reviewer routing, historical recordsCan the intake live inside your product?Customer onboarding often belongs inside a portal or applicationEmbedded renderer, white-label controls, developer-owned front endCan the environment be controlled?Some teams need strict data boundary and infrastructure controlSelf-hosted or customer-controlled deployment, database/storage options, logging integrationDoes the product overclaim compliance?Software supports controls; it does not replace legal obligationsClear scope, configuration details, module requirements, evidence of controlsThe checklist helps separate a strong verification tool from a strong intake platform.
Some buyers need both.
## **When A Dedicated KYC Vendor Is The Better Fit**
Use a dedicated KYC vendor when the primary need is verification intelligence.
That includes:
- identity document verification
- biometric or liveness checks
- sanctions, PEP, and adverse media screening
- KYB data and business registry checks
- beneficial ownership data services
- fraud network signals
- country-specific document coverage
- transaction monitoring or AML case management
Those are specialized capabilities. A form platform should not pretend to replace them.
The same is true for a full client lifecycle suite. If the institution needs enterprise case management, risk scoring, remediation workflows, onboarding dashboards, periodic refresh operations, and compliance-team queues in one packaged system, a CLM platform may be the better center of gravity.
Form.io becomes more relevant when the organization already has or plans to choose those systems, but still needs to own the form layer that feeds them.
## **Where Form.io Is The Better Fit**
Form.io is the better fit when the KYC onboarding workflow is also a product, integration, and governance problem.
That usually means:
- onboarding forms need to be embedded inside a customer portal or internal product
- the data model needs to be controlled by the application team
- submissions need to become API-accessible records
- KYC providers need to be called from the workflow rather than own the whole experience
- permissions need to be scoped across applicants, reviewers, admins, and service accounts
- form and submission changes need revision history
- audit logs need to feed operational or compliance tooling
- sensitive intake data needs to remain in customer-controlled infrastructure
- teams need one governed form layer across multiple onboarding use cases
That is the buyer who should evaluate Form.io as part of a KYC onboarding software stack.
A Trustpilot reviewer called Form.io a "powerful embedded form builder" and wrote that it was "seamlessly built into our B2B application" ([Trustpilot](https://www.trustpilot.com/review/form.io)). That is a small proof point, but it points at the right fit: Form.io is strongest when developers and regulated teams need data management, integration, and control around forms, not just a hosted questionnaire.
## **Bottom Line**
KYC onboarding software is not one product category.
It is a stack.
Verification vendors help confirm identity, screen risk, and supply data. CLM platforms help manage onboarding cases and lifecycle operations. Form infrastructure governs the intake layer: what gets asked, how it is validated, where the submission lives, which systems receive it, who can access it, and what evidence remains when the process changes.
For financial-services teams, that layer deserves its own evaluation.
If the problem is buying verification coverage, choose a KYC provider. If the problem is owning regulated intake across products, portals, APIs, reviewers, audit trails, and customer-controlled infrastructure, evaluate Form.io as the form/application infrastructure around the KYC workflow.
## **FAQ**
### **What is KYC onboarding software?**
KYC onboarding software helps financial-services teams collect customer information, verify identity, assess risk, route exceptions, and preserve records during account opening or customer onboarding. The category can include identity verification tools, KYB providers, CLM platforms, and form/application infrastructure. Buyers should separate those layers before comparing vendors.
### **Is Form.io a KYC verification provider?**
No. Form.io is not an identity verification bureau, sanctions database, biometric provider, AML case-management system, or KYB data provider. It can provide the embedded form, submission, API, permissions, and workflow infrastructure around those services.
### **Where does Form.io fit in a KYC onboarding stack?**
Form.io fits at the intake and application-infrastructure layer. Teams can use it to build embedded onboarding forms, collect structured data, manage submissions, connect APIs and webhooks, scope access, preserve revisions, and deploy in customer-controlled environments. Dedicated verification vendors can still handle identity checks and screening.
### **Why are forms important in KYC onboarding?**
The form layer determines what information is collected, how it is validated, how it is stored, and how it moves into downstream systems. Weak forms create incomplete data, manual rework, inconsistent review paths, and poor audit evidence. In KYC workflows, form design is also data architecture.
### **What should financial-services teams look for in KYC intake software?**
Look for dynamic forms, conditional logic, document upload support, structured submissions, API access, webhooks, role-based permissions, revision history, audit logging, authentication integration, and deployment control. Also confirm what the product does not do, especially around legal compliance, AML policy, sanctions data, and identity verification.
### **Can Form.io help with beneficial ownership collection?**
Form.io can help teams build intake workflows that collect business entity and beneficial ownership information, validate required fields, store submissions, and route data to review or verification systems. It does not determine the legal obligation by itself. Teams should map fields and processes to current regulatory counsel and compliance requirements.
### **Can Form.io connect to KYC or AML vendors?**
Yes, Form.io is built for API-connected form workflows. Forms and submissions can be exposed through REST APIs, and webhook actions can send submission data to external systems. Teams still need to implement and govern the specific integration with their chosen KYC, AML, CRM, banking, or case-management systems.
### **Does Form.io make a financial institution compliant?**
No software makes a financial institution compliant on its own. Form.io can support regulated onboarding controls through structured intake, permissions, APIs, revisions, audit logging, and customer-controlled deployment. Compliance still depends on policy, configuration, monitoring, staff judgment, legal review, and the broader control environment.
### **When should a team choose a full KYC platform instead of Form.io?**
Choose a full KYC platform when the main need is identity verification coverage, fraud signals, sanctions screening, KYB datasets, adverse media, transaction monitoring, or packaged case workflows. Choose Form.io when the main need is to own the embedded intake layer and connect it to those specialized services.
### **Is self-hosting important for KYC onboarding software?**
It depends on the organization's risk posture, architecture, and regulatory environment. Some teams can use hosted KYC products. Others need more control over data, authentication, file storage, logging, network boundaries, and deployment. Form.io is relevant when customer-controlled infrastructure is part of the requirement.
### **How should teams start evaluating Form.io for KYC onboarding?**
Start by mapping the intake workflow: customer types, fields, documents, verification calls, exception paths, reviewer roles, submission records, audit needs, and downstream systems. Then evaluate whether Form.io can provide the governed form and API layer around the verification tools the organization already uses or plans to adopt.
[Build controlled onboarding workflows](/try-formio-for-free/) with Form.io.
# Typeform Alternatives for Self-Hosted and Regulated Teams
[  ](https://form.io/typeform-alternatives-self-hosted-compliance-bound/)Most searches for **typeform alternatives** start with a simple frustration: response limits, pricing, branding, or the one-question-at-a-time format.
Those are real reasons to compare tools. But they are not the whole decision.
If your forms collect regulated data, live inside a customer portal, support tenant-specific workflows, or need to connect directly to your application APIs, the better question is not "Which tool costs less than Typeform?" It is "Which layer of the system should own this form?"
## **Key takeaways**
- Typeform is strong for polished conversational forms, surveys, quizzes, and lead capture.
- Many Typeform alternatives compete on price, free response limits, design flexibility, or survey features.
- Self-hosted alternatives matter when the buyer needs more control over where response data lives.
- Compliance-bound teams need more than a form UX: they need permissions, auditability, deployment control, data routing, and clear responsibility boundaries.
- Form.io is a better fit when forms become embedded, API-backed application infrastructure rather than standalone surveys.
## **Quick comparison: which Typeform alternative fits the job?**
## **Scenario****Better-fit category****Examples to evaluate**Marketing forms, lead capture, quizzes, landing pagesPresentation-first form buildersTypeform, Tally, Fillout, JotformProduct feedback, NPS, CSAT, in-app surveysSurvey and feedback platformsFormbricks, SurveyMonkey, Qualtrics, SurveySparrowOpen-source or privacy-first survey collectionSelf-hosted survey toolsFormbricks, LimeSurvey, HeyForm, OpnFormRegulated intake, portals, claims, onboarding, internal workflowsForm infrastructureForm.ioCustomer-facing SaaS form buildingEmbedded and white-labeled form infrastructureForm.ioForms that need generated APIs and submission permissionsSchema-driven form/API platformsForm.io**Why teams look for Typeform alternatives**
Typeform has a clear job. It helps teams create polished, conversational forms without building a custom form experience from scratch. For many marketing, survey, quiz, and customer-feedback workflows, that is enough.
But the market around Typeform alternatives has grown because buyers often hit one of five limits.
First, pricing and response limits can become frustrating. Tally positions itself directly against Typeform by emphasizing unlimited forms and responses on its free plan, while Typeform's free plan is limited to 10 monthly responses in Tally's comparison.
Second, some teams want more layout flexibility. Fillout argues that Typeform is recognizable and polished, but more opinionated, while Fillout gives teams multi-page forms with more control over page structure and integrations.
Third, privacy and self-hosting are becoming a separate buying category. Formbricks frames itself as an open-source Typeform alternative with a self-hosted Community Edition for teams that want more control over data ownership.
Fourth, regulated teams need clearer data boundaries. Typeform publishes security, data-handling, and compliance guidance, including a compliance article stating that Typeform can provide a BAA for customers on its Enterprise plan. Its help center also documents that Typeform data is hosted on AWS, with main servers in Virginia and EU data hosting available for Enterprise and Growth Custom customers.
Fifth, some teams discover that the form is not really a survey anymore. It is intake. It is workflow. It is a record. It is a customer-facing feature. It is part of the application.
That fifth case is where Form.io belongs in the conversation.
## **The three types of Typeform alternatives**
The mistake is treating all Typeform alternatives as one category.
They are not.
### **1. Presentation-first form builders**
These tools compete with Typeform on form creation speed, design, free tiers, templates, payment collection, embeddability, and basic automation.
They are often the right answer when the form is a marketing asset or a lightweight business workflow. If the team needs a better-looking contact form, a free survey, a quiz, a registration form, or a lead-capture flow, a presentation-first tool may be enough.
This category is where Tally, Fillout, Jotform, Paperform, and similar tools usually compete.
The tradeoff is that the form usually remains a standalone tool. It may integrate with the rest of the stack, but it does not become the infrastructure layer that governs submissions, permissions, APIs, tenants, and deployment environments.
### **2. Privacy-first survey and feedback platforms**
These tools compete on self-hosting, open-source access, feedback workflows, product surveys, NPS, CSAT, in-app micro-surveys, and user research.
Formbricks is a good example. Its Typeform-alternative page emphasizes open source, self-hosting, link surveys, in-app micro-surveys, pop-up surveys, Dockerized deployment, and an open API.
That is a strong fit when the main object is feedback.
But feedback is not the same as application intake. A survey platform may own responses, contacts, segments, and feedback analytics. It may not be designed to become the form/API layer inside a regulated portal, insurance claim workflow, government service, or B2B SaaS product.
### **3. Form infrastructure platforms**
This is the category most Typeform-alternative lists miss.
Form infrastructure is for teams whose forms need to do more than collect answers. These forms need to render inside an application, validate structured data, create submission records, expose APIs, route data to internal systems, respect permissions, survive audits, and remain under the customer's deployment control.
That is the Form.io case.
Form.io describes itself as a self-hosted developer productivity platform for building forms, APIs, and workflows. Its "How Form.io Works" page explains that the drag-and-drop builder creates forms and APIs together, that every form and resource has an automatically generated REST API, and that the platform can be embedded in the customer's own environment ([How Form.io Works](https://form.io/how-it-works/)).
When the buyer needs that layer, Typeform alternatives should not be judged only by design, templates, or monthly response caps.
## **Where self-hosting changes the decision**
Self-hosting is not automatically required. Plenty of teams are better served by a managed SaaS form tool.
But self-hosting changes the evaluation when forms collect sensitive data, connect to internal systems, support regulated workflows, or sit inside a product your team owns.
IBM's 2025 Cost of a Data Breach report puts the global average cost of a data breach at $4.4 million ([IBM Cost of a Data Breach 2025](https://www.ibm.com/reports/data-breach)). That is not a form-builder statistic, and it should not be used that way. It is a reminder that data collection boundaries have real financial and operational consequences.
Data-control expectations are also moving into mainstream architecture decisions. BARC's 2026 data sovereignty survey found that 76% of respondents expect data sovereignty to become more important, which helps explain why "where does this form data live?" is no longer a niche legal question ([BARC data sovereignty survey](https://barc.com/news/data-sovereignty-2026-survey/)).
Verizon's 2026 DBIR summary says 31% of breaches now start with software vulnerabilities and 48% involve ransomware ([Verizon DBIR 2026](https://www.verizon.com/business/resources/reports/dbir/)). Again, that does not mean a form tool causes the risk. It means buyers should care about where software runs, how it is patched, how access works, and who controls the data path.
For a lightweight survey, a hosted form tool can be perfectly reasonable.
For regulated intake, the questions change:
- Where is submission data stored?
- Can the platform run in our environment?
- Can fields be encrypted where needed?
- Can permissions apply to submissions, not just workspace users?
- Can audit logs show what happened?
- Can dev/test/prod environments support controlled changes?
- Can forms connect to our APIs without routing sensitive data through unnecessary third parties?
Those are infrastructure questions.
## **Why Form.io is different from most Typeform alternatives**
Form.io is not trying to be a prettier Typeform clone.
That matters.
Form.io is built around the idea that a form can be a governed schema. The form definition can drive rendering, validation, submitted data shape, generated API endpoints, permissions, and workflow actions.
The practical difference shows up in four places.
### **Forms and APIs are connected**
In Typeform and many alternatives, the form is mainly a collection surface. You can export data, trigger integrations, or connect webhooks, but the form itself is not usually the application data layer.
Form.io's model is different. Its builder and platform center on JSON-powered forms and APIs. Form.io's own product documentation says every form and resource has an automatically generated REST API associated with it.
That is useful when every new form would otherwise require engineering work to create endpoints, validation, storage, and integration behavior.
### **Deployment can stay inside your environment**
Typeform and many alternatives are hosted SaaS products. Some newer alternatives offer self-hosting, especially in the open-source survey category.
Form.io's self-hosted story is more infrastructure-oriented. Its configuration-based pricing page describes API server environments, enterprise projects, PDF server options, dev/test/prod configurations, self-hosted databases, and security compliance features in API Plus configurations ([Form.io configuration-based pricing](https://form.io/configuration-based-pricing/)). Its self-hosted enterprise forms page also frames the Developer Portal, forms, projects, permissions, and submissions as running inside the customer's own environment ([self-hosted forms for enterprise](https://form.io/features/self-hosted-forms-for-enterprise/)).
That is a better match when the buyer is not allowed to treat form data as a casual SaaS export.
### **Governance is tied to the form layer**
Regulated forms often need more than account-level access control. Teams may need form-level permissions, submission-level access, field-level encryption, revision history, action logs, submission revision logs, and audit evidence.
Form.io's security-compliance materials describe advanced audit logging, action logs, form revisions, submission revision logs, submission collections, field-level encryption, and container security scanning as part of its security module and API Plus feature set ([Form.io secure forms compliance readiness](https://form.io/features/secure-forms-compliance-readiness/)).
That is also how broader security frameworks talk about control. NIST SP 800-53 treats security and privacy controls as part of organization-wide risk management, not as isolated software checkboxes ([NIST SP 800-53 Rev. 5](https://csrc.nist.gov/pubs/sp/800/53/r5/upd1/final)).
That does not mean every Form.io buyer needs every module. It does mean the platform is designed for teams that need those questions answered at the form infrastructure layer.
### **Embedded form building is a platform feature**
Some Typeform alternatives let you embed a form. That is not the same as embedding a governed form-building capability inside your own product.
Form.io can support teams that need form rendering and form building inside their application experience, including white-labeled and tenant-aware scenarios. Its Enterprise Form Builder Module is positioned for exposing a customized form-building experience inside the customer's own application ([Enterprise Form Builder Module](https://form.io/enterprise-form-builder-module/)).
That is where Form.io becomes relevant to SaaS platforms, government portals, healthcare products, insurance workflows, and financial services onboarding.
## **A practical shortlist of Typeform alternatives**
### **Choose Typeform when presentation matters most**
Typeform still makes sense when the primary goal is polished conversational UX, surveys, quizzes, lead capture, and a familiar visual form-building experience. If the form is not regulated, not deeply embedded, and not part of your product architecture, Typeform may be enough.
### **Choose Tally when free limits are the issue**
Tally is a strong fit when the buyer wants a simpler and more generous free form builder. Its comparison page emphasizes unlimited forms, unlimited responses, conditional logic, file uploads, payments, and API access on lower-cost or free tiers.
### **Choose Fillout when the issue is flexibility**
Fillout is worth evaluating when the buyer wants modern form building, stronger free response limits, database-style integrations, multi-page forms, and more layout flexibility than Typeform's one-question-at-a-time format.
### **Choose Formbricks when the job is self-hosted surveys**
Formbricks is a strong fit when the buyer wants open-source, self-hosted surveys, product feedback, NPS, CSAT, website surveys, or in-app micro-surveys. It is especially relevant when the team wants a privacy-first Typeform alternative but still thinks in survey and feedback terms.
### **Choose Form.io when forms become infrastructure**
Form.io is the better fit when the buyer needs forms to become part of the application stack: embedded rendering, generated APIs, submission storage, permissions, actions, security/compliance modules, self-hosted deployment, and controlled form lifecycle.
A Form.io customer proof point from Safety Mojo captures the reason this matters: "Form.io cleans up all the dirty work and does it for you" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)). On G2, another reviewer points to "the level of customization that can go into every form" ([Form.io reviews on G2](https://www.g2.com/products/form-io/reviews)). That is the value when the dirty work is not just building a form, but keeping forms, data, APIs, and workflow behavior aligned.
The scale proof points point in the same direction. Form.io's publicplan case study describes support for more than 400 services and 1,000+ forms in a German public-sector context, while the TauRes case study reports an estimated 50% reduction in data-processing workload after standardizing acquisition workflows around Form.io ([publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/), [TauRes case study](https://form.io/case-studies/taures-case-study-data-acquisition-and-analysis/)).
## **Decision framework**
Ask these questions before choosing a Typeform alternative:
**Question****If yes, look at**Do we mainly need a better free plan or lower-cost form builder?Tally, Fillout, JotformDo we mainly need surveys, NPS, CSAT, or product feedback?Formbricks, SurveyMonkey, QualtricsDo we need open-source or self-hosted survey collection?Formbricks, LimeSurvey, HeyFormDo forms need to live inside our application or portal?Form.ioDo submissions need generated APIs, permissions, and audit-relevant controls?Form.ioDo customers or tenants need to build forms inside our product?Form.ioDo we need a simple marketing form this week?Typeform or a presentation-first alternativeThe strongest decision comes from naming the job.
If the job is presentation, choose a presentation-first tool.
If the job is feedback, choose a survey platform.
If the job is governed application intake, choose form infrastructure.
## **FAQ**
### **Which Typeform alternative should you choose?**
There is no single universal Typeform alternative. Tally and Fillout are strong for lower-cost form building, Formbricks is strong for open-source and self-hosted surveys, and Form.io is stronger when forms need to become embedded, API-backed application infrastructure.
### **Is there a self-hosted Typeform alternative?**
Yes. Formbricks is a strong self-hosted survey alternative. Form.io is also self-hosted, but it solves a different problem: governed forms, generated APIs, submissions, permissions, and workflow behavior inside customer-controlled environments.
### **Is Typeform good for regulated data collection?**
Typeform publishes security and compliance materials and says it can provide a BAA for Enterprise customers in relevant HIPAA contexts. Regulated teams should still verify hosting, data residency, contractual scope, retention, access control, audit, and integration requirements before choosing any hosted form tool.
### **When is Form.io a Typeform alternative?**
Form.io is a Typeform alternative when the real requirement is not just a nice form experience, but embedded forms, self-hosted deployment, generated APIs, submission records, permissions, and governed workflow infrastructure.
### **Is Form.io a survey tool?**
Form.io can collect survey-like data, but it is better understood as a form and API platform. It is usually a stronger fit for application forms, portals, regulated intake, workflow forms, and customer-facing form infrastructure than for simple standalone surveys.
### **Which Typeform alternative fits product feedback?**
Formbricks is worth evaluating for product feedback, in-app micro-surveys, NPS, CSAT, and privacy-first survey workflows. It is designed around feedback collection rather than general form infrastructure.
### **Which Typeform alternative fits embedded forms?**
Form.io is usually the better fit when forms need to be embedded into a customer-facing application and governed as part of the product architecture rather than embedded as standalone survey widgets.
### **Which Typeform alternative fits compliance-bound workflows?**
It depends on the compliance requirement. A hosted tool may be enough for low-risk workflows with the right contracts and settings. For stricter control over deployment, storage, APIs, permissions, and audit evidence, Form.io is often the more relevant category fit.
### **Can Form.io replace Typeform?**
Form.io can replace Typeform when the organization needs self-hosted, embedded, API-backed form infrastructure. It may be too much platform for a simple marketing survey, quiz, or event-registration form.
### **What should developers compare before choosing?**
Developers should compare hosting model, schema ownership, API behavior, validation, permissions, submission storage, audit needs, SDK/rendering model, deployment environments, and whether the form needs to live inside an application users already trust.
## **Final recommendation**
For simple campaigns and surveys, choose the form tool that gets the job done with the least operational burden.
For feedback programs, choose a survey platform with the right data and research workflow.
For regulated intake, embedded portals, tenant-aware SaaS forms, and form-driven application workflows, evaluate Form.io as infrastructure, not as another prettier form builder.
The distinction matters because a form is sometimes just a form. But when the data, API, permissions, workflow, and deployment boundary all depend on it, the form has become part of the architecture.
[Try Form.io for free](https://form.io/try-formio-for-free/) to see how self-hosted forms, generated APIs, and governed submission workflows fit inside your application environment.
# Jotform Alternative for Regulated Teams: When Hosted Forms Are Not Enough
[  ](https://form.io/alternatives-to-jotform-regulated-industries/)Jotform is a strong hosted form builder when the job is to create a form quickly.
That is not the same as choosing form infrastructure for regulated work.
If your forms collect sensitive data, drive downstream decisions, live inside a product, or need to satisfy audit and security teams, the real question is not only which builder is easiest. It is which platform gives you enough control after the form is submitted.
## **The Short Version**
Most Jotform alternative lists compare templates, pricing, free plans, conditional logic, integrations, and form design.
Those things matter. They just do not settle the decision for regulated teams.
If your use case is a marketing form, event registration form, internal survey, or lightweight intake workflow, a hosted builder may be the right answer. If your use case is healthcare intake, government services, insurance claims, financial onboarding, customer portals, or embedded SaaS workflows, you need to evaluate a different layer.
For those teams, a serious Jotform alternative should be judged by:
- where the platform runs
- who controls submission data
- how authentication and permissions work
- whether forms generate APIs
- whether form and submission changes are auditable
- whether the form builder can be embedded and white-labeled
- whether the platform can fit into the systems you already govern
That is where Form.io belongs in the conversation.
Form.io is not the fastest option for a one-off hosted form. It is the stronger fit when forms become part of application infrastructure.
## **Why Most Jotform Alternative Lists Miss the Regulated Buyer**
Most search results for `jotform alternative` are written for broad software shoppers.
They usually ask familiar questions:
- Which tool is cheaper?
- Which one has better templates?
- Which one is easier for a nontechnical team?
- Which one has the most integrations?
- Which one has the cleanest form design?
That comparison is useful for simple workflows. It is incomplete for regulated ones.
A hospital intake workflow, public-sector application, insurance claim, KYC onboarding flow, or embedded customer portal cannot be evaluated only by front-end form features. The submitted data becomes part of a larger system. It may need to be retained, corrected, audited, routed, exported, approved, signed, versioned, or tied to a specific policy decision.
That moves the decision out of the form-builder category and into the architecture layer.
The right question becomes: can the form platform respect the control surface around the form?
## **The Real Buying Question: Hosted Builder or Controlled Infrastructure?**
There are two different jobs hiding behind the same keyword.
The first job is form creation. A team needs to publish a polished form, collect responses, and send data somewhere useful. Hosted builders are good at this. They reduce setup time, give nontechnical users a friendly workspace, and make common forms easy to ship.
The second job is governed data collection. A team needs forms to run inside a larger application boundary, use existing authentication, expose durable APIs, preserve record history, and support audit evidence when something changes.
Those are not the same job.
The first job rewards speed. The second rewards control.
That does not make hosted builders bad. It means regulated teams need to know when the category changes.
## **Where Hosted Form Builders Work Well**
A hosted form builder can be the right choice when the workflow is narrow and the organization accepts the vendor-managed model.
Use a hosted builder when:
- the form is standalone
- the data does not need to stay inside your own environment
- the workflow can live in the vendor's dashboard
- standard integrations are enough
- nontechnical creation matters more than developer control
- the form does not need to become part of a product or governed application
This is why broad Jotform alternative lists often recommend tools like Typeform, Google Forms, Tally, Fillout, Cognito Forms, Formstack, FormAssembly, or other hosted builders. For simple forms, those recommendations can make sense.
Regulated teams should be more careful.
The moment the form sits inside a controlled business process, the tool has to answer questions that template libraries cannot answer.
## **Where Regulated Teams Need More Than a Hosted Builder**
Regulated workflows usually fail at the edges.
The form itself looks fine. The problem appears after submission.
Who can see the data? Which system owns the record? What happens when the form schema changes? Can a historical submission still be understood against the form version that captured it? Did the webhook fire? Who changed the claim amount, diagnosis note, eligibility field, or approval status? Can the organization prove it later?
These are ordinary questions in healthcare, government, finance, education, insurance, and other regulated settings.
They also map directly to formal control programs. NIST SP 800-53 Rev. 5 organizes security and privacy controls across families such as [Access Control, Audit and Accountability, Identification and Authentication, Incident Response, Risk Assessment, and System and Communications Protection](https://csrc.nist.gov/pubs/sp/800/53/r5/upd1/final). HHS says the [HIPAA Security Rule](https://www.hhs.gov/hipaa/for-professionals/security/laws-regulations/index.html) establishes national standards for electronic protected health information and requires administrative, physical, and technical safeguards. A form platform used in regulated work does not sit outside those concerns. It becomes one of the places those concerns show up.
IBM's 2025 Cost of a Data Breach report gives the risk scale. IBM reports a [global average breach cost of $4.4 million](https://www.ibm.com/reports/data-breach), and also reports that 63% of organizations lacked AI governance policies to manage AI or prevent shadow AI. Verizon's [2026 Data Breach Investigations Report](https://www.verizon.com/business/resources/reports/dbir/) adds another useful warning: software vulnerabilities now start 31% of breaches, which is why regulated teams should evaluate the form platform as software infrastructure, not only as a form-design surface.
Forms are one of those systems.
## **What a Regulated Jotform Alternative Should Prove**
A regulated team should not start with "Which form builder is easiest?"
Start with the control requirements.
### **Deployment Boundary**
Where does the platform run?
For some teams, vendor-managed SaaS is acceptable. For others, sensitive data must remain inside a private cloud, on-premise environment, government-approved network, customer-controlled database, or specific regional boundary.
That is one of Form.io's clearest differences. Form.io's [self-hosted forms for enterprise](/features/self-hosted-forms-for-enterprise/) model is built so the platform can deploy inside environments the customer controls. The same core surfaces, including form builder, REST API generation, submission handling, and renderer libraries, can run within the customer's infrastructure.
This matters because deployment is not just an IT preference. It shapes data residency, incident response, logging, backup strategy, access review, and compliance ownership.
### **Data Ownership and Submission Control**
The form response is not just a row in a vendor dashboard.
For regulated teams, a submission may become a patient record, claim record, case file, intake record, eligibility input, identity artifact, or workflow event. The platform needs to fit the system that owns that record.
Form.io's architecture stores forms, resources, submissions, users, and project data as JSON documents in the customer's MongoDB or MongoDB-compatible database. That document model is part of why Form.io can treat form definitions and submission records as application data rather than isolated form entries.
If your team needs application-owned data, this distinction matters more than builder polish.
### **Authentication and Permissions**
Regulated forms rarely have one kind of user.
A healthcare intake flow may involve patients, providers, administrators, support staff, and compliance reviewers. A government service workflow may involve applicants, case workers, supervisors, auditors, and external systems. A SaaS product may need tenant admins, end users, implementation teams, and internal support roles.
The platform has to respect those boundaries.
Form.io's [roles and permissions](/features/forms-for-teams/) model is built around controlling who can create forms, view submissions, modify data, manage projects, and interact with APIs. That matters when the same form infrastructure supports different departments, customers, tenants, or workflow stages.
For regulated teams, permissions are not an admin convenience. They are part of the evidence trail.
### **Generated APIs**
Many hosted form tools expose APIs. That does not mean the form is the API contract.
The stronger architecture is schema-driven: the same definition that renders the form also defines the submission structure and API behavior around it. Form.io's [form from JSON](/features/form-from-json/) model gives teams a JSON-based form definition that can render interfaces and support generated APIs from the same source.
This is useful when forms feed applications, not just spreadsheets.
It lets developers treat forms as governed application surfaces: forms, resources, submissions, validation, webhooks, and workflow actions can be reasoned about together instead of being scattered across a visual builder, a separate API layer, and custom glue code.
### **Audit Trails and Revisions**
Regulated teams need to know more than whether a form was submitted.
They need to know what changed.
Form.io's [complete audit trail](/features/log-forms-complete-audit-trail/) capabilities distinguish between submission revisions and server audit logging. Submission revisions track field-level changes to submitted data. Server audit logging captures system activity such as authentication, form access, API requests, and data modification events.
That distinction matters. An auditor may need to know that a submission was created by one user, modified by another, and later viewed through a specific role or project context. A support team may need to know whether a webhook ran. A compliance team may need to know which form revision captured a historical record.
For financial services, this is not an abstract preference. The [FTC Safeguards Rule](https://www.ecfr.gov/current/title-16/chapter-I/subchapter-C/part-314) requires financial institutions to monitor and log authorized-user activity and detect unauthorized access, use, or tampering with customer information. It also creates retention and change-management expectations around customer information systems.
Form.io's [secure forms compliance readiness](/features/secure-forms-compliance-readiness/) capabilities also include advanced audit logging, action logs, form revisions, submission revision logs, submission collections, and container security scanning as part of the Security Module.
That is a different category of answer than "the form has an activity log."
### **Embedded and White-Labeled Use**
Many regulated forms do not belong on a third-party hosted page.
They belong inside a patient portal, citizen service portal, claims application, financial onboarding flow, education system, or B2B SaaS product.
That creates two requirements at once: the form needs to feel native to the product, and the form data needs to move through the product's security and workflow model.
Form.io is designed for embedded use. Developers can render forms inside their own applications, use the platform's APIs, and let business users modify schemas after the application is in place. For software teams, this is often the useful compromise: developers own the system boundary, while business teams can still manage many form changes without reopening every application ticket.
## **Comparison Table: Jotform Alternative Categories**
**Category****Best fit****Strength****Risk for regulated teams**Hosted no-code form builderSimple forms, surveys, registration, marketing captureFast setup and low technical burdenData and workflow live primarily in the vendor-managed modelHosted enterprise form suiteBusiness teams that need more compliance features and admin controlBetter security, SSO, compliance options, supportMay still be separate from the customer's application infrastructureIndustry-specific form toolNarrow healthcare, education, legal, or government workflowsBetter fit for one vertical's common use casesCan be too narrow for cross-department or product-embedded workflowsCustom-built formsUnique internal systems with strong engineering ownershipMaximum controlExpensive to build, secure, document, version, and maintainSelf-hosted form infrastructureRegulated teams where forms are part of real applicationsDeployment control, APIs, permissions, revisions, audit evidence, embedded useRequires technical ownershipThe last row is where Form.io fits.
It is not the right answer for every team looking for a Jotform alternative. It is the right answer when the team has outgrown the assumption that forms are standalone assets.
## **Why Form.io Is Different From a Normal Form Builder**
Form.io is easier to understand when you stop treating it as a lighter or heavier version of a hosted form builder.
It is infrastructure for forms and the APIs around them.
The visual builder creates schemas. The renderer turns those schemas into forms inside applications. The API server manages forms, resources, submissions, permissions, projects, and actions. The self-hosted deployment model lets the customer run that infrastructure inside their own environment.
That is why Form.io's own guidance is direct about fit. In Form.io's article on [why teams should not use Form.io without a developer team](https://form.io/why-you-shouldnt-use-formio-if-you-dont-have-a-dev-team/), the product is framed as infrastructure software for software developers building custom applications, not a simple form builder for nontechnical users. In other words, it is the wrong choice if a marketing team needs a simple form live this afternoon, and the better choice if a software team needs forms to behave like governed application infrastructure.
That honesty is valuable.
The buyer who only wants speed should not be pushed into infrastructure. The buyer who needs control should not be pushed into convenience software that will fail later.
## **Proof That This Is a Real Deployment Problem**
This is not theoretical positioning.
Form.io's public case-study library includes publicplan GmbH, where the project supported [more than 400 public-sector services and 1,000+ forms](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/) with strict standards and a short timeline. That kind of workload is not a normal contact-form problem. It is a repeatable public-service infrastructure problem.
The same pattern shows up in customer sentiment. A Trustpilot reviewer described Form.io as useful for both integration and standalone use and praised support when users get stuck ([Trustpilot](https://www.trustpilot.com/review/form.io)). The wording is simple, but the integration point is doing real work. Regulated teams are rarely buying a form in isolation. They are buying a form layer that has to connect to the rest of the system.
## **When Form.io Is the Wrong Jotform Alternative**
Form.io is not the right replacement if the team wants the fastest possible hosted form with the least technical setup.
Choose a simpler hosted builder when:
- the form is temporary
- the data is low risk
- the workflow is not part of a product
- the team does not have developers available
- vendor-managed hosting is acceptable
- the organization does not need custom API, identity, or audit architecture
That is not a failure case. It is buyer fit.
For simple forms, infrastructure can be too much.
## **When Form.io Is the Right Jotform Alternative**
Form.io becomes the stronger answer when the form is part of the system.
That usually means one or more of these conditions is true:
- submission data must stay inside a controlled environment
- forms are embedded in a customer-facing application
- different users need different permissions
- submissions need to become application records
- the team needs APIs generated from form definitions
- changes to forms and submissions need revision history
- workflows depend on webhooks, actions, approvals, or integrations
- the organization needs audit evidence after submission
- the platform must support multiple teams, tenants, projects, or environments
These are the use cases where "easy form builder" becomes too small a category.
For those teams, Form.io's advantage is not that it hides complexity. It is that it gives the team places to put the complexity where it belongs: deployment, schema, API, permissions, revisions, audit logs, workflow actions, and application integration.
## **Key Takeaways**
- A broad Jotform alternative list is useful for simple form-building needs.
- Regulated teams need to evaluate deployment boundary, data ownership, permissions, APIs, auditability, and embedded use.
- Hosted builders can work when the form is standalone and vendor-managed storage is acceptable.
- Form.io is strongest when forms become application infrastructure inside customer-controlled environments.
- The right choice depends less on builder polish and more on what must happen after the form is submitted.
## **FAQ**
### **What is the best Jotform alternative for regulated teams?**
The best Jotform alternative depends on the control requirements. If the team only needs a hosted form with better pricing or templates, a simpler hosted builder may be enough. If the team needs self-hosting, APIs, permissions, audit trails, revisions, and embedded application workflows, Form.io is a stronger fit.
### **Is Form.io easier to use than Jotform?**
Not for simple hosted forms. Jotform is easier for nontechnical teams that need to create and publish forms quickly. Form.io is built for teams that need developer control, application integration, self-hosted deployment, generated APIs, and governance around forms and submissions.
### **When should a team avoid Form.io?**
Avoid Form.io when the form is simple, standalone, low risk, and needs to be created by a nontechnical user without developer involvement. Form.io expects technical ownership, especially for self-hosted deployments and production application integration.
### **Why would a regulated team outgrow a hosted form builder?**
Hosted form builders can become limiting when the workflow needs controlled data residency, internal authentication, custom permissions, API-driven records, audit logs, revision history, or direct embedding inside a product or portal. Those needs turn the form into part of the application architecture.
### **Does Form.io support self-hosted forms?**
Yes. Form.io can be deployed in customer-controlled environments, including cloud, private data center, and Docker-based deployments. That gives teams more control over where form infrastructure runs and how submission data fits their existing security boundary.
### **Does Form.io generate APIs from forms?**
Yes. Form.io's schema-driven model uses form and resource definitions to support REST API behavior around submissions, validation, resources, permissions, and workflow actions. That makes it useful when forms are interfaces into application data, not just hosted pages.
### **Is Form.io HIPAA compliant?**
Form.io provides technical capabilities that can support HIPAA-governed workflows in customer-controlled environments, but the customer remains responsible for its compliance program, configuration, policies, deployment controls, and business associate requirements.
### **Does a BAA make a form workflow compliant?**
No. HHS explains that [business associate contracts](https://www.hhs.gov/hipaa/for-professionals/covered-entities/sample-business-associate-agreement-provisions/index.html) define permitted uses, safeguards, breach reporting, access, amendment, accounting, subcontractor, and termination obligations. A BAA matters, but compliance also depends on how the workflow is configured, secured, monitored, and governed.
### **Why do audit trails matter for form submissions?**
Audit trails help answer who accessed data, who changed it, what changed, when it changed, and which workflow action ran. For regulated teams, that evidence can matter as much as the original submission.
### **Can Form.io be embedded inside a SaaS product?**
Yes. Form.io is designed for embedded application use. Developers can render forms inside their own applications, connect them to Form.io APIs, and let authorized business users manage form schemas after the product infrastructure is in place.
### **What should I ask before choosing a Jotform alternative?**
Ask where data is stored, who controls deployment, how permissions work, whether APIs are generated from the form schema, how revisions are handled, whether audit logs are available, and whether the form can live inside your own application or portal.
## **Build Regulated Form Infrastructure With Form.io**
If you only need a quick hosted form, choose the simplest tool that satisfies the job.
If your forms define application workflows, submission records, permissions, APIs, audit evidence, and deployment boundaries, choose infrastructure that respects that reality.
[Try Form.io for regulated form infrastructure](/try-formio-for-free/).
# Formbricks vs Form.io: Survey Tool or Form Infrastructure?
[  ](https://form.io/formbricks-formio-vs-formbricks-self-hosted-typeform-alternative/)Organizations looking for a self-hosted alternative to Typeform or a privacy-first feedback platform often compare Formbricks and Form.io. Both have open-source and self-hosted evaluation paths, but they solve fundamentally different problems.
Formbricks focuses on surveys, experience management, and product feedback. Form.io is designed as application infrastructure for forms, APIs, workflows, and enterprise governance, including agentic workflow patterns where governed forms and submissions need to stay connected to permissions, validation, actions, and audit evidence.
That distinction matters before the feature checklist begins. The question is not whether both products can build forms. It is whether the form is mainly a survey or part of the application architecture.
## **Key takeaways**
- Formbricks is best understood as an open-source experience management and survey platform for link surveys, website surveys, in-app surveys, email surveys, and customer feedback workflows.
- Form.io is best understood as form-driven application infrastructure: JSON-defined forms, generated APIs, submission data, permissions, workflow actions, self-hosted deployment, and governed patterns for agentic workflows.
- Formbricks is a credible choice when the buyer wants a self-hosted Typeform alternative or privacy-first feedback tool.
- Form.io is the better fit when forms need to be embedded in a product, reused across tenants, governed through submission-level permissions, exposed through APIs, managed across enterprise environments, or used as structured context for agentic workflows.
- The main question is not “Which one is open source?” It is “Does your form need to collect feedback, or does it need to become part of the application architecture?”
## **Quick comparison**
The comparison below summarizes the product jobs documented in Formbricks’ platform, API, self-hosting, and licensing docs and Form.io’s JSON schema, generated API, self-hosting, and embedded builder pages.
## **Decision area****Formbricks****Form.io**Primary jobOpen-source surveys and experience managementForm and API infrastructure for embedded, governed applications and agentic workflowsBest use caseFeedback, NPS, CSAT, product surveys, link surveys, in-app micro-surveysRegulated intake, customer-facing product forms, portals, workflow forms, schema-driven applications, and agentic workflow interfacesForm modelSurvey flows and question types for response collectionJSON schemas that define UI, validation, submission structure, and backend APIsAPI modelPublic Client API for survey interactions and Management API for surveys, contacts, responses, and webhooksForm and resource paths generate schema and submission endpointsEmbeddingWebsite, app, email, and link survey deliveryRenderer and builder embedded directly into customer-controlled applicationsGovernance centerSelf-hosting, privacy, survey data control, open-core packagingProject, form, and submission permissions; roles, actions, audit patterns, stages, and deployment boundariesBest buyerProduct, growth, customer experience, and feedback teams that need open-source surveysDevelopment teams building form-heavy products, portals, and enterprise workflowsWrong fit warningNot designed to be the form/API layer for every application workflowNot the lightest answer for simple surveys or one-off feedback forms**What Formbricks is good at**
Formbricks deserves a fair reading. Its official docs describe it as an open-source platform for collecting and analyzing feedback from customers, users, and employees through targeted surveys.
That is a real product category.
If your team needs NPS surveys, CSAT surveys, product feedback, onboarding feedback, churn surveys, website surveys, in-app micro-surveys, or link-based surveys, Formbricks is built for that motion. Its homepage frames the product around privacy-first experience management, feedback collection across websites and apps, and self-hosting when a team wants more control over data.
Its open-source form builder page also makes the category clear: unlimited forms, unlimited responses, open-source survey building, conditional logic, multi-language surveys, integrations, hidden fields, partial submissions, single-use links, and custom domains.
That matters because the Typeform-alternative search is not only about technical architecture. Many buyers really do want a better survey tool: more generous limits, more privacy control, self-hosting, open-source code, and enough product polish for feedback collection.
Formbricks has a strong claim there.
The question is what happens when the form is not mainly a survey.
## **What Form.io is good at**
Form.io is strongest when the form is not just a feedback surface, but part of the application contract. Its value shows up when a team needs JSON-defined forms, generated APIs, submission records, validation, permissions, workflow actions, audit patterns, and self-hosted deployment to stay aligned.
That includes regulated intake, customer portals, tenant-managed SaaS forms, healthcare and financial workflows, government services, insurance claims, and internal processes where the submitted record needs to remain explainable over time.
It also matters for agentic workflows. If an AI agent or human-in-the-loop workflow needs to ask for data, validate fields, route submissions, require confirmation, or operate inside an enterprise governance boundary, the form layer needs to be more than a survey delivery tool. Form.io gives developers a governed form and API layer that can become part of that workflow infrastructure.
So the Form.io category should appear early in the decision: it is not the survey tool in this comparison. It is the form infrastructure layer when forms, submissions, APIs, and workflow behavior need to be owned by the application.
## **What changes when a survey becomes application infrastructure**
A survey collects feedback. Application infrastructure carries business process.
That line gets blurry at first. A customer feedback form can become a support workflow. A product survey can feed account health. A compliance questionnaire can become an auditable record. A tenant-specific intake form can become a feature inside a SaaS platform. A public-facing form can become the first step in a case management workflow.
At that point, the evaluation changes.
The buyer is no longer asking only whether the tool can collect a response. The buyer is asking:
- Who owns the schema?
- What validates the submission?
- Which API receives and exposes the data?
- Can the form be embedded inside our product?
- Can customers build or modify their own forms inside our app?
- Can roles and permissions apply at the form and submission level?
- Can the same form move through development, test, and production?
- Can historical submissions remain explainable after form definitions change?
Those are Form.io questions.
Form.io’s [drag-and-drop form builder and APIs](https://form.io/features/drag-and-drop-form-builder-apis/) page describes the builder as a JSON schema editor that defines form UI, validation, the data model, and REST API endpoints together. That is the architectural difference.
Formbricks is strong when the workflow is survey-led. Form.io is strong when the form is a contract between the user interface, submitted data, backend API, permissions, and downstream process.
## **Survey flows vs schema contracts**
Formbricks is optimized around survey delivery. Its own Typeform-alternative page describes link surveys, in-app micro-surveys, pop-up surveys, Dockerized self-hosting, an open API, and open-source customization.
That is useful when the main asset is a survey.
Form.io starts from a different object: the form schema. Every Form.io form is a JSON document that defines the title, path, display mode, components, validation, conditional logic, and submission data shape.
That schema can render in an application, accept submissions, validate data, and create predictable API behavior. The form is not only a front-end artifact. It is the source of truth that connects rendering, validation, submission storage, and backend endpoints.
This matters when multiple systems need to trust the same form definition.
If the form is only a feedback survey, a survey-first platform is usually enough. If the form is a reusable business object across applications, tenants, workflows, and environments, the schema needs to carry more responsibility.
That is where Form.io’s model becomes more valuable.
## **API and data model comparison**
Formbricks has APIs, and the comparison should say that clearly. Its REST API documentation describes two API surfaces: a Public Client API for frontend survey interactions and a Management API for backend management tasks. The exposed methods include displays, responses, contacts, surveys, action classes, contact attributes, and webhooks.
That API surface fits a survey and feedback product.
Form.io’s API model is different because the form path and schema define the submission API itself. The [Forms from JSON](https://form.io/features/form-from-json-schema/) documentation explains that a form path can create endpoints for retrieving the schema and creating, listing, reading, updating, and deleting submissions.
That changes the center of gravity.
In Formbricks, the API helps manage and operate surveys. In Form.io, the form can define part of the application data layer.
For feedback collection, Formbricks’ model is sensible. For application intake, regulated submissions, onboarding flows, service requests, claims, eligibility workflows, or tenant-managed forms, Form.io’s generated form/submission API model is usually the more direct fit.
## **Embedding and white-labeling**
Formbricks can reach users in useful places: websites, apps, email, pop-ups, and links. That is exactly what a survey platform should do. For customer experience teams, that flexibility matters because feedback is most useful when it appears at the right moment in the product journey.
Form.io uses embedding for a different purpose.
The [Form.io open-source page](https://form.io/open-source/) explains that forms are rendered from JSON using Form.io renderers for frameworks such as Vanilla JavaScript, Angular, React, and Vue. The [Enterprise Form Builder Module](https://form.io/product-announcement/enterprise-form-builder-module/) goes further: it lets teams embed a customizable, white-labeled form-building interface directly into their own applications.
That is not the same as embedding a survey.
It means a SaaS platform, healthcare product, government portal, insurance system, or internal enterprise app can expose governed form creation to its users without sending those users into a separate form product. The application still controls navigation, authentication, permissions, branding, allowed components, data model, and workflow behavior.
That is a major distinction for platform teams.
If you want to ask users for feedback, Formbricks may be the cleaner answer. If your customers need to build and manage forms inside your product, Form.io fits the architecture more directly.
## **Self-hosting, licensing, security, and governance**
Do not reduce this comparison to “self-hosted vs not self-hosted.” Formbricks is a legitimate self-hosted option. Its self-hosting docs describe cloud hosting, free self-hosting, self-hosting with an Enterprise Edition license, Docker setup, one-click setup, migration, configuration, and integrations.
Formbricks’ license docs also give useful detail. The core source code is AGPLv3, while larger-team and enterprise functionality lives under a separate enterprise license. The Community Edition includes self-hosting for commercial purposes, unlimited surveys, unlimited responses, unlimited users, API access, SDKs, website and app surveys, webhooks, multi-language surveys, and integrations. Enterprise features include items such as teams and access roles, audit logs, SSO, two-factor authentication, contact management, quota management, and prioritized support, depending on the license configuration.
That is a strong open-source story, but buyers need to understand the packaging.
Open source and self-hosting are valuable. They are not the same thing as complete application governance.
GitHub’s 2025 Octoverse report shows why this nuance matters. It says 63% of all repositories are public or open source, while 81.5% of contributions happen in private repositories ([GitHub Octoverse 2025](https://github.blog/news-insights/octoverse/octoverse-a-new-developer-joins-github-every-second-as-ai-leads-typescript-to-1/)). Modern software teams often depend on open source while doing most operational work inside private, governed systems.
Form.io’s self-hosted model is built for that private operational side. Its [self-hosted forms for enterprise](https://form.io/features/self-hosted-forms-for-enterprise/) page describes Form.io as deployable infrastructure that can run in AWS, Azure, Google Cloud, private data centers, or local Docker-based environments. It also describes separate components such as Enterprise Server, PDF Server, Developer Portal, renderer libraries, deployment environments, file storage, database requirements, and dev/test/prod patterns.
The key point is not that Form.io is self-hosted and Formbricks is not. Both can be self-hosted.
The key point is what is governed inside that boundary.
Formbricks governs surveys, feedback, contacts, responses, and experience-management workflows. Form.io governs forms, resources, submissions, generated APIs, roles, permissions, actions, environments, and form lifecycle.
Those are different control surfaces.
## **Pricing basis and scale predictability**
Formbricks has a strong Community Edition story for survey teams: AGPLv3 core access, free self-hosting, unlimited surveys, unlimited users, and unlimited responses. Teams evaluating Enterprise Edition should verify response, feature, workspace, support, and private-fork requirements directly against the current license table.
Form.io’s pricing story is different.
The point is not that Form.io is cheaper in every scenario. The point is that the buying model is designed around configured form/API infrastructure. Form.io’s [configuration-based pricing](https://form.io/configuration-based-pricing/) page lists unlimited API calls, unlimited submissions, unlimited developers and form builders, and unlimited forms and resources in relevant enterprise configurations.
That difference matters when forms become a platform feature.
If every tenant, customer, department, agency, or product line can create forms, usage can grow in ways that are hard to forecast. A per-response survey model may be fine for customer feedback. A configuration-based infrastructure model may be a better fit when submissions, forms, builders, tenants, and APIs are part of the product architecture.
The buyer should ask what is scaling.
If survey responses are scaling, Formbricks may fit. If application forms, submitted records, generated endpoints, customer form builders, and environments are scaling, Form.io deserves closer evaluation.
## **Customer proof: when form infrastructure scale becomes real**
Form infrastructure arguments can sound abstract until the volume shows up.
Form.io’s public case-study pages describe a publicplan GmbH implementation supporting more than 400 services and 1,000+ forms, and a Safety Mojo implementation that Form.io says saved 6-12 months of development time. Those are Form.io-published examples, so they should be read as customer proof rather than independent analyst validation. The Safety Mojo page also includes the customer proof line, “Form.io cleans up all the dirty work and does it for you” ([publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/), [Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)).
Those examples point to the real Form.io use case.
The hard part at that scale is not drawing a field. It is keeping the form, schema, submission record, API behavior, permissions, environment boundary, and downstream workflow aligned as requirements change.
IBM’s 2025 Cost of a Data Breach report puts the global average breach cost at $4.4 million and says 63% of organizations lacked AI governance policies ([IBM Cost of a Data Breach 2025](https://www.ibm.com/reports/data-breach)). That is not a form-specific statistic, and it should not be treated as one. It is a reminder that data workflows and governance boundaries are not minor implementation details when forms collect sensitive or operationally important data.
For teams handling simple feedback, that level of infrastructure may be unnecessary. For teams building regulated intake, customer portals, financial workflows, healthcare workflows, insurance claims, government services, or multi-tenant form platforms, it is often the main issue.
## **When Formbricks is the better choice**
Formbricks is likely the better fit when your team needs:
- a self-hosted Typeform alternative
- product feedback surveys
- NPS, CSAT, CES, onboarding, churn, or market research surveys
- in-app micro-surveys and website surveys
- open-source survey tooling with a clear cloud/self-host path
- privacy-first feedback collection
- a survey API for responses, contacts, and webhooks
- broad survey features without building a survey platform from scratch
In those cases, Form.io may be too much infrastructure. If the primary object is a survey and the output is feedback analysis, Formbricks is a natural choice.
## **When Form.io is the better choice**
Form.io is likely the better fit when your team needs:
- embedded forms inside a customer-facing application
- white-labeled form building inside your own product
- JSON-defined forms that drive rendering, validation, submissions, and APIs
- generated form APIs instead of hand-built backend endpoints for every form
- form, project, and submission permissions
- dev/test/prod form environments and SDLC-aware form promotion
- multi-tenant form workflows
- audit-relevant controls such as permissions, deployment boundaries, submission history, and security/compliance features
- configuration-based pricing for high-volume form infrastructure
- forms that support workflows beyond feedback collection
- governed form and submission context for agentic workflows
In those cases, the form is no longer just a question flow. It is a governed application layer.
## **The decision rule**
Choose Formbricks if the main job is collecting feedback through open-source, self-hosted surveys.
Choose Form.io if the main job is making forms, submissions, APIs, permissions, workflow behavior, and agentic workflow context part of your product or enterprise application infrastructure.
That is the real comparison.
Formbricks helps teams own survey and feedback collection. Form.io helps teams own the form layer when it becomes part of the architecture.
## **FAQ**
### **Is Formbricks a form builder?**
Yes, but it is better understood as an open-source survey and experience management platform. It can build forms and surveys, but its strongest fit is feedback collection across websites, apps, emails, and shared links.
### **Is Form.io a Formbricks alternative?**
Form.io can be an alternative when the buyer’s requirement is governed forms, generated APIs, embedded form rendering, self-hosted deployment, and application infrastructure. It is not a direct replacement for every survey, feedback, or experience-management use case Formbricks supports.
### **Which is better for a self-hosted Typeform alternative?**
Formbricks is usually the stronger fit for a self-hosted Typeform alternative. It is built around surveys, feedback collection, open-source access, and privacy-first response workflows.
### **Which is better for embedded forms?**
Form.io is usually the stronger fit when forms need to be embedded into a customer-facing product or enterprise application as a governed runtime. Formbricks can embed surveys, while Form.io is built around embeddable form rendering and embedded form building.
### **Can Formbricks be self-hosted?**
Yes. Formbricks documents free self-hosting and self-hosting with an Enterprise Edition license. Buyers should verify which features are included in Community Edition and which require Enterprise Edition.
### **Can Form.io be self-hosted?**
Yes. Form.io supports self-hosted deployment with API server environments, portal/authoring environments, renderer libraries, PDF Server options, customer-controlled databases, file storage choices, and common dev/test/prod deployment structures.
### **Does Formbricks have an API?**
Yes. Formbricks documents a Public Client API for frontend survey interactions and a Management API for backend management tasks such as surveys, contacts, responses, action classes, and webhooks.
### **Does Form.io generate APIs from forms?**
Yes. Form.io’s distinction is that form schemas and paths can directly define schema and submission endpoints, making the form itself part of the application API contract.
### **Which is better for regulated form workflows?**
Form.io is usually the better fit when the regulated workflow depends on form schemas, submission permissions, generated APIs, deployment boundaries, submission history, and long-term governance of form changes. Formbricks may still fit regulated feedback collection when a survey-first model is enough.
### **Which is better for customer-facing SaaS platforms?**
Form.io is usually the stronger fit when SaaS customers need to create or use forms inside your product experience, especially with white-labeling, tenant boundaries, permissions, and governed form behavior. Formbricks is stronger when the SaaS product mainly needs in-app feedback and customer surveys.
### **How should teams evaluate Formbricks vs Form.io?**
Start by deciding whether you are choosing a survey platform or a form infrastructure layer. Then compare deployment, embedding, API behavior, permissions, licensing, pricing basis, audit needs, and who will maintain the form model over time.
## **Build form infrastructure without turning every form into a custom project**
When forms become part of the application architecture, the right platform needs to do more than collect responses. It needs to keep schemas, submissions, APIs, permissions, and workflows aligned as the system grows.
[Try Form.io for free](https://form.io/try-formio-for-free/) if your team needs self-hosted form infrastructure that developers can embed, govern, and scale inside the applications you already own.
# Budibase vs Form.io: Internal Tools or Form Infrastructure?
[  ](https://form.io/budibase-formio-vs-budibase/)Organizations comparing self-hosted, open-source builders for internal tools and enterprise forms often put Budibase and Form.io in the same shortlist. Both speak to technical teams that want more control than lightweight SaaS form tools provide, but they solve different layers of the problem.
Budibase focuses on internal operations apps, agents, automations, and workflows around business data. Form.io is designed as application infrastructure for forms, APIs, workflows, and enterprise governance, including agentic workflow patterns where governed forms and submissions need to stay connected to permissions, validation, actions, and audit evidence.
That distinction matters before the feature checklist begins. The question is not whether both products can collect data. It is whether the form is a screen inside an internal app or a governed contract inside the application architecture.
## **Key takeaways**
- Budibase is best understood as an open-source operations platform for internal tools, agents, apps, automations, and connected data.
- Form.io is best understood as form-driven application infrastructure: JSON-defined forms, generated APIs, submission data, permissions, workflow actions, self-hosted deployment, and governed patterns for agentic workflows.
- Budibase is a credible choice for internal apps, request workflows, admin panels, and operational tools.
- Form.io is the better fit when forms need to be embedded in a product, reused across tenants, governed through submission-level permissions, exposed through APIs, managed as part of an enterprise SDLC, or used as structured context for agentic workflows.
- The main question is not "Which product has forms?" It is "What layer do your forms need to own?"
## **Quick comparison**
## **Decision area****Budibase****Form.io**Primary jobInternal operations platform for agents, apps, automations, workflows, and connected dataForm and API infrastructure for embedded, governed, form-driven applications and agentic workflowsForm modelForms are components inside Budibase apps, usually tied to tables, views, custom schemas, or app workflowsForms are JSON schemas that define UI, validation, submission structure, and backend APIsAPI modelPublic API gives access to apps, users, tables, and data through a RESTful APIEach form/resource path can generate REST endpoints for schemas and submissionsEmbeddingPublished apps can be embedded with iframes; enterprise microfrontend options existRenderer and builder can be embedded directly into customer-controlled applicationsGovernanceTenant roles, workspace roles, app roles, SSO, groups, and audit logs depending on planProject, form, and submission permissions; roles, actions, audit patterns, stages, and self-hosted environmentsBest buyerTeams building internal tools and operations workflows quicklyTeams standardizing forms, APIs, submissions, permissions, workflow behavior, and agentic workflow context as product infrastructureWrong fit warningLess ideal when the form layer must be a portable, governed contract outside an internal app surfaceNot a general internal-tools replacement for every dashboard, CRUD app, or admin panel**What Budibase is good at**
Budibase deserves a fair reading. Its own documentation describes it as an open-source platform for internal tools and workflow automation, used by more than 200,000 teams to automate workflows, handle requests, build internal tools, and connect systems using their own data, LLMs, and APIs.
That is a real category.
If your team needs to build an internal approval app, a data-entry screen, an admin panel, a request workflow, an operations dashboard, or an agent-assisted internal process, Budibase is built for that motion. It gives teams a visual app builder, data connections, automations, apps, agents, roles, and deployment options in one operations-oriented surface.
Budibase forms are part of that app-building model. The official forms documentation says forms are built from a Form component, Field group components, and Input components, with optional schemas tied to tables, views, relationships, or custom structures.
That is useful when the form is a screen inside an internal app.
The question is what happens when the form is no longer just a screen.
## **What Form.io is good at**
Form.io is strongest when forms, submissions, validation, permissions, APIs, and workflow actions need to become governed infrastructure rather than app components. The form definition can become a JSON contract that drives rendering, submission shape, validation rules, backend endpoints, and downstream handoffs.
That makes Form.io a better fit for customer-facing forms, regulated intake, tenant-managed SaaS form builders, healthcare and financial workflows, government services, insurance claims, and enterprise processes where the form record needs to stay governed after submission.
It also matters for agentic workflows. When AI-assisted or runtime agents need to collect structured data, validate inputs, trigger actions, or require human confirmation inside enterprise guardrails, the form layer needs stable schemas, permissions, and audit patterns. Form.io is built for that form and workflow infrastructure layer.
So the Form.io category should appear early in the decision: it is not the general internal app builder in this comparison. It is the governed form infrastructure layer when forms, APIs, submissions, and workflow behavior need to be owned by the application architecture.
## **What changes when forms become infrastructure**
Many teams start with a simple internal form and end up with application infrastructure.
The intake form becomes a case creation workflow. The customer form becomes a white-labeled feature inside a SaaS product. The compliance form becomes a regulated submission record. The public-sector form becomes one of hundreds of services that must follow the same standards. The healthcare or financial-services form becomes part of a workflow where validation, access, auditability, and downstream APIs matter as much as the UI.
That is the point where the Budibase vs Form.io decision gets sharper.
Form.io's form builder is not only a visual form editor. The Form.io documentation says the builder creates a JSON schema representation of the form, and that schema is used to dynamically render the form and automatically generate the REST API that supports it ([Form.io form building docs](https://help.form.io/userguide/forms/form-building)).
That is the architectural difference.
In Budibase, forms help users interact with data inside apps. In Form.io, the form schema can become the contract that defines the rendered UI, validation rules, submitted data shape, API endpoints, permissions, and downstream workflow behavior.
For teams whose forms are application infrastructure, that difference is not small.
## **Forms inside apps vs forms as contracts**
Budibase is strongest when you want a visual way to assemble apps around data and process. Its forms can create and update data, use schemas, and participate in workflows. For internal teams, that can be exactly right.
Form.io is stronger when the form definition itself needs to travel across systems.
Every Form.io form is a structured JSON definition. Form.io's JSON-schema forms documentation explains that a form schema can define the form title, path, type, display mode, components, validation, conditional logic, and submission data shape. It also explains that a form path creates endpoints such as schema retrieval and submission create/list/read/update/delete operations ([Forms from JSON](https://form.io/features/form-from-json-schema/)).
That matters when multiple applications, teams, tenants, or agents need to rely on the same form contract.
If a form is only a UI on top of a table, the surrounding system still needs to decide how validation is enforced, how submissions are stored, how APIs behave, how permissions apply, and how downstream services consume the data. If the form is a governed schema with APIs and submissions attached, more of that behavior has one source of truth.
That is why Form.io often resonates with teams that have outgrown simple form building. They are not trying to draw fields faster. They are trying to keep the form, data model, API behavior, permissions, and workflow triggers aligned as requirements change.
## **API and data model comparison**
Budibase has an API, and that should be acknowledged clearly. Its public API documentation says the API provides access to applications, users, tables, and data through a RESTful API and an OpenAPI 3.0 specification.
That makes sense for an internal operations platform. You can integrate with the Budibase environment, work with tables and records, and connect Budibase to broader business systems.
Form.io's API model is more specific to form infrastructure. The form schema defines the path and the submission endpoints that support that form. Form.io's drag-and-drop builder and API documentation explains that saving a form registers endpoints for creating, listing, reading, updating, and deleting submissions, with validation enforced from the schema ([drag-and-drop form builder APIs](https://form.io/features/drag-and-drop-form-builder-apis/)).
That is a different center of gravity.
Budibase helps you build apps around data. Form.io helps you define the form and submission layer that creates, validates, stores, and exposes that data in the first place.
For an internal app, either model may work. For a customer-facing product, regulated intake workflow, or multi-tenant form platform, the form-defined API model can be the safer foundation.
## **Embedding and white-labeling**
Budibase supports embedding, but the default model is app embedding. Its embedded app documentation describes embedding a published Budibase app in an iframe, with access considerations for public screens, allowed domains, and authenticated embedded users. Budibase also documents an enterprise microfrontend option for non-iframe embedding in specific licensed scenarios.
That can be useful when the thing you want to embed is an app.
Form.io is built for a different embedding requirement: embedding form rendering and form building inside the application your team already owns. The open-source `formio.js` renderer and SDK can render JSON schema forms inside an application and communicate with Form.io APIs ([Form.io JavaScript renderer](https://github.com/formio/formio.js)). The [Enterprise Form Builder Module](https://form.io/enterprise-form-builder-module/) lets teams expose white-labeled, preconfigured form building inside their own product while controlling components, guardrails, structured data, APIs, permissions, and workflow behavior.
That distinction is important for SaaS platforms, government service portals, healthcare products, and other systems where customers or internal teams need self-service form creation without leaving the product experience.
If you want to embed a whole operational app, Budibase may fit. If you want to embed governed form creation and rendering as part of your own product architecture, Form.io is the more direct match.
## **Self-hosting, security, and governance**
Do not reduce this comparison to "self-hosted vs not self-hosted." Budibase is a legitimate self-hosted option. Its hosting docs describe Budibase Cloud and self-hosted installation paths, including Docker, Kubernetes, and DigitalOcean. Its security docs say the self-hosted version can be deployed inside your own network, on your own servers, with control over how data is secured and without data needing to leave your VPC.
That is real.
The stronger Form.io argument is not that Budibase lacks deployment control. It is that Form.io's control is organized around form infrastructure.
Form.io's self-hosted deployment documentation describes API server environments, portal/authoring environments, Docker-based deployment, and common dev/test/prod structures ([Form.io self-hosted deployment docs](https://help.form.io/deployments/deployment-guide.md)). Its roles and permissions documentation separates access across project, form, and submission scopes, with permissions governing form definitions and submission data ([Form.io roles and permissions docs](https://help.form.io/developers/roles-and-permissions.md)).
That is the level of detail serious form infrastructure often needs.
Open source is also not a substitute for governance by itself. GitHub's 2025 Octoverse report says 63% of all repositories are open source or public, while 81.5% of contributions happen in private repositories, showing how public software and private enterprise work now depend on each other ([GitHub Octoverse 2025](https://github.blog/news-insights/octoverse/octoverse-a-new-developer-joins-github-every-second-as-ai-leads-typescript-to-1/)). Black Duck's 2026 OSSRA analysis found that 87% of audited codebases contained at least one vulnerability and 78% contained high-risk vulnerabilities, which is why open-source adoption still needs supply-chain governance ([Black Duck 2026 OSSRA](https://www.blackduck.com/blog/open-source-trends-ossra-report.html)). Gartner also predicts that by 2027, 70% of organizations with platform teams will include GenAI capabilities in internal developer platforms, increasing the need for reusable guardrails around generated and internal applications ([Gartner software engineering trends](https://www.gartner.com/en/newsroom/press-releases/2025-07-01-gartner-identifies-the-top-strategic-trends-in-software-engineering-for-2025-and-beyond)).
The practical lesson is simple: open source and self-hosting are valuable, but enterprise teams still need clear controls over data, roles, changes, workflows, and audit evidence.
Budibase has governance features such as tenant roles, workspace app roles, SSO, user groups, and audit logs. Its audit log docs say audit logs track events across a Budibase installation, and also show an upgrade path for free-tier users who need audit logs. That is not a criticism. It is a reminder to verify packaging against the controls your team actually needs.
For Form.io buyers, the governance question is more specific: who can change a form definition, who can submit, who can read submissions, which action fires after submission, which environment owns the schema, and which historical submission was governed by which form state?
Those are form-infrastructure questions.
## **Pricing basis: free tier vs scale predictability**
Budibase has a strong pricing story for many teams. Its pricing page includes a free open-source self-hosted plan, and higher tiers add capabilities such as more logs, custom branding, backups, SSO, user groups, SCIM, audit logs, priority support, and air-gapped deployment options.
For internal tools, that can be compelling.
Form.io's pricing story is different. The point is not that it is cheaper in every scenario. The point is that it is priced around self-hosted form/API configuration rather than usage meters. Form.io's configuration-based pricing page lists unlimited API calls, unlimited submissions, unlimited developers and form builders, and unlimited forms and resources in relevant configurations, and it frames the buying model around projects, API/PDF environments, and enterprise add-ons ([Form.io configuration-based pricing](https://form.io/configuration-based-pricing/)).
That difference matters when forms are high-volume, public-facing, embedded, or tenant-driven.
If every customer, office, agency, or product team can create forms, usage can become difficult to predict. A pricing model that avoids per-form, per-submission, per-end-user, per-developer, and per-API-call charges can make more sense when forms are infrastructure rather than a handful of internal apps.
## **Customer proof: when this becomes real**
Form infrastructure arguments can sound abstract until the scale shows up.
A Form.io public-sector case study for publicplan GmbH describes support for over 400 services and 1,000+ forms under strict standards and a short timeline ([publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)). Another Form.io-hosted customer proof point describes a long-time platform user running multiple production applications with a Form.io backend and saying, "Form.io cleans up all the dirty work and does it for you" ([Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/)).
Those examples point to the same idea: when forms multiply across services, products, departments, or customers, the hard part is not dragging fields onto a page. The hard part is keeping the form layer governed, reusable, API-backed, and operationally stable.
That is the Form.io case.
## **When Budibase is the better choice**
Budibase is likely the better fit when your team needs:
- internal tools for operations, support, HR, IT, finance, or admin workflows
- agent-assisted internal request handling
- dashboards, admin panels, and CRUD apps over business data
- a visual app builder for teams that want to ship internal workflows quickly
- open-source self-hosting for internal app delivery
- automations and app screens in one operations platform
In those cases, Form.io may be too specialized. If the form is just one component inside a broader internal app, Budibase can be the simpler answer.
## **When Form.io is the better choice**
Form.io is likely the better fit when your team needs:
- embedded forms inside a customer-facing application
- white-labeled form building inside your own product
- JSON-defined forms that can drive rendering, validation, submissions, and APIs
- generated form APIs instead of hand-built backend endpoints for every form
- submission-level permissions and form-specific access control
- dev/test/prod form environments and SDLC-aware form promotion
- multi-tenant form workflows
- compliance-oriented audit patterns
- no per-submission, per-form, per-end-user, or per-API-call pricing surprise
- governed form and submission context for agentic workflows
In those cases, the form is no longer a UI component. It is a governed application layer.
## **The decision rule**
Choose Budibase if the main job is building internal operational apps around data, approvals, automations, and agents.
Choose Form.io if the main job is making forms, submissions, APIs, permissions, workflow behavior, and agentic workflow context part of your product or enterprise application infrastructure.
That is the real comparison.
Budibase helps teams build operational applications faster. Form.io helps teams keep form-driven systems governed when the forms themselves become the architecture.
## **FAQ**
### **Is Budibase a form builder?**
Budibase includes form-building capabilities, but it is better understood as an internal operations platform for apps, agents, automations, workflows, and connected data. Forms are one important part of that app-building model.
### **Is Form.io a Budibase alternative?**
Form.io can be an alternative when the specific requirement is governed forms, submissions, generated APIs, embedded form rendering, and self-hosted form infrastructure. It is not a general replacement for every internal app or dashboard use case Budibase supports.
### **Which is better for internal tools?**
Budibase is usually the stronger fit for broad internal tools, admin panels, request workflows, dashboards, and operations apps. Form.io is more specialized around the form and API layer.
### **Which is better for embedded forms?**
Form.io is usually the stronger fit when forms need to be embedded into a customer-facing product or internal application as a governed runtime. Budibase can embed apps, but Form.io is built around embeddable form rendering and embedded form building.
### **Can Budibase be self-hosted?**
Yes. Budibase supports self-hosting and documents deployment paths such as Docker, Kubernetes, and DigitalOcean. Buyers should still verify which governance, audit, SSO, SCIM, support, and air-gapped features are included in the plan they intend to use.
### **Can Form.io be self-hosted?**
Yes. Form.io supports self-hosted deployment with API server environments, portal/authoring environments, Docker-based deployment, customer-controlled databases, and common dev/test/prod structures.
### **Does Budibase generate APIs from forms?**
Budibase has a public API for apps, users, tables, and data. Form.io's distinction is that form schemas and paths can directly define form and submission endpoints, making the form itself part of the API contract.
### **Which is better for regulated form workflows?**
Form.io is usually the better fit when the regulated workflow depends on form schemas, submission permissions, generated APIs, deployment boundaries, audit patterns, and long-term governance of form changes. Budibase may still fit internal regulated workflows when the app-builder model is enough.
### **Which is better for customer-facing SaaS platforms?**
Form.io is usually the stronger fit when SaaS customers need to create or use forms inside your product experience, especially with white-labeling, tenant boundaries, and governed form behavior. Budibase is stronger when the goal is to build internal apps for your own team.
### **How should teams evaluate Budibase vs Form.io?**
Start by deciding whether you are choosing an internal app builder or a form infrastructure layer. Then compare deployment, embedding, API behavior, permissions, pricing basis, audit needs, and who will maintain the form model over time.
## **Build form infrastructure without turning every form into a custom project**
When forms become part of the application architecture, the right platform needs to do more than render fields. It needs to keep schemas, submissions, APIs, permissions, and workflows aligned as the system grows.
[Try Form.io for free](https://form.io/try-formio-for-free/) if your team needs self-hosted form infrastructure that developers can embed, govern, and scale inside the applications you already own.
# HIPAA-Compliant Form Builder: What Healthcare SaaS Teams Should Evaluate
## [  ](https://form.io/hipaa-compliant-form-builder-healthcare-saas-platforms/)**Key Takeaways**
- A HIPAA-compliant form builder is not compliant because it has a healthcare template or a lock icon.
- If a vendor creates, receives, maintains, or transmits ePHI for a covered entity or business associate, the BAA and operational responsibility boundary matter.
- Hosted HIPAA form builders can be a good fit for simple intake, consent, appointment, or website forms.
- Healthcare SaaS teams usually need more than a hosted form link: APIs, embedded rendering, role-aware access, audit logs, revision history, and deployment control.
- Form.io is strongest when HIPAA-governed forms are part of application infrastructure rather than a standalone intake tool.
## **What "HIPAA-Compliant Form Builder" Actually Means**
The phrase "HIPAA-compliant form builder" is useful shorthand, but it can hide the real decision.
HIPAA compliance is not a feature that one vendor turns on for the whole organization. It is a legal, contractual, administrative, technical, and operational responsibility. The form builder can support that responsibility. It cannot replace it.
The U.S. Department of Health and Human Services explains that when a covered entity or business associate uses a cloud service to create, receive, maintain, or transmit ePHI, the cloud service provider is generally a business associate and the parties need a HIPAA-compliant business associate agreement. [HHS also notes](https://www.hhs.gov/hipaa/for-professionals/special-topics/health-information-technology/cloud-computing/index.html) that this can still be true even when the provider stores only encrypted ePHI and does not hold the decryption key.
That point matters for online forms.
If a form collects PHI, the risk does not stop at the submit button. The data may be stored, emailed, exported, routed through webhooks, copied into a CRM, written to a database, attached to a PDF, shown in an admin portal, or sent to downstream systems. A HIPAA-ready form tool has to be evaluated across that whole path.
The [HHS Security Rule](https://www.hhs.gov/hipaa/for-professionals/security/index.html) frames the obligation around administrative, physical, and technical safeguards for the confidentiality, integrity, and availability of ePHI. In plain terms: the form is only one surface. The system around the form has to be governed too.
The risk is not theoretical. IBM's 2025 Cost of a Data Breach report puts the global average breach cost at [$4.4 million](https://www.ibm.com/reports/data-breach?app=true). That is not a healthcare-form-specific number, but it gives the right scale for the decision: a form that collects sensitive health data is not a minor website feature when the surrounding workflow is weak.
## **The Quick Decision: Practice Intake Tool Or Healthcare SaaS Infrastructure?**
Most buyers searching for a HIPAA-compliant form builder fall into one of two groups.
The first group needs a faster way to collect patient information. A clinic, therapy practice, dental office, or small healthcare provider may need intake forms, consent forms, appointment requests, file uploads, and e-signatures. A hosted HIPAA-enabled form builder can work well here if the vendor signs the right BAA, the account is configured correctly, and the workflow keeps PHI inside approved systems.
The second group is building a healthcare product. That buyer does not only need a form. It needs form capability inside an application.
For healthcare SaaS teams, forms may power onboarding, eligibility, clinical screening, referrals, patient-reported outcomes, provider workflows, prior authorization, records updates, care-team routing, and follow-up check-ins. A [third-party digital health article from Light-it](https://lightit.io/blog/5-ways-to-apply-hipaa-compliant-form-builders-to-your-digital-health-product/) describes HIPAA-compliant forms as part of ongoing product workflows such as patient intake, assessments, appointment scheduling, regular check-ins, and feedback surveys. That is a different problem than publishing a secure contact form on a website.
The distinction is simple:
**Buyer situation****Better fit**One practice needs intake forms and patient packetsHosted HIPAA-enabled form builderA healthcare SaaS product needs forms inside its appEmbedded form infrastructureA team needs patient data routed to internal systemsAPI-first form platformA team must keep PHI inside its own environmentSelf-hosted form infrastructureA product needs tenant-specific forms and permissionsWhite-label or multi-tenant form infrastructureThe mistake is treating these as the same purchase.
## **The Requirements Checklist**
Before comparing logos, healthcare teams should define the control boundary.
### **BAA Scope**
A BAA is not a marketing badge. It establishes the permitted uses and disclosures of PHI, requires appropriate safeguards, covers reporting obligations, addresses subcontractors, and should align with the actual workflow. [HHS sample BAA guidance](https://www.hhs.gov/hipaa/for-professionals/covered-entities/sample-business-associate-agreement-provisions/index.html) says these contracts should clarify and limit how a business associate may use or disclose PHI and require safeguards to prevent unauthorized use or disclosure.
The practical question is: which vendor is creating, receiving, maintaining, or transmitting ePHI?
If the form builder stores submissions, handles uploaded files, sends notifications containing PHI, or passes data to another system, the BAA and subcontractor chain need to match that reality.
### **Where PHI Is Stored**
Data location is not a minor implementation detail. It determines who administers the database, where backups live, which security controls apply, who can access logs, what happens at termination, and how incident response works.
For a simple hosted form workflow, vendor-managed storage may be acceptable. For a healthcare SaaS product, the team may need submissions in its own database, cloud account, region, network, or compliant infrastructure boundary.
This is one reason self-hosting matters. It does not make an application HIPAA compliant by itself. It gives the customer more control over where PHI lives and which controls surround it.
### **Access Control And Identity**
HIPAA-governed forms usually need more than a shared admin login.
Ask who can view submissions, edit forms, export data, upload files, change permissions, configure webhooks, or see audit logs. Then map those permissions to real roles: patient, provider, customer admin, internal support, implementation partner, compliance reviewer, and developer.
For SaaS products, this gets harder. One customer's admin should not see another customer's submissions. A support user may need temporary access. A provider may need access to only assigned patients. A form builder may need schema-editing rights without PHI access.
The form system has to support those boundaries instead of forcing the application to patch them later.
### **Audit Logs And Revision History**
The highest-risk part of a healthcare form often starts after submission.
What changed? Who changed it? Which version of the form captured the original data? Did a webhook run? Did an email action send? Did the submitted value get edited later? Can the team reconstruct the record if an auditor asks?
Generic form builders often focus on collection. Healthcare SaaS teams need evidence.
Form.io's Security Module is built around this kind of evidence. Its [secure forms and compliance readiness documentation](https://form.io/features/secure-forms-compliance-readiness/) describes advanced audit logging, action logs, form revisions, submission revision logs, submission collections, and container security scanning. The important distinction is that form revisions track changes to the form schema, while submission revisions track changes to submitted data.
That distinction sounds small. It is not.
A historical submission is not only the answers a patient gave. It is the form version, validation rules, field labels, conditional logic, workflow context, and submission state that governed the data at the time.
### **APIs And Integration Control**
Healthcare forms rarely stay inside the form tool.
An intake form may need to create a patient profile, update a resource, trigger a referral workflow, generate a PDF, route a task to a care team, or feed an internal dashboard. A screening form may need validation, conditional follow-up, file uploads, and downstream review. A provider form may need to connect with legacy systems or internal case management.
If the form builder only gives you CSV exports or a fragile integration layer, the application team inherits the risk.
Form.io's [concepts documentation](https://help.form.io/start/form.io-concepts) explains that as a form is built, Form.io constructs the JSON schema and defines a REST API endpoint. Submissions are API-accessible, owned by users for permission enforcement, portable, and revision-trackable with the Security & Compliance package. That is the infrastructure argument: the form definition, submitted data, API, and access model belong in the same system.
### **Tenant And Customer Boundaries**
Healthcare SaaS teams often serve many customers from one product. That means the form layer may need tenant-aware configuration, customer-specific forms, white-labeled experiences, separate roles, different workflows, and different data retention expectations.
This is where "HIPAA form builder" searches become too small. The issue is not only whether one form can collect PHI. It is whether a platform can support repeated, governed form workflows across customers without collapsing into one-off custom code.
## **Common HIPAA Form Builder Categories**
The market is easier to understand when you separate platform types.
**Category****Best fit****Strength****Gap**Hosted HIPAA form builderPractices and clinics that need intake, consent, and website formsFast setup, templates, vendor-managed hostingLimited architecture and data-boundary controlHealthcare intake platformPatient intake, appointment, and engagement workflowsHealthcare-specific UX and workflowsMay be too narrow for broader SaaS infrastructureEnterprise form/workflow platformLarger teams with governed workflowsMore controls and integrationsOften still vendor-hosted or workflow-product centeredSelf-hosted form infrastructureHealthcare SaaS and regulated product teamsDeployment control, APIs, data ownership, auditabilityRequires technical ownershipCustom buildUnique workflows with no acceptable platform fitMaximum controlExpensive to build, secure, test, document, and maintainThere is no universal winner. There is only the right layer for the job.
## **Where Form.io Fits For Healthcare SaaS**
Form.io is not the lightest way to publish a HIPAA-ready website form. It is a stronger fit when forms are part of healthcare application infrastructure.
That usually means the team needs some combination of embedded forms, generated APIs, custom roles, submission storage, workflow actions, form revisions, submission revisions, audit logs, file/PDF handling, and customer-controlled deployment.
Form.io's [self-hosted forms documentation](https://form.io/features/self-hosted-forms-for-enterprise/) says the platform can run in AWS, Azure, Google Cloud, private data centers, or Docker-based environments, with submission data stored in the customer's MongoDB instance and security boundary. The same page is careful about the boundary: self-hosted deployment enables compliance control, but the customer still needs proper access controls, encryption, audit logging, network security, and the rest of the compliance program.
That honesty is useful.
Healthcare SaaS teams do not need another vendor promising that complexity disappears. They need a platform that gives them the right control surfaces: forms, resources, generated APIs, submissions, actions, [roles and permissions](https://form.io/features/forms-for-teams/), revisions, and audit evidence.
Form.io's [healthcare forms page](https://form.io/industries/healthcare-forms/) points to use cases such as patient registration, records, appointments, routing inquiries, notifications, [conditional logic](https://form.io/features/form-conditional-logic-form-validation/), mobile-responsive forms, offline mode, form revisions, autosave, accessibility, and the Security Module. The better strategic reading is not "Form.io makes healthcare simple." It is that Form.io gives healthcare teams a form infrastructure layer they can govern inside their own architecture.
The [CHESS Health case study](https://form.io/how-a-flexible-form-solution-helped-get-to-market-in-6-weeks-instead-of-6-months/) is a useful proof point. Form.io describes a healthcare technology company managing EMRs, EHRs, interoperability, strict security and compliance requirements, sensitive data in its own environment, legacy integrations, and the need to get to market faster. The case headline says CHESS Health got to market in 6 weeks instead of 6 months. That is the category fit: not a simple intake form, but a healthcare product workflow that needed speed without giving up architectural control.
There is also a buyer sentiment signal from [Trustpilot](https://www.trustpilot.com/review/form.io), where one reviewer called Form.io "really great software, both for integration and standalone." The quote is broad, but it matches the central buying reason for this article: the form layer has to work as part of a larger system.
## **When A Hosted HIPAA Form Builder Is Enough**
A hosted HIPAA form builder may be the better answer when the workflow is simple and the organization accepts the vendor-managed model.
That can include:
- Patient intake forms for one practice
- Consent forms
- Appointment request forms
- Simple file uploads
- Basic medical history forms
- Feedback surveys
- Website-embedded forms
- Staff-created forms with limited integration needs
In these cases, speed matters. Templates matter. A no-code builder matters. A signed BAA, encrypted submissions, access controls, and a clean admin experience may be enough.
The important word is "enough."
If a workflow starts simple but will later need custom identity, tenant-specific configuration, deeper APIs, application-owned submission records, role-aware workflows, and evidence-grade revision history, the cheapest or fastest hosted option can become expensive later.
## **When Healthcare SaaS Teams Should Avoid Standalone Form Tools**
Standalone form tools become risky when the form is part of the product's core workflow.
Watch for these signals:
- PHI must remain inside your own cloud, database, or approved deployment boundary.
- Forms need to be embedded directly into your product experience.
- Customers need their own form configuration, roles, branding, or workflows.
- Submissions need to become application records, not just entries in a vendor dashboard.
- The product needs generated APIs, webhooks, resources, permissions, and workflow actions.
- Historical records need to resolve to the form version that captured them.
- Support, operations, providers, and customer admins need different access rules.
- Exports, notifications, analytics, and AI tools must not create uncontrolled PHI copies.
These are not edge cases for healthcare SaaS. They are ordinary product requirements.
The wrong tool can still pass the first demo. The problem appears later, when the team needs to prove who accessed PHI, why a submission changed, whether a field existed at the time of capture, where a file was stored, or why one tenant's workflow affected another.
That is the moment when "just use a form builder" stops being a plan.
## **Evaluation Table**
##  **Evaluation question****Why it matters****What to look for**Will the vendor sign the right BAA?PHI handling needs a contractual boundaryBAA scope, subcontractors, permitted uses, breach/security incident termsWhere is PHI stored?Data location shapes risk and responsibilityCustomer-controlled database, approved region, backup and termination termsCan access map to real roles?Healthcare workflows are role-sensitiveRBAC, SSO/MFA options, admin separation, own-vs-all submission accessAre form changes versioned?Historical records need contextForm revisions, schema history, promotion/stage controlsAre submission changes versioned?Modified PHI needs accountabilitySubmission revisions, who/when/what logs, revert or history viewsAre actions auditable?Integrations are common failure pointsAction logs for emails, webhooks, resource saves, and workflow stepsDoes the platform generate APIs?SaaS products need system integrationREST APIs, submission endpoints, resources, webhooksCan forms be embedded and white-labeled?Healthcare SaaS forms live inside productsRenderer libraries, embedded builder, brand controlCan the platform be self-hosted?Some teams need customer-controlled infrastructureDocker, cloud/on-prem deployment, environment variables, customer databaseDoes the vendor overclaim compliance?Overclaiming creates riskClear shared-responsibility language and technical-control boundaries**What Not To Assume**
Do not assume a healthcare template makes a workflow compliant.
Do not assume encryption solves the whole problem. HHS cloud guidance is clear that encryption alone does not remove business associate obligations when a provider maintains ePHI.
Do not assume a BAA covers every downstream action. If submissions are emailed to the wrong inbox, copied into a non-approved CRM, exported to spreadsheets, or passed through an unreviewed automation, the form builder's feature list is not the whole risk picture.
Do not assume self-hosting removes responsibility. It increases control. It also increases the customer's obligation to configure and operate the environment correctly.
Do not assume a standalone form tool will scale into product infrastructure. Sometimes it will. Often it will not.
## **FAQ**
### **Is A Form Builder HIPAA Compliant If It Signs A BAA?**
No. A BAA is necessary in many PHI workflows, but it is not the whole compliance answer. The organization still needs appropriate safeguards, policies, configuration, access control, risk analysis, monitoring, and incident-response processes.
### **Can Healthcare Teams Use Google Forms For PHI?**
Do not use a general form workflow for PHI unless the entire vendor relationship, configuration, storage model, access controls, and BAA requirements are approved for that use. For most healthcare SaaS teams, the safer default is to use a platform designed for regulated data workflows.
### **What Features Should HIPAA-Compliant Forms Have?**
At minimum, evaluate BAA support, encryption, access control, audit logs, secure storage, user management, file handling, retention/deletion, and integration behavior. For healthcare SaaS, also evaluate APIs, embedding, tenant boundaries, revision history, and deployment control.
### **Do Healthcare SaaS Teams Need Self-Hosted Forms?**
Not always. But self-hosting becomes important when PHI must stay inside the customer's environment, when the form layer needs to align with internal security controls, or when product architecture requires direct control over database, network, logging, and deployment boundaries.
### **Does Self-Hosting Make A Form Platform HIPAA Compliant?**
No. Self-hosting enables more control over infrastructure and data boundaries. Compliance still depends on how the environment is configured, monitored, documented, and governed.
### **Can Form.io Be Used For HIPAA Workflows?**
Form.io provides healthcare-oriented form infrastructure and security/compliance capabilities that can support HIPAA-governed workflows in customer-controlled environments. The customer's organization remains responsible for its HIPAA compliance program, configuration, policies, and deployment controls.
### **Does Form.io Certify My Application As HIPAA Compliant?**
No. Form.io's own compliance-readiness language is clear that the platform provides technical capabilities that support regulated deployments; it does not certify a customer's application or organization for HIPAA.
### **Why Do Audit Logs Matter For HIPAA Forms?**
Audit logs help answer who accessed or changed data, when it happened, what entity was affected, and which workflow action ran. For healthcare SaaS teams, that evidence can matter as much as the original form submission.
### **Should PHI Be Stored In A Third-Party Form Vendor Account?**
It depends on the workflow, BAA, risk analysis, and organizational policy. For simple intake forms, vendor-managed storage may be acceptable. For healthcare SaaS platforms, application-owned or customer-controlled storage may be a better fit.
### **What Should I Ask Before Collecting PHI Through An Online Form?**
Ask where PHI is stored, who can access it, which BAA covers it, whether uploads and notifications are protected, how audit logs work, how long data is retained, how submissions are deleted or exported, and what happens when the form changes.
## **Build HIPAA-Governed Form Infrastructure With Form.io**
If your healthcare product only needs a simple intake form, choose the fastest HIPAA-enabled tool that satisfies your compliance review.
If your forms define product workflows, API contracts, submissions, permissions, audit evidence, and data boundaries, choose infrastructure that respects that complexity from the start.
[Try Form.io for healthcare SaaS form infrastructure](/try-formio-for-free/).
# When Your Forms Don’t Match Your Design System Part 2
[  ](https://form.io/when-your-forms-dont-match-your-design-system-part-2/)In [Part 1](/when-your-forms-dont-match-your-design-system-part-1/), we established the design system compliance problem. Now let’s solve it for 98% of cases using class overrides alone.
Class names let you replace the CSS classes on your form components without touching the HTML structure. This is faster, less fragile, and easier to maintain than template-level customization. Start with this method in every case, and only reach for template overrides if you can’t accomplish your design goals with classes alone.
### **What Is the Class Names Method?**
Form.io templates are built from components, and each component has named parts: `input`, `label`, `button`, and so on. Class names let you define exactly which CSS classes apply to each part. The HTML structure stays the same; only the classes change. Because you’re working at the class level, this approach works with any CSS framework, whether you’re using Tailwind, Bootstrap, or something entirely your own, so you’re never locked into a particular toolchain.
### **Before You Start**
This guide assumes you already have a working Form.io application using the `@formio/js` renderer. To add the Standard Template, install it from npm:
```
npm install @formio/standard-template
```
**Note:** The Standard Template is a new and actively evolving package. Check the[ GitHub repository](https://github.com/formio/standard-template) for the latest version and API details before adopting it in production.
### **The Structure**
Here’s what a theme definition looks like:
```
import { standardTemplate } from '@formio/standard-template';
import type { TemplateClasses } from '@formio/standard-template';
const myTheme: TemplateClasses = {
// Component definitions go here
};
Formio.use(standardTemplate('my-custom-theme', myTheme));
```
Each component you want to customize gets an entry, and each entry defines classes for different contexts (`form` mode versus `html` display mode) and for the different parts of that component. Once you’ve seen one component defined, the rest follow the same shape.
### **Building a Complete Theme**
Let’s build a complete theme from scratch using Tailwind classes, transforming a basic contact form to match a modern design system. We’ll add one piece at a time.
#### **Our goal:**
- Minimal, underline-style input fields with an accent focus state
- Small, uppercase labels in the accent color
- A gradient pill button with hover effects
- Comfortable spacing between fields
#### **Step 1: Input Fields**
```
const myTheme: TemplateClasses = {
input: {
form: {
input: [
'block',
'w-full',
'px-0',
'py-2.5',
'text-base',
'text-slate-800',
'bg-transparent',
'border-0',
'border-b-2',
'border-slate-300',
'focus:outline-none',
'focus:border-violet-600',
'placeholder:text-slate-400',
'transition-colors',
'duration-200'
]
}
}
};
```
Pause on the shape of that definition, because every other component follows it:
- `input` (the outer key) is the component type: text fields, email fields, and so on
- `form` is the context (edit mode; there’s also html for read-only display)
- `input` (the inner key) is the specific element within that component
- The array contains all the Tailwind classes applied to that element
The result is an underline-style input: no box, no background, just a bottom border that shifts to violet when the field has focus.
#### **Step 2: Add Labels**
```
const myTheme: TemplateClasses = {
label: {
form: {
label: [
'block',
'text-xs',
'font-bold',
'uppercase',
'tracking-wider',
'text-violet-600',
'mb-2'
]
}
},
input: {
// ...input classes from Step 1
}
};
```
Labels now have their own styling: small, bold, uppercase, with letter-spacing and the accent color picking up the same violet as the input focus state. This sits alongside the input definition rather than inside it, because labels and inputs are independent components.
#### **Step 3: Add Buttons**
```
const myTheme: TemplateClasses = {
button: {
form: {
button: [
'w-full',
'px-6',
'py-3',
'text-sm',
'font-bold',
'uppercase',
'tracking-wider',
'text-white',
'bg-gradient-to-br',
'from-violet-600',
'to-violet-700',
'rounded-full',
'shadow-lg',
'shadow-violet-600/30',
'cursor-pointer',
'transition',
'duration-150',
'hover:opacity-90',
'hover:-translate-y-px',
'disabled:opacity-50',
'disabled:cursor-not-allowed'
]
}
},
label: {
// ...label classes from Step 2
},
input: {
// ...input classes from Step 1
}
};
```
The button becomes a full-width gradient pill: violet gradient background, a soft glow shadow, a subtle lift on hover, and proper disabled states. Notice the pattern: each component is self-contained, and adding a new one never disturbs the others.
#### **Step 4: Add Field Spacing**
```
const myTheme: TemplateClasses = {
component: {
form: {
component: [
'mb-6'
]
}
},
button: {
// ...button classes from Step 3
},
label: {
// ...label classes from Step 2
},
input: {
// ...input classes from Step 1
}
};
```
The `component` entry wraps every field in the form, so a single `mb-6` here gives each field comfortable breathing room below it. That’s the last piece of the theme.
### **The Complete Theme**
Here’s the full theme definition:
```
import { standardTemplate } from '@formio/standard-template';
import type { TemplateClasses } from '@formio/standard-template';
const myTheme: TemplateClasses = {
label: {
form: {
label: [
'block',
'text-xs',
'font-bold',
'uppercase',
'tracking-wider',
'text-violet-600',
'mb-2'
]
}
},
input: {
form: {
input: [
'block',
'w-full',
'px-0',
'py-2.5',
'text-base',
'text-slate-800',
'bg-transparent',
'border-0',
'border-b-2',
'border-slate-300',
'focus:outline-none',
'focus:border-violet-600',
'placeholder:text-slate-400',
'transition-colors',
'duration-200'
]
}
},
button: {
form: {
button: [
'w-full',
'px-6',
'py-3',
'text-sm',
'font-bold',
'uppercase',
'tracking-wider',
'text-white',
'bg-gradient-to-br',
'from-violet-600',
'to-violet-700',
'rounded-full',
'shadow-lg',
'shadow-violet-600/30',
'cursor-pointer',
'transition',
'duration-150',
'hover:opacity-90',
'hover:-translate-y-px',
'disabled:opacity-50',
'disabled:cursor-not-allowed'
]
}
},
component: {
form: {
component: [
'mb-6'
]
}
}
};
// Apply it globally
Formio.use(standardTemplate('my-custom-theme', myTheme));
```
Apply this once when your application initializes, and every form in your application will use the styling.
### **Before:**
### **After:**
### **Next Steps**
You now have everything you need to style Form.io forms to match your design system using class overrides. From here, the work is mostly a matter of breadth. The same pattern extends to every other component:
- **Radio buttons and checkboxes:** `radio`, `checkbox`
- **Select dropdowns:** `select`
- **Text areas:** `textarea`
- **Error and help text:** `errorLabel`, `helpBlock`
- **Field containers:** `component`, `field`
In every case you define classes for the component type and its parts, exactly as we did above. A textarea, for example, would take the same underline treatment as the inputs, plus `resize-y` and a `min-h-20` so users can expand it comfortably.
As your themes grow, it helps to pull them into their own modules so you can reuse them across projects:
```
// themes/tailwind-modern.ts
export const tailwindModern: TemplateClasses = {
// Your theme definition
};
// app.ts
import { tailwindModern } from './themes/tailwind-modern';
Formio.use(standardTemplate('tailwind-modern', tailwindModern));
```
Do this consistently and you end up with a library of themes you can share across your organization and maintain as part of your design system.
### **Additional Resources**
- [**Standard Template Playground**](https://apps.form.io/standard-template/): Interactive examples of different themes and styling approaches
- [**GitHub Repository**](https://github.com/formio/standard-template): Inspect the code and learn more about what you can target with CSS
# When Your Forms Don’t Match Your Design System Part 1
[  ](https://form.io/when-your-forms-dont-match-your-design-system-part-1/)Your design team just shipped an updated component library. New focus rings, refined spacing, updated color tokens. Engineering updates the React components, the dashboard layouts, and the navigation. Everything looks cohesive.
Then someone opens a form.
Form.io has been powering your dynamic forms beautifully. It handles complex conditional logic, multi-step workflows, and validation rules that would take many engineering hours to build from scratch. The form builder itself is invaluable: non-technical team members can create and modify forms without engineering involvement.
But visually, those forms still use the Bootstrap classes and markup they shipped with. Now there’s a mismatch. The rest of your application has evolved, and the forms haven’t.
This isn’t a Form.io problem. It’s a sign of success. Your product has matured to the point where your design system requirements go beyond any form builder’s defaults.
## **Why This Happens**
Form.io ships with professional, well-designed templates based on Bootstrap, and that’s exactly what you want when you’re getting started. These defaults handle everything: inputs, buttons, radio groups, validation messages, error states. They’re accessible, well-tested, and work across browsers. For many teams, they’re perfect and require no customization at all.
But as your product matures, specific visual requirements tend to surface. Maybe your design system has standardized on Tailwind rather than Bootstrap. Maybe you’ve built up custom brand colors, spacing scales, and typography, or your design team has defined particular interaction patterns. And at some point, “close enough” stops being good enough. You need the forms to match the rest of your application pixel-for-pixel. That’s the moment you need to customize Form.io’s visual layer while keeping everything else that makes it valuable.
## **What Teams Try Today**
Before Standard Template When teams hit this point in their product evolution, they usually reach for one of four approaches. Each comes with real trade-offs.
1. **Convince design to accept the form builder’s defaults.** Sometimes that works for internal tools, but for a customer-facing product with established brand guidelines, it’s usually a non-starter.
2. **Write custom CSS that overrides the defaults.** This works until it doesn’t: you can change colors and spacing, but you can’t restructure HTML with CSS, future updates might break your overrides, and maintenance gets expensive.
3. **Rebuild the component templates from the ground up.** You could use the default Form.io Bootstrap 5 template as a guide for writing your own. That gives you complete control, but now you’re maintaining even more code. It’s technically possible, but operationally expensive.
4. **Build a custom form system from scratch.** The most drastic option. Do this and you throw away Form.io’s conditional logic, validation rules, and visual builder, everything that made it valuable in the first place. It’s rarely justified. You chose Form.io for a reason.
What most teams actually want is something none of those quite delivers: keep Form.io’s powerful form logic and builder interface, but adapt the visual layer to match their design system.
## **The Standard Template**
After Standard Template The Standard Template introduces a customization system that works *with* Form.io’s existing architecture instead of against it. Its core mechanism is **Style Map**: you replace the CSS classes on existing HTML elements without changing the underlying structure. It works with any CSS framework, whether that’s Tailwind, Bootstrap, or a fully custom design system, and it’s fast to implement and easy to maintain. With the Standard Template, you’re configuring Form.io’s rendering layer, not fighting it.
This approach makes sense when you have an established design system with specific requirements, several forms that need to stay visually consistent, and a product where design system compliance matters, and you want all of that without giving up Form.io’s form logic and builder.
Just as important is knowing when you *don’t* need it. If Form.io’s default Bootstrap theme already works for you, if you only have a form or two, if your forms are internal tools where strict visual consistency isn’t a concern, or if you’re just getting started and should be optimizing for speed over pixel-perfection, then reaching for customization only creates work. Form.io’s defaults are professionally designed and serve most use cases well. Don’t make work for yourself unless you have a clear requirement.
## **Wrapping Up**
Adopting the Standard Template gives you the best of both worlds: Form.io’s powerful form capabilities with your design system’s visual consistency. Once it’s in place, your forms match your design system’s colors, spacing, and typography, while non-technical users keep building and modifying forms in the Form.io builder exactly as before. All of Form.io’s logic, validation, conditionals, and calculations keep working, your maintenance burden shrinks to a set of class definitions and the occasional template override, and new Form.io features and updates apply without conflicts.
The Standard Template is now available with the [release of Form.io 9.8.0](/release-notes/formio-enterprise-9-8-0-and-pdf-server-5-14-0/).
In [Part 2](/when-your-forms-dont-match-your-design-system-part-2/), I’ll show you how class overrides work with concrete examples. You’ll build a complete Tailwind theme from scratch without touching a single line of HTML.
# MCP Server List: What Regulated Enterprise Developers Should Actually Use
[  ](https://form.io/mcp-server-list-regulated-enterprise-developers/)You can find an MCP server list in seconds. That is not the hard part. The hard part is deciding which servers deserve access to your source code, cloud accounts, tickets, documentation, test environments, and production-adjacent business data.
For regulated enterprise developers, the question is not "which MCP servers are popular?" It is "which MCP servers can we trust inside a governed workflow?"
## **The quick answer**
Start with the official MCP Registry, then filter by control surface.
For regulated enterprise development, the strongest shortlist usually includes:
**MCP surface****Best fit****Enterprise question**Official MCP RegistryDiscovery and metadataIs this server officially published, namespace-authenticated, and still current?GitHub MCP ServerRepos, pull requests, issues, Actions, security findingsCan the agent work inside the same SDLC boundary developers already use?GitLab MCP ServerGitLab.com, self-managed GitLab, Duo workflowsDoes it respect the deployment model and permissions your GitLab instance already enforces?AWS MCP ServersCloud architecture, docs, API operationsAre IAM, least privilege, CloudWatch metrics, and CloudTrail evidence understood before use?Azure MCP ServerAzure resources, Entra ID-backed cloud workflowsDoes the server inherit the identity and guardrail model your Azure teams already use?Atlassian Rovo MCP ServerJira, Confluence, CompassDoes the agent see only what the user has permission to see?Playwright MCPBrowser automation and UI testingAre unsafe direct-code tools disabled unless the client is trusted?Sentry MCPDebugging and observabilityCan the agent inspect errors without turning observability into an unbounded data pipe?Docker MCP toolingLocal gateway, catalog, containerized MCP operationsCan servers be packaged and scoped consistently across teams?Form.io MCP ServerForms, resources, actions, APIs, and schema-driven application infrastructureCan the agent build against governed form and API patterns instead of improvising them?That is the useful MCP server list for regulated teams: not a popularity contest, but a map of which systems an agent can touch, how it authenticates, what it can change, and where the audit evidence lands.
## **What an MCP server list can and cannot tell you**
MCP, or Model Context Protocol, gives AI clients a standard way to connect to external tools and data. An MCP server is the bridge between the agent and a system such as GitHub, AWS, Jira, a browser, a database, or a domain platform such as Form.io.
An MCP server list helps with discovery. It does not prove that a server belongs in your enterprise agent environment.
That distinction matters because the official MCP Registry itself is a metadata layer. The registry documentation describes it as the official centralized repository for publicly accessible MCP server metadata, while also noting that it is still in preview and does not support private servers. It supports discovery, namespace authentication, installation metadata, and REST API access. It is not a substitute for enterprise security review.
That is the first mistake many teams make. They treat discovery as approval.
For a developer testing locally, that may be tolerable. For a regulated team, it is a weak control. A server that reads public docs is not in the same risk category as a server that can open pull requests, read customer tickets, execute cloud API calls, or inspect production error traces.
The list is the beginning. The trust decision comes after.
## **The regulated-enterprise filter**
Before you add a server to Claude Code, Cursor, VS Code, Windsurf, or another MCP client, ask six questions.
### **Who maintains it?**
Prefer official or vendor-maintained servers when the system is critical. A community server can be useful, but enterprise teams need a clear owner, release trail, issue history, and support path.
This is why GitHub, GitLab, AWS, Azure, Atlassian, Playwright, Docker, Sentry, and Form.io deserve separate treatment from generic directories. They are not just "available MCP servers." They are maintained by, or directly tied to, the systems they expose.
### **What identity model does it inherit?**
A lower-risk server is usually one that inherits the identity and permission model already governing the system.
[GitLab's MCP docs](https://docs.gitlab.com/user/gitlab_duo/model_context_protocol/mcp_server/), for example, describe OAuth registration and HTTP transport options, and they support GitLab.com, Self-Managed, and Dedicated environments. [Atlassian's remote MCP server](https://support.atlassian.com/atlassian-rovo-mcp-server/docs/getting-started-with-the-atlassian-remote-mcp-server/) uses OAuth 2.1 and respects Jira, Confluence, and Compass permissions. [Azure MCP Server](https://learn.microsoft.com/en-us/azure/developer/azure-mcp-server/overview) uses Microsoft Entra ID through Azure Identity.
That matters more than convenience. If the server works around identity, it works around governance.
### **What can it mutate?**
Read-only access is one risk. Write access is another. Production mutation is another.
A server that searches docs can still leak context. A server that changes infrastructure, submits forms, opens tickets, or modifies code can create operational state. Treat those differently.
The [MCP security guidance](https://modelcontextprotocol.io/specification/2025-06-18/basic/security_best_practices) calls out risks such as confused deputy behavior, token passthrough, SSRF, session hijacking, local server compromise, and the need to minimize scopes. Those are not abstract security concerns. They are what happens when an agent can act through a server whose authority is broader than the user's intent.
### **Where are logs written?**
Regulated teams need evidence. If an agent uses a server to retrieve context, change an issue, call an API, or update a form definition, the team needs to know where that action is logged.
AWS is a useful benchmark here. AWS announced the [AWS MCP Server general availability](https://aws.amazon.com/about-aws/whats-new/2026/05/aws-mcp-server/) on May 6, 2026, describing IAM-based guardrails, Amazon CloudWatch metrics, and AWS CloudTrail logging. That does not make every AWS MCP use case automatically approved, but it does give enterprise teams a familiar evidence model.
### **What data crosses the boundary?**
Some MCP servers expose local files. Some expose SaaS data. Some connect to cloud accounts. Some connect to internal systems. Some domain-specific servers, such as the Form.io AI toolset, connect to a customer's self-hosted environment.
The boundary is the point.
Form.io describes its MCP Server as connecting to a customer's self-hosted Form.io deployment so AI coding agents can work with forms, resources, actions, and APIs without moving that governed surface outside the enterprise boundary. That is a different posture from a generic public directory listing.
### **Is this build-time or runtime?**
Do not collapse every agentic tool into one bucket.
MCP servers are usually build-time or operator-time connectors. They help coding agents and assistants read context, call tools, scaffold work, or interact with systems.
Runtime agent governance is different. Form.io's [Universal Agent Gateway](https://form.io/uag/) belongs in that adjacent category. UAG is not the same thing as the Form.io MCP Server. The MCP Server helps AI coding agents build against Form.io patterns. UAG governs production agent workflows at runtime.
Regulated teams need both concepts, but they should not confuse them.
## **The MCP servers worth knowing**
### **1. Official MCP Registry**
Use the official registry as the starting point, not the finish line.
The [official registry](https://modelcontextprotocol.io/registry/about) is valuable because it gives teams a canonical discovery surface for public MCP servers. It supports server metadata, namespace authentication, REST API discovery, package references, and standardized installation information.
For enterprise teams, the important detail is the limit. The registry is public. It is still in preview. It is not where private enterprise servers should live. It also does not remove the need to review code, packages, transport, authentication, scopes, and data handling.
Use it to find servers. Do not use it as your approval workflow.
### **2. GitHub MCP Server**
The [GitHub MCP Server](https://github.com/github/github-mcp-server) belongs in many enterprise developer shortlists because GitHub is where source code, issues, pull requests, Actions, security findings, and review state already live for many teams.
That makes it powerful. It also makes it sensitive.
A coding agent that can inspect a repo, summarize issues, open a pull request, or reason over security findings is operating close to the SDLC evidence trail. That can be a good thing when the team scopes access properly. It can be a problem when every repo is available by default.
Use GitHub MCP when the agent needs to work inside the same development boundary developers already use. Scope it to the repositories and operations needed for the task.
### **3. GitLab MCP Server**
GitLab deserves its own place because many regulated organizations use self-managed GitLab or GitLab Dedicated rather than a purely public SaaS setup.
The official GitLab MCP documentation supports GitLab.com, Self-Managed, and Dedicated environments. It also warns that users are responsible for guarding against prompt injection and should use MCP tools only with trusted GitLab objects.
That warning is useful. It says the quiet part plainly: permission inheritance is not the whole security model. If an agent reads hostile issue content, merge request comments, or documentation, those objects can become part of the instruction stream.
Use GitLab MCP where GitLab is already the system of record for code and planning, but pair it with prompt-injection hygiene and object-scope limits.
### **4. AWS MCP Servers**
AWS MCP belongs in the list because cloud infrastructure is where agent mistakes become expensive.
AWS has multiple MCP surfaces, including [AWS Labs servers](https://github.com/awslabs/mcp/) and the generally available [AWS MCP Server](https://aws.amazon.com/blogs/aws/the-aws-mcp-server-is-now-generally-available/). The managed server is especially relevant to enterprise teams because AWS describes IAM guardrails, SigV4-style authenticated access through the Agent Toolkit, CloudWatch metrics, CloudTrail logging, AWS Knowledge MCP, AWS API MCP capabilities, and access to more than 15,000 AWS APIs.
That is exactly why the risk bar is high.
An agent that can ask AWS docs questions is one thing. An agent that can call AWS APIs is another. The minimum viable control is least-privilege IAM, environment separation, and CloudTrail visibility. Without those, cloud MCP access is too broad for regulated workflows.
Use AWS MCP for documentation, architecture support, and tightly scoped operations. Do not give a general coding agent broad cloud authority just because the server exists.
### **5. Azure MCP Server**
Azure MCP is important for teams whose cloud control plane already sits under Microsoft identity.
Microsoft's Azure MCP Server documentation describes integration with Azure resources, developer tools such as VS Code and GitHub Copilot, and authentication through Azure Identity. For enterprise teams, the key phrase is not "Azure resources." It is identity inheritance.
If the server can operate through Entra ID-backed access patterns and the same Azure permissions teams already govern, it fits better than a standalone connector with its own unmanaged secrets.
Use Azure MCP where the team already has mature Azure role design, environment separation, and resource governance.
### **6. Atlassian Rovo MCP Server**
Jira and Confluence are where a lot of enterprise work actually lives: requirements, tickets, runbooks, decisions, incident notes, acceptance criteria, and stakeholder context.
Atlassian's Rovo MCP Server documentation describes OAuth 2.1, support for Jira, Confluence, and Compass, permission inheritance, and IP allowlisting behavior in Atlassian Cloud.
That makes it a strong context server, especially for coding agents that need product intent or implementation history.
The risk is also obvious. Tickets and docs often contain sensitive business context, customer details, credentials copied where they should not be, and architectural notes. Permission inheritance helps, but it does not classify the content for you.
Use Atlassian MCP for project and documentation context, with clear limits on what spaces, projects, and user scopes are exposed.
### **7. Playwright MCP**
Playwright MCP is one of the most useful developer servers because it gives agents a structured way to interact with web pages and browser workflows.
The [Playwright MCP docs](https://playwright.dev/docs/getting-started-mcp) describe use of accessibility snapshots rather than screenshots or pixel-based interaction. That is the right foundation for repeatable browser automation.
But the same documentation also warns that direct Playwright code execution is effectively remote code execution and should only be enabled for trusted MCP clients.
That is the regulated-enterprise lesson in miniature. A tool can be both useful and unsafe if enabled in the wrong mode.
Use Playwright MCP for testing, QA, browser workflows, and UI validation. Disable unsafe direct-code tools unless the client and execution environment are trusted.
### **8. Sentry MCP**
The [Sentry MCP Server](https://github.com/getsentry/sentry-mcp) belongs in the operational layer. It helps agents inspect errors, traces, issues, and debugging context.
That can compress the time between "the build failed" and "the actual production error is understood." It also exposes operational data that may include request context, user metadata, stack traces, and environment details.
For regulated teams, observability MCP should be scoped like production support access, not like a convenience plugin.
Use Sentry MCP when the agent is doing debugging or remediation work, and restrict the projects, environments, and data fields that should be visible.
### **9. Docker MCP tooling**
[Docker's MCP tooling](https://docs.docker.com/reference/cli/docker/mcp/) is less about one business system and more about packaging, gateway behavior, and local developer operations.
That makes it useful for standardization. Enterprise teams do not want every developer hand-rolling MCP server installation and transport decisions in a different local config file.
Use Docker MCP tooling to make server setup more repeatable, especially when you need a catalog or gateway-style operating model across teams.
### **10. Form.io MCP Server**
Form.io belongs in this MCP server list because regulated applications often begin at the data-capture layer: forms, resources, validation rules, submission records, workflow actions, APIs, permissions, revisions, and audit evidence.
That is the layer where generic coding agents can create drift fastest.
One team builds a React form. Another builds a different submission API. A third adds an agent workflow. Each piece works. None of them share the same governance contract.
The [Form.io AI toolset](https://form.io/ai/) exists to push the agent toward the governed path at build time. The Form.io MCP Server connects AI coding agents to a customer's self-hosted Form.io deployment so they can read, create, and scaffold forms, resources, actions, and APIs from the same platform primitives. Form.io Skills guide the agent toward platform-specific patterns. The Agentic Coding Plugin brings that MCP Server and skill library into the developer's coding environment.
That makes Form.io different from a generic connector.
It is not just giving an agent another data source. It is giving the agent a governed application primitive: schemas that can produce interfaces, APIs, validation behavior, submissions, permissions, and workflow hooks from the same definition.
For teams using Form.io as [schema-driven application infrastructure](https://form.io/platform/), this is the right kind of MCP server: one that makes the governed path easier than building around it.
That value shows up in customer language too. In a [Safety Mojo case study](https://form.io/case-studies/nextgen-flexibility-for-a-nextgen-application/), a long-time Form.io platform user put it plainly: "Form.io cleans up all the dirty work and does it for you." The surrounding case study frames that value as months of development time saved on a next-generation application launch.
## **How to decide what belongs in your agent context**
The fastest way to create MCP sprawl is to install every useful server globally.
Do not do that.
Treat MCP servers like permissions. Most should be project-specific, task-specific, or environment-specific.
Use this sequence:
1. Start with read-only discovery.
2. Prefer official or vendor-maintained servers.
3. Scope by project, repo, workspace, tenant, or environment.
4. Keep mutation tools disabled until the workflow needs them.
5. Separate local development access from production access.
6. Route secrets through existing identity systems where possible.
7. Log agent actions in the system of record.
8. Review prompt-injection exposure when the server reads user-authored content.
9. Revoke unused servers.
That may sound slower than "install the top 20 MCP servers." It is not slower when you count remediation.
A regulated team that cannot explain which server had which permission at which point in a workflow does not have an MCP strategy. It has a collection of shortcuts.
## **Why domain-specific MCP matters**
Generic MCP servers are good at giving agents access to tools. Domain-specific MCP servers are better when the agent needs to create governed artifacts.
That difference is especially important for forms and workflow data.
A generic file server can read a schema file. A GitHub server can modify code. A browser server can test a form. None of those, by itself, tells the agent what a valid governed form workflow should look like inside the enterprise.
Form.io's MCP Server does.
The reason is architectural. Form.io is not only a form renderer. Its [drag-and-drop form builder and API model](https://form.io/features/drag-and-drop-form-builder-apis/) treats form definitions as JSON-backed application infrastructure. Forms can produce APIs. Submission data is managed separately from Form JSON. Form revisions and submission management matter because historical state and current state are not always the same thing.
That is why the Form.io MCP Server matters for regulated developers. It helps the coding agent build with the same primitives the platform governs: forms, resources, actions, APIs, roles, group permissions, server-side actions, [form revision history](https://form.io/features/form-revisions-form-json-schema/), and [complete audit trails](https://form.io/features/log-forms-complete-audit-trail/).
That does not mean Form.io replaces GitHub, GitLab, AWS, Azure, Playwright, Sentry, or Atlassian. It means Form.io occupies a different layer: the form and workflow infrastructure layer where business data enters the system and becomes governed submission state.
## **What proof should enterprise teams look for?**
Popularity is weak proof.
Stars, upvotes, and directory rank tell you that a server is visible. They do not tell you whether the server is appropriate for regulated work.
Better proof looks like this:
- Official or vendor-maintained source.
- Clear authentication model.
- Clear transport model.
- Least-privilege configuration.
- Permission inheritance from the system of record.
- Audit logging for meaningful actions.
- Environment separation.
- Versioned releases.
- Security guidance.
- Support for private or self-managed deployment where needed.
The production-readiness gap is real. A [2026 research paper on production MCP](https://arxiv.org/abs/2603.13417) reports more than 10,000 active MCP servers and 97 million monthly SDK downloads, while also arguing that production MCP still needs stronger identity propagation, adaptive tool budgeting, structured error semantics, and observability.
That is the point. MCP adoption is moving faster than MCP governance.
The answer is not to wait. The answer is to be precise.
Use servers that inherit controls you already trust. Scope them narrowly. Prefer domain-specific servers when the agent is creating governed artifacts. Treat runtime agent governance as a separate layer from coding-time MCP.
## **Key takeaways**
- An MCP server list helps you discover options, but it does not approve them for regulated use.
- Official and vendor-maintained servers should carry more weight than generic directory entries.
- Evaluate each server by identity, permissions, audit evidence, transport, data boundary, and mutation risk.
- GitHub, GitLab, AWS, Azure, Atlassian, Playwright, Sentry, Docker, and Form.io each occupy different control surfaces.
- Form.io's MCP Server is a build-time path into governed form and API infrastructure; UAG is the separate runtime governance layer.
## **FAQ**
### **What is an MCP server list?**
An MCP server list is a directory, registry, repository, or article that helps developers find Model Context Protocol servers. The best starting point is the official MCP Registry, but regulated teams should treat any list as discovery rather than approval.
### **What is the safest way to find MCP servers?**
Start with official sources: the official MCP Registry, vendor documentation, vendor-maintained GitHub repositories, and your own internal registry for private servers. Avoid installing servers only because they appear in a public directory or social post.
### **Are MCP servers secure?**
MCP servers are not automatically secure or unsafe. Security depends on the server's code, maintainer, transport, authentication model, tool scope, permissions, data access, and execution environment. The MCP security guidance specifically calls out risks such as confused deputy behavior, token passthrough, SSRF, session hijacking, local compromise, and scope minimization.
### **Should regulated teams use community MCP servers?**
Sometimes, but not casually. A community server can be useful for low-risk local workflows, prototypes, or read-only tasks. For sensitive systems, prefer official or vendor-maintained servers, or run an internal review before adding the server to an enterprise agent environment.
### **Which MCP servers are best for developers?**
A practical regulated-enterprise list usually starts with GitHub or GitLab for SDLC work, Playwright for browser testing, AWS or Azure for cloud workflows, Atlassian for ticket and documentation context, Sentry for debugging, Docker for packaging and gateway patterns, and Form.io for governed form/API infrastructure.
### **What is the difference between an MCP registry and an MCP server?**
An MCP registry helps you discover servers and their metadata. An MCP server is the actual connector that exposes tools, data, or actions to an MCP client. A registry is not a security review, and it does not mean the server is safe for your environment.
### **How does Form.io fit into an MCP server list?**
Form.io fits when the agent needs to work with governed form and workflow infrastructure. The Form.io MCP Server gives AI coding agents access to Form.io forms, resources, actions, and APIs inside the customer's deployment boundary, while Form.io Skills guide the agent toward platform-specific implementation patterns.
### **Is Form.io UAG an MCP server?**
No. Form.io's MCP Server is build-time infrastructure for AI coding agents. UAG is runtime governance for production agent workflows. They belong in the same agentic architecture conversation, but they are not the same component.
### **Should MCP servers be installed globally?**
Usually no. Global installation encourages overbroad access. Regulated teams should scope MCP servers by project, workspace, environment, repository, tenant, or task. Mutation tools should be enabled only when the workflow requires them.
### **What should an enterprise MCP policy include?**
At minimum, it should define approved server sources, identity requirements, permission scopes, logging expectations, data-boundary rules, prompt-injection handling, environment separation, and a removal process for unused or deprecated servers.
### **When should a team build its own MCP server?**
Build your own MCP server when the system is internal, private, highly regulated, domain-specific, or poorly represented by public servers. Private systems should not be forced into public registries just to make them usable by agents.
## **Build Governed Form And API Workflows With Form.io**
If your team needs AI coding agents to build against governed forms, generated APIs, submission records, permissions, revisions, and self-hosted infrastructure, [try Form.io for governed form and API workflows](/try-formio-for-free/).
# AI Governance Platform: Agentic Workflow Governance Layers Compared
[  ](https://form.io/ai-governance-platform-agentic-workflow-governance-layers-compared/)AI governance platform searches hide several different problems under one phrase. A policy registry is not runtime tool-call control. A process engine is not schema-driven data access. If agents can read data, invoke tools, submit records, and trigger workflows, governance has to live where the agent acts. This comparison names the layer before judging the tool.
## **The AI Governance Gap Is Now Operational**
Most AI governance conversations started with model risk, policy documentation, and compliance review. Those still matter.
But agentic workflows add a sharper question: what happens when the AI system can do something?
Grant Thornton's 2026 AI Impact Survey found that 78% of senior business leaders lacked full confidence that their organization could pass an independent AI governance audit within 90 days. The same survey said 46% of leaders believed AI underperformed because controls and compliance were not working ([Grant Thornton](https://www.grantthornton.com/insights/press-releases/2026/april/grant-thornton-survey-on-ai-proof-gap)).
That is not just a board-level policy problem. It is an infrastructure problem.
Gartner's 2025 strategic technology trends report predicted that by 2028, at least 15% of day-to-day work decisions would be made autonomously through agentic AI, up from 0% in 2024 ([Gartner](https://www.gartner.com/en/newsroom/press-releases/2024-10-21-gartner-identifies-the-top-10-strategic-technology-trends-for-2025)). If even a small share of ordinary operational decisions moves through agents, governance has to follow the action, not only the policy record.
If an agent can approve a request, update a record, route a case, draft a decision, trigger an integration, or submit structured data into a system of record, the organization needs more than a governance statement. It needs an execution path that can answer:
- What was the agent allowed to do?
- Which identity or role gave it that permission?
- What schema, validation rule, or process state constrained the action?
- Was a human required to approve it?
- What audit evidence exists after the action?
An AI governance platform can help with policy, inventory, and risk. An agentic workflow needs that, plus runtime controls at the exact layer where the agent touches the business system.
## **Five Governance Layers To Compare**
The phrase "AI governance platform" is too broad unless you name the layer.
For agentic workflows, the main layers are:
**Governance layer****What it governs****Example fit**AI policy and risk governanceAI inventory, use cases, risk tiering, compliance evidence, board reportingCredo AI, OneTrust, IBM watsonx.governance, classic GRC-style AI governance suitesRuntime agent governanceTool calls, resource access, inter-agent messages, action-level policy enforcementMicrosoft Agent Governance ToolkitProcess orchestration governanceBPMN, case state, human tasks, SLAs, process audit trails, exception handlingCamunda 8.9, Flowable 2025.1, Appian process workflowsPlatform-native agent governanceAgents built and managed inside a specific app/process platformAppian Agent StudioSchema/API/data-access governanceThe forms, fields, validation rules, submissions, APIs, roles, and actions an agent uses to do workForm.io Universal Agent GatewayThese layers can overlap. They can also coexist.
A bank might use Microsoft Entra for agent identities, Microsoft Agent Governance Toolkit for action-level policy, Camunda for cross-system process orchestration, and Form.io UAG for governed access to intake forms, validation, submissions, and downstream workflow actions.
The mistake is treating those as interchangeable.
## **Quick Comparison**
## **Platform or toolkit****Governance center of gravity****Strongest fit****Watch the boundary**Form.io UAGSchema, form, API, submission, RBAC, and action governance exposed to agents through MCPAgents that need governed access to forms, submissions, validation, and workflow infrastructureNot a generic AI GRC dashboard or full BPMN engineAppian Agent StudioAgents embedded inside Appian's process/application platformTeams already building workflows in AppianStrong inside Appian's platform boundary; less about portable schema/API ownershipCamunda 8.9BPMN-based agentic orchestration, human tasks, process state, audit logs, MCP/A2ATeams that govern work through explicit process modelsGovernance starts at orchestration; the data-capture/schema layer may still live elsewhereFlowable 2025.1Agent engine beside BPMN/CMMN/DMN, agent exchange tracking, case/process controlDynamic case work and process automation with first-class agentsStrong process layer; still needs source-of-truth data contractsMicrosoft AGTRuntime policy enforcement, identity, sandboxing, OWASP agentic risk controlsDevelopers adding action-level governance to agent frameworksA toolkit, not a business workflow or forms infrastructure platform**Form.io UAG: When The Governed Schema Should Become Agent Context**
Form.io's Universal Agent Gateway is strongest when the agent has to operate through a governed form and workflow layer instead of a loose collection of prompts, tools, and credentials.
Form.io's core argument starts below the agent. In Form.io, Form JSON is the schema created by the form builder. The Form.io documentation says that schema is used to render forms inside applications, generate REST API interfaces on the server, and host the form schema at the embed URL ([Form.io Form JSON documentation](https://help.form.io/userguide/forms/form-building/form-json)).
That matters because an agent needs structured context.
An agent does not need a vague prompt saying "collect the right onboarding details." It needs to know which fields exist, which fields are required, what validation rules apply, how submissions are shaped, which actions can run, and what permissions apply to the current actor.
Form.io UAG turns that existing application infrastructure into the agent surface. The UAG page explains that agents can authenticate through existing Form.io auth and SSO, inherit enterprise RBAC, retrieve and route secure data inside the private network, and execute actions governed by Form.io Actions and audit trails ([Form.io UAG](https://form.io/uag/)).
That is a specific kind of governance. It is not "AI governance" as a board dashboard. It is governance at the layer where forms, APIs, submissions, validation, and workflow actions already meet.
This is why Form.io should not be framed as simply another AI agent platform. Form.io's AI page describes UAG as the runtime governance layer for production agentic workflows, while the MCP Server, Skills, and Agentic Coding Plugin support build-time development ([Form.io AI](https://form.io/ai/)). That separation is important. Build-time agents need patterns for creating software. Runtime agents need permissioned, logged access to production workflow surfaces.
The customer proof is not AI-specific yet, so it should be used carefully. But it does show why this infrastructure layer matters. In one Form.io public-sector case study, publicplan supported more than 400 digital public-sector services and 1,000+ forms while meeting strict standards and a short timeline ([Form.io publicplan case study](https://form.io/case-studies/the-digital-transformation-of-supporting-new-services-for-the-german-public-sector-on-repeat/)). In another Form.io banking case study, an international banking deployment served 5,000 banking groups and recovered 50% of the team's capacity ([Form.io banking case study](https://form.io/case-studies/how-many-technologies-can-actually-support-the-business-process-transformation-of-serving-5000-banking-groups/)).
Those are not UAG deployment claims. They are infrastructure claims. They show why a governed forms/API/submission layer is valuable before agents arrive. UAG extends that same layer to agents.
### **Strongest Fit**
Form.io UAG is the strongest fit when:
- forms are part of the application contract, not just hosted collection pages
- agents need to understand field structure, validation rules, submission shape, and workflow actions
- the customer needs self-hosted or private-network control
- RBAC, auth, audit trails, and form revisions are already part of the governance model
- the team wants humans and agents operating through the same governed schema layer
Form.io is not the right answer if the buyer only needs a general AI policy registry. It is the right answer when the agent's work touches form-driven application infrastructure.
## **Appian Agent Studio: When Agents Belong Inside The Appian Process Platform**
Appian's governance story is platform-native.
Agent Studio is built for teams that already use Appian to design applications, workflows, data fabric patterns, and enterprise processes. Appian's 25.4 release material frames Agent Studio as a guided way to create enterprise AI agents and drag them into business processes. Appian also says agents embedded in processes can use guardrails, tools, data, and human review inside the process context (Appian Agent Studio release material).
That is a clear fit when Appian is already the process application platform.
The governance center is not the open schema/API layer. It is the Appian platform boundary. Agents live inside the Appian design and process model, use Appian objects and tools, and inherit governance from the Appian environment.
That can be exactly what an Appian customer wants. It is less compelling when a team needs agent access to application-owned forms, APIs, validation rules, submissions, and deployment boundaries outside Appian.
### **Strongest Fit**
Appian Agent Studio fits when:
- the business process already lives in Appian
- low-code process design is the center of gravity
- agents need to operate inside Appian's app/process/data fabric layer
- the organization wants human review and process guardrails inside the same platform
The Form.io contrast is not "Appian cannot govern agents." It can govern them inside its platform. The Form.io distinction is that governance starts at the schema and form infrastructure layer agents use to collect, validate, submit, and route data.
## **Camunda 8.9: When BPMN Orchestration Is The Governance Backbone**
Camunda approaches agentic governance from the process orchestration layer.
In its 8.9 release, Camunda frames agentic orchestration as coordinating AI agents, knowledge workers, tools, and systems across end-to-end business processes. The release emphasizes deterministic process logic, global user task listeners, centralized audit logs, MCP access to running clusters, and A2A support for multi-agent communication (Camunda 8.9 release material).
That is a strong governance story for teams that already model work as BPMN.
The useful distinction is this: Camunda governs the flow of work. It controls process state, human tasks, incidents, retries, escalation, and the audit trail around the process. That is different from governing the form schema, validation logic, submission payload, or field-level context an agent uses before it reaches a process step.
In many architectures, both layers matter.
A government service workflow might use Form.io to collect and validate service request data through self-hosted forms and generated APIs, then use Camunda to orchestrate downstream case routing, approvals, exceptions, and cross-system work. The agent should respect both layers.
### **Strongest Fit**
Camunda fits when:
- BPMN is already the operating language for process governance
- the organization needs explicit process state and incident handling
- agents participate in workflows with human tasks and deterministic rules
- auditability needs to follow the end-to-end process path
Form.io fits earlier in the path: where the agent needs governed access to the structured data, forms, validation rules, and APIs that feed the process.
## **Flowable 2025.1: When Case And Process Work Need First-Class Agents**
Flowable's 2025.1 release puts agents beside BPMN and CMMN rather than treating them as external helpers.
Flowable says the release adds an agent engine alongside its BPMN and CMMN automation engines, with internal agent types such as utility, document, knowledge, and orchestrator agents. It also describes agent exchange tracking as a way to store AI interactions for traceability and audit support (Flowable 2025.1 release material).
That makes Flowable a serious process/case governance comparison.
Its strongest fit is dynamic work: cases, documents, human judgment, process variation, and AI-assisted decisions that need to stay inside a process/case model. If a case state determines what an agent can and cannot do, Flowable's governance center makes sense.
The Form.io distinction is again layer ownership.
Flowable can govern the case or process. Form.io can govern the structured form and submission layer that feeds the case. In agentic workflows, those are connected but not identical.
### **Strongest Fit**
Flowable fits when:
- work is case-heavy and may not follow one fixed process path
- AI agents need to operate inside CMMN/BPMN-style orchestration
- traceability of agent exchanges matters
- the organization wants an agent engine inside the process platform
Form.io fits when the agent's most important constraint is the governed schema, validation, permission, submission, and action surface around data intake and form-driven workflows.
## **Microsoft Agent Governance Toolkit: When Developers Need Runtime Action Controls**
Microsoft Agent Governance Toolkit is the most developer-centered entry in this comparison.
Microsoft introduced AGT as an open-source runtime security governance project for autonomous AI agents. The announcement says the toolkit is designed to work with existing frameworks and includes deterministic policy enforcement, identity, sandboxing, reliability controls, and mapping to OWASP agentic AI risks ([Microsoft open-source announcement](https://opensource.microsoft.com/blog/2026/04/02/introducing-the-agent-governance-toolkit-open-source-runtime-security-for-ai-agents/)).
That layer matters because agents can misuse tools even when the surrounding workflow looks well designed.
Microsoft's later Agent Framework guidance makes the layer even clearer: Agent Framework handles build and orchestration, while Agent Governance Toolkit handles govern and audit. It evaluates tool calls, resource access, and inter-agent messages against policy before execution ([Microsoft Agent Framework and AGT](https://devblogs.microsoft.com/agent-framework/governance-at-the-speed-of-agents-microsoft-agent-framework-and-agent-governance-toolkit-better-together/)).
That is not the same job as Form.io UAG.
AGT helps govern the agent's actions at runtime. Form.io UAG gives agents governed access to Form.io's form, submission, schema, API, RBAC, and action layer. In some architectures, AGT could sit beside or around an agent framework, while UAG provides the business-specific tools and context the agent is allowed to use.
### **Strongest Fit**
Microsoft AGT fits when:
- developers need action-level policy checks inside an agent framework
- tool-call misuse, goal hijacking, rogue agents, or inter-agent trust are the main concern
- the team wants an open-source runtime governance toolkit
- the application/workflow platform is already chosen elsewhere
Form.io fits when the agent needs a governed business surface for form-driven work, not only a policy wrapper around tool calls.
## **How To Choose The Right Governance Layer**
The useful question is not "which AI governance platform should we buy?"
The useful question is: where can the agent create the most risk?
### **If The Risk Is AI Inventory And Compliance Evidence**
Start with a classic AI governance platform.
This is the layer for model inventory, use-case approvals, risk tiers, policy mapping, regulatory documentation, monitoring, and executive accountability. It matters most when the organization cannot answer which AI systems exist, who owns them, what risk category they fall into, or what evidence supports approval.
Form.io does not replace that layer.
### **If The Risk Is Tool-Call Misuse**
Look at runtime agent governance.
This is where Microsoft Agent Governance Toolkit is relevant. It helps evaluate actions before execution and provides runtime security controls for autonomous agent frameworks.
Form.io can supply governed business tools and context; AGT can help enforce broader action-layer policies.
### **If The Risk Is Process Visibility**
Look at process orchestration.
Camunda, Flowable, and Appian are stronger when the work has to be governed as a process or case: state, sequence, incidents, handoffs, human review, SLAs, escalation, and full process auditability.
Form.io can still matter if the workflow starts with governed forms, submissions, and APIs.
### **If The Risk Is Data, Schema, And API Drift**
This is where Form.io belongs.
If humans use one form definition, APIs use another contract, agents use a prompt-based tool description, and workflow actions use yet another set of assumptions, governance will drift. The agent may still complete the task. The organization may not be able to prove that the task followed the governed path.
Form.io's stronger argument is that the same Form JSON and platform layer can define the form, the validation, the generated API surface, the submission shape, permissions, and the runtime agent context.
That starts with deployment control. A [self-hosted Form.io](https://form.io/features/self-hosted-forms-for-enterprise/) environment lets the form and submission layer live inside the customer's own infrastructure boundary.
It also starts with the form contract itself. The [drag-and-drop form builder with APIs](https://form.io/features/drag-and-drop-form-builder-apis/) is not only a visual authoring surface; it produces structured definitions that can become application interfaces.
Governance then depends on behavior, not just fields. [Conditional logic and validation](https://form.io/features/form-conditional-logic-form-validation/) help define what data is acceptable before a workflow or agent acts on it.
Finally, the work has to map to people and roles. [Teams and permissions](https://form.io/features/forms-for-teams/) belong in the same architecture conversation because agent access should inherit the same governance model that controls human access.
## **Where Form.io Fits**
Form.io is not trying to be every layer of AI governance.
That is a strength, not a weakness.
Form.io is strongest when forms are application infrastructure: the schema, user interface, generated API, validation model, submission record, permission boundary, and workflow trigger are connected. When agents enter that environment, the agent should not get a separate shadow contract. It should operate through the same governed layer as the application.
That is the UAG argument.
If your organization only needs an AI policy dashboard, choose an AI governance suite. If it needs action-level runtime policy enforcement across agent frameworks, evaluate a toolkit like Microsoft AGT. If it needs process orchestration, evaluate Camunda, Flowable, or Appian.
If the agent needs governed access to forms, fields, submissions, APIs, validation rules, permissions, and workflow actions inside a customer-controlled deployment, Form.io should be in the conversation.
## **Key Takeaways**
- AI governance platform is too broad unless you name the layer.
- Agentic workflows need governance where agents act, not only where policies are documented.
- Form.io UAG governs the schema/API/form/submission/action layer for production agents.
- Appian, Camunda, and Flowable govern agents through process or case platforms.
- Microsoft AGT governs runtime tool calls and action policies.
- The strongest architecture can combine layers instead of forcing one product to do every job.
- Form.io's strongest claim is not generic AI governance. It is governed application infrastructure for agents working through forms, APIs, validation, submissions, permissions, and actions.
## **FAQ**
### **What Is An AI Governance Platform?**
An AI governance platform helps organizations manage AI risk, policy, accountability, compliance evidence, monitoring, and operational controls. In classic enterprise usage, it often includes AI inventory, use-case approvals, risk classification, policy mapping, audit evidence, and reporting.
For agentic workflows, the term needs more precision. A platform that governs model risk is not automatically the same as a tool that governs agent actions, process state, form submissions, or API access.
### **What Is Agentic Workflow Governance?**
Agentic workflow governance is the set of controls that determines what an AI agent can do inside a business process. It covers tool access, data access, identity, permissions, validation, human review, logging, audit trails, exception handling, and policy enforcement.
The key difference is action. A chatbot that answers a question needs content safety. An agent that updates a submission or triggers a workflow needs execution governance.
### **Is Form.io UAG An AI Governance Platform?**
Form.io UAG is most accurately understood as a runtime governance layer for agents operating through Form.io infrastructure. It is not a general AI GRC dashboard.
UAG gives agents governed access to the Form.io layer: forms, field definitions, validation, submissions, actions, auth, RBAC, and application workflow context. That makes it highly relevant to agentic workflow governance, especially when forms and APIs are part of the customer-controlled application stack.
### **How Is Form.io UAG Different From Microsoft Agent Governance Toolkit?**
Microsoft Agent Governance Toolkit focuses on runtime policy enforcement for agent actions: tool calls, resource access, identity, sandboxing, and auditability around the agent framework.
Form.io UAG focuses on the business surface the agent uses when work involves forms, submissions, validation, APIs, and workflow actions. AGT can help govern the agent's behavior. UAG gives the agent a governed Form.io context to operate through.
### **How Is Form.io UAG Different From Process Engines?**
Process engines such as Camunda and Flowable govern processes and cases. They are strong when the main governance problem is end-to-end orchestration: state, sequence, human tasks, incidents, escalation, and process audit trails.
Form.io governs the form and data infrastructure layer. It is stronger when the main governance problem is schema, validation, submissions, permissions, APIs, and form-driven workflow actions. Many enterprise architectures can use both layers.
### **When Should A Team Use A Classic AI Governance Suite Instead?**
Use a classic AI governance suite when the main problem is enterprise oversight: AI inventory, use-case approvals, risk scoring, regulatory mapping, model monitoring, audit evidence, and board-level accountability.
Use Form.io UAG when the main problem is operational: agents need governed access to forms, submissions, validation, APIs, and workflow actions. The two layers can complement each other.
### **Why Does Schema Matter For Agent Governance?**
Agents need structured context. A schema tells the agent what fields exist, which data is required, what validation rules apply, how submissions are shaped, and which actions are meaningful.
When the same schema drives human forms, APIs, validation, and agent context, the organization reduces drift. The agent is less likely to operate from stale prompt instructions or a parallel tool definition that no longer matches the application.
### **Can Form.io Replace A Process Engine?**
No. Form.io should not be framed as a full process engine replacement.
Form.io is infrastructure for forms, APIs, submissions, validation, permissions, and workflow-related actions. If the organization needs full BPMN or case orchestration, a process engine may still be appropriate. Form.io's role is to make the form and data capture layer governed enough for humans, developers, systems, and agents to use safely.
## **Build Governed Agentic Workflows With Form.io**
If your agents need to work through forms, submissions, APIs, validation rules, permissions, and workflow actions inside your own deployment boundary, start with the governed infrastructure layer.
[Try Form.io for governed agentic workflow infrastructure](/try-formio-for-free/).
#### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# Form.io Features
*Published:* 2024-02-03
*Author:* Form.io Wizard
*URL:* https://form.io/features/
*Description:* LLM Description: Full feature catalog — auth, RBAC, server-side Actions, integrations, PDF workflows, mobile, accessibility, audit, white-label, and multi-tenancy.
## What Can You Do With Form.io?
### Everything you need to build complex, form-driven, business process workflow applications with less effort, in less time, without sacrificing scope, security, or sanity.
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
![]()#### [](https://form.io/features/)
Form.io is incredible and exactly what we've been searching for. For years, we have gone through many different form builders and while most of them had some good features, they were all lacking in crucial areas that made it impossible for us to continue using them. After many years of struggling, we found Form.io and now we're able to do exactly what we wanted to do for years but couldn't. The team at Form.io is also incredible helpful and knowledgeable. This is review is for organizations who are in a similar situation that we were in and haven't been able to find the RIGHT solution that ticks all boxes. Give Form.io a try, you won't be disappointed! —Lesley Van De Mortel ### Looking for an ultra-specific answer to your question? Check our help documentation:
## OR The Fundamental Toolset For Building Apps That Make AI Work For Enterprise
### If You're Building An AI-Powered App, This WILL Save You Headaches And Time
## Before Writing Another Line Of Code What's In The Embedded Enterprise Configurations?
### Your configuration in your environment means no surprise usage fees.
#### Developer Portal
Included Form.io's primary interface that enables developers to manage projects, sub-projects, teams, resources, forms, PDFs, submission data, and more.
#### Form & API Builder
Included The drag and drop interface that enables developers to build forms and their APIs in one step automatically.
#### Form Renderer
Included The JavaScript rendering engine, compatible with all major frameworks, that renders a single string into forms on page at the application level.
#### FormView Pro
Included Launch completed forms in a single-page application, manage users and authentication, view, manage, and export submission data, and define form permissions.
#### PDF Plus Server
Optional Convert PDFs into forms to collect data, output to PDF for user-facing downloads, enable pixel-perfect form backgrounds, and digital webform overlays.
#### Enterprise Form Builder
Optional The Enterprise Form Builder is a configurable module that enables you to provide your customers a fully white-labeled, customized, pre-wired form building experience in your app.
#### Premium Components
Optional Revisions, collision control, automatic accessibility, security and encryption, translations, e-signatures, audit logging, email integration, offline mode, and more.
#### Multi-Tenancy
Optional Provide your customers with their own form, API, and data management tools, fully white-labeled under your brand or your customers' brands.
### Self-Hosted, Enterprise Deployments That Won't Burden Your IT People
The flexible, configurable main API platform and portal interface for Form.io plus your selection of à la carte enterprise addons, completely wired, licensed, and maintained for you with all dependencies, delivered to you through your orchestration of choice, including Docker container.
Deploy within your own on-premise or private cloud production and non-production environment(s) with total control and peace of mind.
#### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---
# How Form.io Works
*Published:* 2024-01-31
*Author:* Form.io Wizard
*URL:* https://form.io/how-it-works/
*Description:* Architectural overview of the platform — JSON schema as a single source of truth, auto-generated REST APIs per form and resource, server-side Actions as configurable middleware, and forms embedded directly into your application.
## Form.io does for you the costly, frustrating, and time-consuming things required to connect your data and systems by decoupling forms and API building from your application development.
## Or ask us about a self-hosted trial Embrace the strategy that provides you a scalable, performant, open-architected, unopinionated, and configurable, solution
### That's embedded in your environment so you can maintain control of your data and security.
##### Form.io Does What You Need It To Without Getting In Your Way
It has an Open Source Core that's supported by hundreds of developers and is constantly improving so you never feel trapped.
It's Unopinionated so it works the way you want, down to every individual field, data flow, validation, logic, and style.
It's Extensible which lets you add whatever you need or create whatever you can dream up, which will make your engineering team love you.
It's Fully deployed in your environment giving you 100% control of your data with zero added risk.
##### Thin Application Layer
With dynamic, JSON-rendered forms
 ##### Submission Database
IN: Pre-populated data from existing databases
OUT: Submission data to external databases
##### Form.io Embedded Platform
With the Developer Portal that manages your bank of interchangeable forms, APIs, user access, integrations, and submit actions.
1. ##### Thin Application Layer
With dynamic, JSON-rendered forms
2. ##### Form.io Embedded Platform
With the Developer Portal that manages your bank of interchangeable forms, APIs, user access, integrations, and submit actions.
3. ##### Submission Database
IN: Pre-populated data from existing databases
OUT: Submission data to external databases
## Decouple Form Building From Application Code Development
### Eliminate the costly, frustrating, and time-consuming things with forms, form data, and their APIs by empowering non-developers to build them for you.
#### With Form.io's Drag And Drop Form & API Builder
Form.io's Developer Portal provides you with the drag-and-drop Form Builder that automatically generates the necessary API in real time so you don't have to spend excessive time writing the syntax.
It also includes everything you need to manage users, admins, and permissions and view form submissions within your enterprise project—ALL of which is deployed in your environment—embedded.
#### And Render Forms Directly In Your App For Speed, Flexibility, And Simple Integration
Form.io's Form Renderer is compatible with all major JavaScript frameworks and it's deployed in your environment so that nothing happens outside of your control that could pose an additional security risk—embedded.
PLUS, your forms can be fully embedded into your apps (NO iframes) with your custom CSS so that your brand is in front of your users or your customers’ brands are in front of their users—embedded.
#### With Plug And Play Data Management
Slash your operational costs with Form.io's pre-configured data management that automatically collects and stores form submission data and provides you the tools to view, manage, and export.
AND, you don't have to worry about scalability because there are no arbitrary limits, nor meeting security or compliance requirements either because they're built in.
Since everything is an API, you have the flexibility to integrate with other applications and create automated workflows that can save time across your organization.
## Your Uptime And Performance Aren't Dependent On Form.io Or Any Third Party
### Because when everything is deployed in your environment, you have full control.
### PLUS, the core [Form & API platform is open source](https://github.com/formio/formio) so you are welcome to modify it, extend it, or just see how it works.
## What Technologies Are Compatible With Form.io?
### For self-hosting the Form.io platform in your environment.
#### Cloud Environments
Any environment where you can stand up a load balancer, container, and a database, including but not limited to the big 3:
- Azure
- AWS
- GCP
#### Authentication Schemas
Any authentication schema including the following:
- SAML
- OAuth / OIDC
- LDAP
- Custom JWT Tokens
- Email with 2FA
#### Application Environments
Regardless of what you use, as long as JavaScript is loaded, Form.io's platform can be a thin layer within your application, including but not limited to:
- React
- Angular
- Vue
- .NET
- Node.js
- CMS's
#### Orchestrations
Regardless of your devops strategy for deployment, scaling, or management of containerized solutions, Form.io can be deployed in any way including leveraging the following:
- Kubernetes
- Docker Compose
- Helm Charts
- Terraform
- GCP Cloud Run
- AWS Cloud Formation
#### Databases
Form.io requires MongoDB or equivalent to run (remember, data can also be sent to any 3rd-party database), including:
- MongoDB Atlas
- AWS Document DB
- Azure Cosmos DB
- Mongo Enterprise Advanced (for on premise deployments)
## Get Started With Your First Project
### Try our SaaS to see how it works right now
#### 1. Create Your Project
A project contains the Resources and Forms necessary to build a Progressive application. You can create a new project from scratch or from an existing pre-built template.
In this example, we're creating a project from scratch, which includes a default set of forms and resources for user authentication.
#### 2. Build Resources
Resources serve as the common data model objects required for your application. Using our simple drag-and-drop form builder interface, you can build the data Resource models for your application, which can then be used within other Forms and Resources to create sophisticated data model relationships so you're not limited in what your app can do.
Resources and forms are nearly identical in structure, but they are classified differently to help you stay organized and know what's used to store data (Resources) and what's rendered on the page (Forms).
#### 3. Create Forms
Create the form interfaces that will be used within your application. Every form and resource has an automatically generated REST API associated with it!
Our form building capabilities can also be embedded within your own application so that you can offer the same powerful form building experience to your customers.
#### 4. Trigger Actions
Each form can have an unlimited number of Actions associated with it which allows for sending Emails, 3rd Party Integrations, Authentication, and much more.
In this example, we're editing the Save Action on a form to save the data to a resource where each field in the form is mapped to a field in the resource.
#### 5. Embed Your Forms
Our form embedding technology allows you to utilize one single tag to embed a dynamic [JSON powered form](/json-forms) in your application using [Angular 1 or 2](/angular), [React.js](/react) or [Vue.js](/vue).
Our form building capabilities can also be embedded within your own application so that you can offer the same powerful form building experience to your customers.
## What's Included With Form.io?
### The Embedded Enterprise And SaaS Offerings all include:
#### Developer Portal
Form.io's primary interface that enables developers to manage projects, sub-projects, teams, resources, forms, PDFs, submission data, and more.
#### Form & API Builder
The drag and drop interface that enables developers to build forms and their APIs in one step automatically.
#### Form Renderer
The JavaScript rendering engine, compatible with all major frameworks, that renders a single string into forms on page at the application level.
#### FormView Pro
Launch completed forms in a single-page application, manage users and authentication, view, manage, and export submission data, and define form permissions.
## Start Building Forms & APIs In 5 Minutes With Form.io Enterprise SaaS
### Get the open embedded platform hosted for you on [portal.form.io](https://portal.form.io "Form.io Developer Portal") so you can start rapid-prototyping on your customer-centric apps today, no credit card required.
## What's In The Embedded Enterprise Configurations?
### Your configuration in your environment means no surprise usage fees.
#### Developer Portal
Included Form.io's primary interface that enables developers to manage projects, sub-projects, teams, resources, forms, PDFs, submission data, and more.
#### Form & API Builder
Included The drag and drop interface that enables developers to build forms and their APIs in one step automatically.
#### Form Renderer
Included The JavaScript rendering engine, compatible with all major frameworks, that renders a single string into forms on page at the application level.
#### FormView Pro
Included Launch completed forms in a single-page application, manage users and authentication, view, manage, and export submission data, and define form permissions.
#### PDF Plus Server
Optional Convert PDFs into forms to collect data, output to PDF for user-facing downloads, enable pixel-perfect form backgrounds, and digital webform overlays.
#### Enterprise Form Builder
Optional The Enterprise Form Builder is a configurable module that enables you to provide your customers a fully white-labeled, customized, pre-wired form building experience in your app.
#### Premium Components
Optional Revisions, collision control, automatic accessibility, security and encryption, translations, e-signatures, audit logging, email integration, offline mode, and more.
#### Multi-Tenancy
Optional Provide your customers with their own form, API, and data management tools, fully white-labeled under your brand or your customers' brands.
### Self-Hosted, Enterprise Deployments That Won't Burden Your IT People
The flexible, configurable main API platform and portal interface for Form.io plus your selection of à la carte enterprise addons, completely wired, licensed, and maintained for you with all dependencies, delivered to you through your orchestration of choice, including Docker container.
Deploy within your own on-premise or private cloud production and non-production environment(s) with total control and peace of mind.
## Complex Connections Made Simple
### Immediately connect your application to the 3rd-party apps you rely on with the combination of our dynamic JSON powered forms and our 3rd-party integrations.
 #### Need More Answers?
Ask and we'll get back with you in 1 business day.
###### Contact Us
[Send us a message](/contact-us "Contact Us") to contact support or ask a question.
Schedule a meeting
###### Open Source Platform
Read our [FAQ](/faq) to find out what exactly is Open Source
View the [Platform Documentation](https://help.form.io/)
View the [API Documentation](https://apidocs.form.io/?version=latest)
View the [Open Source Code](https://github.com/formio/formio)
###### Learn More
Learn [How It Works](/how-it-works)
Read the [Release Notes](/release-notes)
Discover [Industries](/industries) that use Form.io
Read our [Blog](/blog)
---